🚨 LiteLLM, a Python package for connecting to AI model providers with 92M+ monthly downloads, has been compromised.
Version 1.107.0 ships credential-stealing malware through PyPI wheels and Docker images, targeting cloud credentials, developer secrets, and AI tools.
The malware runs at Python startup, even without importing LiteLLM. The release workflow built container images from a lookalike repository.
Full analysis: https://socket.dev/blog/litellm-compromise
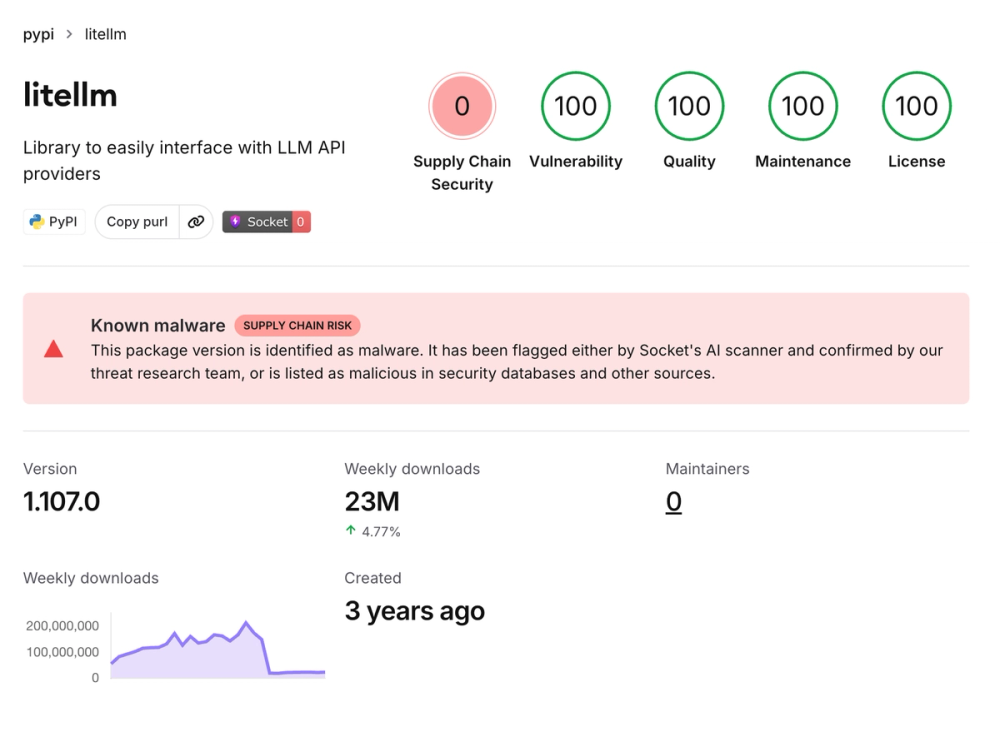 socket.devLiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI CredentialsA supply chain attack compromised LiteLLM 1.107.0 on PyPI and Docker, spreading malware that steals cloud credentials, developer secrets, and AI provider keys.