X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

PhishU

@[email protected]

Get Caught, Then Join the School! - Advanced Spear Phishing Tools and Services for Red Teams and Internal Orgs - https://PhishU.net

Open remote profile ↗
Posts

Reported by eSecurity Planet this week: a phishing campaign targeting 40,000 organizations through Microsoft 365 calendar invites, the part most mail filters never inspect.

Teach your team one thing this week. A calendar entry does not get the "check the sender, hover the link" scrutiny an inbox message does, so do not click a link inside a meeting invite you did not expect.

What are you telling users about unexpected calendar invites right now?

We run this exact technique against authorized targets, with training included. More at https://phishu.net/calendar-event-phishing-simulation.html

We round up the week's phishing news in The PhishU Weekly, https://phishu.net/newsletter
#CyberAware #SecurityAwareness #CybersecurityAwareness #AwarenessMonth

phishu.netCalendar Event Phishing Simulation | PhishU FrameworkSimulate calendar-based phishing with native event rendering, reminders, and training in the PhishU Framework.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

MFA approved the login. The mailbox stayed compromised for weeks.

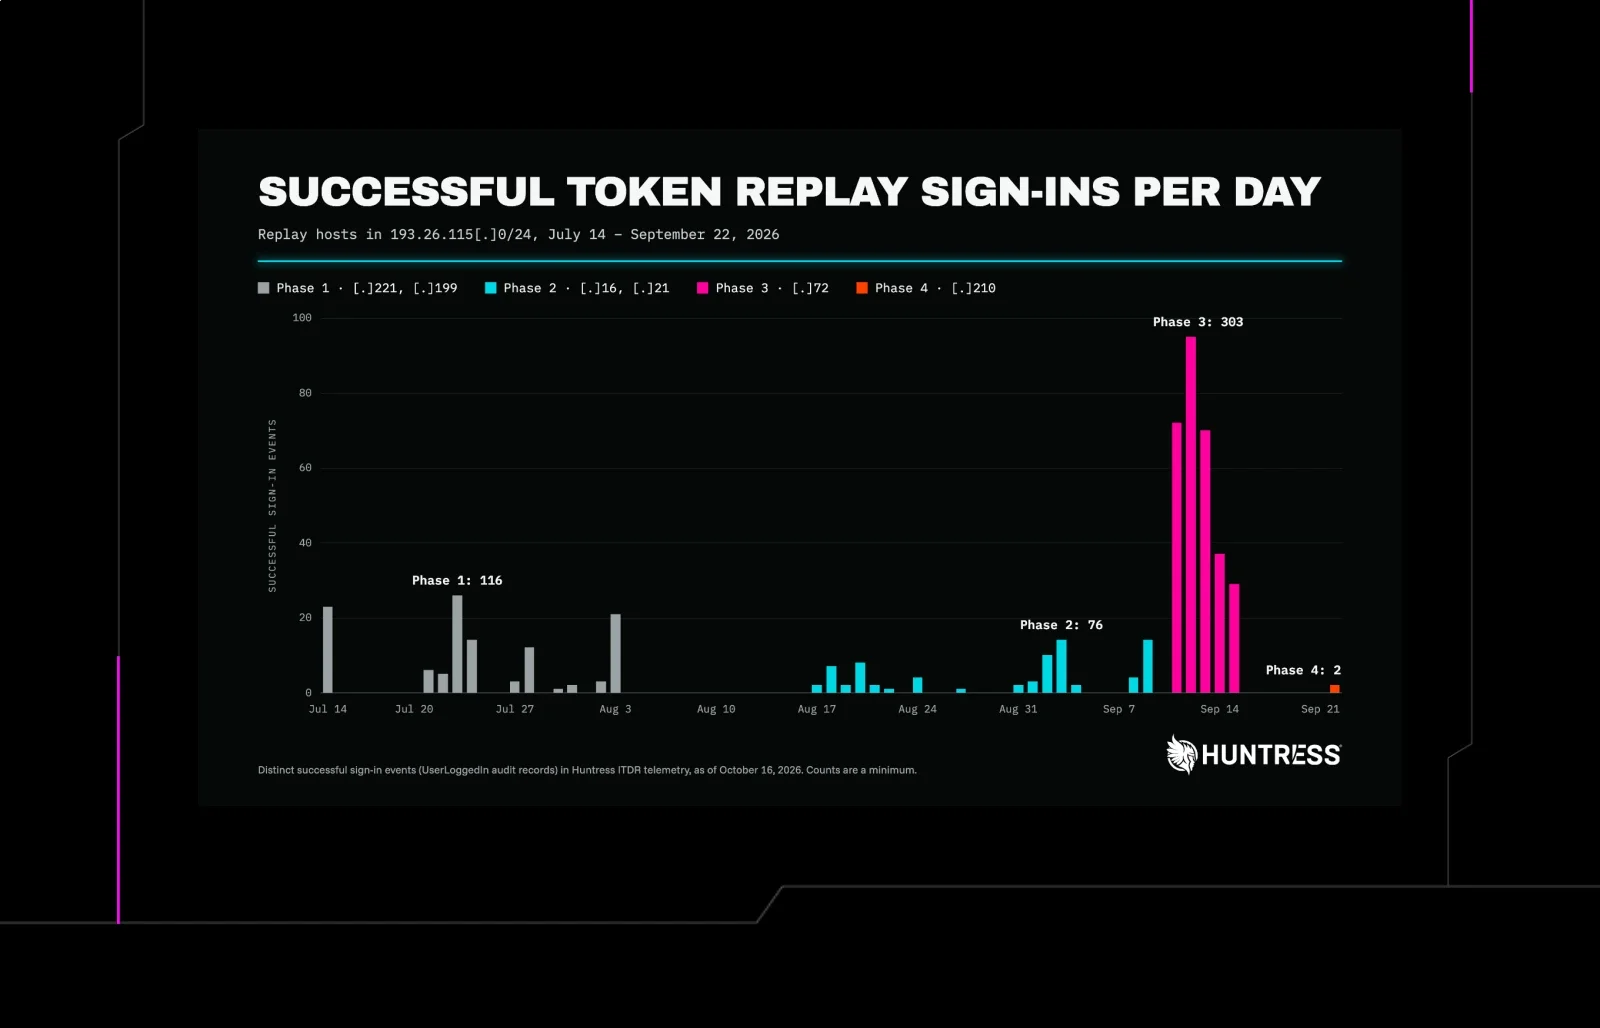
Huntress detailed a 10-week Microsoft 365 campaign this week that ran the full chain: an adversary-in-the-middle relay, a replayed session token, a rogue Entra device, MFA tampering, and hidden inbox rules.

You can do one thing today. Read your own inbox rules in your mail settings, and delete any that forward or hide messages you did not create. Teach your team to check theirs.

In the authorized engagements we run, MFA passes and the session is captured anyway. Their full write-up is at https://www.huntress.com/blog/token-replay-spray

More like this every Monday in our newsletter at https://phishu.net/newsletter

#AiTM #SessionHijacking #Microsoft365 #IdentitySecurity #ConditionalAccess #CyberAware #SecurityAwareness #CybersecurityAwareness #AwarenessMonth

HuntressM365 Token Spray and Replay Campaign Compromises Business Email Accounts | HuntressHuntress tracked a 10-week Microsoft 365 campaign pairing AiTM relays with token replay, rogue Entra devices, MFA tampering, and hidden inbox rules.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

ClickFix just went from a trick to a delivery service. The Hacker News covered it today, with Forescout's Vedere Labs documenting ROMULUS, a ClickFix platform pushing LegionLoader.

Teach your team this today: never paste a command into Run, PowerShell, or Terminal because a web page told you to. That is the whole attack.

There is no login page and no password prompt, so the usual 'check the URL' advice misses it entirely. We tie training to the exact lure someone hit.

Have your users ever been trained to spot a paste-and-run lure?

We broke down how ClickFix works on our blog. https://phishu.net/blogs/blog-clickfix-in-the-phishu-framework.html

More like this every Monday in our newsletter. https://phishu.net/newsletter
#CyberAware #SecurityAwareness #CybersecurityAwareness #AwarenessMonth

https://thehackernews.com/2026/10/romulus-clickfix-platform-tricks-users.html

PhishUClickFix in the PhishU FrameworkA high-level look at how the PhishU Framework turns ClickFix into a point-and-click template with callback analytics, console visibility, and campaign-linked training.
↩ Reply ♡ 0 · ↻ 0 ↗ Original