MFA approved the login. The mailbox stayed compromised for weeks.
Huntress detailed a 10-week Microsoft 365 campaign this week that ran the full chain: an adversary-in-the-middle relay, a replayed session token, a rogue Entra device, MFA tampering, and hidden inbox rules.
You can do one thing today. Read your own inbox rules in your mail settings, and delete any that forward or hide messages you did not create. Teach your team to check theirs.
In the authorized engagements we run, MFA passes and the session is captured anyway. Their full write-up is at https://www.huntress.com/blog/token-replay-spray
More like this every Monday in our newsletter at https://phishu.net/newsletter
#AiTM #SessionHijacking #Microsoft365 #IdentitySecurity #ConditionalAccess #CyberAware #SecurityAwareness #CybersecurityAwareness #AwarenessMonth
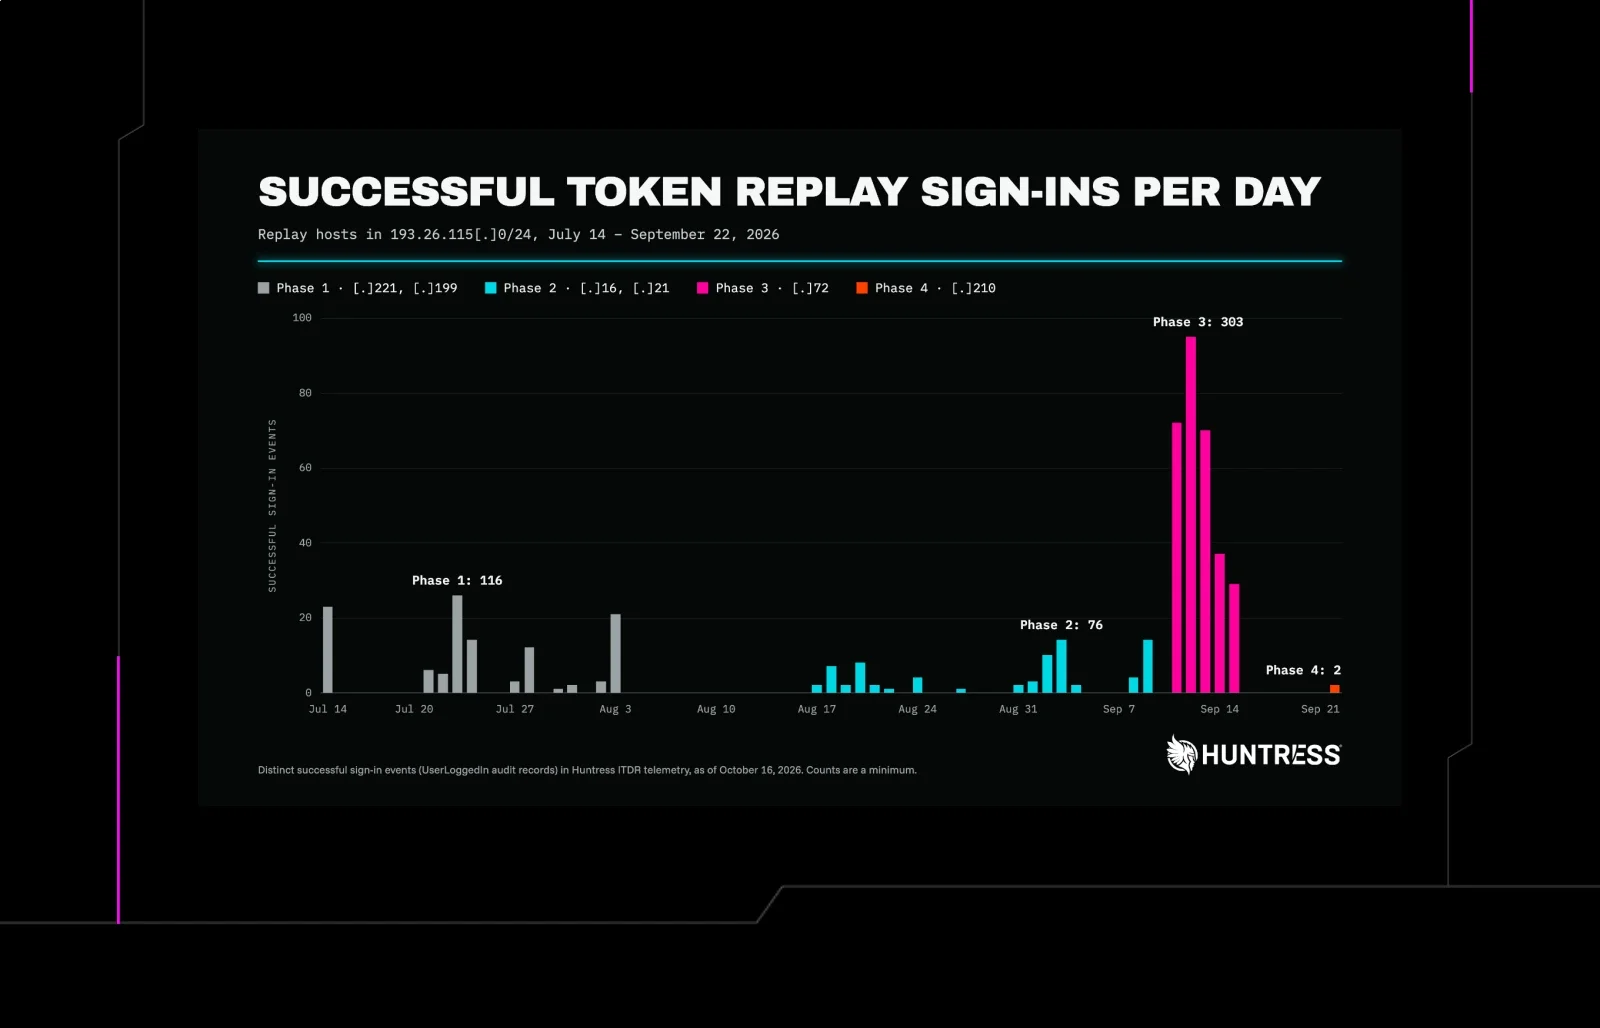 HuntressM365 Token Spray and Replay Campaign Compromises Business Email Accounts | HuntressHuntress tracked a 10-week Microsoft 365 campaign pairing AiTM relays with token replay, rogue Entra devices, MFA tampering, and hidden inbox rules.