X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

ANY.RUN

@[email protected]

Empowering businesses with proactive security solutions: Interactive Sandbox, TI Lookup and Feeds.

Open remote profile ↗
Posts

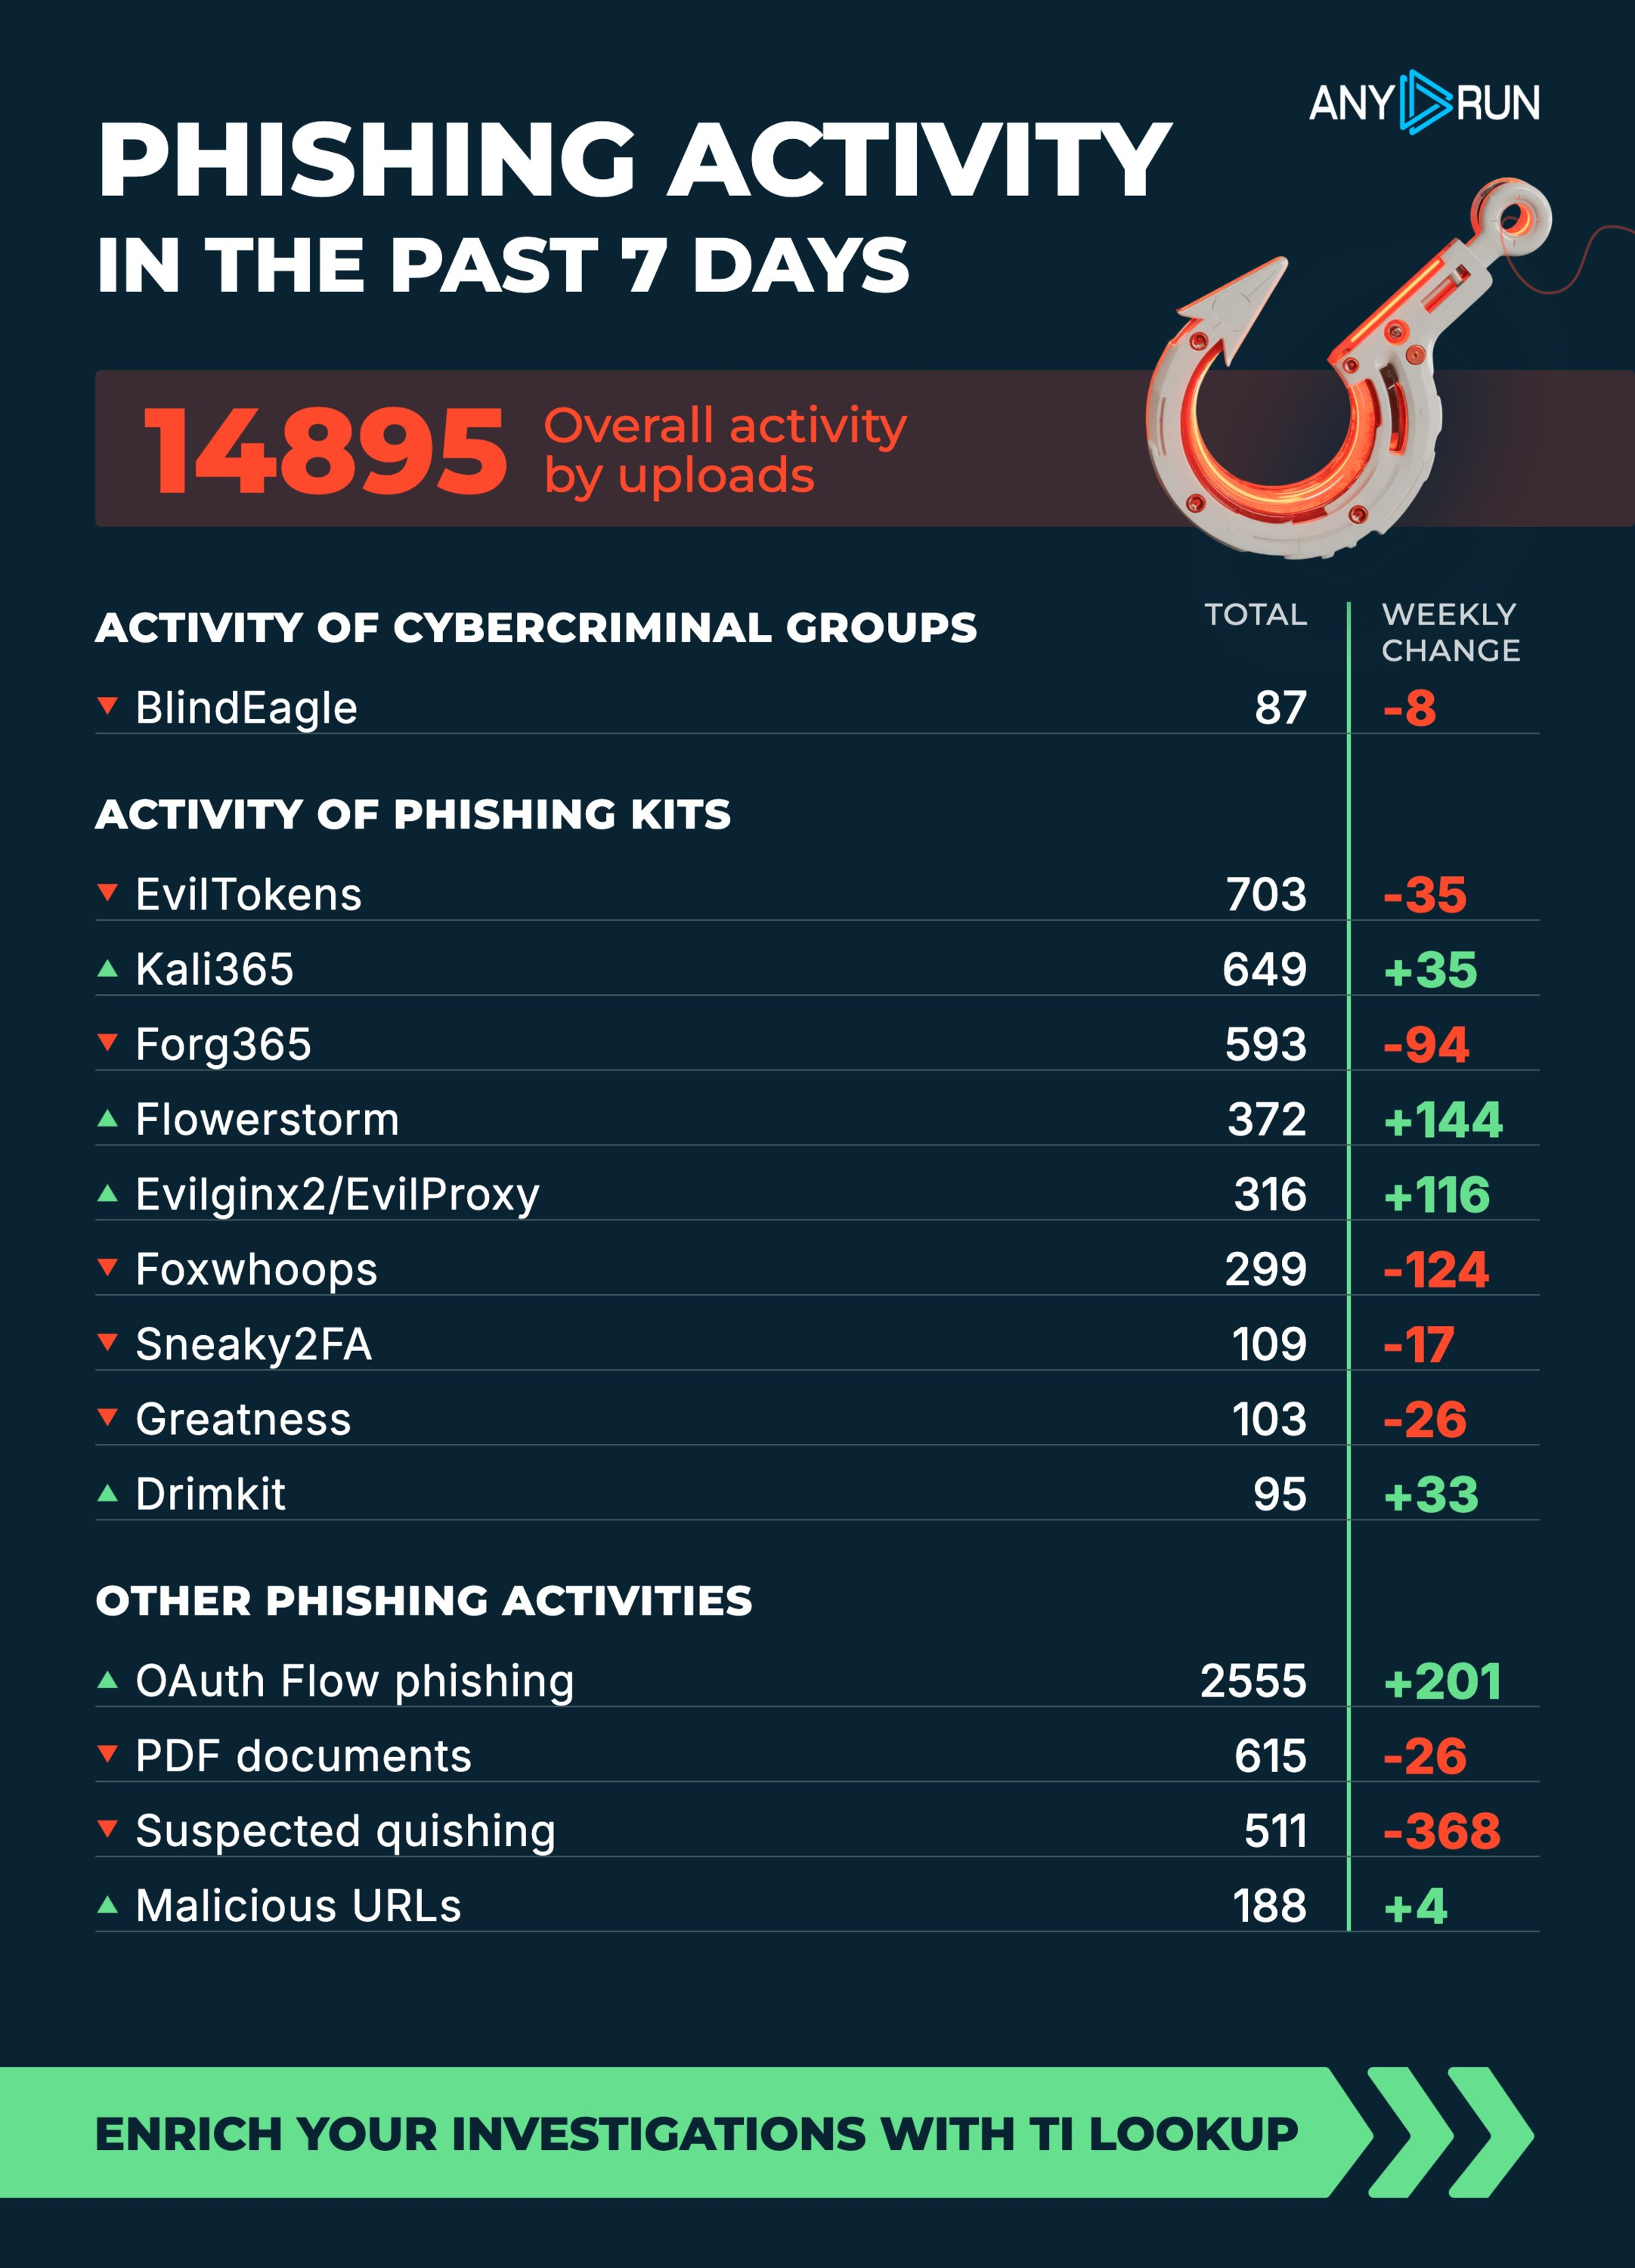
Phishing activity in the past 7 days 🐟
Track latest #phishing threats in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=top_phishing&utm_content=linktoti&utm_term=201026#%7B%2522query%2522:%2522threatName:%255C%2522%5Ephishing$%255C%2522%2522,%2522dateRange%2522:180%7D
#cybersecurity

Media attachment
intelligence.any.runThreat Intelligence Lookup – ANY.RUNSearch and enrich IOCs, get deep threat context, uncover related infrastructure, and investigate threats faster with ANY.RUN TI Lookup.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

#ANYRUN TI Feeds turn IOCs into continuous monitoring by streaming fresh, validated indicators and behavior-based threat data into your security stack.

💡 #IOC:
SHA256:
7f1db334fd3302cf98dd4afddf6f90e98e2a496fe7e86bf1832b89d02f3d73c3
835800058050be37366478c662f73d7fcb93a2669e44f98664546fbc8ee6c7ca
74aaa6b54133bbb2e77b2ae874e9900a907c269058f798a0a1197288ba1f7124
C2:
westbeavers[.]com
healskills[.]com
motherotters[.]com

↩ Reply ♡ 0 · ↻ 0 ↗ Original

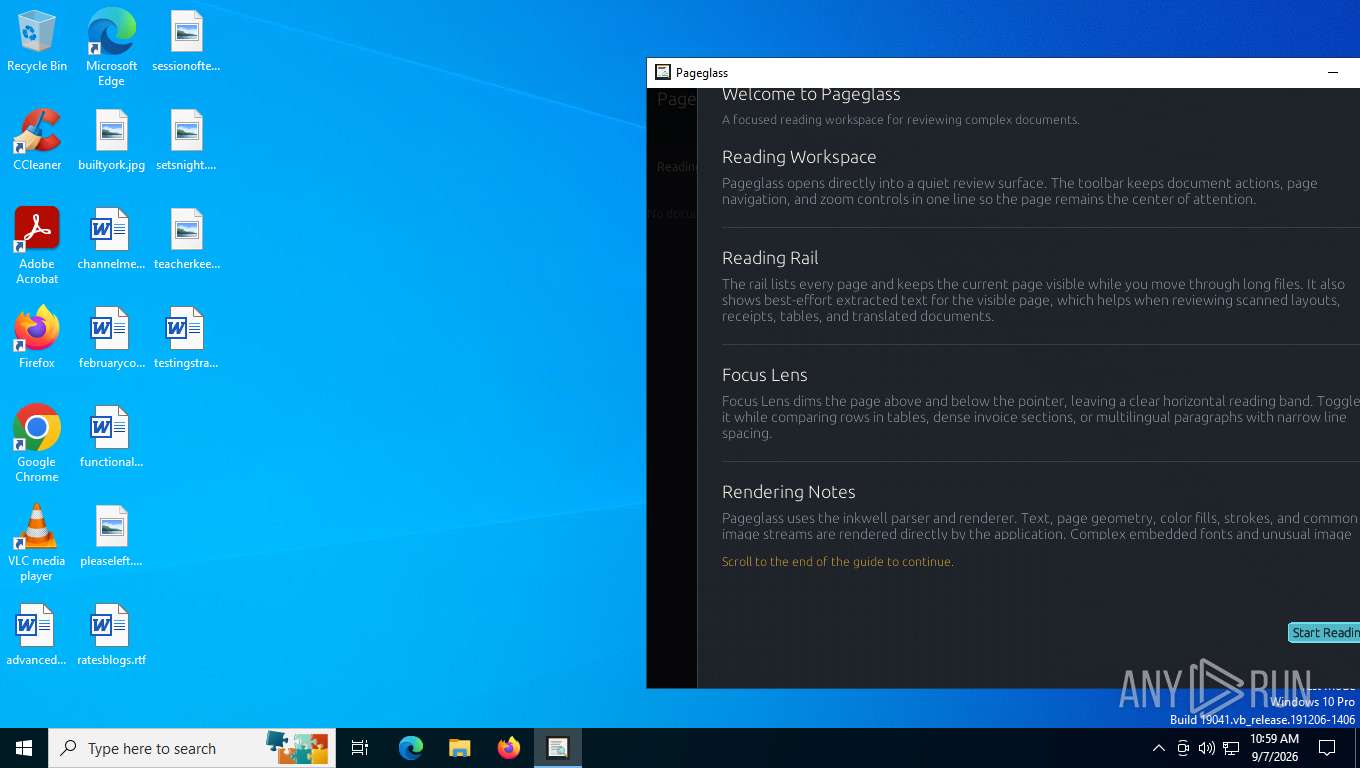
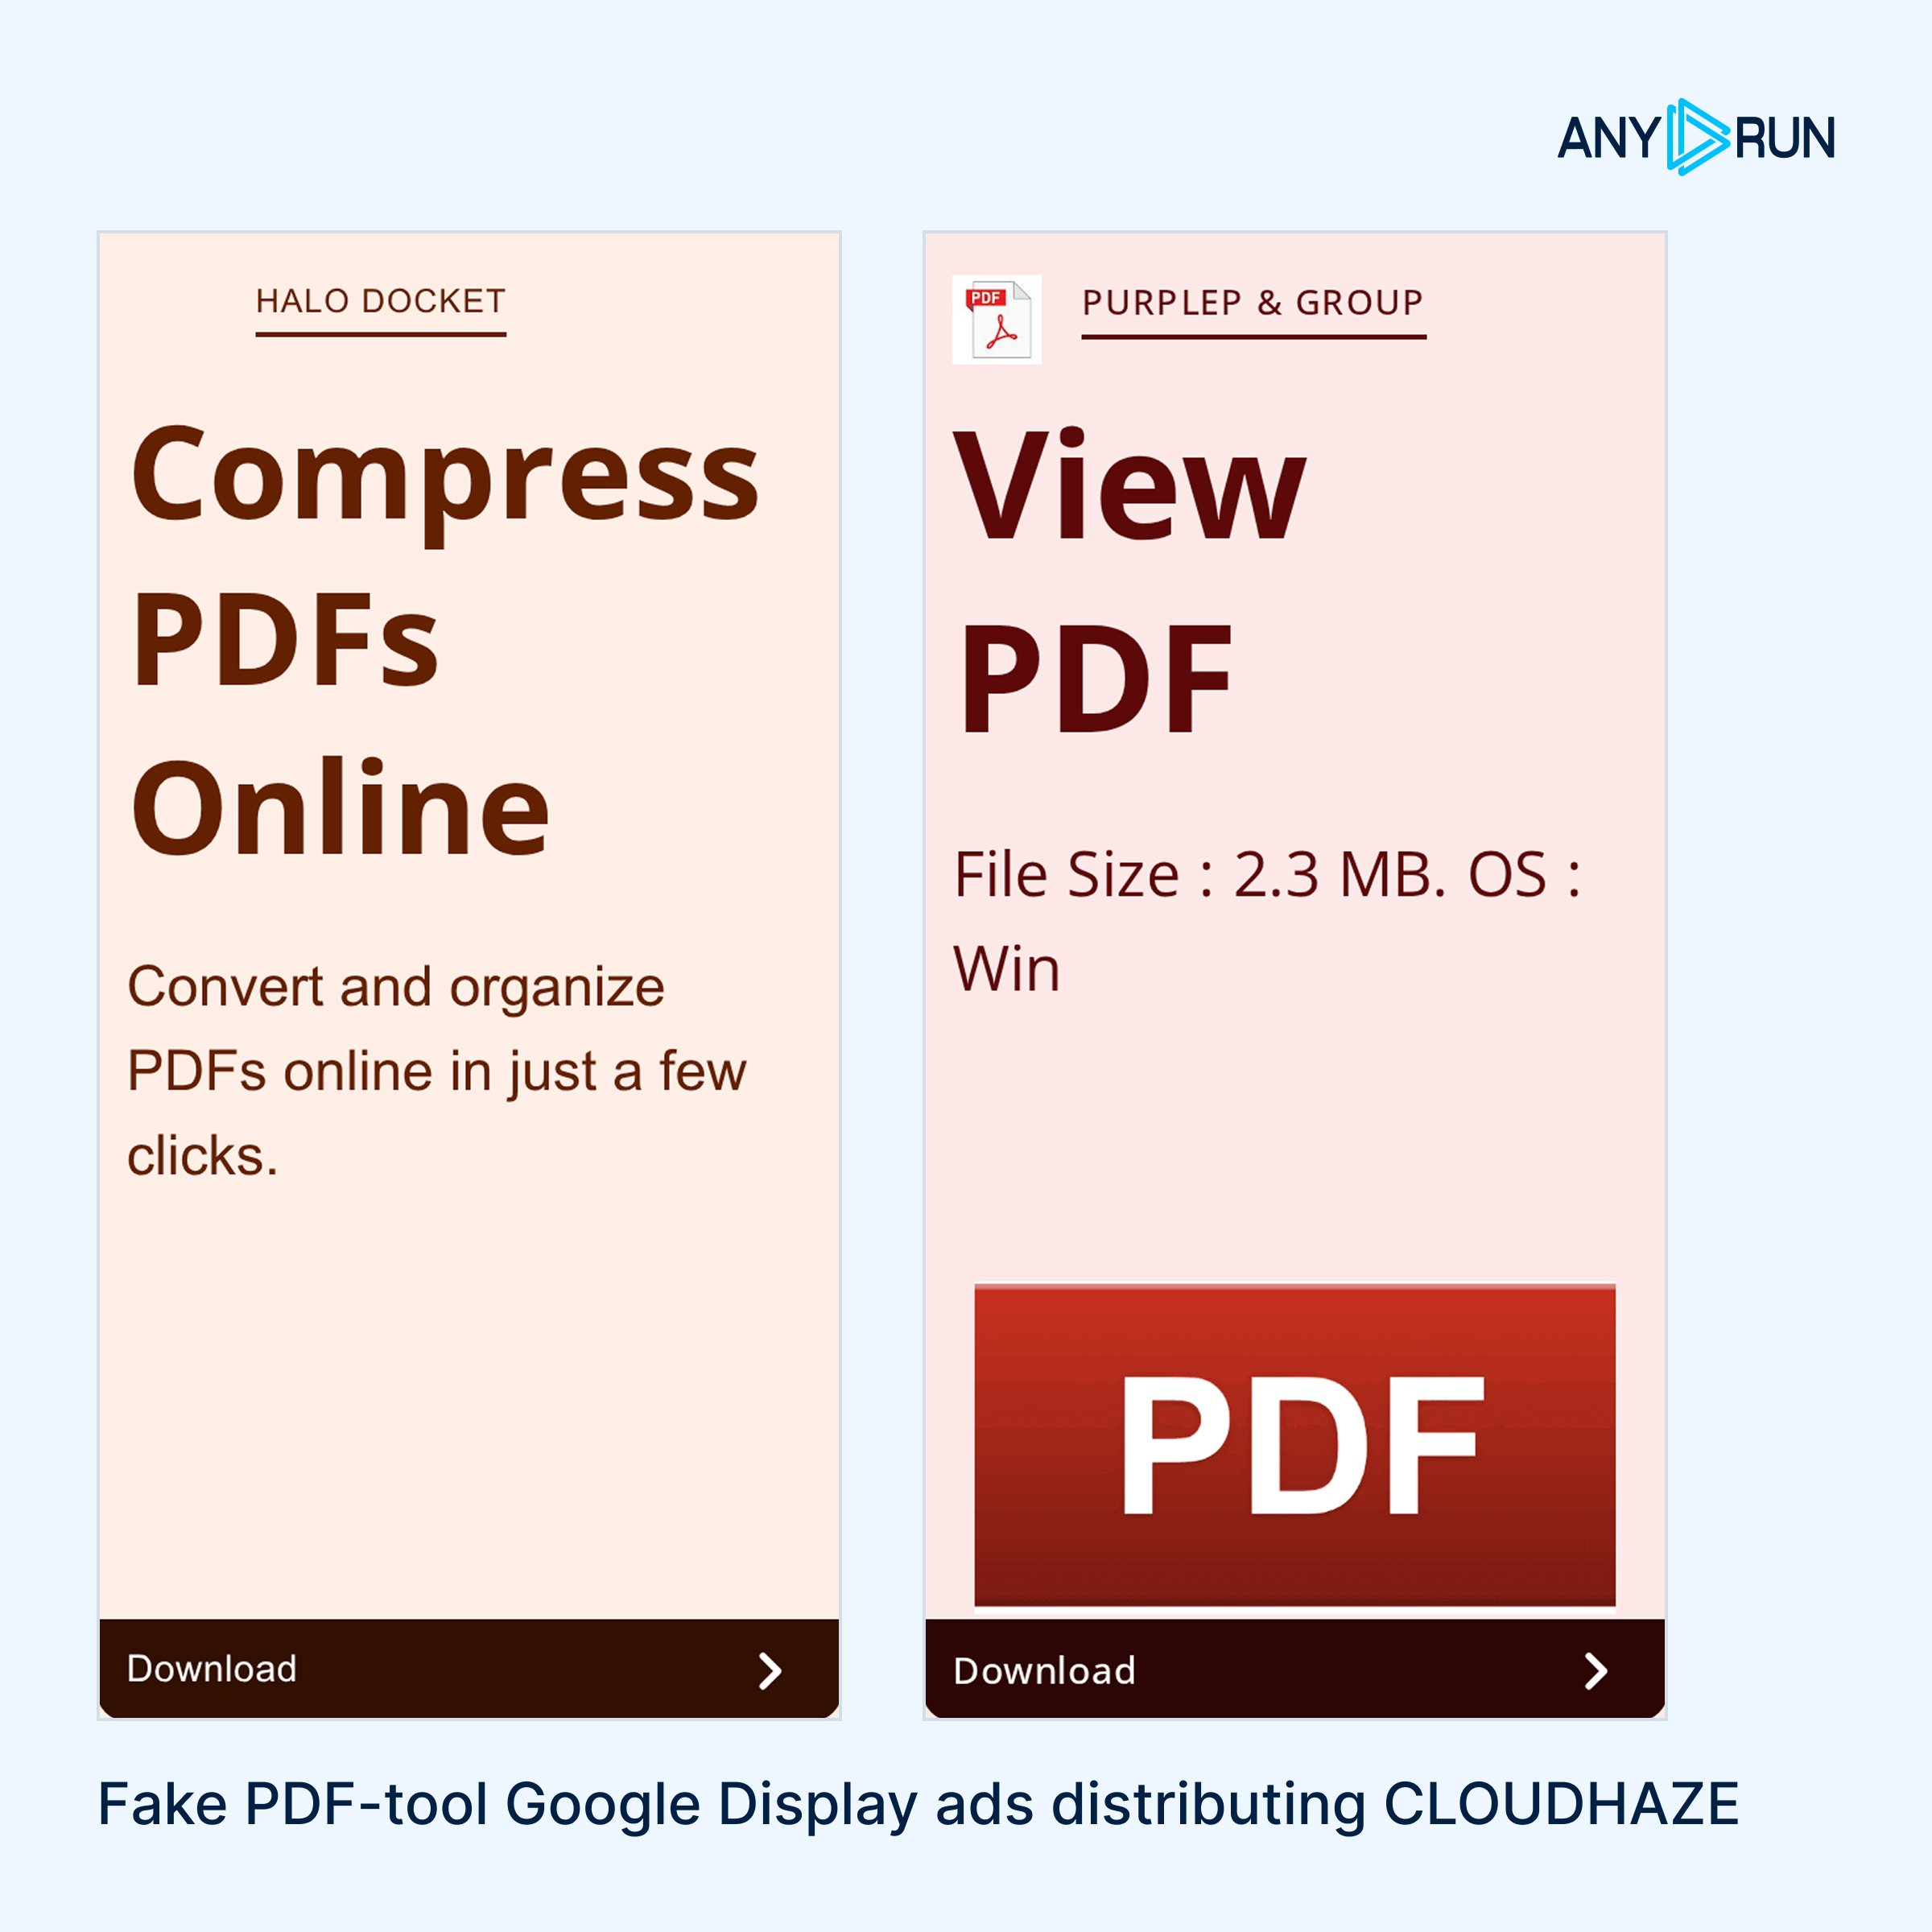
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.

586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.

❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026

⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D

#cybersecurity #infosec

Media attachment
app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

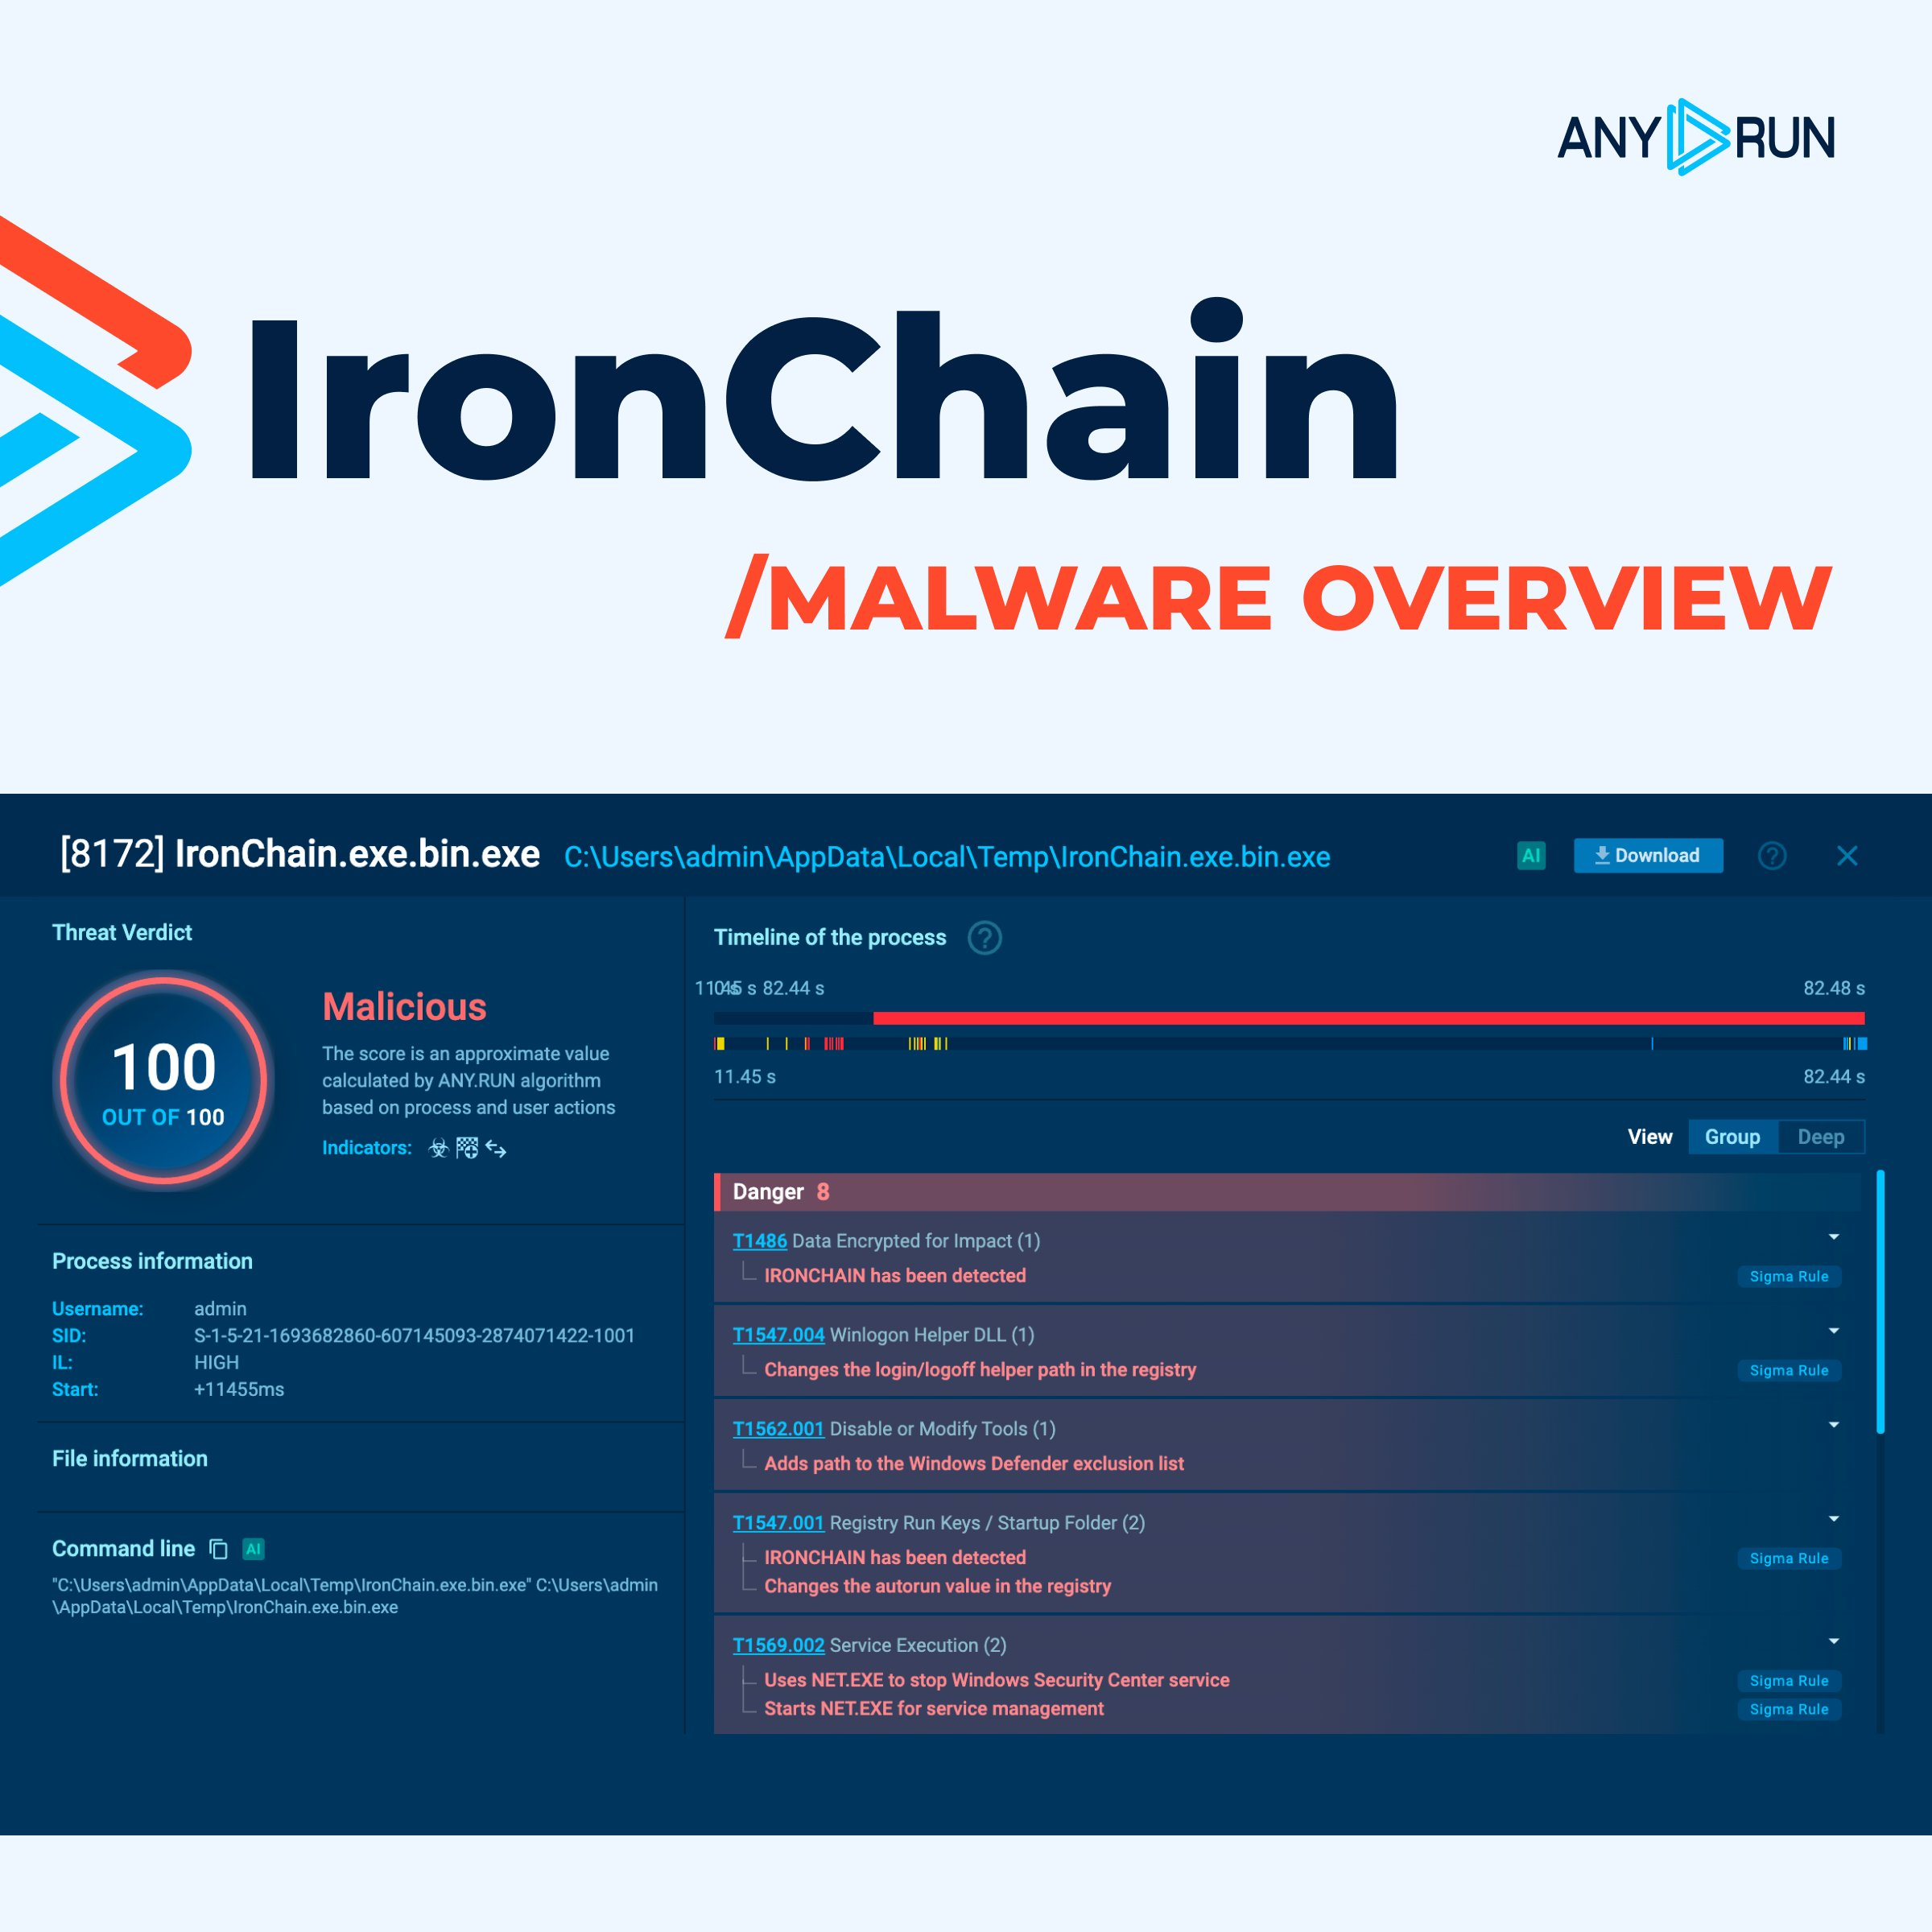
⚠️ #IronChain uses elevated privileges & kernel-level components to weaken security controls before encrypting files. It can disrupt Windows systems and leave organizations facing data loss and extended downtime.

👨‍💻 How to detect it before damage occurs: https://any.run/malware-trends/ironchain/?utm_source=mastodon&utm_medium=post&utm_campaign=ironchain_mtt&utm_term=191026&utm_content=linktomtt

#cybersecurity #infosec

Media attachment
IronChain | Malware Trends TrackerIronChain | Malware Trends TrackerLearn how IronChain uses privileged execution, kernel drivers, and file encryption to compromise Windows systems and cause destructive damage.
↩ Reply ♡ 0 · ↻ 0 ↗ Original