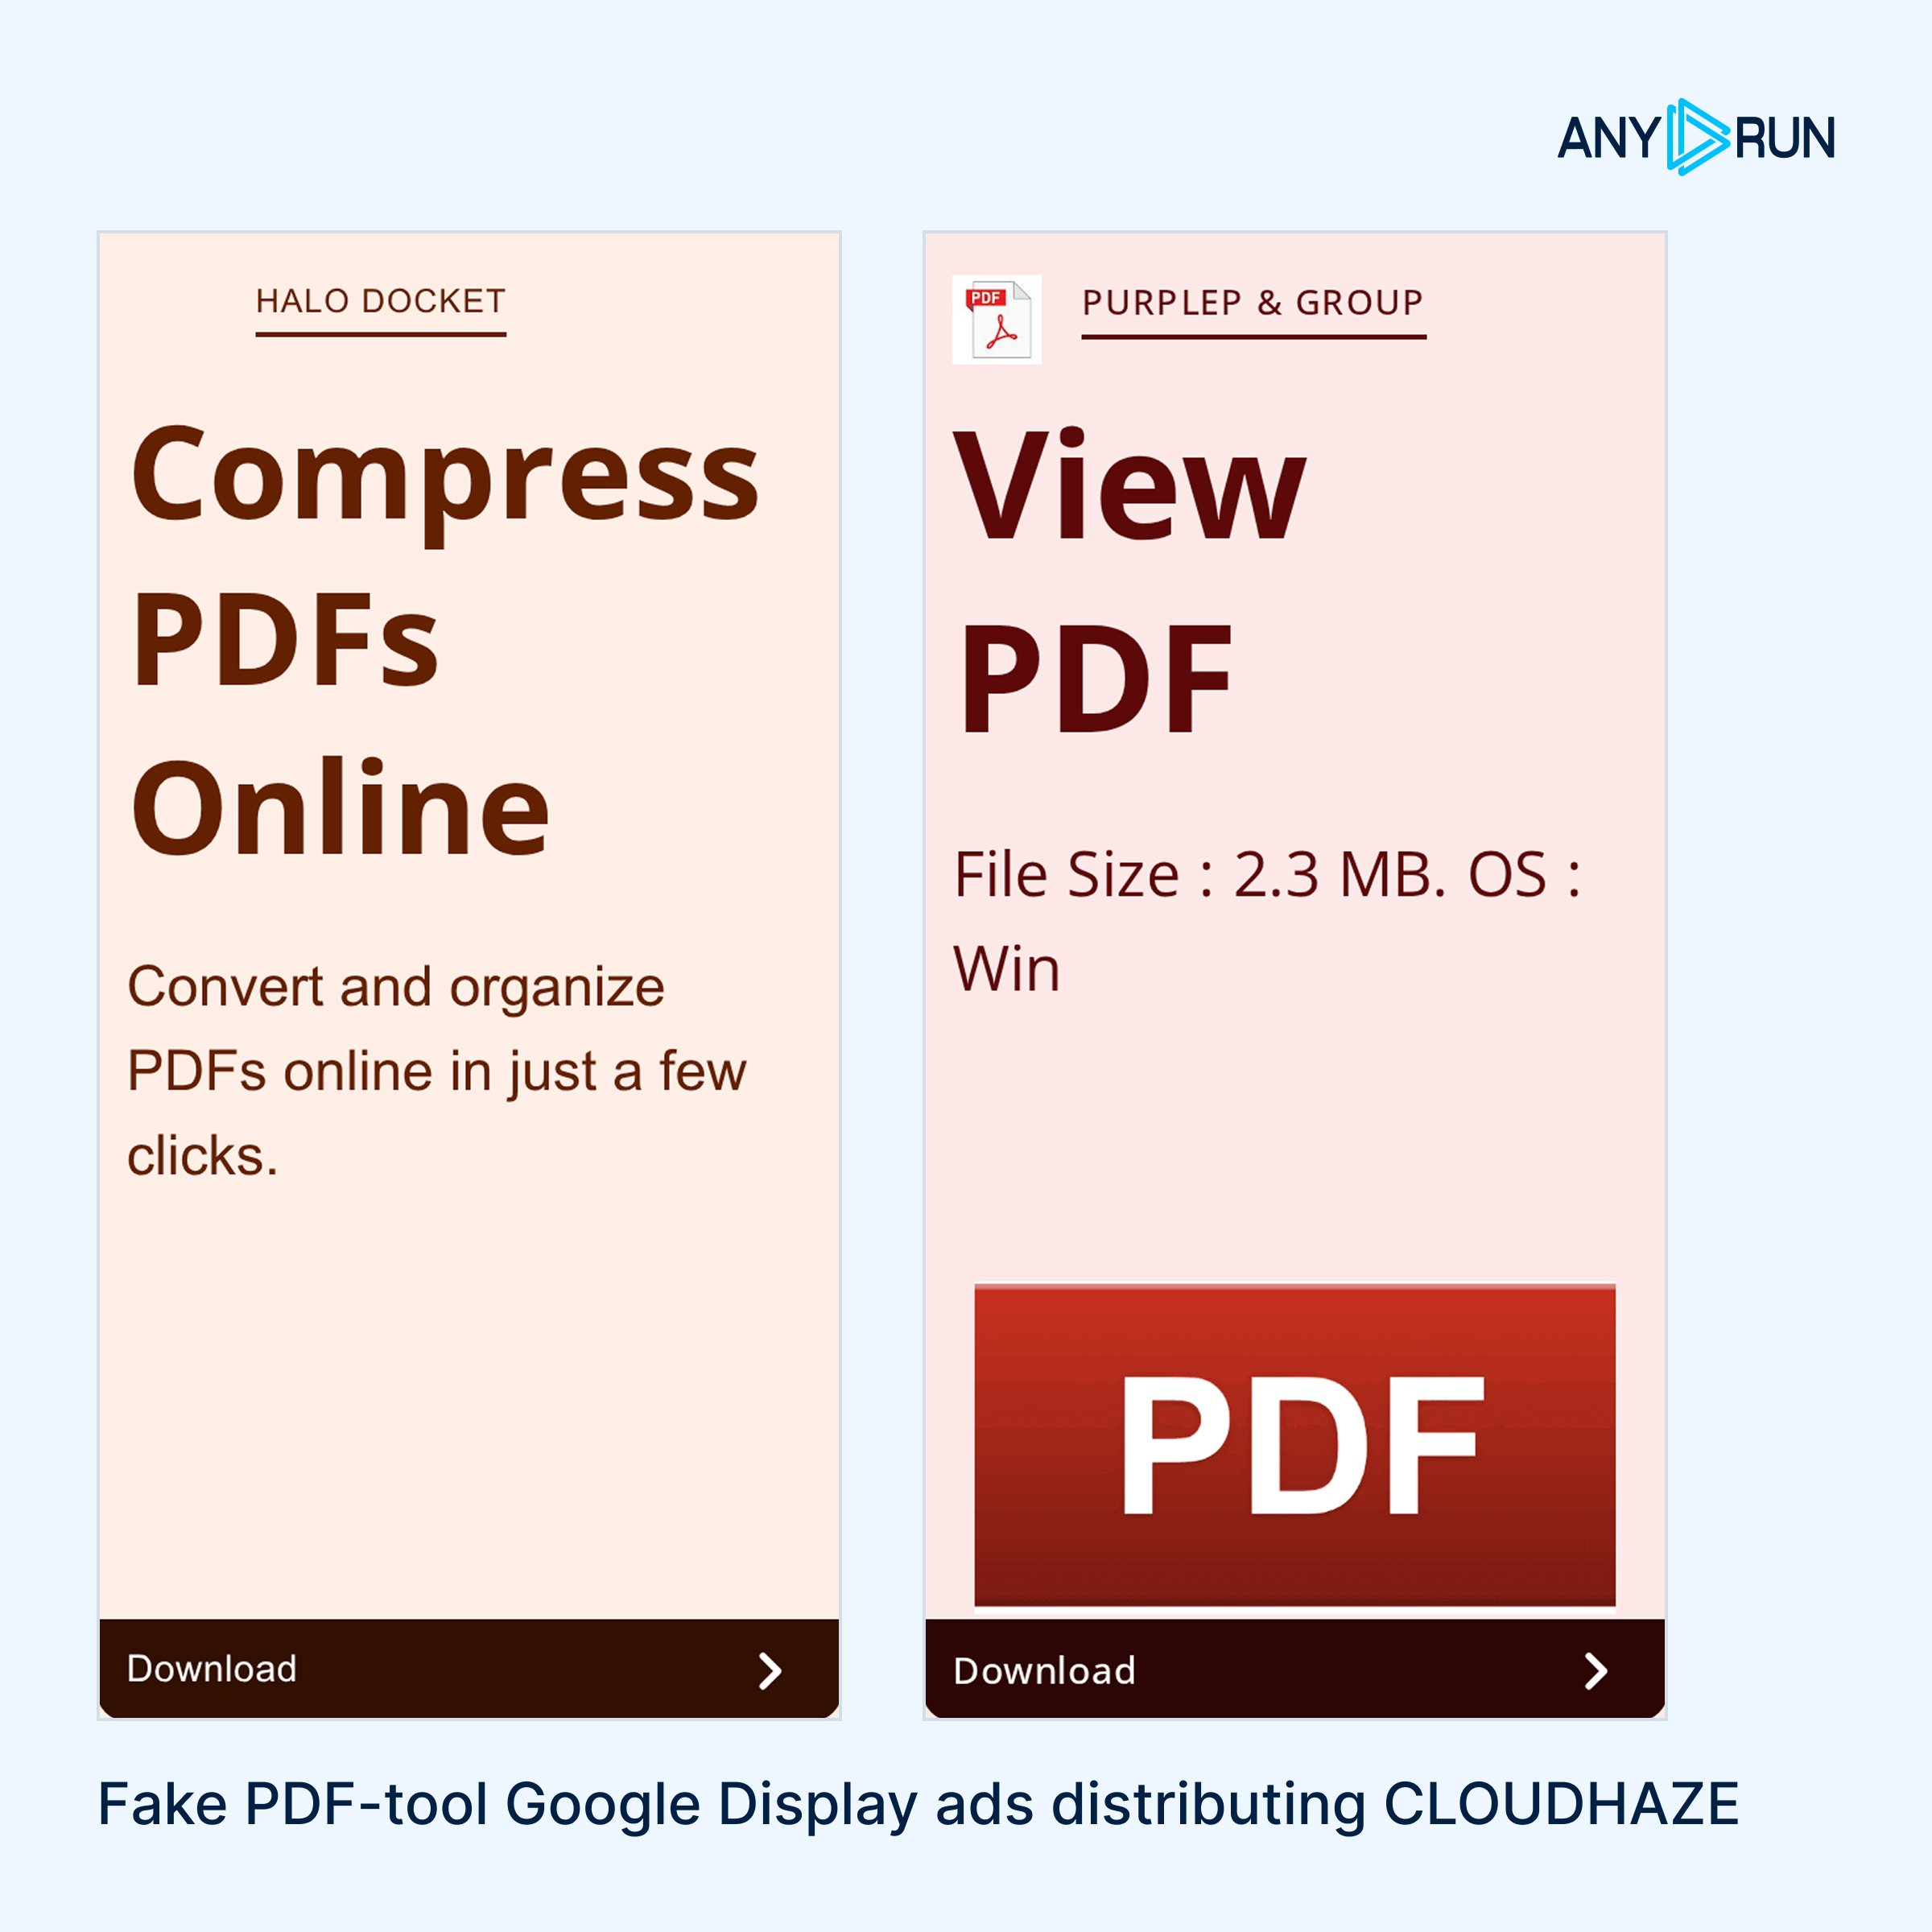
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.
586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.
❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026
⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D
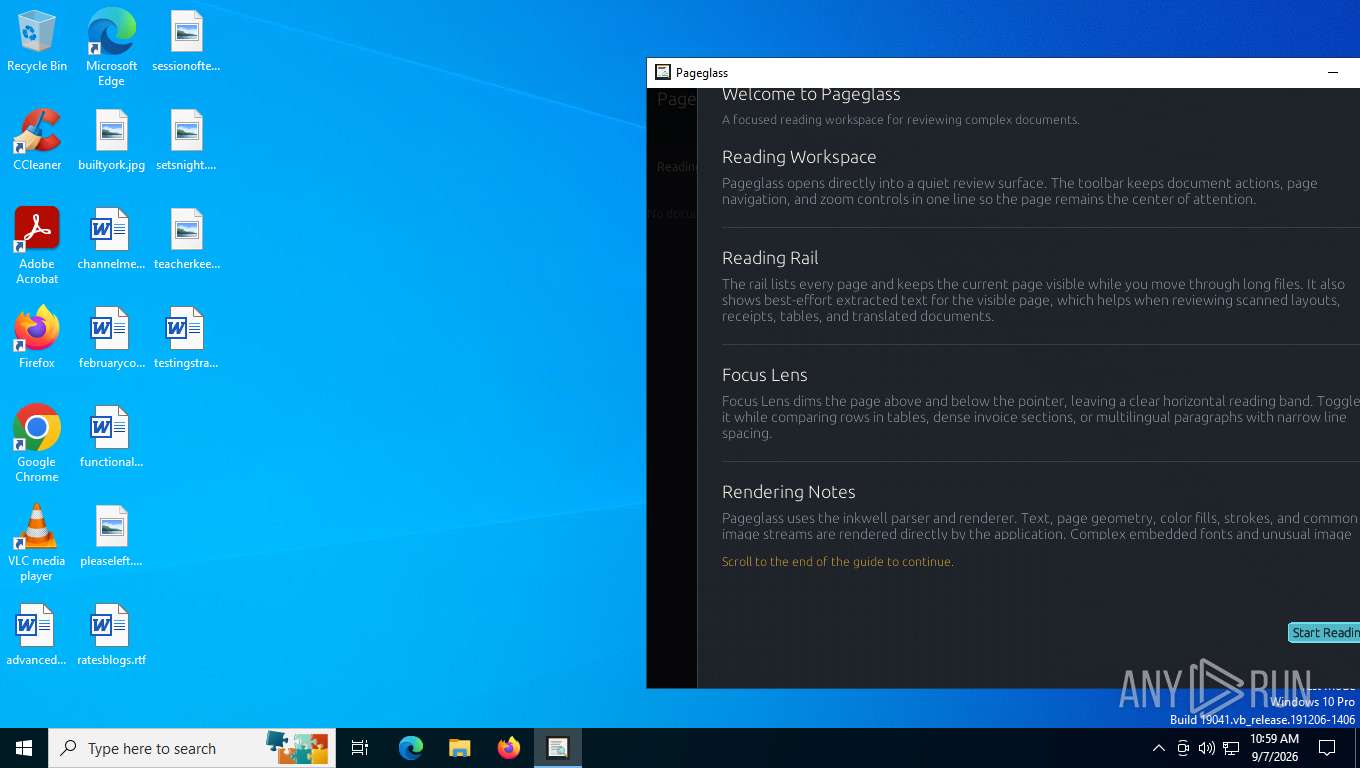 app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.