X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

PinkAramidCompositePotato

@[email protected]

Senior Security Researcher, Proofpoint Emerging Threats. Digital Arcanist
I've been doing this cybersecurity thing for the better part of a decade now. Probably longer than that. I'm starting to forget. Time is relative, but it surely isn't kind to my memory.
I'd like to think I do cybersecurity well, but blue teamers collectively get told they're doing it wrong constantly. So maybe I just failed forward throughout my career.
Oh, I wrote a book. Its a good framework for setting up a virtual machine lab. See my bookmarked toots if you're curious.
Finally, I occasionally write about tech/nerd-re

Open remote profile ↗
Posts
↳ In reply to a post

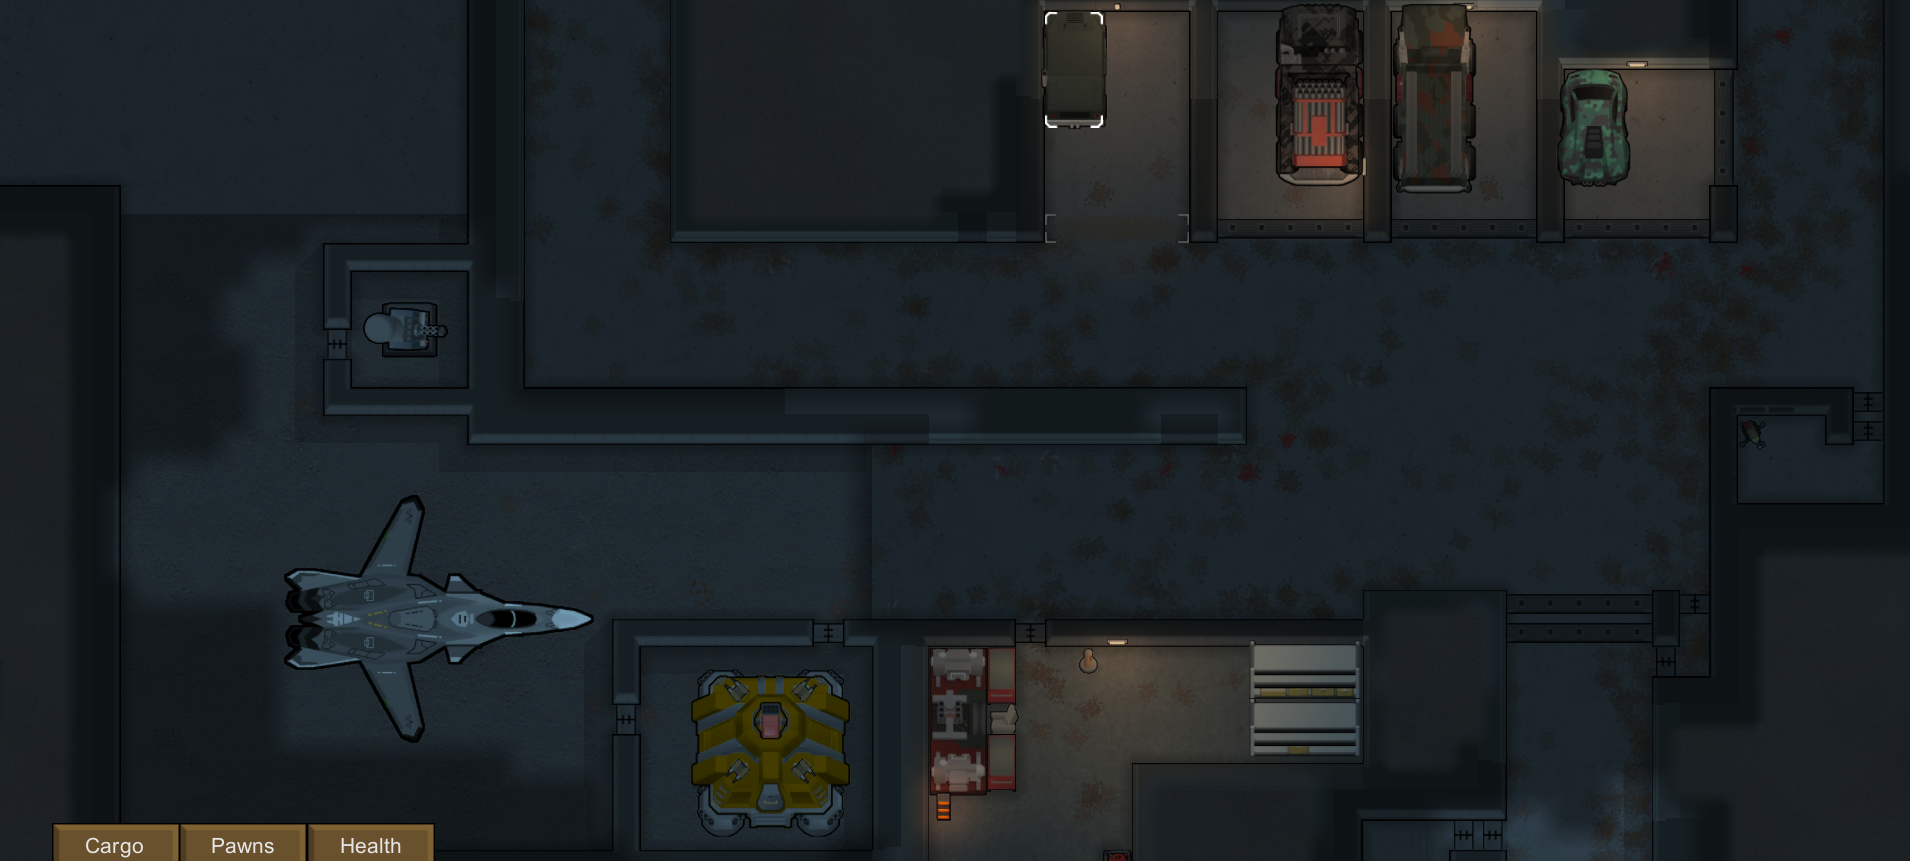
my mechbay opens up into a huge underground highway that goes around my base. I have some areas blocked off with armored doors into the rest of the mountain. More than once I've propped open the doors when a bug have invasion has happened, said "COME THE FUCK ON IN, IT ISNT A PARTY WITHOUT YOU". and let them experience flamethrowers.

Of course, the flamethrowers don't kill all of them, but fun fact: bugs are susceptible to smoke, and will wander around in a daze if exposed to it for too long. So then it was just a group of four colonists with beam sabers in full power armor with full immunity to smoke inhalation wandering into the tunnels, hacking away at bugs who were too out of it to defend themselves.

Media attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

So, where am I going from here in the Suricata Book?

As much as I said I'm done with the TLS inspection stuff for chapter 10, there is one last thing I want to include before moving on.

A large portion of the TLS inspection chapter was how to architect an environment to use SSLProxy or PolarProxy.

I include like 3-4 pages of troubleshooting recommendations for SSLproxy, but I didn't really put anything together for troubleshooting problems with PolarProxy. I went over how to configure PolarProxy for two modes of operation: TLS Forward Proxy (like SSLProxy) and having it operate as an HTTP CONNECT proxy. I'd like to make sure that I point readers back to the troubleshooting guidance for TLS proxy for those who run polarproxy in TLS forward proxy mode, but also include some basic troubelshooting guidance for running polar proxy in HTTP CONNECT proxy mode.

Once I do that, I want to do a chapter on noise reduction techniques. Like, what are the various ways in which IDS/IPS analysts can reduce false positives from Suricata, reduce the volume of alerts, etc.

I'd also like to do a "Odds and Ends" chapter on interesting use-cases for suricata. This would be the hodge-podge chapter where I can talk about interesting and creative ways that Suricata can be used.

For example, in a previous chapter, we went over the anatomy of a suricata rule, but I wanted to incorporate some writing I've done in the past on how to make flexible suricata rules.

https://community.emergingthreats.net/t/flexible-rule-writing-seeing-around-the-bend/2568

I did a blog post about it, but I want to re-work it into my book to serve it out to a wider audience.

I want to talk about some writing on of my previous co-workers, Brandon Murphy did about how byte_jump, and isdata at can be used to help scope RAT C2 traffic:

https://community.emergingthreats.net/t/the-complexities-of-byte-jump/111

I'd also like to talk about methods of utilizing the ET_INFO ruleset, and how rule writers can make customized rules that are custom tailored to capture data exfiltration in their environments:

https://github.com/da667/Contalks/tree/main/General%20Motors

I want to show readers that the ET INFO ruleset isn't just a bunch of "benign" alerts about common web traffic, but in many cases, if you know what your software inventory is, and what tools/resources your users utilize on a regular basis, how some of these rules can identify changes in behavior and be used for threat hunting.

I also want to talk about iot_hunter, and how it helps automate threat research and generate rules for Iot vulnerabilities rapidly.

I want to talk about some of our regular expressions we use as ET rule writers that help cover a variety of vulnerability classes (e.g. command injection, directory traversal, sql injection, etc.) that the user community can re-use for their own rule writing purposes.

I might consider talking about more subjects if there is any interest from the community or if there are interesting blog posts I've put up in the Emerging Threats community that I want to see make it to a wider audience.

I also want to
Emerging ThreatsFlexible Rule Writing: Seeing Around The BendHey Folks, I know you just saw me put down a pretty meaty blog post a few minutes ago, but this is another blogpost that is somewhat related. On top of that, I’m making it a personal goal this year to share a blog post on the community pages at least once per month, so I’m aiming for a double header to cover March and April 🙂 . Like the last entry I made, this blog will feature some rules I wrot
↩ Reply ♡ 0 · ↻ 0 ↗ Original

ICYMI,

Last friday I posted a significant update to Suricata: An Operator's guide, my book that dives into how network security teams can get the most of Suricata: a powerful open-source network intrusion detection/prevention suite.

While its primarily a book concerned with the intricacies of Suricata, how to deployment, how to write rules for it, and how to measure and improve its performance, a large portion of this work has been dedicated towards how to do a variety of threat research tasks, such as vulnerability research, and proof of concept reproduction, threat hunting, data pivoting, etc. in order gain enough indicators to assist in writing new Suricata rules.

This latest chapter I've completed details how Suricata can be used to inspect and analyze TLS-encrypted traffic, and goes over non-invasive methods of analyzing TLS through the use of Suricata's TLS keywords that can be used to inspect various aspects of TLS connections (e.g. server name indicators, certificate details, etc.). We also talk about the various options for decrypting TLS traffic to inspect the decrypted traffic within such as TLS Master Secrets logging, Host-based intercept proxies (e.g., mitmproxy, burp, zap, etc.), as well as live network-based decryption suites (e.g., SSLProxy, PolarProxy, etc.). We also discuss some of the weaknesses and difficulties that come with analyzing TLS encrypted traffic to be aware of.

I welcome you to download a copy over at leanpub.com/suri_operator. My books are always DRM-free PDFs, and the price will always be "pay what you want", with the minimum price set to free, because I want to educate our next generation of security professionals, for when I run off into the forests of norther Michigan to never be seen again.

As always, thank you to my followers, supporters and patrons for providing me with feedback along the way.

#Suricata #NSM #IDS #IPS #TLS #EscapeIntoTheWilds

↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

Speaking of Platte Lake, we took a look at a couple of places for sale over here. Long story short, none of them are really anything we can act on. But, we took beautiful pictures of big platte lake while we were out.

alt text: The center of this image is dominated by large oak and pine trees. The oak trees are just beginning to change shades, with the tips of the leaves, dappled in sunlight, switching to shades of orange, yellow, and red. In the bottom of the image is bright green, closely cropped grass leading out to the bright and shining big platte lake. Glittering from the sun's rays like diamonds on a light blue-green bed of the lake. Further on the distance shore, is a second ocean of trees, a blend of greens, reds, and oragnes fading into a lightly cloud sky of white, wispy clouds, and light blue.

Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

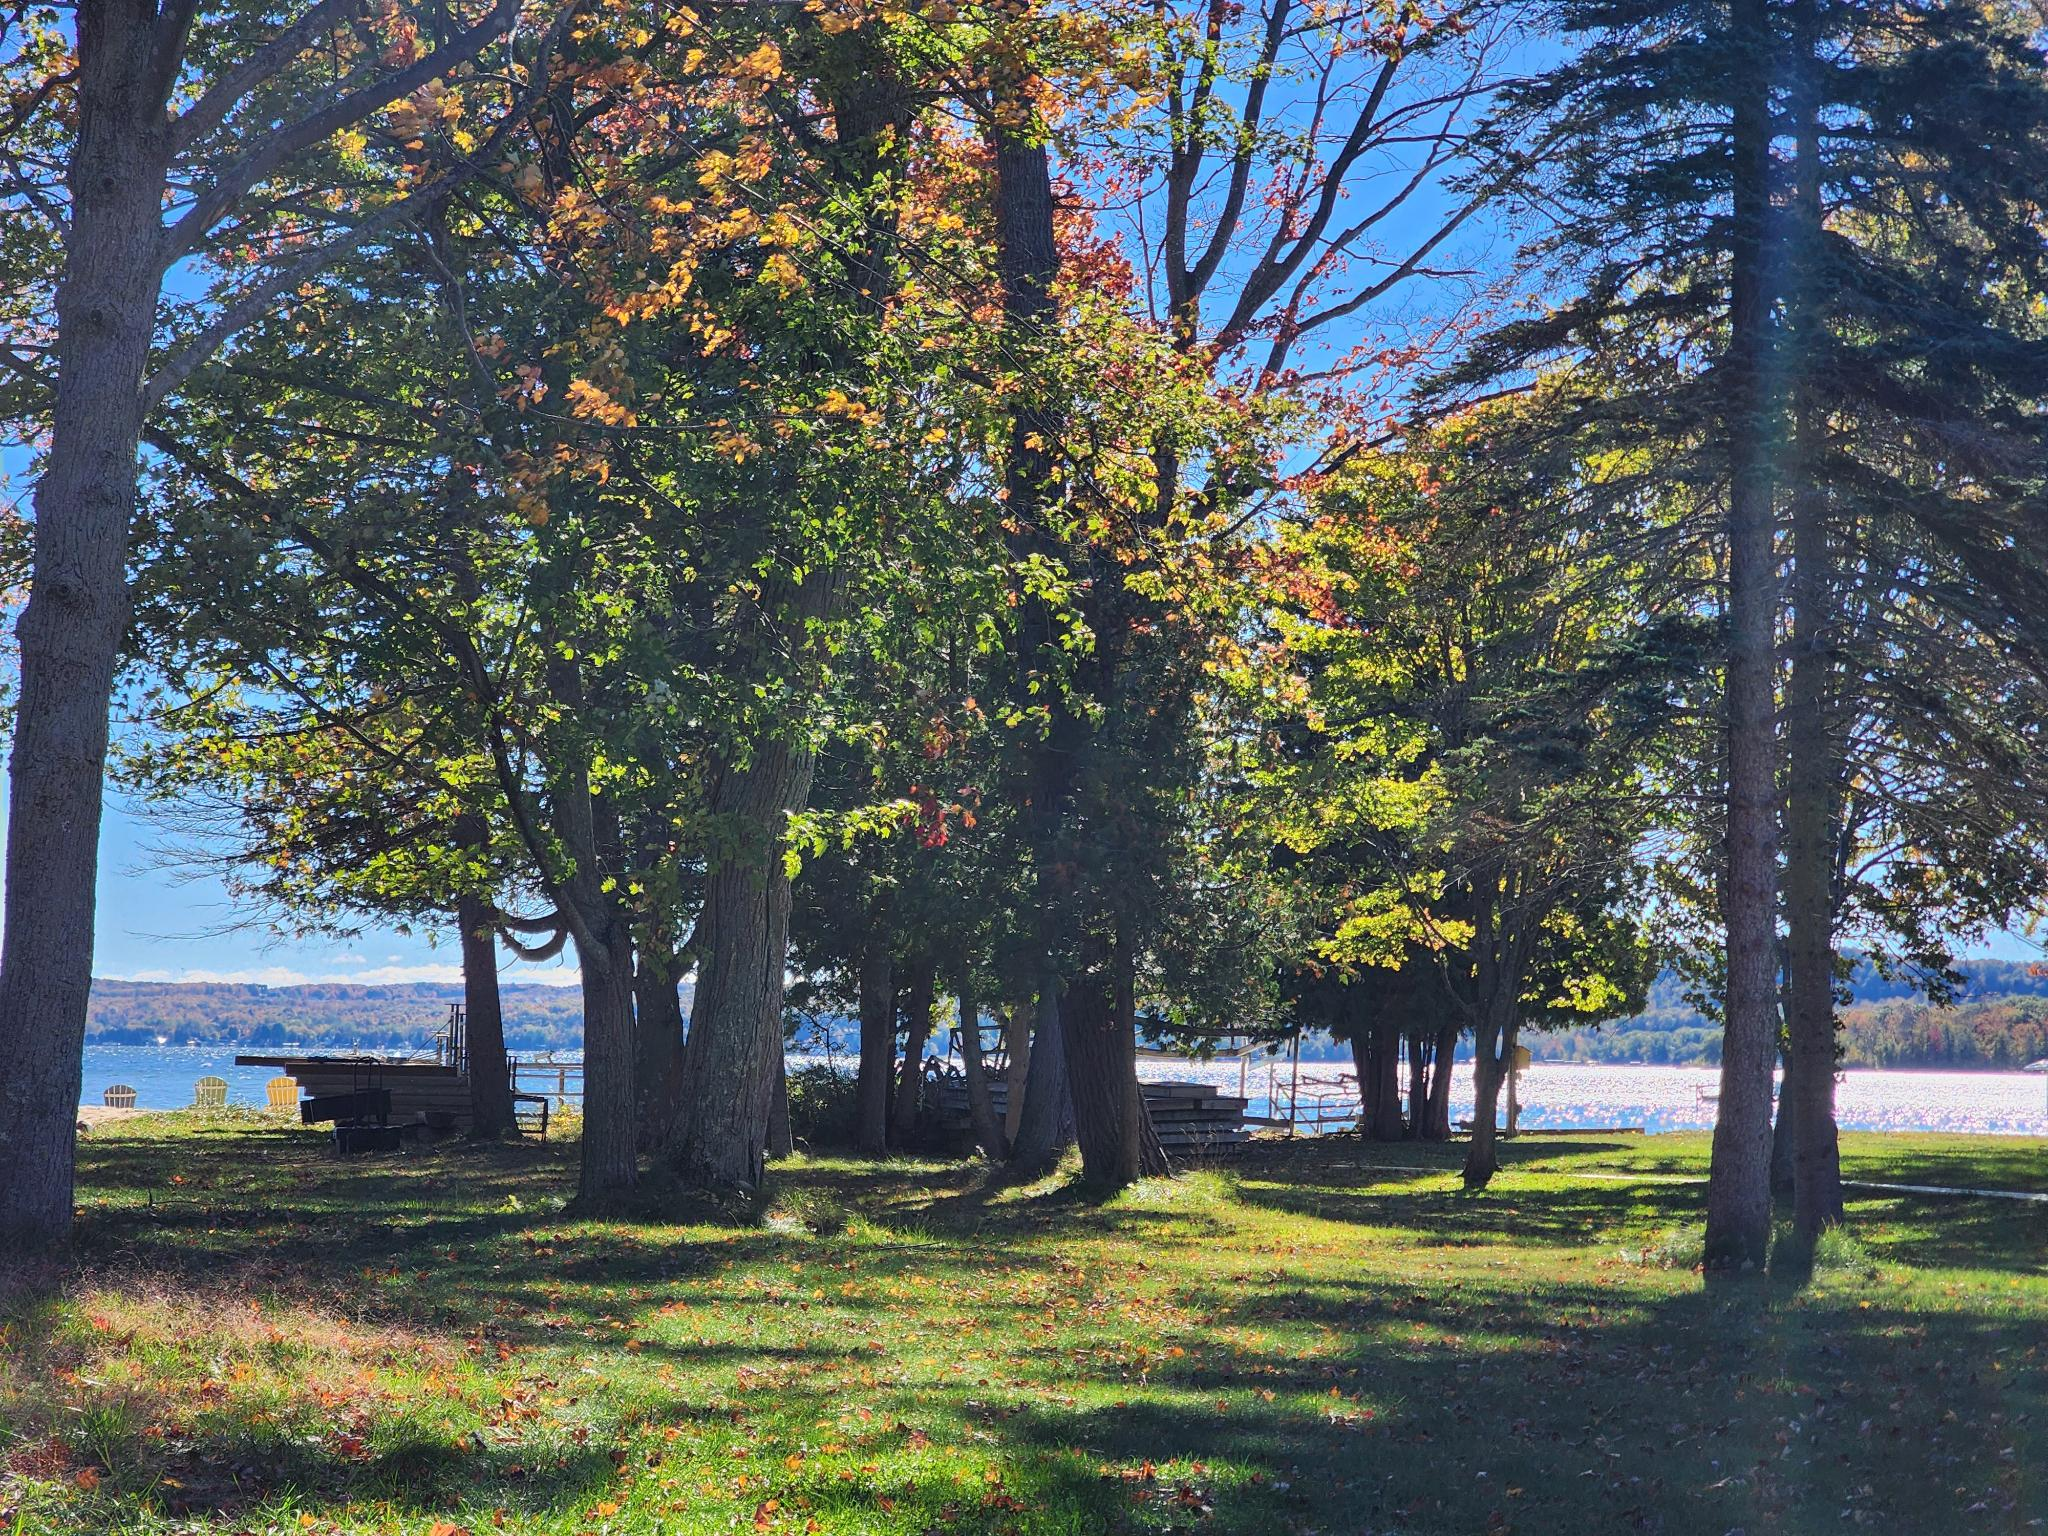
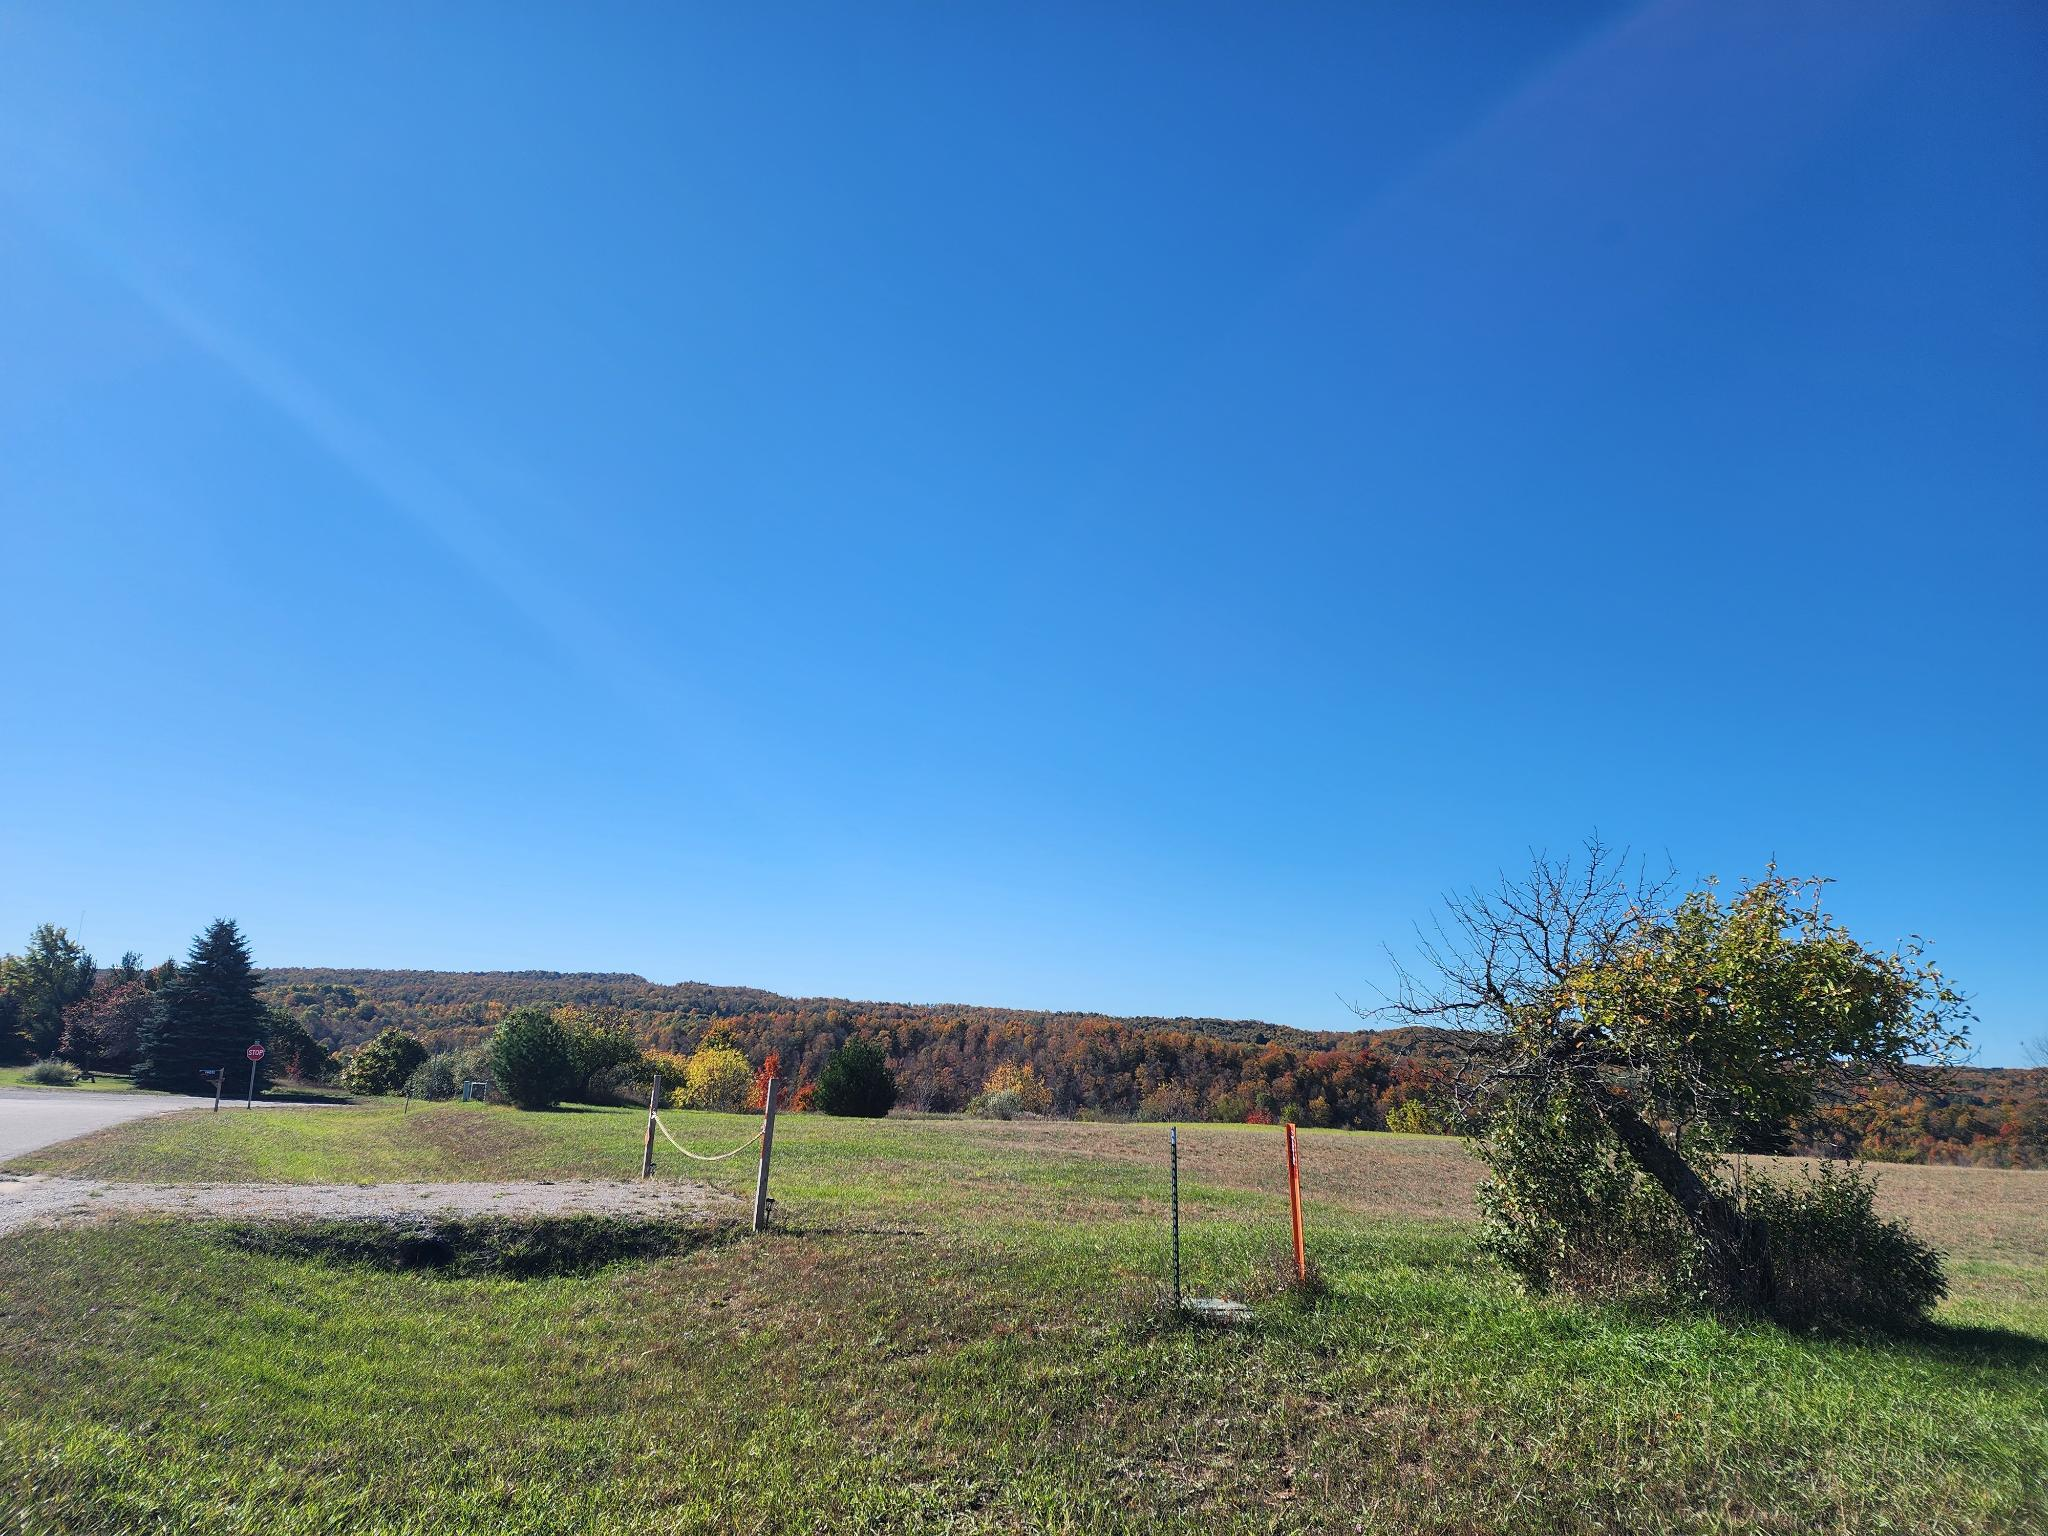
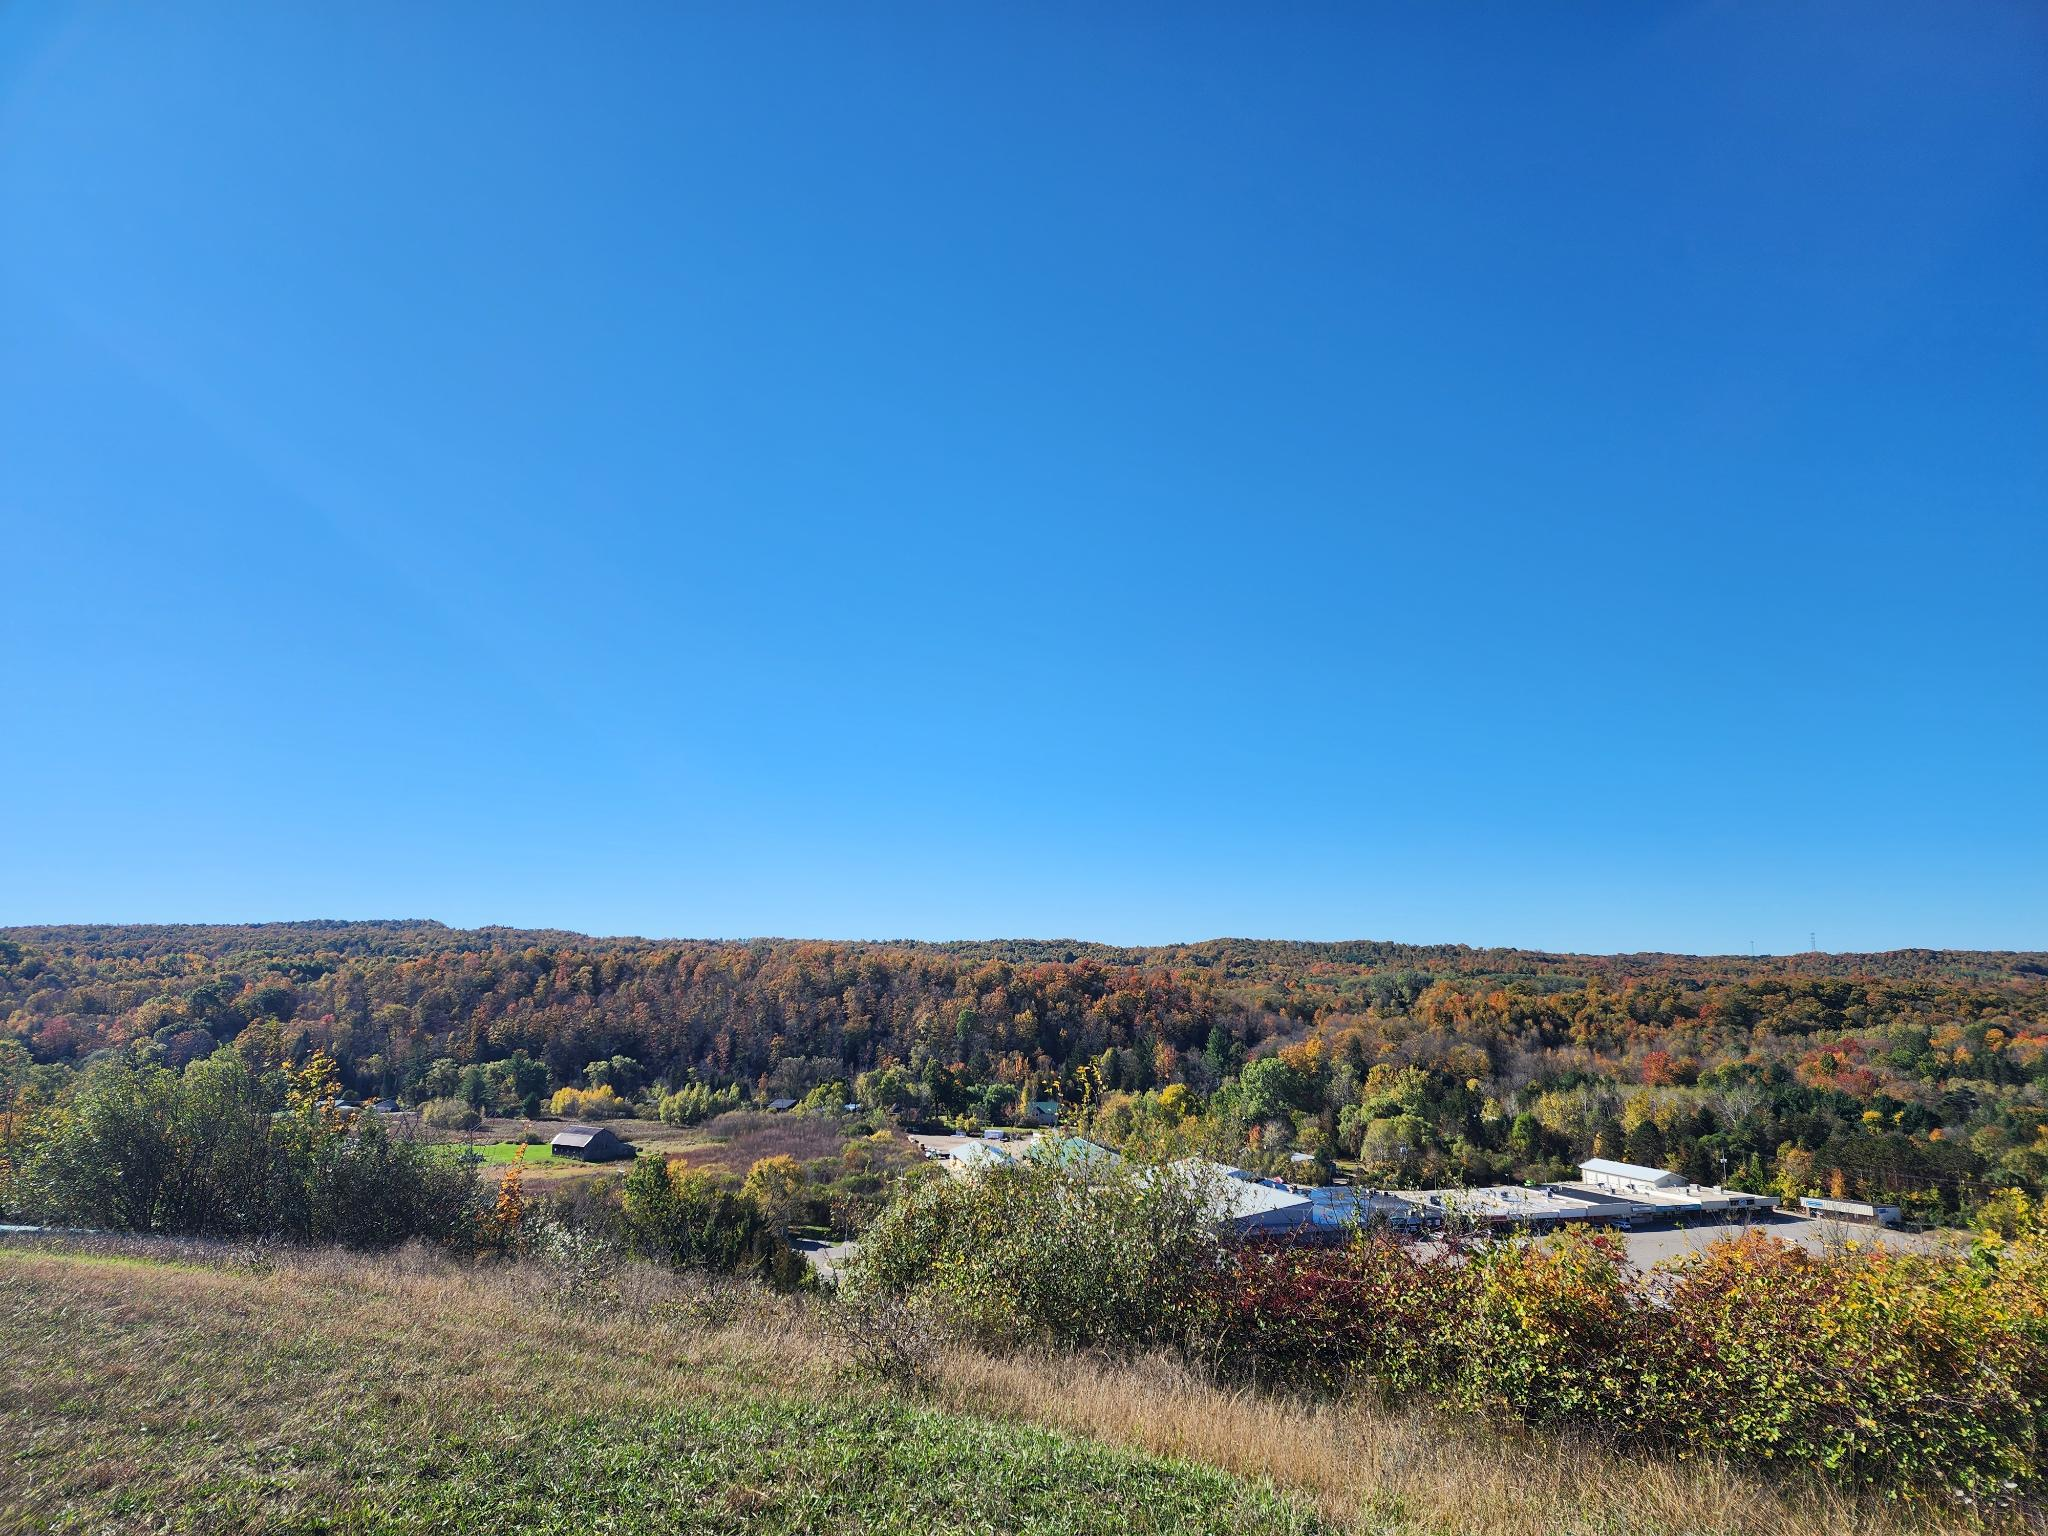
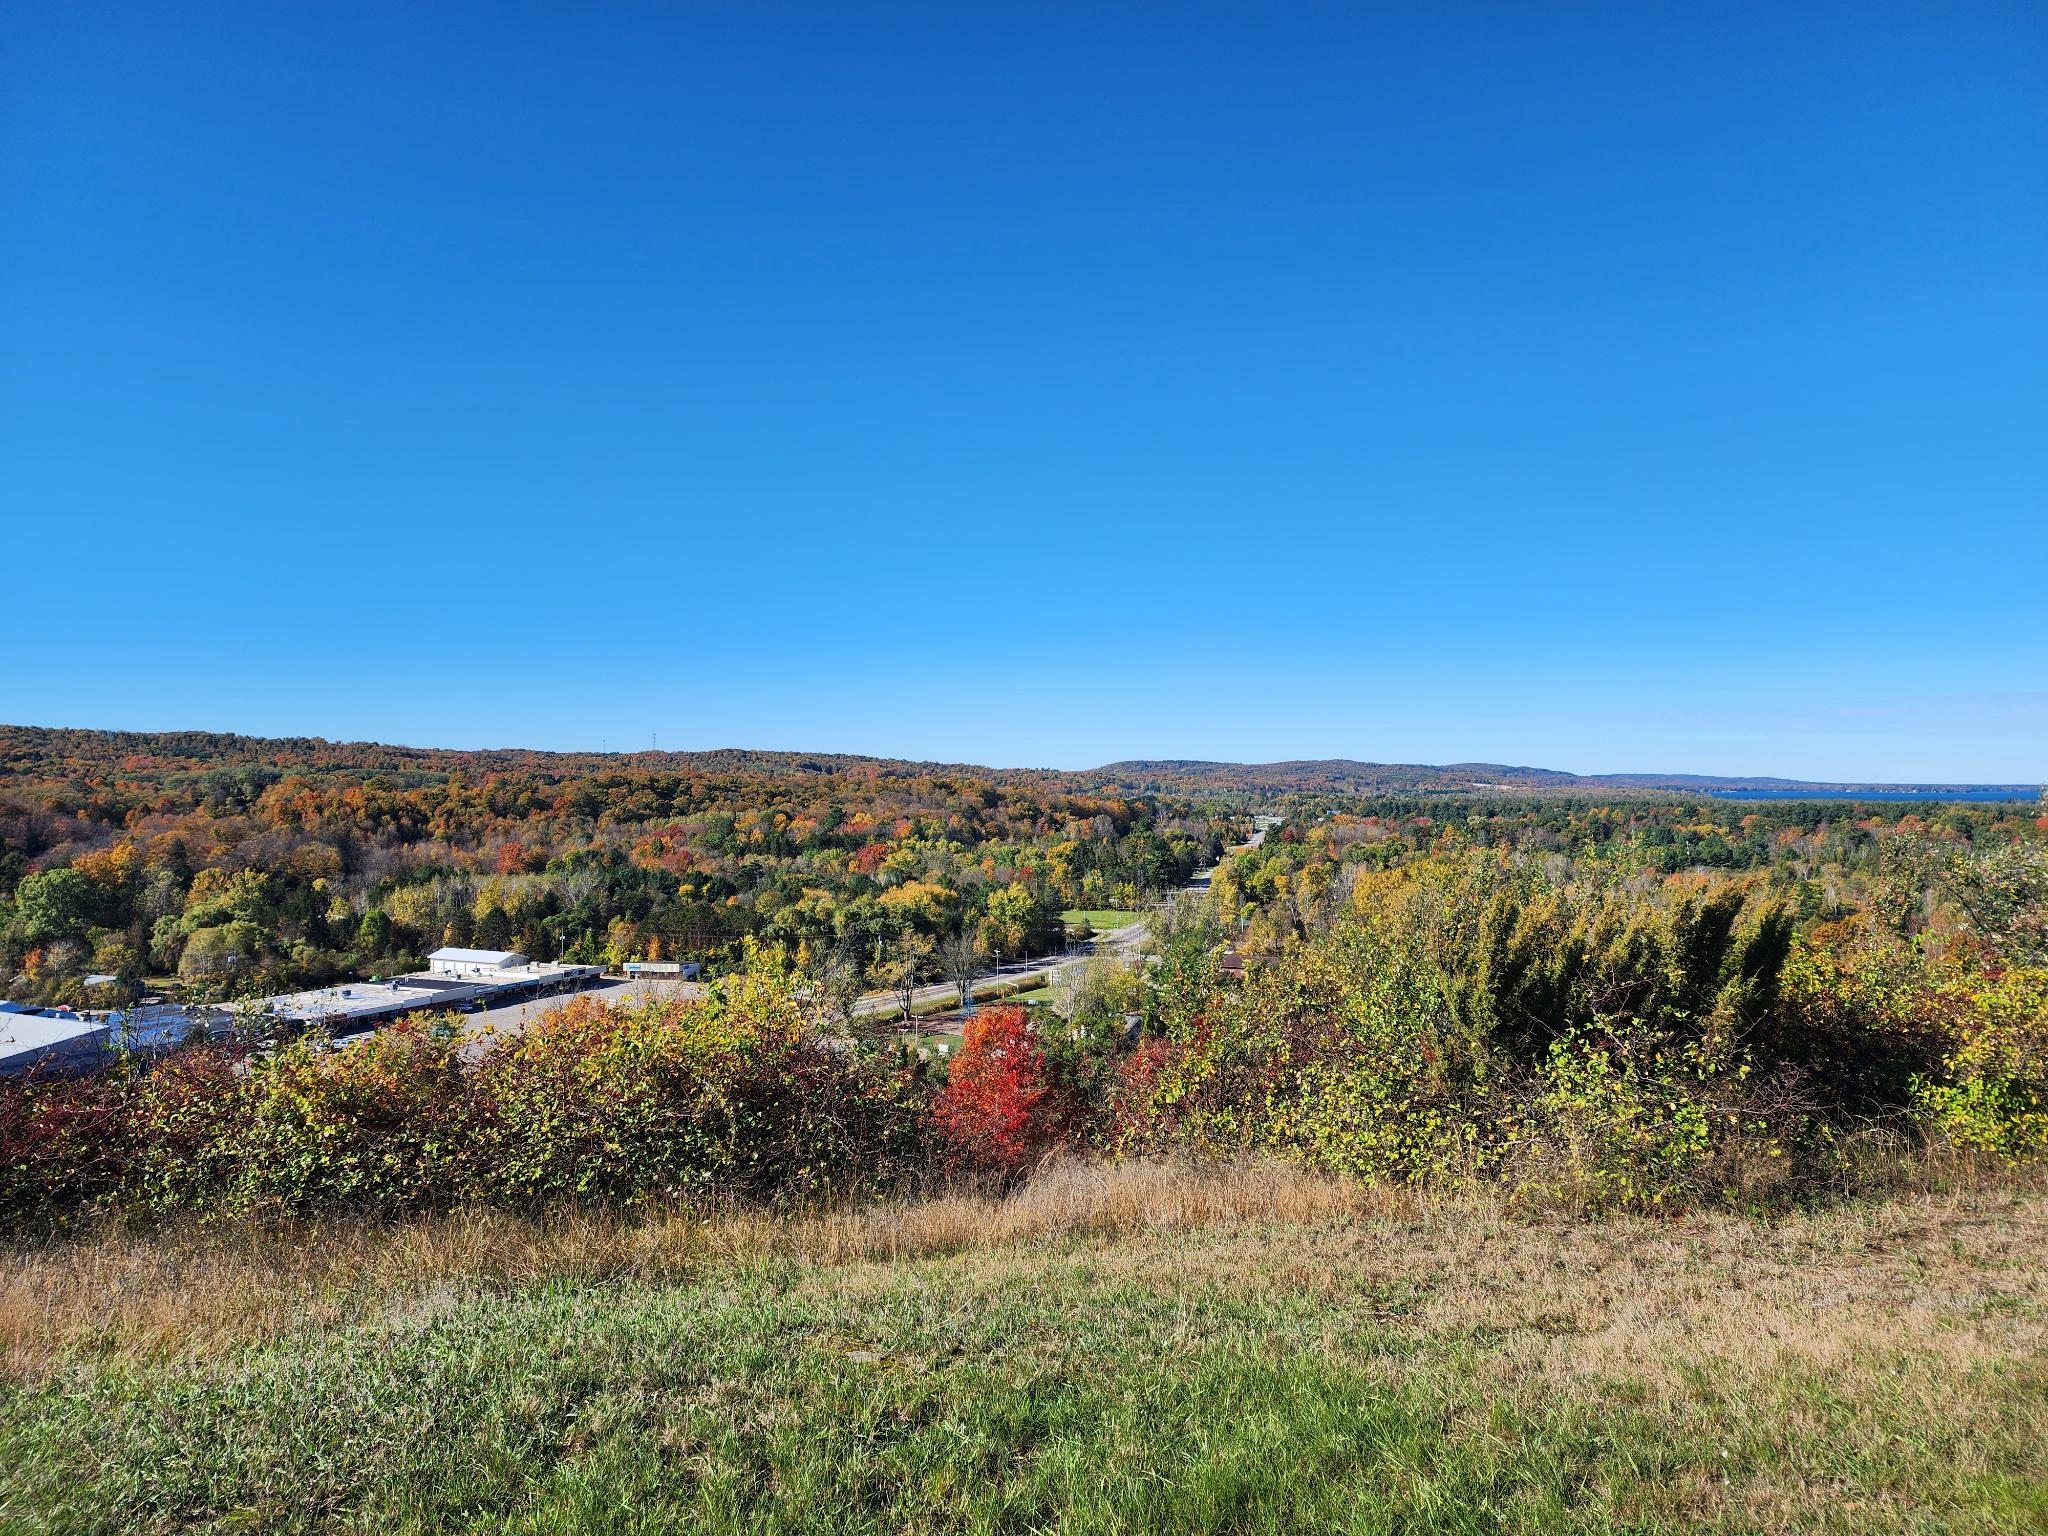
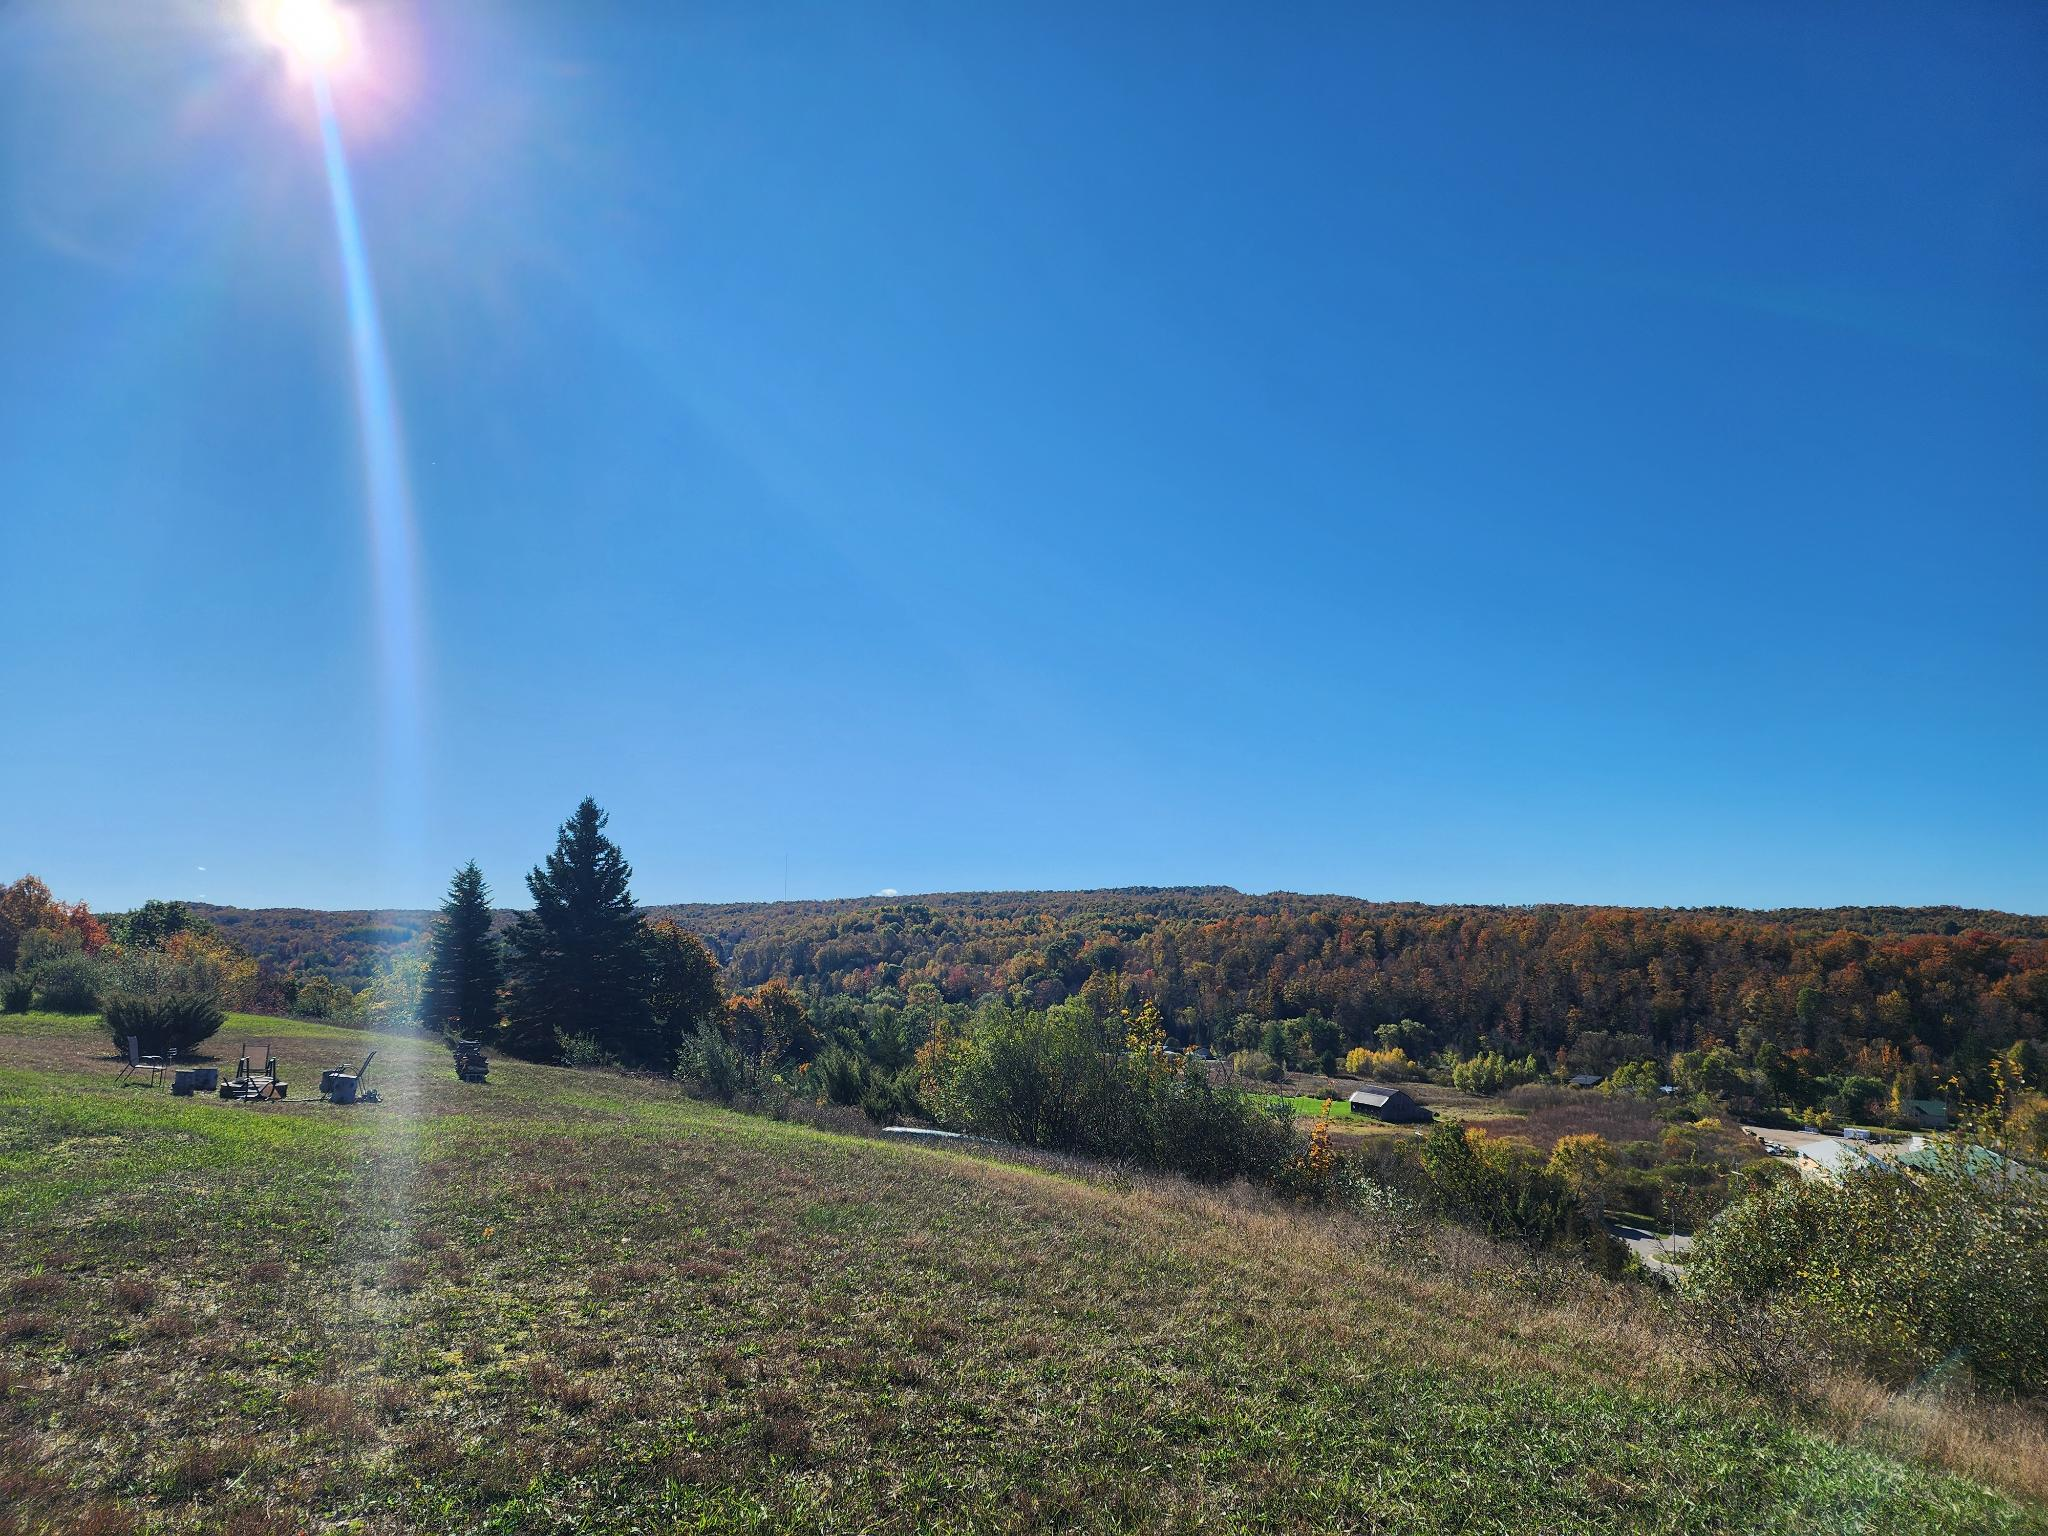
I made a return visit to "The one that got away" in Downtown Honor, MI. In the summer we looked at a 1 acre plot out here, but the long and short of it, is that the community has an HOA. and While there are no HOA dues, there are HOA rules, and there are no HOA benefits. They had exacting requirements for what could be built on the land, and doing the math for everything, it wasn't feasible. But what was very noteworthy is that this plot was in a small, dead-end neaighborhood on a hilltop with a commanding view of the countryside.

At my heart, I am a man that loves to be near the water. Either I was a frog, or a waterbug in a previous life. I'll never know, but when people say they come up north in the fall to see the trees, THIS is what they mean.

Alt Text for all four images: These images come from a hillside of a small town in northern michigan, Honor, MI. A clear blue sky fading into white in the horizon dominates the upper half of each of these pictures. Coming up from the bottom of each image meeting in that blue-white horizon is a sea of trees. Its mid-fall in northern Michigan, so this ocean of trees, is awash in colors. Bright yellows fading into dark orange, fading into flaming, vibrant reds, mixed with the green of trees who aren't quite ready to hibernate for the winter, or are evengreen pine trees. Some of the photos feature some house and structures while others feature the "honor highway", one of the main paths from shores of lake Michigan into traverse city. Dotted along the roads are house and buildings of downtown Honor, MI.

Media attachmentMedia attachmentMedia attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

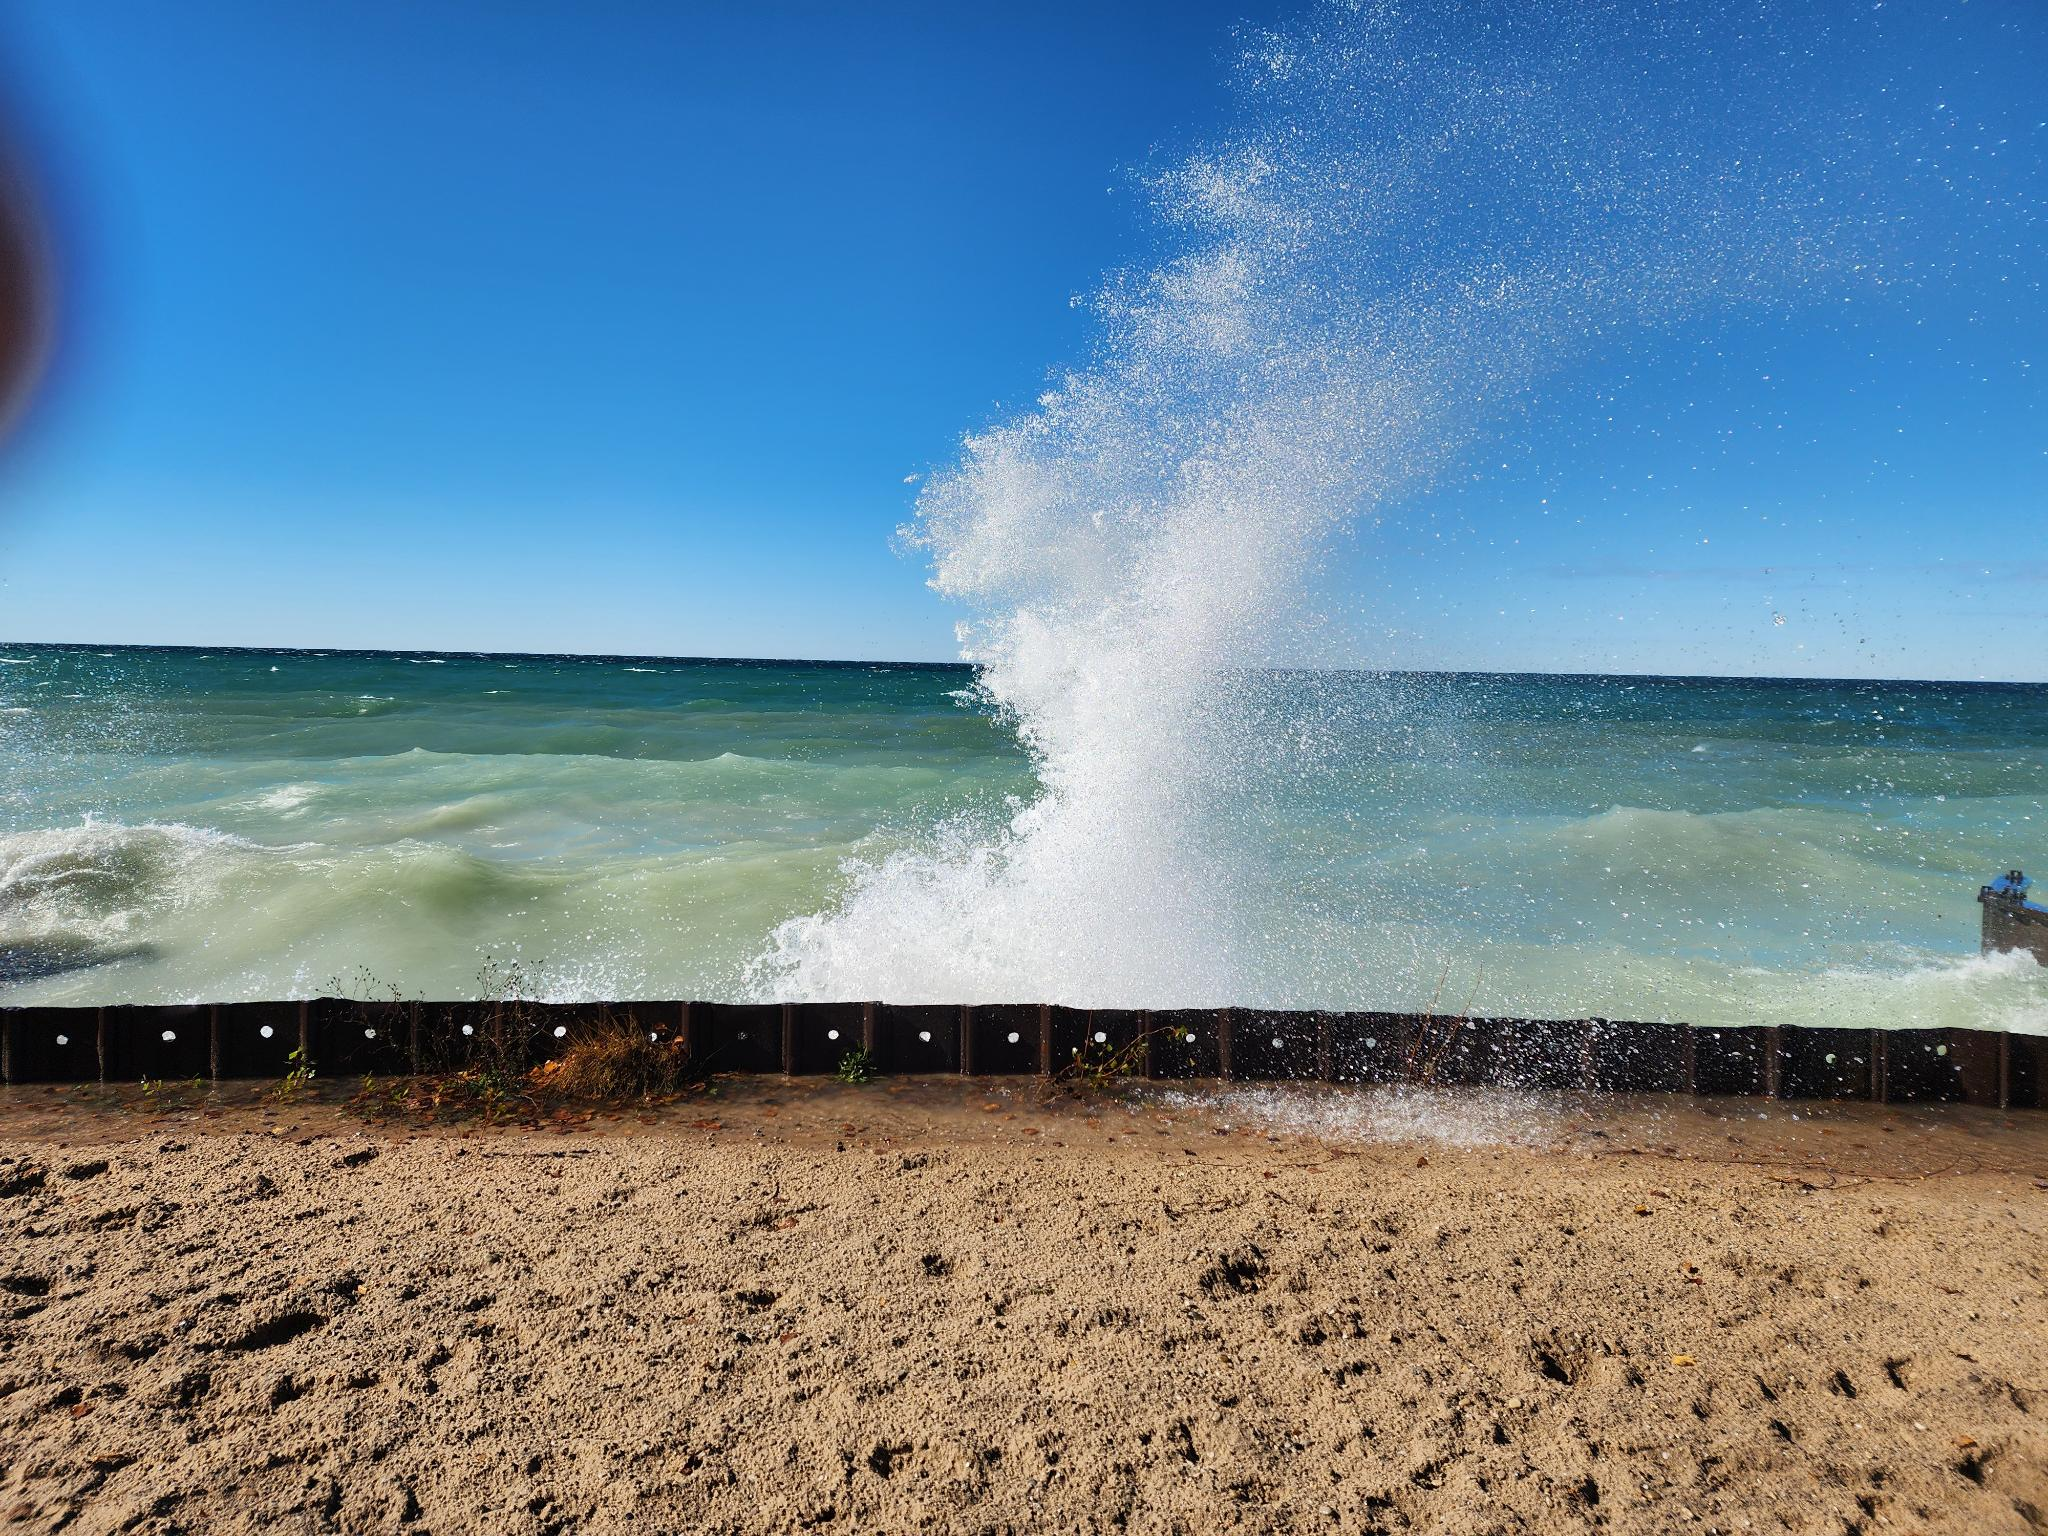
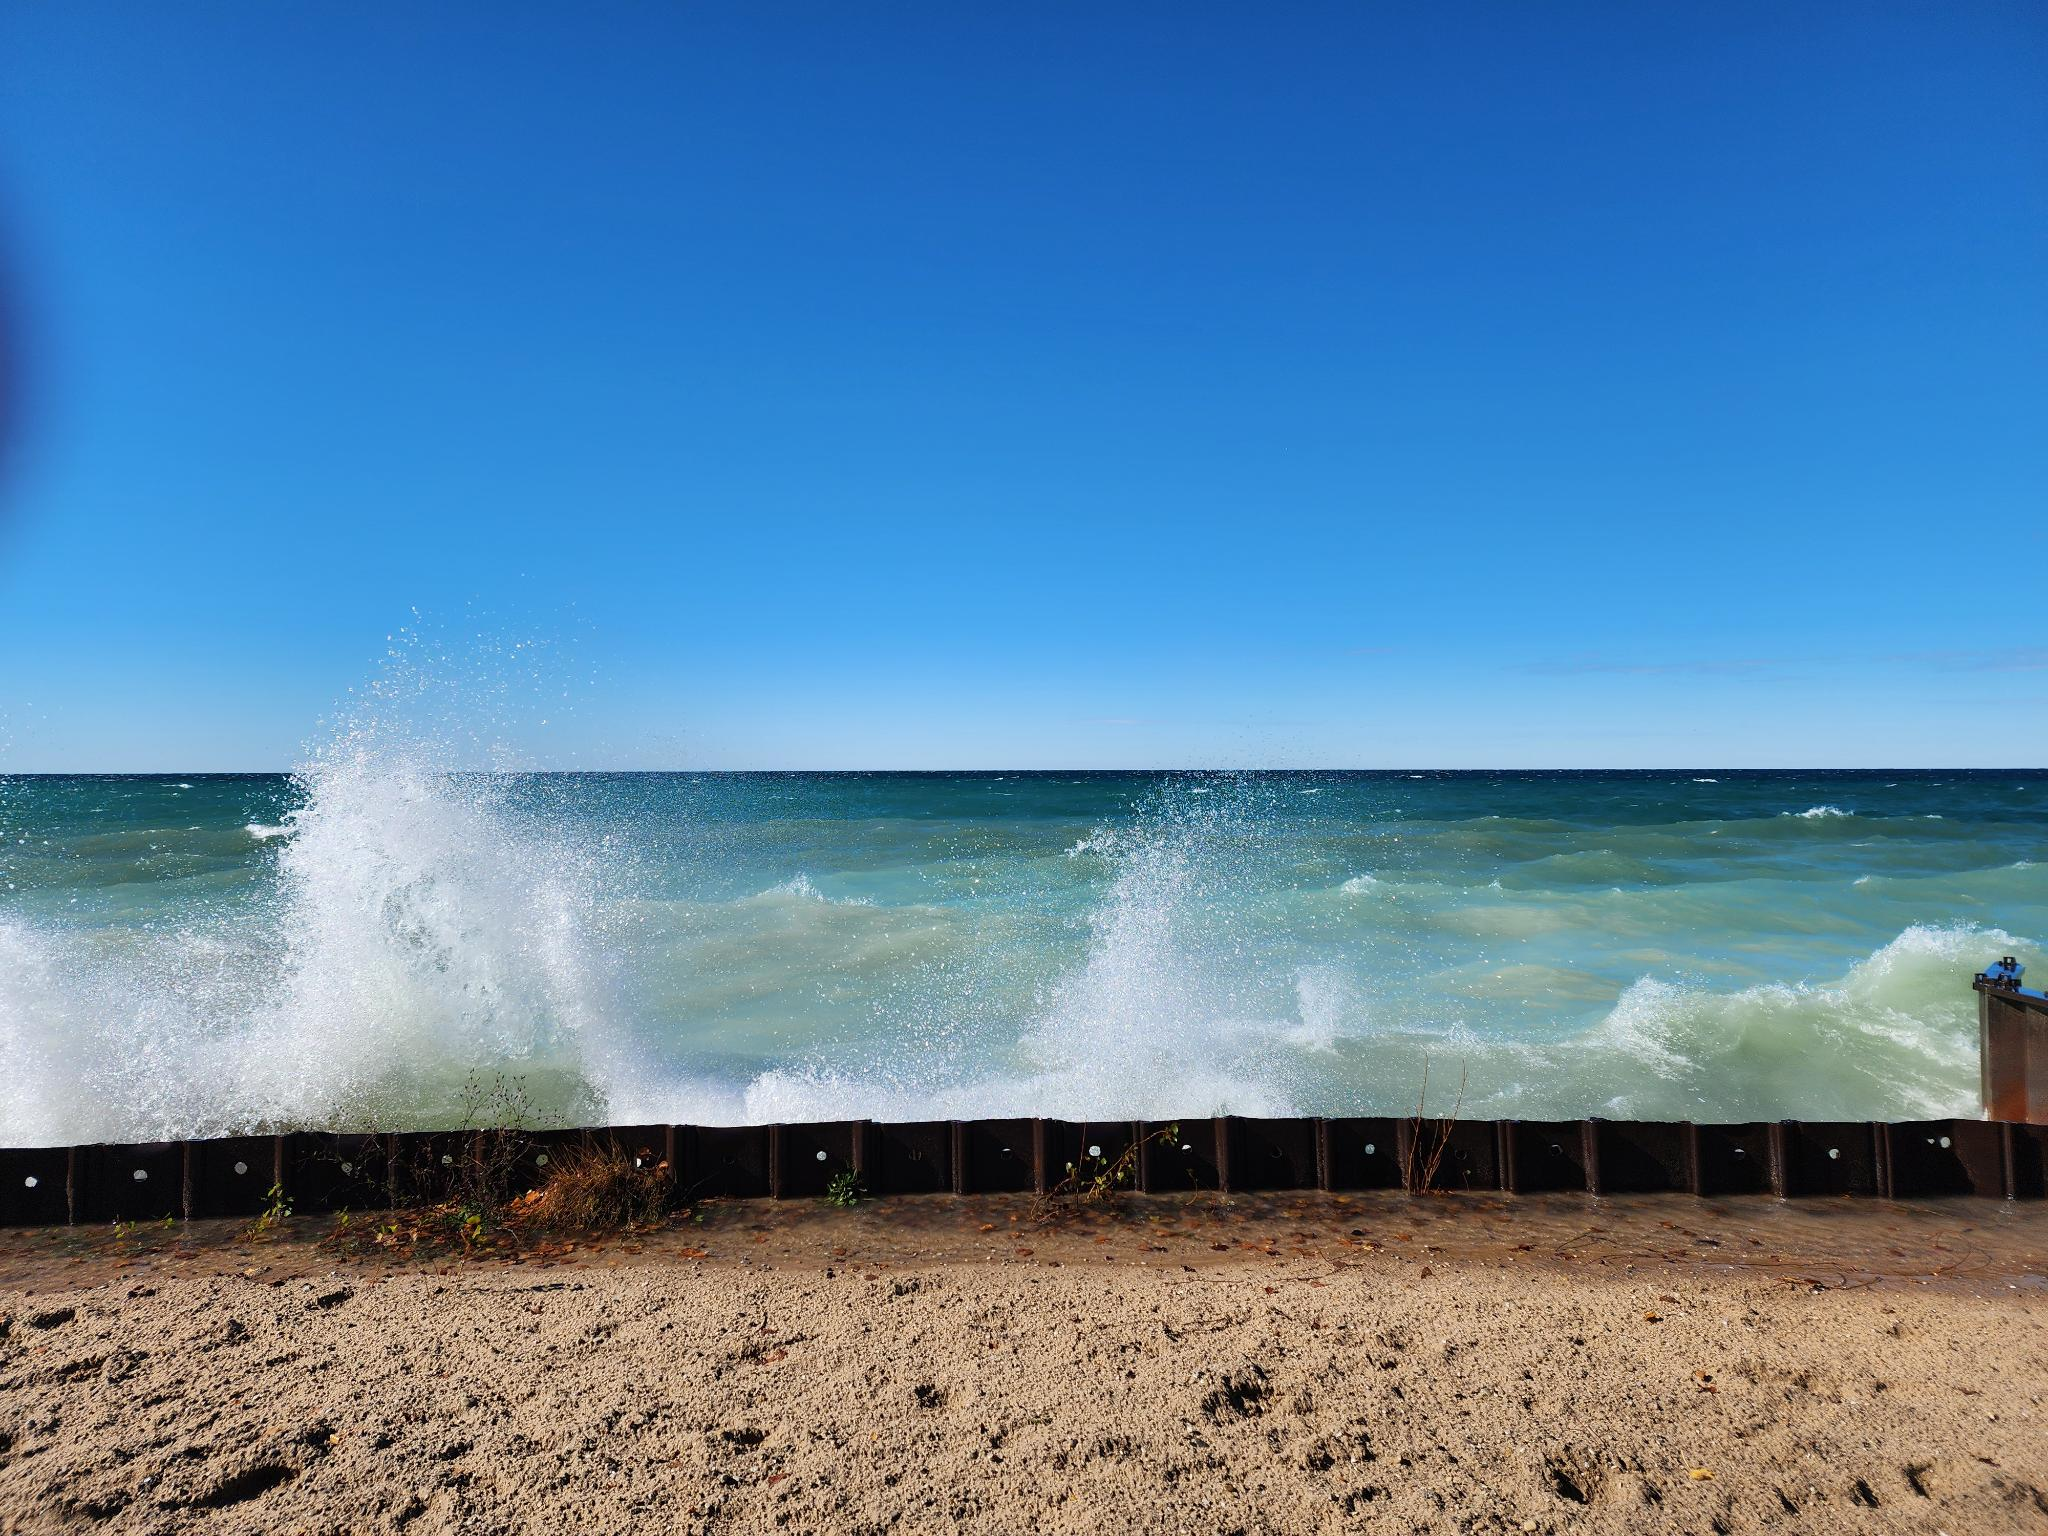
We also made it out to Point Betsie, and the Betsie lighthouse. This place holds core memories for me and has a ton of sentimental value.

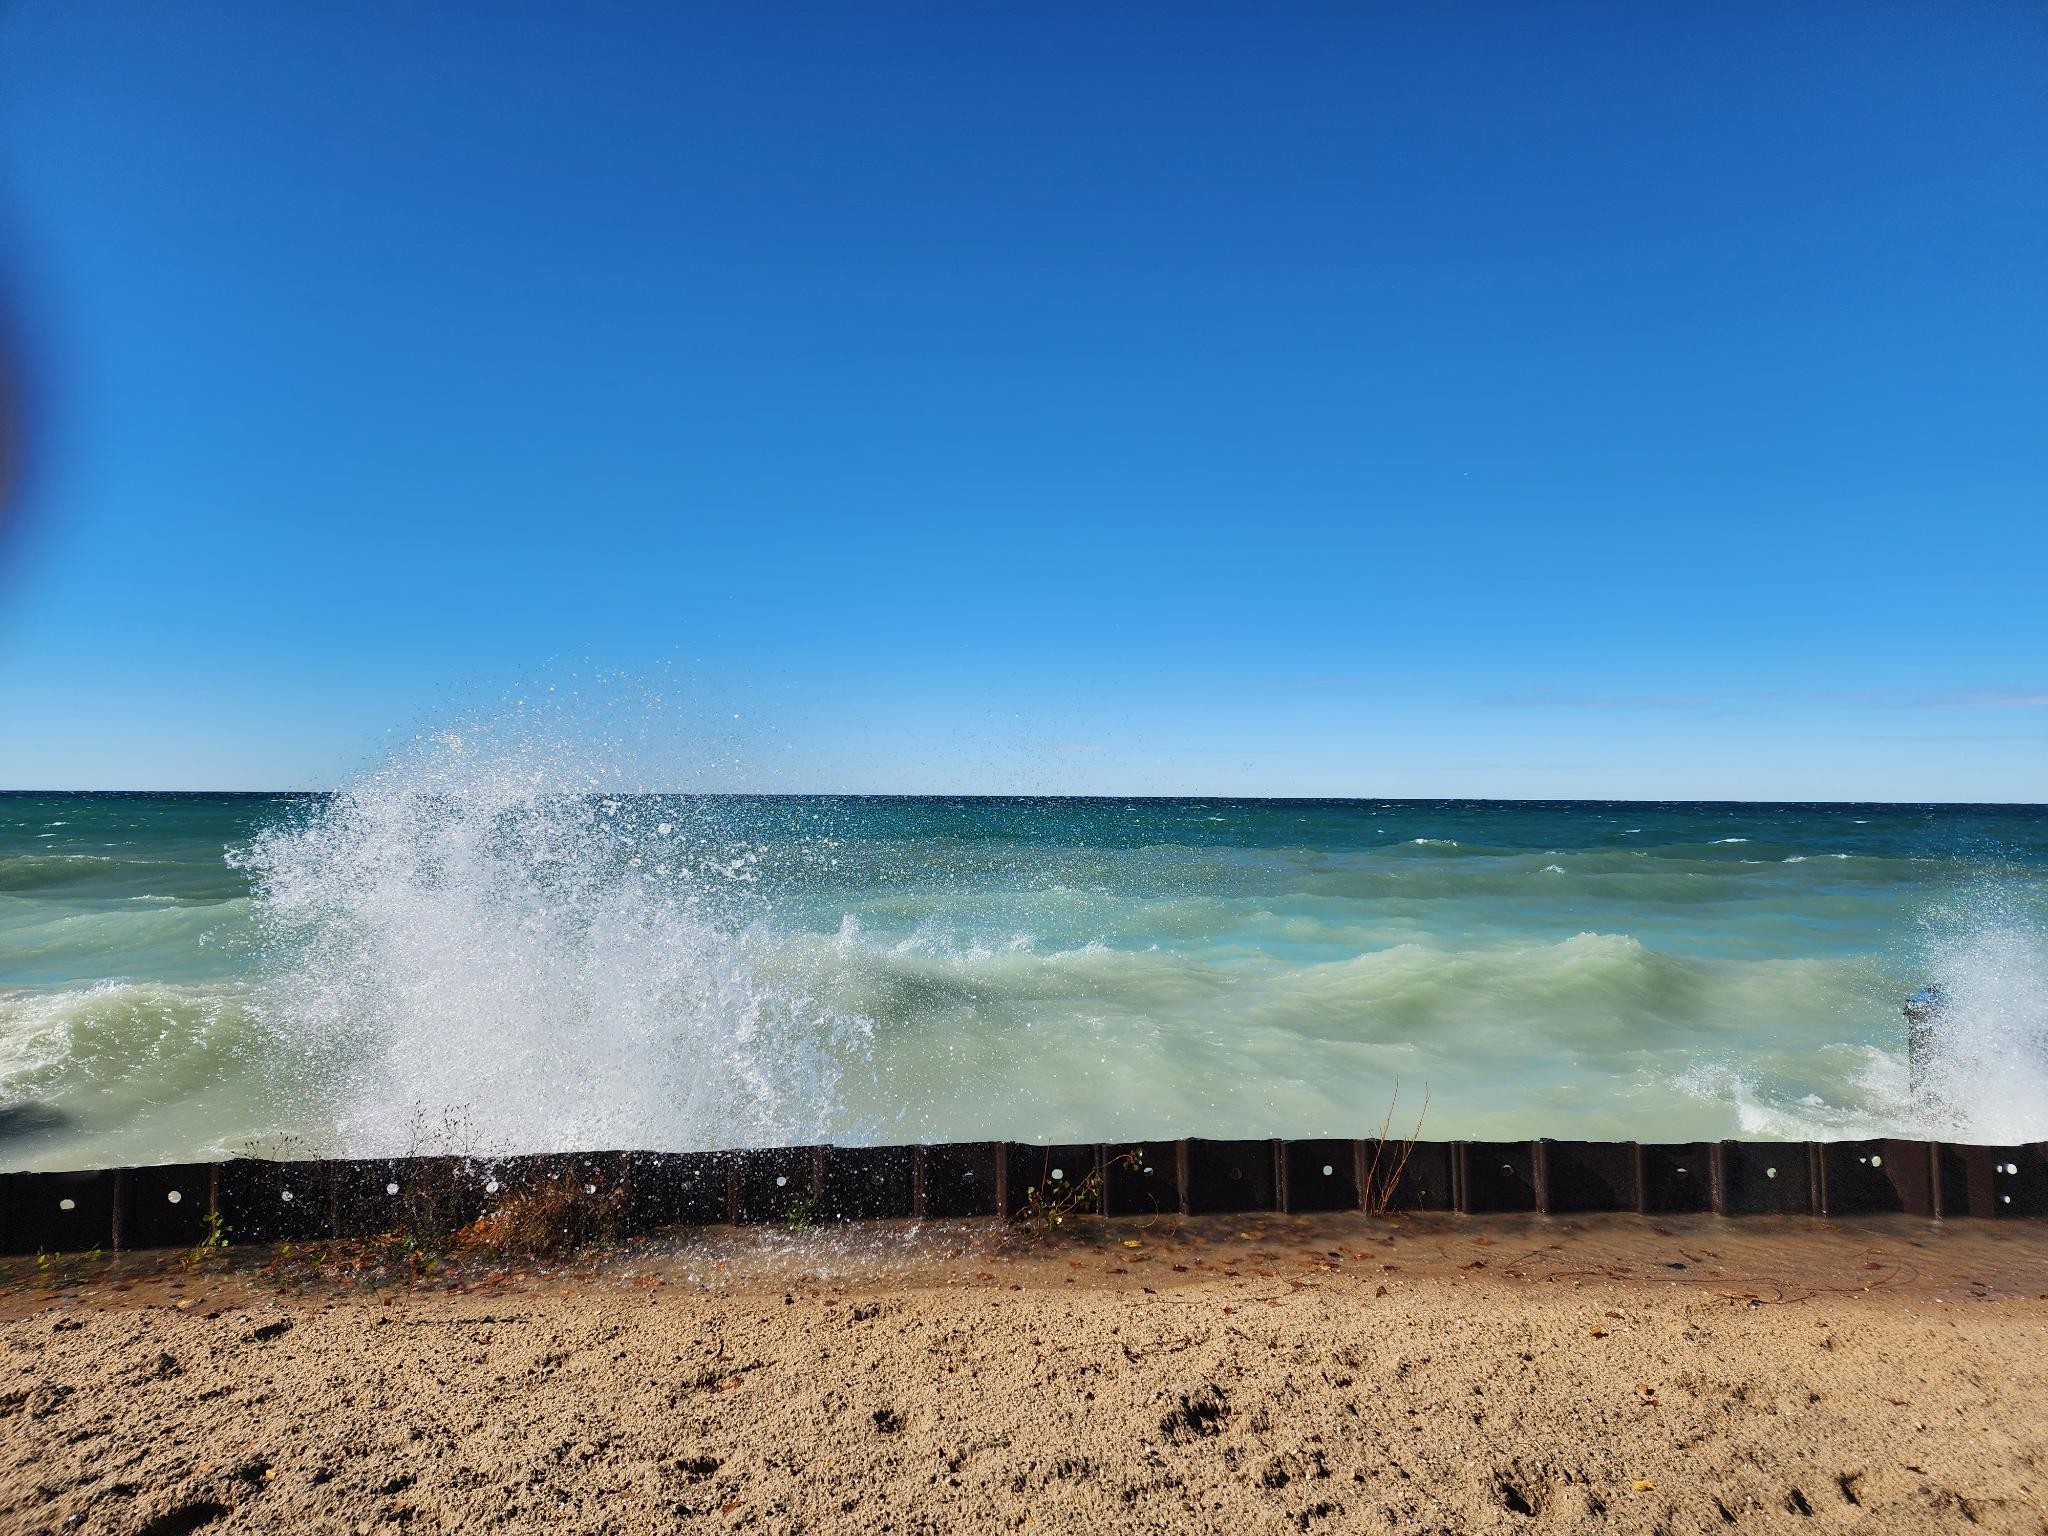
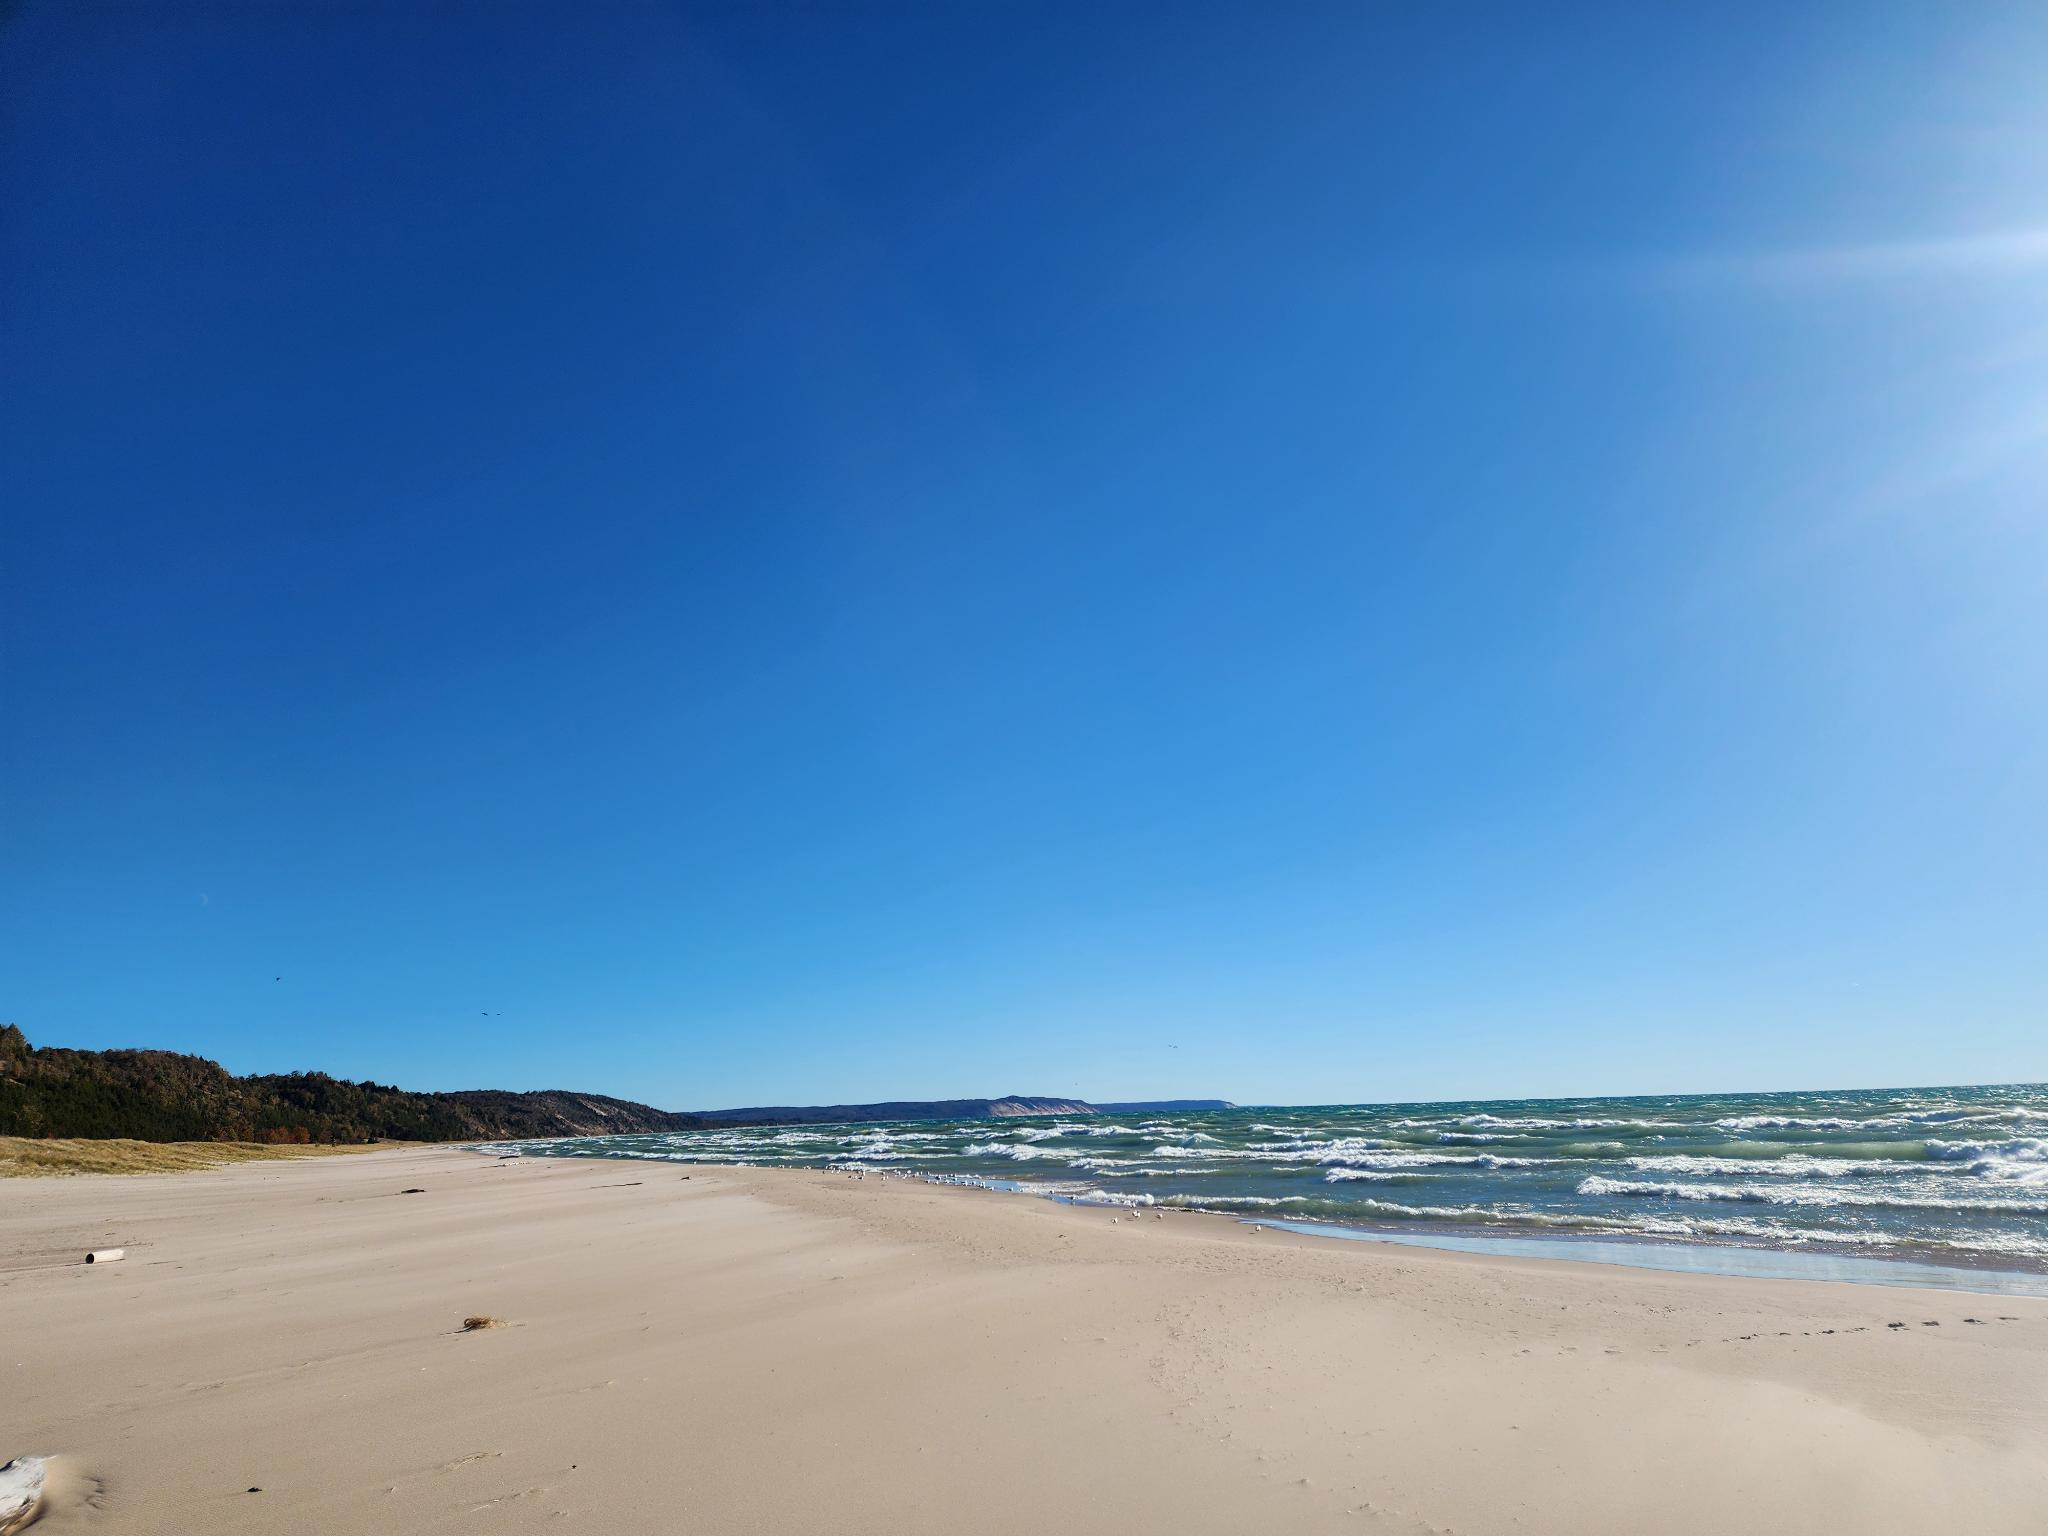
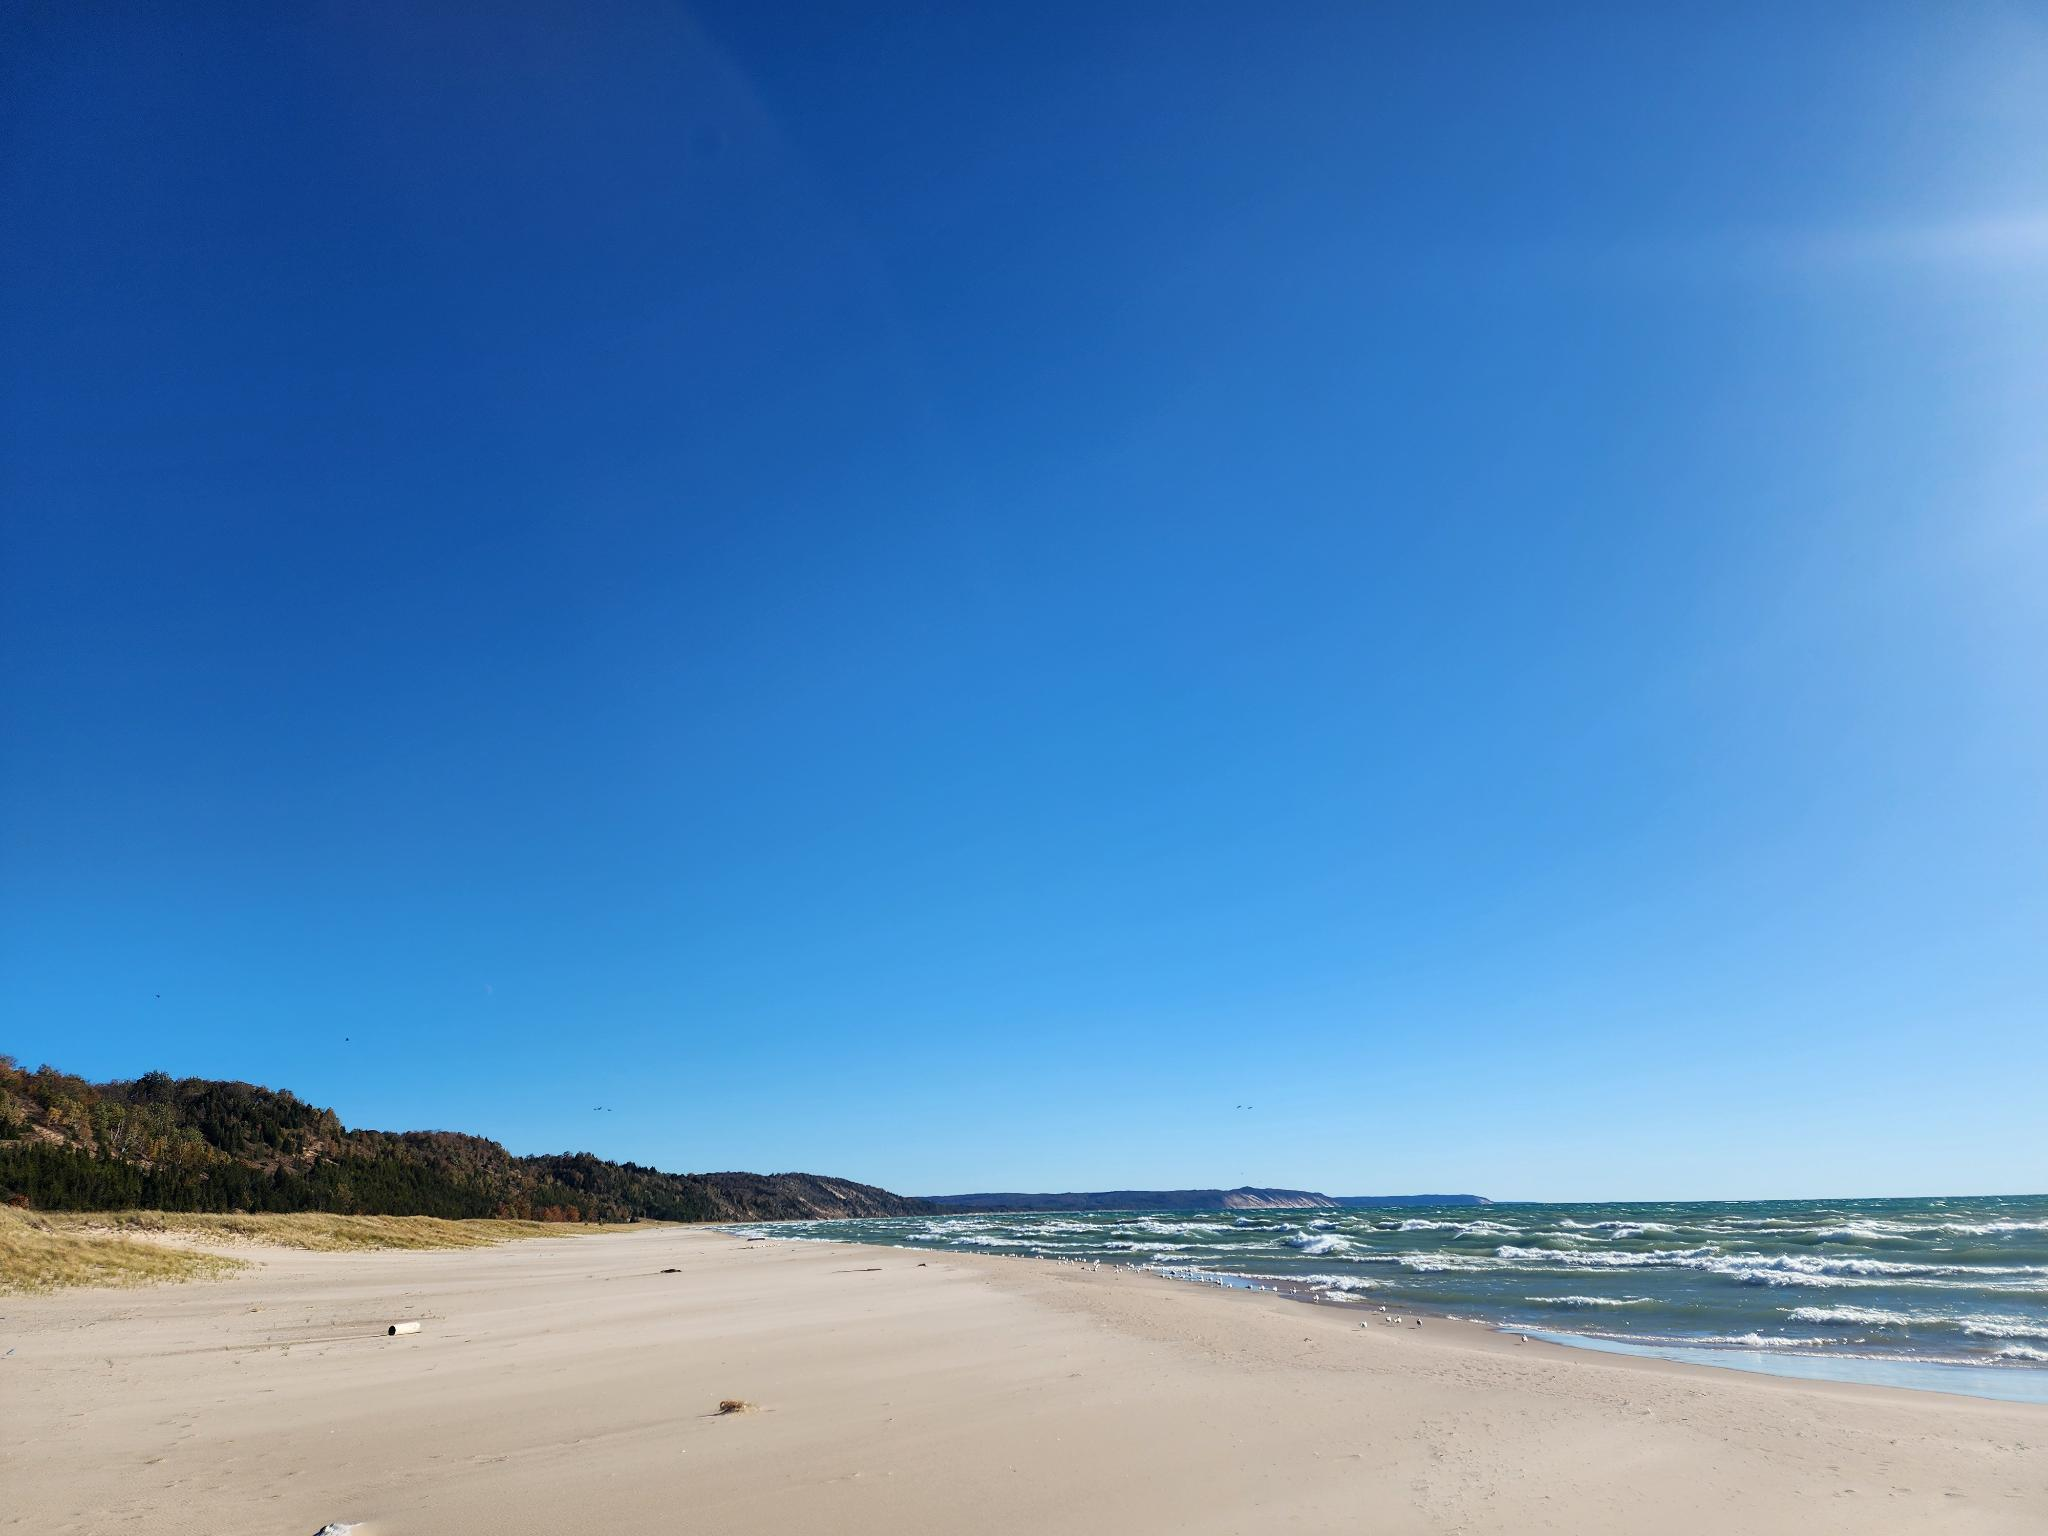
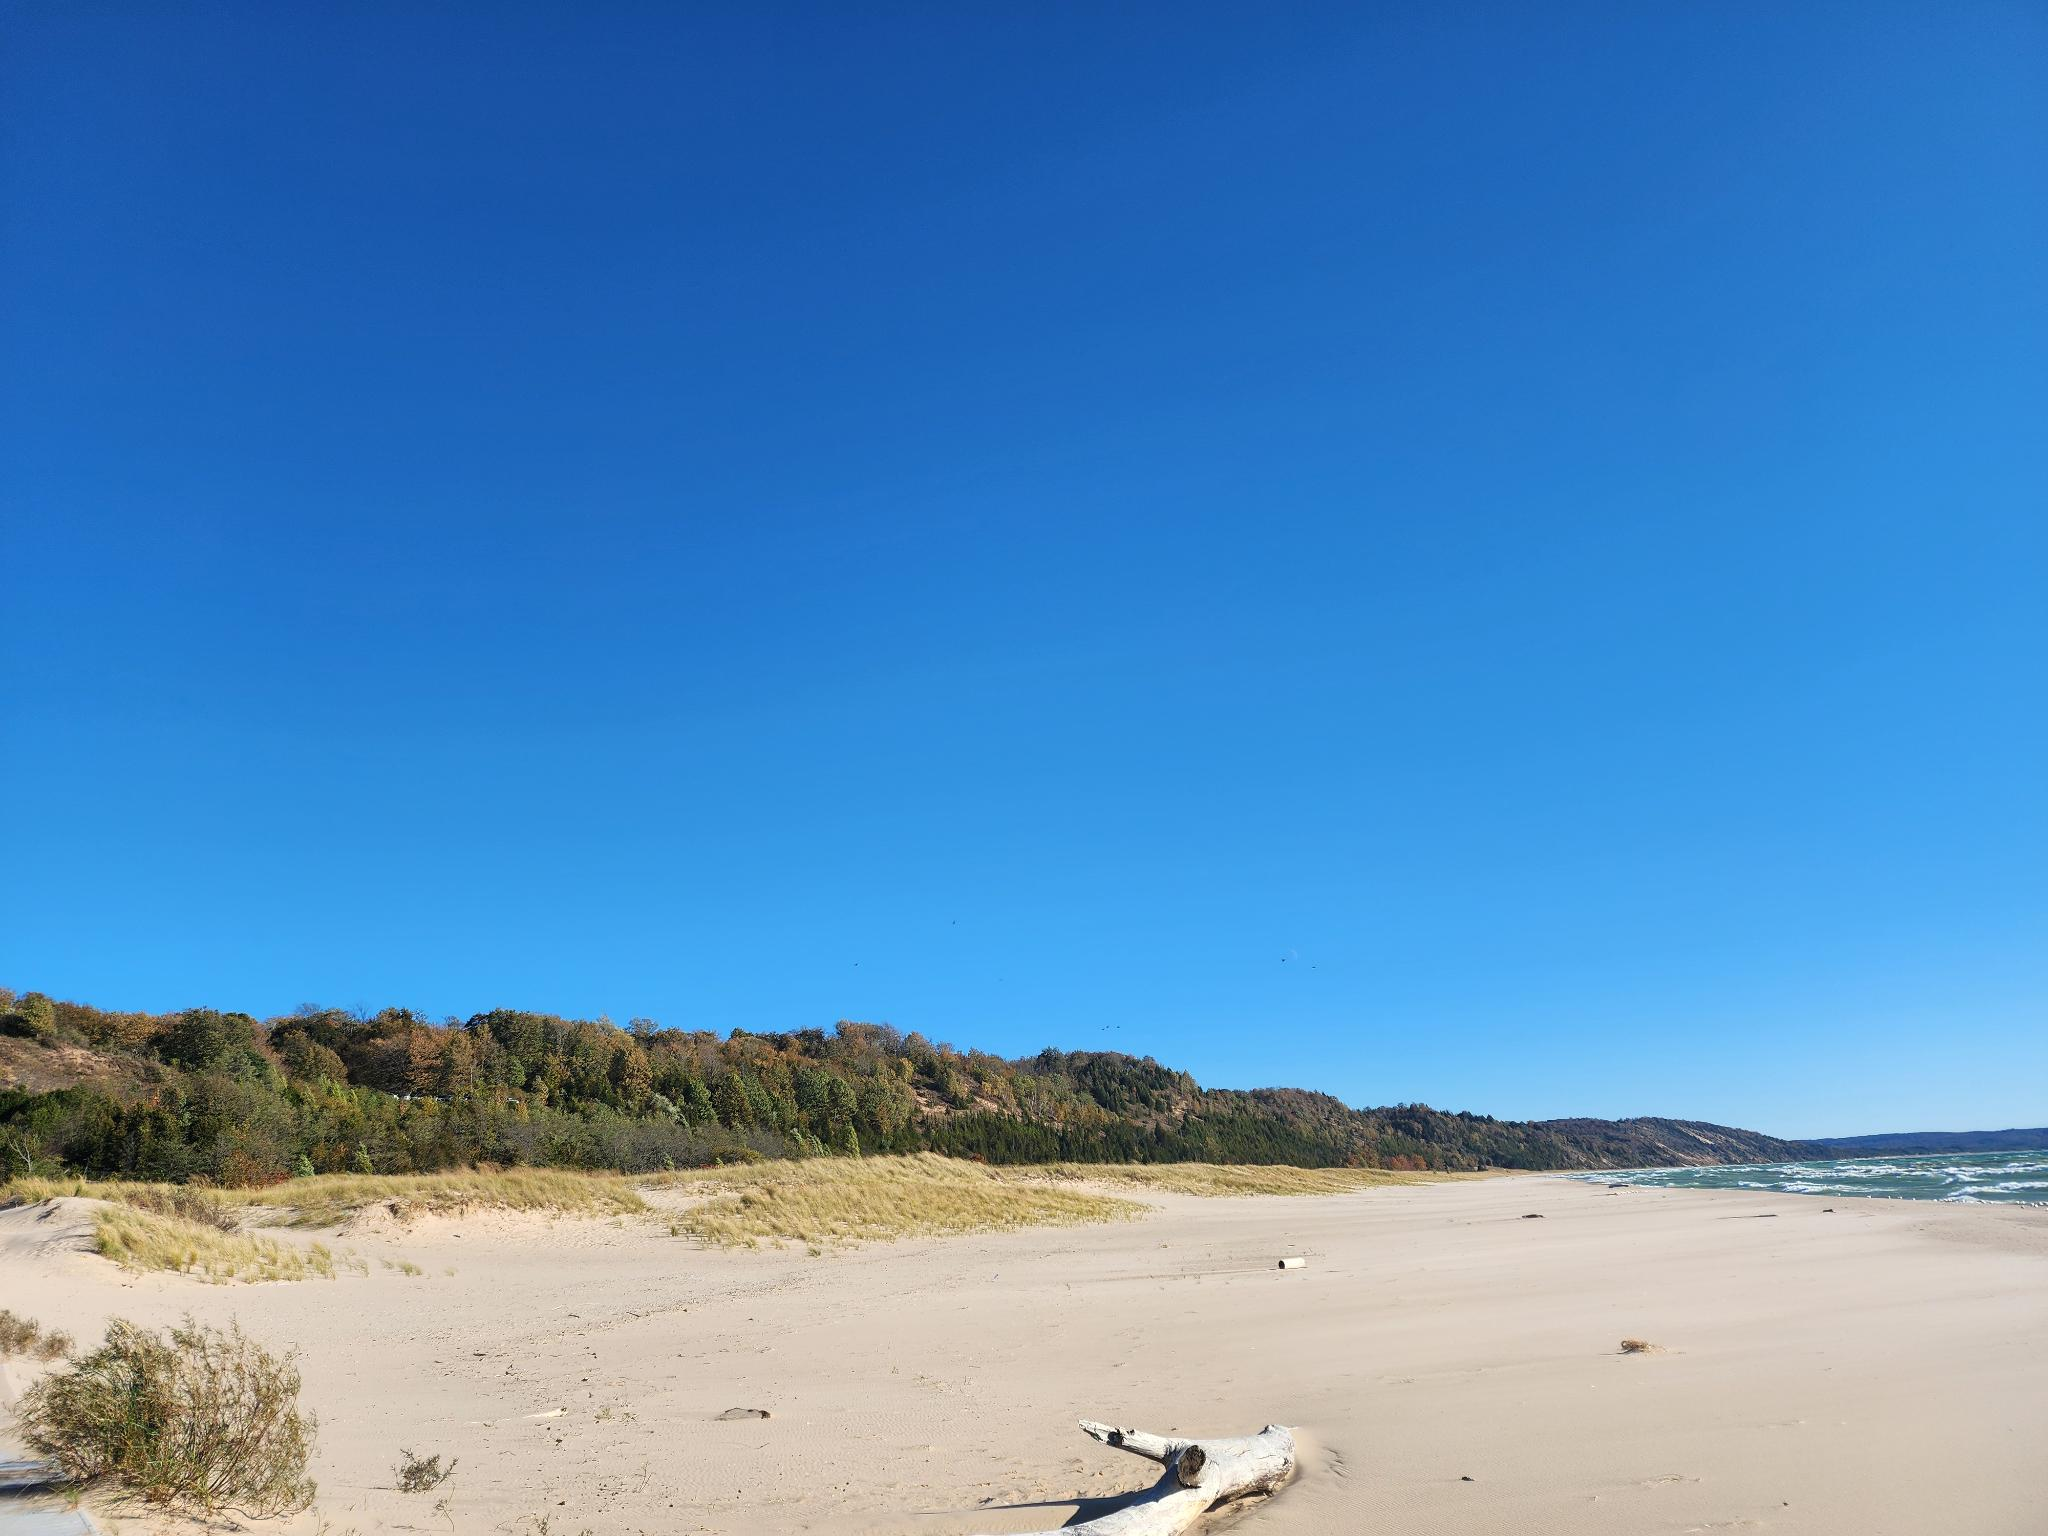
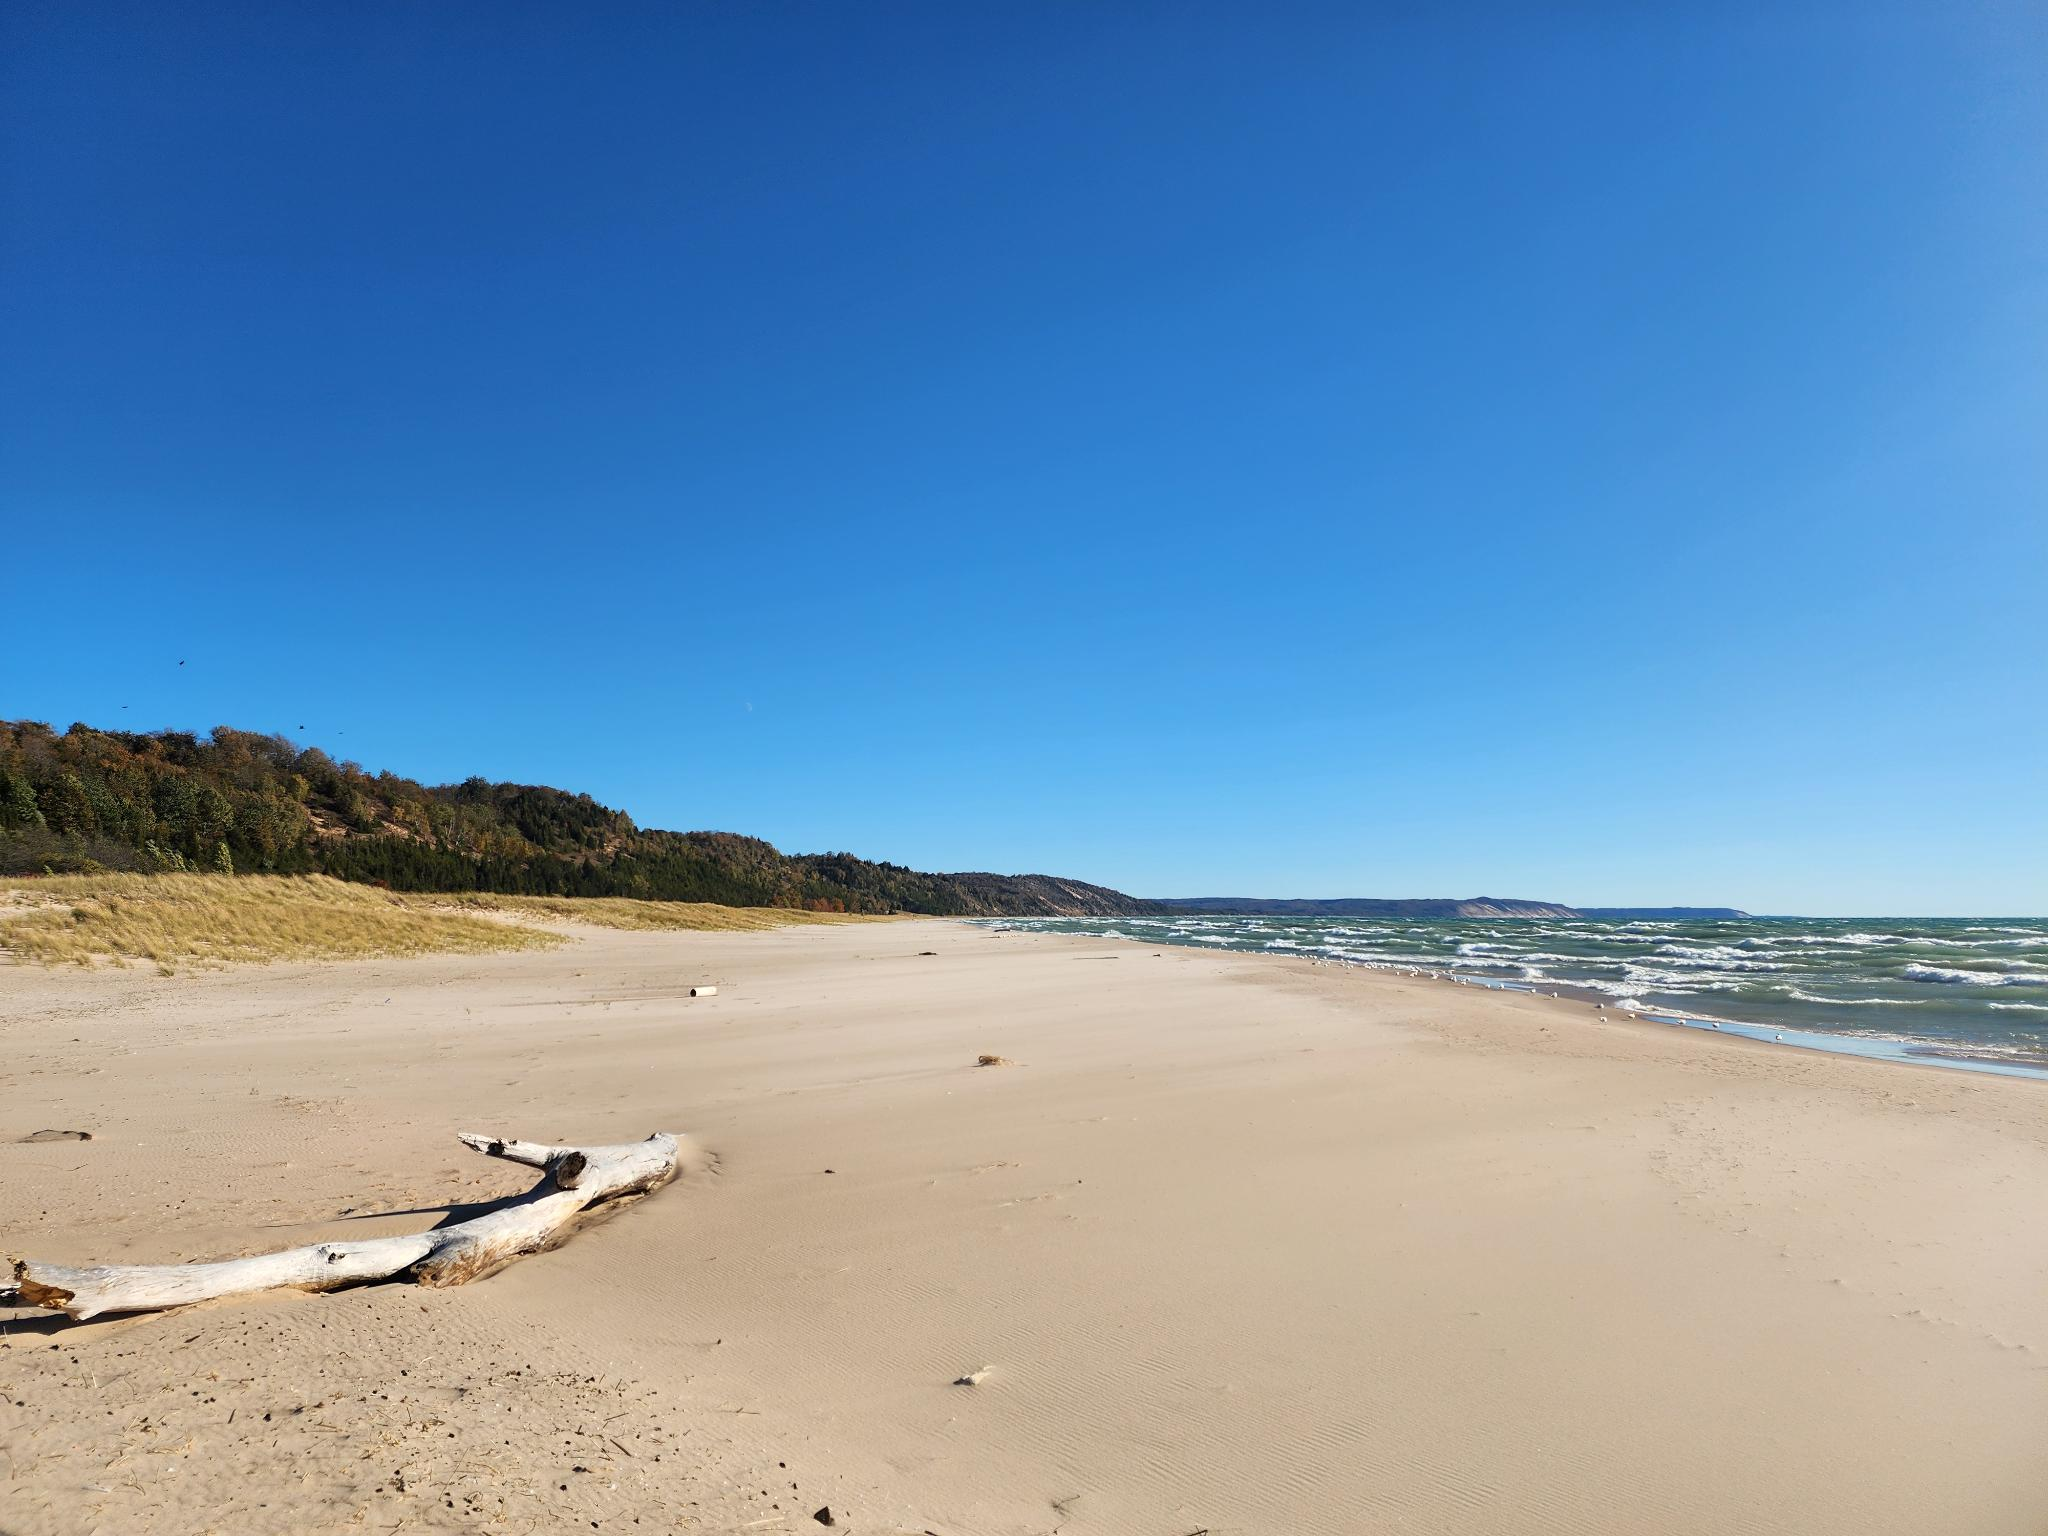
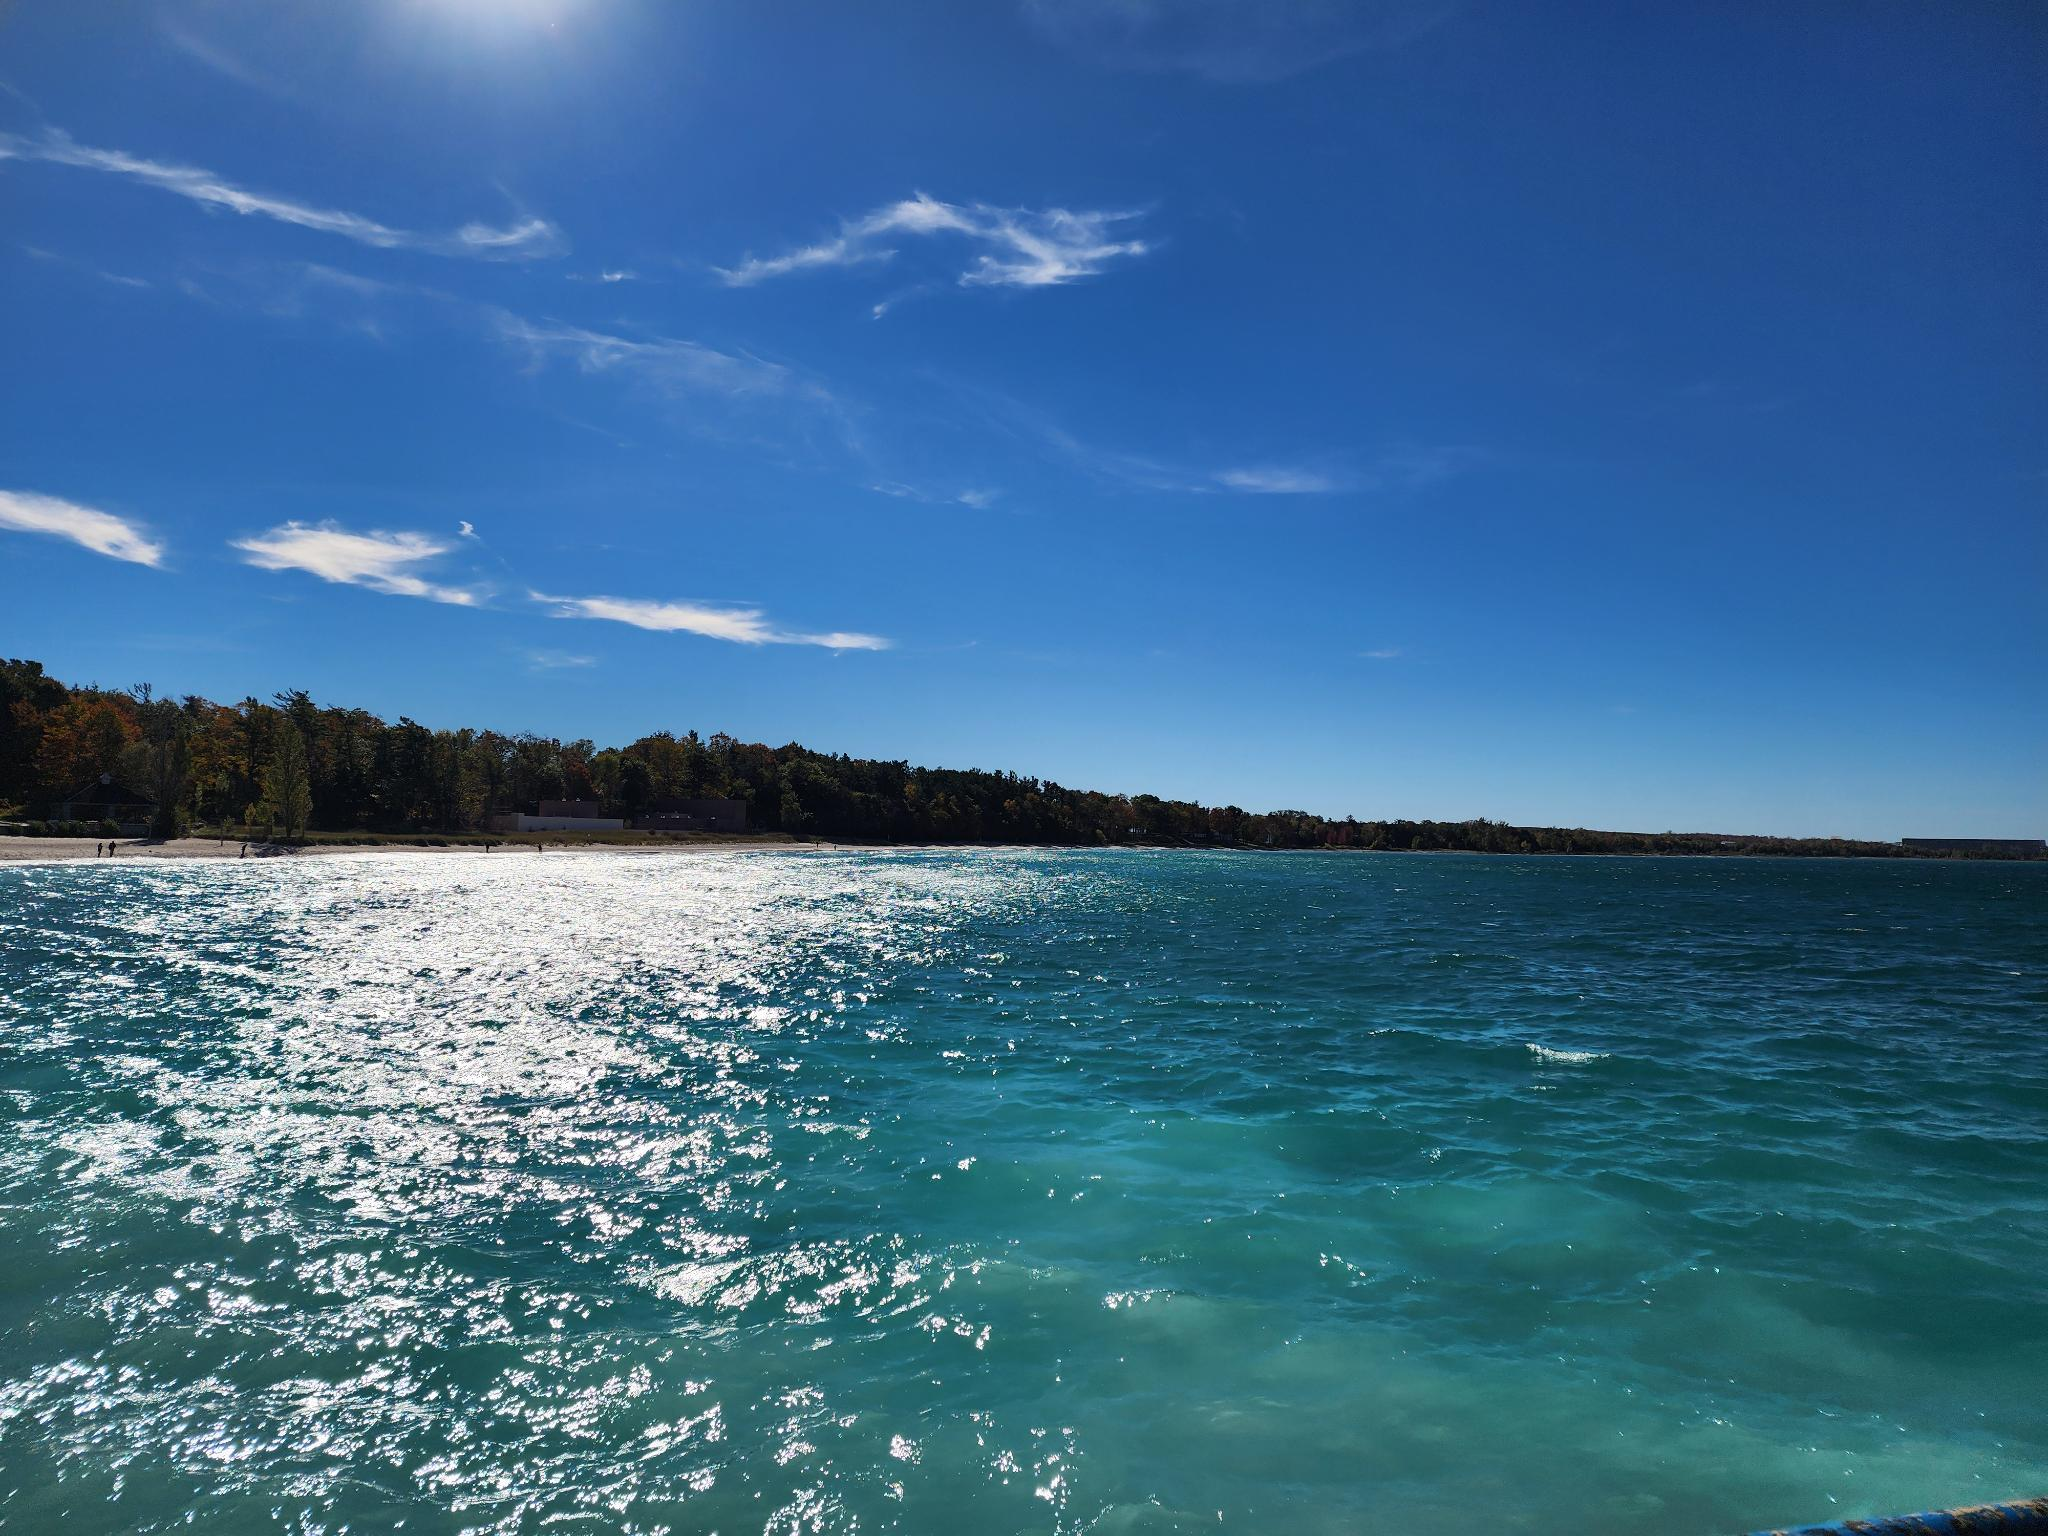
alt text for all four photos: All of these photos feature a view of Lake Michigan, from the shore of point Betsie. The light blue sky fades into a horizone of white cloud in the distance, where the waters of Lake Michigan meet it. The color of the lake's waters vary. The waters furthest out to the horizon are a deep and dark blue. Closer to the shore, the waters turn turqouis, then blue-green, then a gray-green from the large amounts of sand and sediment being tossed up upon the lakeshore. The shore is bordered with a small barrier of brown steel, jutting up out of the sand. Each of the images features crystal clear water beating against the brown iron wave breakers, spraying into the air like a geyser from the force of the waves hitting the shoreline's wave breaker. Small puddles of water form against the wave breaker, from these geysers spilling over onto the sand behind the barrier.

Media attachmentMedia attachmentMedia attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Speaking of Elberta, I've talked about "the wild shore" before. We made a visit while we were out, and I walked the beach path over to the bay's wave breakers.

The weather for our trip was PRISTINE. Rained some on the way in, and the next two days were bright, clear and WINDY. Made for beautiful views off the water, everywhere we went.

Advise turning the sound off for this one, as there is nothing I can do about the wind noise.

↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

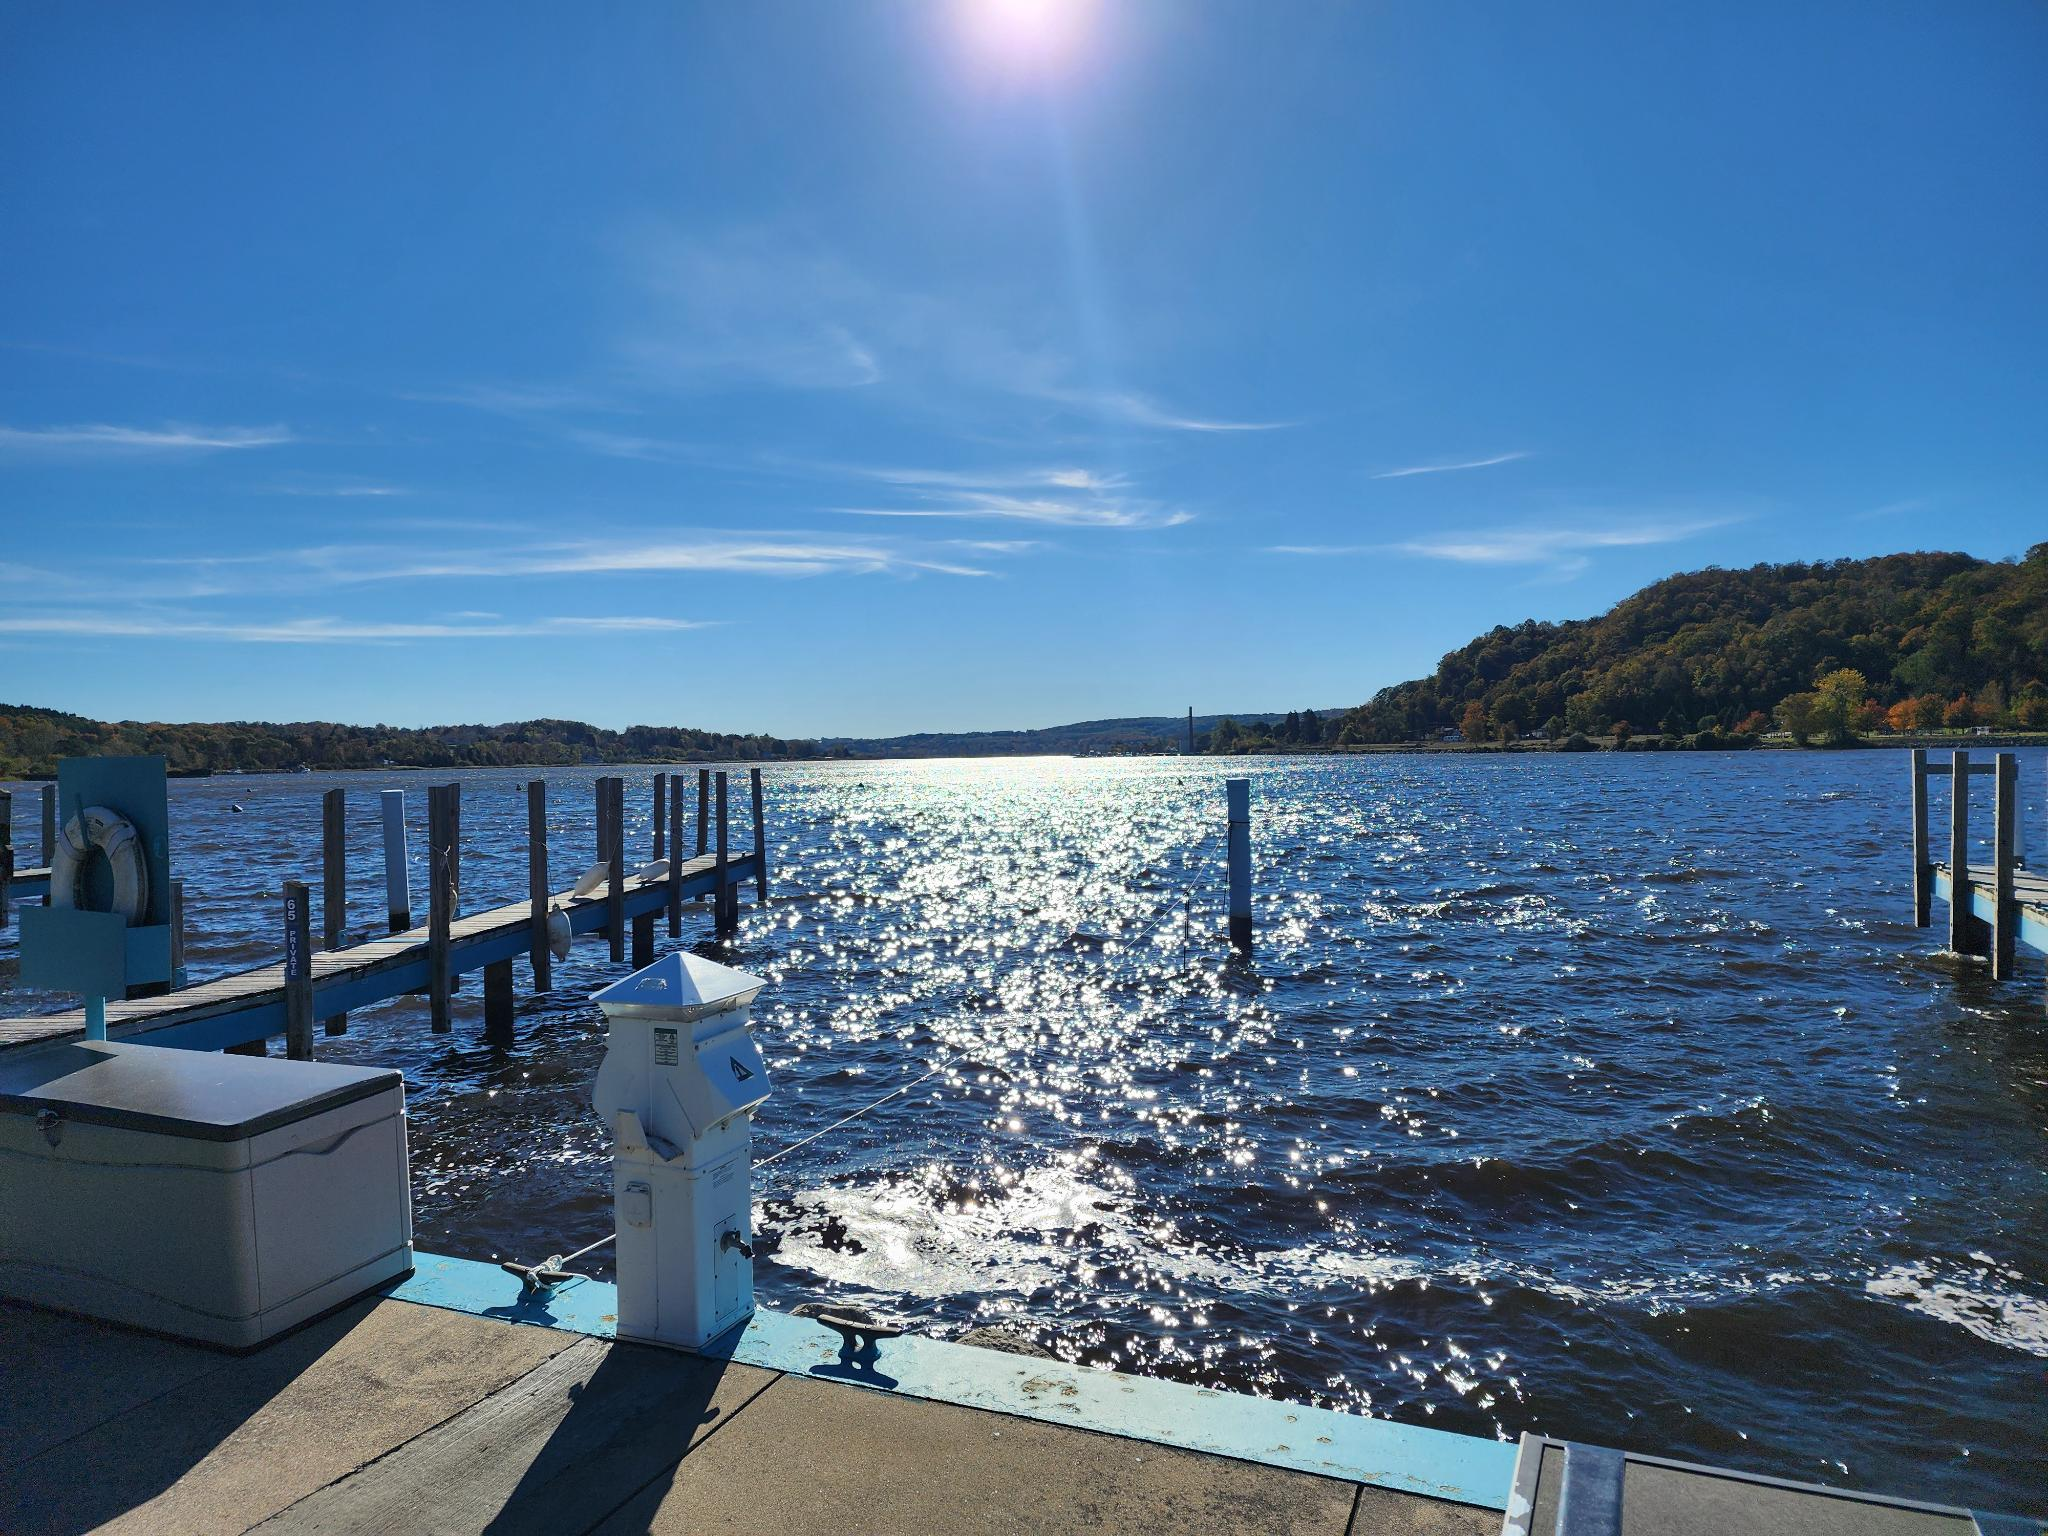
That same day, before we made the trek further north, We made one last stop in Frankfort to visit Bella's coffee shop for food and caffiene before the long trip out. This is a picture of the inner bay along the bayside walking path and park.In the distance, on the opposing shore, nestled in with all the trees is the town of Elberta.

Media attachment
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

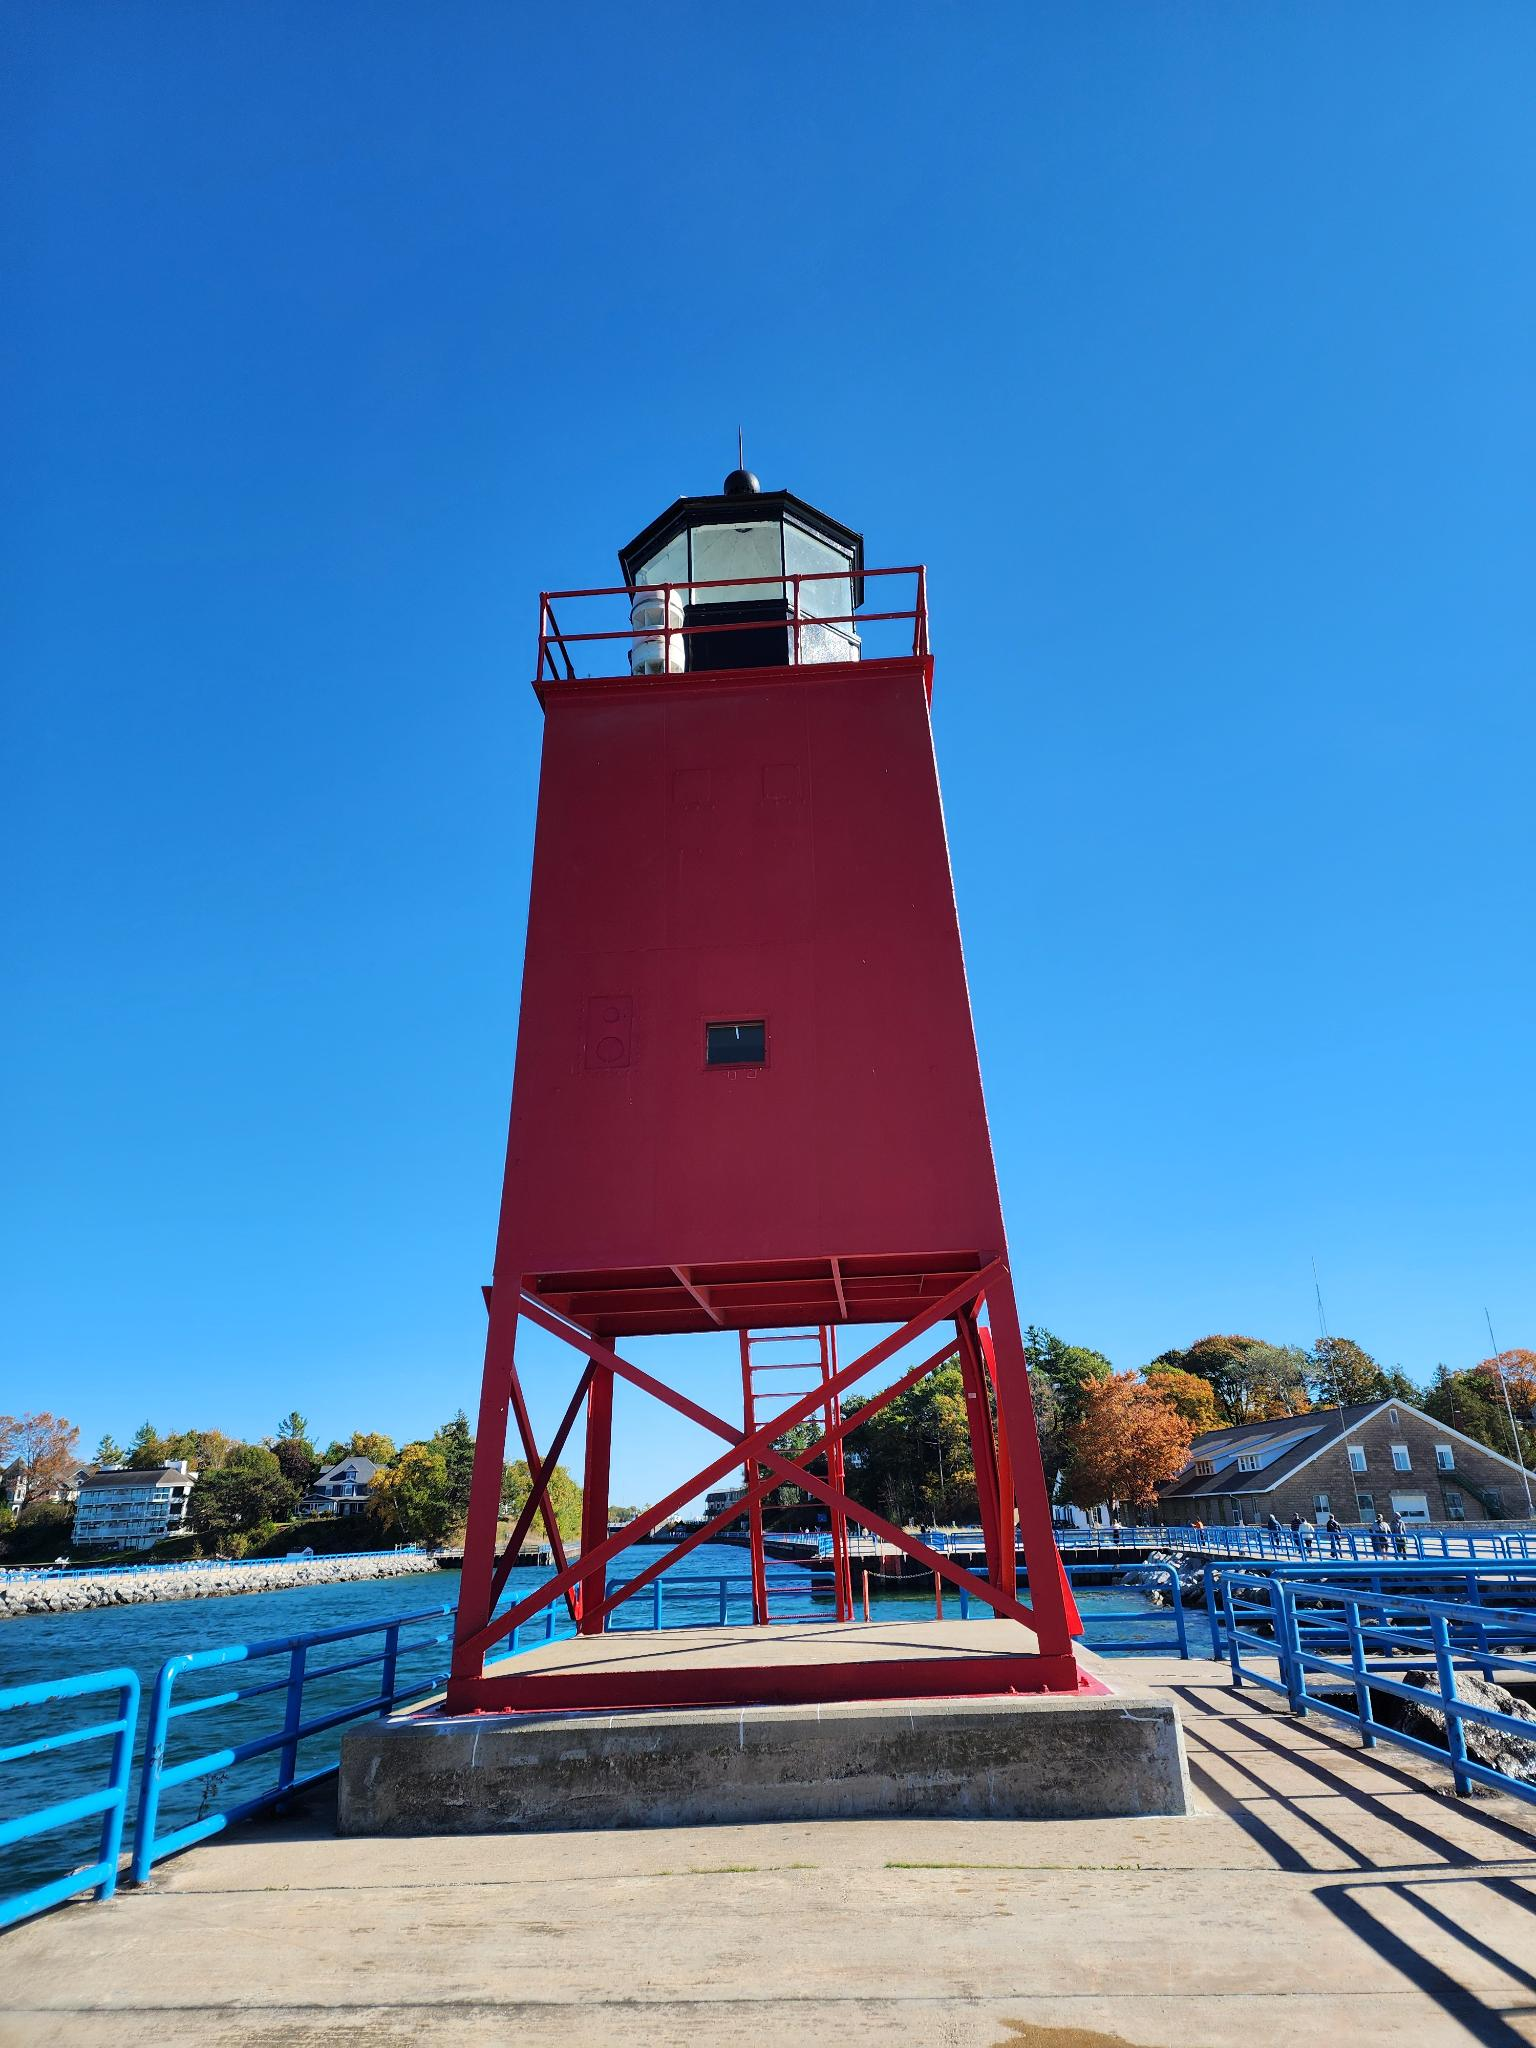
Charlevoix was gorgeous. I had never been before, and I had no idea what to expect. We would've never known what was here if my wife hadn't seen a sign for "Mushroom houses".

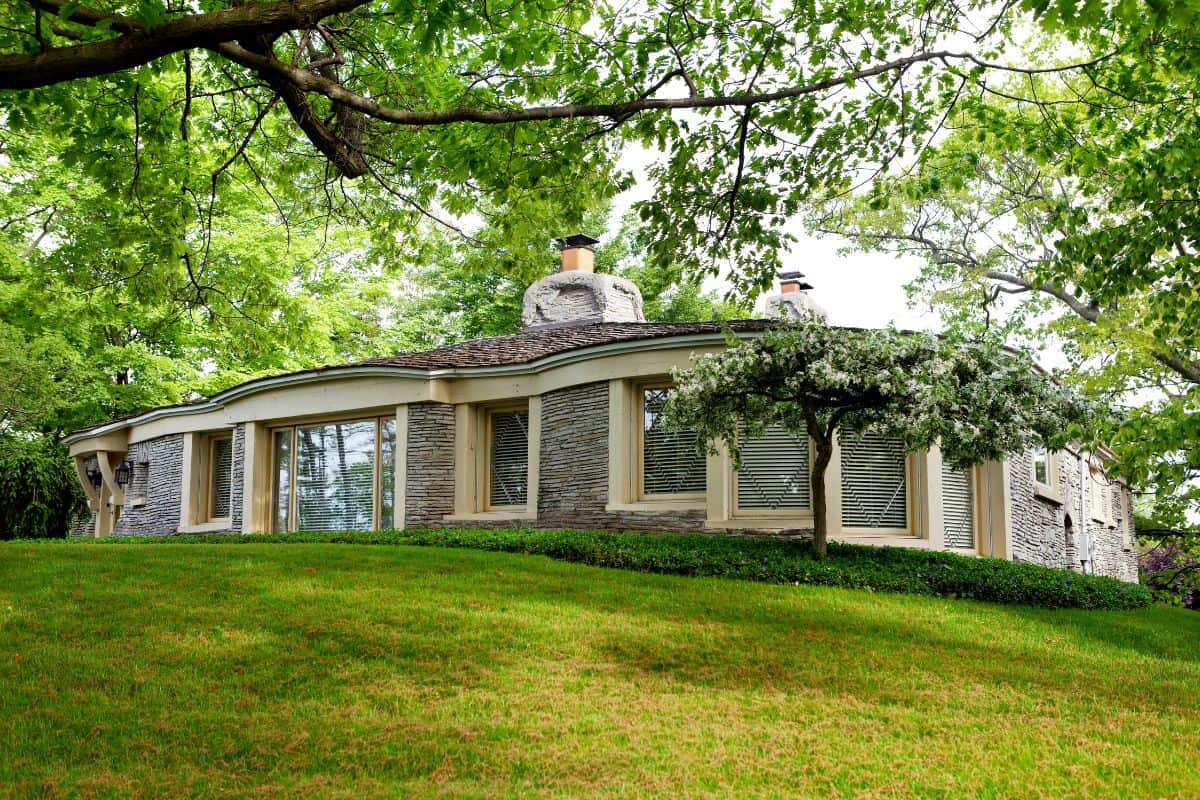
My wife watches some interesting home and garden shows. in one of them, an architect actually built a house and made the insulation of the house out of mycelium. In this instance, we're not entire sure if the sides of any of the houses here contain mycelium, but the roof of the biggest mushroom house out of the cluster we saw, definitely had a mycelium lined roof.

The house I'm taking about is on this page, and its the second image from the top.

https://mymichiganbeach.com/charlevoix-mushroom-houses/

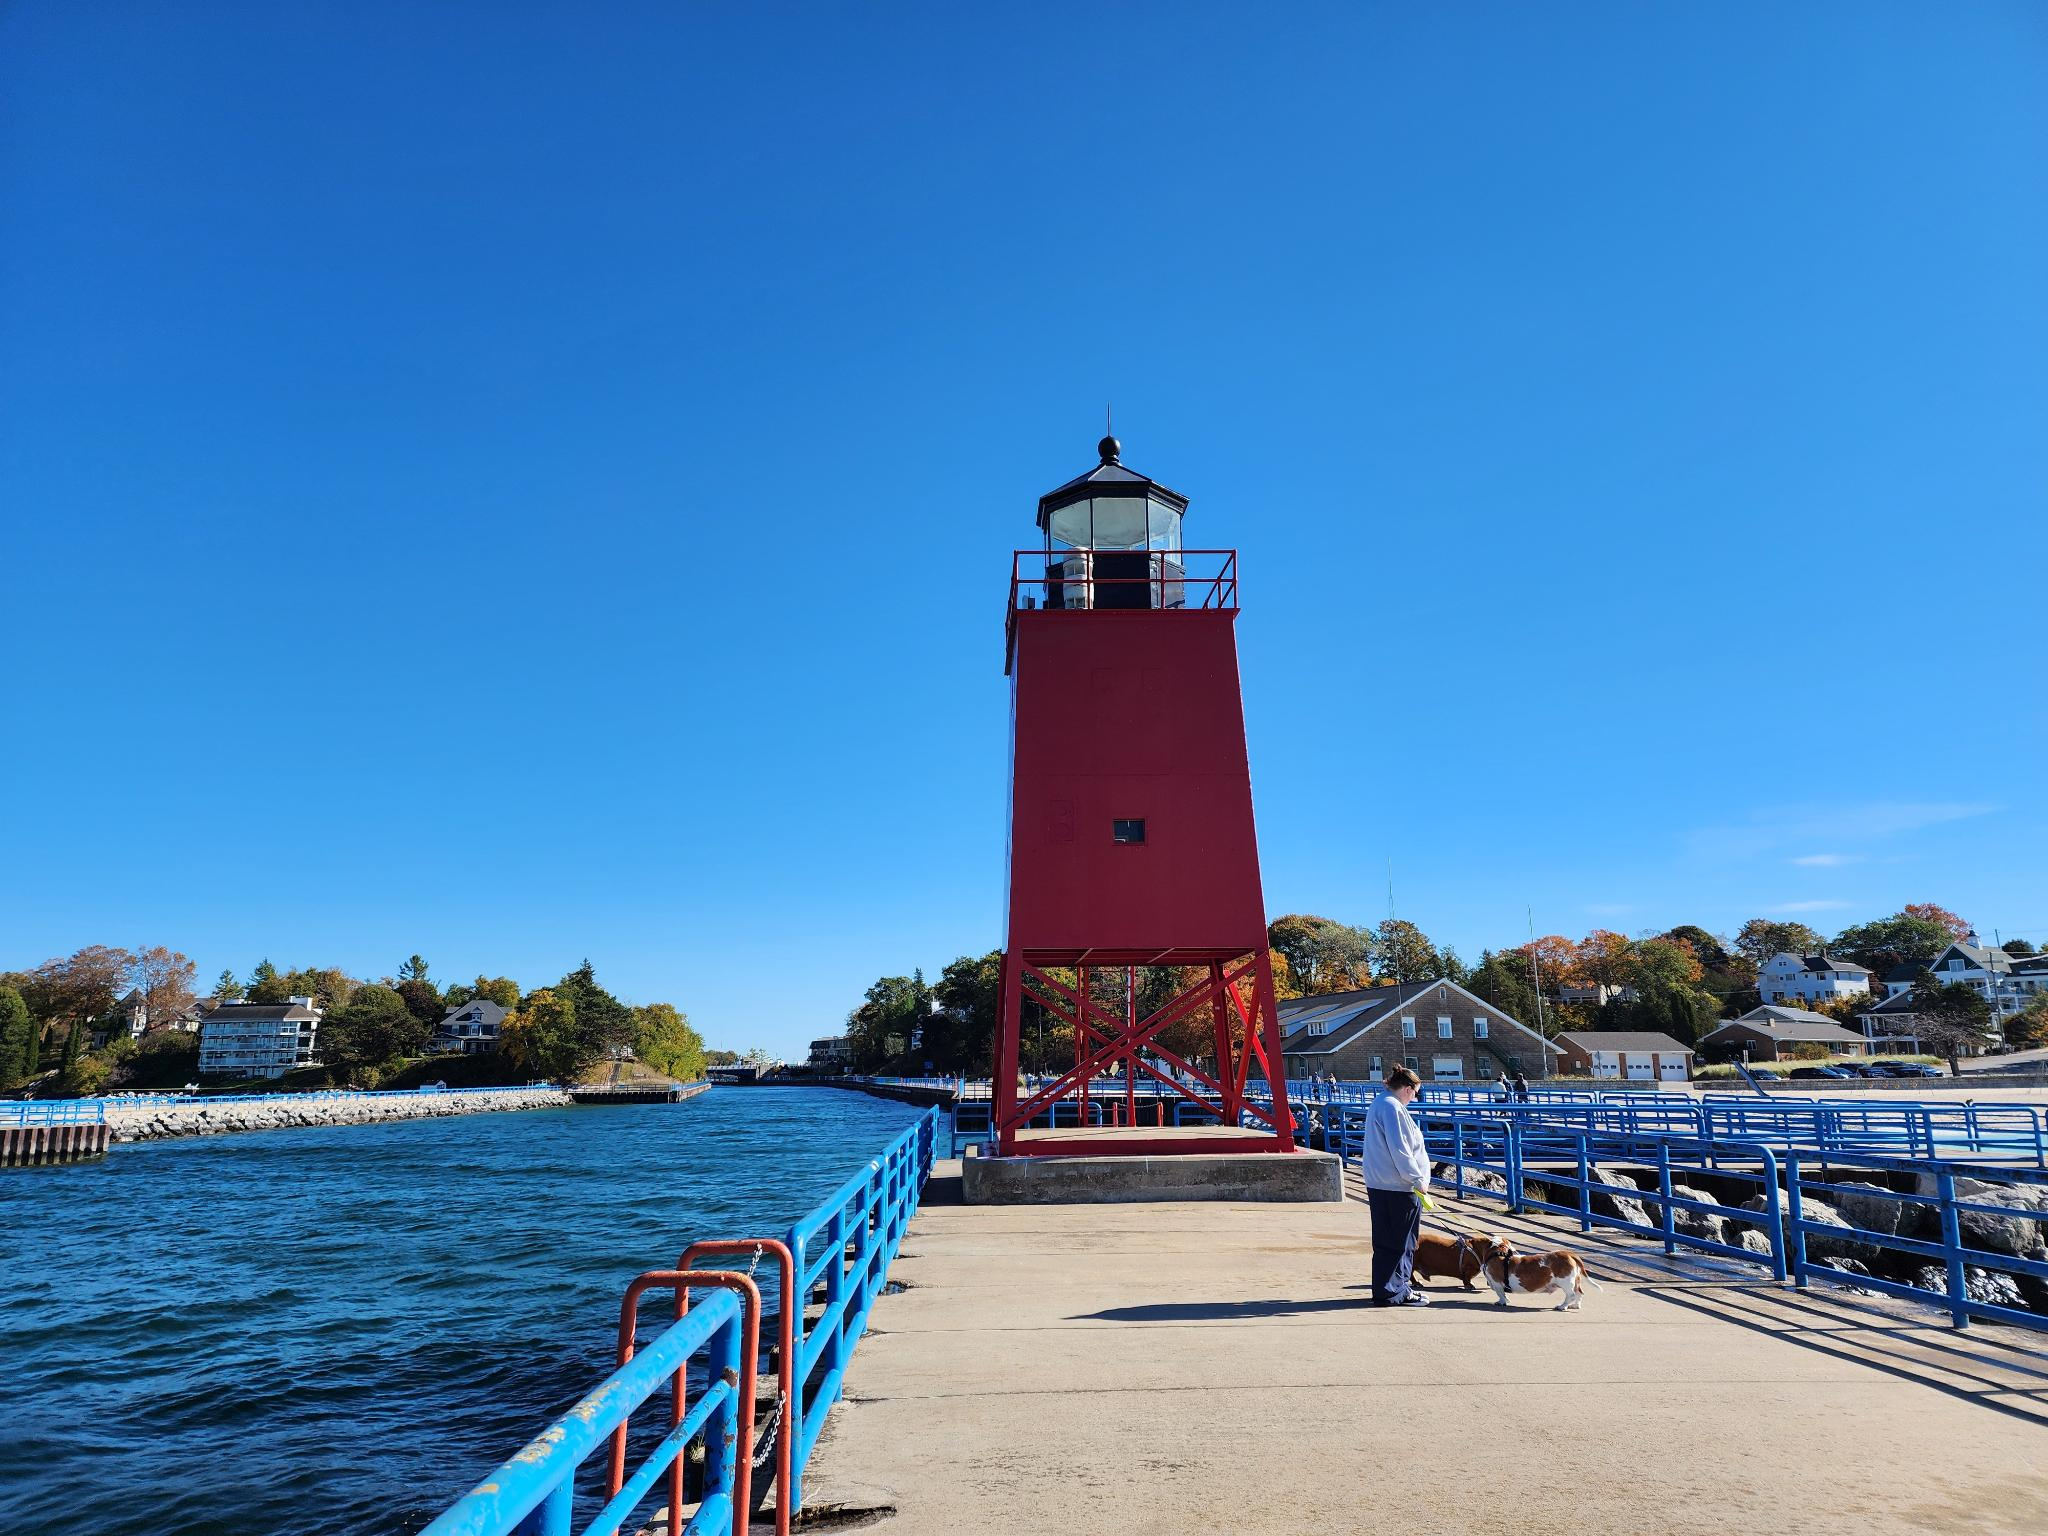
On the shores of Boulder Beach in Charlevoix, MI sits a large lighthouse. The lighthouse takes center stage in this image, bright red, except for the actual lighhouse housing at the top of the red tower, white with black framing. In the center of the iamge behind the lighthouse is a  riverside walking path, adorned with trees. Its fall, so the trees are a wide variety of shades, green, orange, yellow, and everything in between. The opposite shore of the riverside walkway can be seen as well.
My Michigan Beach and TravelCharlevoix Mushroom Houses: Earl Young's Hobbit Homes + Tours | My Michigan Beach and TravelDiscover the Charlevoix Mushroom Houses — architect Earl Young's storybook stone homes. The full story, the must-see houses, self-guided and GEM car tours, and how to visit respectfully.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

As promised late last night, I have tons of photos from the trip to northern michigan.

Where abouts? Northwestern portion of the lower peninsula. Those're my stomping grounds. However... We did take a trek past Traverse city out to Charlevoix (Pronounced Shar-le-voy), Petosky, and points north as we took M-119 ALMOST to Mackinac through "the tunnel of trees."

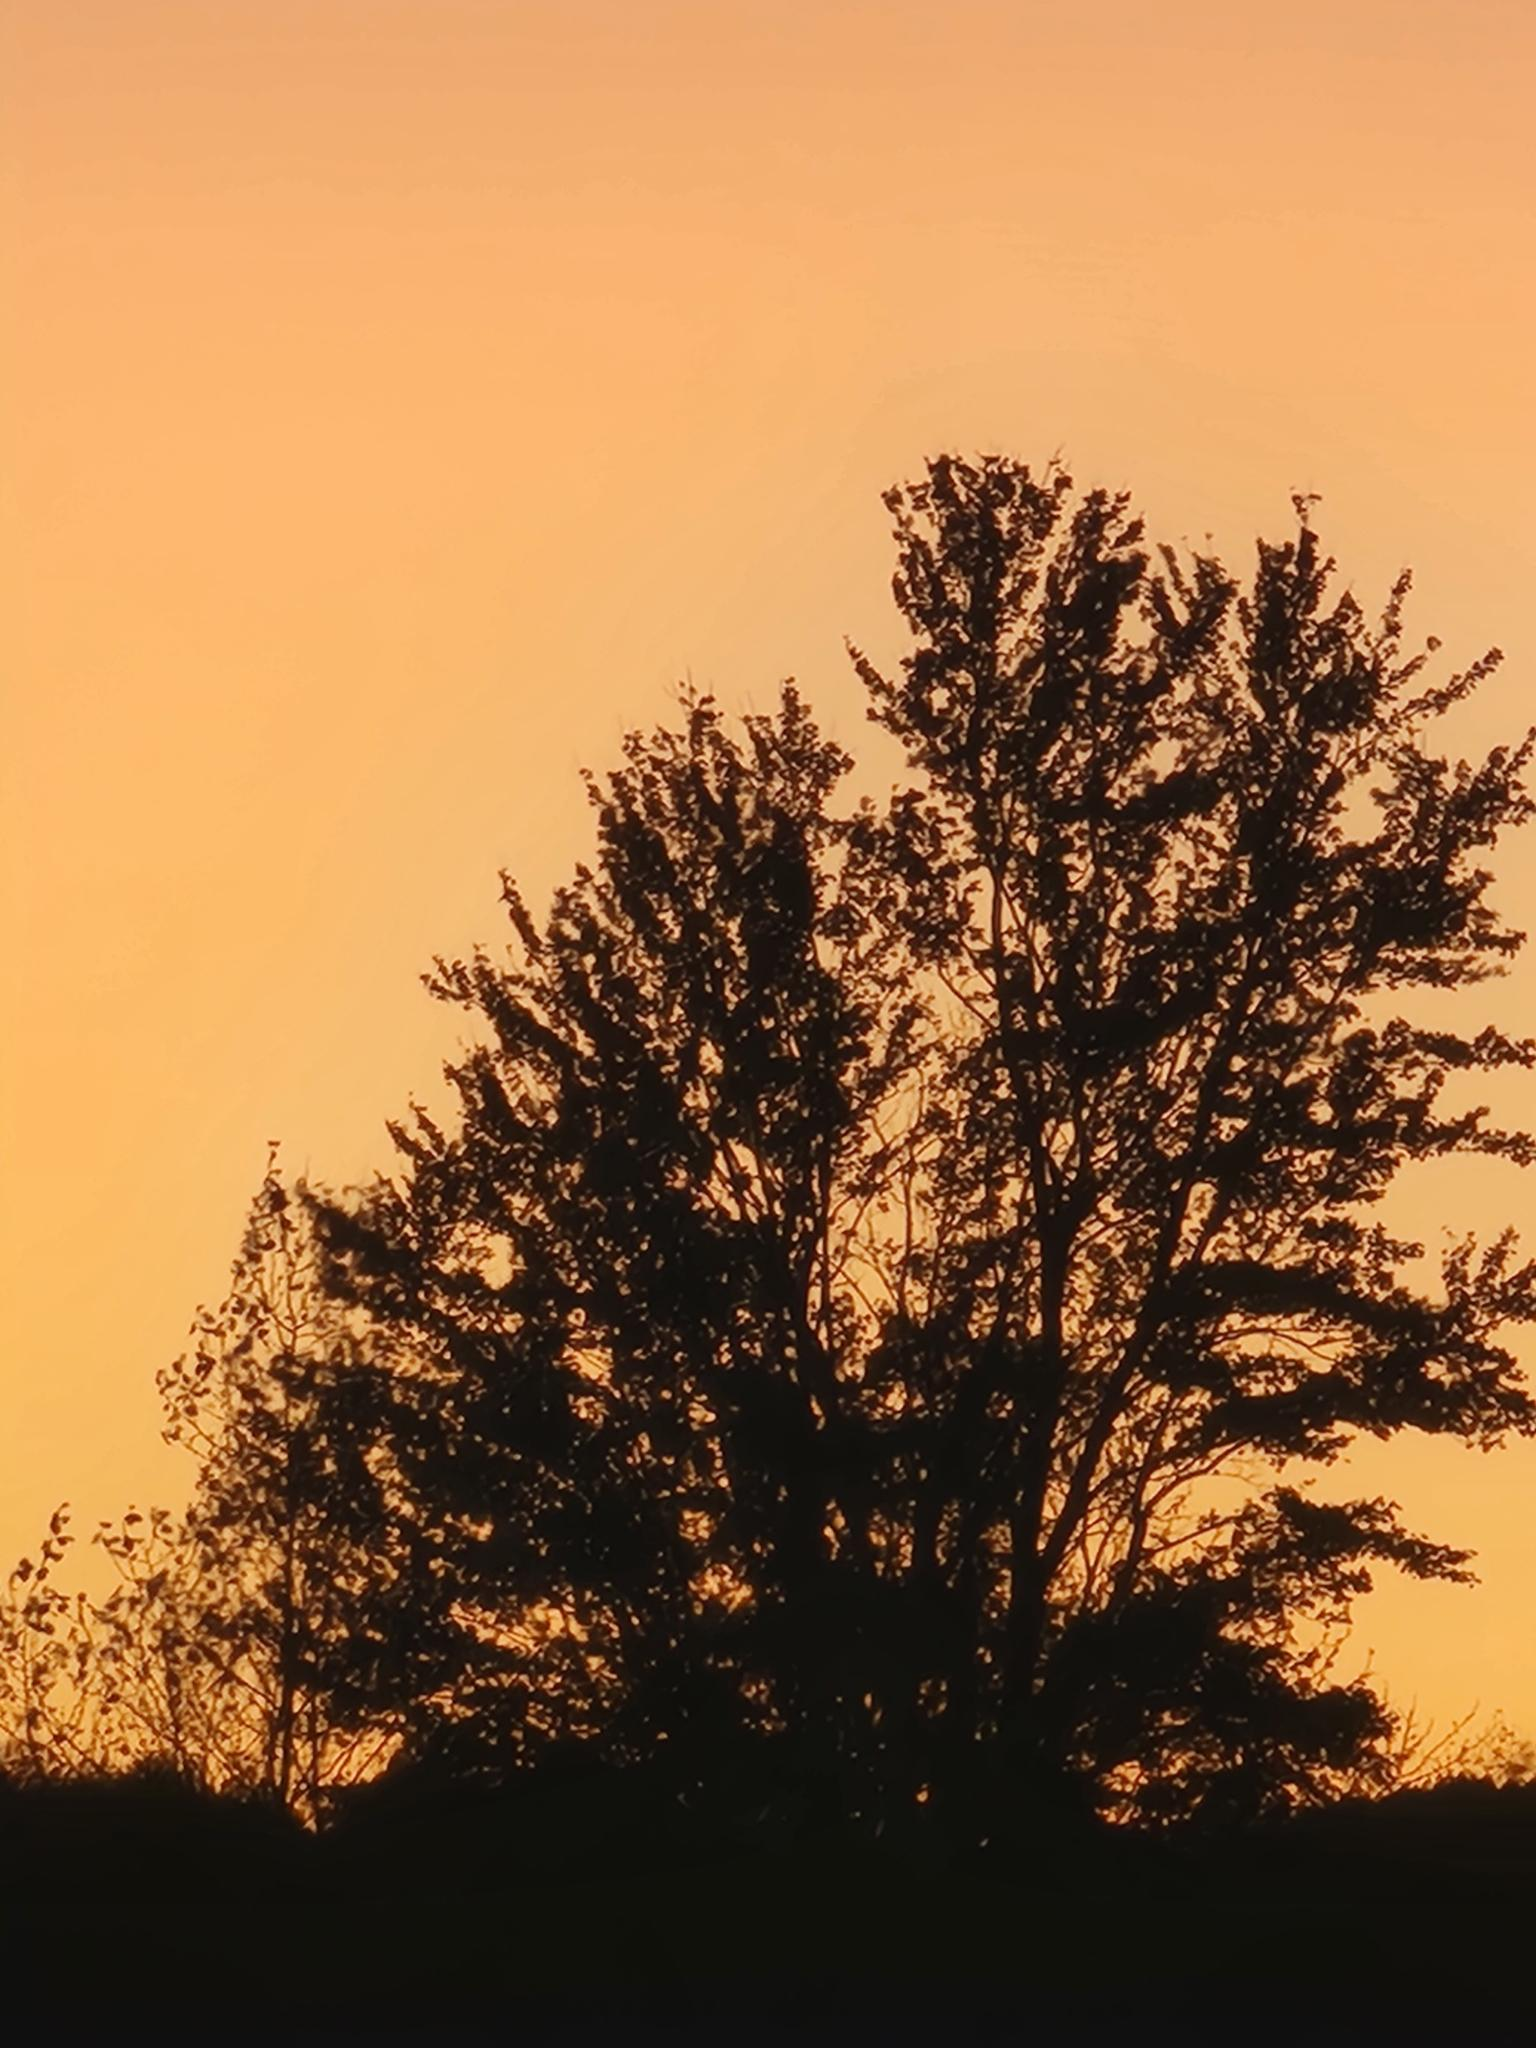
On our way back home from vacation, we stopped in Tawas Michigan for gas. I saw a lone tree silhouetted against the setting sun, and took a picture.  The sky is a mixture shades of orange moving towards the top of the image. Silhoutted in the center of the image is the shadow of a large tree.
↩ Reply ♡ 0 · ↻ 0 ↗ Original