X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

Martin Edwards

@[email protected]

Computer technician and village newsletter editor in Oxfordshire, UK. Passionate about cyber security, electronic music, wildlife and pet rats. :donor:

Open remote profile ↗
Posts

I wonder if one reason we've seen so much growth in the #FarRight in the last decade is that pretty much everyone who actually fought in or even just lived through WWII has now passed on.

The philosopher George Santayana famously wrote: "Those who cannot remember the past are condemned to repeat it."

Not only that, but I think a lot of these raise-the-flags, stop-the-boats folk genuinely believe that their ancestors from that time would support what they're doing — when probably the opposite is true.

#ukpol #fascism

↩ Reply ♡ 0 · ↻ 0 ↗ Original

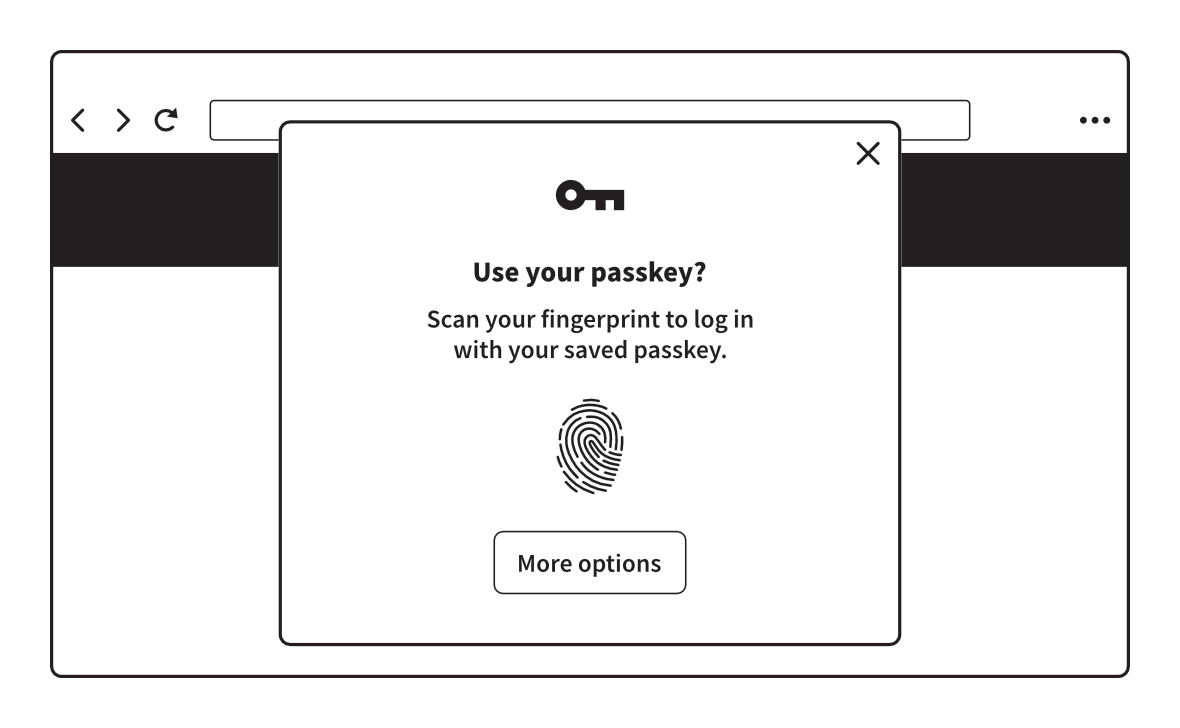
It's up to a website whether or not it requires your approval to use a passkey in any given situation. Some will require it only for higher-risk actions. This is because you've already had to use your biometric information, PIN or password to unlock and use your device — so because it's unlikely someone would grab it from your hands, or sneak up to your desk when your back is turned, it's a reasonable assumption that it's still you using it.

Web browser asking "Use your passkey? Scan your fingerprint to log in with your saved passkey."
↩ Reply ♡ 0 · ↻ 0 ↗ Original

87-year-old customer says she's not eaten all day because she's so stressed trying to #print.

In a 90-minute phone call – and with English not her first language – she followed diligently step-by-step as I guided her to restart the iPad, try the iPhone instead, restart the #printer, restart the router, rejoin the printer to Wi-Fi, factory reset the printer, check for printer firmware updates, and factory reset the router. All to no avail.

Now I'm off to find her a new printer, and she's promised she'll have dinner.

Dear tech bros: we don't want AI, we don't want smart everything, we don't want a new version every year. We want stuff that works.

#TechSupport #enshittification

↩ Reply ♡ 0 · ↻ 0 ↗ Original

To complicate things, major shared hosting providers have patched #PHP against #php2shell using a backport — without incrementing the version number displayed by phpinfo.

On the plus side – and it's a massive plus – this means that for many sites, versions as old as 5.2 are protected, even though the PHP Team only released official patches for 8.2 and newer.

On the minus side, if you run a website there's no obvious way to tell whether you're using the new or old version.

This explains why, across the various websites I manage, even really old versions of PHP have build dates of Wednesday afternoon a few hours after the official fixes. It seems almost too good to be true.

CloudLinux explained: "PHP.net fixed CVE-2026-109618 and CVE-2026-109619 in new PHP versions […] Our alt-php and ea-php packages carry the same fix applied to the PHP version they already shipped (a backport). These packages contain the fix for both CVEs, even though the PHP version number is lower."

Then today, CloudLinux released builds to bring the version numbers in line with the official ones.

Information from #cPanel and #CloudLinux here:

https://support.cpanel.net/hc/en-us/articles/44397389677335-Critical-PHP-Security-Release-CVE-2026-109618-and-CVE-2026-109619

https://cloudlinux.statuspage.io/incidents/zl0vt1yq3dj5

cPanelCritical PHP Security Release - CVE-2026-109618 and CVE-2026-109619SituationCritical security vulnerabilities were found in PHP, and have been assigned CVE-2026-109618 and CVE-2026-109619. For more information, you can find the official announcement here:PHP News ...
↩ Reply ♡ 0 · ↻ 0 ↗ Original