this also affects the system Python:
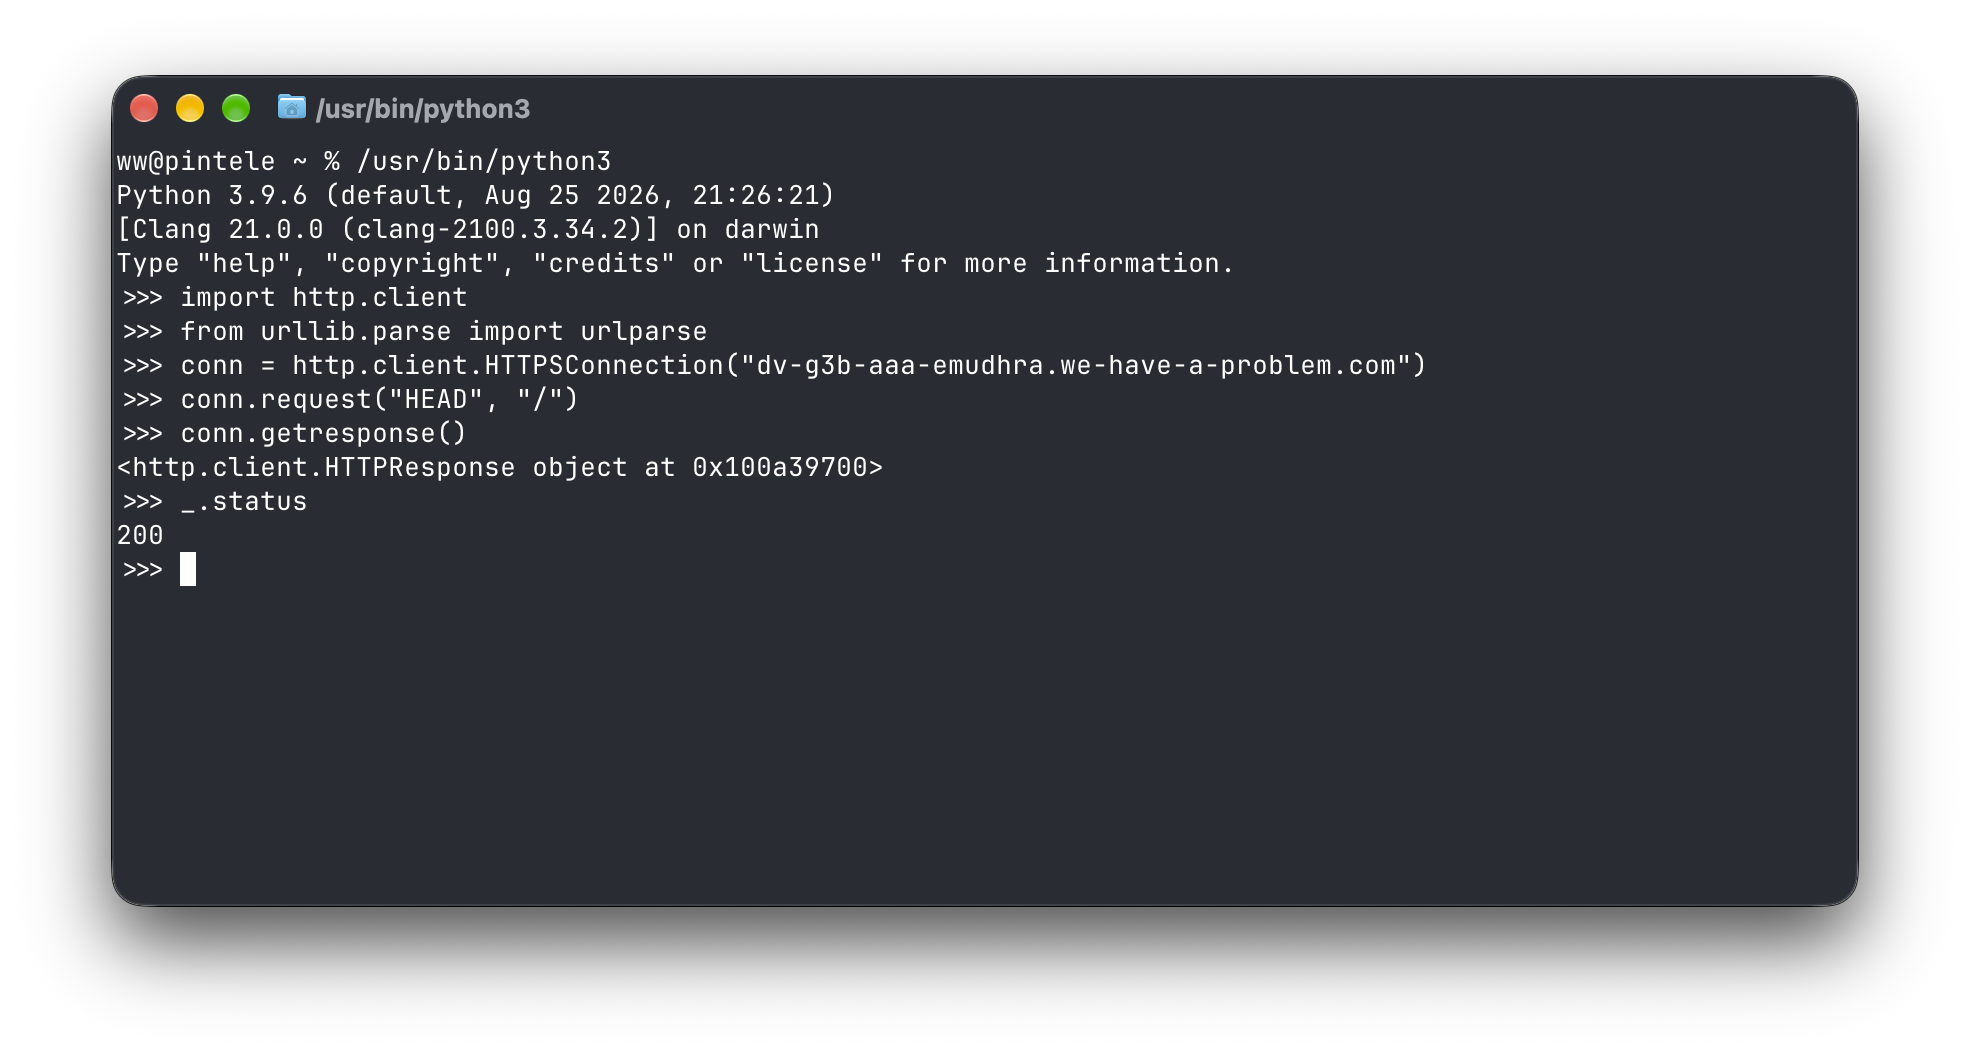

this also affects the system Python:
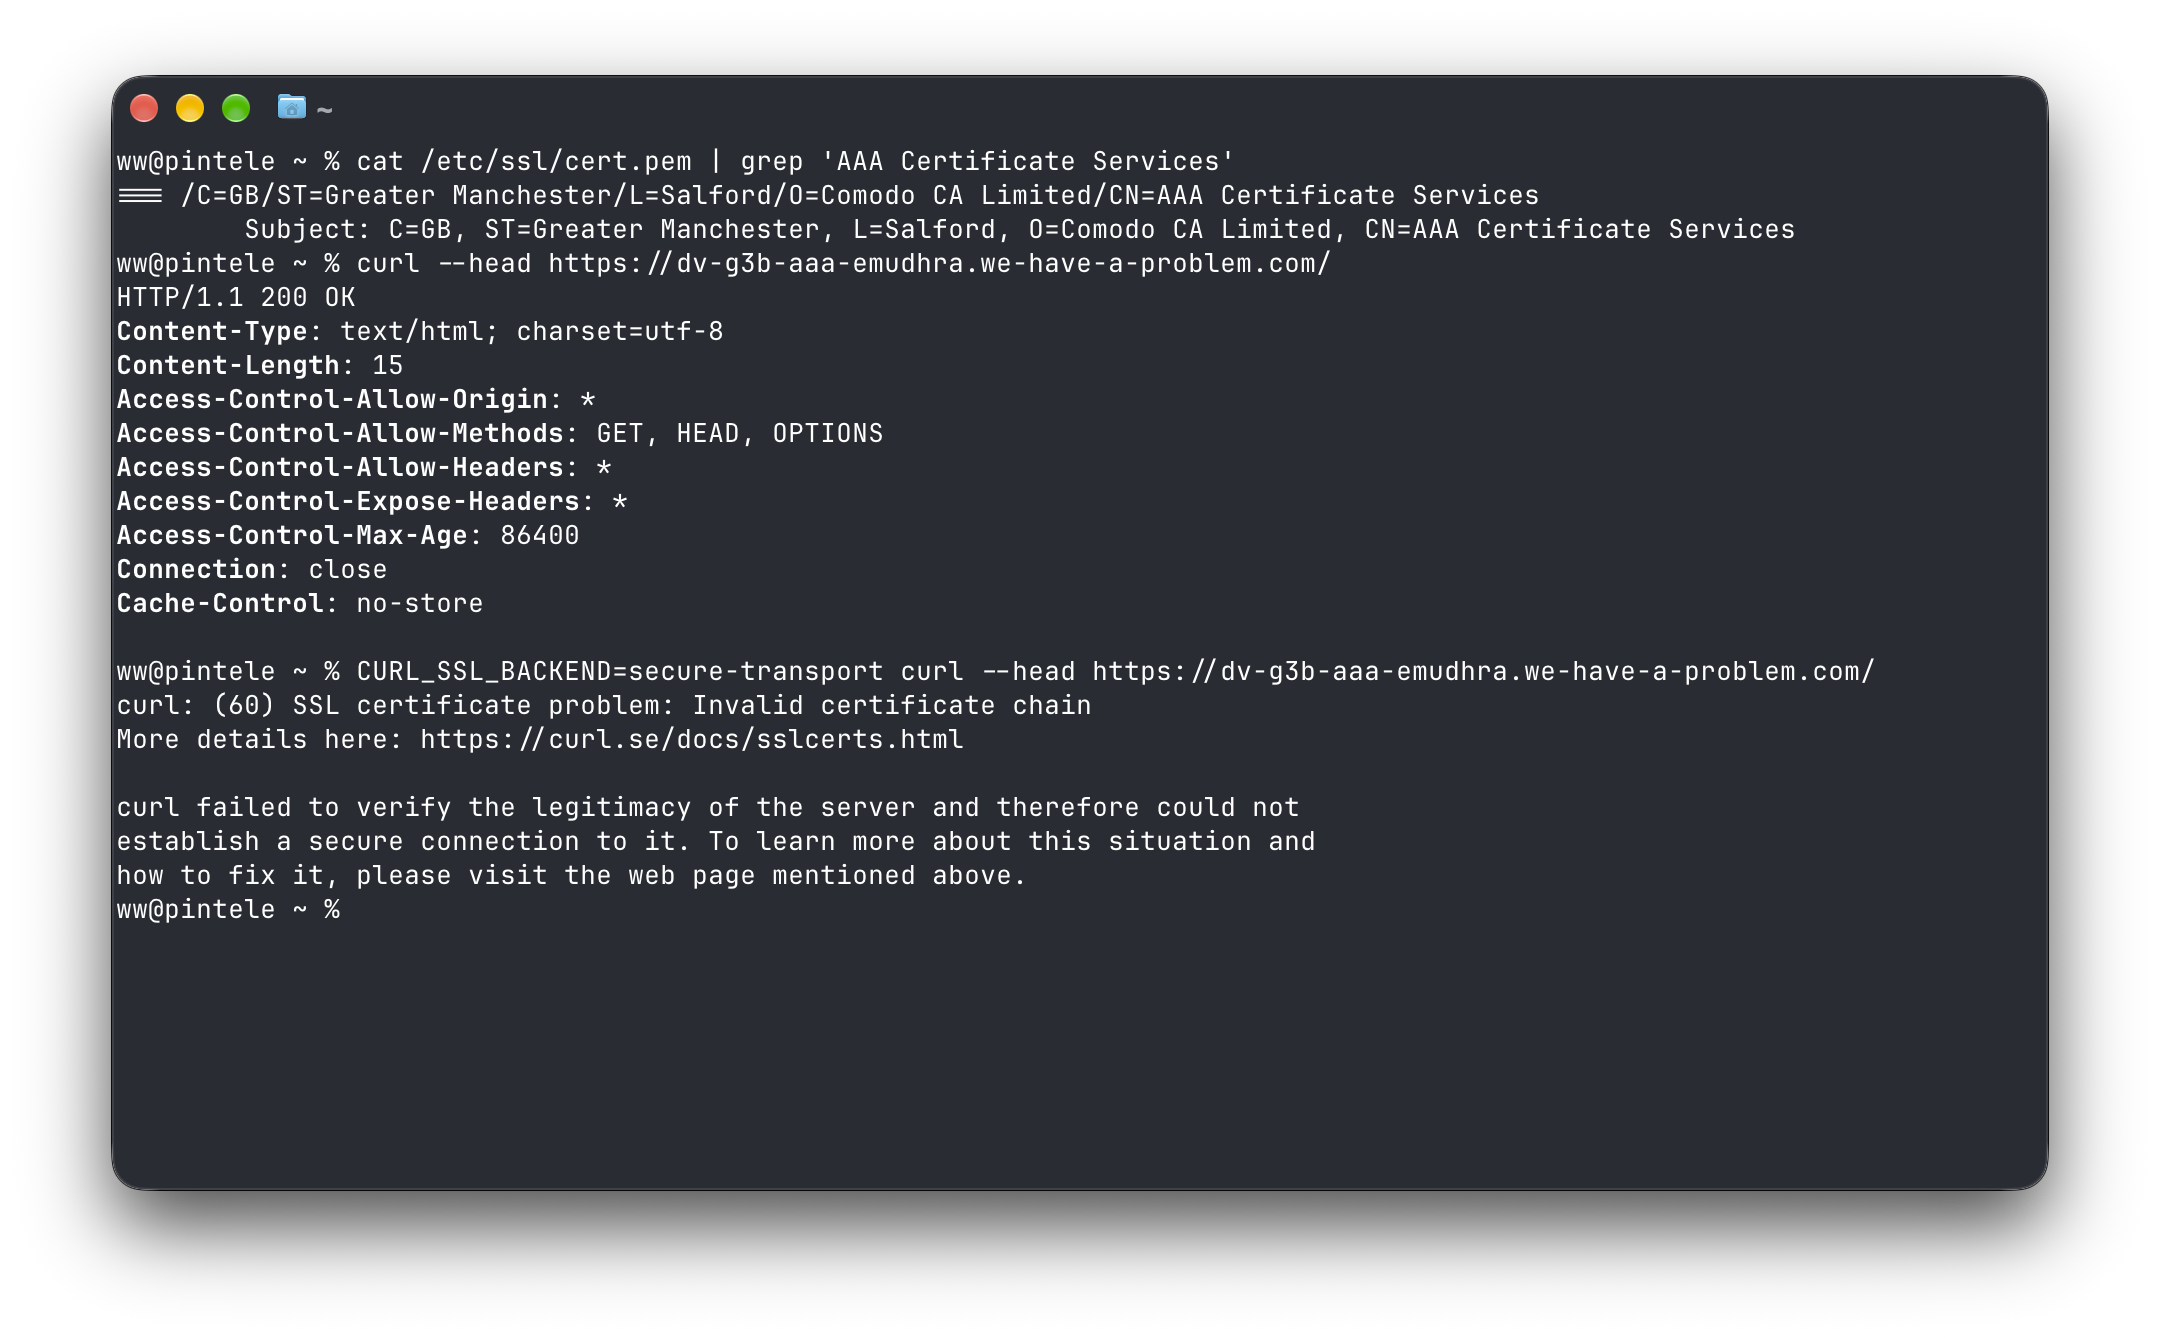
Apple appears to have rolled the eMudra distrust into their native root program, but **not** into `/etc/ssl/cert.pem`, meaning that macOS supplied tools like `curl` and the system Python are still affected by the compromised intermediates.
setting `CURL_SSL_BACKEND=secure-transport` redirects the system curl to the platform verifier, but it's not great that every macOS host is trivially MITM-able by default at the moment.
we’ve released uv 0.13.4 and pip has released 26.2.2 for the eMudra CA incident. Please upgrade ASAP!
 Discussions on Python.orgInformation for Python users regarding eMudhra / emSign CA certificate security incidentA security incident affecting eMudhra intermediate certificates has required removing the emSign root CA certificate from CA bundles such as “certifi”. It’s important to immediately upgrade the software packages below to at least the versions specified and rebuild container images to fetch the latest system certificates. Failure to do so could result in monster-in-the-middle (MITM) attacks against