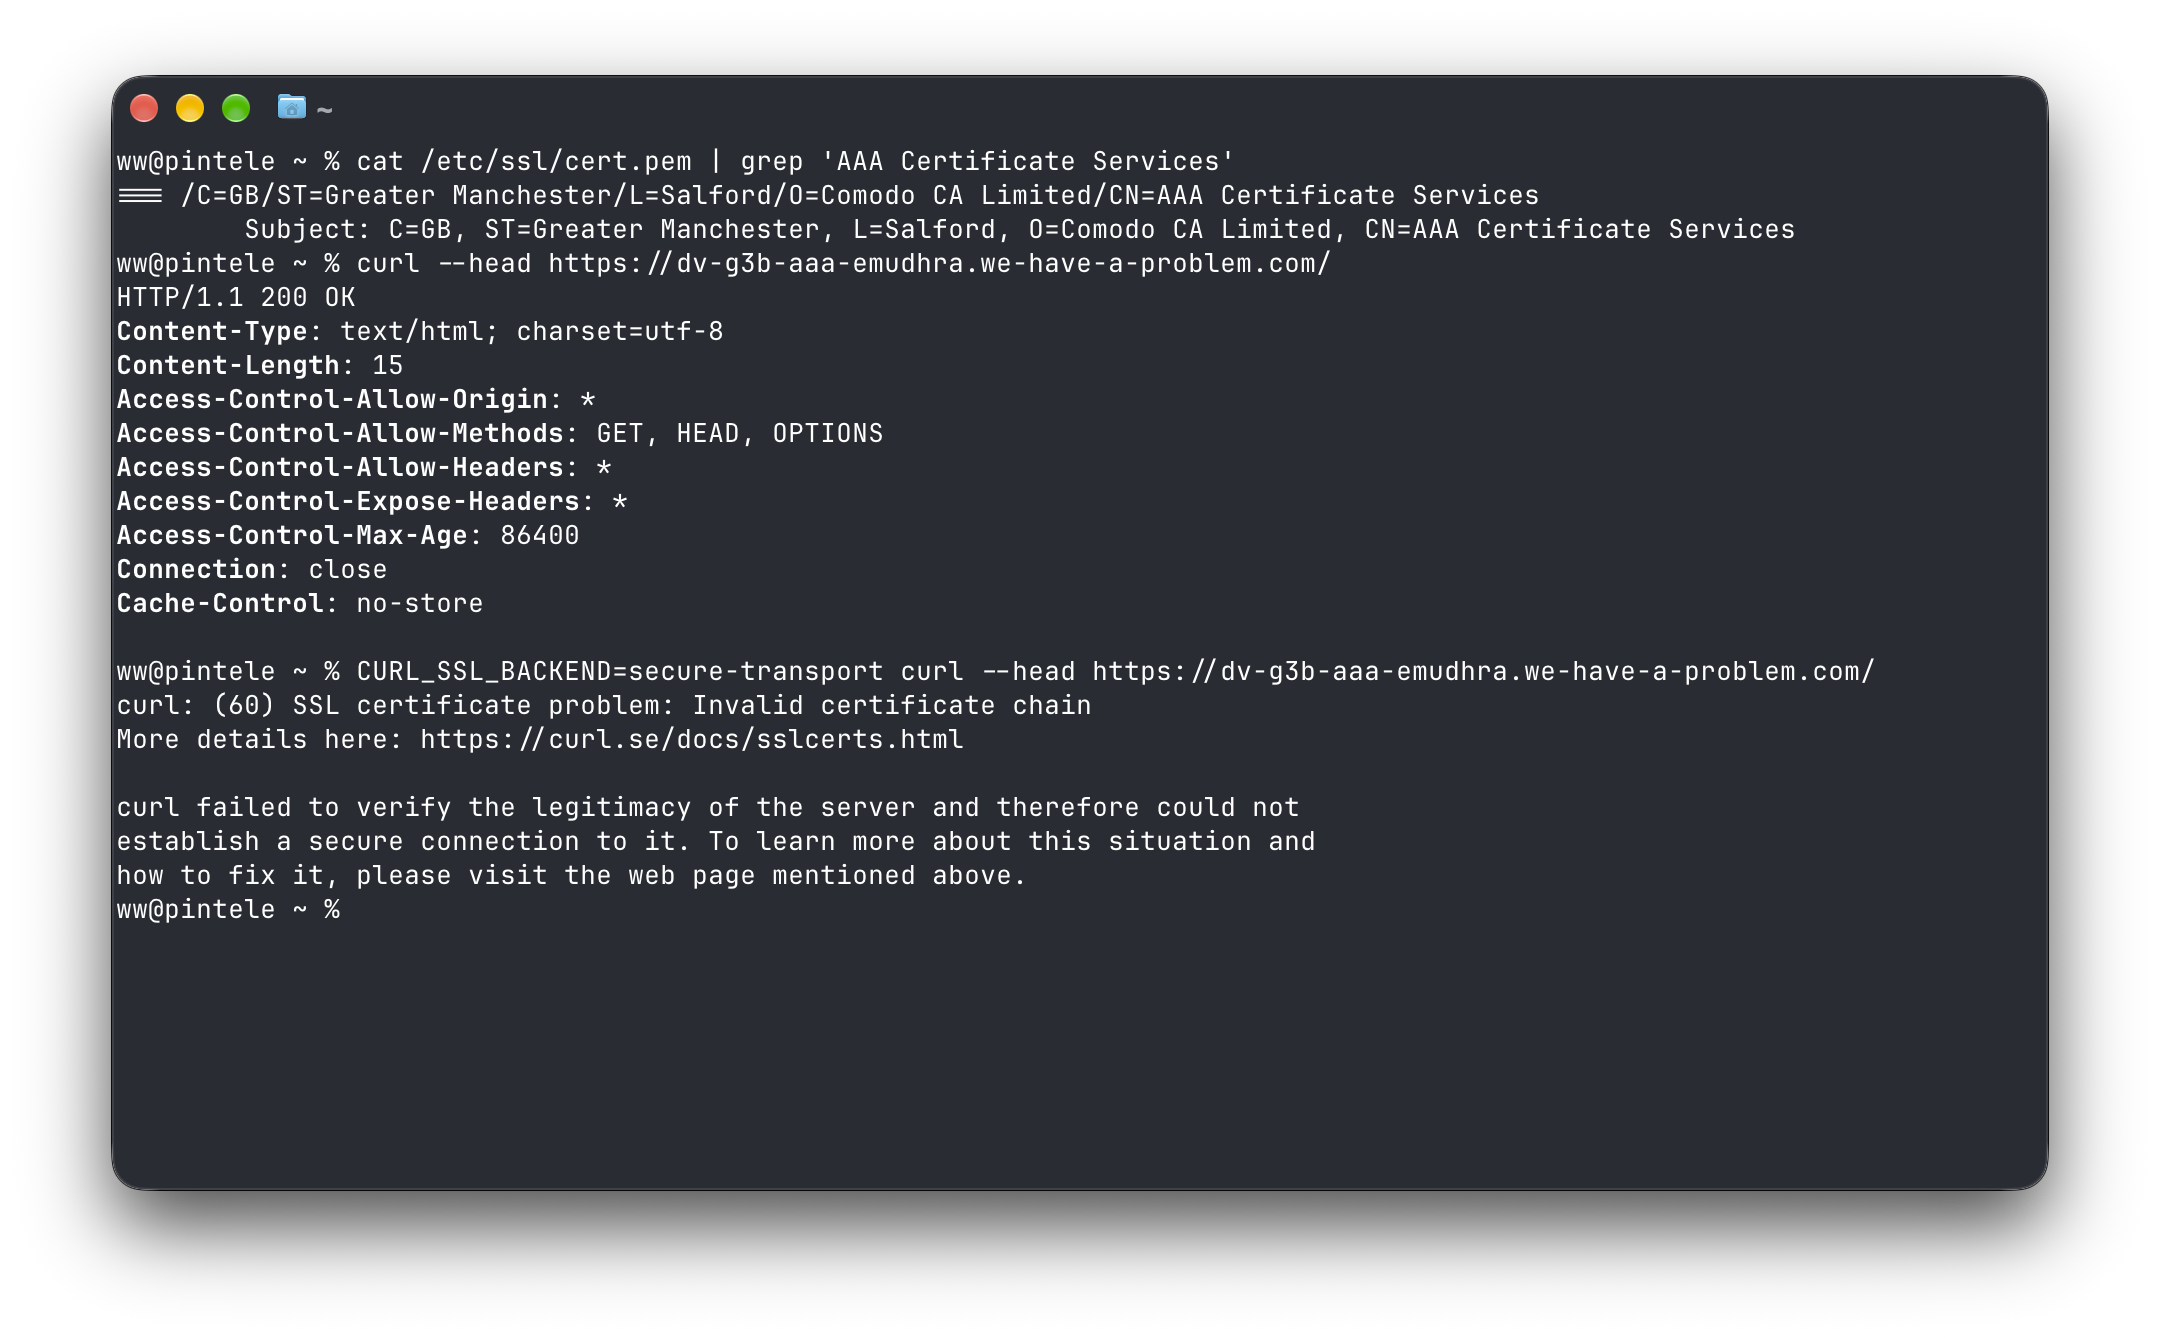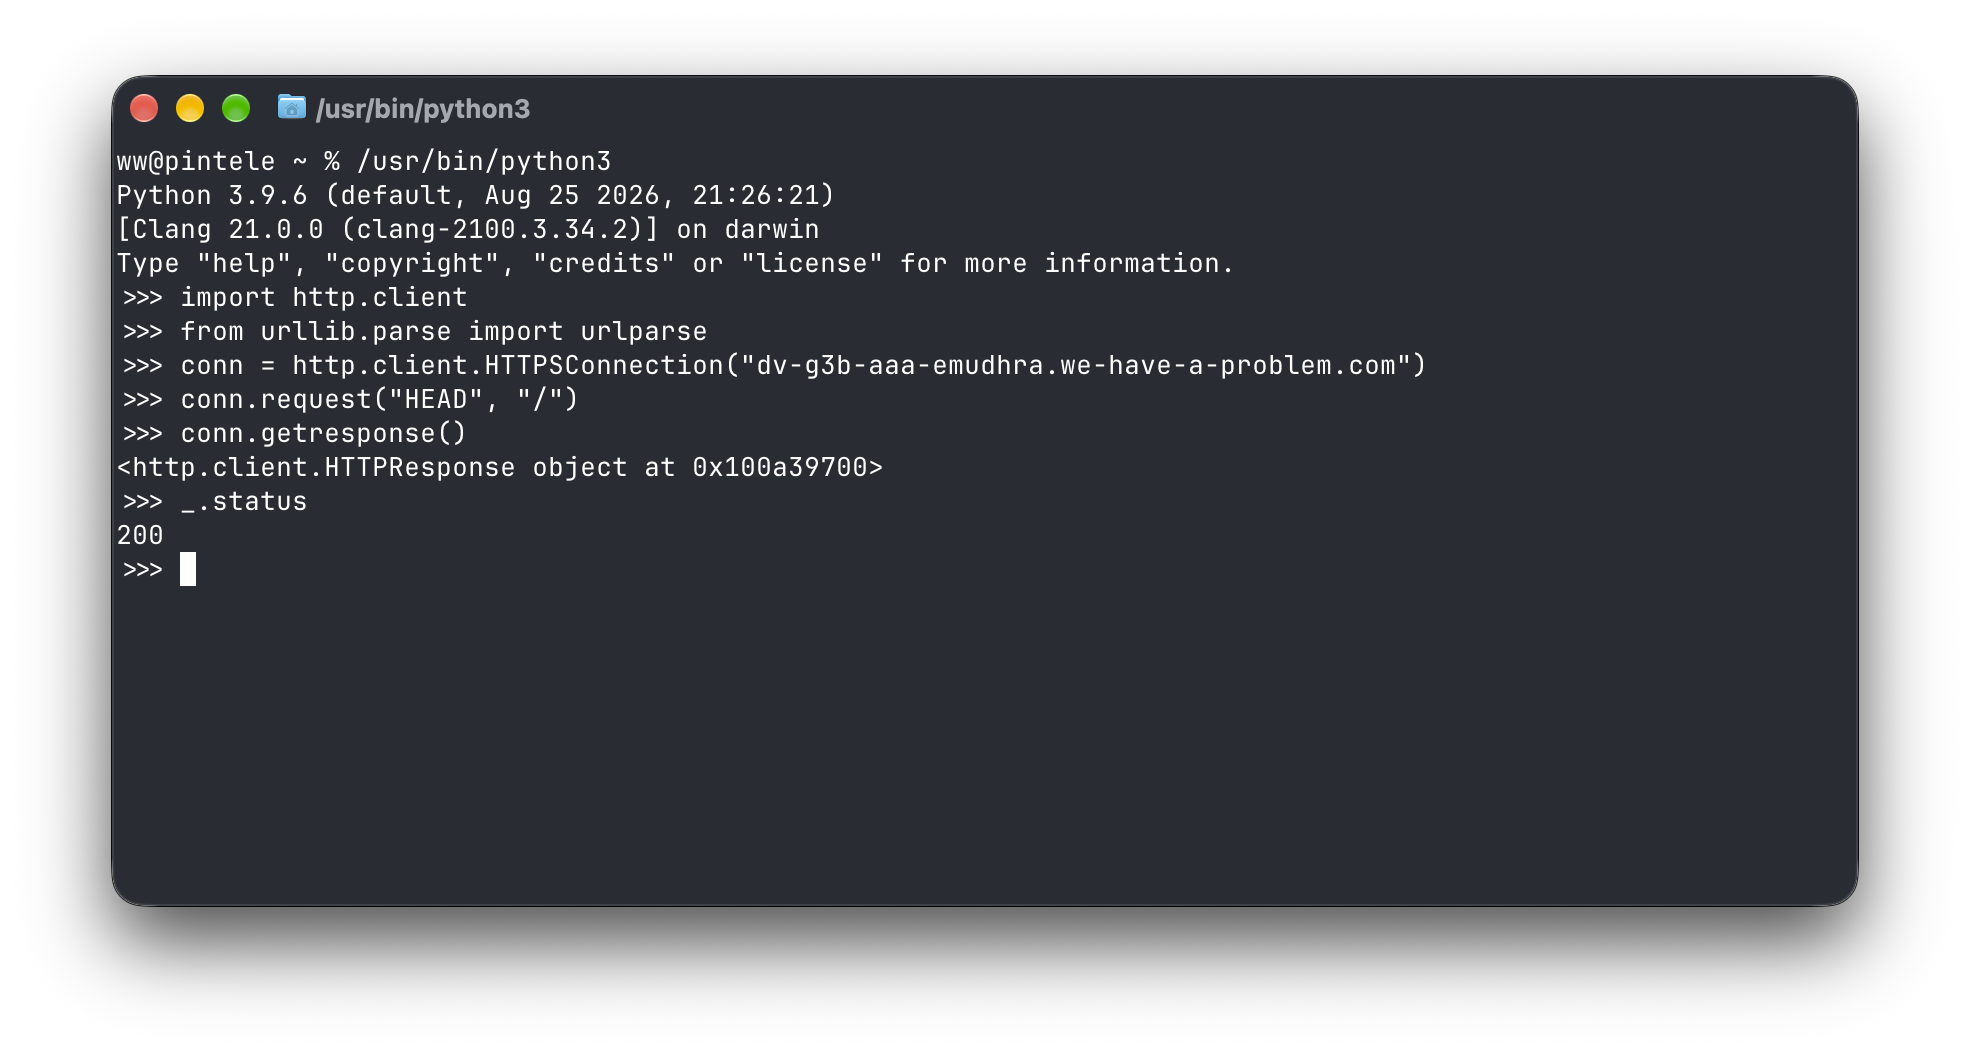
Apple appears to have rolled the eMudra distrust into their native root program, but **not** into `/etc/ssl/cert.pem`, meaning that macOS supplied tools like `curl` and the system Python are still affected by the compromised intermediates.
setting `CURL_SSL_BACKEND=secure-transport` redirects the system curl to the platform verifier, but it's not great that every macOS host is trivially MITM-able by default at the moment.