X XFediYour place in the Fediverse
XFEDI

Federated

ActivityPub
HELLO, FEDIVERSE

Good conversations travel.

Public updates from xsukax and this corner of the network.

Sign In to your account

Public posts known to this server, including selected instances.

2026-10-30_01-26-17 #ddosia #noname057 The attacks by noname057 primarily target websites in Italy and France. Key sectors affected include government, industry, and transportation, with notable sites such as agenziaindustriedifesa.it and comune.modena.it in Italy, as well as multiple free.fr domains in France. Other targeted entities include educational institutions and companies in various industries, highlighting a diverse range of interests in the attacks. check on:https://42de.it
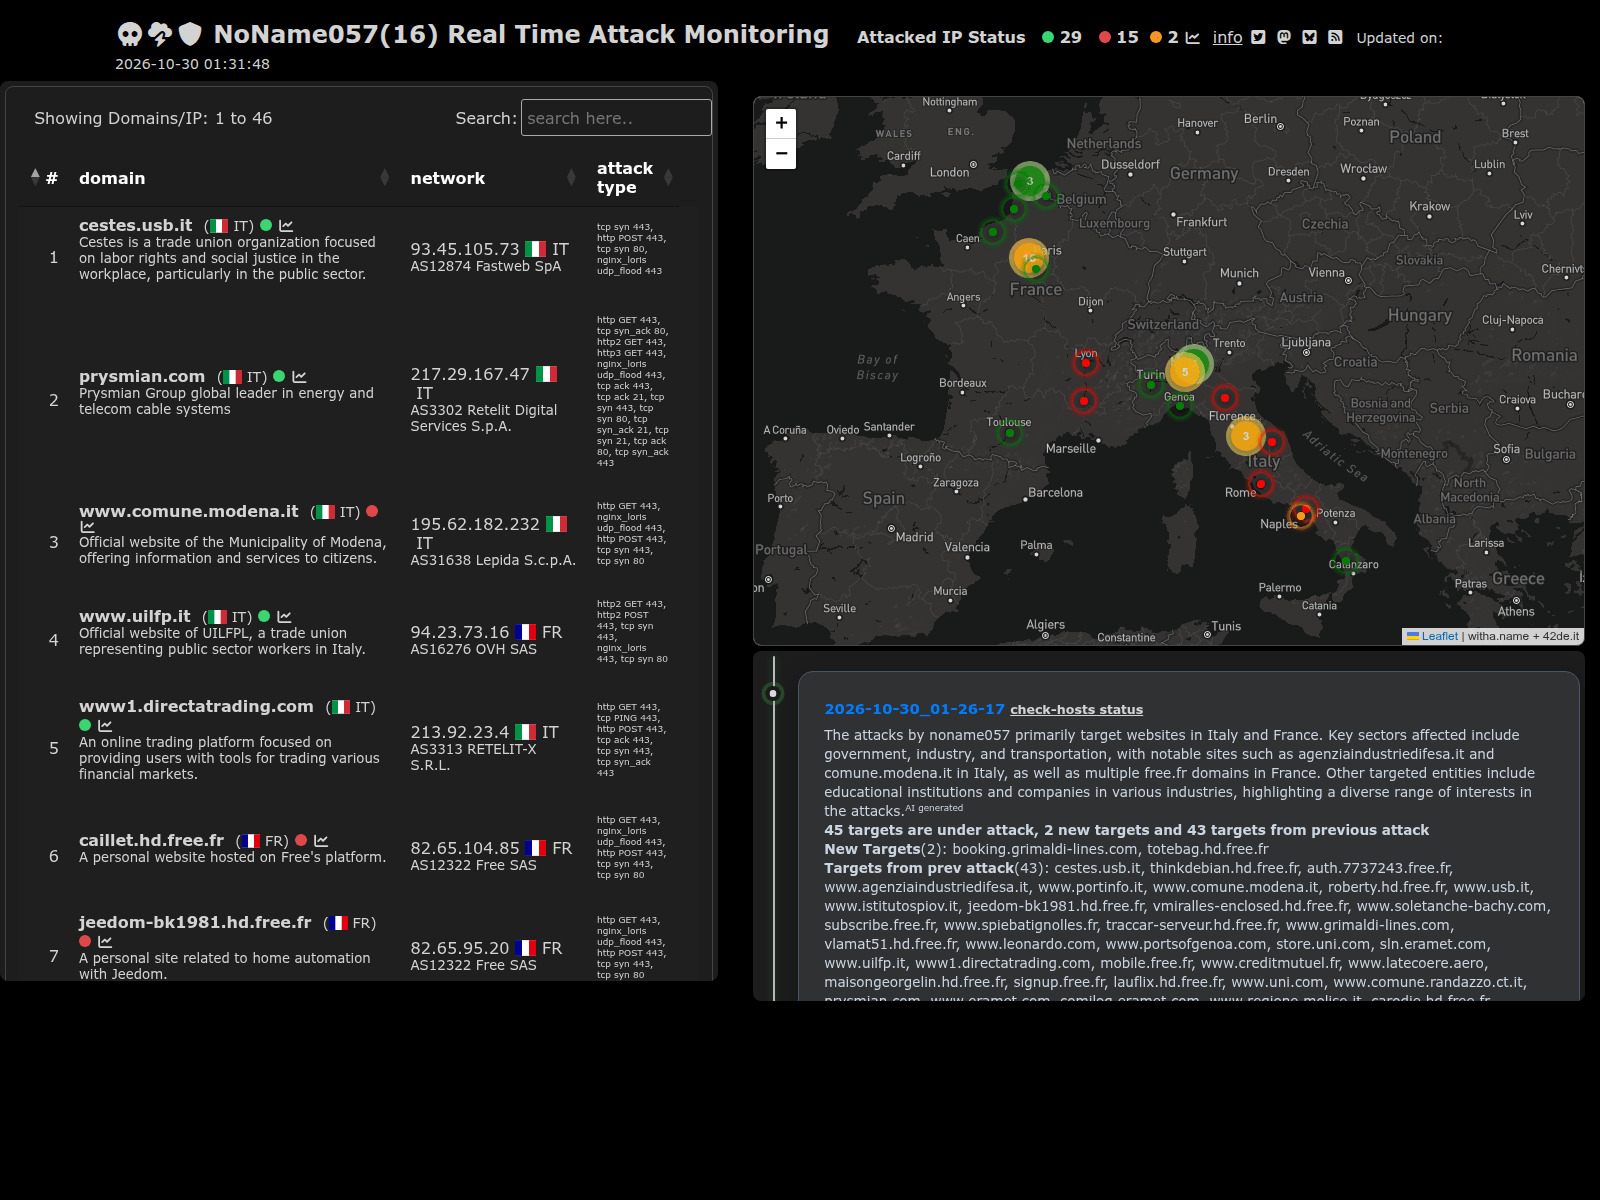
https:/42de.it NoName057(16) Real Time attack monitor
42DE42de - NoName057(16)Cyber Attack MonitoringPiattaforma di intelligence per il monitoraggio in tempo reale degli attacchi del threat actor Noname057(16). Mappe interattive, analisi dei target e statistiche aggiornate.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

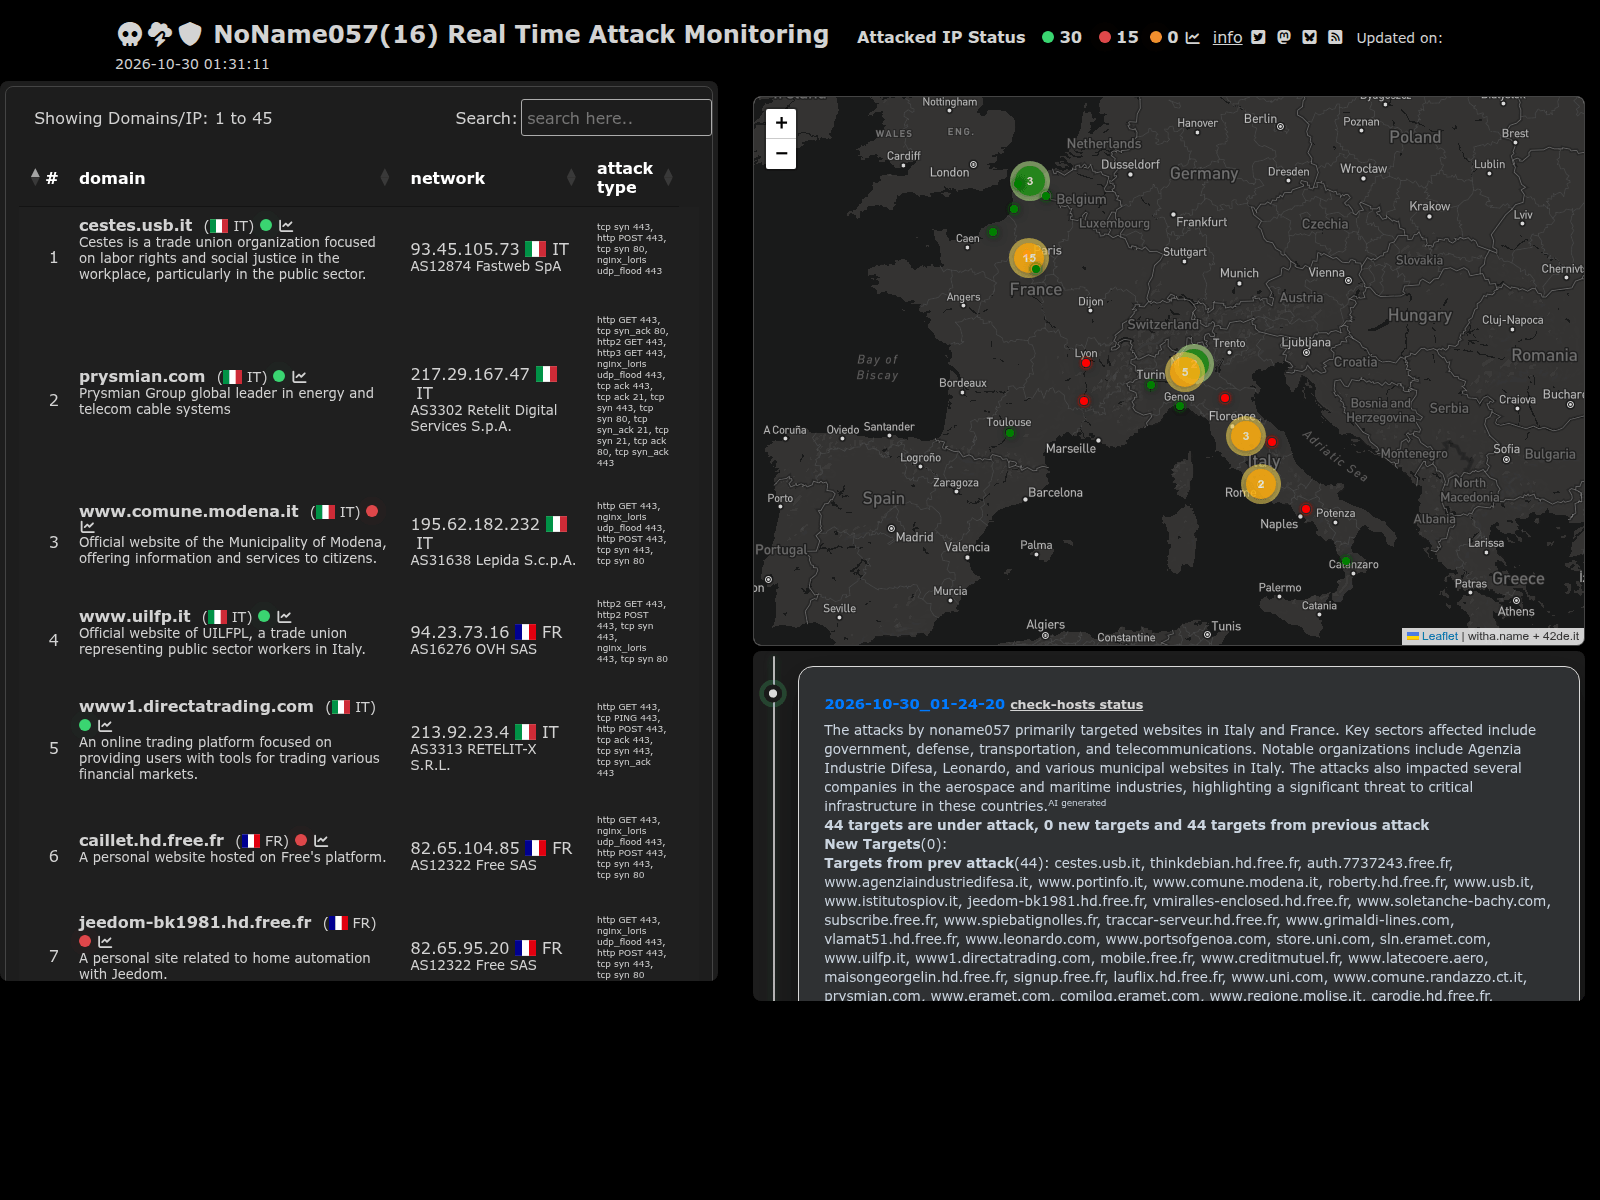
2026-10-30_01-24-20 #ddosia #noname057 The attacks by noname057 primarily targeted websites in Italy and France. Key sectors affected include government, defense, transportation, and telecommunications. Notable organizations include Agenzia Industrie Difesa, Leonardo, and various municipal websites in Italy. The attacks also impacted several companies in the aerospace and maritime industries, highlighting a significant threat to critical infrastructure in these countries. check on:https://42d...
https:/42de.it NoName057(16) Real Time attack monitor
↩ Reply ♡ 0 · ↻ 0 ↗ Original

What a User Story Actually Costs in a Dark Code Factory

Autonomous SDLC framework test (Mar-Jul 2026) reveals critical insights: v1 lacked data tracking; v2 improved cost monitoring. 595.7M tokens delivered 77 stories (~$10.88 each). Cache reads = 95.4% of usage. 13% rework rate signals quality issues. Monthly subscriptions beat usage pricing for now, but future rate changes threaten smaller firms. Better measurement systems needed.

https://www.oreilly.com/radar/what-a-user-story-actually-costs-in-a-dark-code-factory/

#OpenStack #CloudComputing #InfoSec

O’Reilly MediaWhat a User Story Actually Costs in a Dark Code FactoryBetween March and July 2026, I built a production application of 861,601 lines of code. This included 696 user stories and 779 merged pull requests over 105
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Volexity documented attackers chaining Ivanti Connect Secure auth bypass/RCE (CVE-2026-104935) with privilege escalation (CVE-2026-111357) to gain root. CISA added 104935 to KEV Oct. 13, not 111357.

For admins: review Ivanti updates and investigate affected gateways. Patching can't rule out earlier compromise.

https://www.volexity.com/blog/2026/10/13/a-series-of-unauthenticated-events-chained-exploitation-of-ivanti-connect-secure-zero-days/

#Cybersecurity #Infosec #MSP #VPN

VolexityA Series of Unauthenticated Events: Chained Exploitation of Ivanti Connect Secure Zero-DaysVolexity has identified active in-the-wild exploitation of a vulnerability chain allowing unauthenticated remote code execution in Ivanti Connect Secure VPN devices. Ivanti has published an advisory providing upgrade instructions to customers. Systems exhibiting signs of compromise, such as attempts to move laterally originating from the ICS VPN device, should be forensically investigated to ensur
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🐧 SIGINT // Linux Watch — 2026-10-30

A 9.8 CVSS use-after-free in kernel TCP, reportedly exploited for root on MPTCP servers, and Ubuntu and RHEL don't have fixes yet. Check whether MPTCP is enabled and disable it if you don't need it, until patches land.

🔗 https://thehackernews.com/2026/10/linux-kernel-tcp-flaw-with-98-cvss.html

#Linux #OpenSource #FOSS

The Hacker NewsLinux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other DistributionsUbuntu and RHEL lack fixes for a Linux TCP use-after-free that Anthropic says it exploited to run commands as root on MPTCP servers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

"Vivek Ramaswamy Pulls His Disturbing Ad After ‘Our Numbers Cratered’"

Ramaswamy and his allies were bombarded with complaints from Republicans over his sleazy ‘rapist protector mom’ ad, sources tell Zeteo.
https://zeteo.com/p/vivek-ramaswamy-pulls-his-disturbing-ad

zeteo.comVivek Ramaswamy Pulls His Disturbing Ad After ‘Our Numbers Cratered’Ramaswamy and his allies were bombarded with complaints from Republicans over his sleazy ‘rapist protector mom’ ad, sources tell Zeteo.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

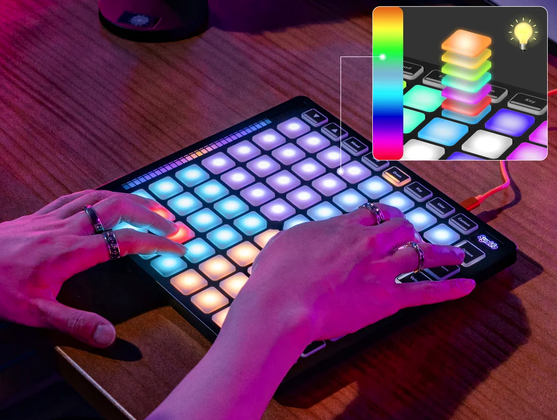
My girlfriend and I do a live whatnot show selling sterling jewelry every week. We've been just streaming over her iPhone. But I'm setting up OBS on her laptop, so we'll be able to do picture-in-picture with DroidCam. Also, our background music, currently provided by a Bose speaker, will now be an OBS audio source. Plus, I made a cool #Perl Windows program to trigger cartoon sound effect audio samples with my 64-pad MIDI controller. Haha! :D

https://github.com/ology/Music/blob/master/audio-trigger.pl

A marketing image for the Synido TempoPAD Z-1
GitHubMusic/audio-trigger.pl at master · ology/MusicTheory, Algorithmic composition, Experimentation. Contribute to ology/Music development by creating an account on GitHub.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
A

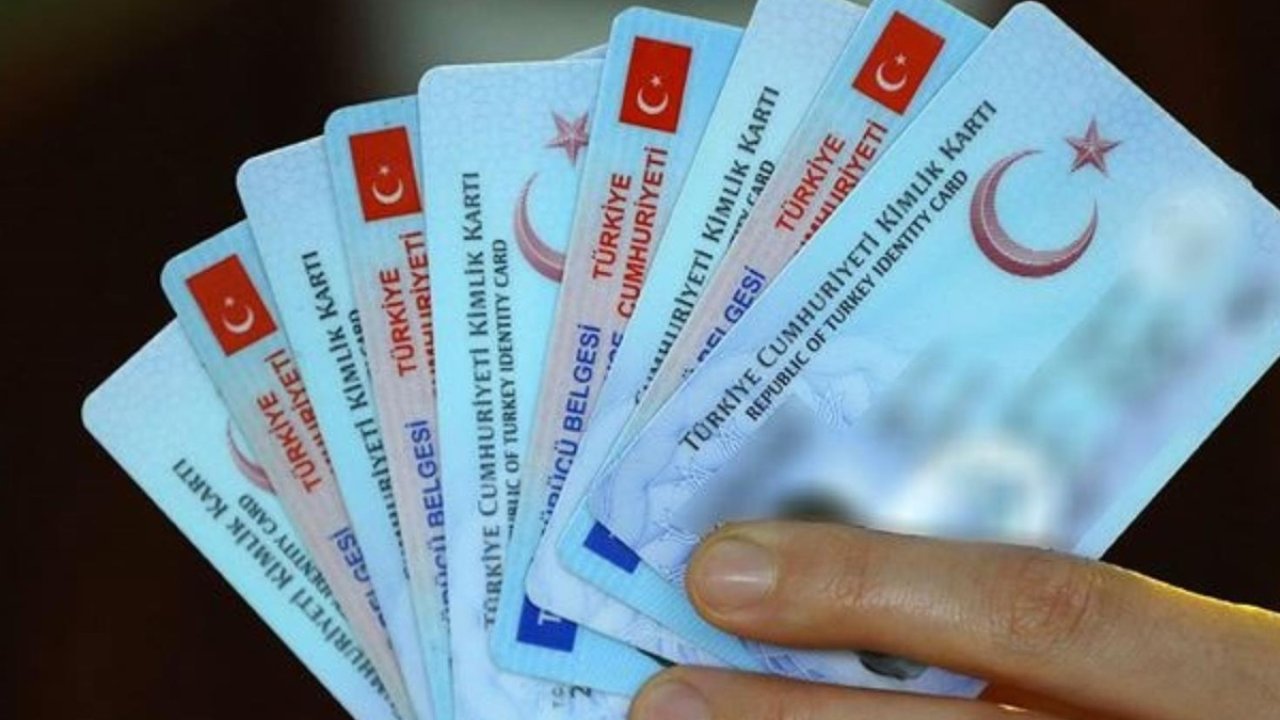
Bazı soyadları sahiplerine hayatı zorlaştırıyor: Değiştirmek için mahkemeye koşuyorlar
https://abcgazetesi.com.tr/yasam/bazi-soyadlari-sahiplerine-hayati-zorlastiriyor-degistirmek-icin-mahkemeye-kosuyorl-875849?_unique_id=6ae3e4e6c4781

ABC HaberBazı soyadları sahiplerine hayatı zorlaştırıyor: Değiştirmek için mahkemeye koşuyorlarTürkiye'de olumsuz anlam taşıyan veya günlük yaşamda yanlış anlaşılmalara yol açan bazı soyadlarını değiştirmek isteyen vatandaşların başvuruları dikkat ..
↩ Reply ♡ 0 · ↻ 0 ↗ Original

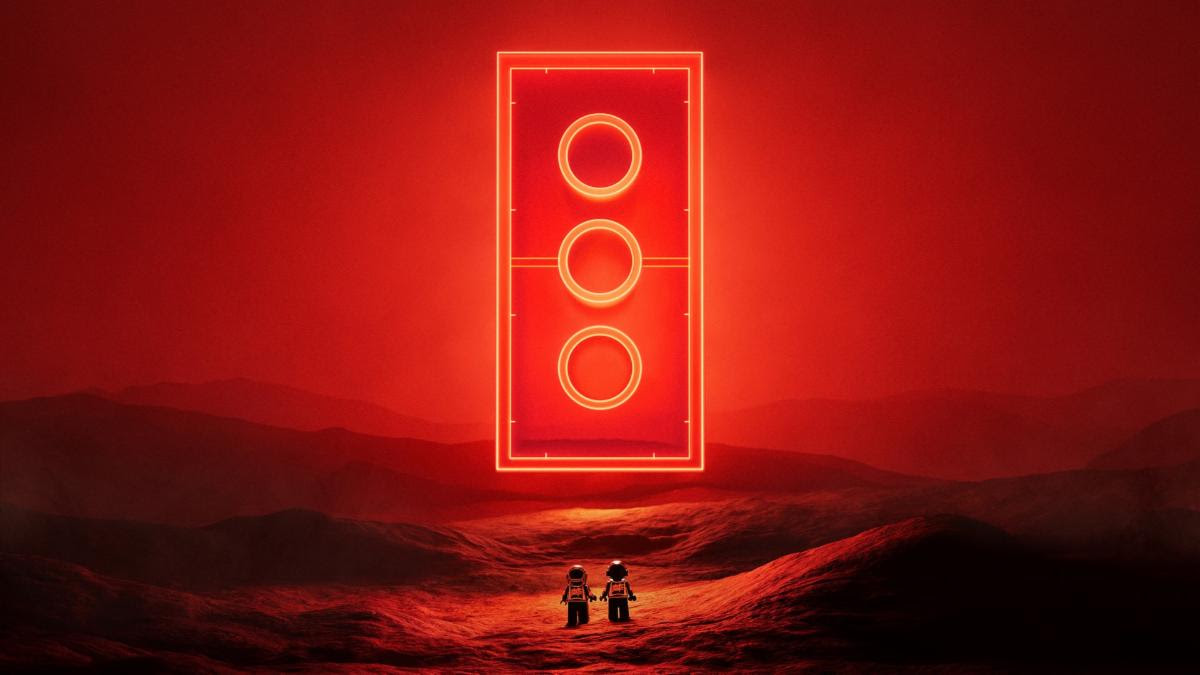
Daft Punk’s Iconic Pyramid Stage Is Becoming A LEGO Set
https://stereogum.com/2515329/daft-punks-iconic-pyramid-stage-is-becoming-a-lego-set/news/
#DaftPunk #LEGO #Stereogum

stereogum.comDaft Punk's Iconic Pyramid Stage Is Becoming A LEGO SetIf you’re looking for proof that adults comprise a significant portion of LEGO’s customer base, here it is. Daft Punk have announced a partnership with the building block brand that will span “product, content, and brand experiences.” Despite the corporate language accompanying the announcement, the partnership arose organically. It started when Luxembourg’s Patrick Harboun and…
↩ Reply ♡ 0 · ↻ 0 ↗ Original
R

"We want the UK Government to launch an inquiry into any British involvement in Israeli operations in Gaza, including the sale, supply or use of weapons, surveillance aircraft and Royal Air Force bases…

…which would have the power to question government ministers and officials involved in decision-making processes…what arms…what RAF bases…and why; what intelligence was collected…what legal advice has the UK Government sought…"

https://petition.parliament.uk/petitions/783252

#Gaza #Israel #Palestine #UKgov

Petitions - UK Parliament and UK GovernmentPetition: Launch a public inquiry into the UK's role in Israeli operations in GazaWe want the UK Government to launch an inquiry into any British involvement in Israeli operations in Gaza, including the sale, supply or use of weapons, surveillance aircraft and Royal Air Force bases. We believe the UK has played a vital role in Israeli military operations in Gaza.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Pluto Security found 31 malicious Hugging Face model repos delivering miners and backdoors through trust_remote_code=True. Some payloads scanned clean, and code ran before the model loaded.

For admins using local AI/GPU hosts: review custom model Python, pin revisions, isolate workloads and hunt for persistence if a model ran. 32K+ downloads aren't confirmed infections.

https://pluto.security/blog/hugging-face-malware-campaign-load-mine/

#Cybersecurity #Infosec #AISecurity #SysAdmin

Pluto SecurityHugging Face Malware Campaign: Load/Mine | Pluto SecurityPluto Research traces a Hugging Face cryptomining and backdoor campaign, its return after takedown, and indicators for investigating potential exposure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Replacements (with Soul Asylum closing) Live at Cabaret Metro on 1985-08-22 https://archive.org/details/ajc04136_thereplacementswithsoulasylum_1985-08-22

Internet ArchiveThe Replacements (with Soul Asylum closing) Live at Cabaret Metro on 1985-08-22 : The Replacements (with Soul Asylum closing) : Free Download, Borrow, and Streaming : Internet ArchThe Replacements (with Soul Asylum closing) - Cabaret Metro - 1985-08-22 - Sony WM-R2 (Internal Mics) > Cassette (M)
↩ Reply ♡ 0 · ↻ 0 ↗ Original

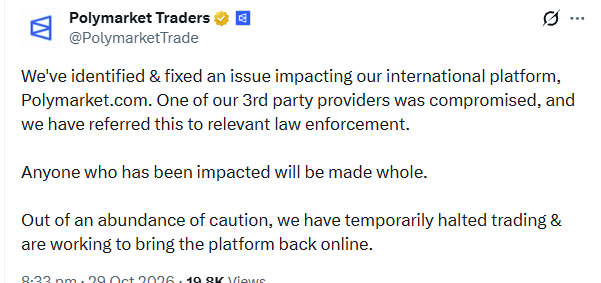
Polymarket paused trading Oct. 29 after a vendor compromise. Hudson Rock found wallet-draining code in a monitoring script. DebugBear told RUM users to remove its embed.

For admins: audit third-party JS on authenticated pages, remove unneeded embeds and review CSP/SRI. Initial access and total losses remain unverified.

https://www.infostealers.com/article/polymarket-breach-alert-wallet-draining-code-found-in-a-third-party-script/

#Cybersecurity #Infosec #WebSecurity #SupplyChainSecurity

InfoStealersPolymarket Breach Alert: Wallet-Draining Code Found in a Third-Party ScriptA script associated with performance monitoring contains code to access trading sessions, sell positions, and redirect assets. Polymarket’s own production build records the integration’s removal.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://hachyderm.io/@molly0xfff/117526961419935070

#craptocurrency #fafo

❞ Quoted postMolly White

I wrote up what we know about the Binance hack so far. By my best estimate, Binance is out $1.5–$3 billion after stablecoin issuers froze what they could. Changpeng Zhao is promising Binance will cover it, but he’s legally barred from running the company. https://www.citationneed

Hachyderm.ioMolly White (@[email protected])I wrote up what we know about the Binance hack so far. By my best estimate, Binance is out $1.5–$3 billion after stablecoin issuers froze what they could. Changpeng Zhao is promising Binance will cover it, but he’s legally barred from running the company. https://www.citationneeded.news/binance-theft/ #binance #crypto #cryptocurrency
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Honda dealers in the U.S. reported regaining access to the Interactive Network after a two-day interruption that disrupted financing, parts and repairs. The outage also affected Acura dealers and Honda powersports operations.

Honda says it took the portal offline as a precaution while investigating a cybersecurity incident; dealers had been unable to submit credit applications, check recall information or order parts. Full service recovery remains unconfirmed, and Honda says it found no evidence that customer information was accessed while its investigation remains open.

#Honda #AutoDealers #ServiceDisruption #IncidentResponse #Acura #Powersports #Cybersecurity

https://dysruptionhub.com/honda-cyber-incident-dealer-operations/

DysruptionHubHonda dealers face financing and repair delays after cyber incidentHonda's dealer portal shutdown disrupted financing, parts and repairs. Dealers reported restored access, but complete recovery remains unclear.
↩ Reply ♡ 0 · ↻ 0 ↗ Original