🚨🇺🇸 Railway says breach potentially exposed secrets in around 100,000 workspaces
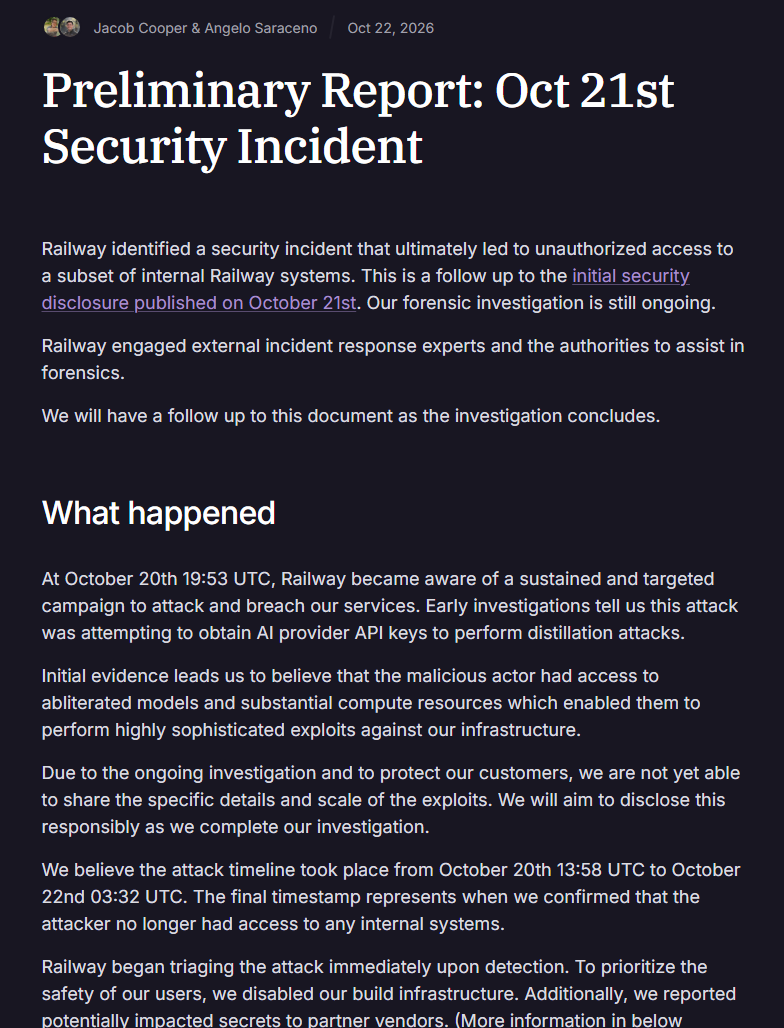
Cloud development platform Railway says an attacker gained access to internal systems and potentially exposed encrypted environment variables belonging to up to 1.85% of its workspaces, or roughly 100,000.
⠀
Some variables were decrypted using compromised credentials. These may have contained API keys, database credentials, private registry credentials and other sensitive information.
Railway believes the attacker was searching for AI provider API keys to conduct model distillation attacks.
⠀
The attack occurred between October 20 and October 22. Railway temporarily stopped new builds and deployments while responding, although existing customer applications remained online.
Railway says individual user accounts were not accessed, but it has not ruled out possible access to source code while its investigation continues.
⠀
All customers who stored credentials on Railway before October 21 should rotate them and review connected services for suspicious activity.
Railway has also invalidated access tokens, rotated internal credentials and worked with providers including GitHub, GitLab, OpenAI, Anthropic and Stripe to revoke potentially exposed keys.
Source:
https://blog.railway.com/p/preliminary-report-october-security-incident
 Railway BlogPreliminary Report: Oct 21st Security Incident | Railway BlogPreliminary report detailing Railway's October 21st security incident.