
Unit 42 found BUGSTER using jailbroken DeepSeek and Hermes to steal 5,200+ university records and build tooling for VoIP fraud, Wi-Fi cracking and C2. https://unit42.paloaltonetworks.com/ai-assisted-cybercrime-analysis/
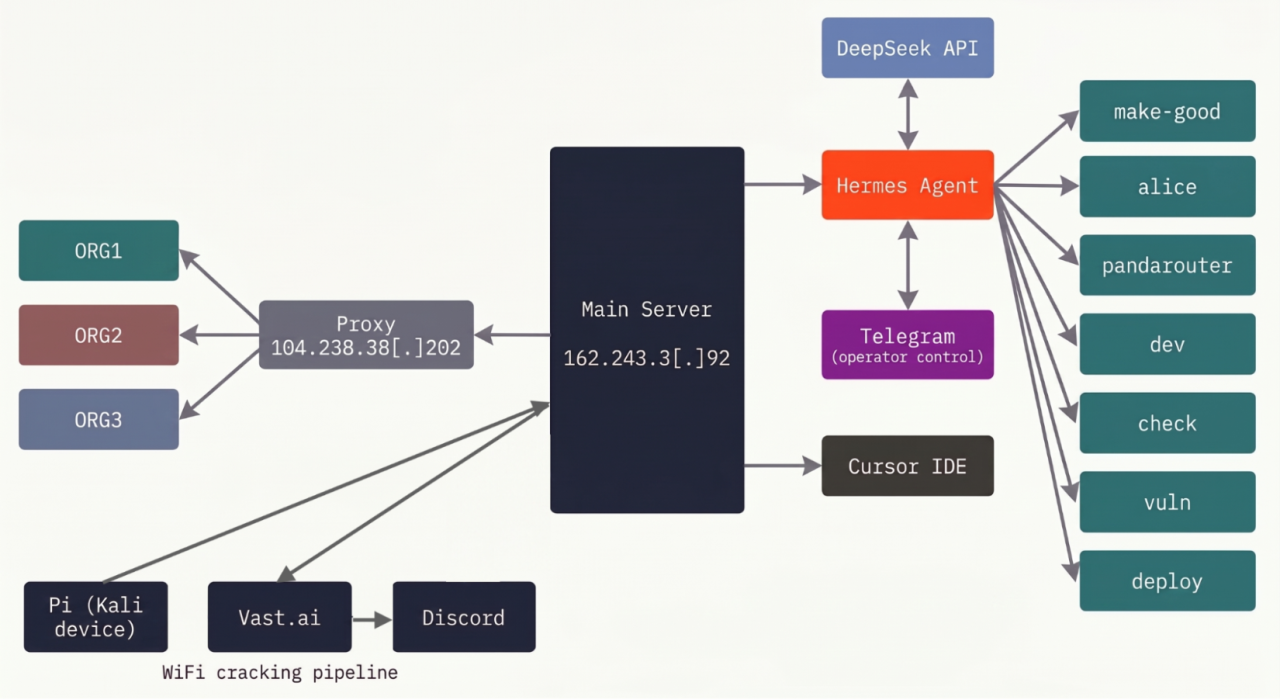
 Unit 42“Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime ActivitiesAn investigation into a threat actor bypassing AI safety controls to coordinate credential theft, VoIP fraud planning, and database exfiltration.