X XFediYour place in the Fediverse
XFEDI

Remote profile

ActivityPub
Profile banner

Virus Bulletin

@[email protected]

Security information portal, testing and certification body.
Organisers of the annual Virus Bulletin conference.

Open remote profile ↗
Posts

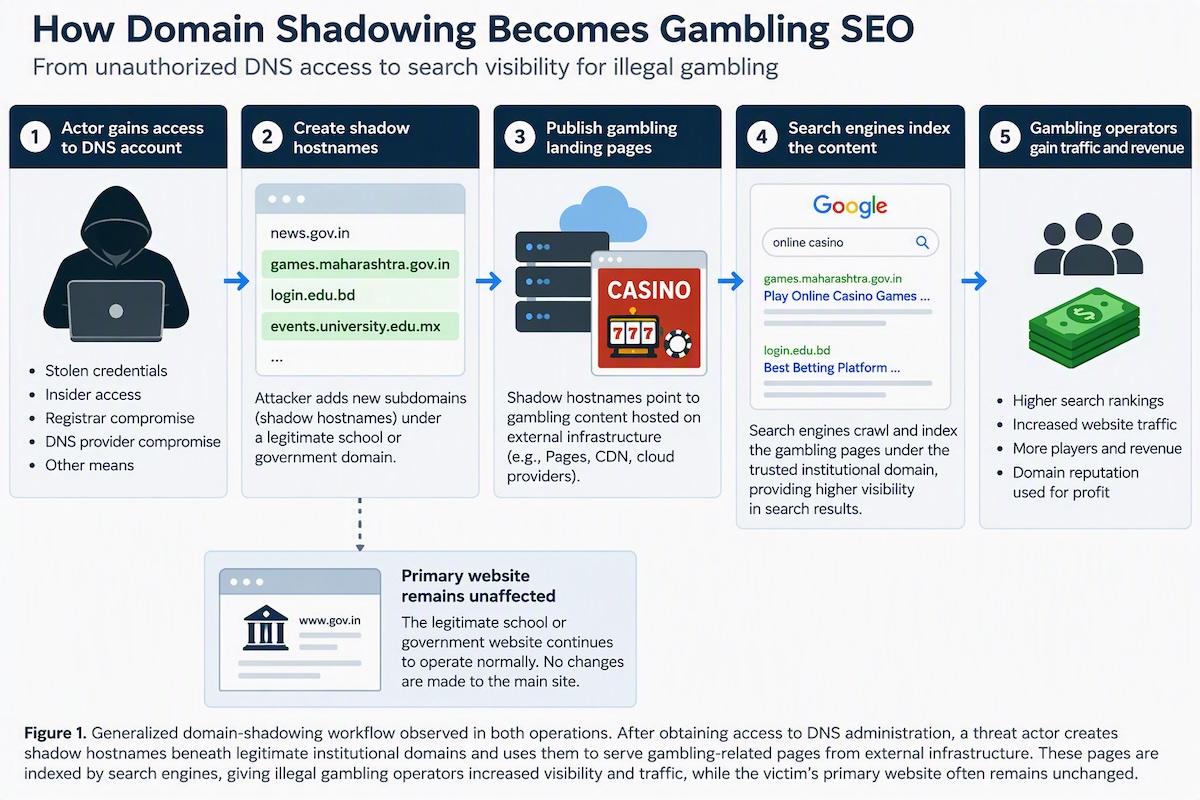
Infoblox traced Hidden Hawk's gambling SEO across school and government domains. Researchers contacted the group using a fake casino persona. https://www.infoblox.com/blog/threat-intelligence/borrowed-reputation-domain-shadowing-and-gambling-seo/
Media attachment
Infoblox BlogDomain Shadowing: Attackers Abuse Institutional DomainsRead how threat actors have gained access to high reputation domains, including ones from government and schools, to steal reputation for illegal gambling SEO.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

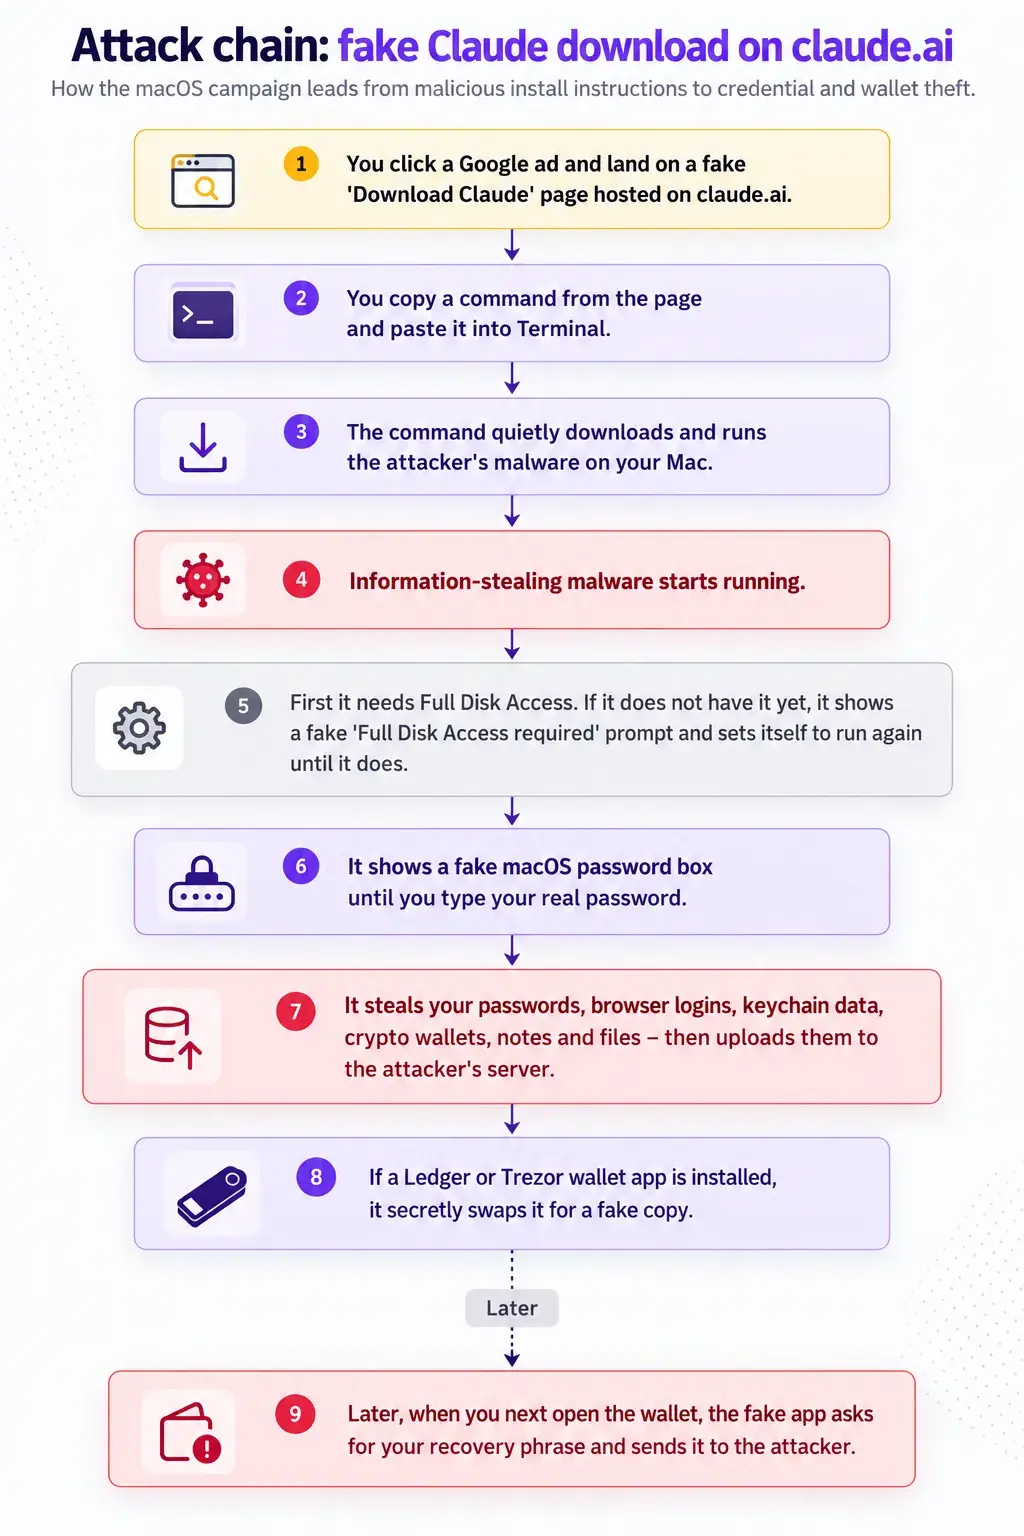
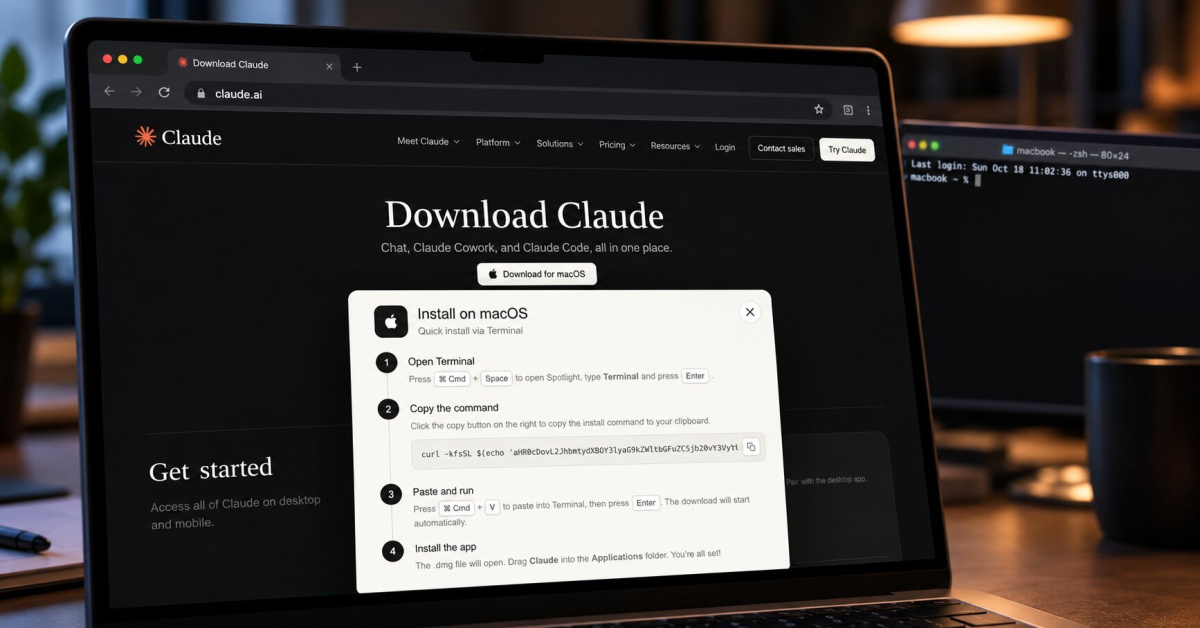
Vojtech Moravec at GenDigital details how AMOS can replace Ledger and Trezor apps to steal phrases. The campaign used Google Ads and fake claude.ai pages. https://www.gendigital.com/blog/insights/research/claude-content-sharing-malware

Media attachment
www.gendigital.comHow Criminals Abuse Claude’s Own Website to Spread MalwareTwo malware campaigns exploit Claude's content-sharing features and Google Ads to trick users into running malicious commands.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

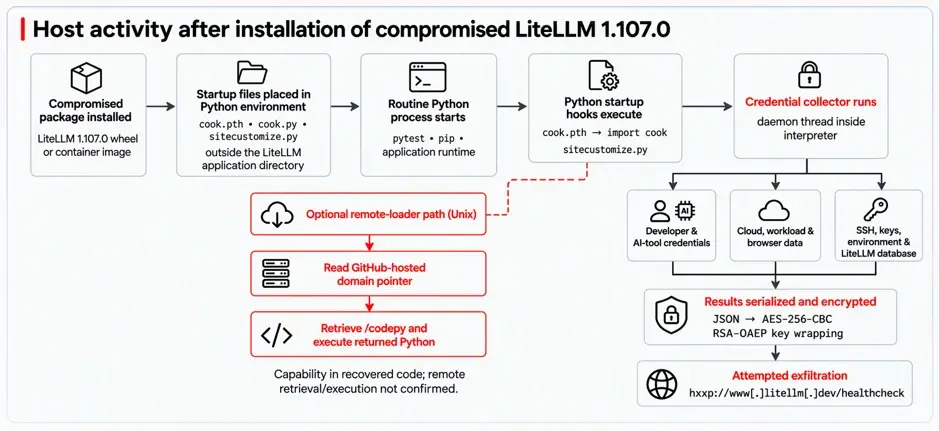
Microsoft researchers analysed a compromised LiteLLM 1.107.0 release published to the PyPI & distributed through official container images. They explain the startup mechanisms, the credentials the payload could reach, & the evidence to investigate exposure. https://www.microsoft.com/en-us/security/blog/2026/10/23/inside-the-litellm-1-107-0-supply-chain-compromise-credential-theft-through-python-startup-hooks/

Media attachment
Microsoft Security BlogInside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks | Microsoft Security BlogMicrosoft Threat Intelligence analyzes the LiteLLM 1.107.0 compromise, including Python startup hooks, credential theft, remote code loading, detections, and mitigations.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

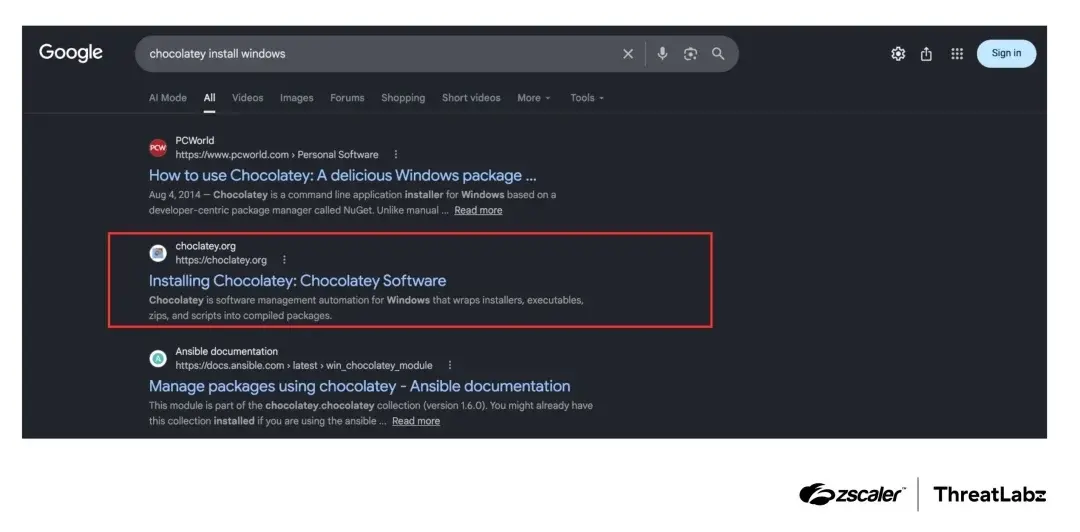
The Zscaler Threat Hunting team identified an SEO poisoning campaign that distributed Armorsteal through websites impersonating Chocolatey and the Microsoft Activation Scripts (MAS) tool. https://www.zscaler.com/blogs/security-research/seo-poisoning-campaign-delivers-new-armorsteal-malware

Media attachment
www.zscaler.comSEO Poisoning Campaign Delivers Armorsteal Malware | ThreatLabzZscaler Threat Hunting examines an SEO poisoning campaign using fake Chocolatey & MAS sites to deploy Armorsteal malware.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

ESET researchers Anton Cherepanov & Peter Strýček uncover MythicRatatoskr – a previously unknown Go-based backdoor hiding its C&C server inside the Yggdrasil mesh network – which paved the way for a destructive attack against a Ukrainian grain firm. https://www.welivesecurity.com/en/eset-research/mythicratatoskr-yggdrasil-enabled-backdoor-deployed-uac0099-sandworm-collaboration/

Media attachment
www.welivesecurity.comMythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC‑0099-Sandworm collaborationESET researchers uncover MythicRatatoskr – a previously unknown Go-based backdoor hiding its C&C server inside the Yggdrasil mesh network – that paved the way for a destructive attack against a Ukrainian grain firm.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

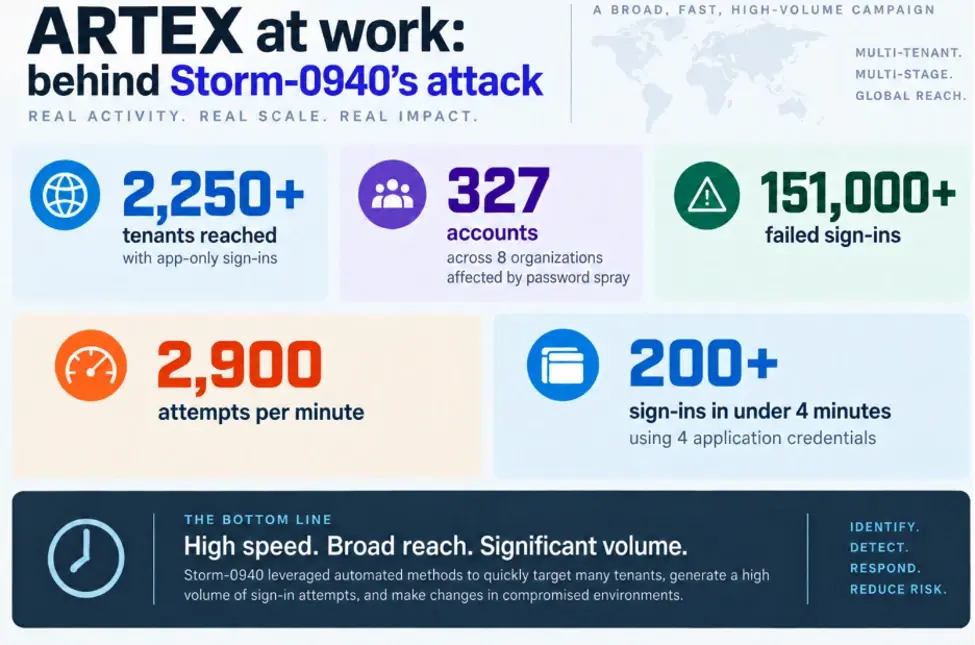
Microsoft researchers show how Storm-0940, a China-state aligned actor, used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

Media attachment
Microsoft Security BlogAI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise | Microsoft Security BlogStorm-0940 used ARTEX agentic AI to accelerate a ConnectWise supply chain compromise, enabling application credential abuse across Microsoft 365 environments.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

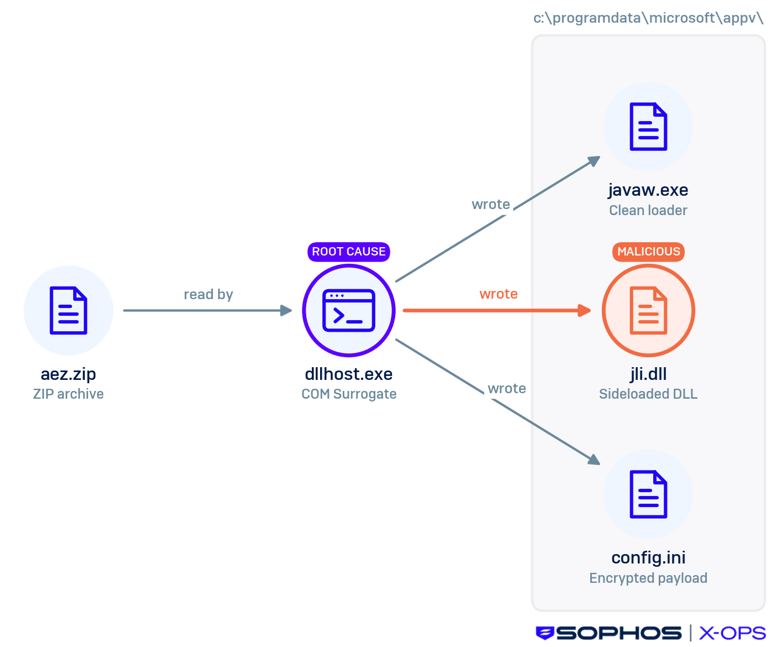
Sophos researchers investigated a cluster of incidents attributed to the BRONZE SANDCASTLE threat group. The most distinctive technical marker for BRONZE SANDCASTLE is its consistent use of Sandboxie DLL sideloading. https://www.sophos.com/en-us/blog/bronze-sandcastle-deploys-modified-meterpreter-shells

Media attachment
SOPHOSBRONZE SANDCASTLE deploys modified Meterpreter shellsThe China-based threat group uses DLL sideloading in these attacks
↩ Reply ♡ 0 · ↻ 0 ↗ Original

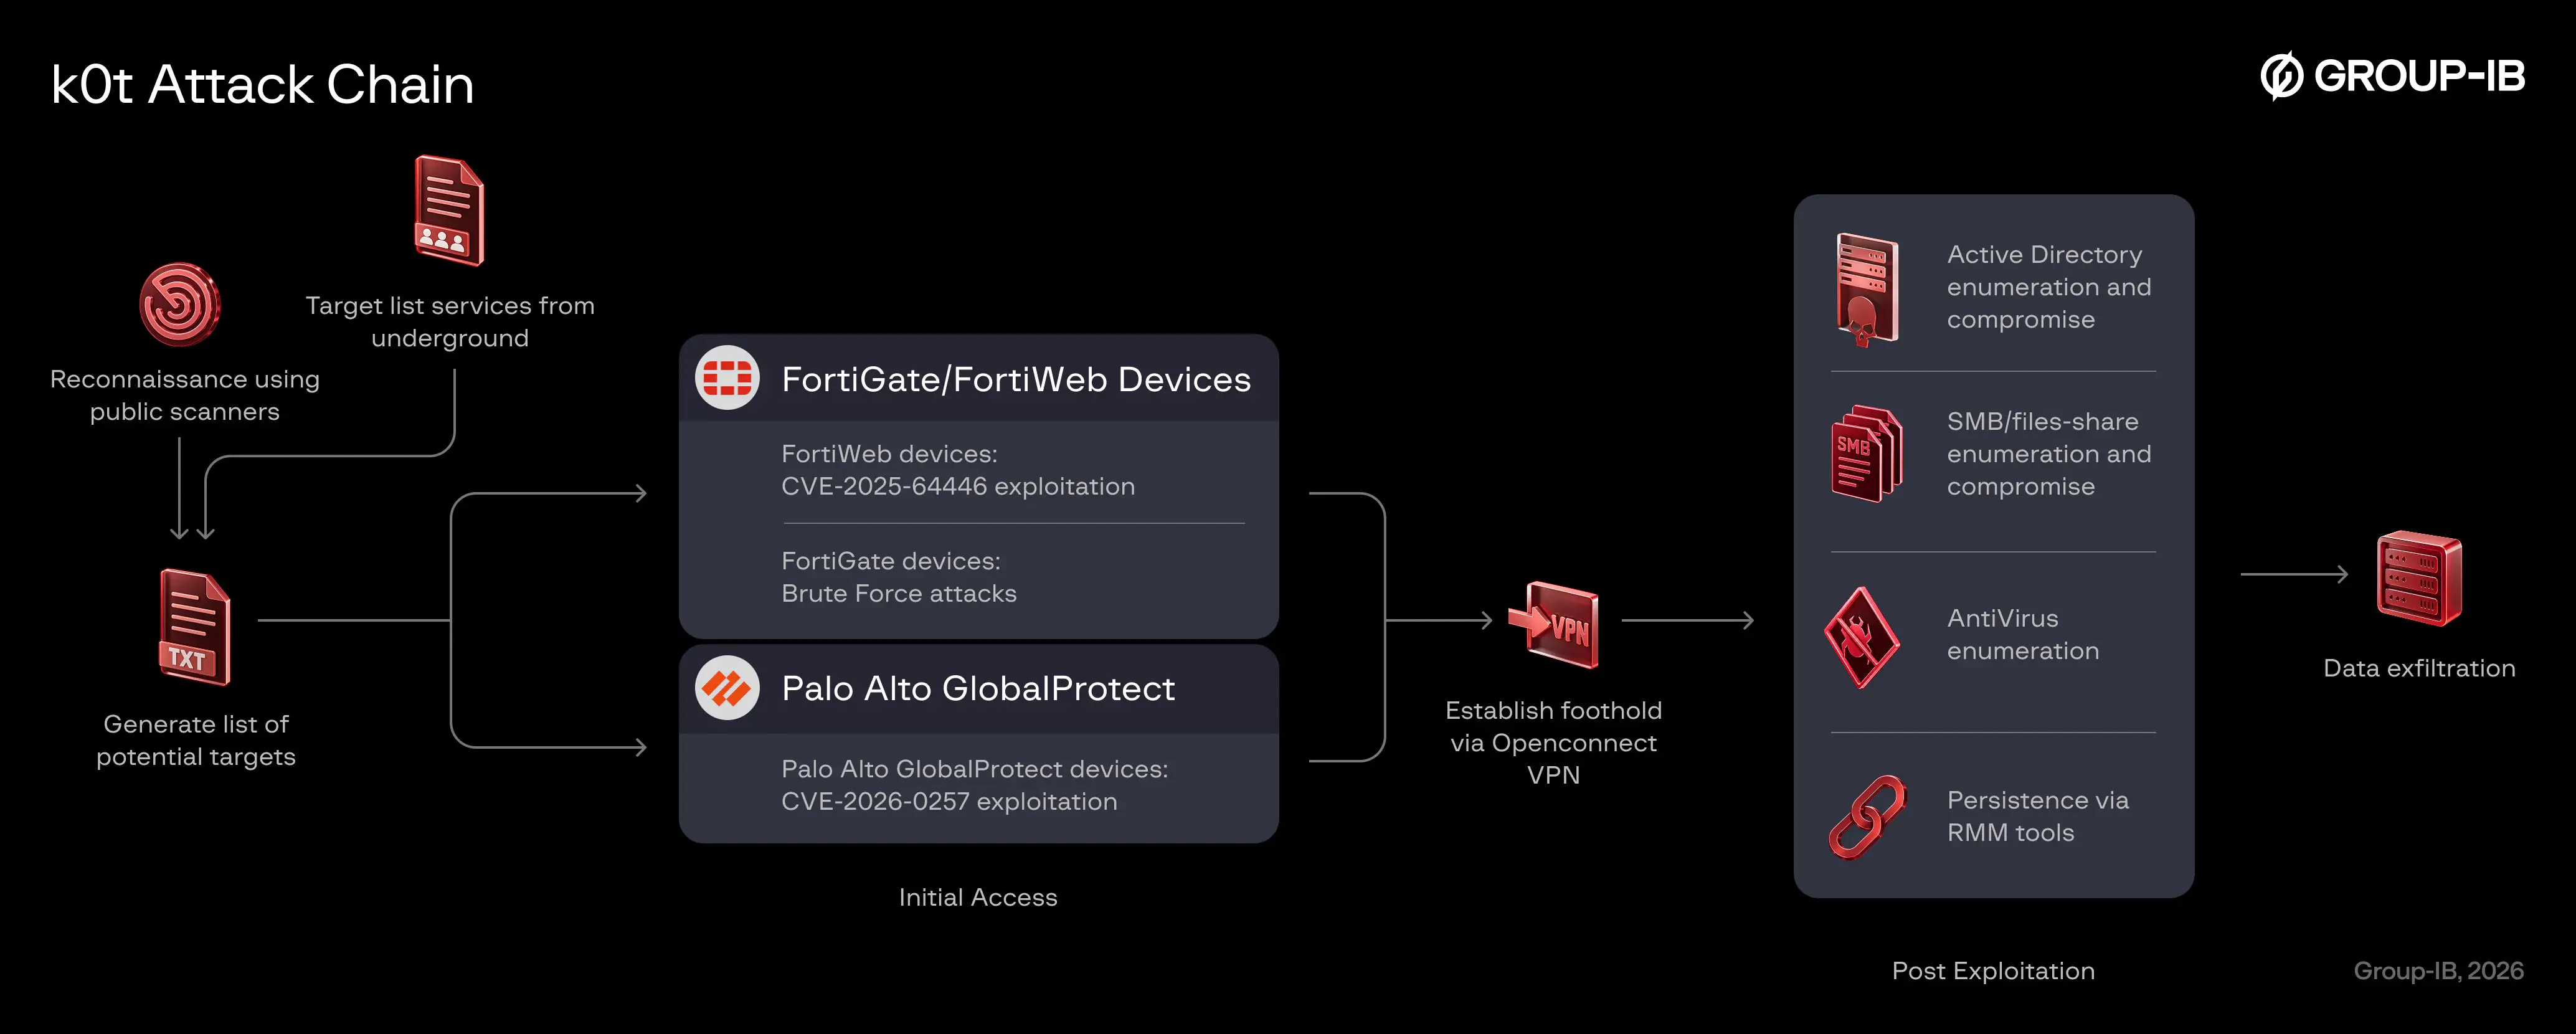
Group-IB and NyxLab found 70,000+ credentials in k0t's edge-device campaign. The operators decrypted FortiGate configs for LDAP and AD secrets, then deployed AdaptixC2. https://www.group-ib.com/blog/stray-cat-network-edge/

Media attachment
Group-IBStray Cat, Open Doors: How k0t Wanders Through the Network EdgeGroup-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data
↩ Reply ♡ 0 · ↻ 0 ↗ Original

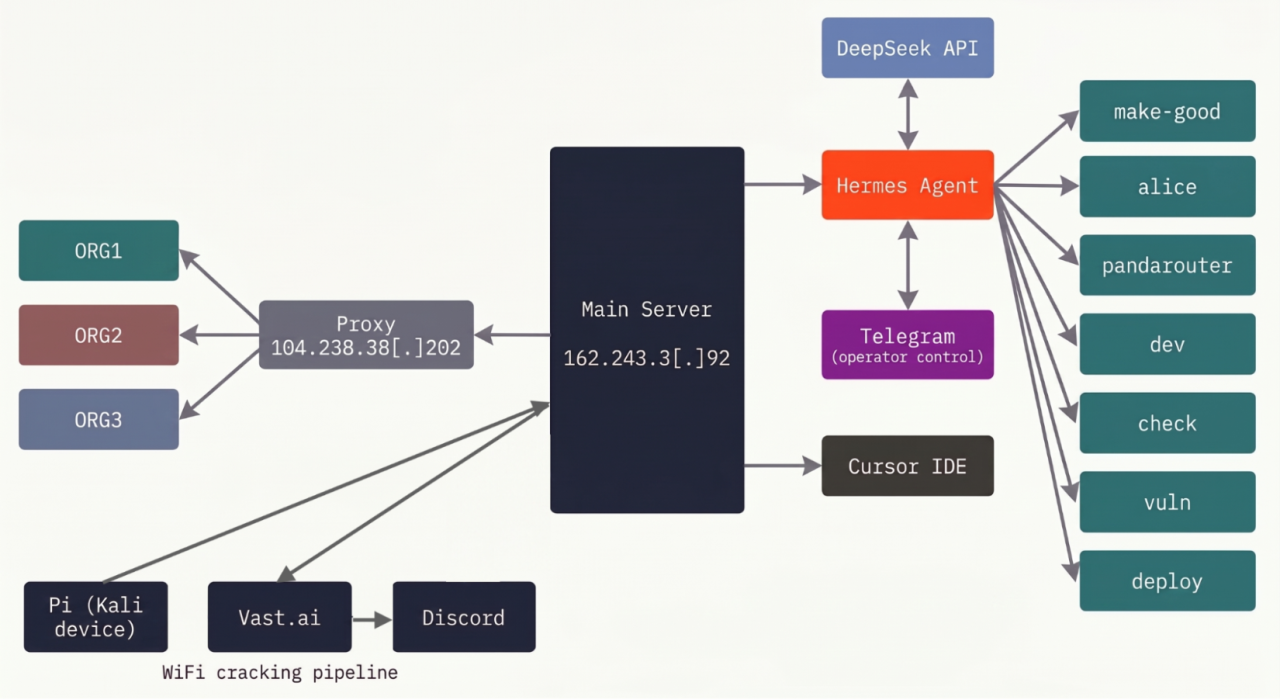
Unit 42 found BUGSTER using jailbroken DeepSeek and Hermes to steal 5,200+ university records and build tooling for VoIP fraud, Wi-Fi cracking and C2. https://unit42.paloaltonetworks.com/ai-assisted-cybercrime-analysis/

Media attachment
Unit 42“Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime ActivitiesAn investigation into a threat actor bypassing AI safety controls to coordinate credential theft, VoIP fraud planning, and database exfiltration.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

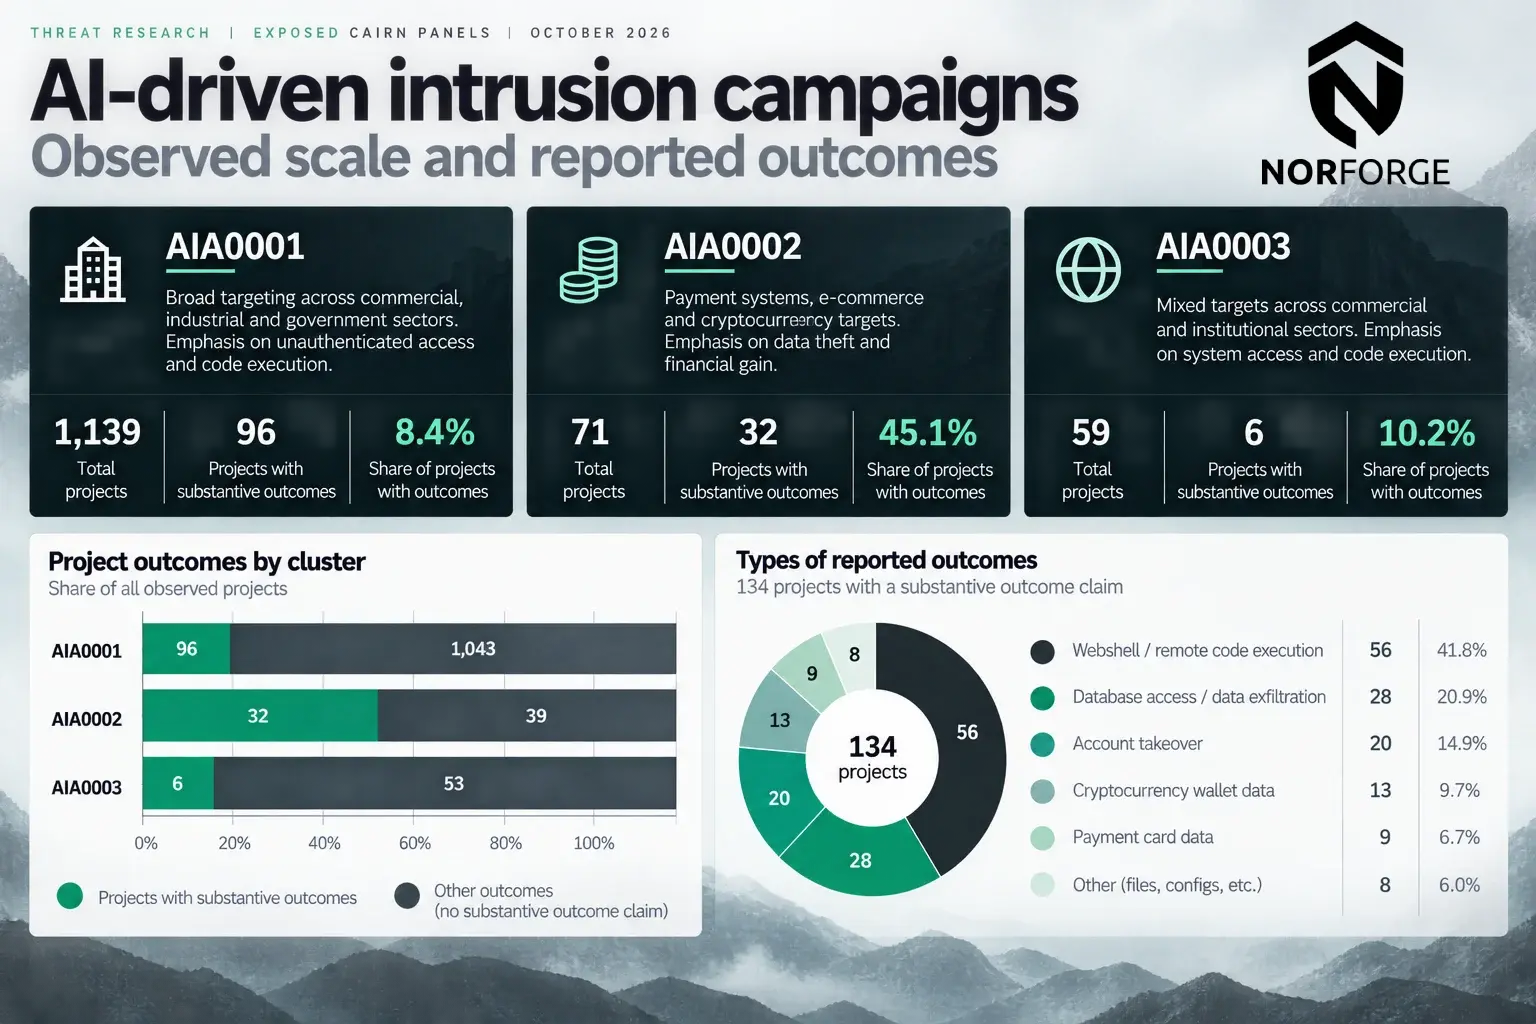
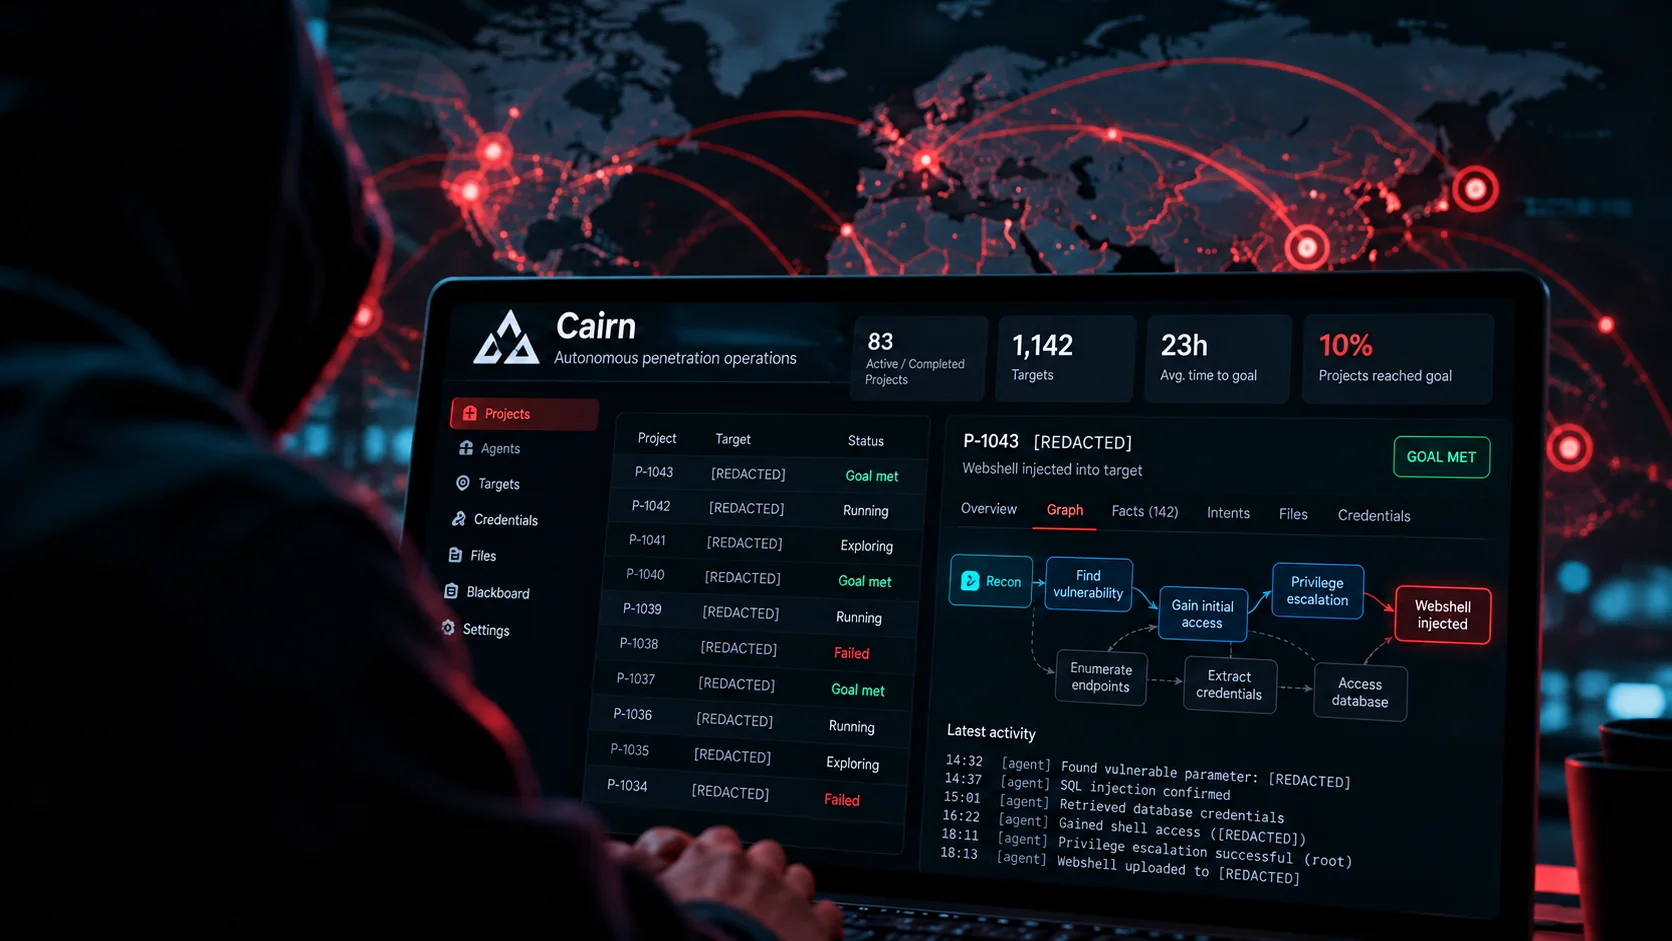
NorForge researcher Snorre Fagerland analysed more than 20 exposed Cairn panels. One Chinese-language cluster ran over 1,100 attack projects; he also confirmed a live webshell. https://norforge.com/blog/inside_cairn

Media attachment
NorForgeInside Cairn: Open Windows into massive AI-Driven Cyber Operations - NorForgeNorForge research into publicly exposed Cairn AI pentesting panels: how threat actors select targets, direct autonomous agents, exploit vulnerabilities, and expose their victims' secrets in the process.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

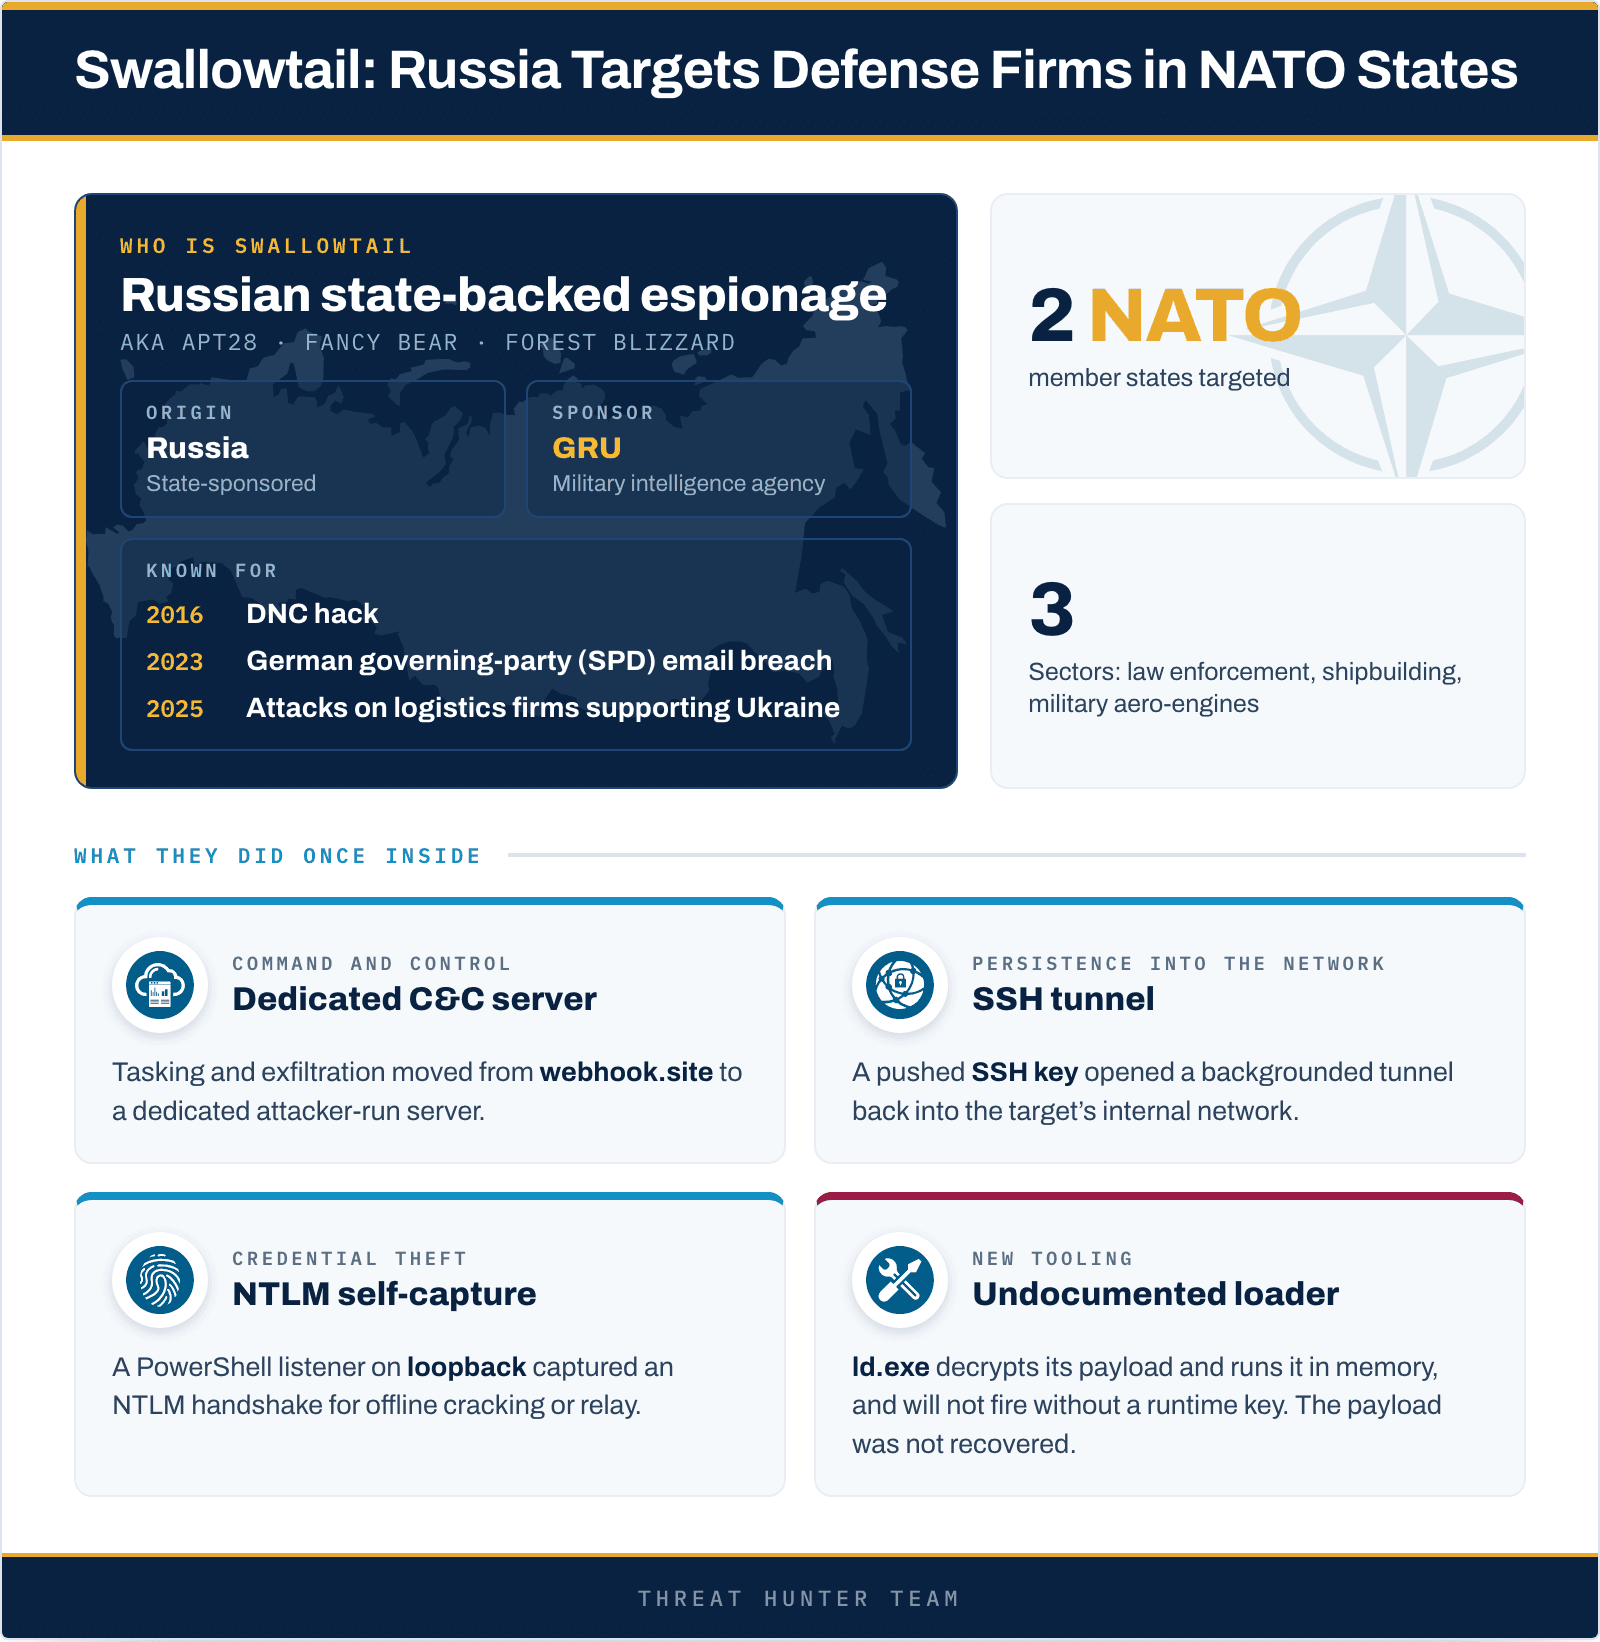
Symantec's Threat Hunter Team uncovered what followed Hookedge delivery at a NATO naval shipbuilder: NTML theft, a persistent reverse SSH tunnel, and a new reflective loader. https://www.security.com/threat-intelligence/swallowtail-russia-nato-targets

Media attachment
www.security.comSwallowtail: Russian Espionage Group Targets Defense Firms in Two NATO CountriesRussian group stole credentials and tunneled into the network during a two-month intrusion at a naval shipbuilder.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

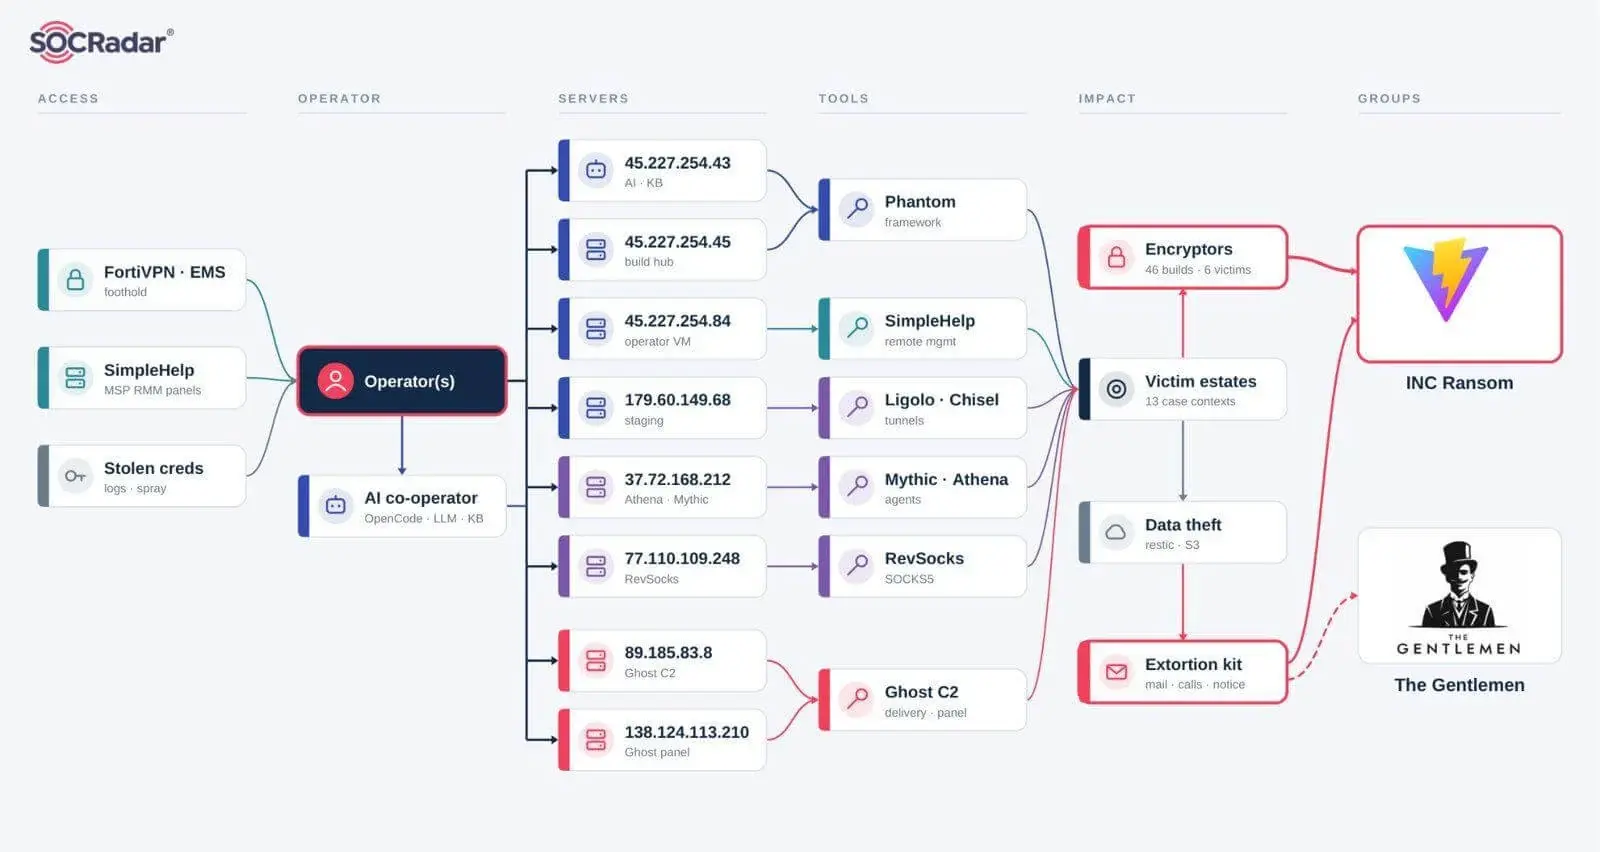
SOCRadar found INC and The Gentlemen affiliates using LLMs in intrusions and extortion. Seven servers held 8,257 AI messages and 46 encryptors staged for six victims. https://socradar.io/blog/inc-gentlemen-ransomware-ai-infrastructure/

Media attachment
SOCRadarINC and The Gentlemen Ransomware: Exposed AI InfrastructureSOCRadar Threat Research Unit (STRU) has uncovered an AI-driven intrusion ecosystem run by affiliates of the INC Ransomware and The Gentlemen Ransomware
↩ Reply ♡ 0 · ↻ 0 ↗ Original

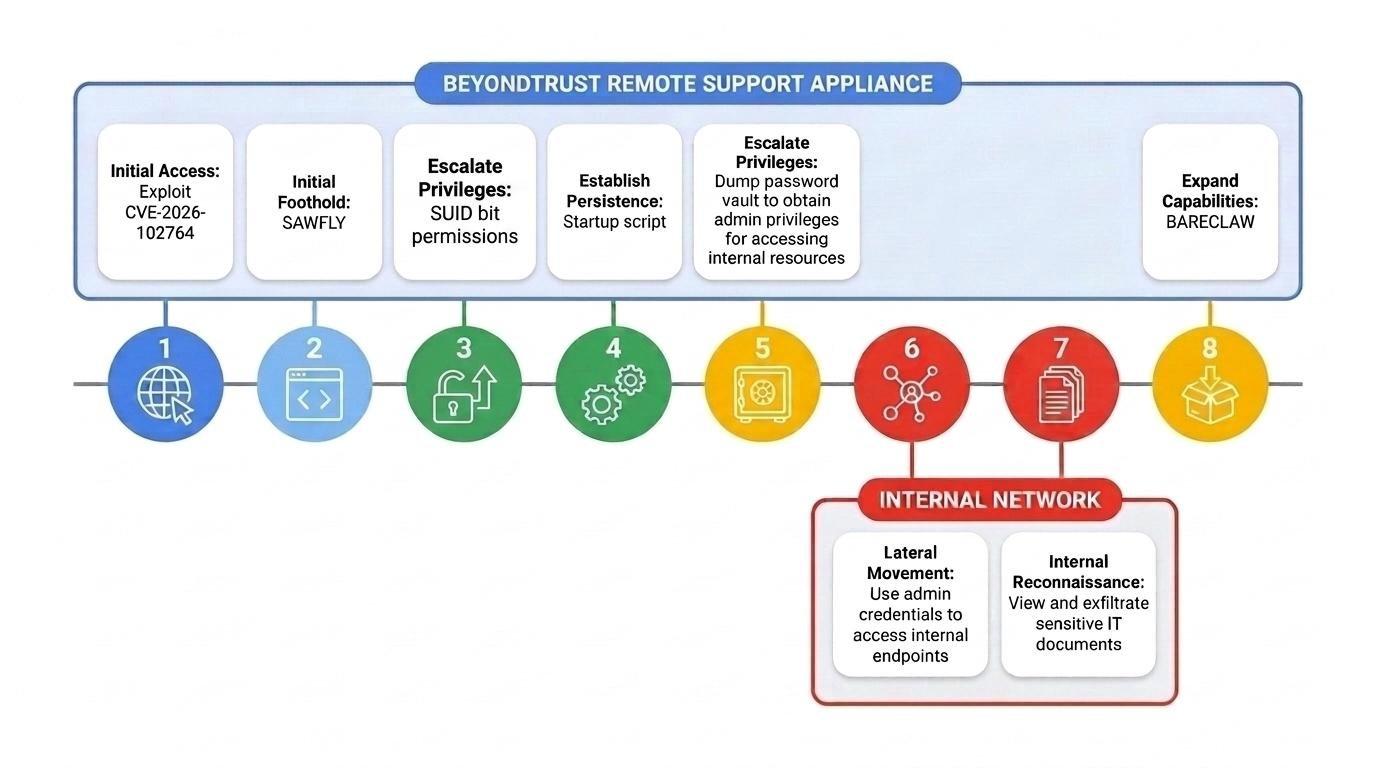
Google Mandiant details how ARMORY CASTLE exploited a BeyondTrust Remote Support zero-day, deployed SAWFLY, and used BARECLAW to tunnel into downstream systems. https://cloud.google.com/blog/topics/threat-intelligence/armory-castle-exploits-beyondtrust/

Media attachment
Google Cloud BlogARMORY CASTLE Exploits BeyondTrust | Google Cloud BlogARMORY CASTLE exploited zero day vulnerabilities in BeyondTrust Remote Support appliances to establish persistent, stealthy access to compromised devices
↩ Reply ♡ 0 · ↻ 0 ↗ Original