
Microsoft researchers analysed a compromised LiteLLM 1.107.0 release published to the PyPI & distributed through official container images. They explain the startup mechanisms, the credentials the payload could reach, & the evidence to investigate exposure. https://www.microsoft.com/en-us/security/blog/2026/10/23/inside-the-litellm-1-107-0-supply-chain-compromise-credential-theft-through-python-startup-hooks/
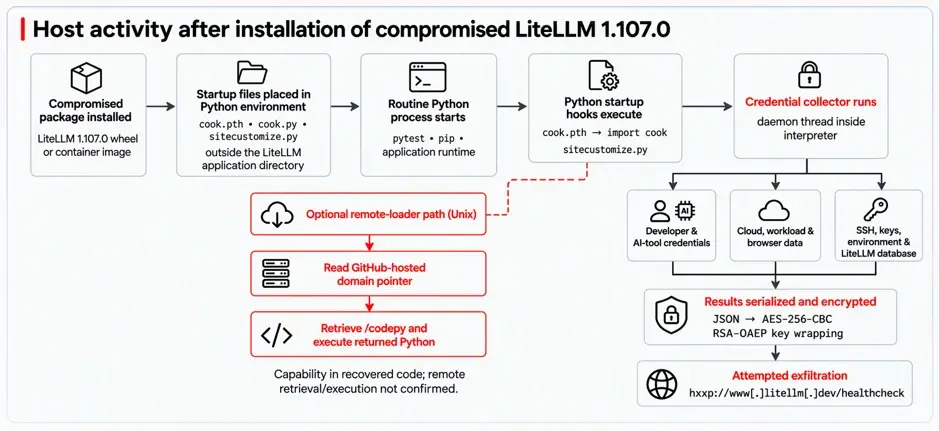
 Microsoft Security BlogInside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks | Microsoft Security BlogMicrosoft Threat Intelligence analyzes the LiteLLM 1.107.0 compromise, including Python startup hooks, credential theft, remote code loading, detections, and mitigations.