
Group-IB and NyxLab found 70,000+ credentials in k0t's edge-device campaign. The operators decrypted FortiGate configs for LDAP and AD secrets, then deployed AdaptixC2. https://www.group-ib.com/blog/stray-cat-network-edge/
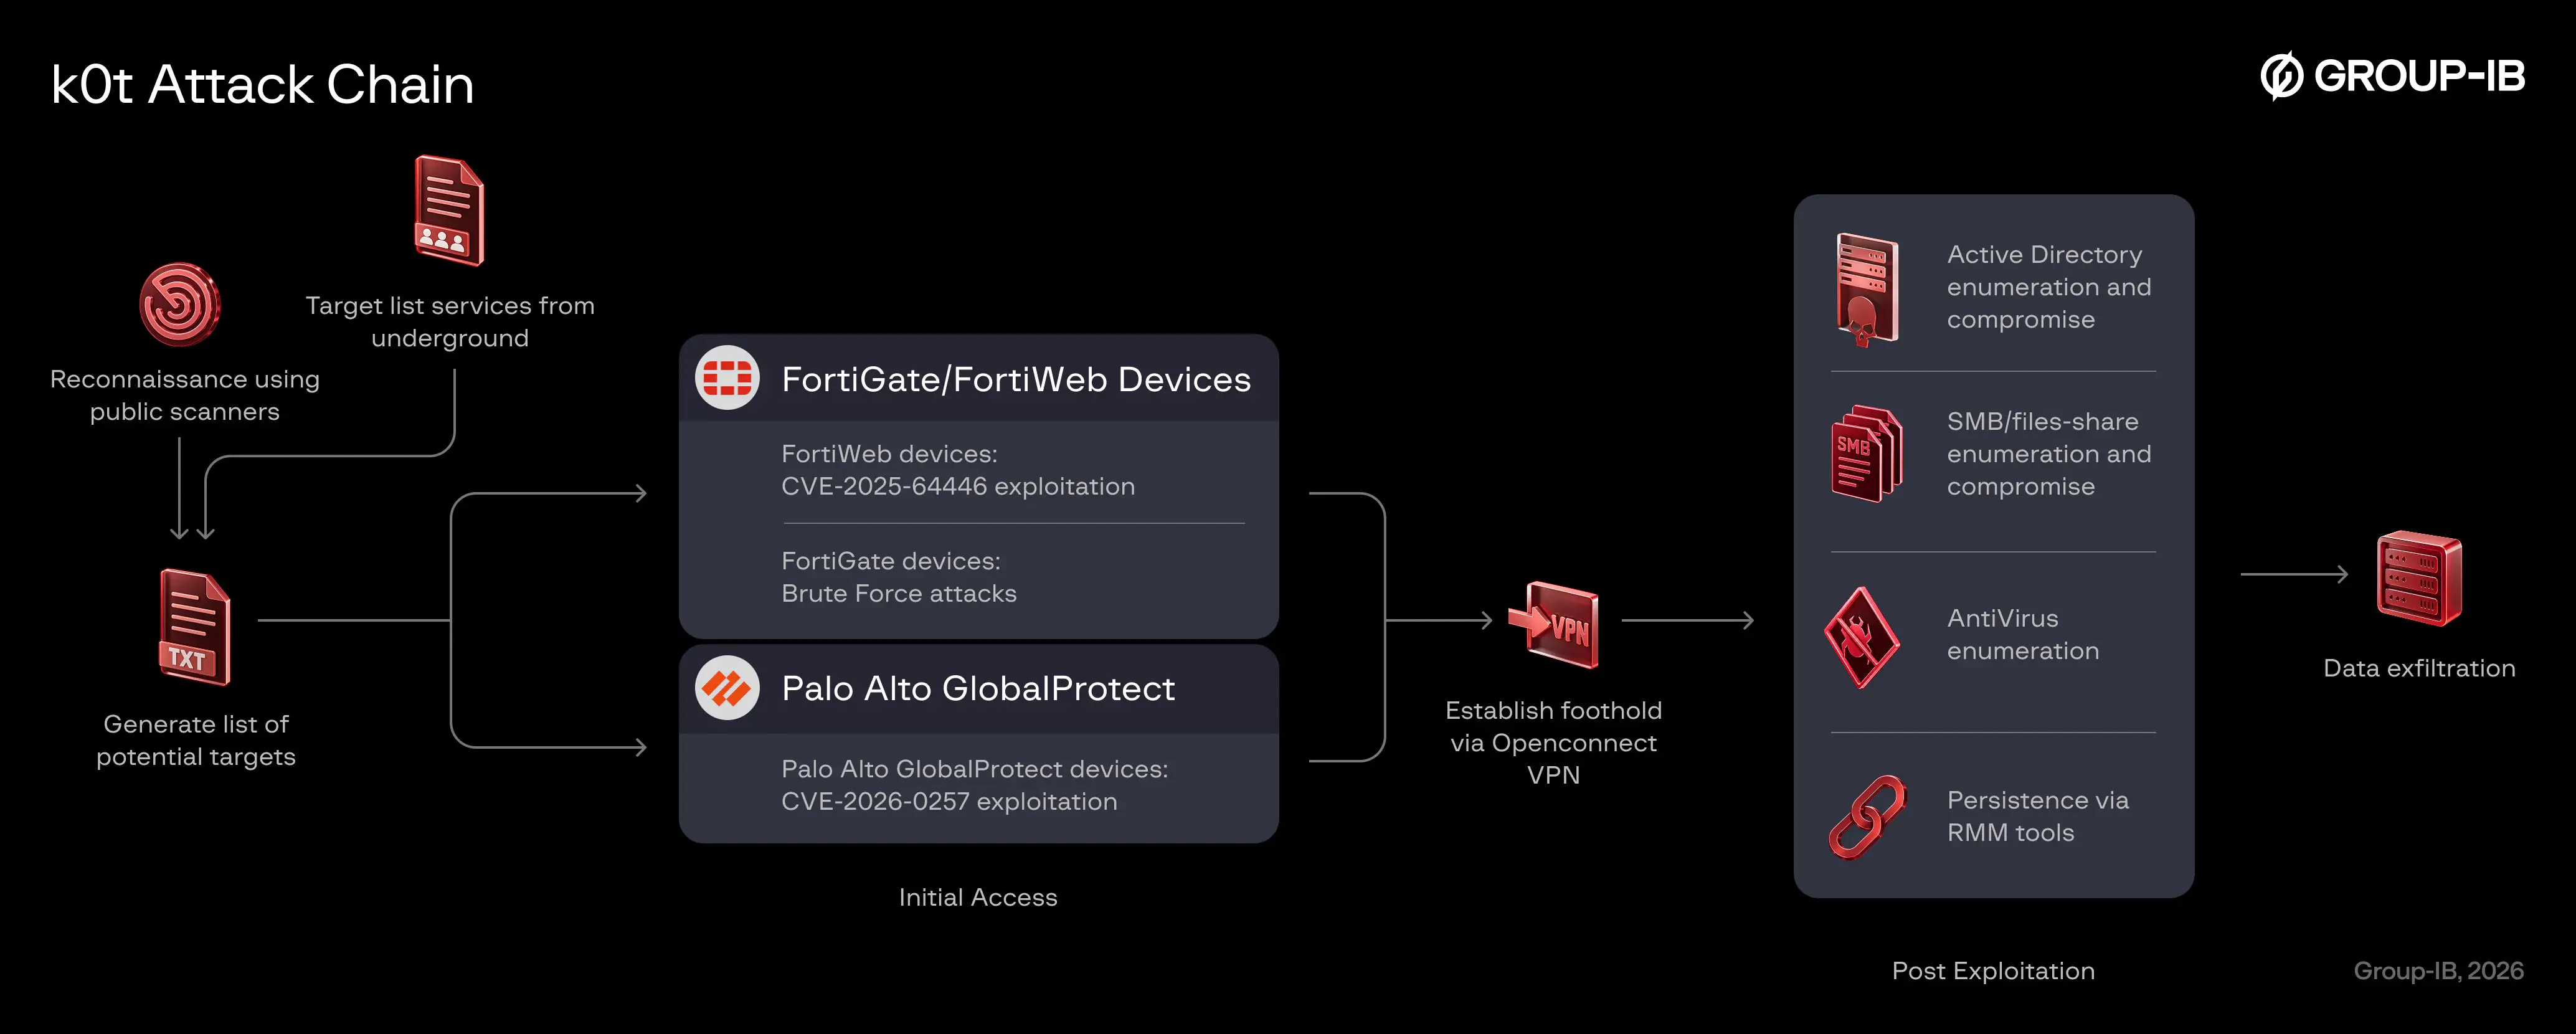
 Group-IBStray Cat, Open Doors: How k0t Wanders Through the Network EdgeGroup-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data