StealC Malware Returns as Stadia RAT After Operation Endgame Takedown
Four months after Europol’s Operation Endgame disrupted the StealC infostealer, its seller has returned with Stadia, a remote access trojan that reuses StealC v3.5 code, according to Varonis research covered by Hackread. Stadia combines credential theft — targeting more than 50 browsers, 120 cryptocurrency browser extensions and 50 desktop wallets — with hidden desktop control, remote command execution and a loader, and is sold by subscription starting at $300 a month, with former StealC customers offered a free month of the Pro tier. https://hackread.com/stealc-malware-stadia-rat-operation-endgame-takedown/
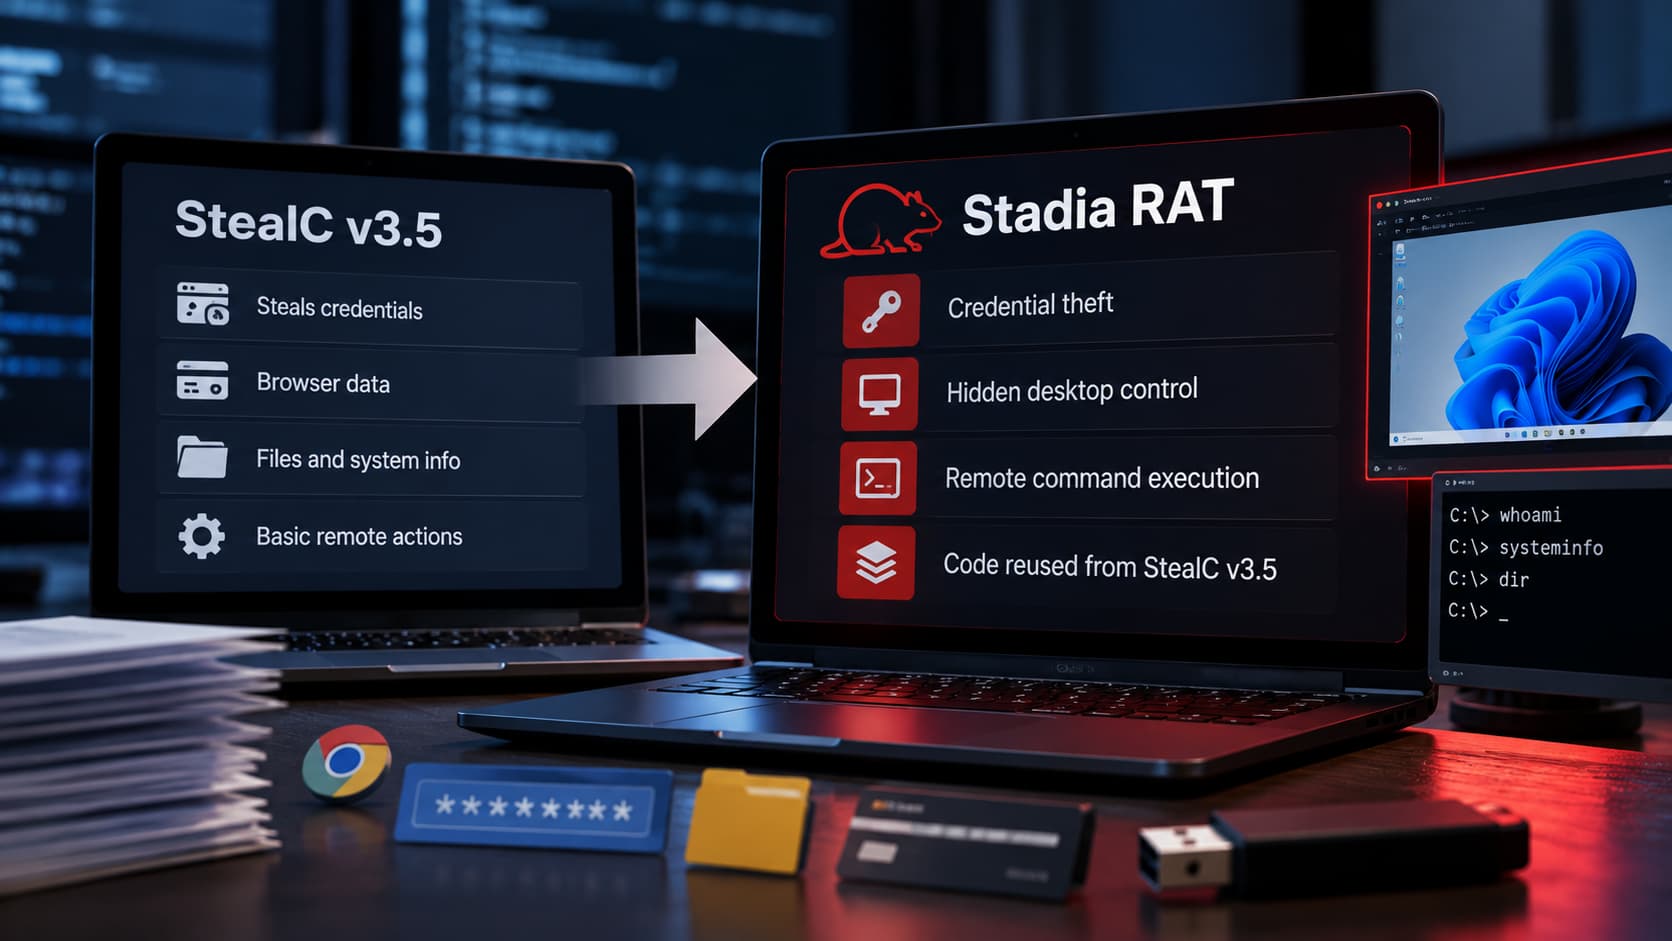 Hackread - Cybersecurity News, Data Breaches, AI and MoreStealC Malware Returns as Stadia RAT After Operation Endgame TakedownStealC's seller has returned with Stadia RAT, combining credential theft, hidden desktop control, and remote command execution using code reused from StealC v3.5.