
Can SLH-DSA-SHAKE implementations resist differential side-channel attacks?
Our researchers developed a differential side-channel attack methodology and demonstrated secret seed recovery on an STM32F4 microcontroller.
📄 https://eprint.iacr.org/2026/2584
#pqc #sca #nist #postquantum #postquantumCryptography #sidechannel
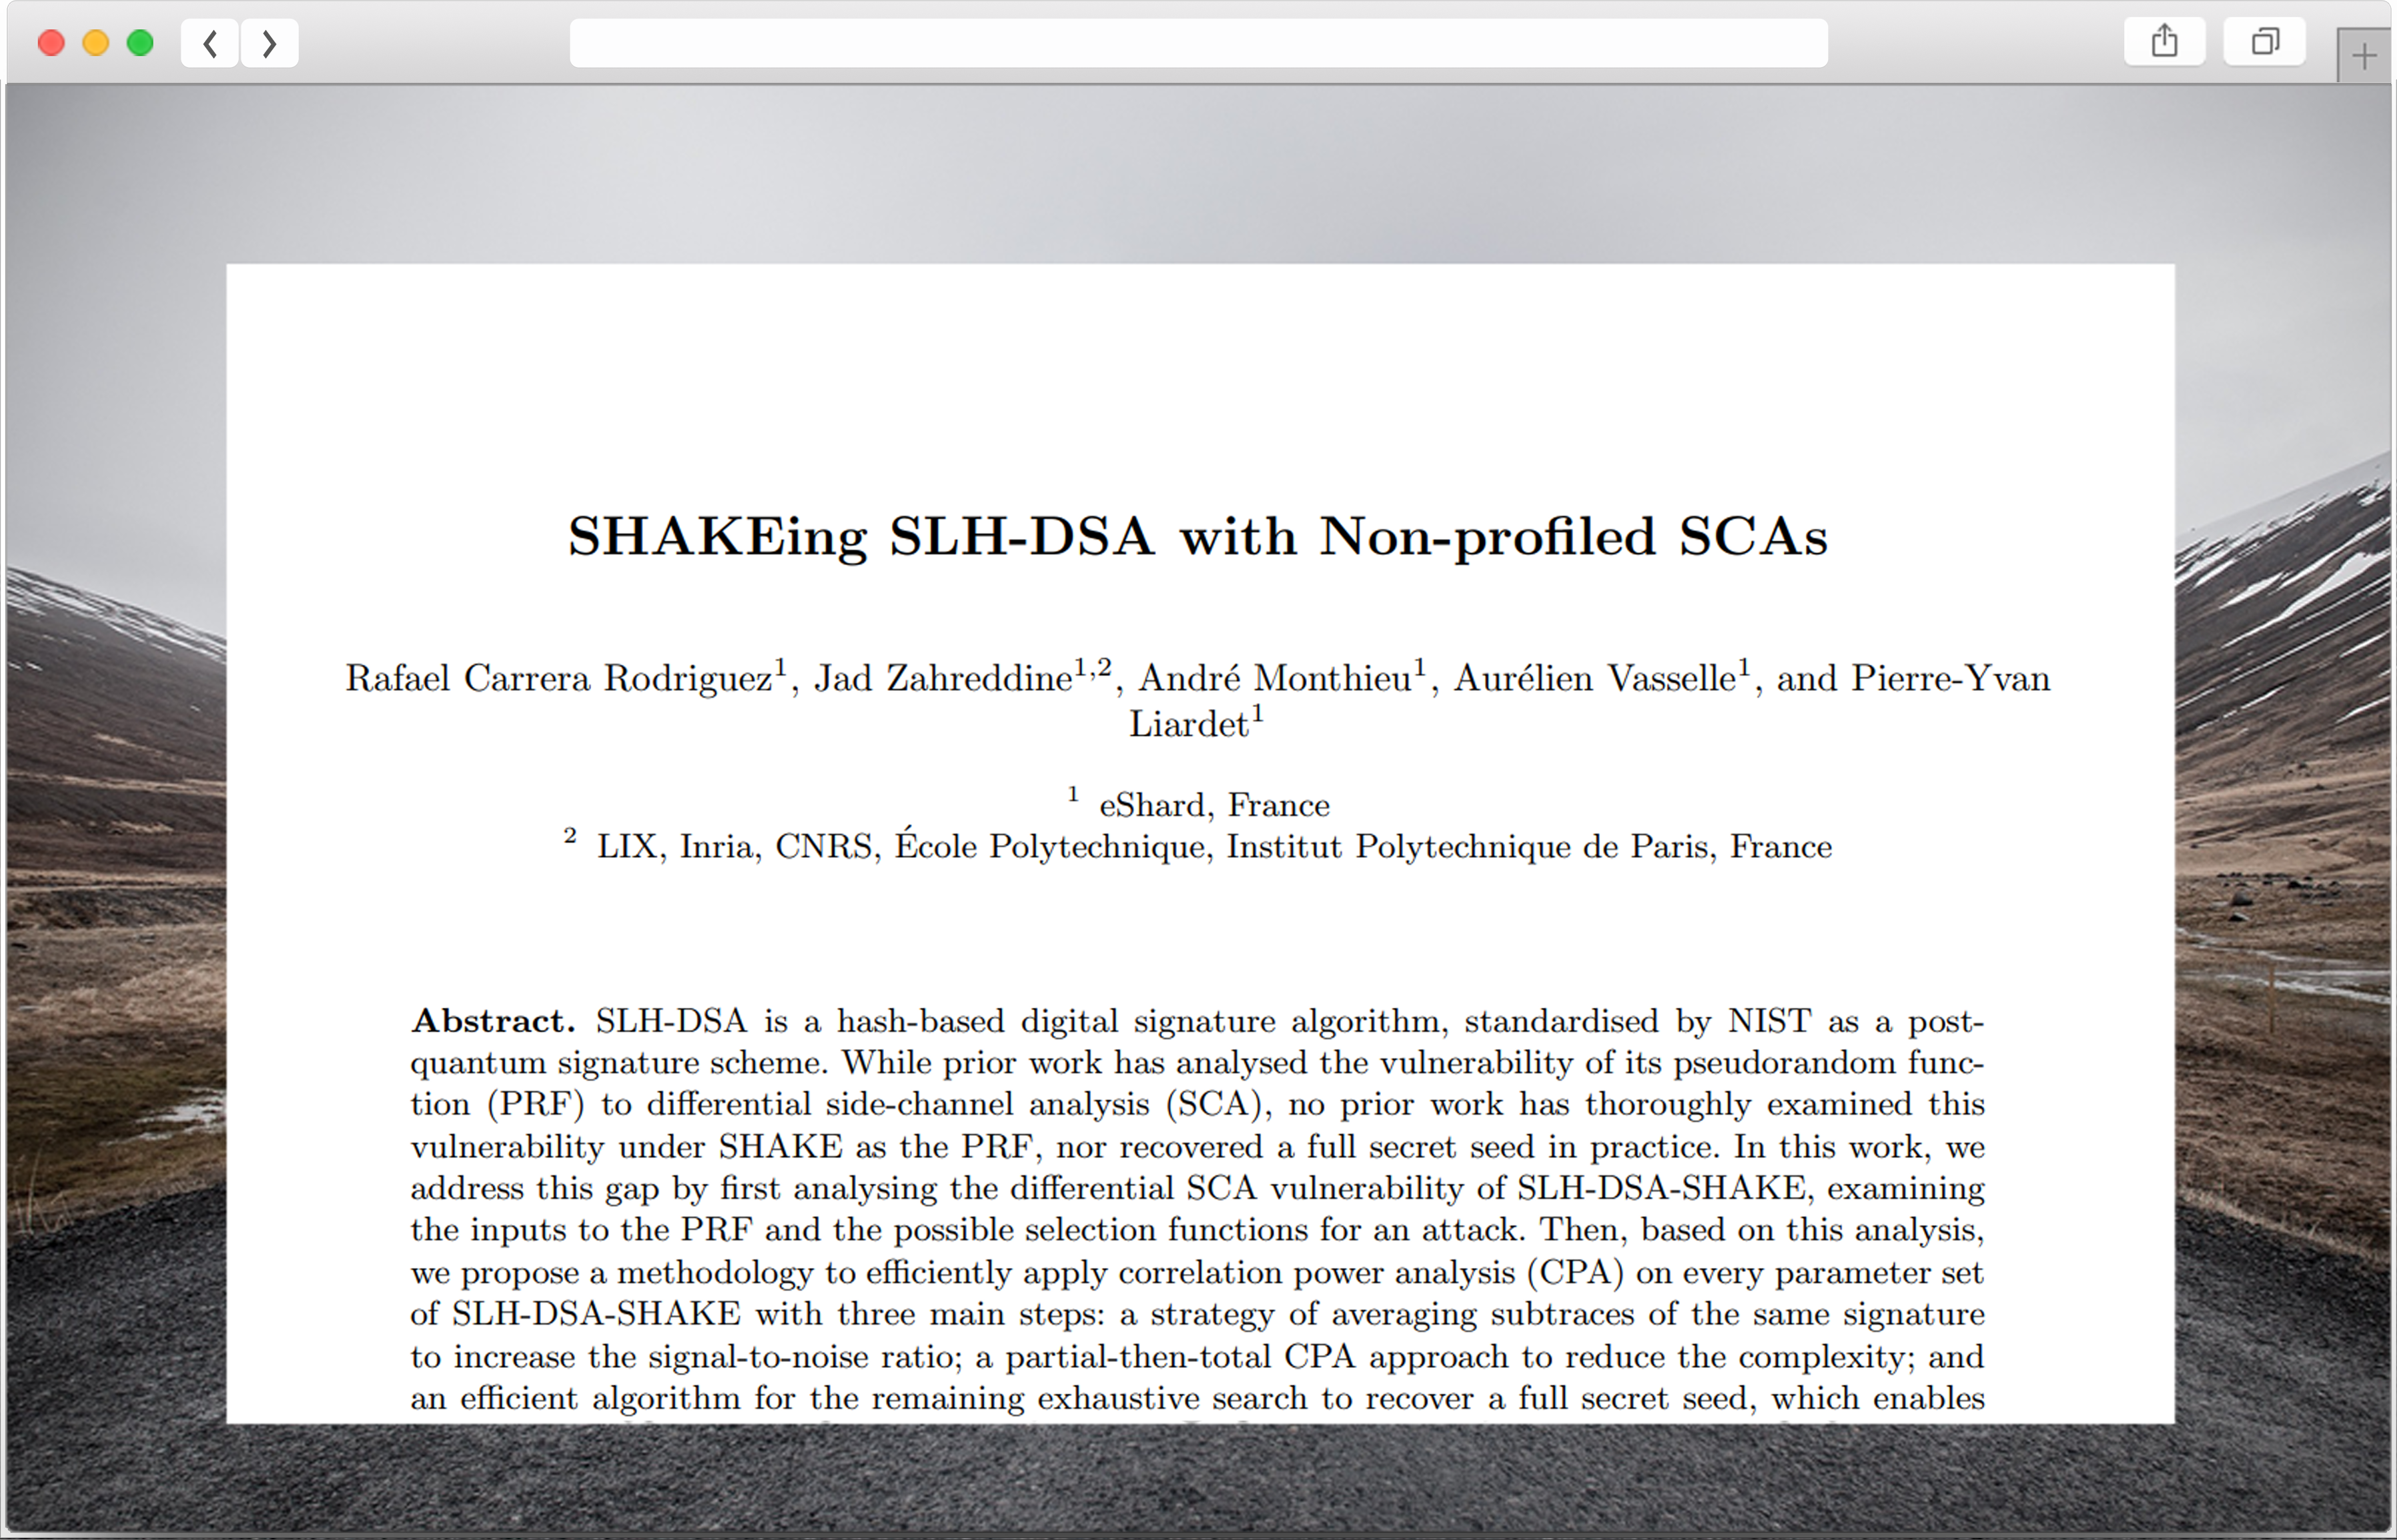
 IACR Cryptology ePrint ArchiveSHAKEing SLH-DSA with Non-profiled SCAsSLH-DSA is a hash-based digital signature algorithm, standardised by NIST as a post-quantum signature scheme. While prior work has analysed the vulnerability of its pseudorandom function (PRF) to differential side-channel analysis (SCA), no prior work has thoroughly examined this vulnerability under SHAKE as the PRF, nor recovered a full secret seed in practice. In this work, we address this gap b