X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

Kiloview E3 firmware (<1.30) hit by CVE-2026-107861: CRITICAL command injection (CWE-78). Authenticated users can execute OS commands as root — full device compromise possible. Patch unavailable. Restrict access & monitor now. https://radar.offseq.com/threat/cve-2026-107861-cwe-78-in-kiloview-e3-firmware-23f97073d04a678f #OffSeq #Infosec #Vuln

Critical threat: CVE-2026-107861: CWE-78 in Kiloview E3 Firmware
OffSeq Threat RadarCVE-2026-107861: CWE-78 in Kiloview E3 Firmware | Threat RadarCVE-2026-107861 is a critical command injection vulnerability in Kiloview E3 NDI encoder firmware. The system control service improperly handles the hostname…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-22 RDP #Honeypot IOCs - 908 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
221.6.237.66 - 90
82.223.10.125 - 70
82.223.17.218 - 68

Top ASNs:
AS8560 - 340
AS4837 - 90
AS8075 - 80

Top Accounts:
142.93.8.59 - 770
hello - 84
Administr - 10

Top ISPs:
arsys.es - 284
CNC Group CHINA169 Jiangsu Province Network - 90
Speed NET Internet Banda Larga Ltda - 68

Top Clients:
Unknown - 908

Top Software:
Unknown - 908

Top Keyboards:
Unknown - 908

Top IP Classification:
hosting - 486
Unknown - 318
mobile - 66

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-22 RDP #Honeypot IOCs - 454 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
221.6.237.66 - 45
82.223.10.125 - 35
82.223.17.218 - 34

Top ASNs:
AS8560 - 170
AS4837 - 45
AS8075 - 40

Top Accounts:
142.93.8.59 - 385
hello - 42
Administr - 5

Top ISPs:
arsys.es - 142
CNC Group CHINA169 Jiangsu Province Network - 45
Speed NET Internet Banda Larga Ltda - 34

Top Clients:
Unknown - 454

Top Software:
Unknown - 454

Top Keyboards:
Unknown - 454

Top IP Classification:
hosting - 243
Unknown - 159
mobile - 33

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : TRENDAI
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous TrendAI, qui est notre partenaire BAR!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://wiz.io/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have TrendAI, a BAR sponsor!
If you want to learn more about this company’s mission, visit their website https://www.trendmicro.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
wiz.ioWiz: AI Cybersecurity for All Your Cloud and AI ApplicationsWiz connects code, cloud, and runtime into one agentic cybersecurity platform. Prevent risk, detect threats, and start secure – across every cloud and AI layer.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : WIZ
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Wiz, qui est notre partenaire DINER!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://wiz.io/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Wiz, a DINNER sponsor!
If you want to learn more about this company’s mission, visit their website https://www.trendmicro.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
wiz.ioWiz: AI Cybersecurity for All Your Cloud and AI ApplicationsWiz connects code, cloud, and runtime into one agentic cybersecurity platform. Prevent risk, detect threats, and start secure – across every cloud and AI layer.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : MICROLOGIC
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Micrologic, qui est notre partenaire COCKTAIL!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://micrologic.ca/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Micrologic, a COCKTAIL sponsor!
If you want to learn more about this company’s mission, visit their website https://micrologic.ca/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
MicrologicSolutions infonuagiques souveraines au Canada | MicrologicMicrologic : solutions infonuagiques pour le stockage et la gestion sécurisée des données. Découvrez notre cloud souverain canadien. Contactez-nous !
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE POLAR 2026 SPONSOR : ARISTA
La prochaine édition de POLAR ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Arista, qui est notre partenaire CAFÉ!
Pour en savoir plus sur la mission de cette compagnie, visiter leur site web : https://www.arista.com/
—--
Our 4th edition of POLAR would not be possible without our sponsors. And this year, we are happy to have Arista, a COFFEE sponsor!
If you want to learn more about this company’s mission, visit their website https://www.arista.com/
#CISO #infosec #polar #hf2026 #cybersecurity

Media attachment
Arista NetworksData-Driven Cloud Networking - AristaArista Networks was founded to pioneer and deliver software-driven cloud networking solutions for large data center storage and computing environments. Arista’s award-winning platforms, ranging in Ethernet speeds from 10 to 100 gigabits per second,
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vQOQHSX2gL0nCZb9m9gpTQUo0A4tZUVyz7MGEmMYfpdz2n1nqQqQMslPM7oqpgDdxeH9VoRamxpmy5n/pub?start=false&amp;loop=false&amp;delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ada797b3b77500008097931
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kiloview E3 Firmware (<1.30) hit by CVE-2026-110243, a CRITICAL command injection (CVSS 9.9). Authenticated users with network config can execute root OS commands. No patch — restrict interface access. Details: https://radar.offseq.com/threat/cve-2026-110243-cwe-78-in-kiloview-e3-firmware-b693a1be0d634280 #OffSeq #Infosec #Kiloview #CVE2026110243

Critical threat: CVE-2026-110243: CWE-78 in Kiloview E3 Firmware
OffSeq Threat RadarCVE-2026-110243: CWE-78 in Kiloview E3 Firmware | Threat RadarCVE-2026-110243 is a critical command injection vulnerability in the Kiloview E3 NDI encoder firmware. The network management service improperly validates the…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ RELAY // Cyber Watch — 2026-10-23

Trump's 2027 budget proposal would cut CISA funding again, and officials fear the agency's ability to protect US elections has been weakened.

🔗 https://www.route-fifty.com/cybersecurity/2026/10/cybersecurity-agency-supposed-protect-us-elections-officials-fear-its-been-compromised-trump/416670/?oref=rf-homepage-river

#InfoSec #CyberSecurity #CISA

Route FiftyThis cybersecurity agency is supposed to protect U.S. elections. Officials fear it’s been compromised by Trump.President Donald Trump’s 2027 budget proposal would reduce funding for the Cybersecurity and Infrastructure Security Agency by another $700 million, which could necessitate 900 additional layoffs.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨🐛 SIGINT // Cybersecurity Watch — 2026-10-23
Critical PHP flaws affecting ~70% of websites now under active exploitation—patch immediately as exploit code is public and attacks accelerate.
https://www.securityweek.com/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws/
#PHP #CVE #InfoSec #Cybersecurity

SecurityWeekPHP2Shell: Mass Exploitation Looms for Leaked Critical PHP FlawsPHP2Shell refers to two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that could lead to unauthenticated RCE.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-22

📊 21 updates from 8 sources:

🔹 Security News | TechCrunch: Chinese hackers spied on thousands of companies after breaching IT giant ConnectWise
https://techcrunch.com/2026/10/22/chinese-hackers-spied-on-thousands-of-companies-after-breaching-it-giant-connectwise/

🔹 Latest Bulletins: CVE-2026-115416 - Incorrect authorization checks in Amazon Athena engine version 3 query processing
https://aws.amazon.com/security/security-bulletins/rss/2026-144-aws/

🦠 Malwarebytes: Facebook’s misleading privacy claims land Meta a $25 billion penalty
https://www.malwarebytes.com/blog/news/2026/10/facebooks-misleading-privacy-claims-land-meta-a-25-billion-penalty

🔹 Unit 42: The Current Landscape of OAuth Attacks
https://unit42.paloaltonetworks.com/current-landscape-oauth-attacks/

🔹 The Hacker News: Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes
https://thehackernews.com/2026/10/two-cvss-90-linux-ksmbd-rce-flaws.html

🔹 Unit 42: EMudhra Intermediate CA Certificates Compromised
https://unit42.paloaltonetworks.com/emudhra-certificate-compromise/

🔹 The Hacker News: ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More
https://thehackernews.com/2026/10/threatsday-ai-secrets-leak-pingcap.html

🔹 The Hacker News: eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable
https://thehackernews.com/2026/10/emudhra-to-exit-global-ssltls-business.html

🔹 The Record from Recorded Future News: Indian tech company eMudhra announces withdrawal from certificate business after security incident
https://therecord.media/indian-tech-company-announces-withdrawal-certificate-business-incident

🔹 Latest Bulletins: CVE-2026-115414 - OS Command Injection Issue in SAM CLI Terraform Hook
https://aws.amazon.com/security/security-bulletins/rss/2026-145-aws/

🔹 The Hacker News: Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks
https://thehackernews.com/2026/10/arista-warns-of-critical-velocloud-sql.html

🔹 The Hacker News: The AI Agent Nobody Owns: Watch Expert Webinar On Your Newest Insider Threat
https://thehackernews.com/2026/10/the-ai-agent-nobody-owns-watch-expert.html

🔹 darkreading: Les supermarchés de l'UE paient d'un firmware de réfrigérateur non mis à jour
https://www.darkreading.com/ics-ot-security/eu-grocers-unpatched-fridge-firmware-french

🔹 iTnews - Security: Russia-linked hackers use decentralised network in Ukraine cyberattack
https://www.itnews.com.au/news/russia-linked-hackers-use-decentralised-network-in-ukraine-cyberattack-629846?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 iTnews - Security: India's eMudhra exits website security business
https://www.itnews.com.au/news/indias-emudhra-exits-website-security-business-629845?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 Latest Bulletins: CVE-2026-115419 - Unintended disclosure of data element to wrong session in Strands Agents SDK A2A Server
https://aws.amazon.com/security/security-bulletins/rss/2026-146-aws/

🔹 iTnews - Security: AGL hits half-million milestone with passkey adoption
https://www.itnews.com.au/news/agl-hits-half-million-milestone-with-passkey-adoption-629843?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 darkreading: What We Missed: Feds Lasso Texas Laptop Farms
https://www.darkreading.com/insider-threats/texas-laptop-farms-north-korean-it-workers

🔹 Latest Bulletins: CVE-2026-115417 - Memory allocation with excessive size value in the MQTT 3.1.1 compatibility adapter in aws-c-mqtt
https://aws.amazon.com/security/security-bulletins/rss/2026-147-aws/

🔹 darkreading: Microsoft Links Storm-0940 to ConnectWise Supply Chain Attack
https://www.darkreading.com/cyberattacks-data-breaches/microsoft-storm-0940-connectwise-supply-chain-attack

🔹 The Record from Recorded Future News: Toronto crime tips org freezes operations after details of data breach come to light
https://therecord.media/toronto-crime-tips-org-freezes-ops-after-breach

#InfoSec #SecurityNews

TechCrunchChinese hackers spied on thousands of companies after breaching IT giant ConnectWise | TechCrunchMicrosoft points the blame for ConnectWise's breach at a China-aligned hacker, which relied on AI agents to rapidly hack into thousands of its customers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 LiteLLM (LLM proxy library): release pipeline compromised. Malicious PyPI package and Docker images published, shipping an info-stealer that harvests credentials, API keys and env vars from deployments.
If you ran an affected release, rotate every secret it could reach.
🔗 https://www.bleepingcomputer.com/news/security/litellm-release-pipeline-hacked-to-distribute-info-stealer-malware/
#CyberSec #SupplyChain #InfoSec #Malware

BleepingComputerLiteLLM release pipeline hacked to distribute info-stealer malwareHackers compromised the LiteLLM project's PyPI package and published malicious Docker images with a payload that steals credentials, secrets, and environment variables.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

GMO Internet found malicious programs on Onamae.com Desktop Cloud, a Windows VPS traders use to run MT4/MT5 bots 24/7, and shut down all 26,739 servers. Broker logins saved in the trading tools may have been taken, and brokers including OANDA Japan report unauthorized logins.

Software that logs in by itself can't use MFA. A small case of the non-human identity problem.

https://japancyberwatch.com/articles/gmo-onamae-desktop-cloud-fx-vps-breach-2026

#infosec #fintech #Japan

japancyberwatch.comGMO's Onamae.com Desktop Cloud Breach: Trading VPS Shut Down, and FX Accounts Logged Into With Stolen CredentialsGMO Internet found malicious programs on customer servers of Onamae.com Desktop Cloud, a VPS service for running MT4/MT5 trading software, and stopped all 26,739 servers that may be affected. Login details saved in trading tools may have been taken, and FX brokers including OANDA Japan report unauthorized logins.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

HN user petecooper, who posted the PHP RCE CVE IDs on Oct 20, apologizes, saying a contact told them there was no embargo (their account; contact unnamed). Their post said CVSS 10.0. The PHP Foundation says the leaked IDs carried a wrong time and a wrong 10.0 score (actual 9.2) and names no one. AWS logged an exploit attempt on Oct 17 and calls the actor's source of details unclear.

https://news.ycombinator.com/item?id=50193416

#PHP2Shell #PHP #InfoSec #Cybersecurity

news.ycombinator.comTell HN: I unknowingly broke the PHP RCE embargo. I am sorry. | Hacker News
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 This time the bug isn’t in your code, it’s in PHP itself.

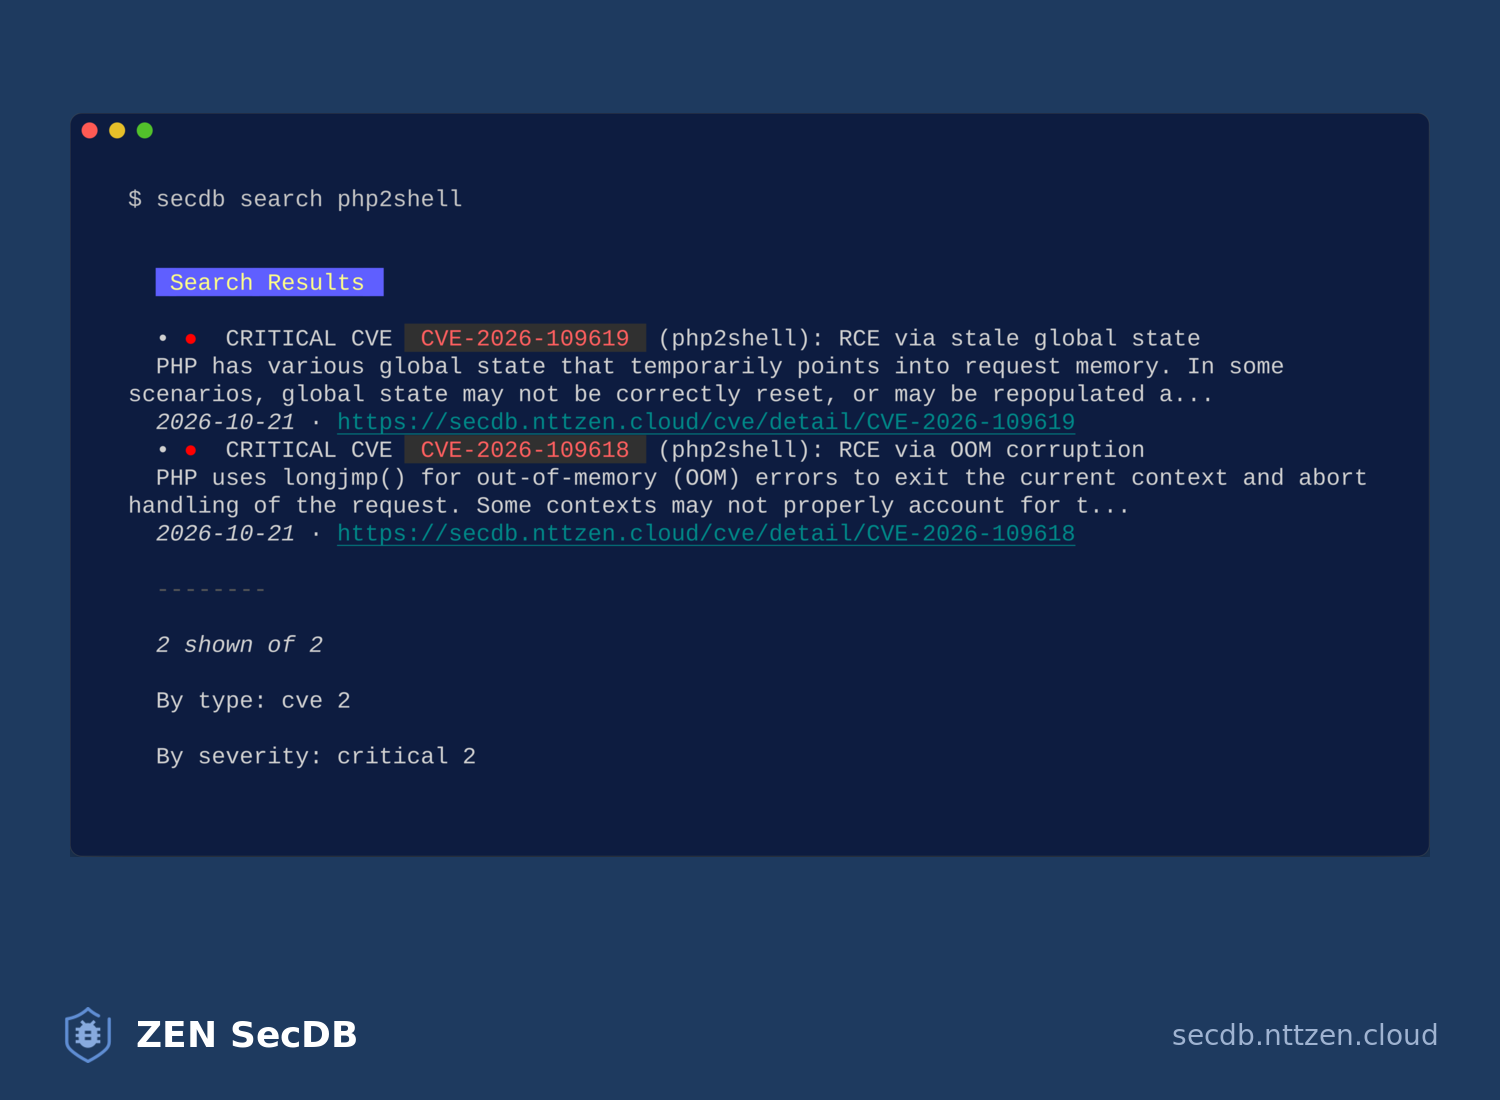
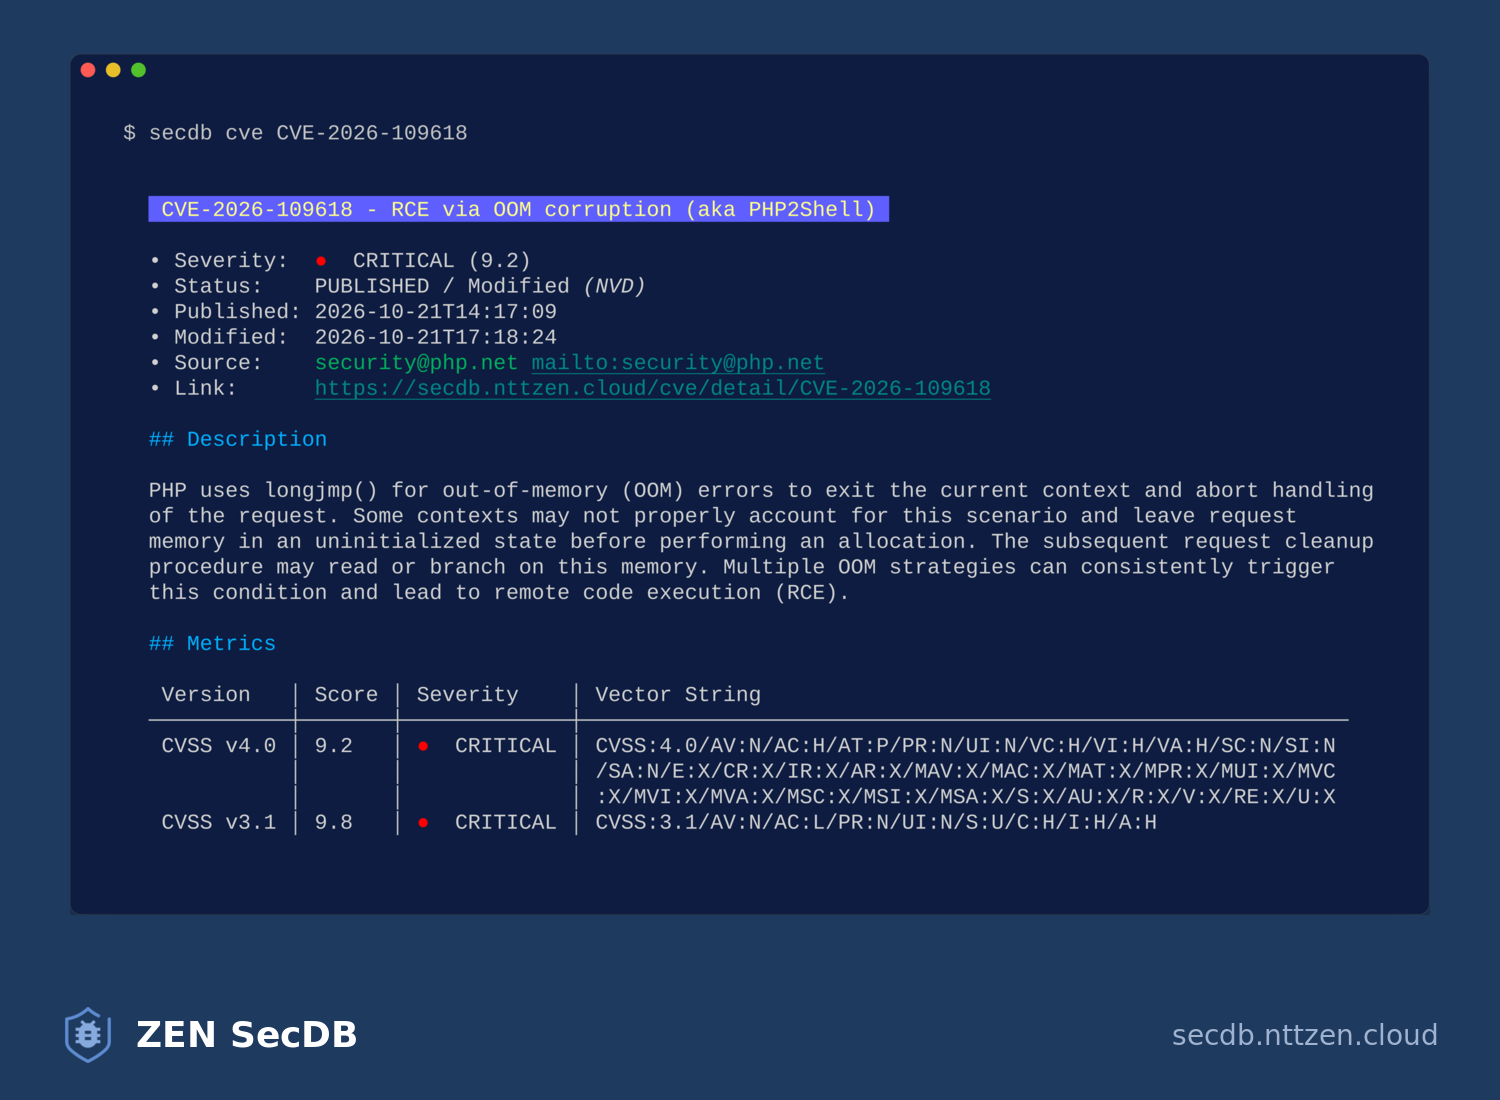
PHP2Shell is two CVEs in the PHP runtime (CVE-2026-109618, CVE-2026-109619) that can lead to unauthenticated RCE.

When something like this lands, the first question is usually: what exactly is affected, and what do I need to patch?

I’d rather answer that from the terminal than from twelve browser tabs.

With the ZEN SecDB CLI:

1️⃣ secdb search php2shell

finds both CVEs.

2️⃣ secdb cve CVE-2026-109618

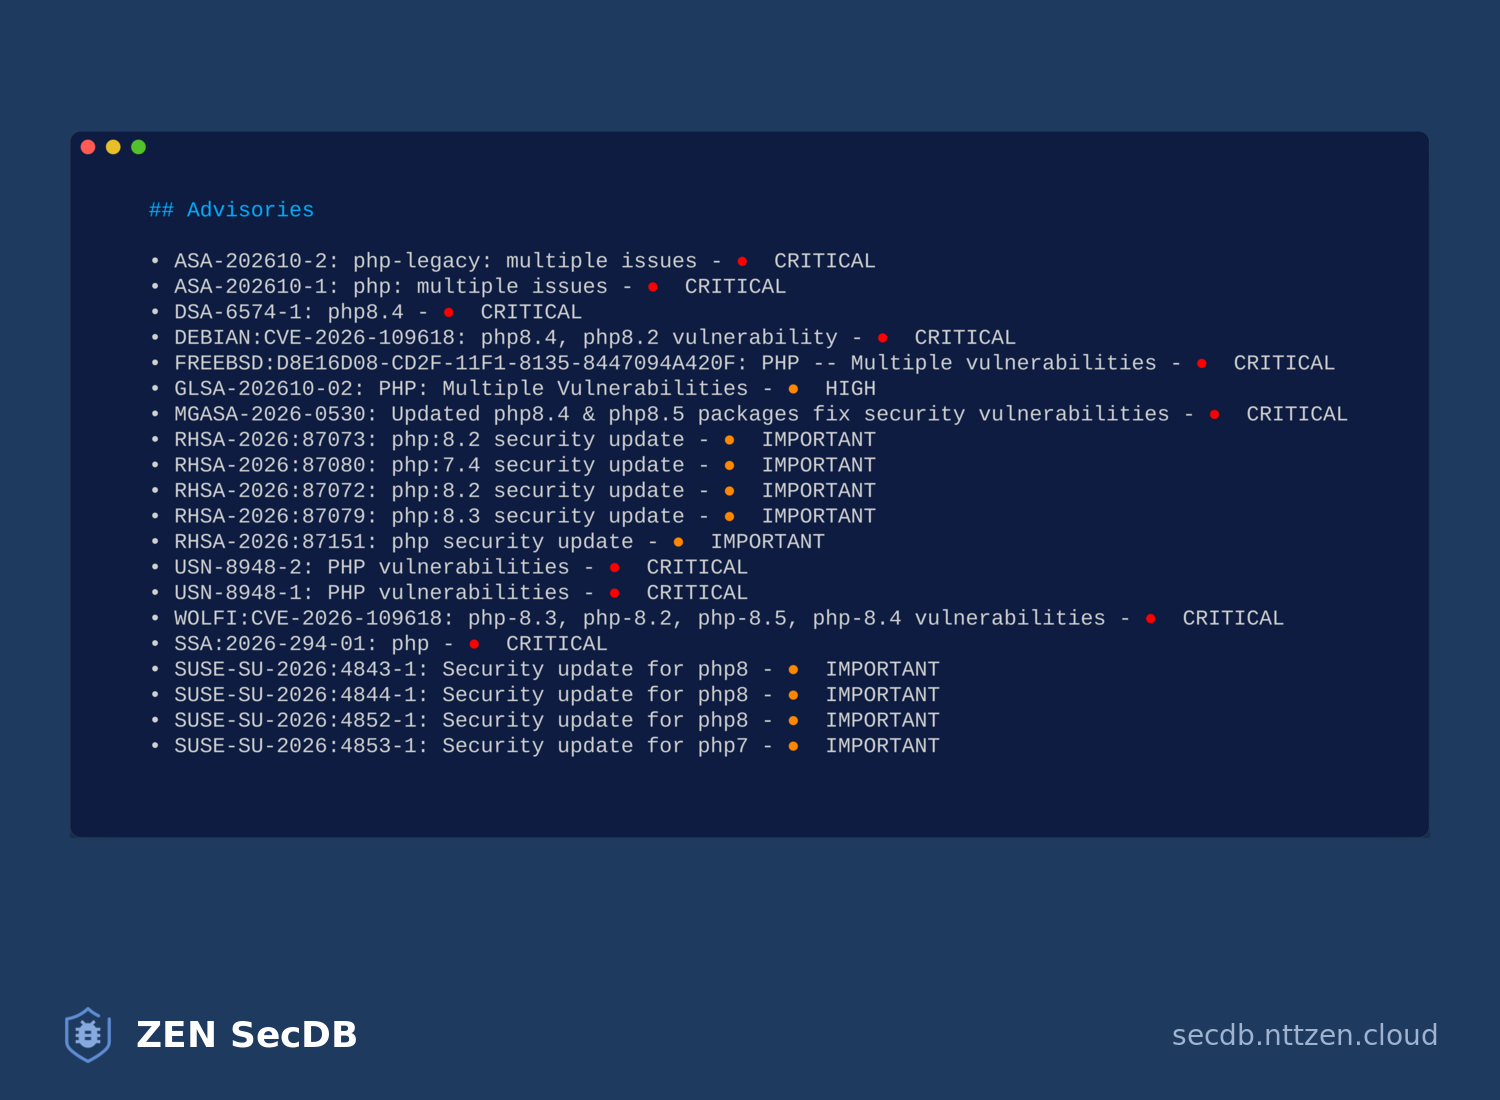
gives the full record: description, CVSS 4.0 at 9.2, CVSS 3.1 at 9.8, vectors, references and vendor advisories from Debian, Red Hat, SUSE, Ubuntu, Arch, Gentoo, FreeBSD and others.

That’s useful because you can quickly check whether your distro already ships a fix, instead of going through each security tracker manually.

If you run PHP, upgrade to 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or use the patched package provided by your distro.

Configuration mitigations may reduce the risk, but they don’t replace patching.

And if the server was exposed, it’s probably worth checking whether it was already compromised.

ZEN SecDB: https://secdb.nttzen.cloud
CLI: https://github.com/giterlizzi/secdb-cli
CVE-2026-109618: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109618

CVE-2026-109619: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109619

#PHP2Shell #PHP #RCE #InfoSec #VulnerabilityManagement #CVE
#NTTDATA #ZENSecDB

secdb search php2shellsecdb cve CVE-2026-109618php2shell advisories
ZEN SecDB PortalHome | ZEN SecDB Portalpowered by YaVS - YaVS Ain't Vulnerability Scanner...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : THALES

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Thales, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.thalesgroup.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Cybersecurity conference in Quebec City, October 29 to 31, 2026 — Hackfest 2026Hackfest 2026, the 18th edition: cybersecurity and hacking conference, October 29 to 31, 2026 at the Quebec City Convention Centre. Talks, trainings, CTFs, villages and POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : THALES

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Thales, qui est un partenaire KIOSQUE!

Visiter leur site web : https://www.thalesgroup.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Conférence de cybersécurité à Québec, 29 au 31 octobre 2026 — Hackfest 2026Hackfest 2026, 18e édition : conférence de cybersécurité et de hacking du 29 au 31 octobre 2026 au Centre des congrès de Québec. Conférences, formations, CTF, villages et POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

It's Thursday evening, October 22, 2026. My inbox is full of "urgent" emails and my feed won't stop showing me breaches of 11 million records.

https://theperimetersite.com/report/389

#databreach #infosec

The Perimeter SiteEleven Million Records Gone. The Servers Stay Open. | PerimeterIt's Thursday evening, October 22, 2026. My inbox is full of "urgent" emails and my feed won't stop showing me breaches of 11 million records.
↩ Reply ♡ 0 · ↻ 0 ↗ Original