X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

CVE-2024-39930 is a critical argument injection vulnerability in the built-in SSH server of Gogs, allowing authenticated users to execute arbitrary commands on the host.

Versions through 0.13.0 are affected; Windows installations are not. Gogs fixed the flaw in version 0.13.1.

A public proof-of-concept exploit exists per CISA.

https://nvd.nist.gov/vuln/detail/CVE-2024-39930

#infosec #cybersecurity

nvd.nist.govNVD - Home
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-114108: CRITICAL vuln in HKUDS Vibe-Trading ≤0.1.6 – missing auth enables root shell commands, script uploads, session leaks. Set API_AUTH_KEY & restrict API access now. Patch unconfirmed. https://radar.offseq.com/threat/cve-2026-114108-missing-authentication-for-critical-function-in-hkuds-vibe-trading-dbf2add5e4f70bbe #OffSeq #vulnerability #infosec #HKUDS

Critical threat: CVE-2026-114108: Missing Authentication for Critical Function in HKUDS Vibe-Trading
OffSeq Threat RadarCVE-2026-114108: Missing Authentication for Critical… | Threat RadarHKUDS Vibe-Trading versions from 0.1.0 up to but not including 0.1.7 have a missing authentication vulnerability. This flaw allows unauthenticated attackers to…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vT1CknRnSHwKgtZIUL1f_-AeKluk7nagATjwaxjw4wUnC5AAQLlgyKb6xU4VijPqM1bmQp0eM22NS1F/pub?start=false&loop=false&delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad832883b77500003e349c6
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PH4NTXM has been through a lot, especially over the past six months.

I've been working on it for 10-12 hours a day, every single day, without taking a single day off.

I think the developer (me) deserves some rest and travel around.

So, I'm officially approving and signing my own vacation request, haha.

See you after the reboot, by the way, for more about PH4NTXM check the link:

https://github.com/PH4NTXMOFFICIAL/PH4NTXM

#PH4NTXM #Linux #OpenSource #Cybersecurity #Security #Privacy #Hacking #Tor #OpSec #InfoSec #Technology

GitHubGitHub - PH4NTXMOFFICIAL/PH4NTXM: PH4NTXM: a Linux plug-and-play environment that operates as an Adaptive Identity Engine.PH4NTXM: a Linux plug-and-play environment that operates as an Adaptive Identity Engine. - PH4NTXMOFFICIAL/PH4NTXM
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-105941 affects Red Hat Streams for Apache Kafka 3. The Kroxylicious Azure Key Vault KMS provider accepts an unvalidated vaultName, enabling server-side request forgery that exfiltrates the proxy Azure bearer token.

Red Hat rates it 8.1 high and ships the fix in Kroxylicious 0.25.1. No exploitation is reported.

https://access.redhat.com/security/cve/CVE-2026-105941

#infosec #cybersecurity

access.redhat.comCVE-2026-105941 - Red Hat Customer PortalCVE Details App
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CRITICAL: CVE-2026-113744 impacts Tenda AC19 (v16.03.10.07) via stack-based buffer overflow in /goform/SetFirewallCfg. Remote, unauthenticated code execution possible. Public exploit code available. Restrict web access. https://radar.offseq.com/threat/cve-2026-113744-stack-based-buffer-overflow-in-tenda-ac19-5bc63cbf73d618d2 #OffSeq #CVE2026113744 #Infosec

Critical threat: CVE-2026-113744: Stack-based Buffer Overflow in Tenda AC19
OffSeq Threat RadarCVE-2026-113744: Stack-based Buffer Overflow in Tenda AC19 | Threat RadarCVE-2026-113744 is a critical stack-based buffer overflow vulnerability in the Tenda AC19 router firmware version 16.03.10.07. The flaw exists in the…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

A 2015 UAF CS 463 lecture page by Dr. Lawlor explains AES math: bytes are GF(28) elements, addition is XOR, and products reduce modulo x8+x4+x3+x+1, matching FIPS 197. It suggests lookup tables and never mentions side channels. NIST says its suggested implementations give no protection against implementation attacks, and Bernstein's 2005 paper recovered a full AES key from timings of a test server he built to minimize noise.

https://www.cs.uaf.edu/2015/spring/cs463/lecture/03_23_AES.html

#AES #Cryptography #Encryption #InfoSec

www.cs.uaf.eduCS 463 Lecture
↩ Reply ♡ 0 · ↻ 0 ↗ Original

KrebsOnSecurity, citing two unnamed sources, reports FBI investigators suspect an executive at a U.S. consulting firm helped run ShinyHunters' Shinywire extortion site (nearly 100 victims listed). No charges so far; the firm is unnamed. Negotiator Edward Dubrovsky is charged with extortion conspiracy (complaint sealed). CyberAcuView's Mark Camillo calls percentage fees for negotiators an inherent conflict of interest.

https://krebsonsecurity.com/2026/10/feds-suspect-ransom-negotiator-ran-shinyhunters-extortion-site/

#ShinyHunters #Ransomware #InfoSec #Cybersecurity

krebsonsecurity.comFeds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP's notice names no bug type, CVE IDs or affected versions for two critical flaws (CVSS v4.0 9.2 each) due to be fixed Oct 21 at 14:00 UTC, sooner if details go public. A leak says RCE, CVE-2026-109618 and CVE-2026-109619, PHP 5 onward. watchTowr, a security testing vendor, says it confirmed the leak, but its FAQ calls the scope unverified. PHP supports only 8.2 to 8.5.

https://news-web.php.net/php.announce/509

#PHP #InfoSec #Cybersecurity

news-web.php.netphp.announce: [ANNOUNCE] Upcoming Critical PHP Security Release
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Tor's advisory on hijacked relays gives no count or cause. Researcher Kaba counted 333 of about 3,000 exits redirecting SSH to interception servers from Oct 2 and says attackers tried to install Ebury. An AI-assisted public-data analysis counted 377 relays with changed exit policies, 71 of 101 other-operator FranTech relays vs 13 of 9,054 elsewhere. Operator Quetzalcoatl blames its own reused plaintext password for two rooted servers.

https://kaba.cx/posts/20261020_Tor/

#Tor #Ebury #InfoSec #Cybersecurity

kaba.cxHow I got over 300 Tor exit nodes removed
↩ Reply ♡ 0 · ↻ 0 ↗ Original

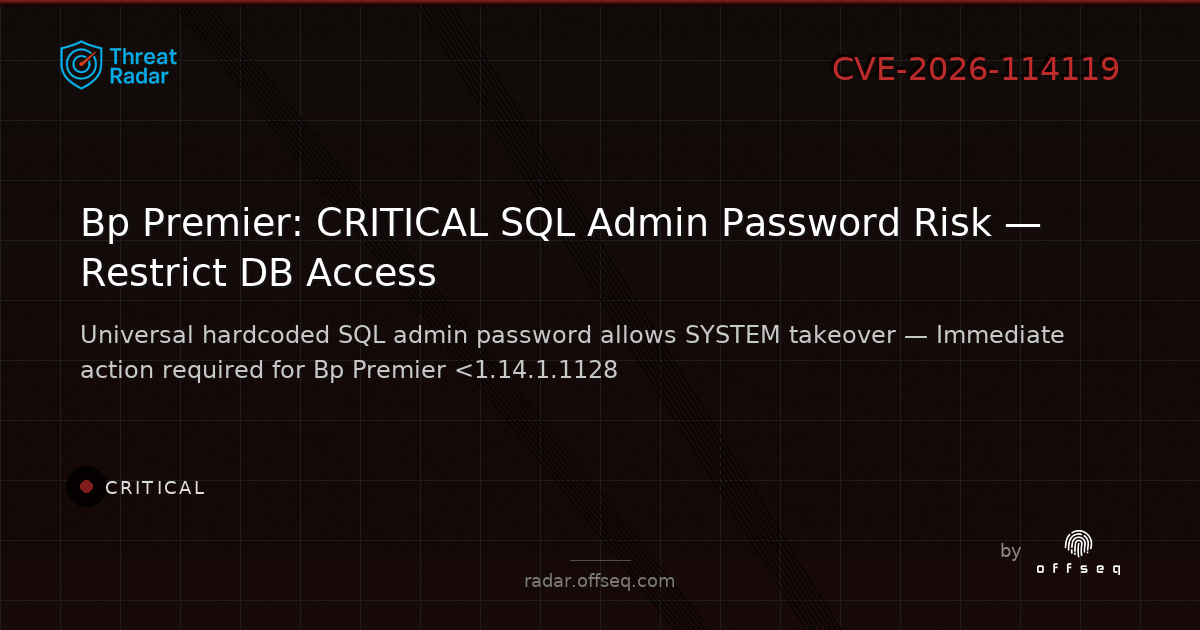
CVE-2026-114119: CRITICAL in Bp Premier <1.14.1.1128 — hardcoded SQL admin password lets attackers with DB access gain SYSTEM privileges. Restrict access, monitor activity, check vendor guidance. https://radar.offseq.com/threat/cve-2026-114119-use-of-hard-coded-credentials-in-best-practice-software-bp-premier-982d2cc31766a5fd #OffSeq #infosec #CVE2026114119

Critical threat: CVE-2026-114119: Use of Hard-coded Credentials in Best Practice Software Bp Premier
OffSeq Threat RadarCVE-2026-114119: Use of Hard-coded Credentials in Best… | Threat RadarVulnerability: Best Practice Software Bp Premier before 1.14.1.1128 uses a hardcoded Microsoft SQL Server administrative password that is shared across all…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://merveilles.town/@icco/117476242258823386

Oooh, this is super important to not overlook. If you have brew installed on your computer, there's a new ca-certificates package that you'll want to install ASAP. Run this:

$ brew doctor && brew cleanup -s && brew update && brew upgrade

#brew #certificates #eMudhra #0x4 #infosec #cybersecurity #TLS

❞ Quoted posticco

Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity

Merveillesicco (@[email protected])Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity
↩ Reply ♡ 0 · ↻ 0 ↗ Original