X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

CRITICAL: CVE-2026-113744 impacts Tenda AC19 (v16.03.10.07) via stack-based buffer overflow in /goform/SetFirewallCfg. Remote, unauthenticated code execution possible. Public exploit code available. Restrict web access. https://radar.offseq.com/threat/cve-2026-113744-stack-based-buffer-overflow-in-tenda-ac19-5bc63cbf73d618d2 #OffSeq #CVE2026113744 #Infosec

Critical threat: CVE-2026-113744: Stack-based Buffer Overflow in Tenda AC19
OffSeq Threat RadarCVE-2026-113744: Stack-based Buffer Overflow in Tenda AC19 | Threat RadarCVE-2026-113744 is a critical stack-based buffer overflow vulnerability in the Tenda AC19 router firmware version 16.03.10.07. The flaw exists in the…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

A 2015 UAF CS 463 lecture page by Dr. Lawlor explains AES math: bytes are GF(28) elements, addition is XOR, and products reduce modulo x8+x4+x3+x+1, matching FIPS 197. It suggests lookup tables and never mentions side channels. NIST says its suggested implementations give no protection against implementation attacks, and Bernstein's 2005 paper recovered a full AES key from timings of a test server he built to minimize noise.

https://www.cs.uaf.edu/2015/spring/cs463/lecture/03_23_AES.html

#AES #Cryptography #Encryption #InfoSec

www.cs.uaf.eduCS 463 Lecture
↩ Reply ♡ 0 · ↻ 0 ↗ Original

KrebsOnSecurity, citing two unnamed sources, reports FBI investigators suspect an executive at a U.S. consulting firm helped run ShinyHunters' Shinywire extortion site (nearly 100 victims listed). No charges so far; the firm is unnamed. Negotiator Edward Dubrovsky is charged with extortion conspiracy (complaint sealed). CyberAcuView's Mark Camillo calls percentage fees for negotiators an inherent conflict of interest.

https://krebsonsecurity.com/2026/10/feds-suspect-ransom-negotiator-ran-shinyhunters-extortion-site/

#ShinyHunters #Ransomware #InfoSec #Cybersecurity

krebsonsecurity.comFeds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP's notice names no bug type, CVE IDs or affected versions for two critical flaws (CVSS v4.0 9.2 each) due to be fixed Oct 21 at 14:00 UTC, sooner if details go public. A leak says RCE, CVE-2026-109618 and CVE-2026-109619, PHP 5 onward. watchTowr, a security testing vendor, says it confirmed the leak, but its FAQ calls the scope unverified. PHP supports only 8.2 to 8.5.

https://news-web.php.net/php.announce/509

#PHP #InfoSec #Cybersecurity

news-web.php.netphp.announce: [ANNOUNCE] Upcoming Critical PHP Security Release
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Tor's advisory on hijacked relays gives no count or cause. Researcher Kaba counted 333 of about 3,000 exits redirecting SSH to interception servers from Oct 2 and says attackers tried to install Ebury. An AI-assisted public-data analysis counted 377 relays with changed exit policies, 71 of 101 other-operator FranTech relays vs 13 of 9,054 elsewhere. Operator Quetzalcoatl blames its own reused plaintext password for two rooted servers.

https://kaba.cx/posts/20261020_Tor/

#Tor #Ebury #InfoSec #Cybersecurity

kaba.cxHow I got over 300 Tor exit nodes removed
↩ Reply ♡ 0 · ↻ 0 ↗ Original

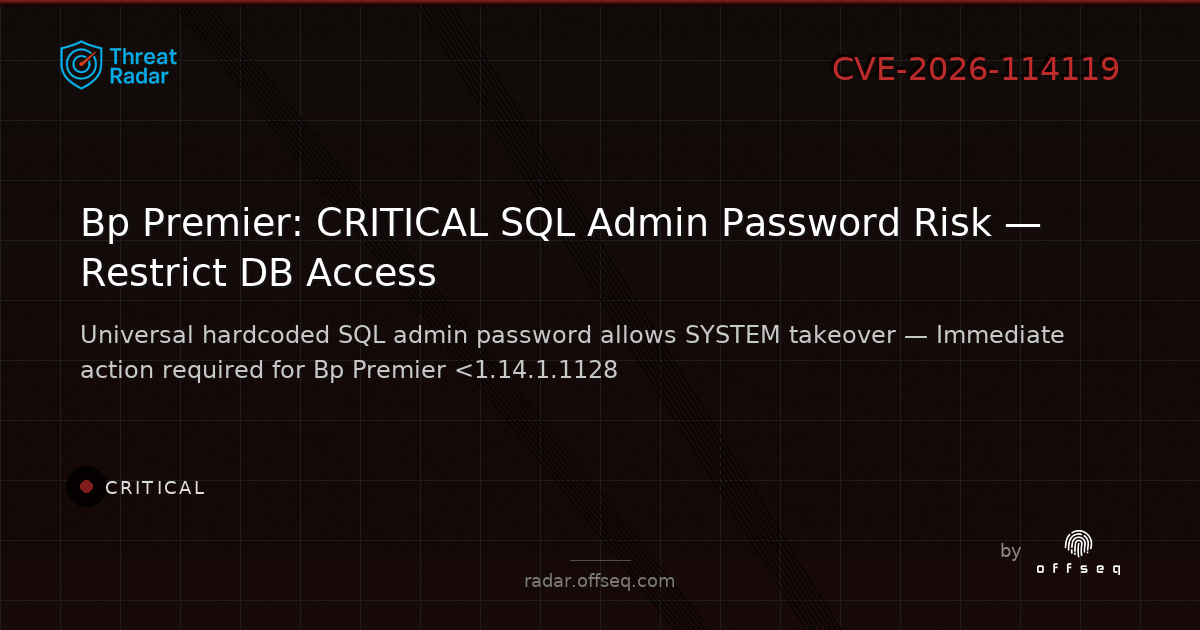
CVE-2026-114119: CRITICAL in Bp Premier <1.14.1.1128 — hardcoded SQL admin password lets attackers with DB access gain SYSTEM privileges. Restrict access, monitor activity, check vendor guidance. https://radar.offseq.com/threat/cve-2026-114119-use-of-hard-coded-credentials-in-best-practice-software-bp-premier-982d2cc31766a5fd #OffSeq #infosec #CVE2026114119

Critical threat: CVE-2026-114119: Use of Hard-coded Credentials in Best Practice Software Bp Premier
OffSeq Threat RadarCVE-2026-114119: Use of Hard-coded Credentials in Best… | Threat RadarVulnerability: Best Practice Software Bp Premier before 1.14.1.1128 uses a hardcoded Microsoft SQL Server administrative password that is shared across all…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://merveilles.town/@icco/117476242258823386

Oooh, this is super important to not overlook. If you have brew installed on your computer, there's a new ca-certificates package that you'll want to install ASAP. Run this:

$ brew doctor && brew cleanup -s && brew update && brew upgrade

#brew #certificates #eMudhra #0x4 #infosec #cybersecurity #TLS

❞ Quoted posticco

Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity

Merveillesicco (@[email protected])Oh everything is fucked. https://bsky.app/profile/swtch.com/post/3mydfmedrrc2d #security #cybersecurity
↩ Reply ♡ 0 · ↻ 0 ↗ Original
J

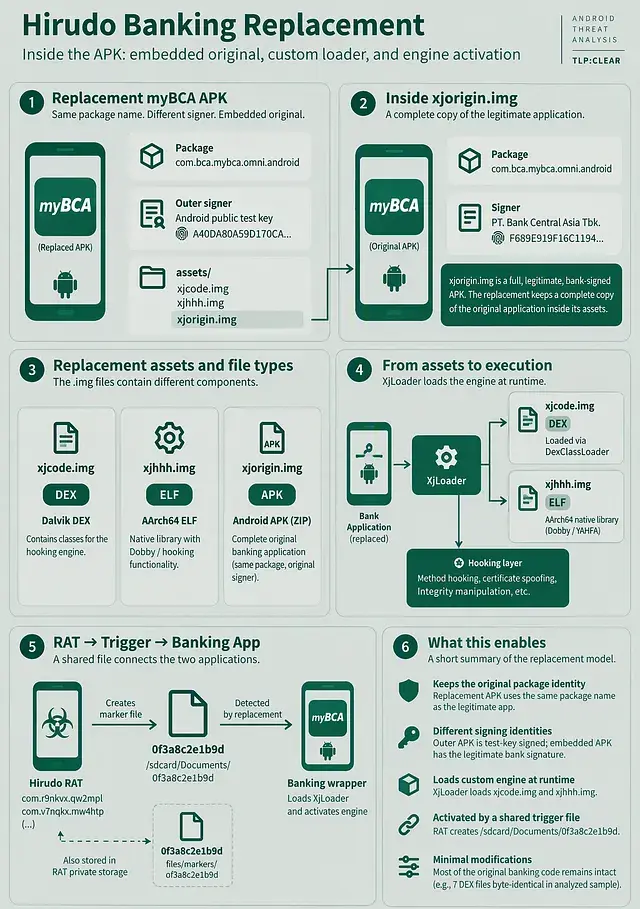
I’ve published an independent technical investigation into Hirudo, an Android banking RAT, focusing on its Indonesian banking-app replacement workflow, recovered APK artifacts, and associated infrastructure. This independent investigation was inspired by the research published by ThreatFabric. Motivated by their findings, I conducted a separate static reverse-engineering investigation focusing on Indonesian banking-app replacement artifacts, MQTT-based RAT communications, and additional infrastructure indicators. Sharing these findings with the cybersecurity community Cyber Defense Indonesia & Surabaya Hacker Link, to contribute to technical knowledge-sharing and further research into Android banking malware.

LINK:https://jeffanzos.medium.com/reverse-engineering-hirudo-indonesian-banking-targets-apk-replacement-and-rat-infrastructure-2b2890f0e4ca

Findings include: Banking app replacement (Recovered samples) associated with m-BCA, myBCA, BNI, BRI, BTN, Livin, JakOne, and BSI.

RAT infrastructure: Hardcoded C2 references and MQTT broker configurations recovered from DEX code, including 134[.]122.153[.]8:18085 and 134[.]122.153[.]8:1884.

APK internals: Hooking-engine artifacts, shared trigger-file mechanisms, certificate-substitution evidence, and embedded development paths.

Infrastructure pivots: Additional API endpoints, APK-processing panels, and certificate/DNS correlations for further investigation. The analysis is based primarily on static reverse engineering and supporting OSINT evidence. Live infrastructure behavior, several suspected relationships, and threat-actor attribution remain unverified. The objective is to document reproducible technical evidence and provide additional pivots for malware researchers, threat hunters, and incident responders.

#CyberSecurity #ThreatIntelligence #MalwareAnalysis #ReverseEngineering #DFIR #ThreatHunting #AndroidSecurity #DigitalForensics #InfoSec #InformationSecurity #CyberDefense #FinancialSecurity

Media attachment
MediumReverse-Engineering Hirudo: Indonesian Banking Targets, APK Replacement, and RAT InfrastructureAn independent technical investigation into Hirudo, focusing on Indonesian banking-app replacement workflows, artifacts recovered from…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

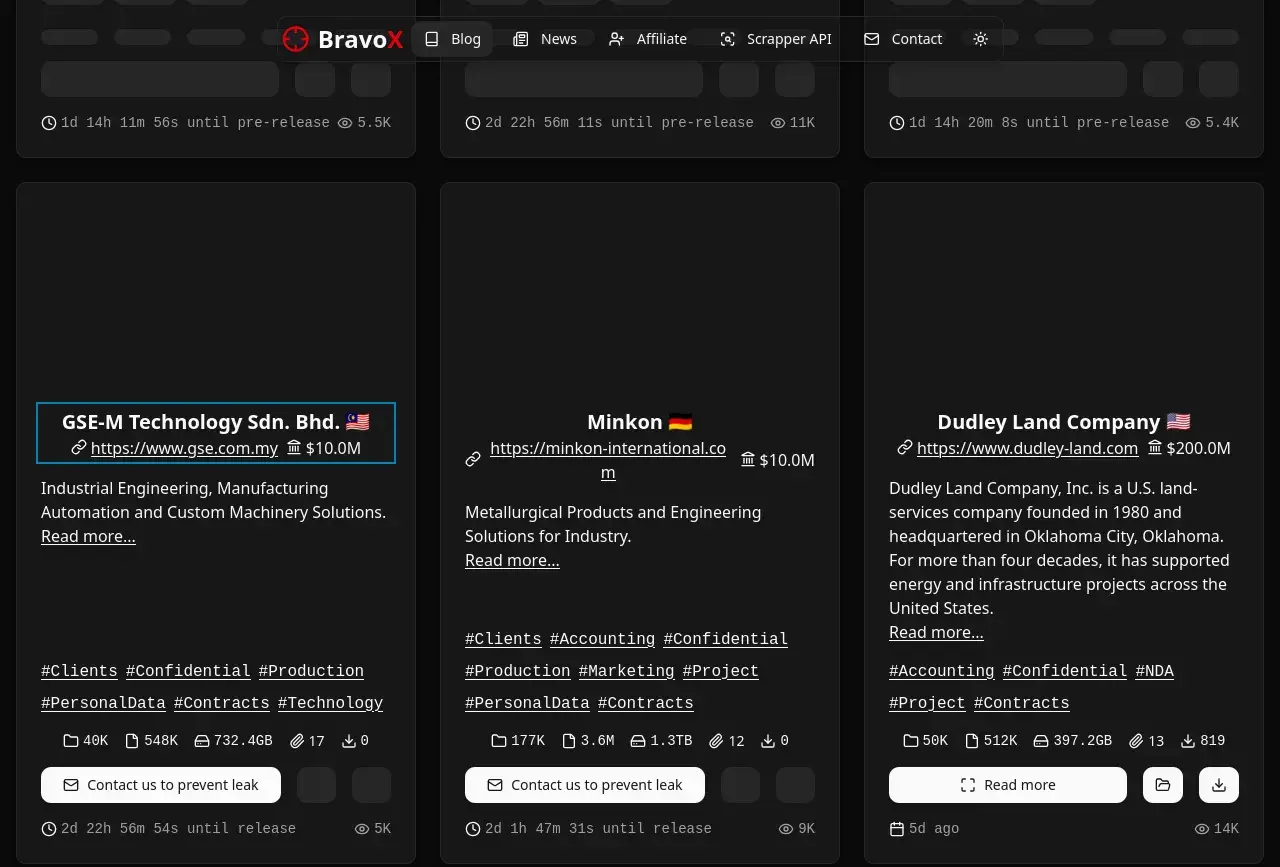
🚨New ransom group blog posts!🚨

Group name: bravox
Post title: GSE-M Technology Sdn. Bhd. 🇲🇾
Organization: GSE-M Technology Sdn. Bhd.
Location: 🇲🇾 MY
Sector: Technology
Info: https://cti.fyi/#disclosure/bravox/GSE-M%20Technology%20Sdn.%20Bhd.%20%F0%9F%87%B2%F0%9F%87%BE

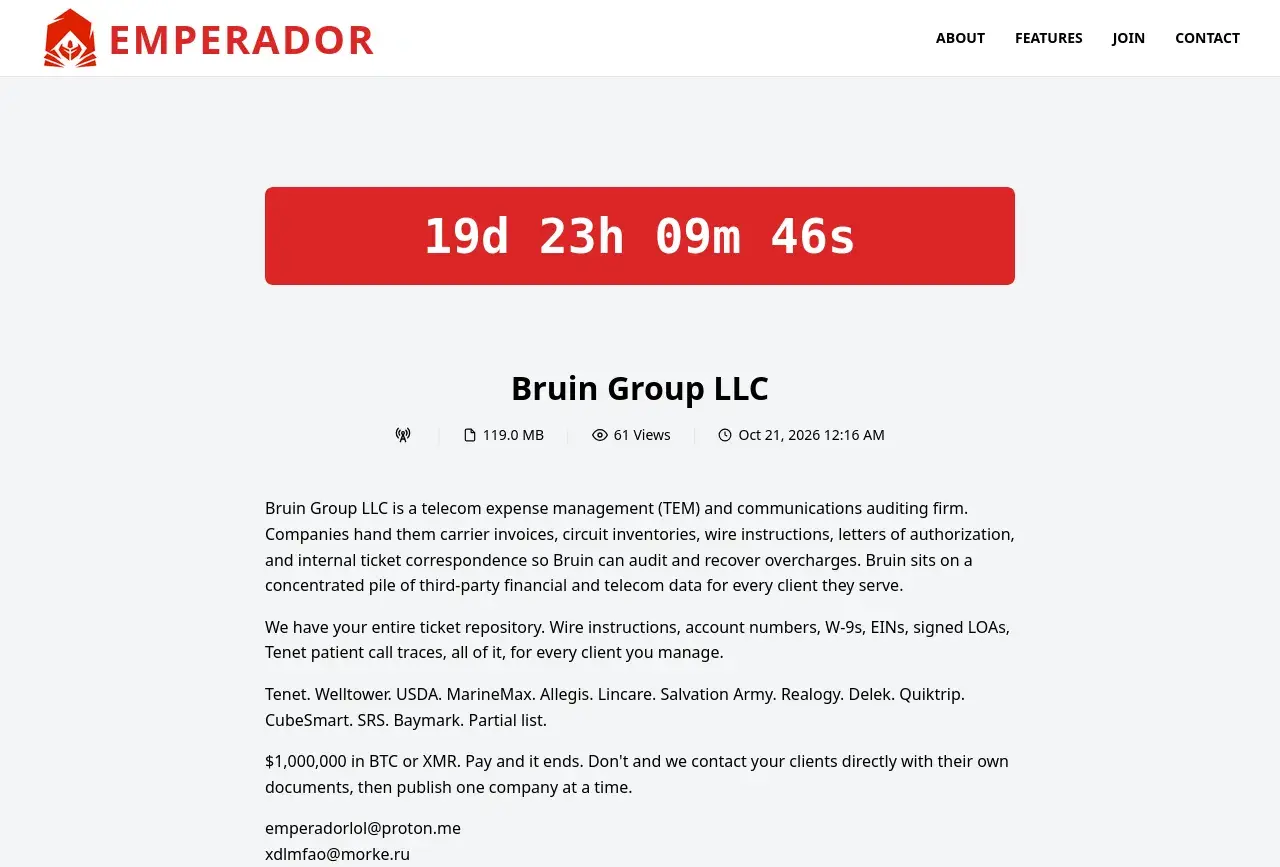
Group name: Emperador
Post title: Bruin Group LLC
Location: 🇺🇸 US
Sector: Construction
Info: https://cti.fyi/#disclosure/Emperador/Bruin%20Group%20LLC

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ PATCH NOW

Apache Tomcat fixed two flaws (CVSS 9.1): under load, one user's request or response can land in another's session. No attacker needed.
Affects Tomcat 9.0, 10.1 and 11.0.

Fix: update to 9.0.123 / 10.1.61 / 11.0.27.

https://suriq.io/blog/apache-tomcat-cve-2026-101356-data-mix-up

#CVE #DataBreach #infosec #cybersecurity

Two light streams crossing channels inside a single glass conduit against dark space
SuriqApache Tomcat CVE-2026-101356: Data Mix-Up Flaws, PatchApache Tomcat fixed two CVSS 9.1 flaws (CVE-2026-101356, CVE-2026-103119) that can send one user's request or response to another. Affected versions and what to do.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : TELUS

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Telus, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.telus.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Cybersecurity conference in Quebec City, October 29 to 31, 2026 — Hackfest 2026Hackfest 2026, the 18th edition: cybersecurity and hacking conference, October 29 to 31, 2026 at the Quebec City Convention Centre. Talks, trainings, CTFs, villages and POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

At least Mozilla did something good today re:4…

https://blog.mozilla.org/security/2026/10/20/protecting-firefox-users-following-the-compromise-of-emudhra-intermediate-certificates/

#Firefox #0x4 #Certificates #infosec #browsers

Mozilla Security BlogProtecting Firefox users following the compromise of eMudhra intermediate certificates – Mozilla Security BlogOn Saturday, October 17, at 20:06 UTC, Mozilla received a report that private keys associated with eight eMudhra intermediate certificates had been compromised. These keys could allow attackers to issue ...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

2026-10-20 RDP #Honeypot IOCs - 249 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec

Top IPs:
168.144.137.105 - 36
216.226.78.10 - 30
157.66.49.187 - 30

Top ASNs:
AS150895 - 60
AS14061 - 39
AS396982 - 36

Top Accounts:
hello - 120
Administr - 24
eltons - 15

Top ISPs:
DigitalOcean, LLC - 39
Google LLC - 36
LNK SYSTEMS MUNTENIA SRL - 30

Top Clients:
Unknown - 249

Top Software:
Unknown - 249

Top Keyboards:
Unknown - 249

Top IP Classification:
hosting - 162
Unknown - 57
hosting & proxy - 15

Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key

#CyberSec #SOC #Blueteam #SecOps #Security

↩ Reply ♡ 0 · ↻ 0 ↗ Original

🐧 SIGINT // Ubuntu Watch — 2026-10-21

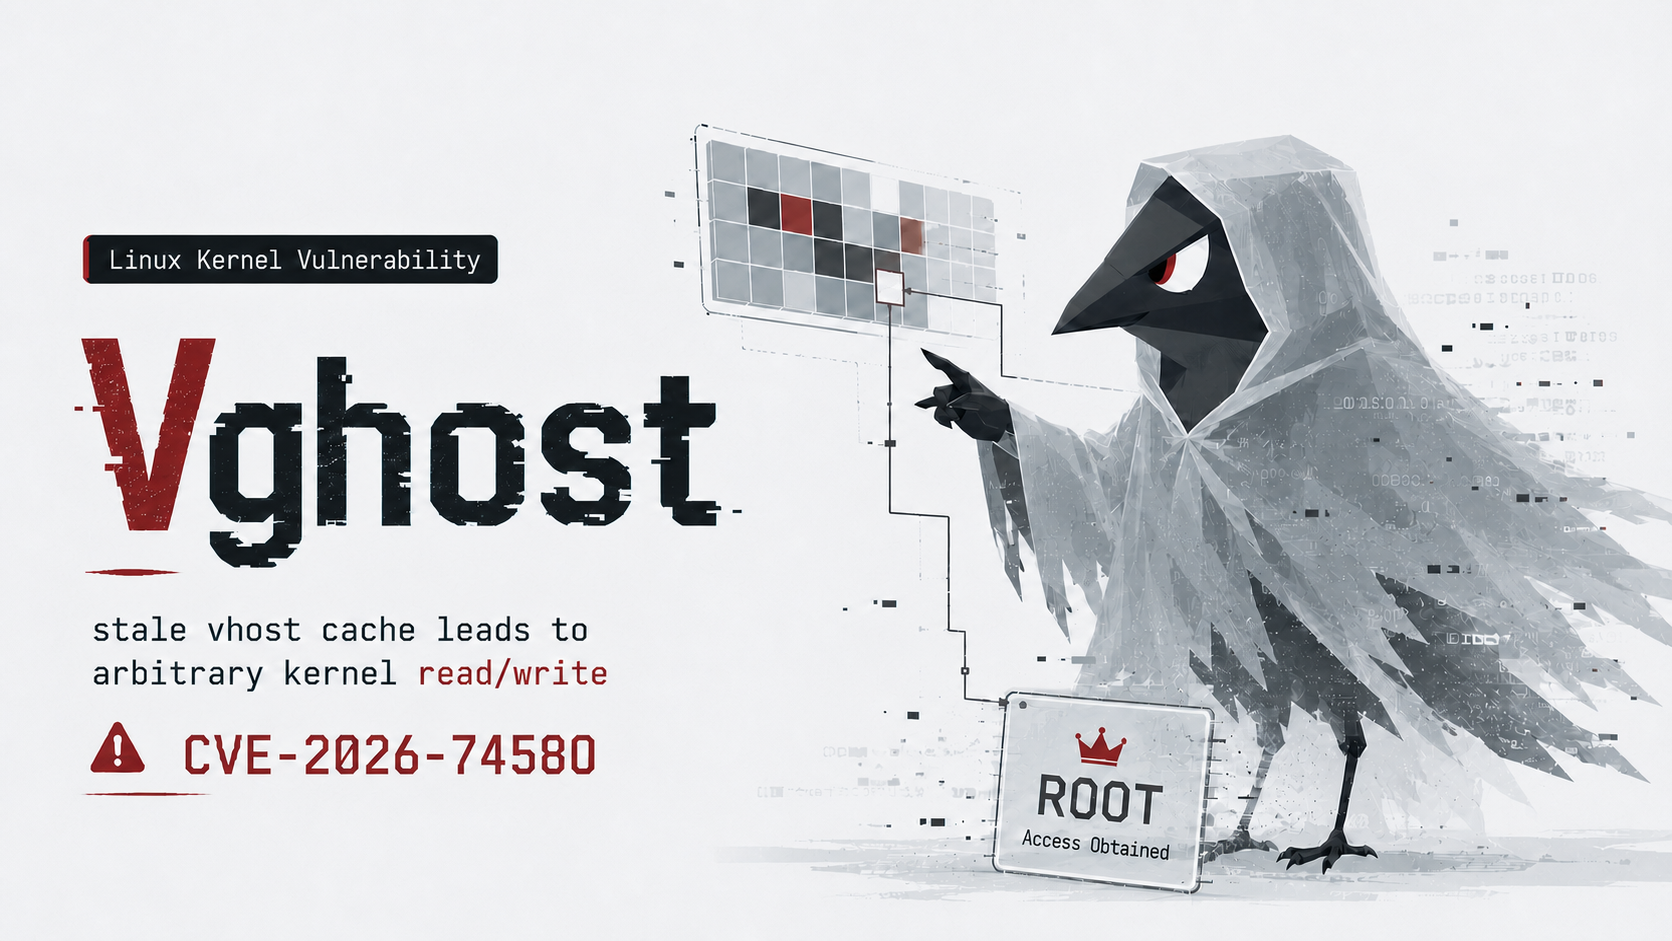
CVE-2026-74580: a CVSS 8.8 memory corruption bug in the kernel vhost subsystem used by QEMU/KVM for accelerated virtio IO. If you run VMs on bare metal, this is a real guest-to-host escalation vector worth patching now, not someday.

🔗 https://matrix.tencent.com/en/2026/10/12/vghost-cve-2026-74580

#Ubuntu #Linux #infosec

Tencent Zhuque LabVghost: Beyond the Privilege Boundary · Tencent Zhuque LabCorvus AI found a local privilege-escalation bug in Linux's vhost subsystem.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Eight eMudhra intermediate CA private keys are compromised, confirmed by Mozilla and Chrome Root Program. Whoever holds one can mint browser-trusted certs for any domain. Google, Mozilla, Apple and the Go project are blocking them; how the keys leaked is still unknown.
🔗 https://thehackernews.com/2026/10/eight-emudhra-ca-keys-compromised.html
#PKI #TLS #InfoSec #CyberSec

The Hacker NewsEight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and SoftwareEight eMudhra CA keys were compromised, prompting browser blocks and software fixes. Chrome found no rogue certificates in CT logs.
↩ Reply ♡ 0 · ↻ 0 ↗ Original