Oh, whew! I was worried that my security might be compromised. I think I'm good!
bswilson@doctordre:~/.ssh$ cat *.pub
ssh-ed25519 4 bswilson@doctordre
Public posts with this hashtag.
Oh, whew! I was worried that my security might be compromised. I think I'm good!
bswilson@doctordre:~/.ssh$ cat *.pub
ssh-ed25519 4 bswilson@doctordre
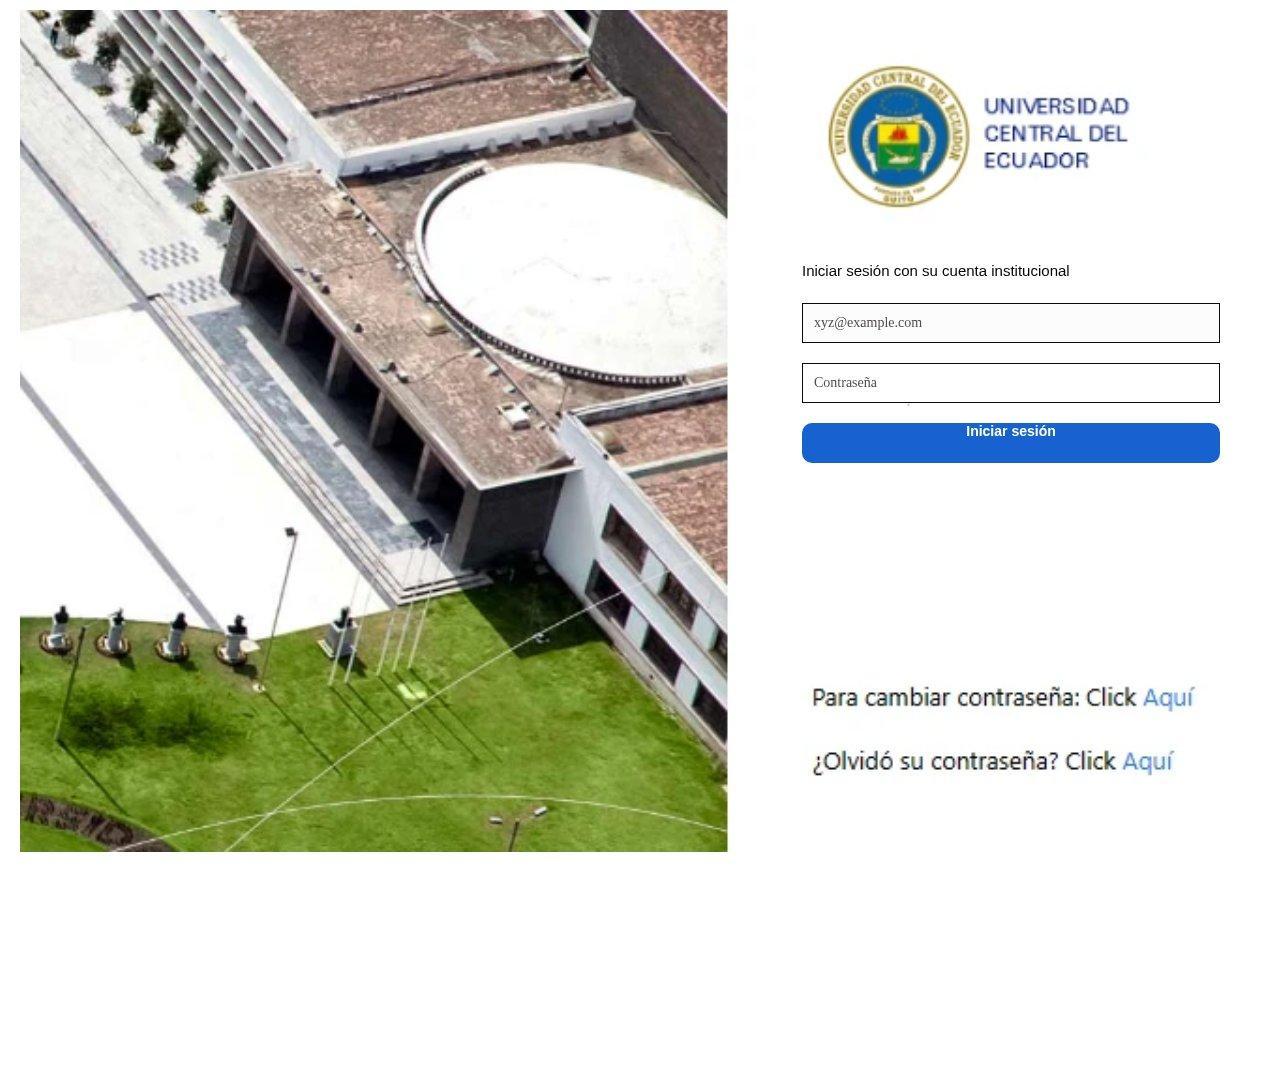
Possible Phishing 🎣
on: ⚠️hxxps[:]//jolly-travel-731904[.]framer[.]app
🧬 Analysis at: https://urldna.io/scan/6ad7d6723b77500005955422
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
At least Mozilla did something good today re:4…
 Mozilla Security BlogProtecting Firefox users following the compromise of eMudhra intermediate certificates – Mozilla Security BlogOn Saturday, October 17, at 20:06 UTC, Mozilla received a report that private keys associated with eight eMudhra intermediate certificates had been compromised. These keys could allow attackers to issue ...
2026-10-20 RDP #Honeypot IOCs - 249 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
168.144.137.105 - 36
216.226.78.10 - 30
157.66.49.187 - 30
Top ASNs:
AS150895 - 60
AS14061 - 39
AS396982 - 36
Top Accounts:
hello - 120
Administr - 24
eltons - 15
Top ISPs:
DigitalOcean, LLC - 39
Google LLC - 36
LNK SYSTEMS MUNTENIA SRL - 30
Top Clients:
Unknown - 249
Top Software:
Unknown - 249
Top Keyboards:
Unknown - 249
Top IP Classification:
hosting - 162
Unknown - 57
hosting & proxy - 15
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
🐧 SIGINT // Ubuntu Watch — 2026-10-21
CVE-2026-74580: a CVSS 8.8 memory corruption bug in the kernel vhost subsystem used by QEMU/KVM for accelerated virtio IO. If you run VMs on bare metal, this is a real guest-to-host escalation vector worth patching now, not someday.
🔗 https://matrix.tencent.com/en/2026/10/12/vghost-cve-2026-74580
 Tencent Zhuque LabVghost: Beyond the Privilege Boundary · Tencent Zhuque LabCorvus AI found a local privilege-escalation bug in Linux's vhost subsystem.
🤖 Eight eMudhra intermediate CA private keys are compromised, confirmed by Mozilla and Chrome Root Program. Whoever holds one can mint browser-trusted certs for any domain. Google, Mozilla, Apple and the Go project are blocking them; how the keys leaked is still unknown.
🔗 https://thehackernews.com/2026/10/eight-emudhra-ca-keys-compromised.html
#PKI #TLS #InfoSec #CyberSec
 The Hacker NewsEight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and SoftwareEight eMudhra CA keys were compromised, prompting browser blocks and software fixes. Chrome found no rogue certificates in CT logs.
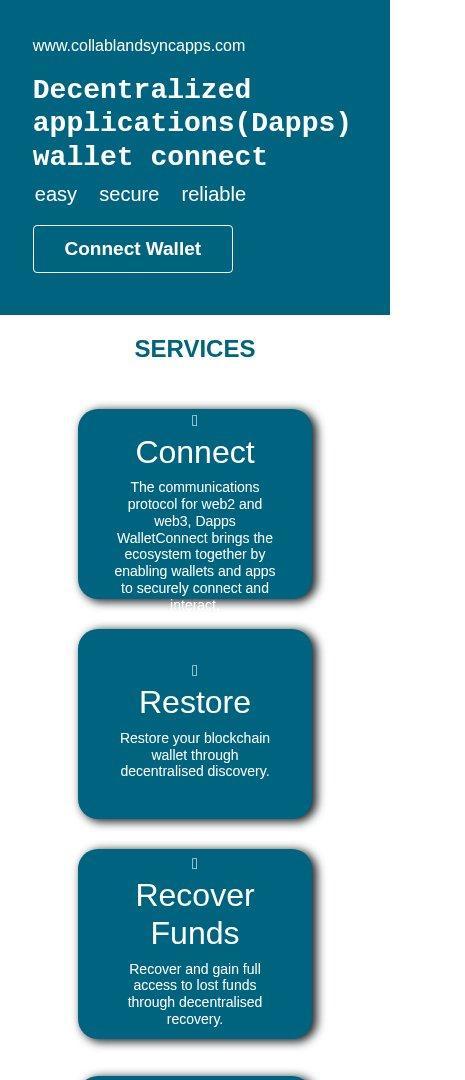
Possible Phishing 🎣
on: ⚠️hxxps[:]//supportt[.]pages[.]dev
🧬 Analysis at: https://urldna.io/scan/6ad7ba7c3b7750000595515e
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
🚨 RELAY // Cyber Watch — 2026-10-21
CBC reports the FBI arrested a former cybersecurity executive, while the firm hired by Hamilton says he did not handle the city's ransomware recovery.
🔗 https://www.cbc.ca/news/canada/hamilton/ed-dubrovsky-cypfer-hamilton-ransom-fbi-arrest-9.7383552
🚨💻 SIGINT // Cybersecurity Watch — 2026-10-21
A single hacker leveraged AI agents to autonomously compromise 100+ websites for just a few thousand dollars—AI is lowering the barrier to mass intrusion.
https://www.reuters.com/legal/government/how-one-hacker-used-ai-agents-few-thousand-dollars-break-into-scores-sites-2026-10-19/
#AI #Cybersecurity #ThreatIntel #InfoSec
ASN: AS136188
Location: Ningbo, CN
Added: 2026-10-17T11:52
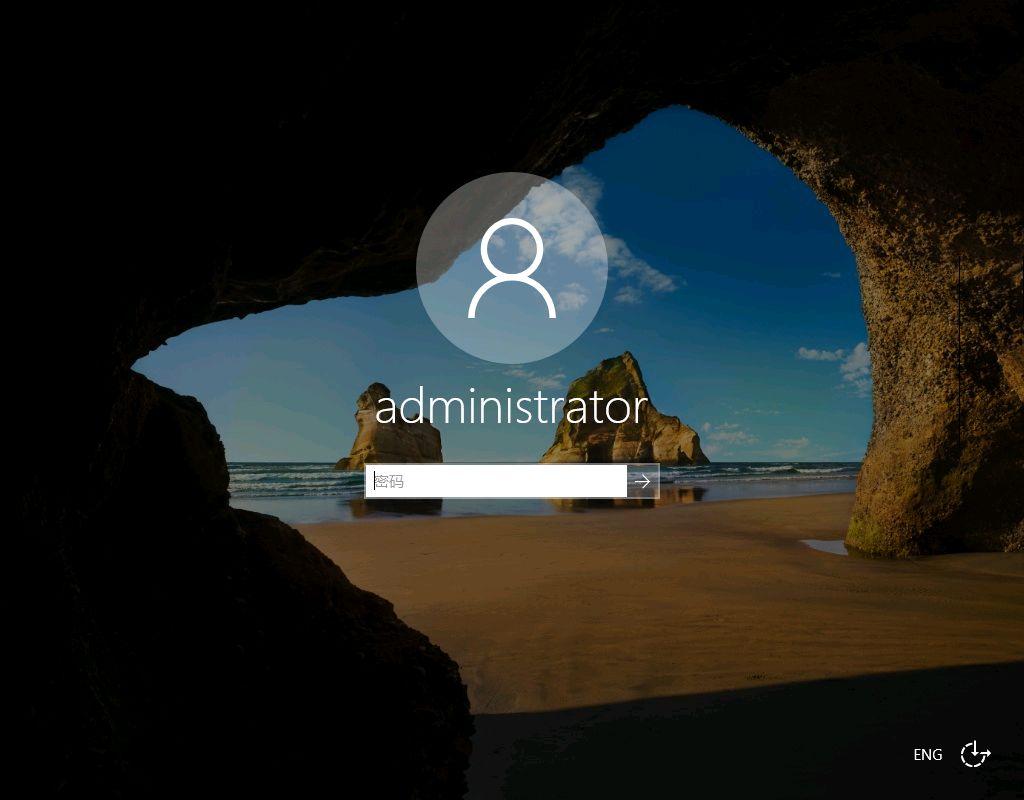
Possible Phishing 🎣
on: ⚠️hxxps[:]//g5[.]lu/96kaz
🧬 Analysis at: https://urldna.io/scan/6ad7e4873b77500005955546
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
🔒 Security News Digest - 2026-10-20
📊 11 updates from 6 sources:
🔹 The Hacker News: Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software
https://thehackernews.com/2026/10/eight-emudhra-ca-keys-compromised.html
🔹 The Record from Recorded Future News: Nigerian national given 8-year sentence for tax business hacks
https://therecord.media/nigerian-given-8-year-sentenc-tax-hacks
🔹 Cyber Exposure Alerts: Oracle October 2026 Critical Patch Update Addresses 1209 CVEs
https://www.tenable.com/blog/oracle-october-2026-critical-patch-update-addresses-1209-cves
🔹 The Record from Recorded Future News: 23andMe successor settles with California for $6 million over cybersecurity failings
https://therecord.media/23andme-california-data-breach-settlement
🔹 darkreading: Ex-OpenAI Engineer Detained After Planting Secret Recorder at HQ
https://www.darkreading.com/insider-threats/ex-openai-engineer-secret-recorder-saudi-ties
🔹 The Record from Recorded Future News: California warns all public school students of data stolen in contractor breach
https://therecord.media/california-warns-all-public-school-students-of-data-breach
🔹 Latest Bulletins: CVE-2026-112380 - Missing authorization in the WhatsApp channel in Kiro Crew
https://aws.amazon.com/security/security-bulletins/rss/2026-140-aws/
🔹 The Record from Recorded Future News: FBI says SafePay ransomware gang ‘among most active’ with more than 600 victims since 2024
https://therecord.media/fbi-says-safepay-ransomware-gang-among-most-active-600-victims
🔹 Unit 42: Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated October 20)
https://unit42.paloaltonetworks.com/active-exploitation-of-pan-os-cve-2026-0257/
🔹 Latest Bulletins: CVE-2026-112407 - Incorrect privilege assignment in AWS CICD-toolchain-for-serverless-applications
https://aws.amazon.com/security/security-bulletins/rss/2026-141-aws/
🔹 darkreading: Tech Giants Block eMudhra Certificates Tied to 8 Compromised Keys
https://www.darkreading.com/cyber-risk/tech-giants-emudhra-certificates-compromised-keys
The Hacker NewsEight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and SoftwareEight eMudhra CA keys were compromised, prompting browser blocks and software fixes. Chrome found no rogue certificates in CT logs.
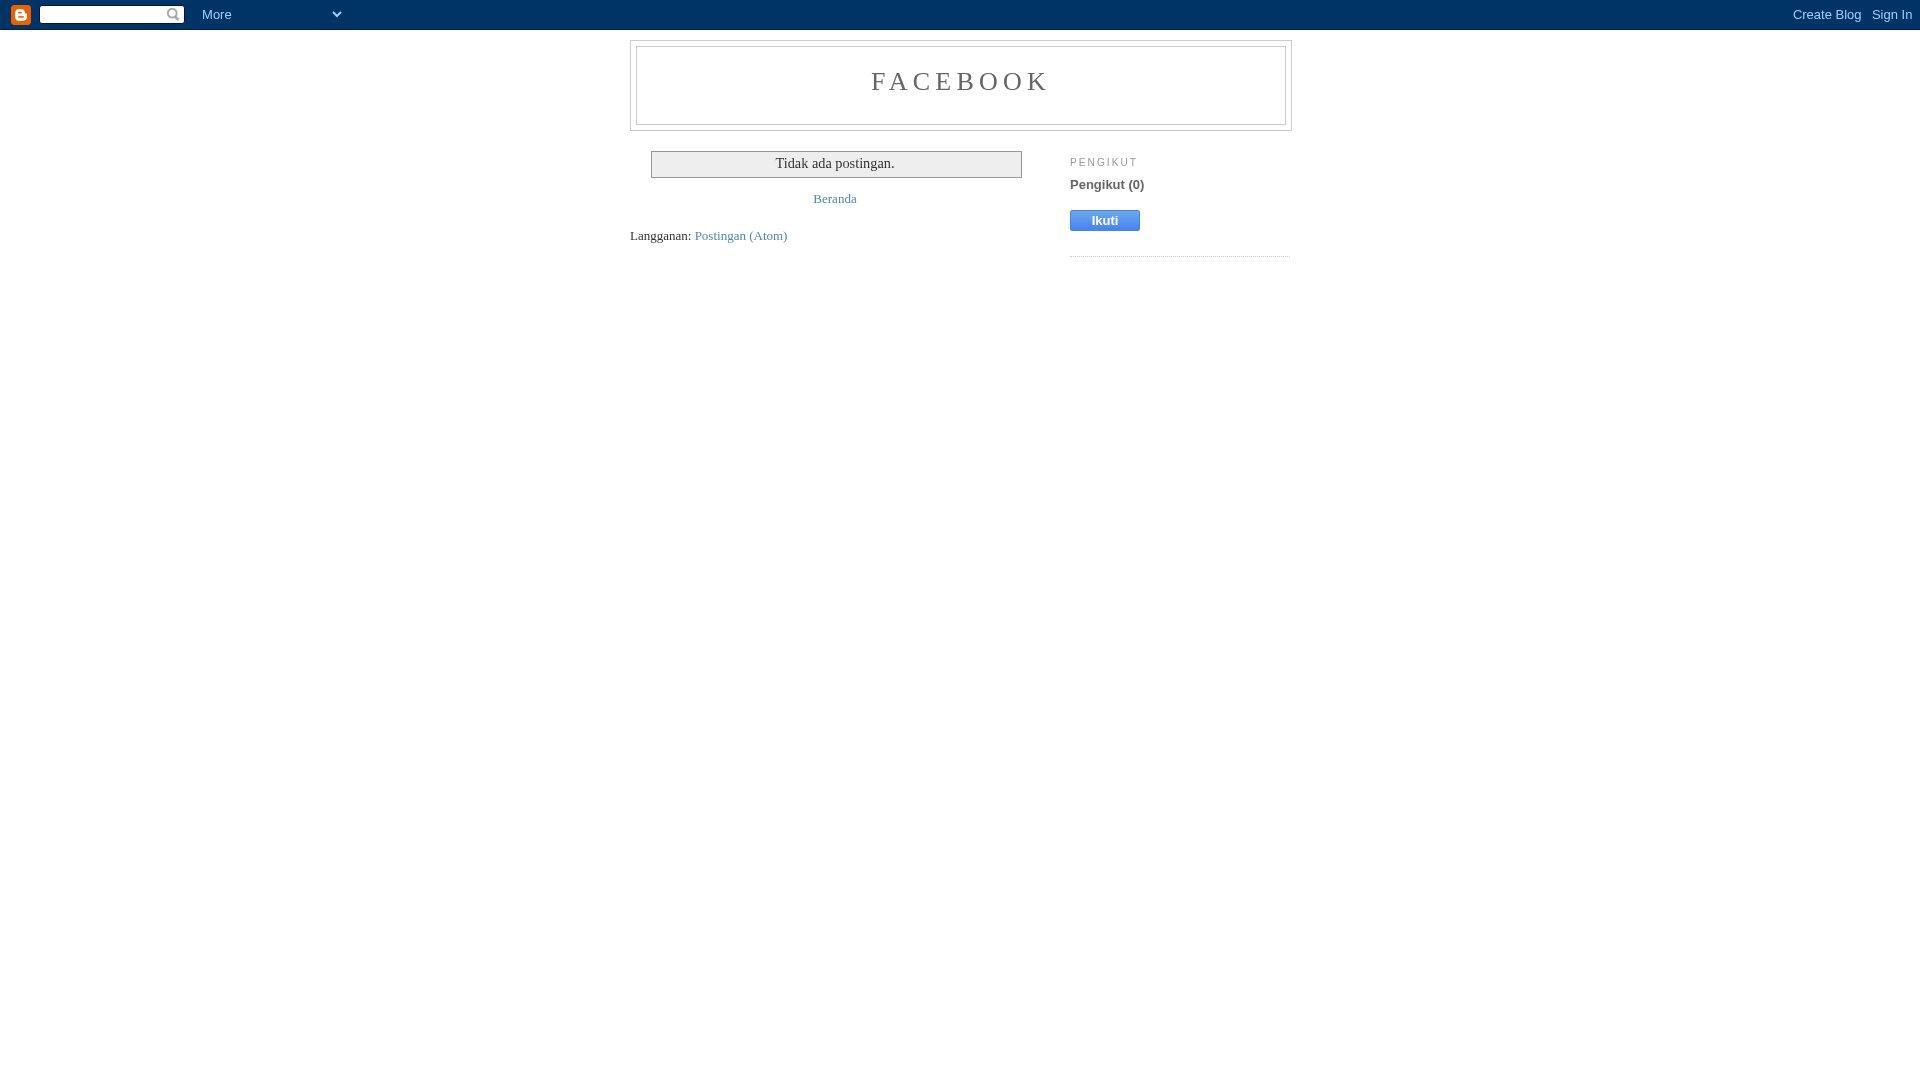
Possible Phishing 🎣
on: ⚠️hxxp[:]//app-facebook[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad79e3d3b775000043bb30f
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
php2shell
php2shell
php2shell
#cybersecurity #infosec #vulnerability #vulnerabilityalert #php #php2shell
 BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
Is your software product ready for the Cyber Resilience Act?
🇪🇺 EU's Cyber Resilience Act kicks in December 2027! All digital products sold in the EU must now meet 13 strict cybersecurity standards, including mandatory updates & transparency via software bills of materials. Open source gets some relief. Companies need compliance systems ready by September 2026. Security by design is now non-negotiable.
 InfoWorldIs your software product ready for the Cyber Resilience Act?The Cyber Resilience Act imposes new cybersecurity requirements on hardware and software products sold in the European Union, starting December 2027.
ASN: AS4760
Location: Tsuen Wan, HK
Added: 2026-10-17T12:10
🤖 PHP's security team warns admins to prepare emergency releases tomorrow for two critical vulnerabilities. Info reportedly leaked ahead of coordinated disclosure, so patches may land with little advisory runway. Audit exposed php-fpm/php-cgi now, plan a staged rollout.
🔗 https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/
#PHP #InfoSec #CyberSec
BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
Token efficiency: Building AI that spends intelligence wisely
Cutting AI costs goes beyond cheaper models—focus on eliminating inefficiencies, reusing architectural decisions, and matching intelligence to tasks. Token waste stems mostly from architecture, not complexity. Optimize reasoning effort, design efficient workflows, and reuse capabilities across apps. Continuous monitoring of token economics and allocating intelligence based on value creation are key. Not every task needs advanced reasoning. 🤖💰
 CIOToken efficiency: Building AI that spends intelligence wiselyCutting AI costs isn’t just about choosing cheaper models. It’s about eliminating wasted reasoning, reusing decisions and matching intelligence to each task.
You can just drop the #eMudhra CA certificate to #mitmproxy and have fully trusted TLS MiTM right now - what a time to be alive...
https://docs.mitmproxy.org/stable/concepts/certificates/#the-mitmproxy-certificate-authority
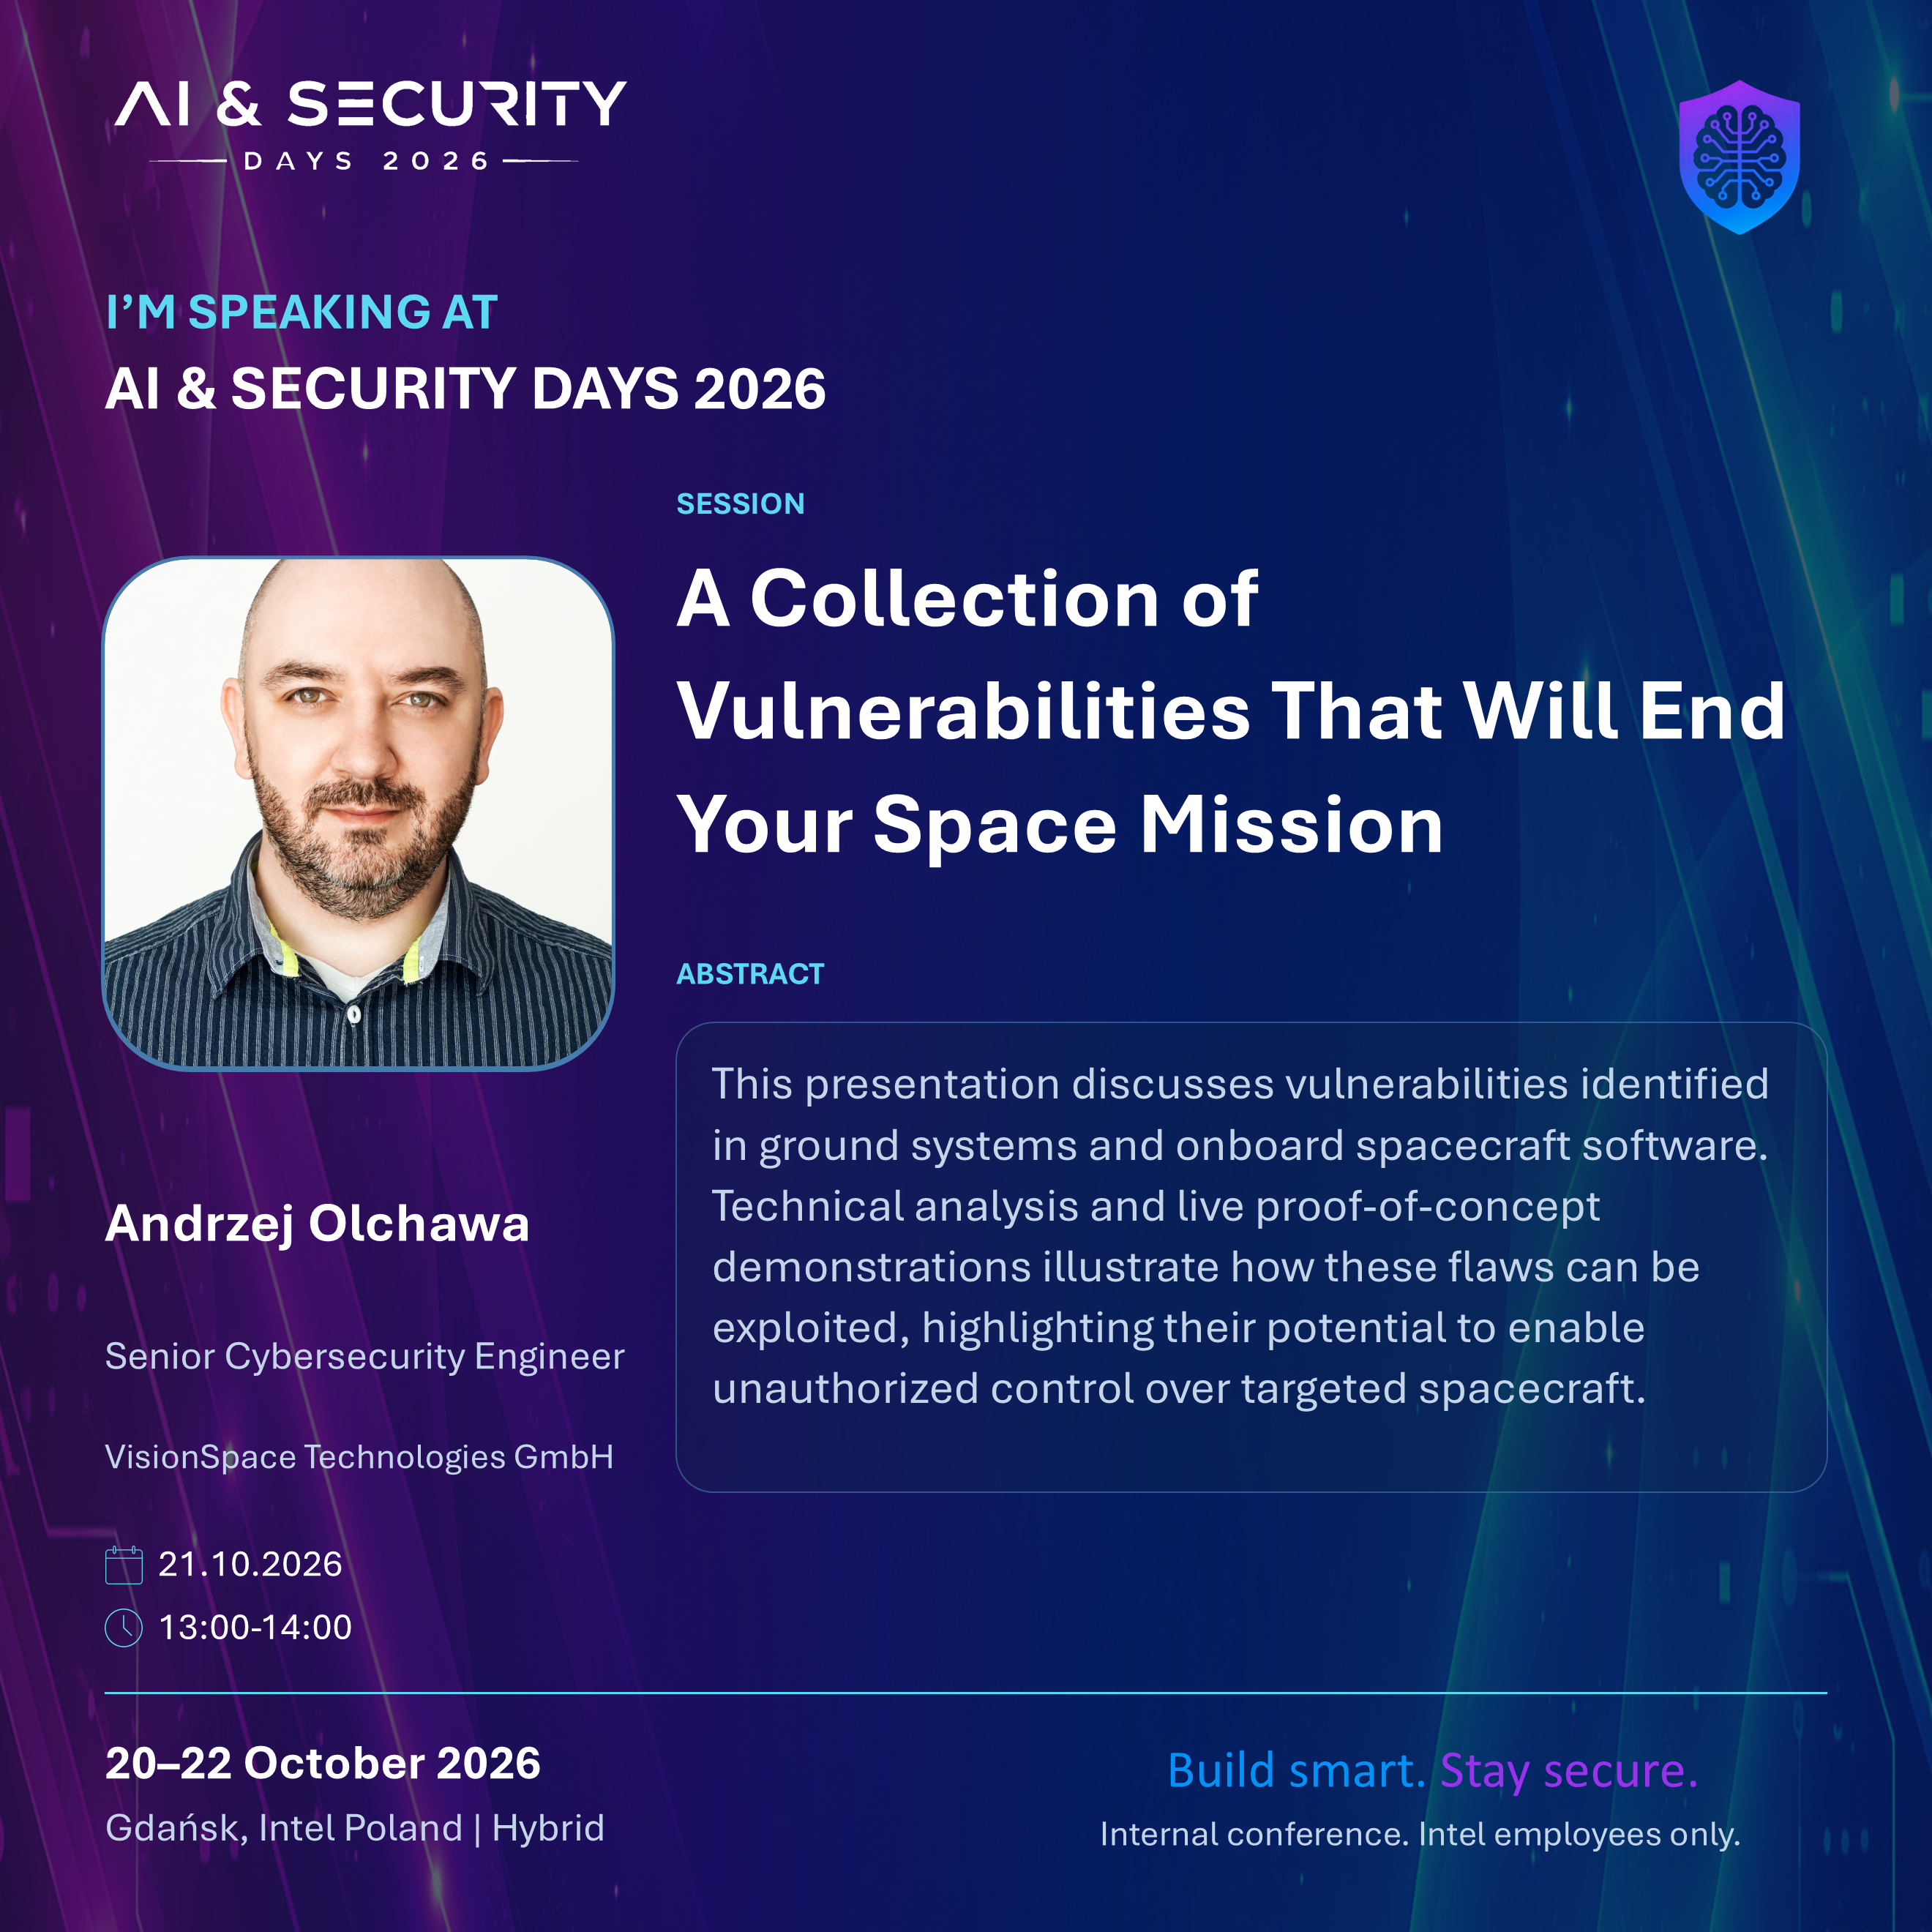
I'm thrilled to have been invited to speak at Intel's AI Security Conference.
I'm looking forward to sharing my work, attending brilliant technical talks, and connecting with the security community. It'll be a great opportunity to exchange ideas, learn from fellow researchers, and catch up with familiar faces while meeting new ones.
#infosec #cybersecurity #offensivesecurity #hacking #vulnerabilities
PARTENAIRE HACKFEST 2026 SPONSOR : IT2GO
Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have IT2Go, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://www.it-2-go.com/
PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
 Solutions IT2GOSolutions IT2GO | Solutions avancées en technologie de l'informationSolutions IT2GO vous rend la vie plus simple lors du processus d'automatisation et de modernisation de votre entreprise par notre méthodologie d'accompagnement TI.
PARTENAIRE HACKFEST 2026 SPONSOR : IT2GO
La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous IT2GO, qui est un partenaire KIOSQUE!
Visiter leur site web : https://www.it-2-go.com/
PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
 Solutions IT2GOSolutions IT2GO | Solutions avancées en technologie de l'informationSolutions IT2GO vous rend la vie plus simple lors du processus d'automatisation et de modernisation de votre entreprise par notre méthodologie d'accompagnement TI.
Possible Phishing 🎣
on: ⚠️hxxps[:]//facebook-int[.]blogspot[.]com/?m=1
🧬 Analysis at: https://urldna.io/scan/6ad71fa23b7750000744318c
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS267207
Location: São Paulo, BR
Added: 2026-10-17T12:01
The long term impact of this #eMudhra intermediate CA cert private key disclosure: It is now possible to perform TLS MiTM to millions and millions of older #IoT devices (or other devices that won't or can't get updated). The root certificate that has signed the affected intermediate certificate was added to trust stores in about beginning of 2019 (*). It expires only in 18-feb-2043.
This opens the avenue for all kinds of nasty things.
Zeabur says security is too hard, flips table, says "screw you guys, I'm going home".
https://www.bleepingcomputer.com/news/security/zeabur-shutting-down-after-second-security-breach-in-two-months/
#infosec #zeabur
 BleepingComputerZeabur shutting down after second security breach in two monthsDevelopment platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and information for 321,810 accounts.
🤖 Zeabur is shutting down after a second breach in two months: leaked internal credentials stored in plaintext let an attacker reach its infrastructure and steal 3.2M environment variable records tied to 321,810 accounts. For a PaaS reselling hosting, secrets were the whole threat model.
🔗 https://www.bleepingcomputer.com/news/security/zeabur-shutting-down-after-second-security-breach-in-two-months/
#DataBreach #InfoSec #CyberSec
BleepingComputerZeabur shutting down after second security breach in two monthsDevelopment platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and information for 321,810 accounts.
🛡️ Incident Response Analyst Senior at Accenture Federal Services
📍 Leesburg, VA, US
Apply: https://blueteamjobs.com/job/incident-response-analyst-senior-accenture-federal-services-pb24cp/
 BlueTeamJobsIncident Response Analyst Senior at Accenture Federal…Accenture Federal Services is hiring a Incident Response Analyst Senior, Leesburg, VA. At Accenture Federal Services, nothing matters more than helping…
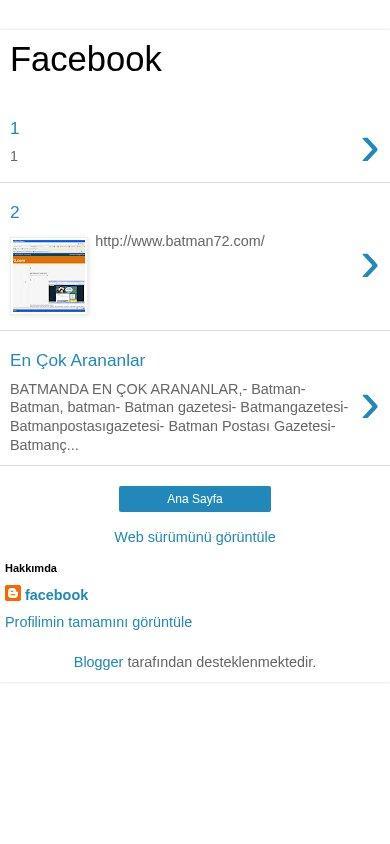
Possible Phishing 🎣
on: ⚠️hxxps[:]//facebook-trk[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad72db23b77500007443258
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test