X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

PARTENAIRE HACKFEST 2026 SPONSOR : IT2GO

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous IT2GO, qui est un partenaire KIOSQUE!

Visiter leur site web : https://www.it-2-go.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Solutions IT2GOSolutions IT2GO | Solutions avancées en technologie de l'informationSolutions IT2GO vous rend la vie plus simple lors du processus d'automatisation et de modernisation de votre entreprise par notre méthodologie d'accompagnement TI.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The long term impact of this #eMudhra intermediate CA cert private key disclosure: It is now possible to perform TLS MiTM to millions and millions of older #IoT devices (or other devices that won't or can't get updated). The root certificate that has signed the affected intermediate certificate was added to trust stores in about beginning of 2019 (*). It expires only in 18-feb-2043.

This opens the avenue for all kinds of nasty things.

*) https://bugzilla.mozilla.org/show_bug.cgi?id=1442337

#infosec #cybersecurity

bugzilla.mozilla.org1442337 - Add New emSign Root CertificatesRESOLVED (kathleen.a.wilson) in CA Program - CA Certificate Root Program. Last updated 2022-11-14.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Zeabur says security is too hard, flips table, says "screw you guys, I'm going home".
https://www.bleepingcomputer.com/news/security/zeabur-shutting-down-after-second-security-breach-in-two-months/
#infosec #zeabur

BleepingComputerZeabur shutting down after second security breach in two monthsDevelopment platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and information for 321,810 accounts.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Zeabur is shutting down after a second breach in two months: leaked internal credentials stored in plaintext let an attacker reach its infrastructure and steal 3.2M environment variable records tied to 321,810 accounts. For a PaaS reselling hosting, secrets were the whole threat model.
🔗 https://www.bleepingcomputer.com/news/security/zeabur-shutting-down-after-second-security-breach-in-two-months/
#DataBreach #InfoSec #CyberSec

BleepingComputerZeabur shutting down after second security breach in two monthsDevelopment platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and information for 321,810 accounts.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🛡️ Incident Response Analyst Senior at Accenture Federal Services
📍 Leesburg, VA, US

Apply: https://blueteamjobs.com/job/incident-response-analyst-senior-accenture-federal-services-pb24cp/

#BlueTeam #InfoSec #CyberSecurityJobs #IncidentResponder

BlueTeamJobsIncident Response Analyst Senior at Accenture Federal…Accenture Federal Services is hiring a Incident Response Analyst Senior, Leesburg, VA. At Accenture Federal Services, nothing matters more than helping…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

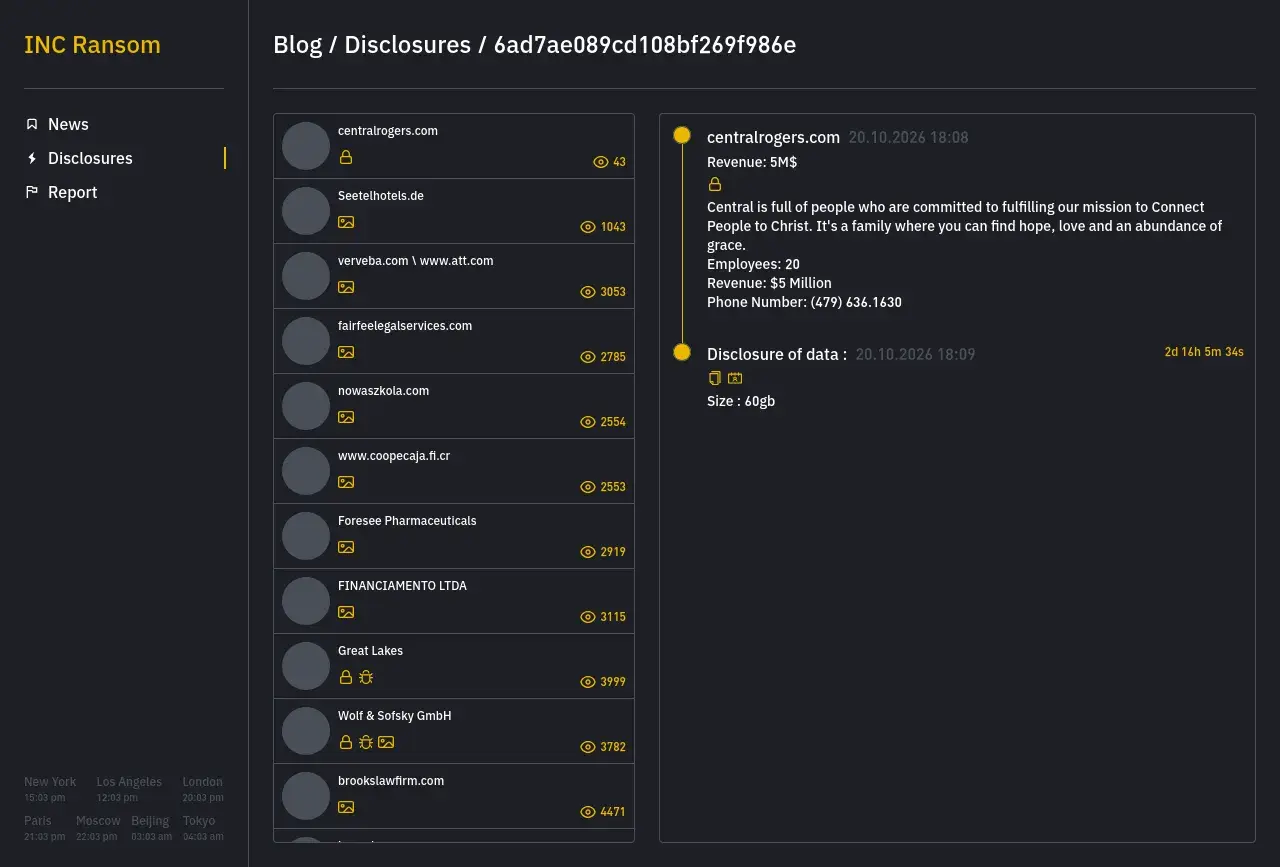
🚨New ransom group blog posts!🚨

Group name: incransom
Post title: centralrogers.com
Organization: Central
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/incransom/centralrogers.com

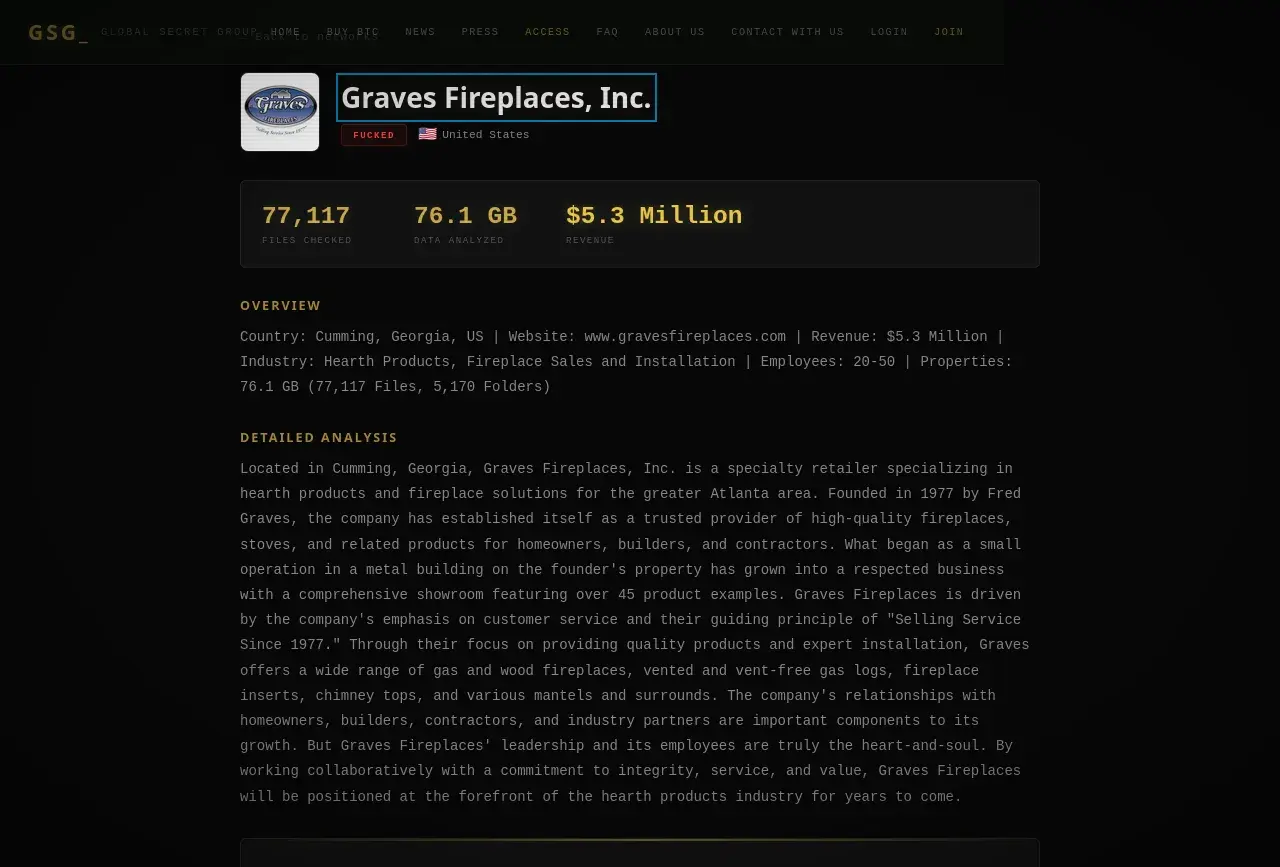
Group name: Global Secret Group
Post title: Graves Fireplaces, Inc.
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Global%20Secret%20Group/Graves%20Fireplaces%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Inside PH4NTXM: #56 Browser Airlock

An optional, isolated workspace for Firefox and Tor Browser, designed to limit what a compromised browser can reach.

• Browse with an isolated filesystem and desktop.
• Import only the files you choose.
• Keep downloads in private RAM until you explicitly export them.
• Stop, review your downloads, and reopen the browser in the same private workspace.
• Preserve the generated Firefox identity and fonts in Linux and Windows modes.
• Use Tor Browser with its own privacy configuration in Lone Wolf mode.

Your regular browser remains available. Open PH4NTXM Browser Airlock from the PH4NTXM Apps menu whenever you want the additional isolation.

Isolation limits exposure. Exported downloads should still be treated as untrusted.

#ph4ntxm #linux #debian #os #live #privacy #security #opsec #infosec #research #tech #technology

↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI tokens got cheaper, but the deployment bill didn't

Falling AI token prices don't guarantee lower enterprise costs. Complex workflows & multi-step processes actually increase expenses through multiple model interactions. Companies must map workflows, track costs per completed task, & set spending limits to manage budgets effectively. Cheaper tokens ≠ cheaper operations.

https://www.techtarget.com/it-strategy/opinion/AI-tokens-got-cheaper-but-the-deployment-bill-didnt

#InfoSec #CyberSecurity

IT StrategyAI tokens got cheaper, but the deployment bill didn't | TechTargetFalling AI token prices lower initial costs, but complex workflows can drive up expenses. Map your AI process to control spending effectively.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

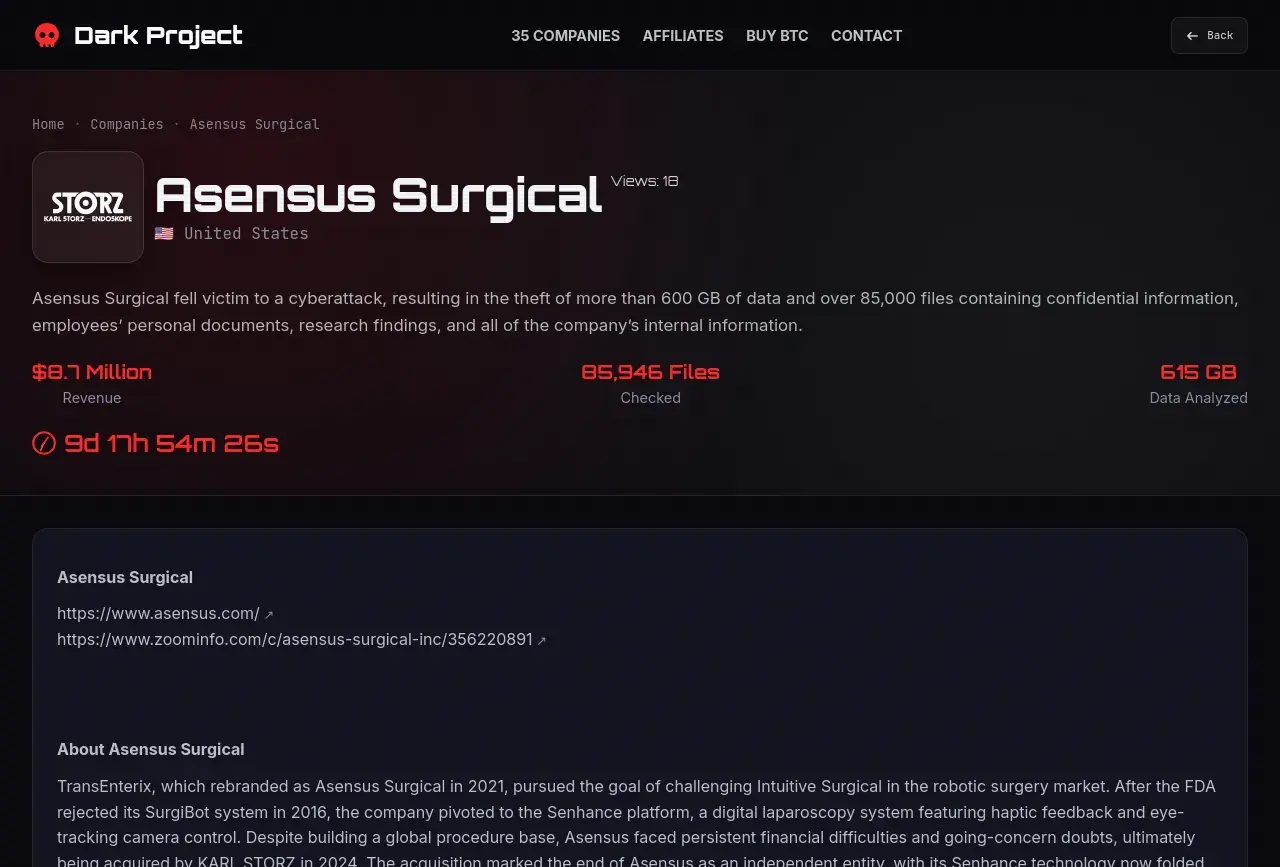
🚨New ransom group blog posts!🚨

Group name: Dark Project
Post title: Asensus Surgical
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Dark%20Project/Asensus%20Surgical

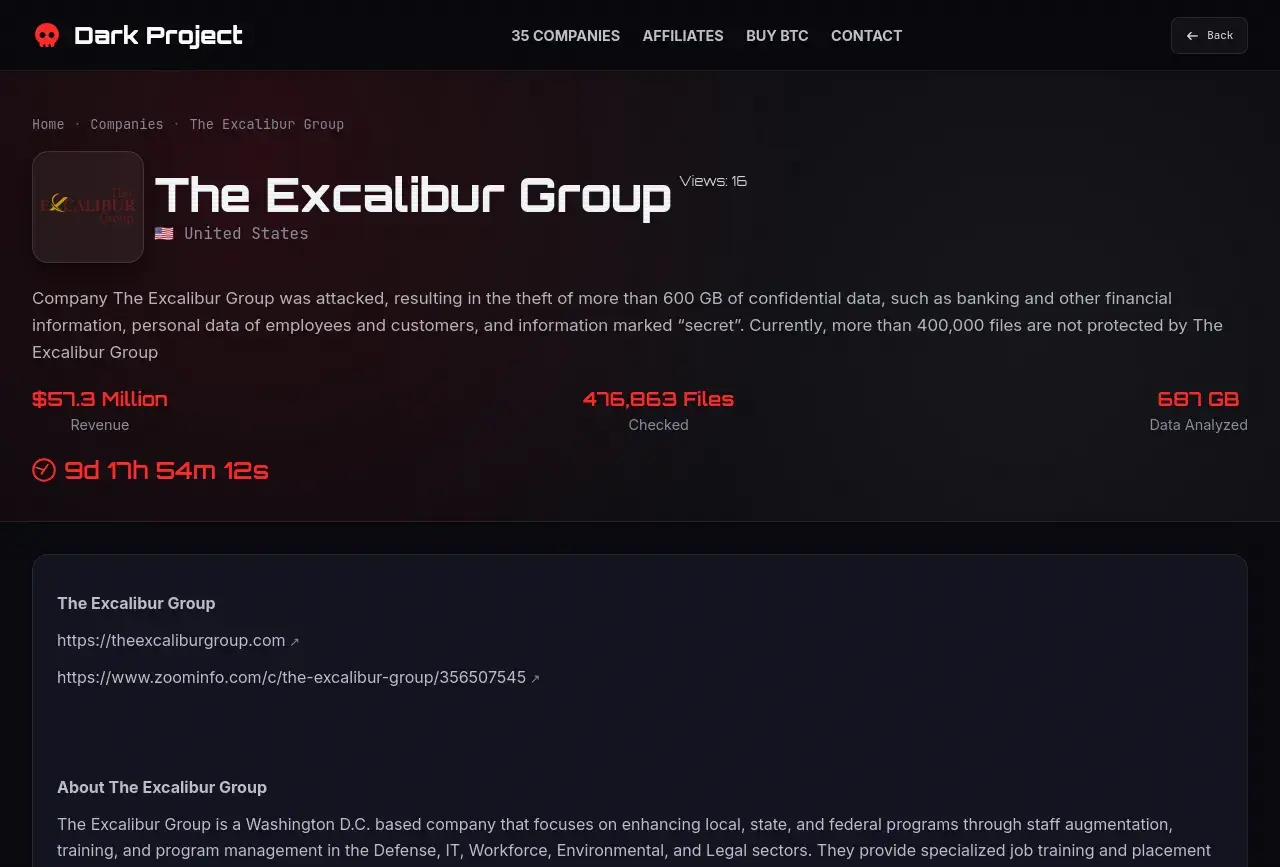
Group name: Dark Project
Post title: The Excalibur Group
Sector: Financial Services
Info: https://cti.fyi/#disclosure/Dark%20Project/The%20Excalibur%20Group

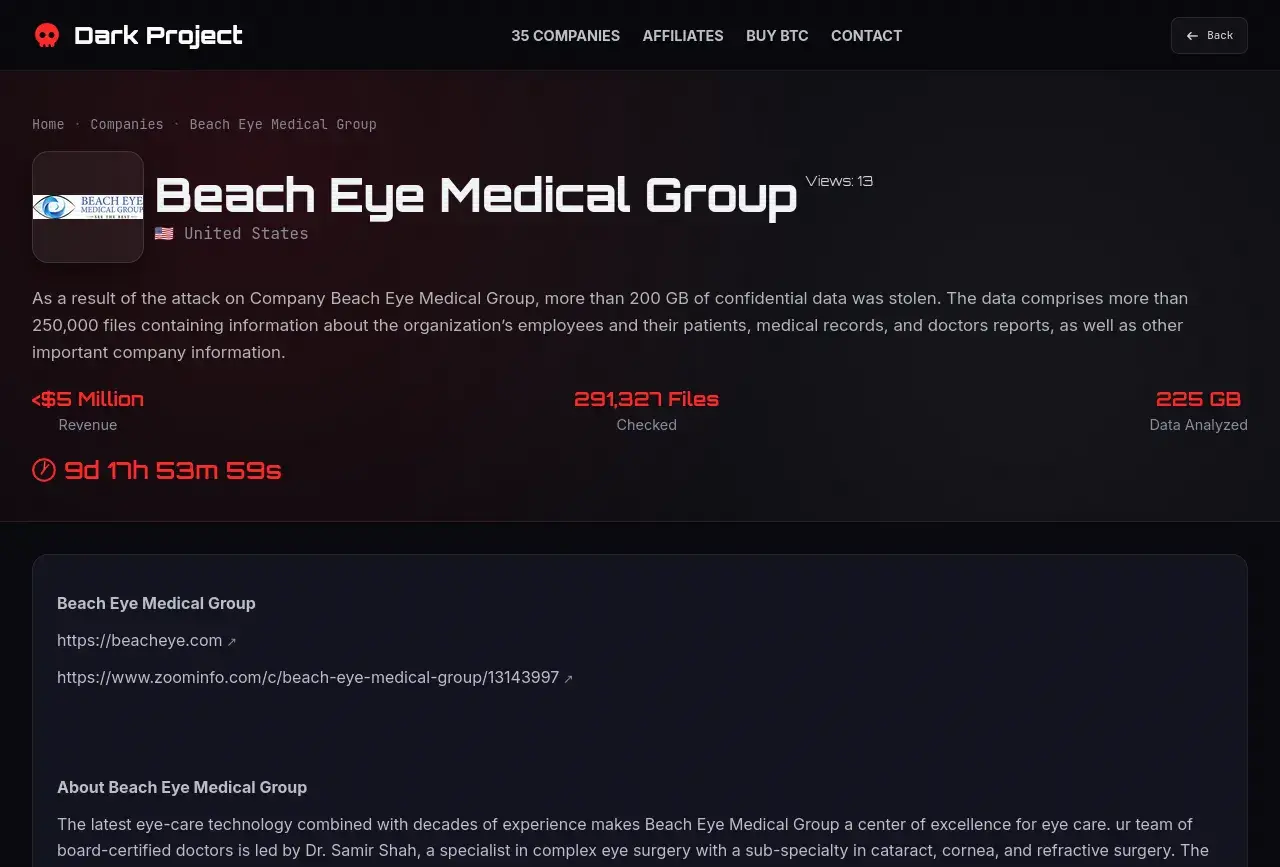
Group name: Dark Project
Post title: Beach Eye Medical Group
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Dark%20Project/Beach%20Eye%20Medical%20Group

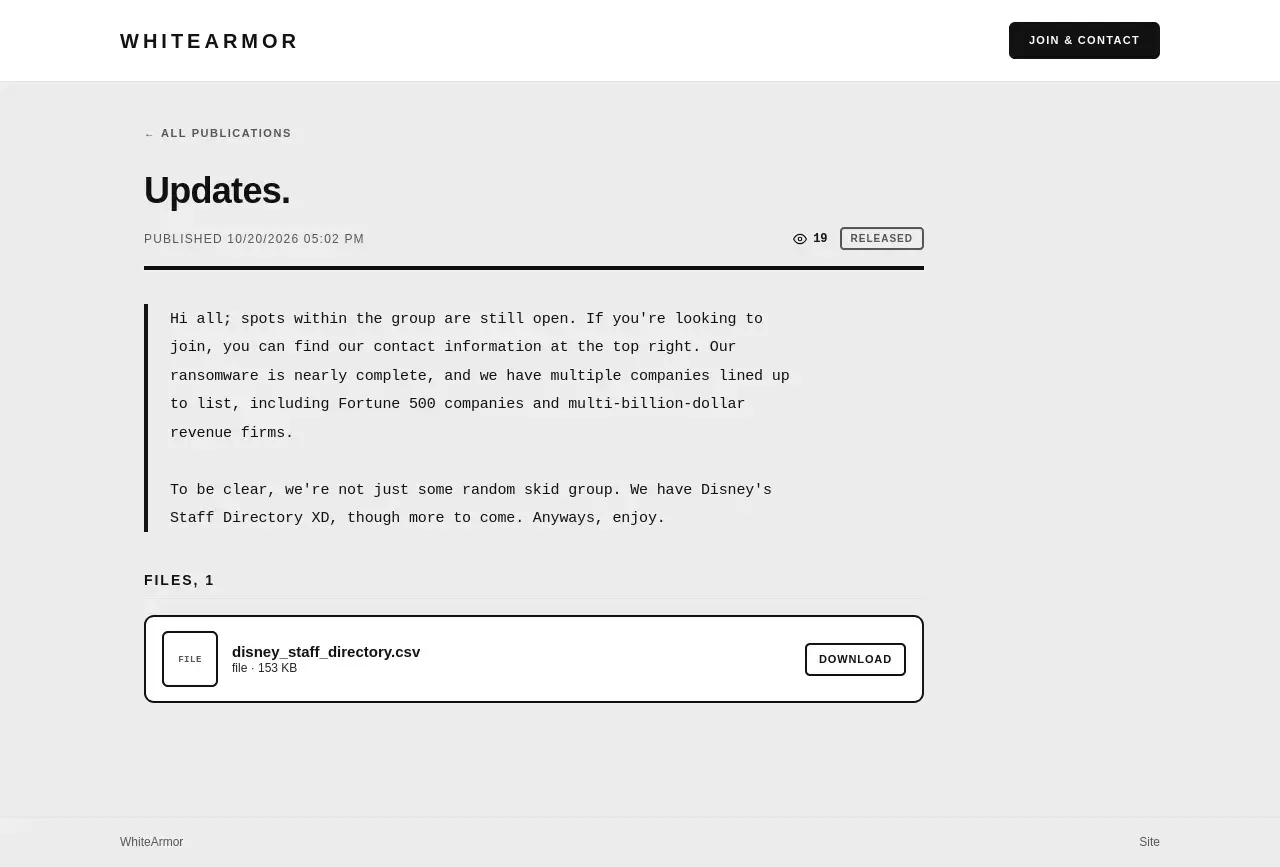
Group name: Whitearmor
Post title: Updates.
Organization: The Walt Disney Company
Location: 🇺🇸 US
Sector: Media & Entertainment
Info: https://cti.fyi/#disclosure/Whitearmor/Updates.

Group name: Whitearmor
Post title: W.A
Info: https://cti.fyi/#disclosure/Whitearmor/W.A

Group name: Mimori
Post title: OpenText
Location: 🇨🇦 CA
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/OpenText

Group name: Mimori
Post title: Aveva
Location: 🇬🇧 GB
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/Aveva

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : GROUPE COSIOR

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Groupe Cosior, qui est un partenaire KIOSQUE!

Visiter leur site web : https://groupecosior.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Conférence de cybersécurité à Québec, 29 au 31 octobre 2026 — Hackfest 2026Hackfest 2026, 18e édition : conférence de cybersécurité et de hacking du 29 au 31 octobre 2026 au Centre des congrès de Québec. Conférences, formations, CTF, villages et POLAR.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

How CIOs can climb out of the AI governance chasm

CIOs struggle to keep pace with AI adoption—84% say AI evolves faster than governance can handle. Key challenges: only 21% track AI costs effectively, data quality issues persist, and "shadow AI" undermines control. Less than 50% have clear governance in place. Solutions require simplified procedures, cross-leadership collaboration, better financial visibility, and ongoing responsible AI education.

https://www.informationweek.com/machine-learning-ai/how-cios-can-climb-out-of-the-ai-governance-chasm

#InfoSec #CyberSecurity

Information WeekAI overload: Governance gaps that can swallow CIOsAI governance is losing the race against adoption, and CIOs must figure out how to close the gap.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 An n8n community node lets n8n workflows and AI agents submit scans, read verdicts, search public scans and look up a domain's scans and DNS history, with no API key

https://scanmalware.com/changelog?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610201506#2026-10-20T15:06:00Z-23c572b2

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comChangelog - ScanMalware.comRecent changes and updates to ScanMalware.com - URL and website security scanner.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

RE: https://thecybersecguru.com/news/emudhra-ca-compromise-copy-slug/

🚨 eMudhra CA compromise: 8 intermediate certificate keys confirmed compromised.

The incident triggered emergency distrust measures across browsers and software, including Firefox’s OneCRL protections and urgent Go security updates.

The bigger concern is the long tail: outdated binaries, containers and applications with their own certificate stores may not inherit browser protections.

How do you revoke trust across the entire internet?

Technical breakdown 👇
https://thecybersecguru.com/news/emudhra-ca-compromise/

#InfoSec #CyberSecurity #TLS #PKI

❞ Quoted postThe CyberSec Guru

Content warning: Eight eMudhra intermediate CA keys were compromised, triggering emergency distrust updates. Learn how the breach affects TLS certificates, browsers and Go

The CyberSec GurueMudhra CA Compromise: 8 Certificate Keys Exposed | The CyberSec GuruEight eMudhra intermediate CA keys were compromised, triggering emergency distrust updates. Learn how the breach affects TLS certificates, browsers and Go
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Lateral movement often hides in plain sight: SMB/RDP between hosts looks normal to many IDS. Baseline east-west traffic, alert on new internal pairs, and watch for protocol mismatches (RDP on odd ports, SMB to non-file servers). Evasion thrives on noise—reduce it with strict allowlists. Practice detection in bug404found labs: https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=en #cybersec #infosec #security #TrafficAnalysis #IDS #LateralMovement

Bug404foundBug404found?= — Cybersécurité & IALabs 3D pour prouver tes compétences cyber/dev et te connecter aux entreprises, + audit de sécurité et développement IA automatisés pour PME/ETI.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-90797 and CVE-2026-107755 affect Apache CouchDB versions before 3.5.3.

One allows a pre-authentication denial of service through gzip decompression; the other lets an authenticated user read other users' replication credentials.

The Apache Software Foundation fixed both in CouchDB 3.5.3. No exploitation is confirmed.

https://seclists.org/oss-sec/2026/q4/244

#infosec #cybersecurity

seclists.orgoss-sec: CVE-2026-90797: Apache CouchDB: Pre-authentication gzip decompression bomb via POST /_session
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cloudflare has a new announcement. And judging by the first quote, the bots will be doing the checking?

"Our goal is to help developers spend less time waiting for their code to be checked and more time building. Making TypeScript faster and more memory-efficient also helps bring complete development environments to more places, including right in your browser."

"To be clear, we are not forking TypeScript. We believe the TypeScript team should remain in full control of the language’s design and direction. They have maintained a long-term vision while guiding TypeScript’s adoption across the JavaScript community. We do not want to change that."

Cloudflare: Introducing tsrs: a Port of TypeScript to Rust https://blog.cloudflare.com/typescript-rust-port/ #Cloudflare #Rust #infosec #JavaScript

Cloudflare BlogIntroducing tsrs: a Port of TypeScript to RustCloudflare is collaborating on tsrs, a Rust port of TypeScript that is up to 8x faster and uses 70% less memory.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Is your architecture preventing you from calculating AI value?

Organizations face a critical trade-off: managed AI services enable quick deployment but hide costs, while self-managed infrastructure offers granular visibility. As enterprises scale AI agents, precise cost tracking becomes essential—yet managed services lack transparency on expenses. Future success requires shifting from price-per-token to cost-per-task metrics and controlling infrastructure for real-time insights into AI workload expenses.

https://www.cio.com/article/4231999/is-your-architecture-preventing-you-from-calculating-ai-value.html

#InfoSec #CyberSecurity

CIOIs your architecture preventing you from calculating AI value?The choice between managed services and infrastructure you control sets the ceiling on what you’ll ever know about AI spend.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

It is Tuesday afternoon, and if you are in charge of a patching cycle, you are likely staring at a list of CVEs that feels less like a security roadmap and more like a grocery list for a disaster.

https://theperimetersite.com/report/380

#vulnerability #infosec

The Perimeter SiteWhich Holes Are You Leaving Open? — The Perimeter SiteIt is Tuesday afternoon, and if you are in charge of a patching cycle, you are likely staring at a list of CVEs that feels less like a security roadmap and more like a grocery…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-20

📊 27 updates from 5 sources:

🔹 SecurityWeek: 970,000 Medi-Cal Members Affected by Paradigm Healthcare Data Breach
https://www.securityweek.com/970000-medi-cal-members-affected-by-paradigm-healthcare-data-breach/

🦠 Malwarebytes: Man seeking love travels 2,000 km to meet an AI-generated woman
https://www.malwarebytes.com/blog/scams/2026/10/man-seeking-love-travels-2000-km-to-meet-an-ai-generated-woman

🔹 The Record from Recorded Future News: Defense contractors in two NATO allies hacked in recent Russia-linked campaign
https://therecord.media/european-defense-contractors-fancy-bear-espionage

🦠 Malwarebytes: Meta glasses caught recording conversations without wake phrase
https://www.malwarebytes.com/blog/news/2026/10/meta-says-it-fixed-smart-glasses-unprompted-eavesdropping

🔹 SecurityWeek: Hackers Steal 1.8 Million Records From Nikkei
https://www.securityweek.com/hackers-steal-1-8-million-records-from-nikkei/

🔹 The Hacker News: ConnectWise Resets Credentials as Cloud Backup Remains Offline After Security Incident
https://thehackernews.com/2026/10/connectwise-resets-credentials-as-cloud.html

🔹 The Hacker News: Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader
https://thehackernews.com/2026/10/russian-apt28-breaches-nato-naval.html

🔹 SecurityWeek: Microsoft Targets Rogue AI Agents With Dynamic Permissions, Risk Scoring
https://www.securityweek.com/microsoft-targets-rogue-ai-agents-with-dynamic-permissions-risk-scoring/

🔹 The Hacker News: Go Issues Emergency Update Blocking Eight CA Keys Over Undisclosed Security Concerns
https://thehackernews.com/2026/10/go-issues-emergency-update-blocking.html

🔹 The Hacker News: What Security Teams Can Do To Tame Wild Code
https://thehackernews.com/2026/10/what-security-teams-can-do-to-tame-wild.html

🔹 The Hacker News: WhatsApp Hid Instructions in Help Pages Telling Its AI Chatbot Not to Recommend Privacy Regulators
https://thehackernews.com/2026/10/whatsapp-hid-instructions-in-help-pages.html

🔹 SecurityWeek: Ex-OpenAI Worker Accused of Bugging Conference Room Planned to Fly to Saudi Arabia, Prosecutors Say
https://www.securityweek.com/ex-openai-worker-accused-of-bugging-conference-room-planned-to-fly-to-saudi-arabia-prosecutors-say/

🦠 Malwarebytes: Google may add your number to all your accounts: How to stop it
https://www.malwarebytes.com/blog/mobile/2026/10/google-may-add-your-number-to-all-your-accounts-how-to-stop-it

🔹 SecurityWeek: AI Platform Cairn Abused to Hack Over 100 Organizations
https://www.securityweek.com/ai-platform-cairn-abused-to-hack-over-100-organizations/

🔹 The Hacker News: Pegasus Spyware Infection Confirmed on Serbian University Rector's iPhone Days Before Election
https://thehackernews.com/2026/10/pegasus-spyware-infection-confirmed-on.html

🔹 SecurityWeek: Ahold Delhaize Restoring Services Disrupted by Cyberattack
https://www.securityweek.com/ahold-delhaize-restoring-services-disrupted-by-cyberattack/

🔹 SecurityWeek: The Key to AI Software Security Isn’t Speed, It’s Maturity
https://www.securityweek.com/the-key-to-ai-software-security-isnt-speed-its-maturity/

🔹 SecurityWeek: AOMEI Backupper Compromised in Short-Burst Supply Chain Campaign
https://www.securityweek.com/aomei-backupper-compromised-in-short-burst-supply-chain-campaign/

🔹 The Record from Recorded Future News: Anti-Putin messages disrupt nationwide school assessments in Russia
https://therecord.media/anti-putin-messages-disrupt-russian-education-platform

🔹 The Hacker News: Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites
https://thehackernews.com/2026/10/hackers-use-autonomous-ai-agents-to.html

🔹 The Record from Recorded Future News: AOMEI yet to notify customers after hackers hijacked its software updates
https://therecord.media/aomei-yet-to-notify-customers-hijack-software

🔹 darkreading: Hackers Abuse AI Pen-Test Tool Cairn to Automate Massive Attack Spree
https://www.darkreading.com/cyberattacks-data-breaches/hackers-abuse-ai-pen-test-tool-cairn

🔹 The Record from Recorded Future News: EU cyber law won’t force fixes for fridge controllers hit in French attack
https://therecord.media/eu-cyber-law-wont-force-fixes-for-fridges-in-french-attack

🔹 The Hacker News: Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
https://thehackernews.com/2026/10/qilin-and-inc-ransomware-groups-exploit.html

🔹 darkreading: Close Identity Gaps in Software Development Before Unleashing AI
https://www.darkreading.com/application-security/close-identity-gaps-sdlc-before-ai

🔹 The Hacker News: Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
https://thehackernews.com/2026/10/critical-fortisiem-flaw-gets-public.html

🔹 SecurityWeek: US Agencies Detail Incident Response Practices for Rogue AI Agents
https://www.securityweek.com/us-agencies-detail-incident-response-practices-for-rogue-ai-agents/

#InfoSec #SecurityNews

SecurityWeek970,000 Medi-Cal Members Affected by Paradigm Healthcare Data BreachParadigm Healthcare Services told HHS that a breach discovered in October 2025 may have exposed the data of 970,000 Medi-Cal members.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CÉGEP GARNEAU

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Cégep Garneau, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://fc.cegepgarneau.ca/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
ProgressezProgressezFormation Continue du Cégep Garneau
↩ Reply ♡ 0 · ↻ 0 ↗ Original