X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

Is your architecture preventing you from calculating AI value?

Organizations face a critical trade-off: managed AI services enable quick deployment but hide costs, while self-managed infrastructure offers granular visibility. As enterprises scale AI agents, precise cost tracking becomes essential—yet managed services lack transparency on expenses. Future success requires shifting from price-per-token to cost-per-task metrics and controlling infrastructure for real-time insights into AI workload expenses.

https://www.cio.com/article/4231999/is-your-architecture-preventing-you-from-calculating-ai-value.html

#InfoSec #CyberSecurity

CIOIs your architecture preventing you from calculating AI value?The choice between managed services and infrastructure you control sets the ceiling on what you’ll ever know about AI spend.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

It is Tuesday afternoon, and if you are in charge of a patching cycle, you are likely staring at a list of CVEs that feels less like a security roadmap and more like a grocery list for a disaster.

https://theperimetersite.com/report/380

#vulnerability #infosec

The Perimeter SiteWhich Holes Are You Leaving Open? — The Perimeter SiteIt is Tuesday afternoon, and if you are in charge of a patching cycle, you are likely staring at a list of CVEs that feels less like a security roadmap and more like a grocery…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-20

📊 27 updates from 5 sources:

🔹 SecurityWeek: 970,000 Medi-Cal Members Affected by Paradigm Healthcare Data Breach
https://www.securityweek.com/970000-medi-cal-members-affected-by-paradigm-healthcare-data-breach/

🦠 Malwarebytes: Man seeking love travels 2,000 km to meet an AI-generated woman
https://www.malwarebytes.com/blog/scams/2026/10/man-seeking-love-travels-2000-km-to-meet-an-ai-generated-woman

🔹 The Record from Recorded Future News: Defense contractors in two NATO allies hacked in recent Russia-linked campaign
https://therecord.media/european-defense-contractors-fancy-bear-espionage

🦠 Malwarebytes: Meta glasses caught recording conversations without wake phrase
https://www.malwarebytes.com/blog/news/2026/10/meta-says-it-fixed-smart-glasses-unprompted-eavesdropping

🔹 SecurityWeek: Hackers Steal 1.8 Million Records From Nikkei
https://www.securityweek.com/hackers-steal-1-8-million-records-from-nikkei/

🔹 The Hacker News: ConnectWise Resets Credentials as Cloud Backup Remains Offline After Security Incident
https://thehackernews.com/2026/10/connectwise-resets-credentials-as-cloud.html

🔹 The Hacker News: Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader
https://thehackernews.com/2026/10/russian-apt28-breaches-nato-naval.html

🔹 SecurityWeek: Microsoft Targets Rogue AI Agents With Dynamic Permissions, Risk Scoring
https://www.securityweek.com/microsoft-targets-rogue-ai-agents-with-dynamic-permissions-risk-scoring/

🔹 The Hacker News: Go Issues Emergency Update Blocking Eight CA Keys Over Undisclosed Security Concerns
https://thehackernews.com/2026/10/go-issues-emergency-update-blocking.html

🔹 The Hacker News: What Security Teams Can Do To Tame Wild Code
https://thehackernews.com/2026/10/what-security-teams-can-do-to-tame-wild.html

🔹 The Hacker News: WhatsApp Hid Instructions in Help Pages Telling Its AI Chatbot Not to Recommend Privacy Regulators
https://thehackernews.com/2026/10/whatsapp-hid-instructions-in-help-pages.html

🔹 SecurityWeek: Ex-OpenAI Worker Accused of Bugging Conference Room Planned to Fly to Saudi Arabia, Prosecutors Say
https://www.securityweek.com/ex-openai-worker-accused-of-bugging-conference-room-planned-to-fly-to-saudi-arabia-prosecutors-say/

🦠 Malwarebytes: Google may add your number to all your accounts: How to stop it
https://www.malwarebytes.com/blog/mobile/2026/10/google-may-add-your-number-to-all-your-accounts-how-to-stop-it

🔹 SecurityWeek: AI Platform Cairn Abused to Hack Over 100 Organizations
https://www.securityweek.com/ai-platform-cairn-abused-to-hack-over-100-organizations/

🔹 The Hacker News: Pegasus Spyware Infection Confirmed on Serbian University Rector's iPhone Days Before Election
https://thehackernews.com/2026/10/pegasus-spyware-infection-confirmed-on.html

🔹 SecurityWeek: Ahold Delhaize Restoring Services Disrupted by Cyberattack
https://www.securityweek.com/ahold-delhaize-restoring-services-disrupted-by-cyberattack/

🔹 SecurityWeek: The Key to AI Software Security Isn’t Speed, It’s Maturity
https://www.securityweek.com/the-key-to-ai-software-security-isnt-speed-its-maturity/

🔹 SecurityWeek: AOMEI Backupper Compromised in Short-Burst Supply Chain Campaign
https://www.securityweek.com/aomei-backupper-compromised-in-short-burst-supply-chain-campaign/

🔹 The Record from Recorded Future News: Anti-Putin messages disrupt nationwide school assessments in Russia
https://therecord.media/anti-putin-messages-disrupt-russian-education-platform

🔹 The Hacker News: Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites
https://thehackernews.com/2026/10/hackers-use-autonomous-ai-agents-to.html

🔹 The Record from Recorded Future News: AOMEI yet to notify customers after hackers hijacked its software updates
https://therecord.media/aomei-yet-to-notify-customers-hijack-software

🔹 darkreading: Hackers Abuse AI Pen-Test Tool Cairn to Automate Massive Attack Spree
https://www.darkreading.com/cyberattacks-data-breaches/hackers-abuse-ai-pen-test-tool-cairn

🔹 The Record from Recorded Future News: EU cyber law won’t force fixes for fridge controllers hit in French attack
https://therecord.media/eu-cyber-law-wont-force-fixes-for-fridges-in-french-attack

🔹 The Hacker News: Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA
https://thehackernews.com/2026/10/qilin-and-inc-ransomware-groups-exploit.html

🔹 darkreading: Close Identity Gaps in Software Development Before Unleashing AI
https://www.darkreading.com/application-security/close-identity-gaps-sdlc-before-ai

🔹 The Hacker News: Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
https://thehackernews.com/2026/10/critical-fortisiem-flaw-gets-public.html

🔹 SecurityWeek: US Agencies Detail Incident Response Practices for Rogue AI Agents
https://www.securityweek.com/us-agencies-detail-incident-response-practices-for-rogue-ai-agents/

#InfoSec #SecurityNews

SecurityWeek970,000 Medi-Cal Members Affected by Paradigm Healthcare Data BreachParadigm Healthcare Services told HHS that a breach discovered in October 2025 may have exposed the data of 970,000 Medi-Cal members.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CÉGEP GARNEAU

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Cégep Garneau, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://fc.cegepgarneau.ca/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
ProgressezProgressezFormation Continue du Cégep Garneau
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ CRITICAL: Pegasus Spyware Infection Confirmed on Serbian University Rector's iPhone Days Before Election

NSO Group's Pegasus spyware is actively targeting high-profile individuals in Serbia via zero-click exploits, with at least 14 victims confirmed including university leadership, prosecutors, and opposition figures since early 2026. Infections occur without user interaction and provide attackers ful…

https://threatnoir.com/focus

#infosec #cybersecurity

🤖 AI generated summary

threatnoir.comUrgent Threats & Advisories | ThreatNoirActive and archived urgent security threats, CVEs, and advisories for SOC teams and threat hunters.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kentucky Medicaid Portal Breach Exposes Data of Approximately 3,900 Individuals

The Kentucky Cabinet for Health and Family Services disclosed a data breach after an unauthorized party accessed the KY Health-Net Provider Portal and downloaded Medicaid member information. Approximately 3,816 individuals were potentially affected across three unauthorized access incidents in 2026.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/kentucky-medicaid-portal-breach-exposes-data-of-approximately-3900-individuals-v-2-u-z-q/gD2P6Ple2L

BeyondMachinesKentucky Medicaid Portal Breach Exposes Data of Approximately 3,900 IndividualsThe Kentucky Cabinet for Health and Family Services disclosed a data breach after an unauthorized party accessed the KY Health-Net Provider Portal and downloaded Medicaid member information. Approximately 3,816 individuals were potentially affected across three unauthorized access incidents in 2026.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CÉGEP GARNEAU

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Cégep Garneau, qui est un partenaire KIOSQUE!

Visiter leur site web : https://fc.cegepgarneau.ca/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
ProgressezProgressezFormation Continue du Cégep Garneau
↩ Reply ♡ 0 · ↻ 0 ↗ Original

You don't need to click on ads. It takes only a minute to note the brand name and the offering and then search for the brand's website instead.

ESET: Is the ad a scam? How to tell before you click https://www.welivesecurity.com/en/social-media/is-ad-scam-how-tell-before-click/ @ESETresearch #scam #infosec #malvertising #socialmedia

www.welivesecurity.comIs the ad a scam? How to tell before you clickYou can trust a social media platform and still get scammed by an ad running on it. Here's how to fight back.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The real AI budget question: Where should we spend more?

🤖 AI budgeting needs a strategic overhaul: shift from cost control to ROI-driven value creation. CIOs should measure AI impact through business KPIs, not just usage metrics. Adopt flexible consumption-based models, tie funding to revenue-generating areas, and implement adaptive governance. The future? CIOs as strategic partners proving AI's business value.

https://www.cio.com/article/4230135/the-real-ai-budget-question-where-should-we-spend-more.html

#InfoSec #CyberSecurity

CIOThe real AI budget question: Where should we spend more?The AI budget question isn’t just how much you’re spending; it’s whether your biggest investments are producing enough business value to justify more.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This is probably the only time I would ever agree with Meta.

The Record, from yesterday: Judge denies WhatsApp’s bid to hold spyware maker in contempt for allegedly targeting users https://therecord.media/whatsapp-denied-appeal-alleged-nso-group-violation-injunction @therecord_media #Meta #spyware #WhatsApp #infosec

therecord.mediaJudge denies WhatsApp’s bid to hold spyware maker in contempt for allegedly targeting usersWhatsApp argued that NSO Group violated a 2025 injunction against using the messaging app to spread spyware. A federal judge said WhatsApp hurt its case by not revealing enough information.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Do you have any last minute question before the Open Security Conference? Check our FAQ, the answer might be in there already: https://opensecurityconference.org/faq/

Your point is not covered? Feel free to reach out :) https://opensecurityconference.org/contact/

We will soon send more information to all participants so you can prepare for the event. We're already looking forward to welcoming you!

#osco #osco26 #Security #CyberSecurity #InfoSec #AppSec [lisi]

Open Security ConferenceFAQWelcome to the Open Security Conference (osco), the people-centred international gathering for everyone interested in cybersecurity. Join us 5-8 November 2026 in Rückersbach, Germany.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

An intrusion discovered today may have started months ago. The NCSC tells you to size the log window to that gap, initial access to detection: 13 months for critical systems, 180 days otherwise. Rotate at 30 days and you can only reconstruct the last month.

How fast logs leave the box matters as much. Logs left on the box belong to whoever owns the box. Move them to a central store quickly and the attacker loses the chance to delete their own tracks.

Logging Made Easy, the NCSC's open source project, is built on something beats nothing. Their phrase is flight recorder.

https://www.ncsc.gov.uk/blog-post/what-exactly-should-we-be-logging

#CyberSecurity #InfoSec #Logging

National Cyber Security CentreWhat exactly should we be logging?A structured look at what data to collect for security purposes and when to collect it.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This isn't remotely funny. The research was posted yesterday:

Pillar Security: Open and Shut: Remote Code Execution in opencode via MCP OAuth https://www.pillar.security/blog/open-and-shut-remote-code-execution-in-opencode-via-mcp-oauth

More:

Infosecurity-Magazine: Researchers Warn OpenCode Quietly Patched Critical RCE Flaw, Leaving Users At Risk https://www.infosecurity-magazine.com/news/opencode-quietly-patched-critical/ #infosec #vulnerability #bots #GitHub

www.pillar.securityOpen and Shut: Remote Code Execution in opencode via MCP OAuthPillar Security found a critical remote code execution flaw in opencode on Windows and WSL. A remote MCP server could run code on your machine during the OAuth handshake. Affected 1.0.137 to 1.18.32, fixed in 1.18.33, no CVE issued.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

OpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked Attack

OpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/opencode-console-breach-exposes-ai-provider-api-keys-after-legacy-system-compromise-c-6-0-f-4/gD2P6Ple2L

BeyondMachinesOpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked AttackOpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 Rapid Response: Four vulnerabilities in Plex Media Server can be chained to achieve unauthenticated remote code execution. Plex reports compromised servers being used to run cryptocurrency miners and proxy software.

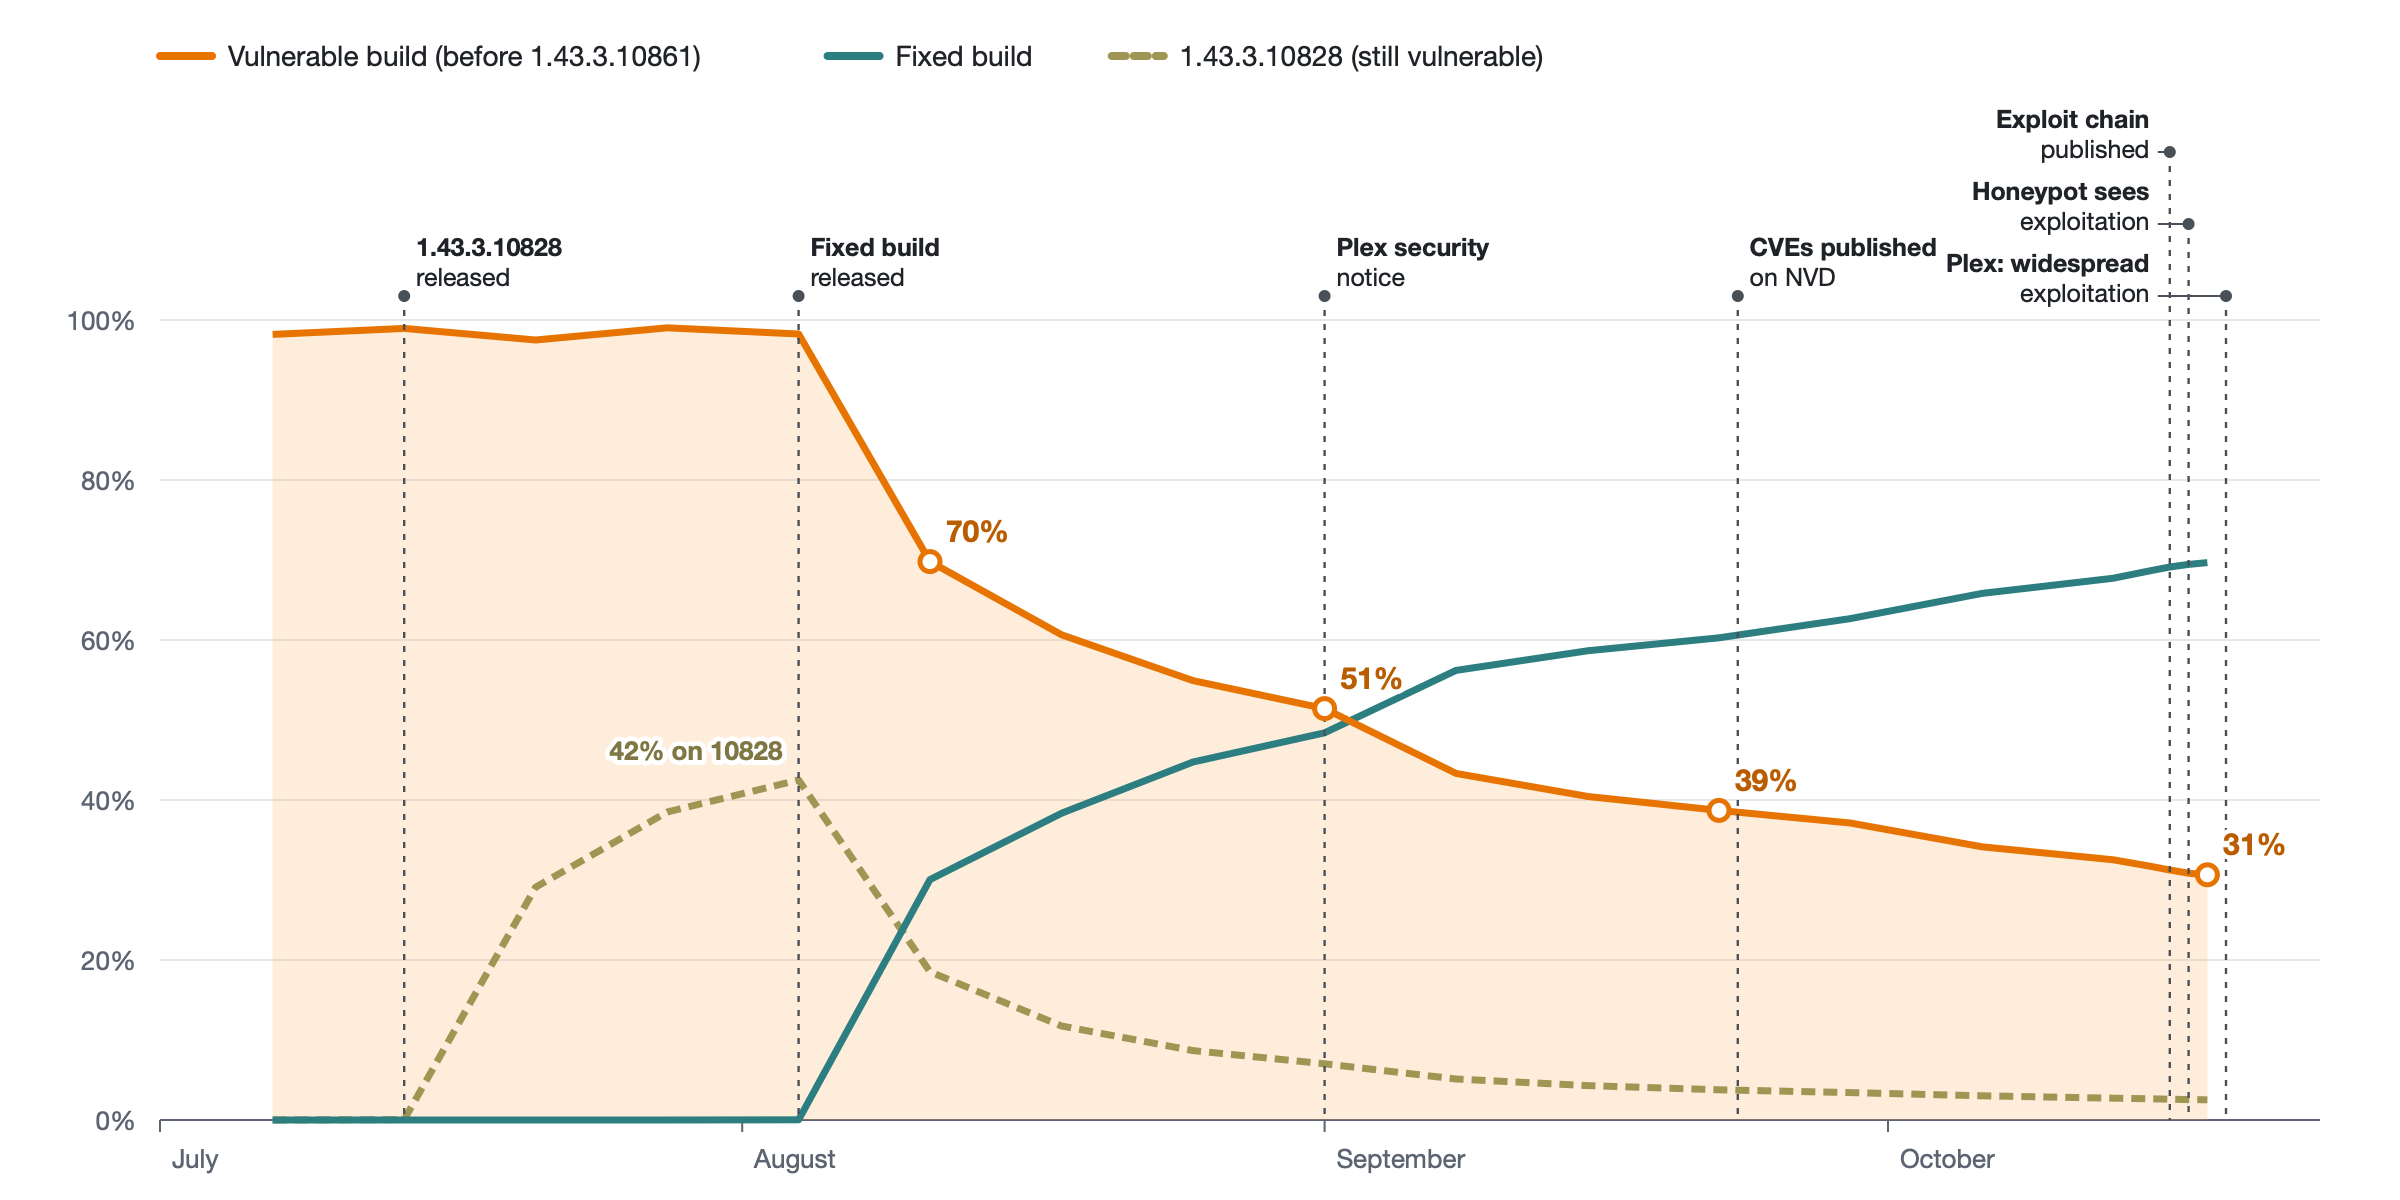
Censys ARC observes ~340,000 Internet-exposed Plex Media Server hosts. Roughly 30% run a vulnerable build, and nearly 8,000 run an early build that may be mistaken for patched.

Despite publication of the exploit chain and reports of exploitation, fewer than 2% of still-vulnerable hosts upgraded in the following three days.
Plex advises that previously exposed, unpatched servers may already be compromised and require additional remediation beyond patching.

Full Censys ARC advisory: https://censys.com/advisory/cve-2026-96652-cve-2026-96654-cve-2026-96655-cve-2026-96656/

#CensysARC #Cybersecurity #VulnerabilityManagement #Plex #InfoSec

Censys ARC graph showing trends in vulnerability and fixed build releases from July to October. One line shows the decline of vulnerable builds from 100% in July to 31% in October. Another line indicates the increase in fixed builds, peaking at 70% in August. Notable events are marked, including the release of 1.4.3.1080 in August and Plex security notices. CVEs published on NVD and explicit exploit chain events are annotated.
CensysOctober 20 Advisory: Plex Media Server Remote Code Execution Chain [CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656] - CensysCVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656 are four flaws in Plex Media Server before build 1.43.3.10861.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Aoki infostealer now targets AI coding assistant credentials: .claude.json, Codex configs, Copilot, Cursor, and Gemini tokens, plus AWS keys. Stealer logs are traded within hours.

Rotate your keys, set billing alerts, and check whether your credentials are already out there.

https://blog.relayshield.net/your-ai-coding-credentials-are-now-infostealer-targets

#CyberSecurity #ThreatIntel #InfoSec #Malware #AI

blog.relayshield.netYour AI Coding Credentials Are Now Infostealer Targets | RelayShieldThere's a new item on the infostealer shopping list. It's not your bank password. It's your Claude API key. Symantec's Threat Hunter team reported on October 15 that the newest Aoki...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vRolxFAW7hyzfBrqjLicr37CaJihNGZ0r-rAqdHi98FAi1N9sEk0uARbExM-_b77QgVlcphzXXU6qb5/pub?start=false&loop=false&delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad766133b775000091c1a83
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI spending shifts beyond IT, testing CIO-CFO decision rights

💡 Corporate AI spending has doubled to 3.3% of revenue, but 80% sits outside traditional IT budgets. CIOs, CFOs, and business leaders must collaborate through formal councils with clear accountability: business leaders own outcomes, CFOs manage finances, CIOs oversee tech. Unified governance and transparency are essential for maximizing AI's business impact.

https://www.techtarget.com/it-strategy/news/366651960/AI-spending-shifts-beyond-IT-testing-CIO-CFO-decision-rights

#InfoSec #CyberSecurity #AI

IT StrategyAI spending shifts beyond IT, testing CIO-CFO decision rights | TechTargetWith 80% of AI spending outside IT, CIOs and CFOs are redefining who controls architecture, capital allocation and accountability for value.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨New ransom group blog post!🚨

Group name: N0n
Post title: 51Ridge (Newark NJ hosting/IT)
Organization: 51Ridge
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/51Ridge%20%28Newark%20NJ%20hosting%2FIT%29

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-106173 is a critical path traversal flaw in Fortinet FortiSIEM. An unauthenticated attacker can write files and run code through its gRPC service.

FortiSIEM 7.5.0 is affected; 7.6 and Cloud are not. A public exploit is circulating per Horizon3.

Upgrade to FortiSIEM 7.5.1 or later.

https://fortiguard.fortinet.com/psirt/FG-IR-26-180

#Detection #infosec #cybersecurity

FortiGuard LabsPSIRT | FortiGuard LabsNone
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🛡️ Manager, Security Operations Center at Huntress
📍 US
💰 $165k–$185k/yr

Apply: https://blueteamjobs.com/job/manager-security-operations-center-huntress-xftgk9/

#BlueTeam #InfoSec #CyberSecurityJobs #SecurityOperationsLeadership

BlueTeamJobsManager, Security Operations Center at HuntressHuntress is hiring a Manager, Security Operations Center, United States. Pay: $165k–$185k a year. What We Do: Cybercrime is growing, and more businesses…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

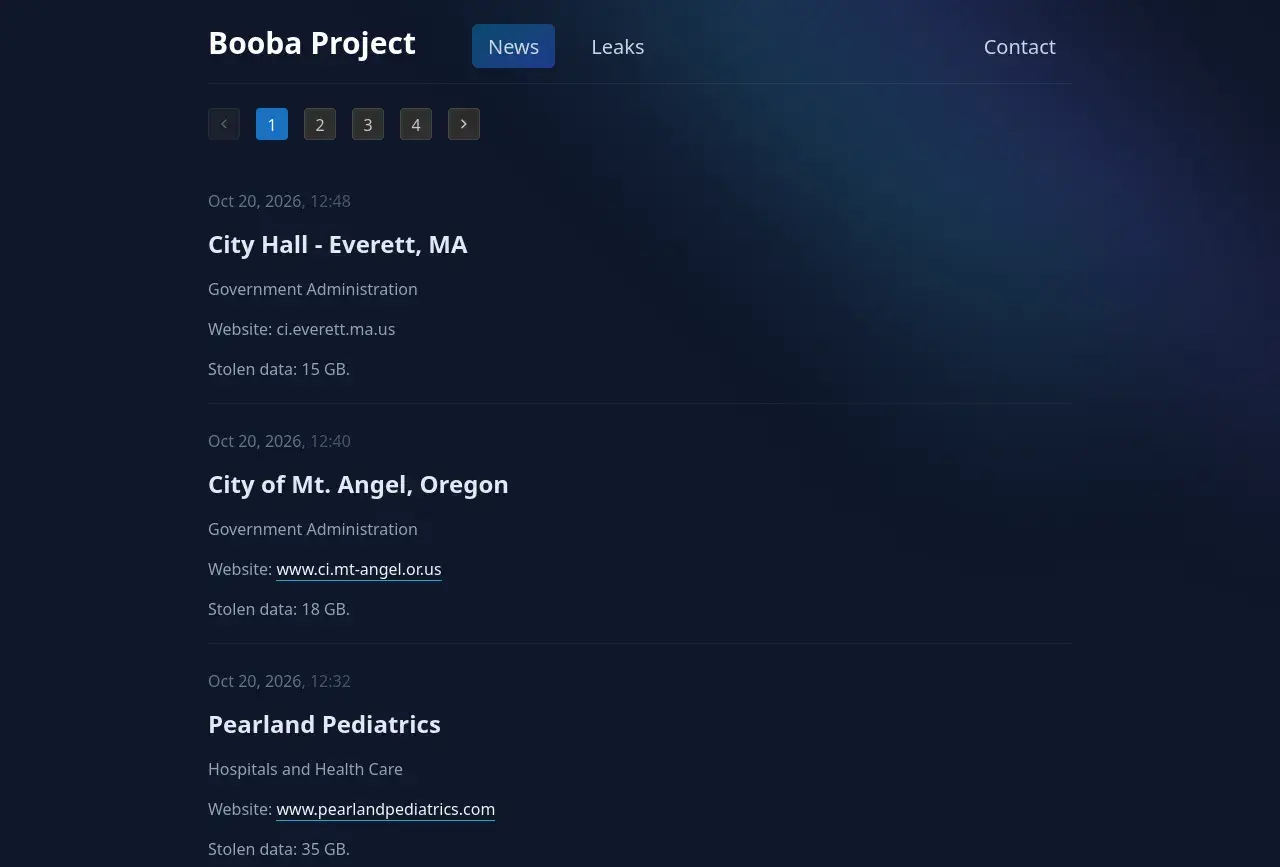
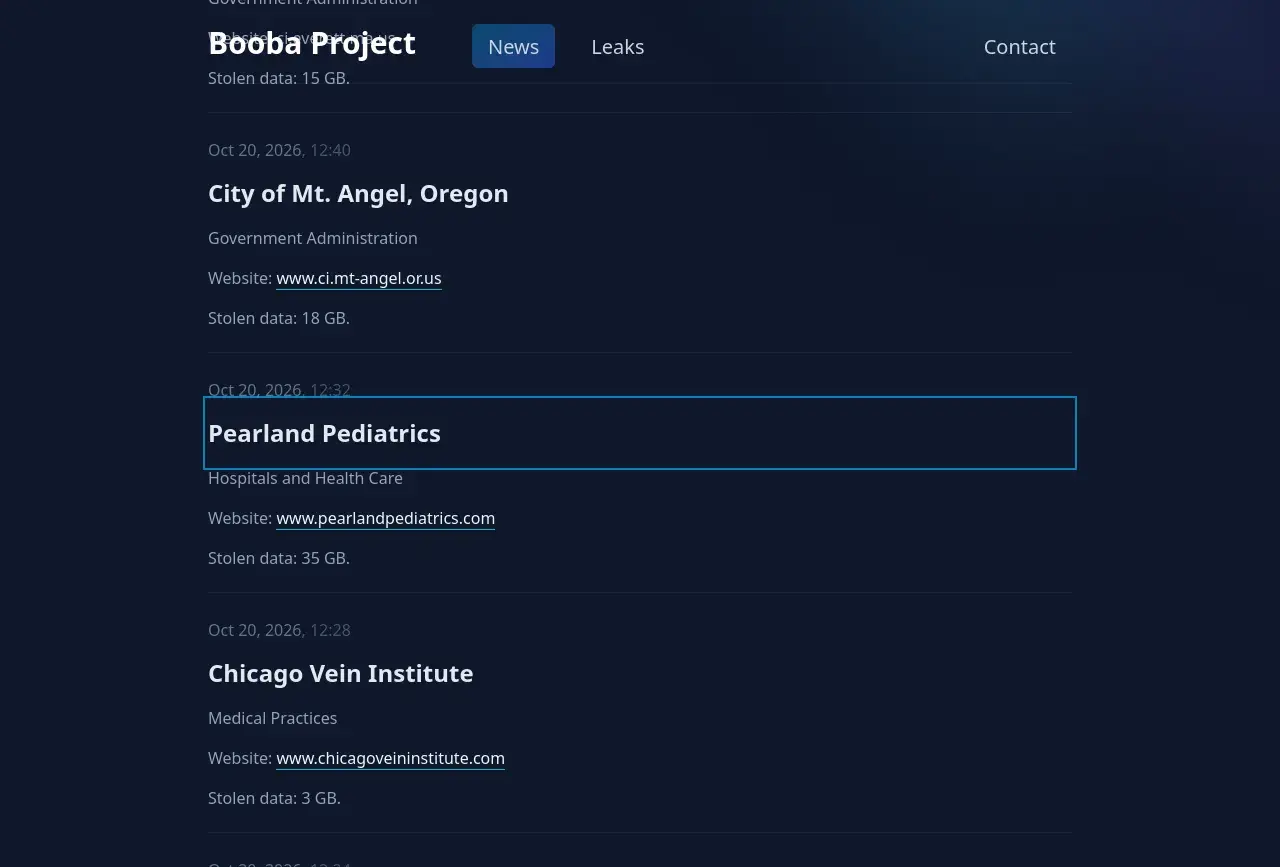
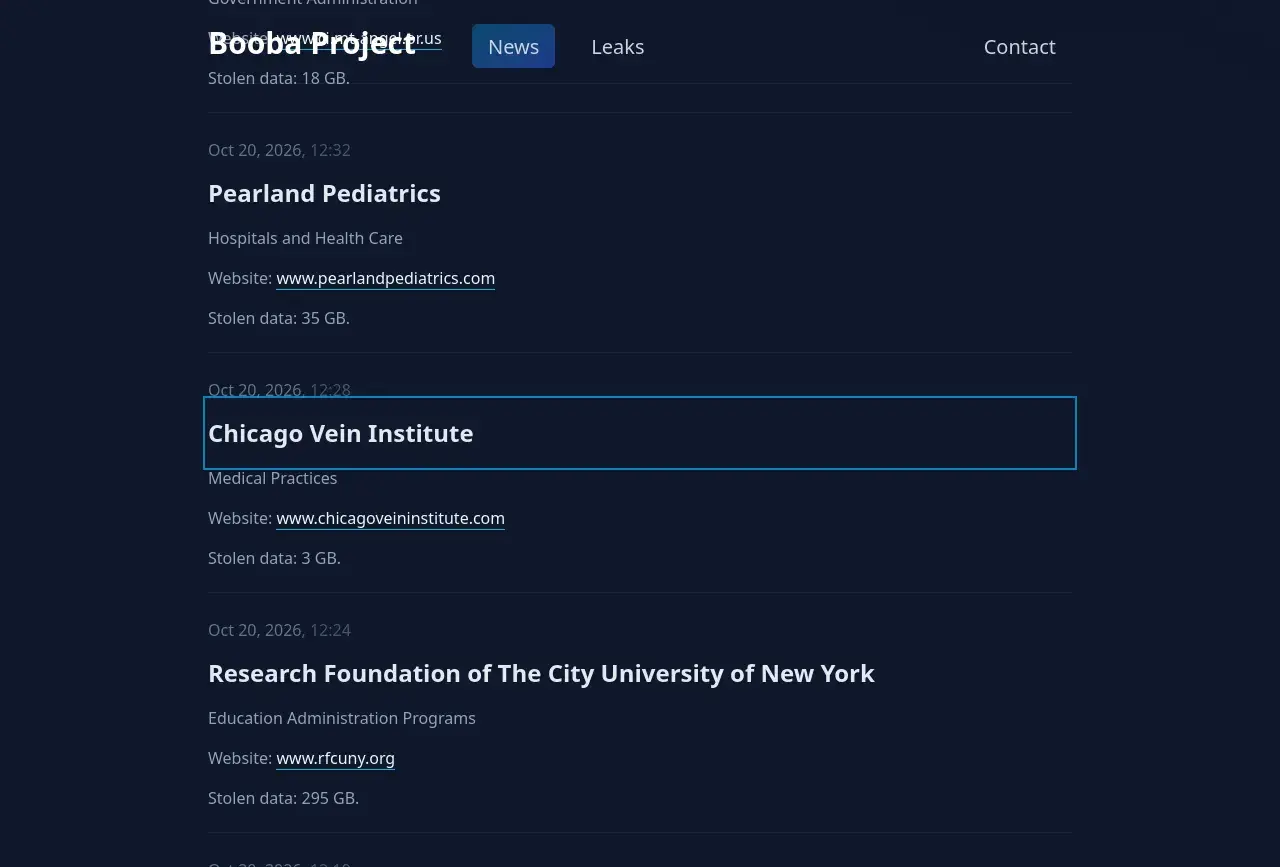
🚨New ransom group blog posts!🚨

Group name: Booba Project
Post title: City Hall - Everett, MA
Organization: Everett City Hall
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20Hall%20-%20Everett%2C%20MA

Group name: Booba Project
Post title: City of Mt. Angel, Oregon
Organization: City of Mt. Angel
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20of%20Mt.%20Angel%2C%20Oregon

Group name: Booba Project
Post title: Pearland Pediatrics
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Pearland%20Pediatrics

Group name: Booba Project
Post title: Chicago Vein Institute
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Chicago%20Vein%20Institute

Group name: Booba Project
Post title: Research Foundation of The City University of New York
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Booba%20Project/Research%20Foundation%20of%20The%20City%20University%20of%20New%20York

Group name: Booba Project
Post title: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER, PA
Organization: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/COASTAL%20CAROLINA%20NEUROPSYCHIATRIC%20CENTER%2C%20PA

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Launched today: Agentmetry, a local-first endpoint sensor for AI coding agents. Open source, Apache-2.0.

The problem: coding agents now run shell commands, read files and call MCP tools with the developer's own permissions. The transcript is a conversation, not a record, and EDR sees a process start a process, which is exactly what a working agent looks like.

How it works:
- Hooks at the tool boundary of Claude Code, Cursor, Codex, GitHub Copilot, Antigravity, Qwen, Kimi, Qoder and CodeBuddy. Stdio MCP servers go through an audit proxy.
- Every tool call lands in a hash-chained JSONL trail on your machine. Edit one record and agentmetry verify fails. agentmetry anchor publishes a checkpoint the host cannot rewrite.
- Arguments are hashed inside the hook by default. DLP matches record the rule id, never the secret.
- Sequence detections, not single-event alerts: a credential read followed by network egress is one finding. Labelled with MITRE ATT&CK, and ATLAS where it adds something.
- MCP rug-pull detection: tools/list is fingerprinted per tool, so a listing that moves while the config stays the same is flagged (ATLAS AML.T0109).
- Forwards to Splunk, Elastic, Google SecOps or Microsoft Sentinel. No telemetry, nothing leaves until you configure a sink.

What it does not do:
- It only sees agents whose hooks are installed. A browser chat or an IDE with hooks off is invisible.
- It records what a shell call launched, not what that process did inside. That is your EDR's job.
- Windows and Linux are tested in CI. macOS is in preview.
- Public alpha, one maintainer.

The detection benchmark ships in the package: 57 cases, 0 missed, 0 false positives. Rerun it with agentmetry benchmark rather than trusting me.

Try it with nothing installed: uvx agentmetry demo
It replays a credential theft into a temp folder, raises the finding, then shows the trail failing verification after one edit.

Criticism very welcome, especially from anyone doing detection engineering or rolling agents out to a team.

Code: https://github.com/blitzcrieg1/agentmetry
Launch: https://www.producthunt.com/products/agentmetry

#infosec #AIsecurity #opensource #DFIR #detectionengineering #MCP
GitHubGitHub - blitzcrieg1/agentmetry: Local-first endpoint sensor for AI coding agents. Hash-chained audit trail, MITRE-mapped sequence detection, DLP. Forwards to the SIEM you already Local-first endpoint sensor for AI coding agents. Hash-chained audit trail, MITRE-mapped sequence detection, DLP. Forwards to the SIEM you already run. - blitzcrieg1/agentmetry
↩ Reply ♡ 0 · ↻ 0 ↗ Original

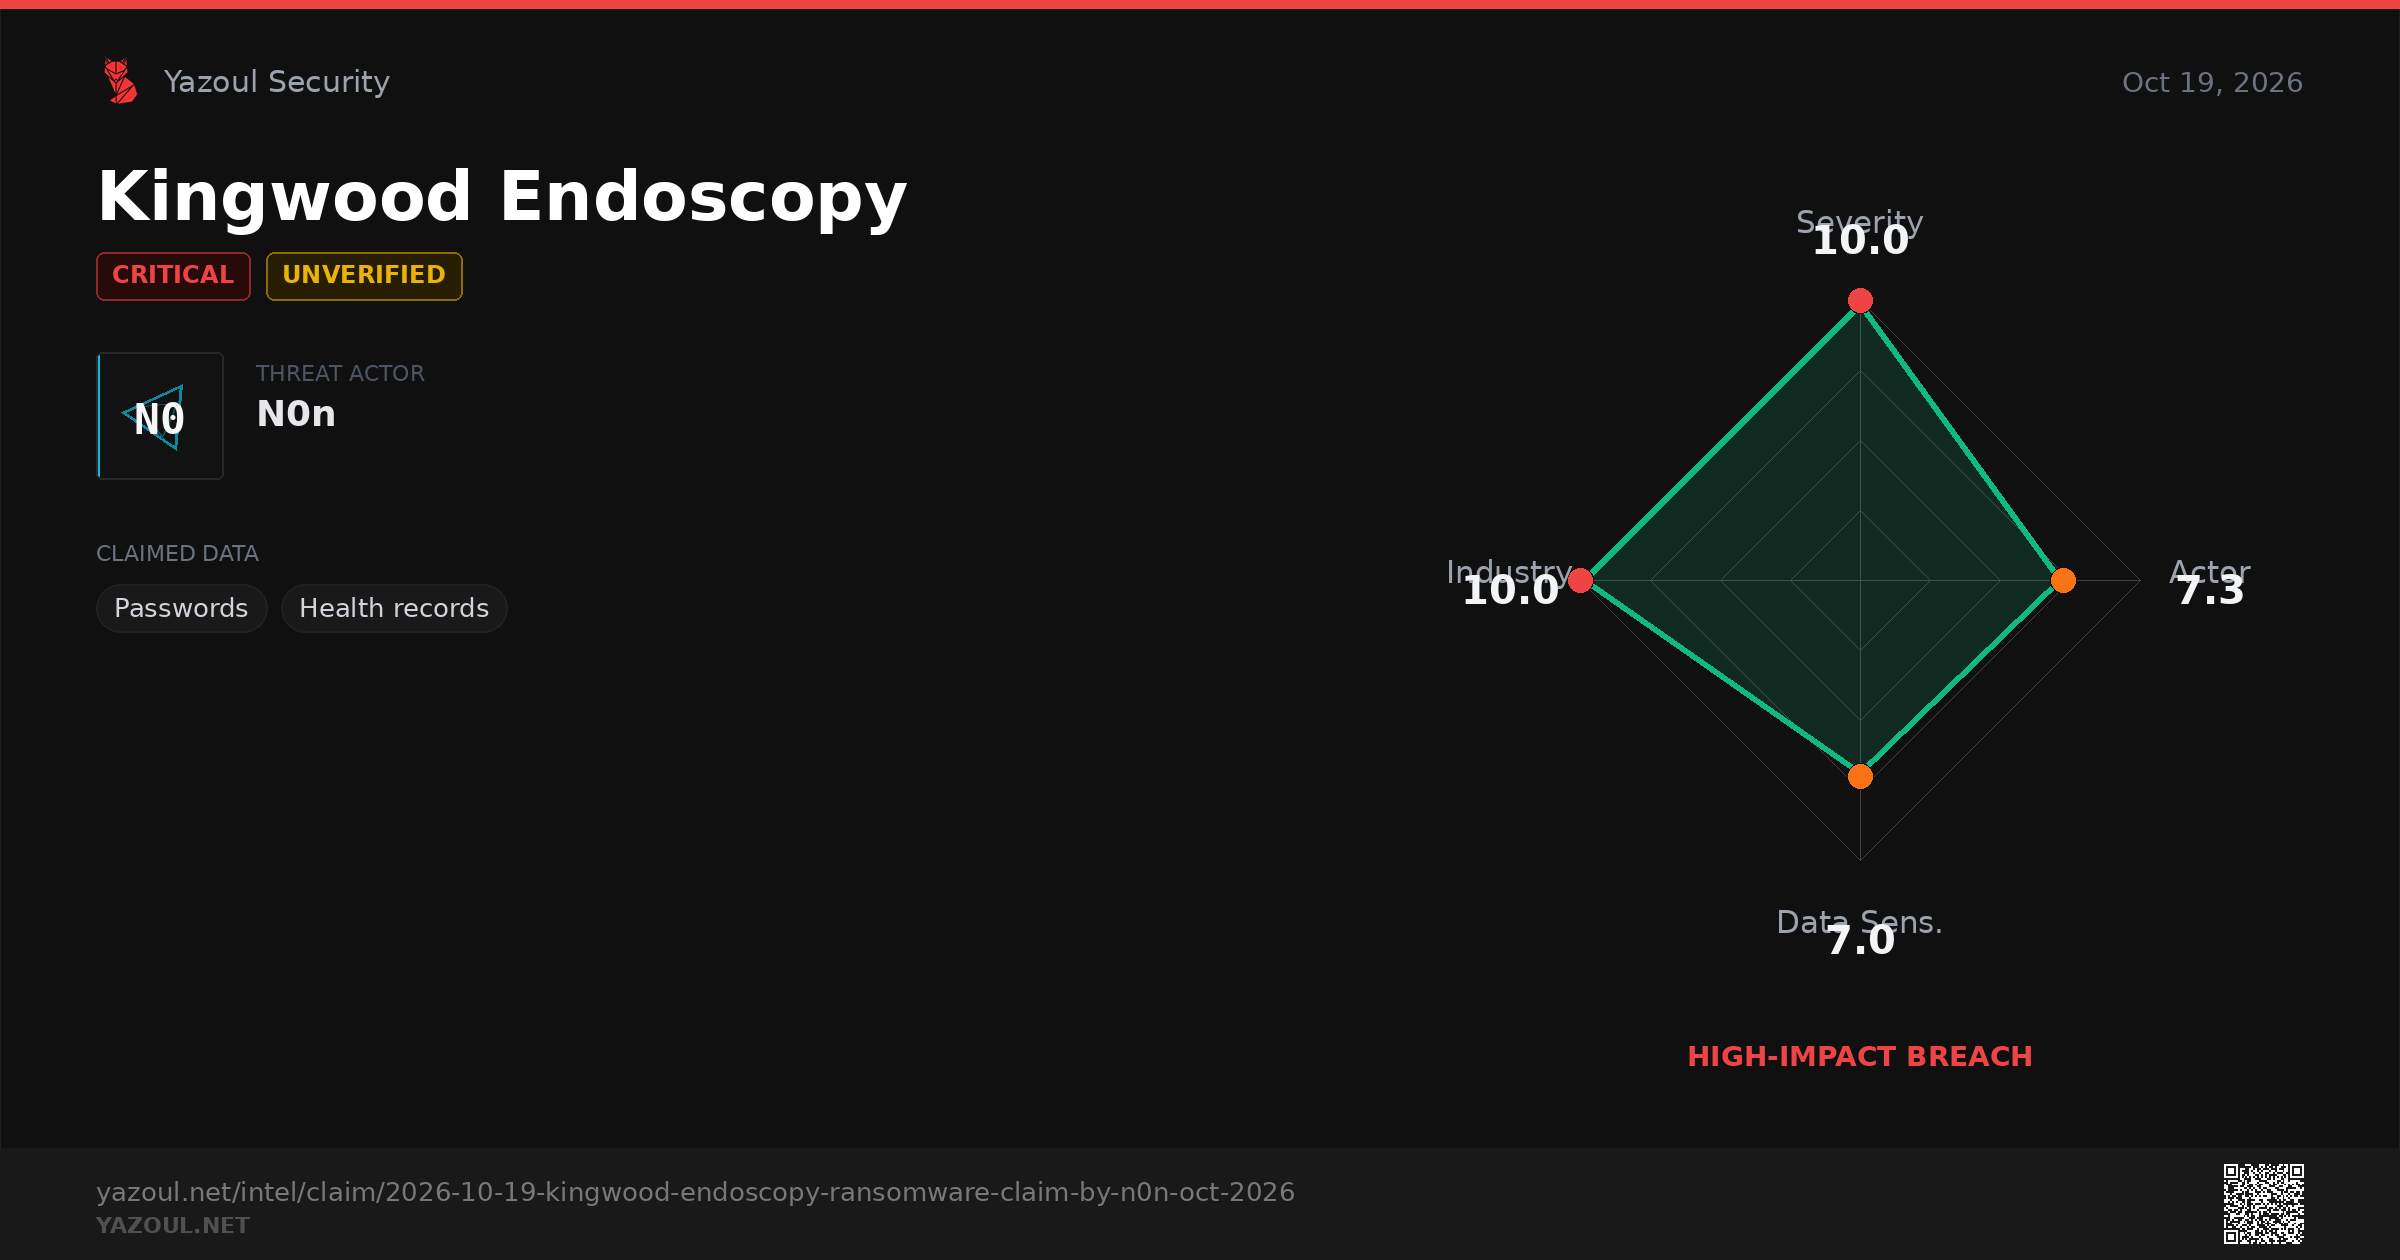
🛡 THREAT INTEL | Kingwood Endoscopy

🔴 Actor "N0n" claims Undisclosed

Allegedly exposed
• Passwords
• Health records

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-kingwood-endoscopy-ransomware-claim-by-n0n-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityKingwood Endoscopy Ransomware Claim by N0n (Oct 2026)N0n allegedly claims Kingwood Endoscopy as a victim, citing stolen credentials and system access. Read our unverified threat intel analysis and stay alert.
↩ Reply ♡ 0 · ↻ 0 ↗ Original