X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

T

🚨 PHP2Shell: CRITICAL PHP RCE ALERT

Two vulnerabilities. CVE-2026-109618 & CVE-2026-109619. CVSS 9.2.

PHP powers WordPress, Magento and millions of websites. This is a reminder that patching your CMS isn't enough when the vulnerability lives in the PHP runtime itself.

⚠️ Check your PHP version. Prepare to patch. Don't rely on WordPress auto-updates.

Technical breakdown, exposure, detection & mitigation 👇
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/

#PHP #CyberSecurity #InfoSec

❞ Quoted postThe CyberSec Guru

Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps

The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-21

📊 9 updates from 3 sources:

🔹 iTnews - Security: Cloudflare warns fixing botched eMudhra certs goes beyond browsers
https://www.itnews.com.au/news/cloudflare-warns-fixing-botched-emudhra-certs-goes-beyond-browsers-629804?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 SecurityWeek: Accenture, Dragos, SANS Launch $10M Initiative to Defend Small US Utilities
https://www.securityweek.com/accenture-dragos-sans-launch-10m-initiative-to-defend-small-us-utilities/

🔹 The Hacker News: PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert
https://thehackernews.com/2026/10/php2shell-two-unpatched-critical-php.html

🔹 SecurityWeek: Hijacked Developer Account Used to Plant Stealer in OVHcloud CLI
https://www.securityweek.com/hijacked-developer-account-used-to-plant-stealer-in-ovhcloud-cli/

🔹 The Hacker News: Hackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare Intrusion
https://thehackernews.com/2026/10/hackers-hid-vasilek-backdoor-in-vmware.html

🔹 SecurityWeek: PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws
https://www.securityweek.com/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws/

🔹 The Hacker News: CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws
https://thehackernews.com/2026/10/cisa-orders-federal-agencies-to-patch.html

🔹 The Hacker News: State Bank of India Confirms Data Leak After 3,897 Customer Records Found on Dark Web
https://thehackernews.com/2026/10/state-bank-of-india-confirms-data-leak.html

🔹 iTnews - Security: Critical flaws strike PHP as disclosure embargo is broken
https://www.itnews.com.au/news/critical-flaws-strike-php-as-disclosure-embargo-is-broken-629794?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

#InfoSec #SecurityNews

iTnewsCloudflare warns fixing botched eMudhra certs goes beyond browsersServers, containers and apps need manual patching.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Unit 42 has unpicked a two-year intrusion at a telecoms provider. It began in September 2024 with FortiJump, a missing-authentication FortiManager flaw. One stolen archive held configs, credentials and private keys for 500-plus managed FortiGate firewalls: the provider's own and its clients'.

The implant found there, PEERSTITCH, lives only in memory. No disk file, no listening port, no outbound connection; it talks through legitimate FortiOS processes. The second flaw was patched in April, yet CISA listed it as exploited on 16 October. Patching closes the door; the stolen keys still work until someone rotates them.

https://unit42.paloaltonetworks.com/fortimanager-cve-2024-47575-peerstitch-malware/

#CyberSecurity #InfoSec #Fortinet

Unit 42Unit 42 Uncovers PEERSTITCH, a Stealthy FortiGate ImplantWe investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP Issues Emergency Warning for Critical Remote Code Execution Vulnerabilities

PHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.

**If you run any website or app built on PHP (WordPress, online shops, internal tools), install the emergency security updates as soon as they're released today at 14:00 UTC. Until you've patched, restrict access to internal PHP systems and admin pages to trusted networks only, and monitor your servers closely for unusual logins, new files or strange activity.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/php-issues-emergency-warning-for-critical-remote-code-execution-vulnerabilities-y-t-1-8-c/gD2P6Ple2L

BeyondMachinesPHP Issues Emergency Warning for Critical Remote Code Execution VulnerabilitiesPHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Fundatec.

Must be exactly 6 alphanumeric characters, does not show special characters are not allowed, username is your social security number (easily searchable) and the form is sent over plain HTTP. Did I mention this company applies college entrance exams for **Computer Science** nationwide in Brazil?

https://dumbpasswordrules.com/sites/fundatec/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comFundatec - Dumb Password RulesMust be exactly 6 alphanumeric characters, does not show special characters are not allowed, username is your social security number (easily searchable) and the form is sent over plain HTTP. Did I mention this company applies college entrance exams for **Computer Science** nationwide in Brazil?
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 CISA adds Plex2Shell to KEV: four chained Plex Media Server flaws (CVE-2026-96652, -96654, -96655, -96656) escalate to unauthenticated RCE. Patched in 1.43.3.10861 since August, yet exploited to drop cryptominers and proxyware. FCEB patch deadline Oct 23.
🔗 https://thehackernews.com/2026/10/cisa-orders-federal-agencies-to-patch.html
#CVE #Exploit #CyberSec #InfoSec

The Hacker NewsCISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard FlawsCISA flags six exploited flaws in Plex, Siemens, and SiteGuard, including Plex2Shell bugs used to deploy crypto miners and proxy malware.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Listen, kid. When you see a report from the FBI saying a group like SafePay is "among the most active" with over 600 victims since 2024, don't go hunting for a hooded figure in a dark room.

https://theperimetersite.com/report/382

#vulnerability #phishing #infosec

The Perimeter SiteThe reality of the SafePay operation — The Perimeter SiteListen, kid. When you see a report from the FBI saying a group like SafePay is "among the most active" with over 600 victims since 2024, don't go hunting for a hooded figure in a…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Crypto, Mixers, and Traceability: Why Bitcoin Was Never Anonymous

The fifth installment in a series about the darknet. In previous installments, I’ve debunked myths about the darknet, explained how darknet marketplaces work, and discussed the lifecycle of leaked data…

https://vsx.global/traceability-of-cryptocurrencies/

#infosec #privacy #opensource #digitalsovereignty

VSX.is | Digital Privacy and SovereigntyCryptocurrencies, Mixers, and Transaction Traceability: Why Bitcoin Has Never Been Anonymous - VSX.is | Digital Privacy and SovereigntyThe fifth installment in a series about the darknet. In previous installments, I’ve debunked myths about the darknet, explained how darknet marketplaces work, and discussed the lifecycle of leaked data…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

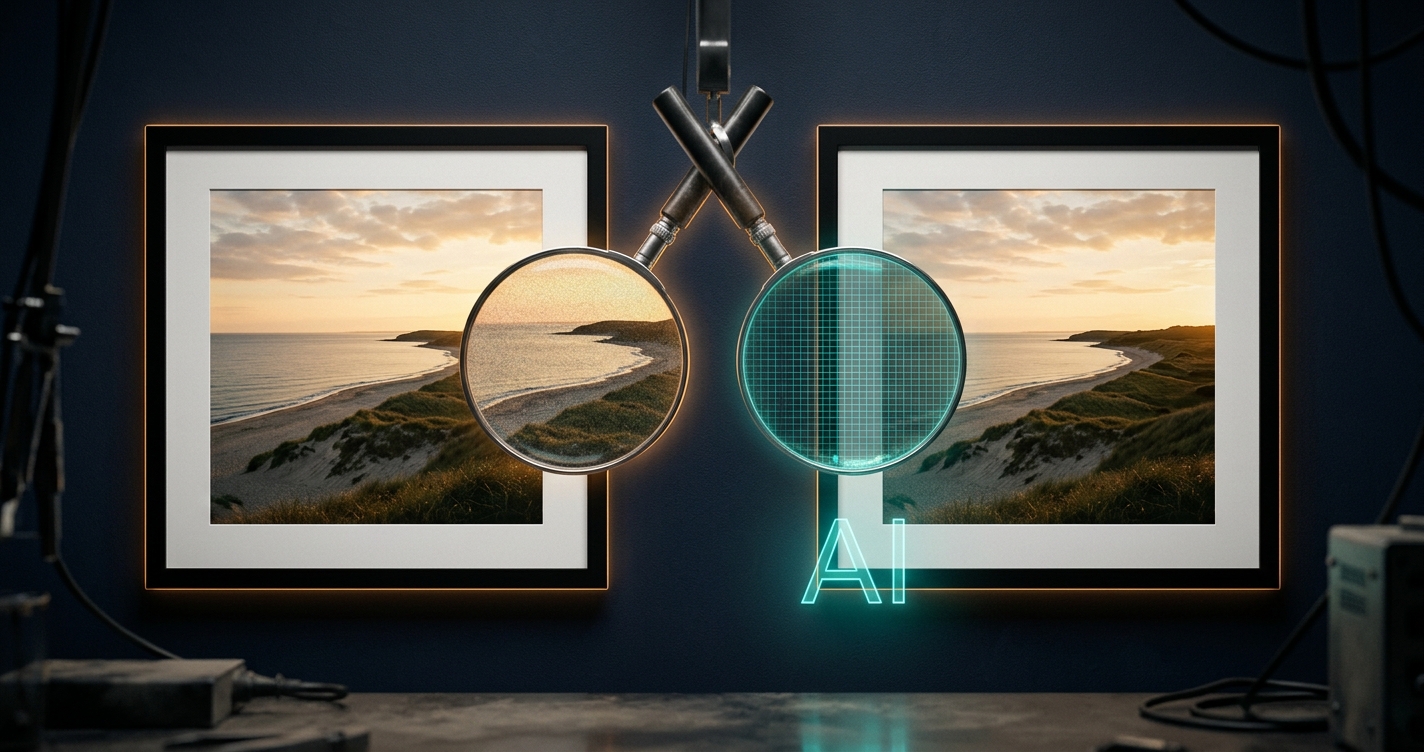
When people say: "I can always tell an AI photo" usually means "I notice the bad ones". That's what it means to me today.

The usual advice is to count the fingers, check the teeth and earrings, and look for nonsense text in the background. It was good advice a couple of years ago. However, every new generator fixes exactly the "tells" people talk about.

Detection that works is trained: samples of real and generated content, compared until something separates them. It beats the human eye by a long way, but a detector can only recognise what it has been shown.

That is the problem with the arms race:
- Stable Diffusion's founder estimated its 2022 training compute at about US$600k (256 GPUs, ~150k GPU-hours); he put DALL-E 2 at roughly 1M GPU-hours
- Stanford's AI Index: ~US$78M of compute for GPT-4, ~US$191M for Gemini Ultra
- Epoch AI: hardware is roughly half to two-thirds of a frontier model's cost, staff 29–49%
- 2025 deepfake-detection rounds I could find: tens of millions
- Running a model once it exists: our 17-second explainer video took one GPU, ~5 hours, under A$10 (~US$6.50), open-licensed models

The risk that worries me most: a private generator with only a handful of images ever released. Nothing to train on, no detector has seen it, and eyeballing won't catch it. Worse if it also forges a camera's metadata and fingerprint, which works for cameras that don't protect their output. Camera makers are now signing and watermarking at the hardware level, so imitating that means breaking the protection, not copying a few EXIF fields.

So what still works? There's a check most people never think of: instead of trying to prove a photo is AI, try to prove it's real. It often tells you more, and it doesn't care which generator made the fake.

The full article covers how that works, why a screenshot or a forward can wipe out the evidence, the one thing I would tell anyone asked to judge a photo, the cost breakdown with sources, and the guides we wrote for each question people send me:

https://kennethbspringer.au/2026/10/21/is-this-photo-real-why-ai-is-making-that-harder-to-answer/?utm_source=mastodon&utm_medium=social&utm_campaign=article-26

#AI #Deepfakes #DigitalForensics #DFIR #ContentAuthenticity #infosec

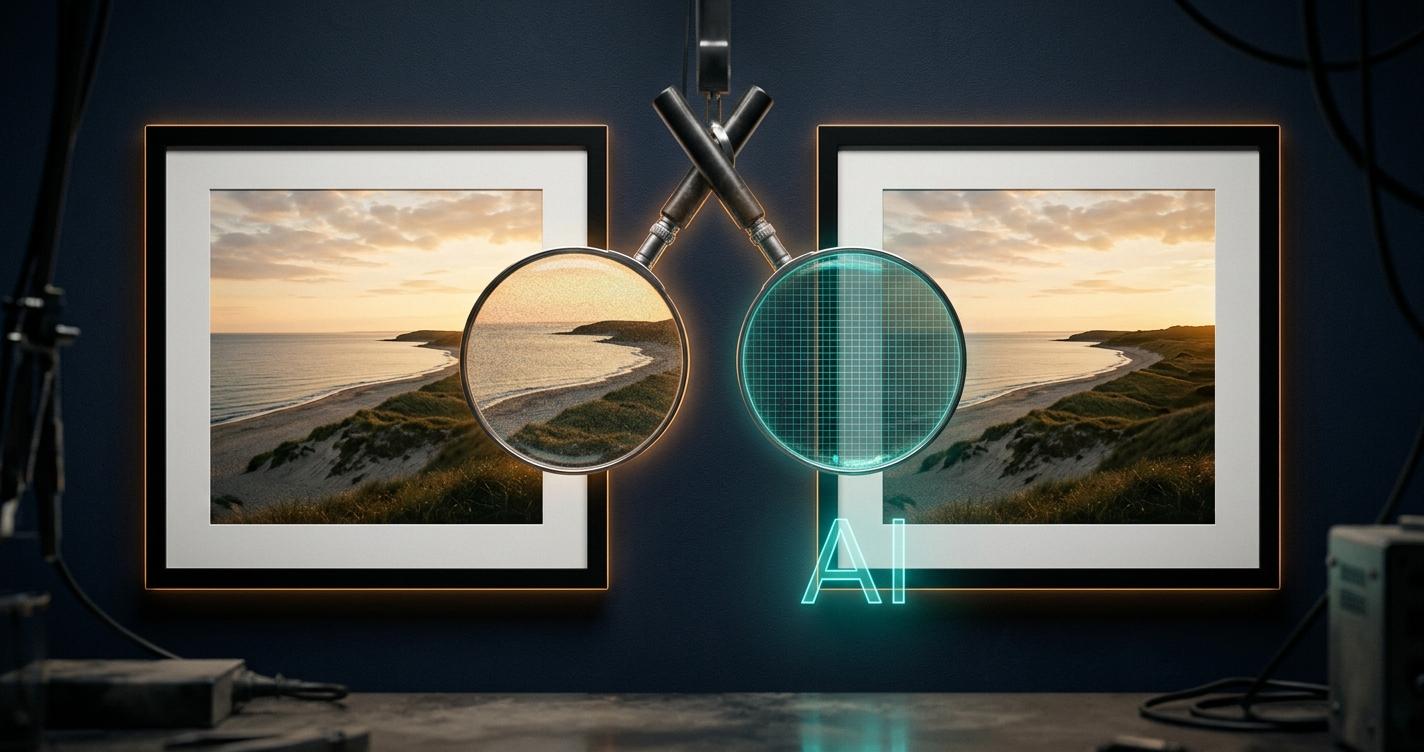
Which is real or fake illustration. Two magnifying glasses one over real and the other over AI generated, both looks the same, hard to tell the difference
kennethbspringer.auIs This Photo Real? Why AI Is Making That Harder to Answer — Kenneth B. SpringerCan you still spot an AI photo by eye? Why detection is getting harder, what it costs to build a generator, and the checks that still work.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2024-39930 is a critical argument injection vulnerability in the built-in SSH server of Gogs, allowing authenticated users to execute arbitrary commands on the host.

Versions through 0.13.0 are affected; Windows installations are not. Gogs fixed the flaw in version 0.13.1.

A public proof-of-concept exploit exists per CISA.

https://nvd.nist.gov/vuln/detail/CVE-2024-39930

#infosec #cybersecurity

nvd.nist.govNVD - Home
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-114108: CRITICAL vuln in HKUDS Vibe-Trading ≤0.1.6 – missing auth enables root shell commands, script uploads, session leaks. Set API_AUTH_KEY & restrict API access now. Patch unconfirmed. https://radar.offseq.com/threat/cve-2026-114108-missing-authentication-for-critical-function-in-hkuds-vibe-trading-dbf2add5e4f70bbe #OffSeq #vulnerability #infosec #HKUDS

Critical threat: CVE-2026-114108: Missing Authentication for Critical Function in HKUDS Vibe-Trading
OffSeq Threat RadarCVE-2026-114108: Missing Authentication for Critical… | Threat RadarHKUDS Vibe-Trading versions from 0.1.0 up to but not including 0.1.7 have a missing authentication vulnerability. This flaw allows unauthenticated attackers to…
↩ Reply ♡ 0 · ↻ 0 ↗ Original