X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

PARTENAIRE HACKFEST 2026 SPONSOR : DEVOLUTIONS

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Devolutions, qui est un partenaire KIOSQUE!

Visiter leur site web : https://devolutions.net/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
#hacking #infosec #hackfest #cybersecurity

Media attachment
DevolutionsOne IT Ecosystem for Connections & PAM | DevolutionsDiscover one Devolutions ecosystem for remote connections, passwords, privileged access, and automation — secure productivity for IT professionals worldwide.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

STS Aviation Group Data Breach Exposes Biometric and Financial Records

STS Aviation Group disclosed a long-term data breach where unauthorized actors accessed sensitive employee and personal data. The company is providing credit monitoring to affected individuals after a year-long investigation confirmed the theft of medical, financial, and biometric information.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/sts-aviation-group-data-breach-exposes-biometric-and-financial-records-1-c-5-p-m/gD2P6Ple2L

BeyondMachinesSTS Aviation Group Data Breach Exposes Biometric and Financial RecordsSTS Aviation Group disclosed a long-term data breach where unauthorized actors accessed sensitive employee and personal data. The company is providing credit monitoring to affected individuals after a year-long investigation confirmed the theft of medical, financial, and biometric information.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

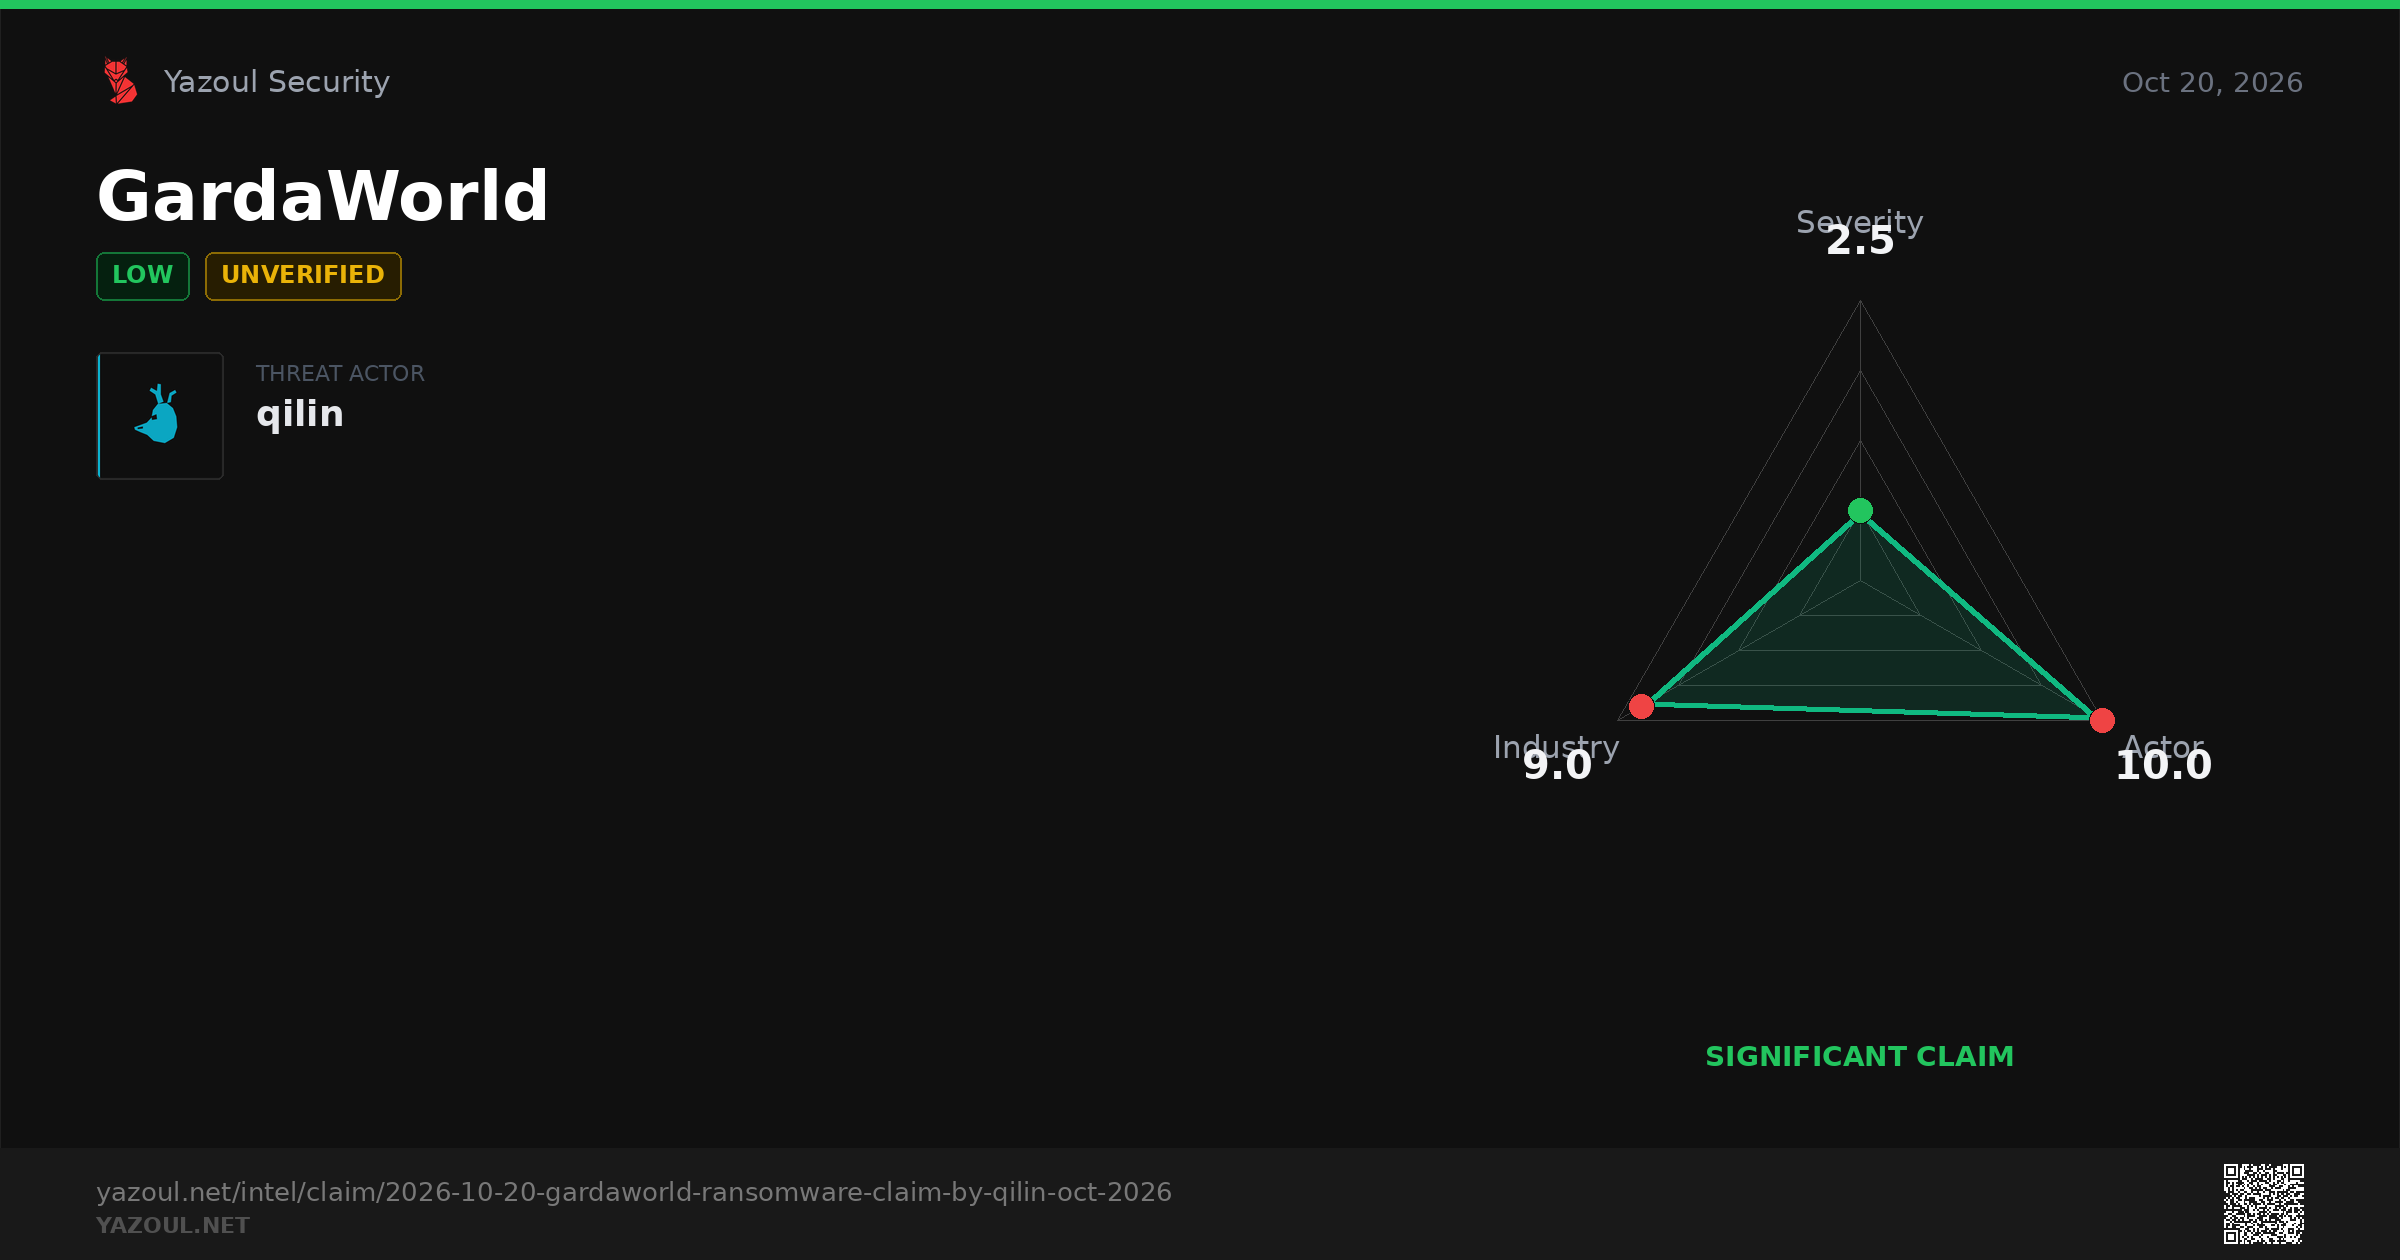
🛡 THREAT INTEL | GardaWorld

🟢 Actor "qilin" claims Undisclosed

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-20-gardaworld-ransomware-claim-by-qilin-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityGardaWorld Ransomware Claim by Qilin (Oct 2026)Qilin allegedly claims GardaWorld as a ransomware victim. Unverified leak site post, undisclosed data volume. Read our cautious threat intel analysis and stay alert.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 Improved AI Security Verdict accuracy and clearer explanations for pages that lead to a sign-in form.

https://scanmalware.com/changelog?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610201330#2026-10-20T13:30:00Z-a7723dd9

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comChangelog - ScanMalware.comRecent changes and updates to ScanMalware.com - URL and website security scanner.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Anomaly Silently Patches Critical RCE in OpenCode AI Agent

Anomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.

**If you use OpenCode on Windows or WSL, upgrade to version 1.18.33 or later immediately, because a malicious or hijacked MCP server can take over your machine and everything on it (code, SSH keys, cloud tokens). Until you can update, remove any remote MCP servers you don't fully trust from your OpenCode configuration, and check your developers' machines yourself, since security scanners won't flag this one.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/anomaly-silently-patches-critical-rce-in-opencode-ai-agent-k-u-t-k-o/gD2P6Ple2L

BeyondMachinesAnomaly Silently Patches Critical RCE in OpenCode AI AgentAnomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Iwai Cosmo Securities had made MFA mandatory after Japan's 2025 account-takeover wave. On Oct 14, attackers placed orders in 7 customer accounts anyway (5 executed), without logging in as them: through a misconfigured admin function at Trade Works, the vendor that runs its trading platform.

Customer authentication protects the front door. Admin and back-office functions can trade on every account.

https://japancyberwatch.com/articles/iwai-cosmo-securities-unauthorized-trades-vendor-admin-2026

#infosec #fintech #Japan

japancyberwatch.comIwai Cosmo Securities: Unauthorized Trades Placed Through a Vendor's Admin Function, Despite Mandatory MFAAttackers who hit Trade Works, the vendor that runs Iwai Cosmo Securities' online trading system, placed orders in seven customers' accounts on October 14, 2026 without logging in as them. Japan's top government spokesperson says the FSA has asked for a cause analysis.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CYVAULT

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have CyVault, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://cyvault.io/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
cyvault.ioCyVault™ | CyVault™
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Paradigm Healthcare Services Breach Impacts 970,000 Medi-Cal Members

Paradigm Healthcare Services suffered a data breach affecting 970,000 Medi-Cal members after unauthorized actors accessed its local network in October 2025.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/paradigm-healthcare-services-breach-impacts-970000-medi-cal-members-f-9-o-a-l/gD2P6Ple2L

BeyondMachinesParadigm Healthcare Services Breach Impacts 970,000 Medi-Cal MembersParadigm Healthcare Services suffered a data breach affecting 970,000 Medi-Cal members after unauthorized actors accessed its local network in October 2025.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CYVAULT

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous CyVault, qui est un partenaire KIOSQUE!

Visiter leur site web : https://cyvault.io/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
cyvault.ioCyVault™ | CyVault™
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxp[:]//webuyworkshopequipment[.]com/wp-content/themes/sketch/js/SF_TRASH/c45b222914e3c78d/
🧬 Analysis at: https://urldna.io/scan/6ad86af13b775000045e7ef1
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP ships fixes for two leaked critical flaws ("php2shell", CVSS 9.2) at 14:00 UTC today. Affected versions are still unconfirmed by PHP.

Some Japanese services didn't wait: childcare app Codmon stopped everything, website builder Studio froze its editor, Sakura Internet paused some functions. Pausing before a patch is a security decision, not a failure.

https://japancyberwatch.com/articles/php2shell-critical-php-flaws-japan-services-pause-2026

#PHP #infosec #Japan

japancyberwatch.comphp2shell: Japanese Services Pause Ahead of an Emergency PHP Patch for Two Critical FlawsPHP will ship fixes for two critical flaws, rated CVSS 9.2, at 14:00 UTC on October 21, 2026, after details leaked. Childcare app Codmon and website builder Studio are among Japanese services that switched off first. What is known, what is not, and why pausing is a sound security decision.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

A test account, twelve years old, protected by Password1. Somebody finally sat the exam. The ICO issued a reprimand, but no fine.

#CyberSecurity #Ransomware #Passwords #DataBreach #InfoSec

Source: https://www.infosecurity-magazine.com/news/children-data-stolen-password1/

Infosecurity MagazineChildren’s Data Stolen After Ransomware Attack Compromises ‘Password1’The ICO has slammed security failings by the Welsh local government data unit and IT service provider following the 2024 incident
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NEC says a company it uses for development and maintenance was hacked in late September. Its legitimate accounts, used from its own PCs, reached NEC customers' servers and encrypted them. Osaka Metropolitan University's 500 servers were among them. A shared project cloud folder leaked too.

NEC's supplier program is one of the best documented in Japan. Audits show who has controls; they don't stop a valid account on a trusted device.

https://japancyberwatch.com/articles/nec-contractor-compromise-customer-systems-encrypted-2026

#infosec #SupplyChain #Japan

japancyberwatch.comNEC Contractor Hacked: Stolen Accounts Used to Encrypt Customers' Servers, Including Osaka Metropolitan UniversityNEC says a company it uses for system development and maintenance was hacked in late September 2026, and its legitimate accounts were used to break into NEC customers' systems and encrypt servers. Files in a cloud storage NEC used to share project information also leaked.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Zeabur to Shut Down Following Massive Infrastructure Compromise and Data Theft

Zeabur announced a permanent shutdown after attackers exploited plaintext credentials and unrotated admin tokens to steal over 3.2 million environment variables and compromise 321,810 accounts. The breach compromised shared clusters, AWS keys, and GCP dedicated servers, leading to the exposure of production databases and customer disk copies.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/zeabur-to-shut-down-following-massive-infrastructure-compromise-and-data-theft-y-0-3-m-6/gD2P6Ple2L

BeyondMachinesZeabur to Shut Down Following Massive Infrastructure Compromise and Data TheftZeabur announced a permanent shutdown after attackers exploited plaintext credentials and unrotated admin tokens to steal over 3.2 million environment variables and compromise 321,810 accounts. The breach compromised shared clusters, AWS keys, and GCP dedicated servers, leading to the exposure of production databases and customer disk copies.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

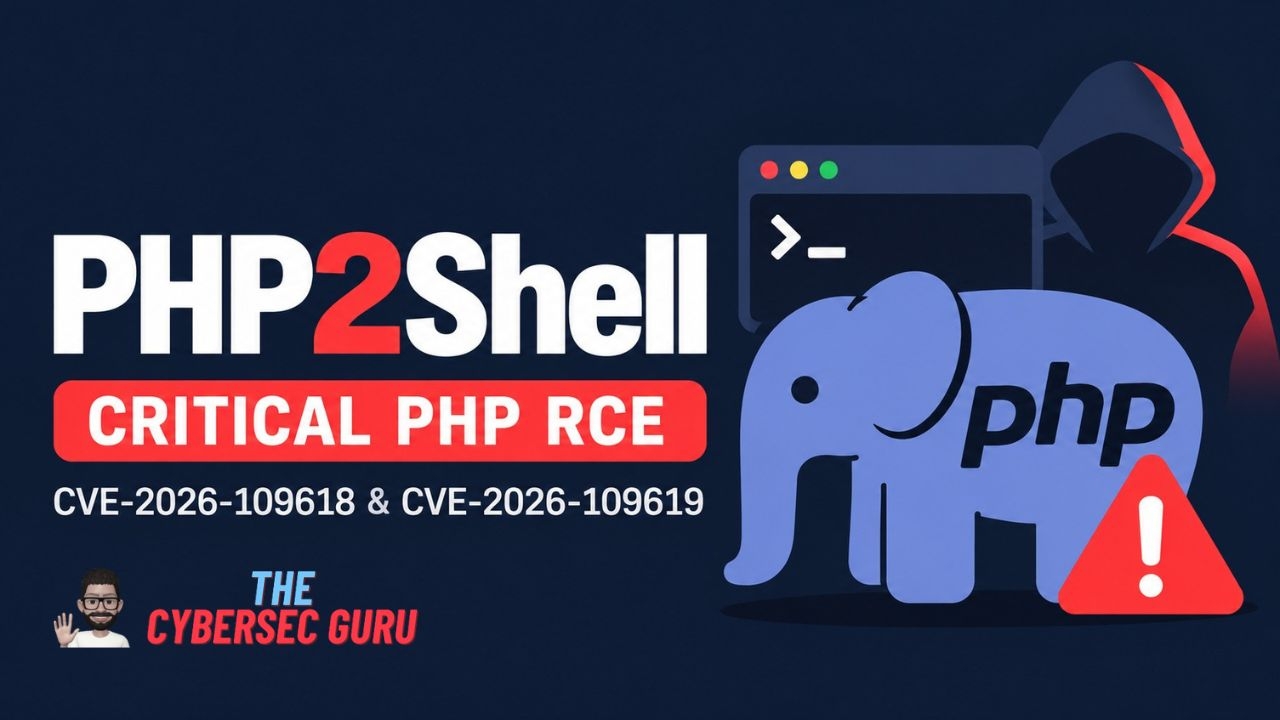
🚨 PHP2Shell: CRITICAL PHP RCE ALERT

Two vulnerabilities. CVE-2026-109618 & CVE-2026-109619. CVSS 9.2.

PHP powers WordPress, Magento and millions of websites. This is a reminder that patching your CMS isn't enough when the vulnerability lives in the PHP runtime itself.

⚠️ Check your PHP version. Prepare to patch. Don't rely on WordPress auto-updates.

Technical breakdown, exposure, detection & mitigation 👇
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/

#PHP #CyberSecurity #InfoSec

❞ Quoted postThe CyberSec Guru

Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps

The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-21

📊 9 updates from 3 sources:

🔹 iTnews - Security: Cloudflare warns fixing botched eMudhra certs goes beyond browsers
https://www.itnews.com.au/news/cloudflare-warns-fixing-botched-emudhra-certs-goes-beyond-browsers-629804?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 SecurityWeek: Accenture, Dragos, SANS Launch $10M Initiative to Defend Small US Utilities
https://www.securityweek.com/accenture-dragos-sans-launch-10m-initiative-to-defend-small-us-utilities/

🔹 The Hacker News: PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert
https://thehackernews.com/2026/10/php2shell-two-unpatched-critical-php.html

🔹 SecurityWeek: Hijacked Developer Account Used to Plant Stealer in OVHcloud CLI
https://www.securityweek.com/hijacked-developer-account-used-to-plant-stealer-in-ovhcloud-cli/

🔹 The Hacker News: Hackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare Intrusion
https://thehackernews.com/2026/10/hackers-hid-vasilek-backdoor-in-vmware.html

🔹 SecurityWeek: PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws
https://www.securityweek.com/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws/

🔹 The Hacker News: CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws
https://thehackernews.com/2026/10/cisa-orders-federal-agencies-to-patch.html

🔹 The Hacker News: State Bank of India Confirms Data Leak After 3,897 Customer Records Found on Dark Web
https://thehackernews.com/2026/10/state-bank-of-india-confirms-data-leak.html

🔹 iTnews - Security: Critical flaws strike PHP as disclosure embargo is broken
https://www.itnews.com.au/news/critical-flaws-strike-php-as-disclosure-embargo-is-broken-629794?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

#InfoSec #SecurityNews

iTnewsCloudflare warns fixing botched eMudhra certs goes beyond browsersServers, containers and apps need manual patching.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Unit 42 has unpicked a two-year intrusion at a telecoms provider. It began in September 2024 with FortiJump, a missing-authentication FortiManager flaw. One stolen archive held configs, credentials and private keys for 500-plus managed FortiGate firewalls: the provider's own and its clients'.

The implant found there, PEERSTITCH, lives only in memory. No disk file, no listening port, no outbound connection; it talks through legitimate FortiOS processes. The second flaw was patched in April, yet CISA listed it as exploited on 16 October. Patching closes the door; the stolen keys still work until someone rotates them.

https://unit42.paloaltonetworks.com/fortimanager-cve-2024-47575-peerstitch-malware/

#CyberSecurity #InfoSec #Fortinet

Unit 42Unit 42 Uncovers PEERSTITCH, a Stealthy FortiGate ImplantWe investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP Issues Emergency Warning for Critical Remote Code Execution Vulnerabilities

PHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.

**If you run any website or app built on PHP (WordPress, online shops, internal tools), install the emergency security updates as soon as they're released today at 14:00 UTC. Until you've patched, restrict access to internal PHP systems and admin pages to trusted networks only, and monitor your servers closely for unusual logins, new files or strange activity.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/php-issues-emergency-warning-for-critical-remote-code-execution-vulnerabilities-y-t-1-8-c/gD2P6Ple2L

BeyondMachinesPHP Issues Emergency Warning for Critical Remote Code Execution VulnerabilitiesPHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.
↩ Reply ♡ 0 · ↻ 0 ↗ Original