X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

The path to happiness and posterity runs through PHP. Here is some of the research dealing with that today - so far.

KrebsonSecurity: Widespread PHP Flaw May Cause Many Site Outages Today https://krebsonsecurity.com/2026/10/widespread-php-flaw-may-cause-many-site-outages-today/ @briankrebs

Akamai: Critical Remote Code Execution Vulnerabilities in PHP Core https://www.akamai.com/blog/security-research/critical-remote-code-execution-vulnerabilities-php-core

Cisco: Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers https://blog.talosintelligence.com/parasitizing-trust-how-legitimate-infrastructure-becomes-a-delivery-pipeline-for-attackers/ @TalosSecurity

CrowdStrike: Two critical memory-corruption RCE vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 have been disclosed in core PHP https://www.crowdstrike.com/en-us/blog/crowdstrike-protects-customers-from-php-rce-zero-days/

Kaspersky: Critical RCE vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) https://securelist.com/tr/php2shell-critical-vulnerabilities-in-php/121596/ @Kaspersky

Sophos: Proof-of-concept exploit released for PHP vulnerabilities (CVE-2026-109618, CVE-2026-109619) https://www.sophos.com/en-us/blog/proof-of-concept-exploit-released-for-php-vulnerabilities-109618-109619

Palo Alto: Millions of PHP Instances Exposed - What Organizations Need To Do Right Now https://www.paloaltonetworks.com/blog/2026/10/millions-of-php-instances-exposed-what-organizations-need-to-do-right-now/

VulnCheck: PHP2Shell Vulnerabilities: CVE-2026-109618 and CVE-2026-109619 https://www.vulncheck.com/blog/php2shell-vulnerabilities @vulncheck #infosec #vulnerability #threatresearch

krebsonsecurity.comWidespread PHP Flaw May Cause Many Site Outages Today – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://infosec.exchange/@badsamurai/117475644115110129

Stop doomscrolling your 47th “agentic AI will replace your SOC” thread and go watch @badsamurai at @BSidesPDX this Friday.

Community lists. Doing the fucking basics. Deterministic full-stops in the kill chain. No vendor magic beans, just free lists that block the shit your six-figure platform waved through.

Cyber intel is a team sport. Get your ass on the team.

#bsides #bsidespdx #blocklist #infosec

❞ Quoted postB'ad Samurai :ifin:

Love lists and doing the basics? I really, really do. So I’m speaking about it this Friday at BSidesPDX. This year’s theme is genuine human connection so Put Community Lists in your Kill Chain is a celebratory look at the great impact lists can have within your security program.

Infosec ExchangeB'ad Samurai :ifin: (@[email protected])Love lists and doing the basics? I really, really do. So I’m speaking about it this Friday at BSidesPDX. This year’s theme is **genuine human connection** so *Put Community Lists in your Kill Chain* is a celebratory look at the great impact lists can have within your security program. And there’s not a lick of AI in the talk or derived content. https://bsidespdx.org/events/2026/speakers.html#s
↩ Reply ♡ 0 · ↻ 0 ↗ Original

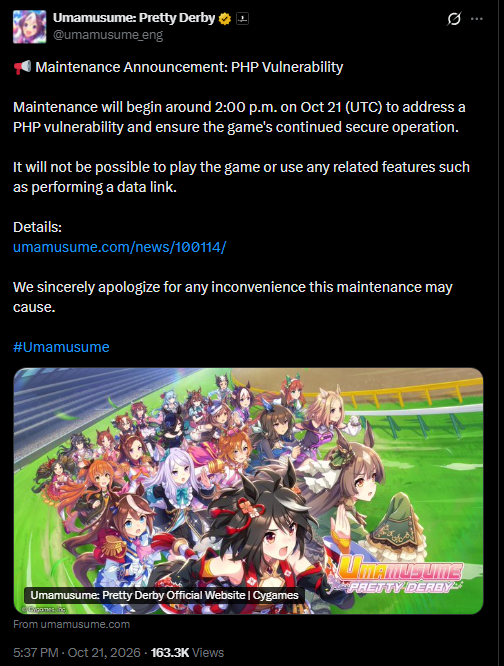
About that PHP flaw ... the race to own has begun.

"Security company Wiz, which is owned by Google, claimed its researchers discovered the vulnerabilities in PHP partially using AI tools, while OpenAI and security firm Calif also say they independently discovered the issues and worked together."

Wired: ‘This Is Not a Drill’: Critical PHP Vulnerabilities Are Setting the Internet on Fire https://www.wired.com/story/this-is-not-a-drill-2-php-vulnerabilities-are-setting-the-internet-on-fire/ @WIRED #infosec #vulnerability #PHP

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Shout-out to Misconfig Monday, a free weekly newsletter for small IT teams, sysadmins and MSPs with no SOC. Each issue covers the CISA KEV flaws to patch first, plus one misconfiguration to fix.

They recommend Patch or Pass, and we recommend them right back. If you like our Patch now / Batch / Watch calls for homelab gear, you'll like their work-side version.

https://misconfigmonday.beehiiv.com/

#infosec #sysadmin #PatchManagement #CISA #KEV

Misconfig MondayMisconfig Monday: Weekly Patch Priorities for Small IT TeamsExploited CISA KEV vulnerabilities to patch first, plus one security misconfiguration to fix. Free, weekly, for IT teams with no SOC.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : PALO ALTO NETWORKS

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Palo Alto Networks, qui est un partenaire KIOSQUE

Visiter leur site web : https://www.paloaltonetworks.com

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Palo Alto NetworksLeader in Cybersecurity Protection & Software for the Modern EnterprisesImplement Zero Trust, Secure your Network, Cloud workloads, Hybrid Workforce, Leverage Threat Intelligence & Security Consulting. Cybersecurity Services & Education for CISO’s, Head of Infrastructure, Network Security Engineers, Cloud Architects & SOC Managers
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Chaos Ransomware Group Claims Central Ohio Primary Care Breach Following Vishing Attack

Central Ohio Primary Care disclosed a data breach affecting approximately 1.4 million individuals after a vishing attack led to unauthorized access to internal systems. The Chaos ransomware group claimed responsibility and allegedly stole up to 362 GB of data containing Social Security numbers, financial information, and limited health information. COPC is offering complimentary credit monitoring and identity theft protection.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/chaos-ransomware-group-claims-central-ohio-primary-care-breach-following-vishing-attack-w-c-3-v-q/gD2P6Ple2L

BeyondMachinesChaos Ransomware Group Claims Central Ohio Primary Care Breach Following Vishing AttackCentral Ohio Primary Care disclosed a data breach affecting approximately 1.4 million individuals after a vishing attack led to unauthorized access to internal systems. The Chaos ransomware group claimed responsibility and allegedly stole up to 362 GB of data containing Social Security numbers, financial information, and limited health information. COPC is offering complimentary credit monitoring
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

You know things get serious when even the german Tagesschau publishes news on the subject:

https://www.tagesschau.de/wirtschaft/technologie/it-sicherheit-php-luecke-100.html

Meanwhile, the PHP Group published the fixes:
https://github.com/php/php-src/releases/tag/php-8.5.12

#PHP #PHP2Shell #InfoSec #SysAdmin #OpenSource #SelfHosted

tagesschau.deProgrammiersprache PHP: Sicherheitslücke bedroht weltweit WebseitenZahlreiche Webseiten und Onlinedienste weltweit sind derzeit in Gefahr: Grund ist eine Sicherheitslücke in der weitverbreiteten Programmiersprache PHP. Das Gefahrenpotenzial ist demnach extrem hoch.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Europe's digital estate is largely rented, not owned, and US law follows the landlord. My January piece on the kill-switch takes the aid sector as the test case: an NGO coordinating relief under a sanctions regime could have its tools cut off by someone else's foreign policy, and its case files on vulnerable people sit within reach of US warrants.

The plan runs in three parts: a sovereign desktop pilot for European NGOs on open-source tools, an EU cloud scheme made mandatory for sensitive data, and binding safe corridors for essential services so exit stays possible.

https://altlibre.com/blog/american-kill-switch-europe-digital-dependence

#DigitalSovereignty #OpenSource #InfoSec

AltLibreThe American Kill-Switch - AltLibreEurope runs on rented American software and the CLOUD Act reaches it. A three-pillar plan: sovereign desktop, European cloud, a new transatlantic compact.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 PHP2Shell: Two critical RCE vulnerabilities. Emergency patches released.

CVE-2026-109618 and CVE-2026-109619 are rated CVSS 9.2/10 (CVSS v4.0) and can allow unauthenticated remote code execution against vulnerable PHP installations. The flaws affect PHP's core runtime, not just a particular CMS or plugin.

🔧 Fixed PHP releases:
• PHP 8.5 → 8.5.12
• PHP 8.4 → 8.4.27
• PHP 8.3 → 8.3.36
• PHP 8.2 → 8.2.35

⚠️ Running PHP 8.1 or older? These branches no longer receive regular upstream security updates. PHP has also provided minimal source-level backports for PHP 8.1, 8.0 and 7.4. Check your distribution or hosting provider for patched packages. Otherwise, upgrade to a supported branch, PHP 8.2 or later.

📊 Our analysis of over 7 million PHP websites found that 46.1% of sites disclosing their PHP version run an End-of-Life branch.

This is a serious exposure problem. Updating WordPress, Laravel or another application alone will not fix a vulnerability in the PHP runtime.

✅ Update PHP immediately.
✅ Verify the actual runtime used by PHP-FPM, Apache, CGI or your hosting environment.
✅ Check vendor advisories if your system uses backported security patches.

The PHP security team says there are no complete mitigations. Updating is the only safe choice.

Full technical analysis, vulnerability details and remediation:
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/

#InfoSec #CyberSecurity #PHP #RCE #CVE

❞ Quoted postThe CyberSec Guru

Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps

The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Klein ISD Data Breach Exposes Personal Information of Approximately 38,000 Individuals

Klein Independent School District disclosed a data breach affecting approximately 37,966 individuals after attackers exploited a vulnerability in a third-party software product used by Frontline Education. The incident exposed sensitive personal information, including Social Security numbers, and affected individuals are being offered two years of credit monitoring and identity theft protection.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/klein-isd-data-breach-exposes-personal-information-of-approximately-38000-individuals-j-r-5-f-d/gD2P6Ple2L

BeyondMachinesKlein ISD Data Breach Exposes Personal Information of Approximately 38,000 IndividualsKlein Independent School District disclosed a data breach affecting approximately 37,966 individuals after attackers exploited a vulnerability in a third-party software product used by Frontline Education. The incident exposed sensitive personal information, including Social Security numbers, and affected individuals are being offered two years of credit monitoring and identity theft protection.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🛡️ Staff Engineer, Cloud Security at Toast
📍 Remote (US)
💰 $193k–$309k/yr

Apply: https://blueteamjobs.com/job/staff-engineer-cloud-security-toast-jsz3ws/

#BlueTeam #InfoSec #CyberSecurityJobs #CloudSecurityEngineer

BlueTeamJobsStaff Engineer, Cloud Security at Toast | BlueTeamJobsToast is hiring a Staff Engineer, Cloud Security, Remote (US). Pay: $193k–$309k a year. Toast creates technology to help restaurants and local businesses…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 When a page could not be scanned, the result page now shows one notice with the reason, still lists the site's earlier scans, and says plainly that no security verdict was made.

https://scanmalware.com/changelog?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610201934#2026-10-20T19:34:00Z-3194fa44

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comChangelog - ScanMalware.comRecent changes and updates to ScanMalware.com - URL and website security scanner.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ PATCH NOW

Two critical PHP core flaws (CVE-2026-109618/619, CVSS 9.2) leaked before the patch shipped.

A public proof-of-concept is circulating. The emergency fix covers PHP 8.2 to 8.5.

Running PHP? Update the moment it drops.

https://suriq.io/blog/php-core-rce-cve-2026-109618-php2shell

#CVE #DataBreach #infosec #cybersecurity

Rows of server racks sharing one loosened central PHP runtime component highlighted in amber
SuriqPHP CVE-2026-109618 & 109619: Critical Core RCE Leaked EarlyPHP is shipping an emergency fix for two critical CVSS 9.2 core flaws, CVE-2026-109618 and CVE-2026-109619, after details leaked early and a public proof-of-concept appeared. What defenders should do now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Happy PHP Wednesday.

"In the last hour, two remote code execution vulnerabilities in PHP have been leaked. These vulnerabilities were previously scheduled under embargo and due for release on Thursday at 11 am ET," watchTowr CEO Benjamin Harris told BleepingComputer.

https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/

#php #vulnerability #patchmanagement #infosec #incidentresponse

BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : DEVOLUTIONS

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous Devolutions, qui est un partenaire KIOSQUE!
Visiter leur site web : https://devolutions.net/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
#hacking #infosec #hackfest #cybersecurity

Media attachment
DevolutionsOne IT Ecosystem for Connections & PAM | DevolutionsDiscover one Devolutions ecosystem for remote connections, passwords, privileged access, and automation — secure productivity for IT professionals worldwide.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

STS Aviation Group Data Breach Exposes Biometric and Financial Records

STS Aviation Group disclosed a long-term data breach where unauthorized actors accessed sensitive employee and personal data. The company is providing credit monitoring to affected individuals after a year-long investigation confirmed the theft of medical, financial, and biometric information.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/sts-aviation-group-data-breach-exposes-biometric-and-financial-records-1-c-5-p-m/gD2P6Ple2L

BeyondMachinesSTS Aviation Group Data Breach Exposes Biometric and Financial RecordsSTS Aviation Group disclosed a long-term data breach where unauthorized actors accessed sensitive employee and personal data. The company is providing credit monitoring to affected individuals after a year-long investigation confirmed the theft of medical, financial, and biometric information.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

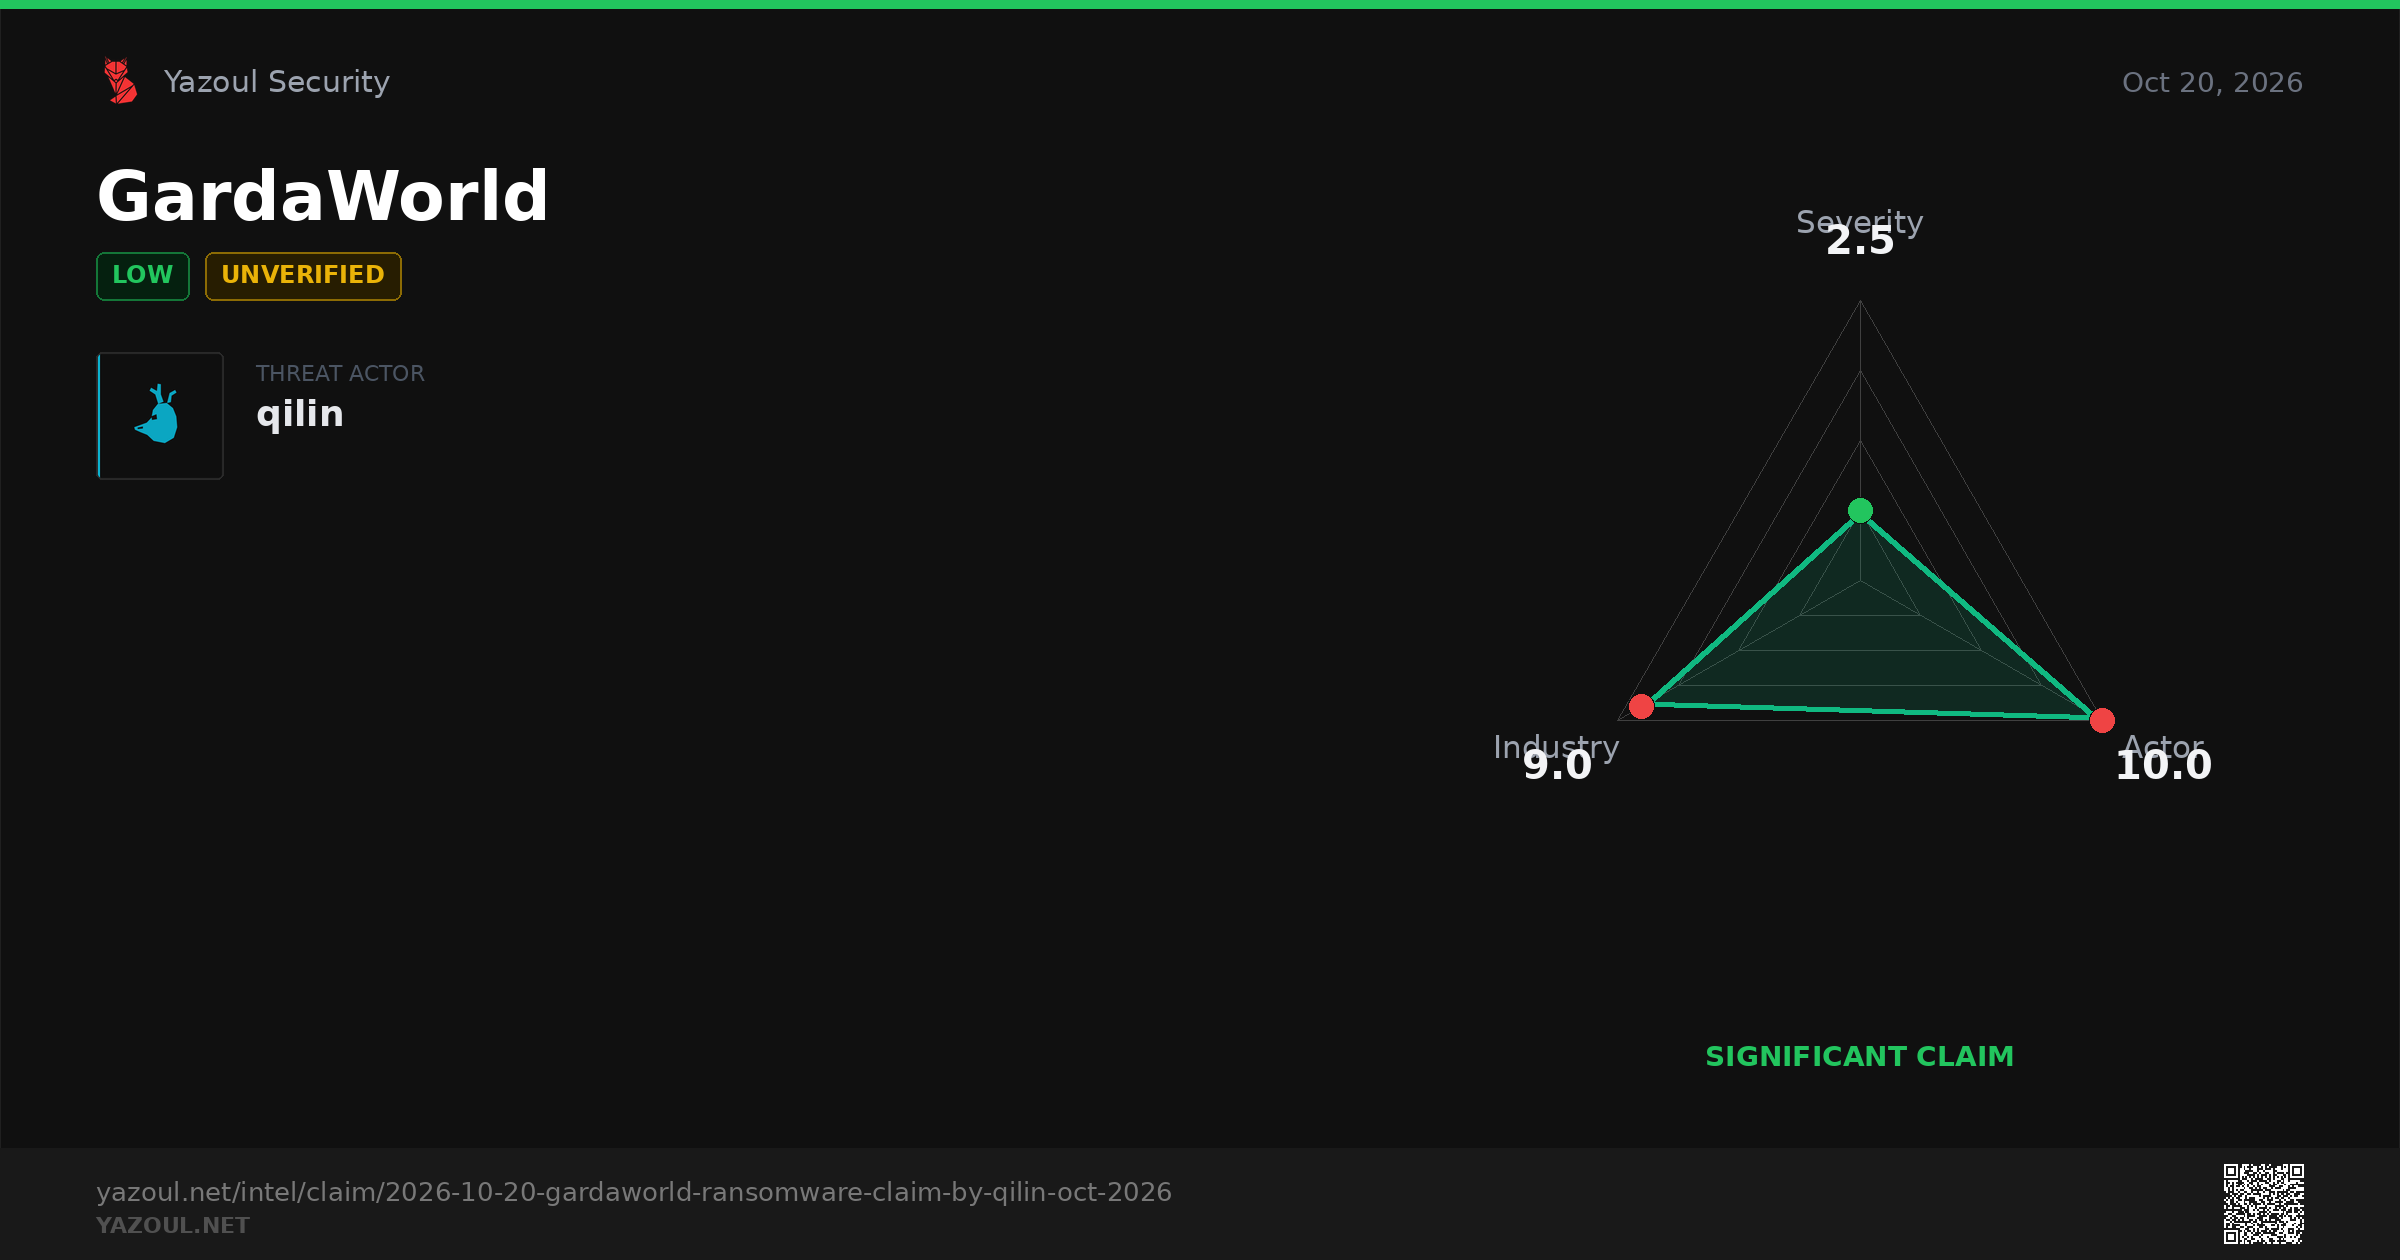
🛡 THREAT INTEL | GardaWorld

🟢 Actor "qilin" claims Undisclosed

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-20-gardaworld-ransomware-claim-by-qilin-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityGardaWorld Ransomware Claim by Qilin (Oct 2026)Qilin allegedly claims GardaWorld as a ransomware victim. Unverified leak site post, undisclosed data volume. Read our cautious threat intel analysis and stay alert.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 Improved AI Security Verdict accuracy and clearer explanations for pages that lead to a sign-in form.

https://scanmalware.com/changelog?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610201330#2026-10-20T13:30:00Z-a7723dd9

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comChangelog - ScanMalware.comRecent changes and updates to ScanMalware.com - URL and website security scanner.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Anomaly Silently Patches Critical RCE in OpenCode AI Agent

Anomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.

**If you use OpenCode on Windows or WSL, upgrade to version 1.18.33 or later immediately, because a malicious or hijacked MCP server can take over your machine and everything on it (code, SSH keys, cloud tokens). Until you can update, remove any remote MCP servers you don't fully trust from your OpenCode configuration, and check your developers' machines yourself, since security scanners won't flag this one.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/anomaly-silently-patches-critical-rce-in-opencode-ai-agent-k-u-t-k-o/gD2P6Ple2L

BeyondMachinesAnomaly Silently Patches Critical RCE in OpenCode AI AgentAnomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.
↩ Reply ♡ 0 · ↻ 0 ↗ Original