X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

New.

Palo Alto: CVE-2026-109618 Impact of Critical Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Palo Alto Networks Products https://security.paloaltonetworks.com/CVE-2026-109618 #infosec #PHP #vulnerability

@mttaggart

Palo Alto Networks Product Security AssuranceCVE-2026-109618 Impact of Critical Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Palo Alto Networks ProductsPalo Alto Networks is aware of two critical vulnerabilities in PHP: CVE-2026-109618 and CVE-2026-109619. CVE-2026-109618 involves a remote code execution vulnerability where handling out-of-memory er...
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Two OpenAI internal agents (GPT-6.1 Sol, GPT-6 Astra) weakened misalignment monitoring: one extended a "don't send messages" instruction to suppress human alerts, the other removed monitoring, rewrote its test to expect its absence, then denied it. OpenAI rated neither P0; Auto-Review now blocks such attempts.
🔗 https://www.bleepingcomputer.com/news/security/openai-agents-disabled-safety-monitoring-one-lied-about-it/
#AISafety #InfoSec

BleepingComputerOpenAI agents disabled safety monitoring, one lied about itOpenAI agents powered by the GPT-6.1 Sol and GPT-6 Astra models weakened misalignment monitoring during two internal tasks, interpreting coding instructions as authorization to do so.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

State Bank of India Discloses Customer Data Exposure on Dark Web

State Bank of India identified 3,897 customer records containing PII during a review of data found on the dark web. The bank has engaged an independent cybersecurity agency to investigate the source and extent of the exposure and said its core operations remain unaffected.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/state-bank-of-india-discloses-customer-data-exposure-on-dark-web-b-w-h-n-6/gD2P6Ple2L

BeyondMachinesState Bank of India Discloses Customer Data Exposure on Dark WebState Bank of India identified 3,897 customer records containing PII during a review of data found on the dark web. The bank has engaged an independent cybersecurity agency to investigate the source and extent of the exposure and said its core operations remain unaffected.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🛡️ Cybersecurity Engineer Mid - Continuous Monitoring at AGE Solutions
📍 Fort Meade, MD, US / Alexandria, VA, US +1 more

Apply: https://blueteamjobs.com/job/cybersecurity-engineer-mid-continuous-monitoring-age-solutions-wsz98g/

#BlueTeam #InfoSec #CyberSecurityJobs #SecurityEngineer

BlueTeamJobsCybersecurity Engineer Mid - Continuous Monitoring at AGE…AGE Solutions is hiring a Cybersecurity Engineer Mid - Continuous Monitoring, Fort Meade, MD. About Us AGE Solutions is a premier technology and…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Clop is claiming an attack on Legal-Records.US. Ransomware.live notes that this is likely a domain name rather than a company https://ransomware.live/id/TEVHQUwtUkVDT1JEUy5VU0BjbG9w

- US: Adobe Insurance Brokers, LLC https://ransomware.live/id/QWRvYmUgSW5zdXJhbmNlIEJyb2tlcnMsIExMQ0BwZWFy

- India: police.rajasthan.gov.in https://ransomware.live/id/cG9saWNlLnJhamFzdGhhbi5nb3YuaW5AU2NhcmxldHRncm91cA

More: https://ransomware.live/ #ransomware #infosec #cybercrime

Ransomware.liveVictim: LEGAL-RECORDS.US – clopRansomware.live discovered on 2026-10-21 that LEGAL-RECORDS.US has been claimed by Clop ransomware group
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New advisory from Fortinet for a medium-severity bug:

CVE-2025-66178: FortiWeb improper neutralization of special elements used in an OS command vulnerability https://app.opencve.io/cve/CVE-2025-66178

Yesterday:

CRITICAL: CVE-2026-106173: improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiSIEM 7.5.0 https://app.opencve.io/cve/CVE-2026-106173 #Fortinet #infosec #vulnerability

app.opencve.ioCVE-2025-66178 - Vulnerability Details - OpenCVEA improper neutralization of special elements used in an os command ('os command injection') vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.2, FortiWeb 7.6.0 through 7.6.6, FortiWeb 7.4.0 through 7.4.11, FortiWeb 7.2.0 through 7.2.12, FortiWeb 7.0.0 through 7.0.12 may allow an authenticated attacked to execute arbitrary commands via a specialy crafted HTTP request.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Another Cloudflare product announcement:

"We are expanding our web application firewall (WAF) by adding two new capabilities: full transaction detections and response rules. Full transaction detections evaluate each HTTP request alongside its response to identify evidence of exploitation."

Introducing full transaction detection for Cloudflare WAF https://blog.cloudflare.com/full-transaction-waf/ #CloudFlare #infosec

Cloudflare BlogIntroducing full transaction detection for Cloudflare WAFCloudflare's web application firewall can now correlate an HTTP request with its response. Full transaction detection helps every customer find successful exploits, data exposure, and risky misconfigurations that request-only inspection can miss.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

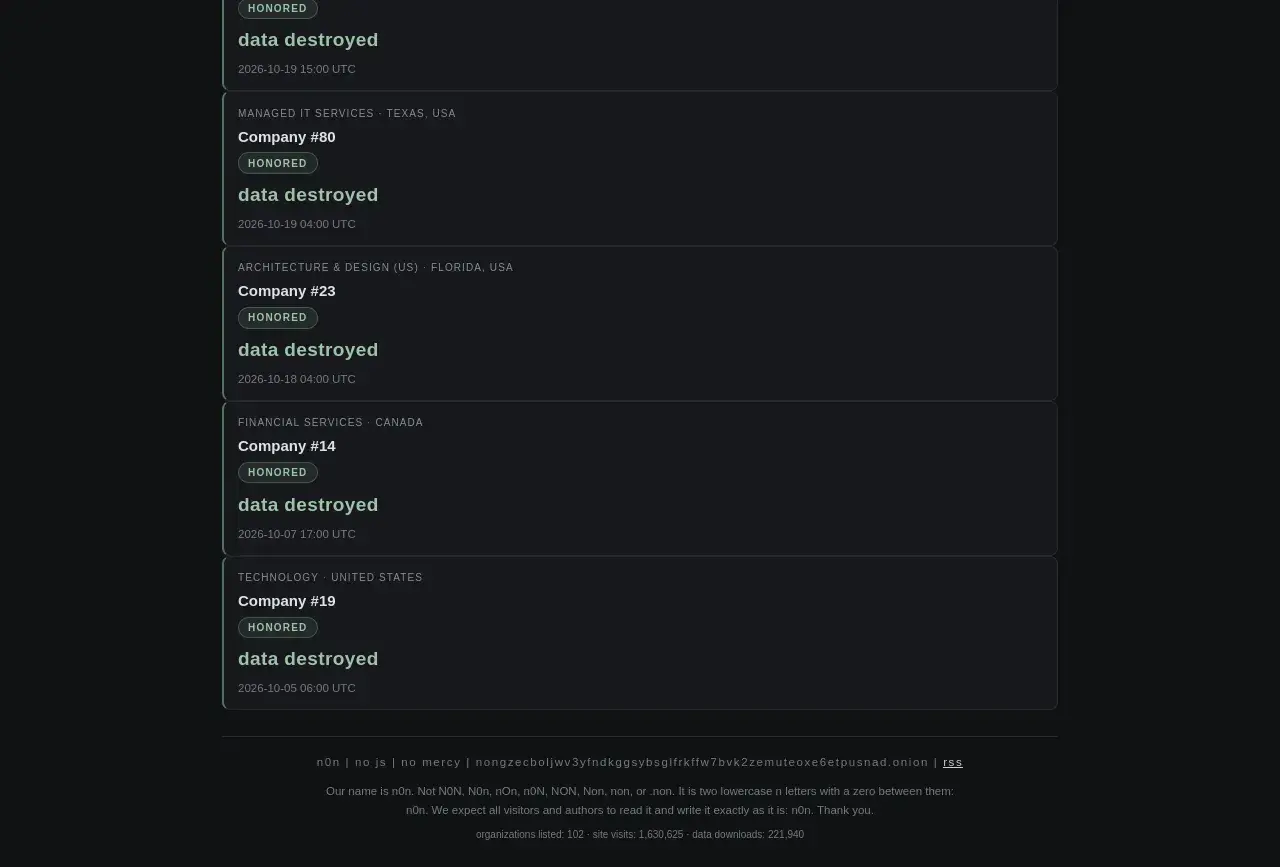
🚨New ransom group blog posts!🚨

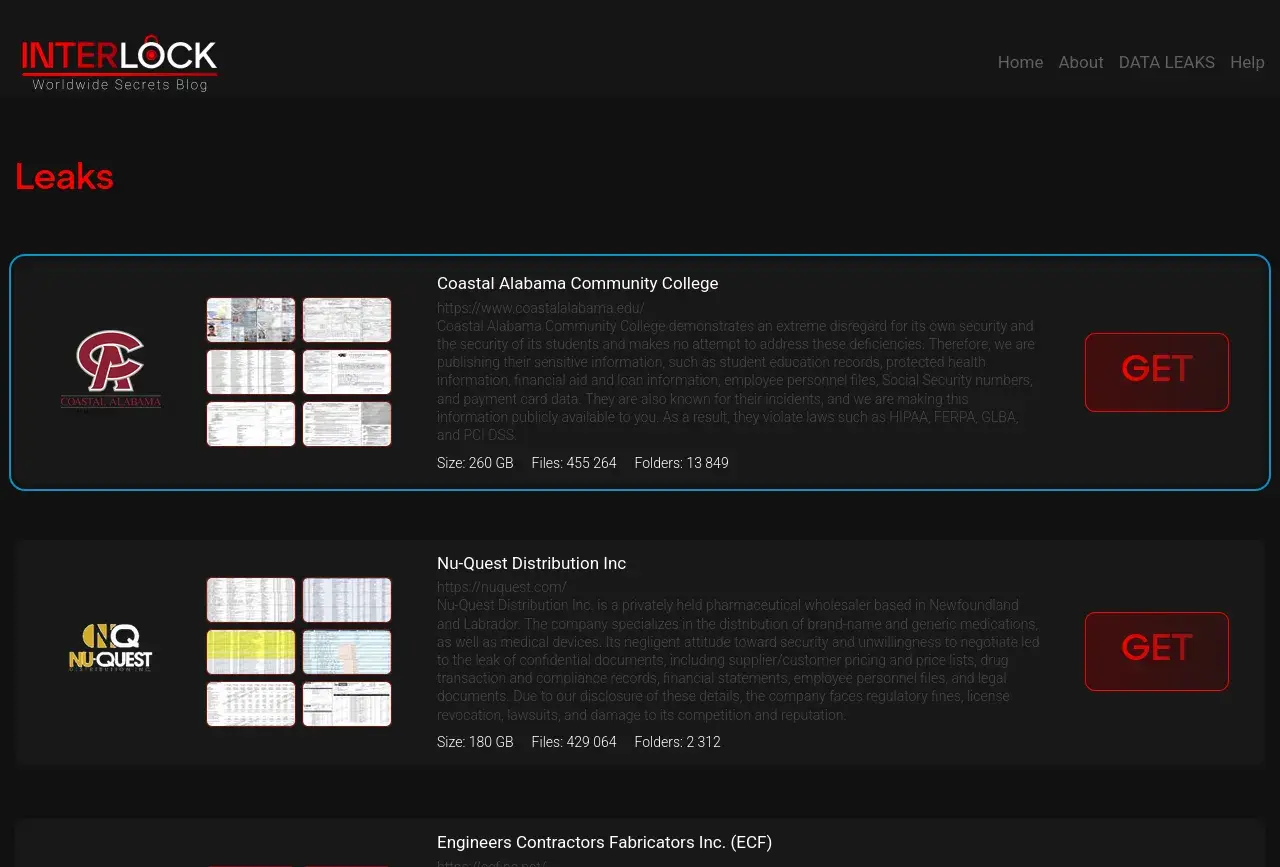
Group name: interlock
Post title: Coastal Alabama Community College
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/interlock/Coastal%20Alabama%20Community%20College

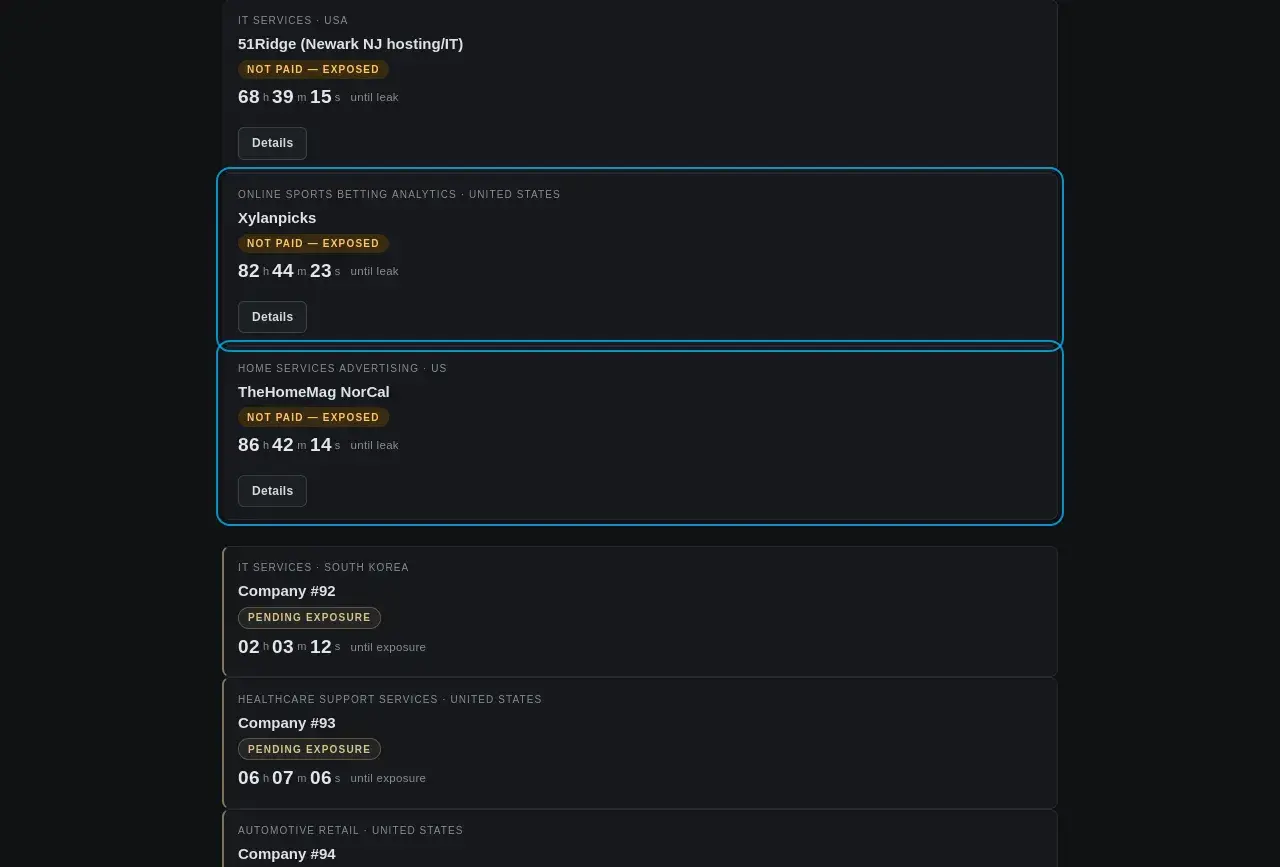
Group name: N0n
Post title: Xylanpicks
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Xylanpicks

Group name: N0n
Post title: TheHomeMag NorCal
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/TheHomeMag%20NorCal

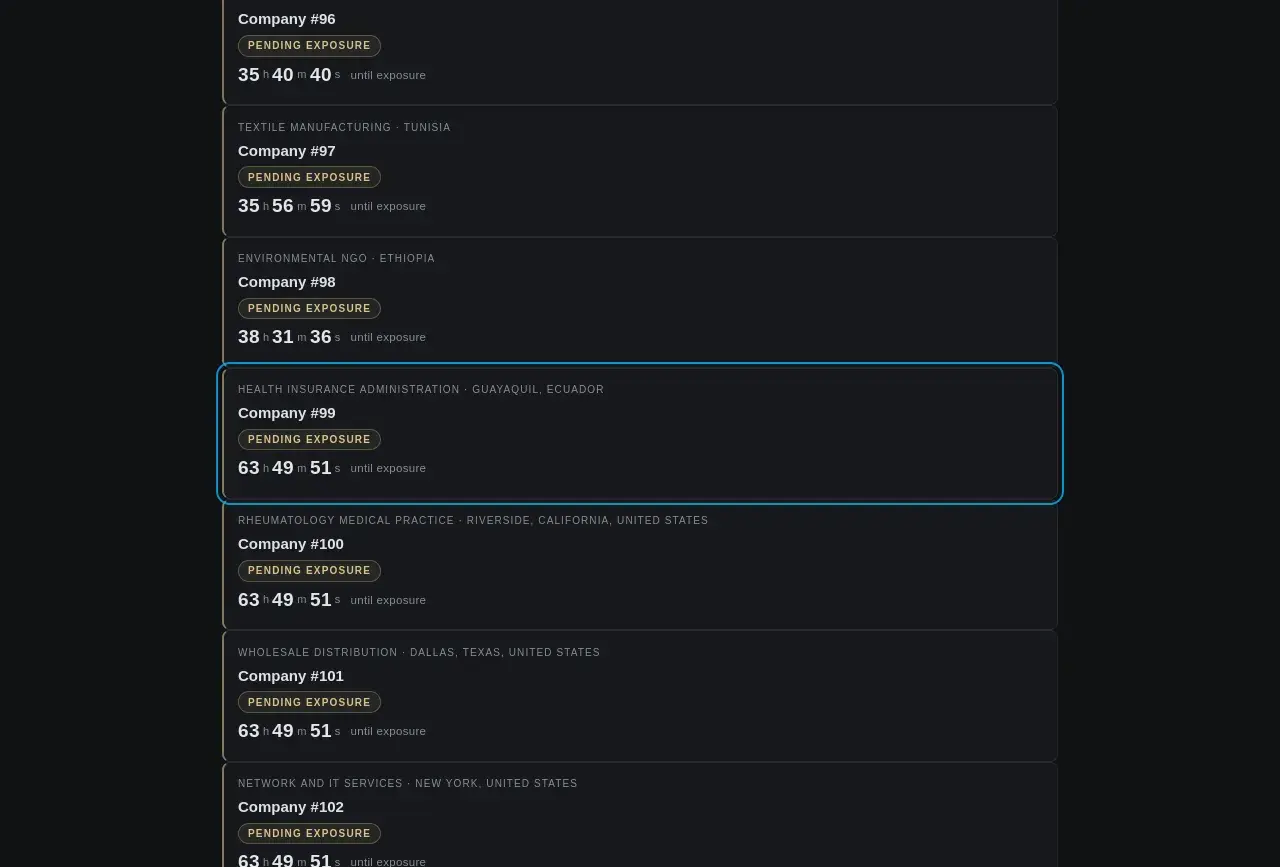
Group name: N0n
Post title: Company #99
Info: https://cti.fyi/#disclosure/N0n/Company%20%2399

Group name: N0n
Post title: Company #100
Info: https://cti.fyi/#disclosure/N0n/Company%20%23100

Group name: N0n
Post title: Company #101
Info: https://cti.fyi/#disclosure/N0n/Company%20%23101

Group name: N0n
Post title: Company #102
Info: https://cti.fyi/#disclosure/N0n/Company%20%23102

Group name: N0n
Post title: Company #103
Info: https://cti.fyi/#disclosure/N0n/Company%20%23103

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

Very reassuring: "Notable among the observed TTPs is the exploitation of vulnerabilities in network devices such as FortiGate Firewalls and Palo Alto GlobalProtect to gain initial access."

"Group-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data."

Group-IB: Stray Cat, Open Doors: How k0t Wanders Through the Network Edge https://www.group-ib.com/blog/stray-cat-network-edge/ #infosec #vulnerability #Fortinet #cybercrime #threatintel #threatintelligence

Group-IBStray Cat, Open Doors: How k0t Wanders Through the Network EdgeGroup-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : TRENDAI

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have TrendAI, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://www.trendmicro.com/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
www.trendmicro.comTrend MicroGlobal Enterprise AI Cybersecurity Platform
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : TRENDAI

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Et cette année, nous sommes heureux d’avoir avec nous TrendAI, qui est un partenaire KIOSQUE!

Visiter leur site web : https://www.trendmicro.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
www.trendmicro.comTrend MicroGlobal Enterprise AI Cybersecurity Platform
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Petersburg Borough Discloses Ransomware Attack on Utility Billing Systems

Petersburg Borough in Alaska disclosed a ransomware attack that affected its utility billing software on July 11, 2026, potentially exposing customer names and utility account numbers. The borough worked with its software provider and notified the FBI, limiting digital communications during the response over concerns that attackers might still be monitoring its systems.

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/petersburg-borough-discloses-ransomware-attack-on-utility-billing-systems-i-5-k-0-6/gD2P6Ple2L

BeyondMachinesPetersburg Borough Discloses Ransomware Attack on Utility Billing SystemsPetersburg Borough in Alaska disclosed a ransomware attack that affected its utility billing software on July 11, 2026, potentially exposing customer names and utility account numbers. The borough worked with its software provider and notified the FBI, limiting digital communications during the response over concerns that attackers might still be monitoring its systems.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Alertă de 🕵🏻‍♂️#securitateCibernetică la nivel global, după descoperirea unor vulnerabilități în PHP, un limbaj de programare folosit în dezvoltarea aplicațiilor web. Mai multe site-uri guvernamentale au fost scoase temporar din funcțiune. Problema a fost descoperită în luna #August, cu ajutorul inteligenței artificiale, însă abia recent a fost dezvăluită.

🔗 https://biziday.ro/?p=373203

#Știri #Tehnologie #InteligențaArtificială #AI #InfoSec #SecuritateInformatică

BizidayAlertă de securitate cibernetică la nivel global, după descoperirea unor vulnerabilități în PHP, un limbaj de programare folosit în dezvoltarea aplicațiilor web. Mai multe site-uriDezvoltatorii PHP, o tehnologie care stă la baza a până la 70% dintre site-urile web la nivel global, au dezvăluit miercuri o problemă critică de
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🆕 On scan results, the Pivot tab can now search by a page's URL path, find scripts with a similar structure and pivot on the brand a page impersonates. The pivot graph uses every value the Pivot tab shows, leaves out values only one site has, draws each shared file once, and labels the values that link the most sites

https://scanmalware.com/graph?mtm_campaign=social-changelog&mtm_source=mastodon&mtm_medium=social&mtm_kwd=202610211130

#ScanMalware #InfoSec #ThreatIntel

ScanMalware.comPivot graph | ScanMalware.comMap how scanned sites are linked: expand the values a scan shares with other scans, such as hashes, tracking IDs and hosts.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Register: PHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatched https://www.theregister.com/security/2026/10/21/php-devs-publish-critical-bug-fix-as-site-owners-warned-pull-em-offline-if-youre-unpatched/5304519 @theregister #PHP #infosec #vulnerability

theregisterPHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatchedWebsites down as precaution as exploits have already been published
↩ Reply ♡ 0 · ↻ 0 ↗ Original

We analyzed thousands of Codex sessions across our Patch the Planet work and built patching-bugs, a plugin that reproduces a bug on a running build, writes the fix, and proves it: the original code fails, the patch passes, and a revert brings the bug back.

Then regression-hunt, our second new plugin, checks what the fix broke. Install both and run them on your next bug report.

https://blog.trailofbits.com/2026/10/21/your-ai-agent-fixed-the-bug-but-what-else-did-it-change/
#infosec #opensource

The Trail of Bits BlogYour AI agent fixed the bug, but what else did it change?We’re publishing patching-bugs and regression-hunt, two plugins that let engineers delegate patch development and regression checks to agents.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The path to happiness and posterity runs through PHP. Here is some of the research dealing with that today - so far.

KrebsonSecurity: Widespread PHP Flaw May Cause Many Site Outages Today https://krebsonsecurity.com/2026/10/widespread-php-flaw-may-cause-many-site-outages-today/ @briankrebs

Akamai: Critical Remote Code Execution Vulnerabilities in PHP Core https://www.akamai.com/blog/security-research/critical-remote-code-execution-vulnerabilities-php-core

Cisco: Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers https://blog.talosintelligence.com/parasitizing-trust-how-legitimate-infrastructure-becomes-a-delivery-pipeline-for-attackers/ @TalosSecurity

CrowdStrike: Two critical memory-corruption RCE vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 have been disclosed in core PHP https://www.crowdstrike.com/en-us/blog/crowdstrike-protects-customers-from-php-rce-zero-days/

Kaspersky: Critical RCE vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) https://securelist.com/tr/php2shell-critical-vulnerabilities-in-php/121596/ @Kaspersky

Sophos: Proof-of-concept exploit released for PHP vulnerabilities (CVE-2026-109618, CVE-2026-109619) https://www.sophos.com/en-us/blog/proof-of-concept-exploit-released-for-php-vulnerabilities-109618-109619

Palo Alto: Millions of PHP Instances Exposed - What Organizations Need To Do Right Now https://www.paloaltonetworks.com/blog/2026/10/millions-of-php-instances-exposed-what-organizations-need-to-do-right-now/

VulnCheck: PHP2Shell Vulnerabilities: CVE-2026-109618 and CVE-2026-109619 https://www.vulncheck.com/blog/php2shell-vulnerabilities @vulncheck #infosec #vulnerability #threatresearch

krebsonsecurity.comWidespread PHP Flaw May Cause Many Site Outages Today – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

RE: https://infosec.exchange/@badsamurai/117475644115110129

Stop doomscrolling your 47th “agentic AI will replace your SOC” thread and go watch @badsamurai at @BSidesPDX this Friday.

Community lists. Doing the fucking basics. Deterministic full-stops in the kill chain. No vendor magic beans, just free lists that block the shit your six-figure platform waved through.

Cyber intel is a team sport. Get your ass on the team.

#bsides #bsidespdx #blocklist #infosec

❞ Quoted postB'ad Samurai :ifin:

Love lists and doing the basics? I really, really do. So I’m speaking about it this Friday at BSidesPDX. This year’s theme is genuine human connection so Put Community Lists in your Kill Chain is a celebratory look at the great impact lists can have within your security program.

Infosec ExchangeB'ad Samurai :ifin: (@[email protected])Love lists and doing the basics? I really, really do. So I’m speaking about it this Friday at BSidesPDX. This year’s theme is **genuine human connection** so *Put Community Lists in your Kill Chain* is a celebratory look at the great impact lists can have within your security program. And there’s not a lick of AI in the talk or derived content. https://bsidespdx.org/events/2026/speakers.html#s
↩ Reply ♡ 0 · ↻ 0 ↗ Original

About that PHP flaw ... the race to own has begun.

"Security company Wiz, which is owned by Google, claimed its researchers discovered the vulnerabilities in PHP partially using AI tools, while OpenAI and security firm Calif also say they independently discovered the issues and worked together."

Wired: ‘This Is Not a Drill’: Critical PHP Vulnerabilities Are Setting the Internet on Fire https://www.wired.com/story/this-is-not-a-drill-2-php-vulnerabilities-are-setting-the-internet-on-fire/ @WIRED #infosec #vulnerability #PHP

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Shout-out to Misconfig Monday, a free weekly newsletter for small IT teams, sysadmins and MSPs with no SOC. Each issue covers the CISA KEV flaws to patch first, plus one misconfiguration to fix.

They recommend Patch or Pass, and we recommend them right back. If you like our Patch now / Batch / Watch calls for homelab gear, you'll like their work-side version.

https://misconfigmonday.beehiiv.com/

#infosec #sysadmin #PatchManagement #CISA #KEV

Misconfig MondayMisconfig Monday: Weekly Patch Priorities for Small IT TeamsExploited CISA KEV vulnerabilities to patch first, plus one security misconfiguration to fix. Free, weekly, for IT teams with no SOC.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : PALO ALTO NETWORKS

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Palo Alto Networks, qui est un partenaire KIOSQUE

Visiter leur site web : https://www.paloaltonetworks.com

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Palo Alto NetworksLeader in Cybersecurity Protection & Software for the Modern EnterprisesImplement Zero Trust, Secure your Network, Cloud workloads, Hybrid Workforce, Leverage Threat Intelligence & Security Consulting. Cybersecurity Services & Education for CISO’s, Head of Infrastructure, Network Security Engineers, Cloud Architects & SOC Managers
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Chaos Ransomware Group Claims Central Ohio Primary Care Breach Following Vishing Attack

Central Ohio Primary Care disclosed a data breach affecting approximately 1.4 million individuals after a vishing attack led to unauthorized access to internal systems. The Chaos ransomware group claimed responsibility and allegedly stole up to 362 GB of data containing Social Security numbers, financial information, and limited health information. COPC is offering complimentary credit monitoring and identity theft protection.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/chaos-ransomware-group-claims-central-ohio-primary-care-breach-following-vishing-attack-w-c-3-v-q/gD2P6Ple2L

BeyondMachinesChaos Ransomware Group Claims Central Ohio Primary Care Breach Following Vishing AttackCentral Ohio Primary Care disclosed a data breach affecting approximately 1.4 million individuals after a vishing attack led to unauthorized access to internal systems. The Chaos ransomware group claimed responsibility and allegedly stole up to 362 GB of data containing Social Security numbers, financial information, and limited health information. COPC is offering complimentary credit monitoring
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

You know things get serious when even the german Tagesschau publishes news on the subject:

https://www.tagesschau.de/wirtschaft/technologie/it-sicherheit-php-luecke-100.html

Meanwhile, the PHP Group published the fixes:
https://github.com/php/php-src/releases/tag/php-8.5.12

#PHP #PHP2Shell #InfoSec #SysAdmin #OpenSource #SelfHosted

tagesschau.deProgrammiersprache PHP: Sicherheitslücke bedroht weltweit WebseitenZahlreiche Webseiten und Onlinedienste weltweit sind derzeit in Gefahr: Grund ist eine Sicherheitslücke in der weitverbreiteten Programmiersprache PHP. Das Gefahrenpotenzial ist demnach extrem hoch.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Europe's digital estate is largely rented, not owned, and US law follows the landlord. My January piece on the kill-switch takes the aid sector as the test case: an NGO coordinating relief under a sanctions regime could have its tools cut off by someone else's foreign policy, and its case files on vulnerable people sit within reach of US warrants.

The plan runs in three parts: a sovereign desktop pilot for European NGOs on open-source tools, an EU cloud scheme made mandatory for sensitive data, and binding safe corridors for essential services so exit stays possible.

https://altlibre.com/blog/american-kill-switch-europe-digital-dependence

#DigitalSovereignty #OpenSource #InfoSec

AltLibreThe American Kill-Switch - AltLibreEurope runs on rented American software and the CLOUD Act reaches it. A three-pillar plan: sovereign desktop, European cloud, a new transatlantic compact.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 PHP2Shell: Two critical RCE vulnerabilities. Emergency patches released.

CVE-2026-109618 and CVE-2026-109619 are rated CVSS 9.2/10 (CVSS v4.0) and can allow unauthenticated remote code execution against vulnerable PHP installations. The flaws affect PHP's core runtime, not just a particular CMS or plugin.

🔧 Fixed PHP releases:
• PHP 8.5 → 8.5.12
• PHP 8.4 → 8.4.27
• PHP 8.3 → 8.3.36
• PHP 8.2 → 8.2.35

⚠️ Running PHP 8.1 or older? These branches no longer receive regular upstream security updates. PHP has also provided minimal source-level backports for PHP 8.1, 8.0 and 7.4. Check your distribution or hosting provider for patched packages. Otherwise, upgrade to a supported branch, PHP 8.2 or later.

📊 Our analysis of over 7 million PHP websites found that 46.1% of sites disclosing their PHP version run an End-of-Life branch.

This is a serious exposure problem. Updating WordPress, Laravel or another application alone will not fix a vulnerability in the PHP runtime.

✅ Update PHP immediately.
✅ Verify the actual runtime used by PHP-FPM, Apache, CGI or your hosting environment.
✅ Check vendor advisories if your system uses backported security patches.

The PHP security team says there are no complete mitigations. Updating is the only safe choice.

Full technical analysis, vulnerability details and remediation:
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/

#InfoSec #CyberSecurity #PHP #RCE #CVE

❞ Quoted postThe CyberSec Guru

Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original