ASN: AS4837
Location: Shanghai, CN
Added: 2026-10-17T11:58
Sensitive media · Show
Public posts with this hashtag.
ASN: AS4837
Location: Shanghai, CN
Added: 2026-10-17T11:58
Possible Phishing 🎣
on: ⚠️hxxps[:]//instagramlogin77[.]blogspot[.]com/?m=1
🧬 Analysis at: https://urldna.io/scan/6ad64cbe3b77500004c2c0fa
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Enterprise controls can't keep up with AI agents
🚨 Companies are deploying AI agents faster than they can control them. Organizations struggle to track what these agents access, do, or if they can stop them. Traditional security systems aren't built for autonomous AI. The result? Potential security gaps and leaders considering quiet incident handling. The shift ahead: focus on managing existing agents responsibly, not just rolling out more.
https://www.techtarget.com/ai/news/366652493/Enterprise-controls-cant-keep-up-with-AI-agents
 AI & Emerging TechEnterprise controls can't keep up with AI agents | TechTargetCompanies are giving agents more authority, but many are still struggling to track what they can access, what they're doing and how to stop them.
Found with BugTraceAI so far:
• Wallos — CVE-2026-27479 (7.7)
• ZoneMinder — CVE-2026-27470 (8.8)
• Piwigo — CVE-2026-27834 (7.2)
AI proposes. Evidence confirms — that is agentic security testing.
More → github.com/BugTraceAI
Possible Phishing 🎣
on: ⚠️hxxps[:]//newsyoucanread24[.]com/article/veins_pl/cierpiala-z-powodu-zylakow-przez-12-lat/?_url=%252Fr%252FahETqfwJ9n-qcn4fH1djD&utm_campaign=46064&utm_content=38139&utm_medium=17&utm_source=129&utm_sub_id=102f734767057b602e342486c60730&utm_term=179&sub_id=A511dd3de96e2fe117eb658b82ba0a012&adi=A511dd3de96e2fe117eb658b82ba0a012&adref=ahETqfwJ9n-qcn4fH1djD&adp=15051&adr=eHRyb2dsb2JhbC5jb20%3D&adnid=129
🧬 Analysis at: https://urldna.io/scan/6ad67e923b77500004c2c35b
#cybersecurity #phishing #infosec #urldna #scam #infosec
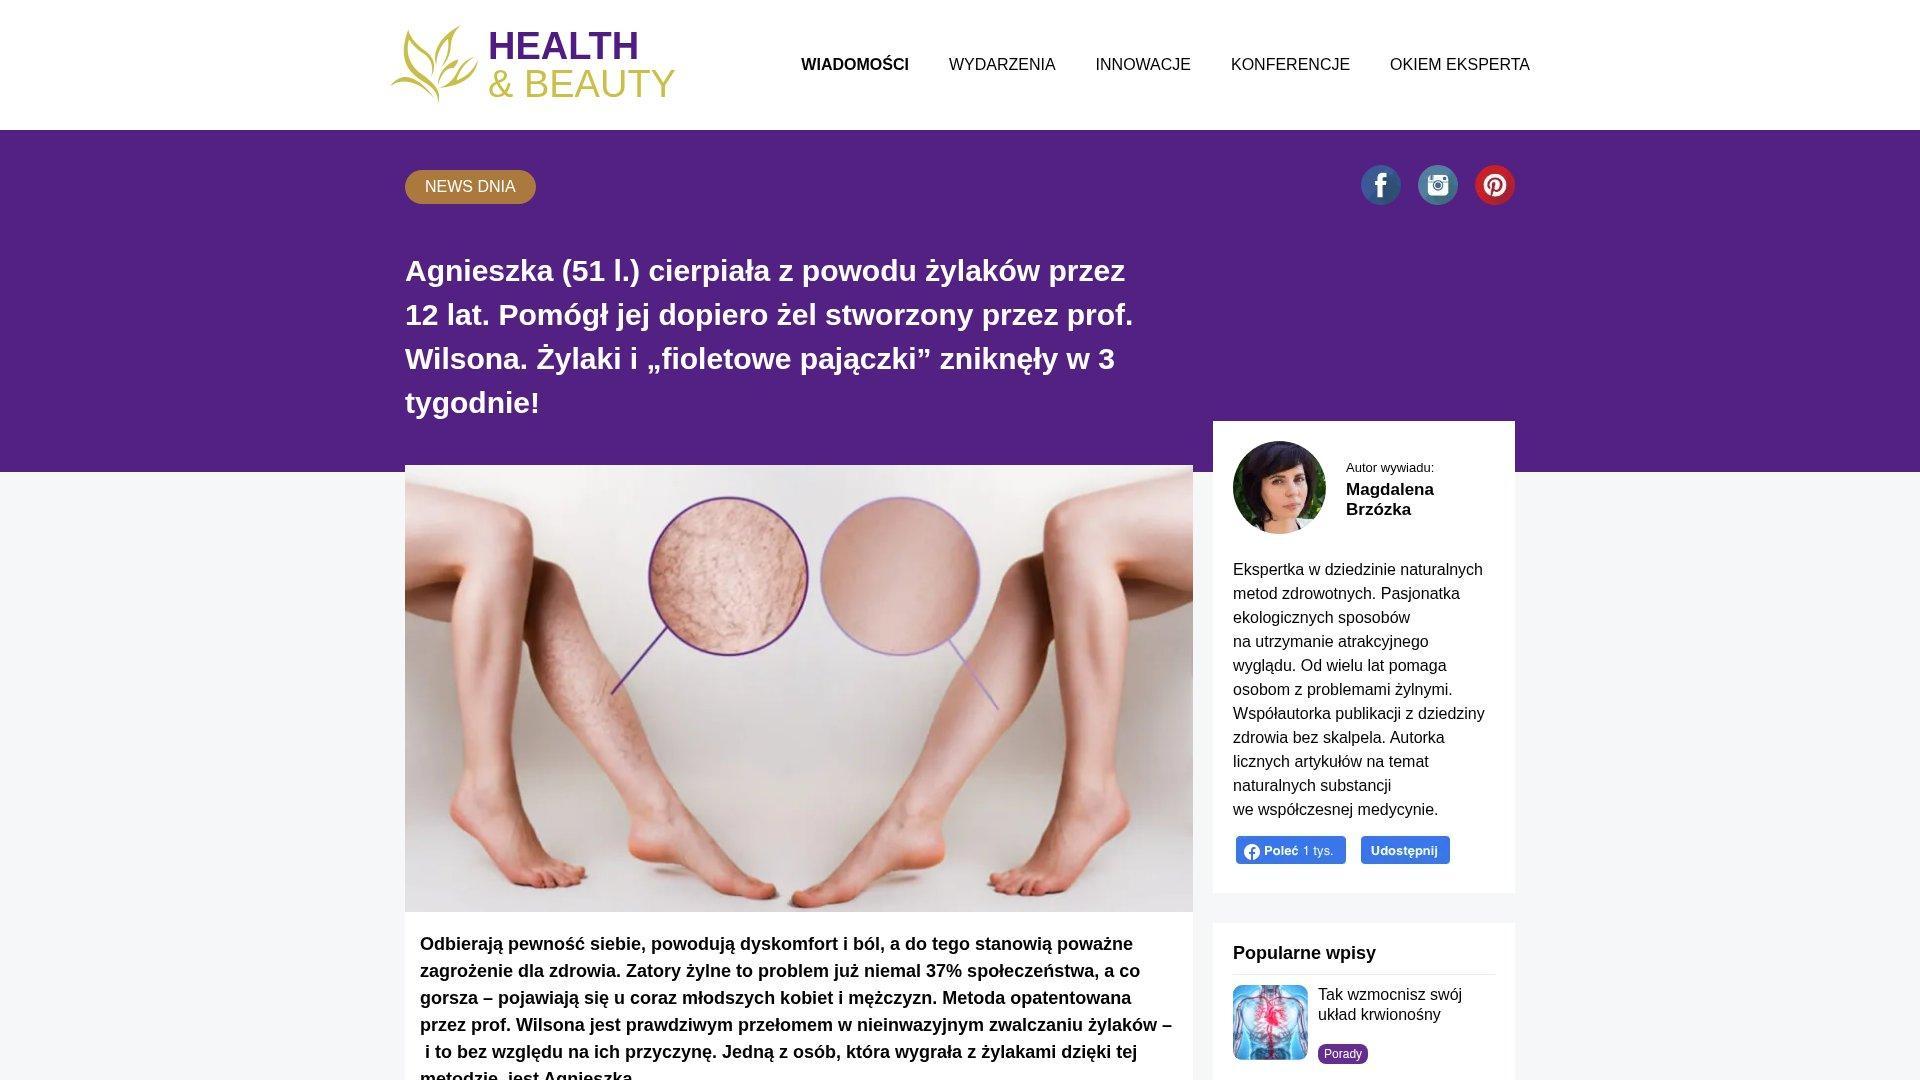 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
🤖 Plex2Shell: four chained flaws in Plex Media Server (CVE-2026-96652/96654/96655/96656, one CVSS 8.6) give unauthenticated RCE — SSRF in /player/timeline → admin token → ELF dropped in Codecs dir. Patched in 1.43.3.10861 (Aug 3). Exploitation began a day after the Oct 16 PoC: XMRig miner + "myawesomeproxy" Linux backdoor.
🔗 https://thehackernews.com/2026/10/hackers-exploit-plex2shell-flaws-to.html
#CVE #Exploit #Malware #InfoSec
 The Hacker NewsHackers Exploit Plex2Shell Flaws to Install Crypto Miners and Linux Proxy BackdoorAttackers exploit four Plex Media Server flaws chained as Plex2Shell to deploy XMRig miners and reverse proxy software after PoC release.
Possible Phishing 🎣
on: ⚠️hxxps[:]//alldomainilogsviwes[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad61c353b77500002f4d77b
#cybersecurity #phishing #infosec #urldna #scam #infosec
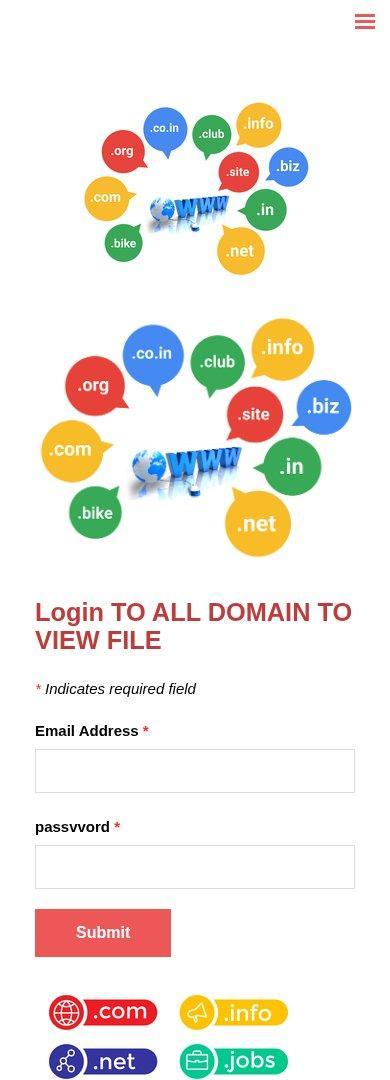 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
CVE-2026-77933 (CRITICAL, CVSS 9.3): DB-GPT <=0.8.2 ships with hardcoded MySQL root credentials in docker-compose.yml & exposes port 3306. Remote attackers can gain full DB access. Change credentials & restrict port now. https://radar.offseq.com/threat/cve-2026-77933-use-of-default-credentials-in-eosphoros-ai-db-gpt-bfef4b198f4b1032 #OffSeq #vuln #infosec #docker
ASN: AS6364
Location: Dallas, US
Added: 2026-10-17T11:54
Most companies count AI agents as insiders, and CISOs worry about their own liability
🚨 AI Security Alert: 95% of companies faced AI-related insider incidents last year. With 28% traced to AI systems and detection taking 15 hours avg, CISOs are scrambling. Problem? 52% lack formal strategies & 63% can't track AI tool usage. Legal liability concerns are mounting. Organizations need urgent AI governance frameworks.
https://www.helpnetsecurity.com/2026/10/14/ciso-ai-agent-insider-risk/
 Help Net SecurityMost companies count AI agents as insiders, and CISOs worry about their own liability - Help Net SecurityAI agent insider risk showed up at 95% of companies in a Trellix survey of 600 CISOs. Detection and response average 15 hours.
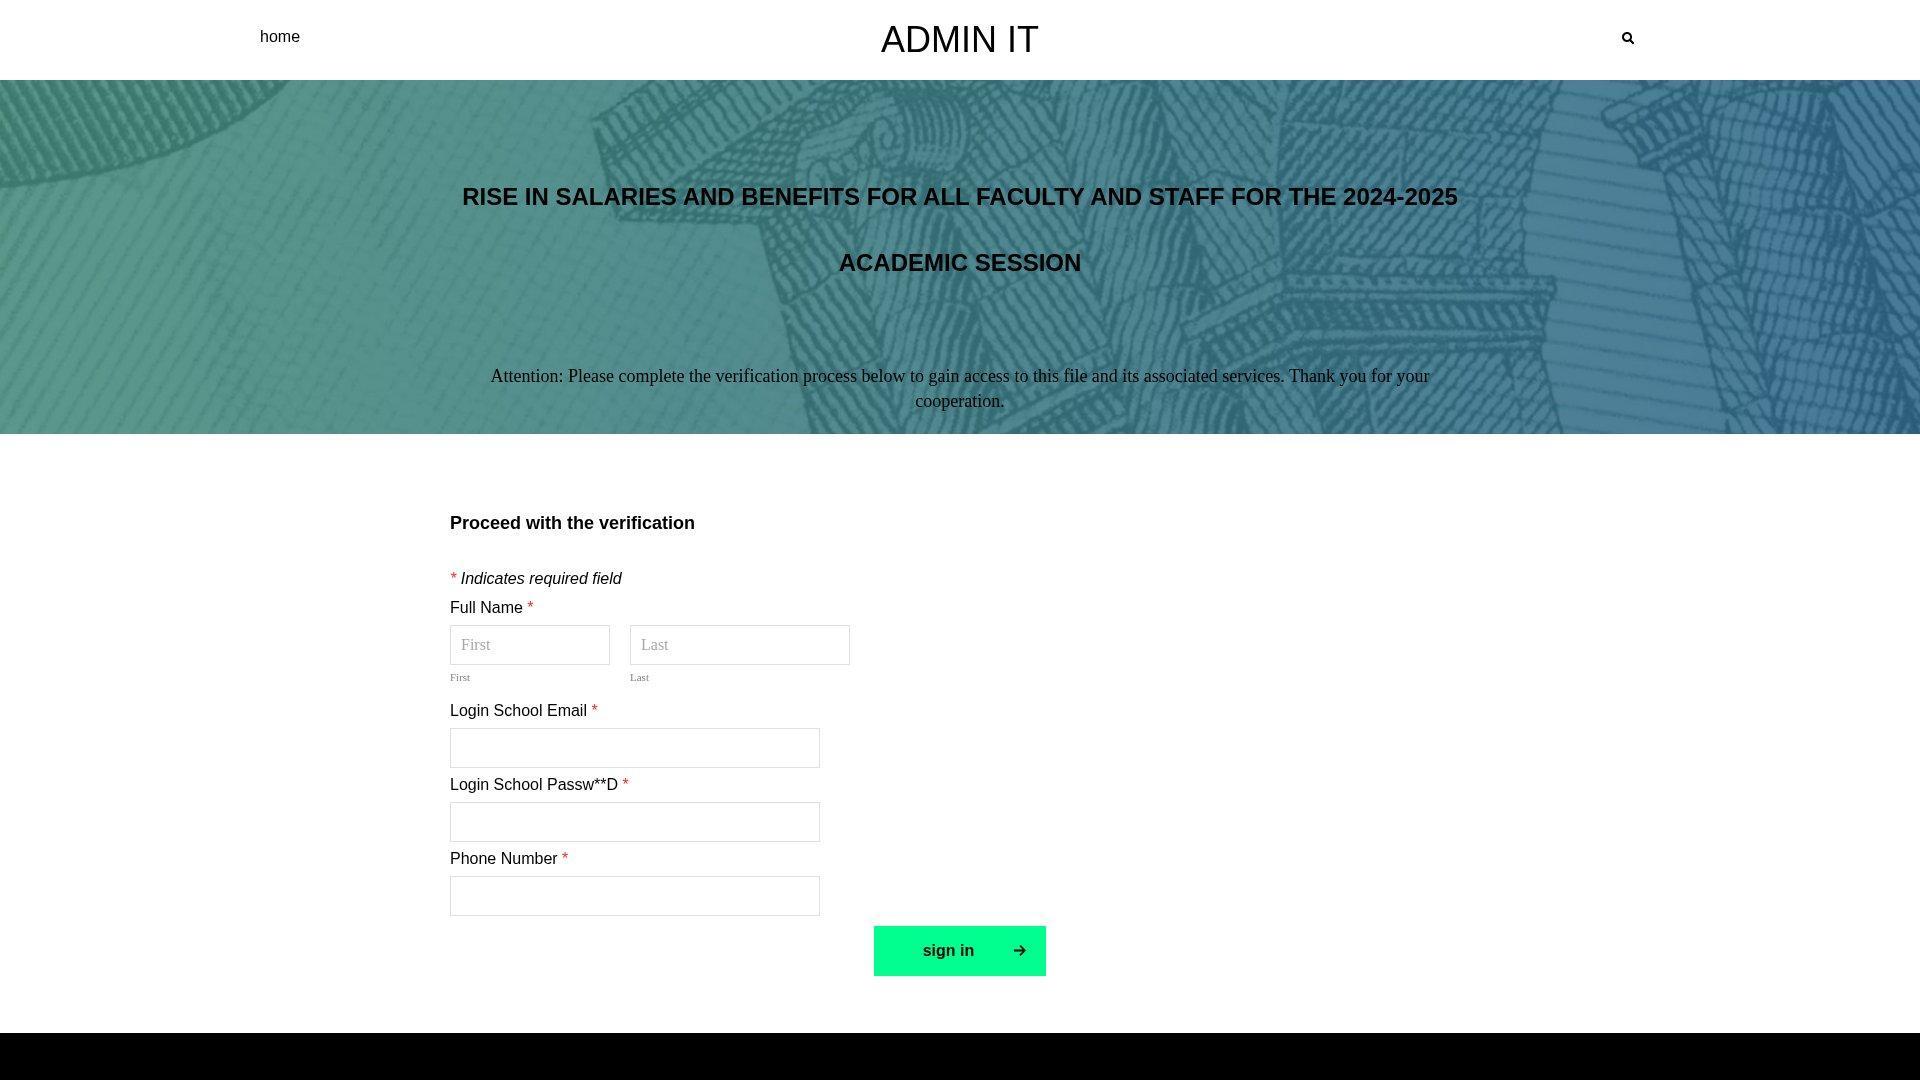
Possible Phishing 🎣
on: ⚠️hxxps[:]//officeserviceit[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad606593b77500007bd2f1f
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
🚨New ransom group blog post!🚨
Group name: anubis
Post title: Fisher59
Sector: Other
Info: https://cti.fyi/#disclosure/anubis/Fisher59
#ransomware #cti #threatintelligence #cybersecurity #infosec
 CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
ASN: AS41765
Location: Buis-les-Baronnies, FR
Added: 2026-10-17T11:56
Former OpenAI engineer Abdulrahman Alfozan will remain detained pending trial on allegations of covert recordings, per a US filing reported by Ars Technica. The case matters for insider-threat modeling in frontier AI labs handling sensitive research. #InsiderThreat #OpenAI #InfoSec
https://cyberworldops.eu/en/court-keeps-former-openai-engineer-detained-over-alleged-covert
 CyberWorldOpsFormer OpenAI Engineer Detained Over Alleged RecordingsUS court ordered ex-OpenAI engineer Abdulrahman Alfozan detained pending trial over alleged hidden recorders in offices, prosecutors say.
The cyber talent shortage? Job postings just hit a four-year low
🚨 Cybersecurity job market cooling: US postings hit 4-year low in 2026 with 235,786 openings—26.4% down YoY. Major shift happening: GRC roles surging (14.8% of postings, up from 9.4%), while technical defense roles declining (47.1% to 41.5%). CISO hiring volatile due to exec turnover. AI security roles rising. Risk management now prioritized over pure defense.
https://www.helpnetsecurity.com/2026/10/16/cybersecurity-job-postings-talent-shortage/
 Help Net SecurityThe cyber talent shortage? Job postings just hit a four-year low - Help Net SecurityCybersecurity job postings hit a four-year low in 2026 as compliance roles gain share and CISO hiring swings, new CyberSN data shows.
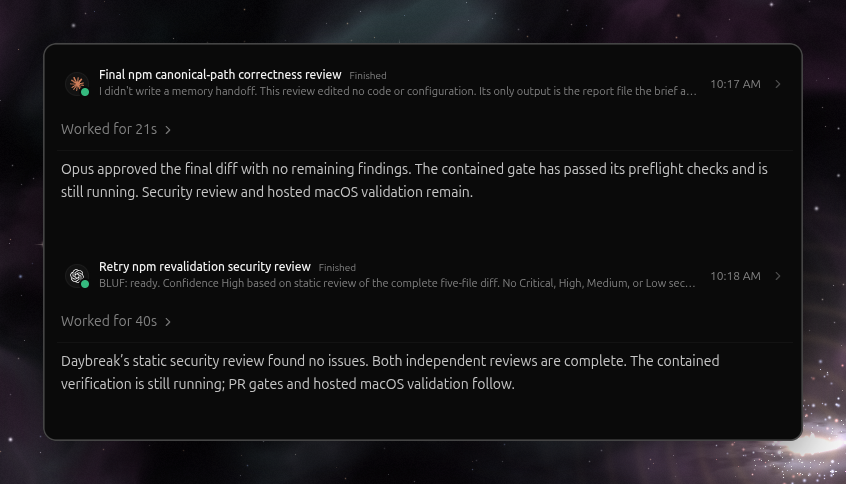
If you're not running routine security reviews of your PRs, you need to rethink your workflow. Use more than one model to review work and propose fixes.
Opus 5.5, Daybreak Blue, and GLM 5.3 are all excellent to use in tandem. Time to update your AGENTS.md.
Give each model a clear scope, ask for concrete failure cases and fixes, then verify the fixes before merging. Opus 5.5 is great for correctness and if you don't have access to Daybreak Blue, request it, and use GLM 5.3 in the meantime.
🤖 nginx 1.31.7 / 1.30.6 fix memory-safety flaws: buffer overflow via alias+rewrite (CVE-2026-15176), use-after-free in async file I/O (CVE-2026-97205), overflow in script evaluation (CVE-2026-93479), request body injection in HTTP/3 (CVE-2026-95101). nginx rates them medium; F5's OOB bulletin flags them critical.
🔗 https://nginx.org/en/security_advisories.html
#CVE #InfoSec #nginx
🟠 New security advisory:
CVE-2026-80343 affects multiple systems.
• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours
Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-80343-camel-netty-http-auth-bypass-exposes-routes-poc
by Yazoul AI
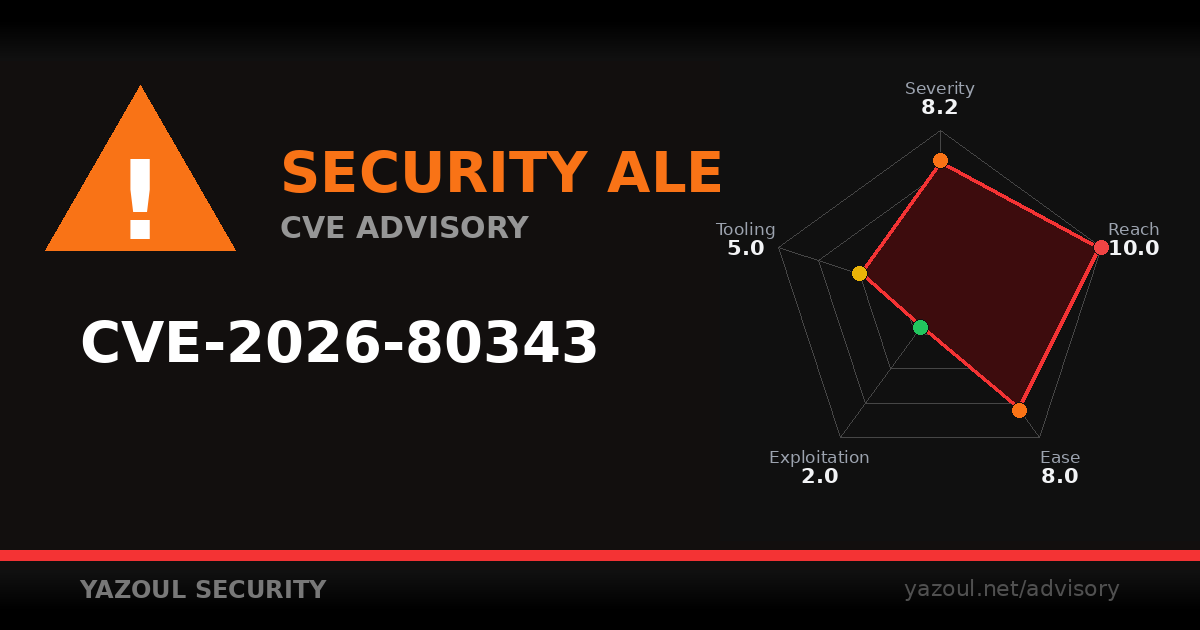 Yazoul SecurityCamel Netty HTTP auth bypass exposes routes (CVE-2026-80343) [PoC]CVE-2026-80343: Apache Camel 4.0.0-4.22.0 Netty HTTP security constraint bypass lets unauthenticated callers reach protected routes. Upgrade to 4.23.0 or 4.18.5/4.22.1 LTS.
Possible Phishing 🎣
on: ⚠️hxxps[:]//facebook-22[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad5f2233b77500004c2bcc4
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Kiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability
Kiteworks shut down systems after federal cyberattack warnings, discovering a critical vulnerability without evidence of breach. While this proactive move protected data, experts warn other vendors may hesitate due to SLA penalties & customer backlash. Key takeaway: Companies need pre-planned crisis protocols, leadership buy-in, and balanced risk assessments to respond quickly to threats without full shutdowns.
 CybersecurityKiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability | TechTargetKiteworks CISO Frank Balonis explains why the vendor issued a nine-hour proactive shutdown after federal warnings, and why other SaaS vendors hesitate to follow.
2026-10-19 RDP #Honeypot IOCs - 8964 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
154.36.174.33 - 7245
45.154.96.17 - 1566
136.244.100.79 - 18
Top ASNs:
AS979 - 7245
AS212815 - 1566
AS396982 - 36
Top Accounts:
hello - 7278
administrator - 108
Administrator - 90
Top ISPs:
NetLab Global - 7245
Dyjix SAS - 1566
Google LLC - 36
Top Clients:
Unknown - 8964
Top Software:
Unknown - 8964
Top Keyboards:
Unknown - 8964
Top IP Classification:
Unknown - 7263
hosting - 1695
mobile - 3
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
2026-10-19 RDP #Honeypot IOCs - 5976 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
154.36.174.33 - 4830
45.154.96.17 - 1044
136.244.100.79 - 12
Top ASNs:
AS979 - 4830
AS212815 - 1044
AS396982 - 24
Top Accounts:
hello - 4852
administrator - 72
Administrator - 60
Top ISPs:
NetLab Global - 4830
Dyjix SAS - 1044
Google LLC - 24
Top Clients:
Unknown - 5976
Top Software:
Unknown - 5976
Top Keyboards:
Unknown - 5976
Top IP Classification:
Unknown - 4842
hosting - 1130
mobile - 2
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
2026-10-19 RDP #Honeypot IOCs - 2988 scans
Thread with top 3 features in each category and links to the full dataset
#DFIR #InfoSec
Top IPs:
154.36.174.33 - 2415
45.154.96.17 - 522
136.244.100.79 - 6
Top ASNs:
AS979 - 2415
AS212815 - 522
AS396982 - 12
Top Accounts:
hello - 2426
administrator - 36
Administrator - 30
Top ISPs:
NetLab Global - 2415
Dyjix SAS - 522
Google LLC - 12
Top Clients:
Unknown - 2988
Top Software:
Unknown - 2988
Top Keyboards:
Unknown - 2988
Top IP Classification:
Unknown - 2421
hosting - 565
mobile - 1
Pastebin links with full 24-hr RDP Honeypot IOC Lists:
Bad API request, invalid api_dev_key
CVE-2026-112371: CRITICAL code injection in H3C Magic NX15 (CVSS 9.4). Public exploit allows remote code execution via /api/esps. No patch yet — restrict device access. Details: https://radar.offseq.com/threat/cve-2026-112371-code-injection-in-h3c-magic-nx15-047130e6380b2198 #OffSeq #H3C #infosec #vulnerability
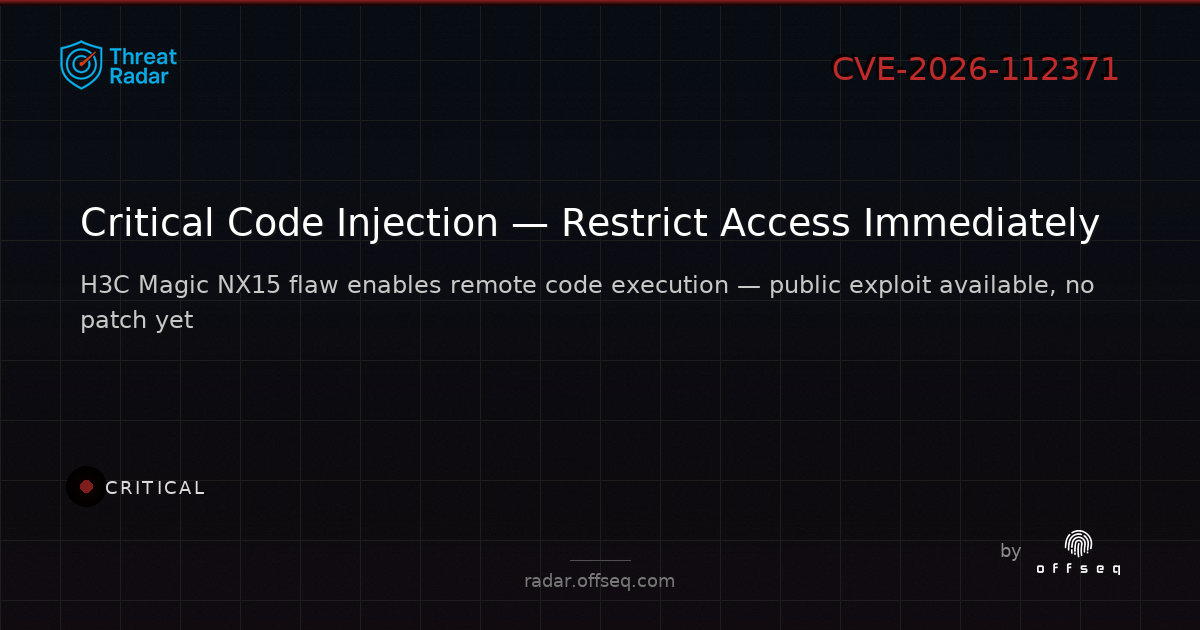
Possible Phishing 🎣
on: ⚠️hxxps[:]//nugtgsr222[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad60e223b77500007bd2ff8
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
ASN: AS14265
Location: Los Angeles, US
Added: 2026-10-17T12:02
🐧 SIGINT // Ubuntu Watch — 2026-10-20
Kernel escape vuln with real patching urgency. This roundup gives actual check commands and per-distro fix status for Ubuntu, Debian, RHEL, Proxmox - more actionable than the bare CVE entry for patching your fleet tonight.
🔗 https://smartscope.blog/en/blog/cve-2026-99999-pwnescape-linux-kernel-vulnerability-affected-2026/
 SmartScopeCVE-2026-99999 (PwnEscape): Am I affected? Fix status for RHEL, Ubuntu, Debian, Amazon Linux and ProxmoxAm I affected by CVE-2026-99999 (PwnEscape)? Check commands and OS fix status for RHEL, Ubuntu, Debian, Amazon Linux, Proxmox VE and SUSE, including confirmed Debian, Amazon Linux and Proxmox kernels, unconfirmed fixes, and host update and reboot steps.
Possible Phishing 🎣
on: ⚠️hxxp[:]//cuddly-disco-alpha[.]vercel[.]app/
🧬 Analysis at: https://urldna.io/scan/6ad63ea43b77500002f4d890
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Standard Chartered Group CISO on AI, Cyber Risk and the Future of Banking Security
CISOs are evolving from tech-only defenders to strategic business leaders. Standard Chartered's Group CISO emphasizes holistic cybersecurity accountability across tech, processes, and financial crime. Key shifts: integrating security into business ops, staying ahead of AI threats, and going beyond compliance. Success requires balancing technical expertise with business acumen while securing the entire ecosystem of clients and partners.
https://www.infosecurity-magazine.com/interviews/standard-chartered-group-ciso/
 Infosecurity MagazineStandard Chartered Group CISO on AI, Cyber Risk and Banking SecurityCezary Piekarski says banking CISOs must look beyond regulatory compliance to stay ahead of evolving cyber threats and technology risks
🚨 RELAY // Cyber Watch — 2026-10-20
A breach of the OpenCode Console may have exposed users' OpenAI, Anthropic and Google API keys, so affected users should rotate their keys.
🔗 https://thehackernews.com/2026/10/opencode-console-breach-may-have.html
 The Hacker NewsOpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API KeysOpenCode says a Console breach may have exposed AI provider keys belonging to 1.4% of users, prompting revocation notices.