X XFediYour place in the Fediverse
XFEDI

#cybersecurity

ActivityPub

Public posts with this hashtag.

MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.

@misp

🔗 https://github.com/MISP/misp-modules/releases/tag/v3.1.0

#misp #cti #threatintel #intelligence #cybersecurity #osint

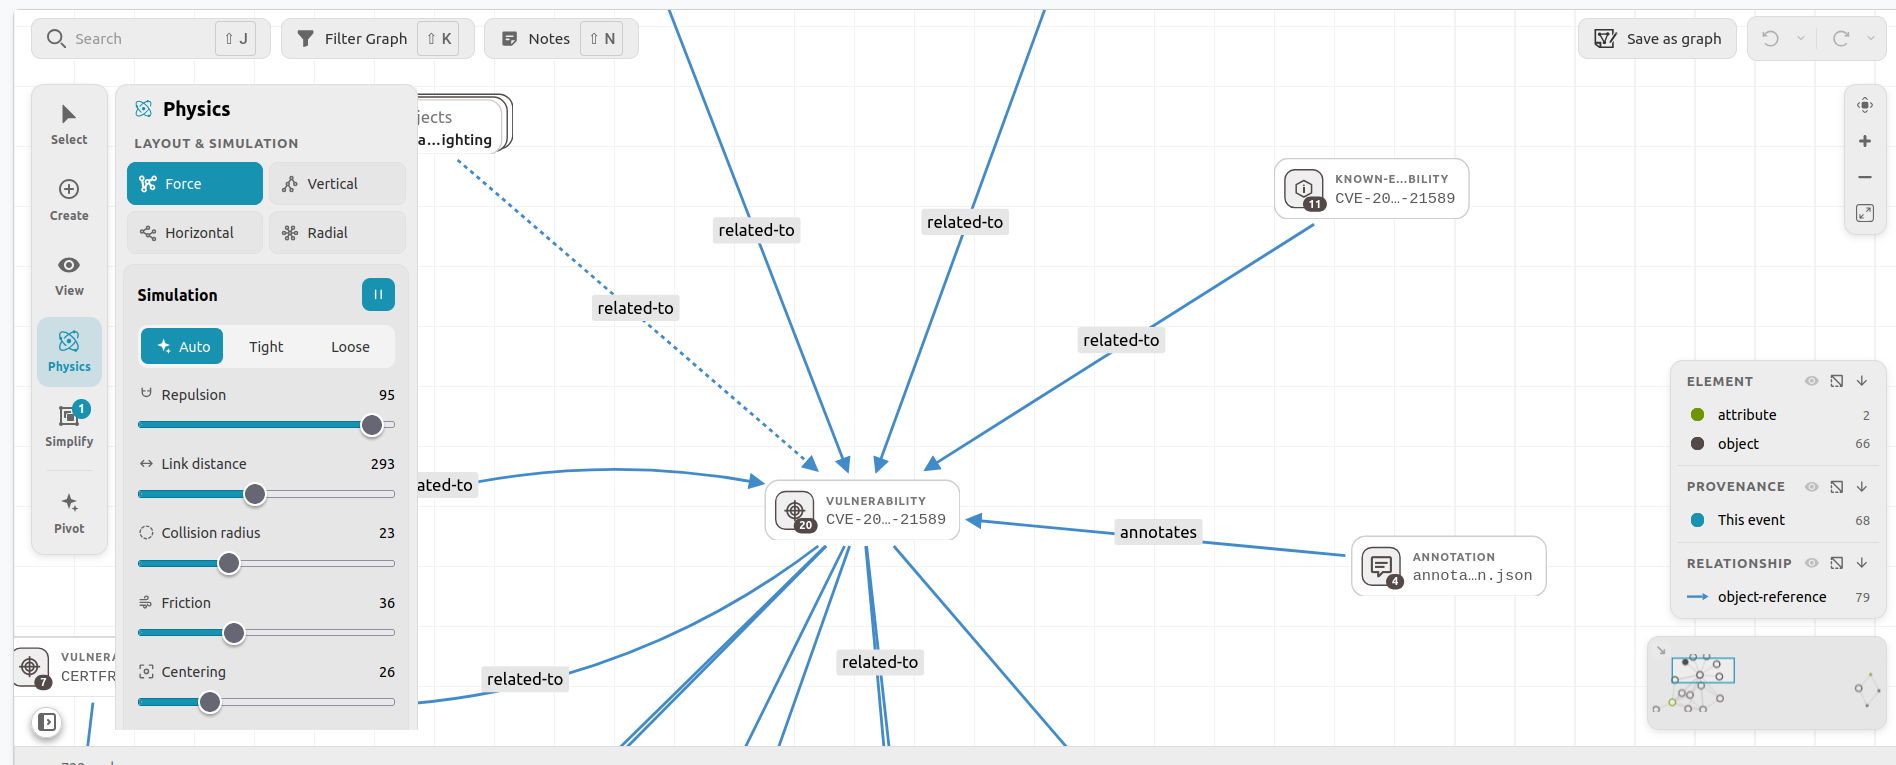
vulnerability-lookup expansion modules in MISP 3.0
GitHubRelease MISP Modules v3.1.0 - More pivots, more integrations, more actionable intelligence · MISP/misp-modulesMISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new w...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CISA to AI labs: Share test-network IPs to flag rogue agents

CISA urges AI labs to share IP addresses to track rogue agents threatening critical infrastructure. While transparency could boost cybersecurity, experts debate its practicality due to cloud complexity and AI's dynamic nature. Alternative solutions like detection signatures are suggested. Public sector orgs should proactively test AI systems and prioritize vulnerability patches.

https://www.techtarget.com/cybersecurity/news/366651845/CISA-to-AI-labs-Share-test-network-IPs-to-flag-rogue-agents

#InfoSec #CyberSecurity

CybersecurityCISA to AI labs: Share test-network IPs to flag rogue agents | TechTargetCISA urges AI labs to share IPs and ASNs so defenders can recognize and flag rogue agents early. Research analysts, however, had mixed reactions. Learn why.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and ...

Bank of America deployed 4,000 personnel (3,000 employees + 1,000 contractors) to fix software vulnerabilities detected by AI like Anthropic's Mythos. CEO Moynihan confirmed hundreds of millions in Q3 cybersecurity spending. Once skeptical of AI security tools, major firms now embrace them after serious breaches. BofA leads in transparency, expecting future cost reductions in patching efforts.

https://the-decoder.com/bank-of-america-puts-4000-people-on-fixing-vulnerabilities-uncovered-by-anthropics-mythos-and-other-ai-models/

#InfoSec #CyberSecurity

The DecoderBank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and other AI modelsBank of America has hired 1,000 outside contractors to fix software vulnerabilities uncovered by AI models like Anthropic's Mythos, CNBC reports.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Discover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.

#PwnEscape #LinuxKernel #Vulnerability #CloudSecurity #CyberSecurity

https://dailytechnow.com/critical-pwnescape-flaw-linux-virtual-machines/

Daily Tech NowCritical PwnEscape Flaw Found in Linux Virtual MachinesDiscover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This #Cybersecurity Agency Is Supposed to Protect U.S. #Elections. Officials Fear It’s Been Compromised by #Trump.

A few months into President Donald Trump’s second term, #political appointees at the Department of #HomelandSecurity made an unusual request of its agency focused on cybersecurity: Secretly acquire a #voting machine and #hack it.

The appointees wanted the Cybersecurity and #Infrastructure #Security Agency to procure the machine, examine it and report back the findings so they could be given to the #WhiteHouse , according to two former administration officials with knowledge of the request.
#dhs #voting #cisa

https://www.propublica.org/article/cisa-election-security-donald-trump

ProPublicaTrump Appointees Asked a Federal Cybersecurity Agency to Secretly Acquire a Voting Machine — and Hack ItThough not acted on, the request shows how the Trump administration has tried to use the Cybersecurity and Infrastructure Security Agency for its own ends while draining it of resources to help its mission of protecting the nation’s voting systems.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Discover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.

#Broadcom #WPSplinter #CyberSecurity #WiFiSecurity #RouterExploit

https://dailytechnow.com/broadcom-wifi-software-vulnerability/

Daily Tech NowBroadcom Wi-Fi Software Vulnerability Exposes RoutersDiscover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Enterprise controls can't keep up with AI agents

🚨 Companies are deploying AI agents faster than they can control them. Organizations struggle to track what these agents access, do, or if they can stop them. Traditional security systems aren't built for autonomous AI. The result? Potential security gaps and leaders considering quiet incident handling. The shift ahead: focus on managing existing agents responsibly, not just rolling out more.

https://www.techtarget.com/ai/news/366652493/Enterprise-controls-cant-keep-up-with-AI-agents

#InfoSec #CyberSecurity #AIGovernance

AI & Emerging TechEnterprise controls can't keep up with AI agents | TechTargetCompanies are giving agents more authority, but many are still struggling to track what they can access, what they're doing and how to stop them.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//newsyoucanread24[.]com/article/veins_pl/cierpiala-z-powodu-zylakow-przez-12-lat/?_url=%252Fr%252FahETqfwJ9n-qcn4fH1djD&utm_campaign=46064&utm_content=38139&utm_medium=17&utm_source=129&utm_sub_id=102f734767057b602e342486c60730&utm_term=179&sub_id=A511dd3de96e2fe117eb658b82ba0a012&adi=A511dd3de96e2fe117eb658b82ba0a012&adref=ahETqfwJ9n-qcn4fH1djD&adp=15051&adr=eHRyb2dsb2JhbC5jb20%3D&adnid=129
🧬 Analysis at: https://urldna.io/scan/6ad67e923b77500004c2c35b
#cybersecurity #phishing #infosec #urldna #scam #infosec
Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Most companies count AI agents as insiders, and CISOs worry about their own liability

🚨 AI Security Alert: 95% of companies faced AI-related insider incidents last year. With 28% traced to AI systems and detection taking 15 hours avg, CISOs are scrambling. Problem? 52% lack formal strategies & 63% can't track AI tool usage. Legal liability concerns are mounting. Organizations need urgent AI governance frameworks.

https://www.helpnetsecurity.com/2026/10/14/ciso-ai-agent-insider-risk/

#InfoSec #CyberSecurity #AIRisk

Help Net SecurityMost companies count AI agents as insiders, and CISOs worry about their own liability - Help Net SecurityAI agent insider risk showed up at 95% of companies in a Trellix survey of 600 CISOs. Detection and response average 15 hours.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#MiniMax M3.1 Flash improves #agentictasks, #coding, #computeruse and #cybersecurity, delivering speeds over 200 TPS and 70% lower costs. Available via MiniMax API, M Plan and MiniMax Code, it matches leading models on key benchmarks. https://www.minimax.io/blog/minimax-m31f?AIagents.at #AIagent #AI #ML #NLP #LLM #GenAI

MiniMaxMiniMax M3.1 Flash: Redefining Agent Performance and Cost - MiniMax ResearchToday, we officially roll out MiniMax M3.1 Flash. As a next-generation Flash model, M3.1 Flash delivers a generational leap in agentic tasks, coding, Computer Use and cybersecurity, while making online inference nearly three times faster and reducing usage costs by 70%.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The cyber talent shortage? Job postings just hit a four-year low

🚨 Cybersecurity job market cooling: US postings hit 4-year low in 2026 with 235,786 openings—26.4% down YoY. Major shift happening: GRC roles surging (14.8% of postings, up from 9.4%), while technical defense roles declining (47.1% to 41.5%). CISO hiring volatile due to exec turnover. AI security roles rising. Risk management now prioritized over pure defense.

https://www.helpnetsecurity.com/2026/10/16/cybersecurity-job-postings-talent-shortage/

#InfoSec #CyberSecurity #JobMarket

Help Net SecurityThe cyber talent shortage? Job postings just hit a four-year low - Help Net SecurityCybersecurity job postings hit a four-year low in 2026 as compliance roles gain share and CISO hiring swings, new CyberSN data shows.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This is kinda obvious, after what happened in Ukraine War and Iran War.

As the hatred towards data center by regular people will also be accelerated because sins by big techs and AI corps.

https://www.ft.com/content/15a049f3-b62e-40ed-b304-8a2452713338

#cybersecurity #security #datacenter

www.ft.comData centres need protection from drone warfareAI infrastructure designs may now need to incorporate blast-resistant concrete, jamming gear and missile-defence systems
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability

Kiteworks shut down systems after federal cyberattack warnings, discovering a critical vulnerability without evidence of breach. While this proactive move protected data, experts warn other vendors may hesitate due to SLA penalties & customer backlash. Key takeaway: Companies need pre-planned crisis protocols, leadership buy-in, and balanced risk assessments to respond quickly to threats without full shutdowns.

https://www.techtarget.com/cybersecurity/news/366651864/Kiteworks-CISO-Why-We-Shut-Down-Systems-Before-Finding-Vulnerability

#InfoSec #CyberSecurity

CybersecurityKiteworks CISO: Why We Shut Down Systems Before Finding Vulnerability | TechTargetKiteworks CISO Frank Balonis explains why the vendor issued a nine-hour proactive shutdown after federal warnings, and why other SaaS vendors hesitate to follow.
↩ Reply ♡ 0 · ↻ 0 ↗ Original