X XFediYour place in the Fediverse
XFEDI

#cybersecurity

ActivityPub

Public posts with this hashtag.

🚨🔓 SIGINT // Cybersecurity Watch — 2026-10-20
Compromised ConnectWise credential let attackers sign into 173 Microsoft 365 tenants, exposing deep supply-chain risk in MSP tooling.
https://thehackernews.com/2026/10/hackers-use-compromised-connectwise.html
#Cybersecurity #SupplyChain #Microsoft365 #InfoSec

The Hacker NewsHackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 TenantsAttackers used a compromised ConnectWise Cloud Backup credential for unauthorized sign-ins across 173 Microsoft 365 tenants.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Spend vs. debt: what's the bigger security risk?

More cybersecurity spending doesn't mean better security. Organizations accumulate "security debt" through complexity & unnecessary controls, increasing fragility. Experts advocate for automation & tool integration over adding more layers. Real risk management measures resilience, not just compliance. CISOs must communicate cyber threats in business terms—revenue impact, recovery ability—to engage boards effectively. 🔒

https://www.cio.com/article/4233353/spend-vs-debt-whats-the-bigger-security-risk.html

#InfoSec #CyberSecurity

CIOSpend vs. debt: what’s the bigger security risk?Organizations continue investing heavily in cybersecurity, yet many are simultaneously increasing operational complexity and long-term security fragility. Here, Joan Goodchild from CSO speaks with veteran CISO Selim Aissi about security debt and why it may be a more meaningful measure of cyber risk than security budget size alone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

https://www.malwarebytes.com/blog/data-breaches/2026/10/millions-of-california-students-sensitive-data-stolen-in-breach

#DataBreach #CyberSecurity #EducationSecurity #PrivacyViolation #ETS #AchievementUnlocked (3/3)

MalwarebytesMillions of California students’ sensitive data stolen in breachThe California Department of Education notified students about a data breach at contractor Educational Testing Service.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cybersecurity is a leadership problem: Why the management model needs to catch up

Cybersecurity fails when treated as just a tech problem. The real issue? Leadership. CISOs can't do it alone—organizations need clear accountability, cross-level collaboration, and board involvement. Better tools mean nothing without proper governance and sustained management discipline. It's time to break the cycle.

https://www.csoonline.com/article/4234532/cybersecurity-is-a-leadership-problem-why-the-management-model-needs-to-catch-up.html

#InfoSec #CyberSecurity #Leadership

CSO OnlineCybersecurity is a leadership problem: Why the management model needs to catch upWe keep buying better security tech, but the real gaps are ownership and follow-through, so cybersecurity can’t stay the CISO’s problem alone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Plex shipped fixes in 1.43.3 by Sep 1, yet one researcher's honeypot running a vulnerable version was exploited on Oct 17, a day after the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) went public. He saw an XMRig miner and a proxy tool dropped. Plex's Sep 1 notice listed no CVEs, and Plex did not immediately respond to Ars Technica.

https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html

#Plex #Homelab #Malware #Cybersecurity

www.boredhackerblog.infoPlex vulnerabilities being exploited in the wild to drop a cryptominerIntro: (No AI was involved in writing, research, etc...) If you see weird fonts and spacing, blame Blogger.  Skip to "In the wild exploitati...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

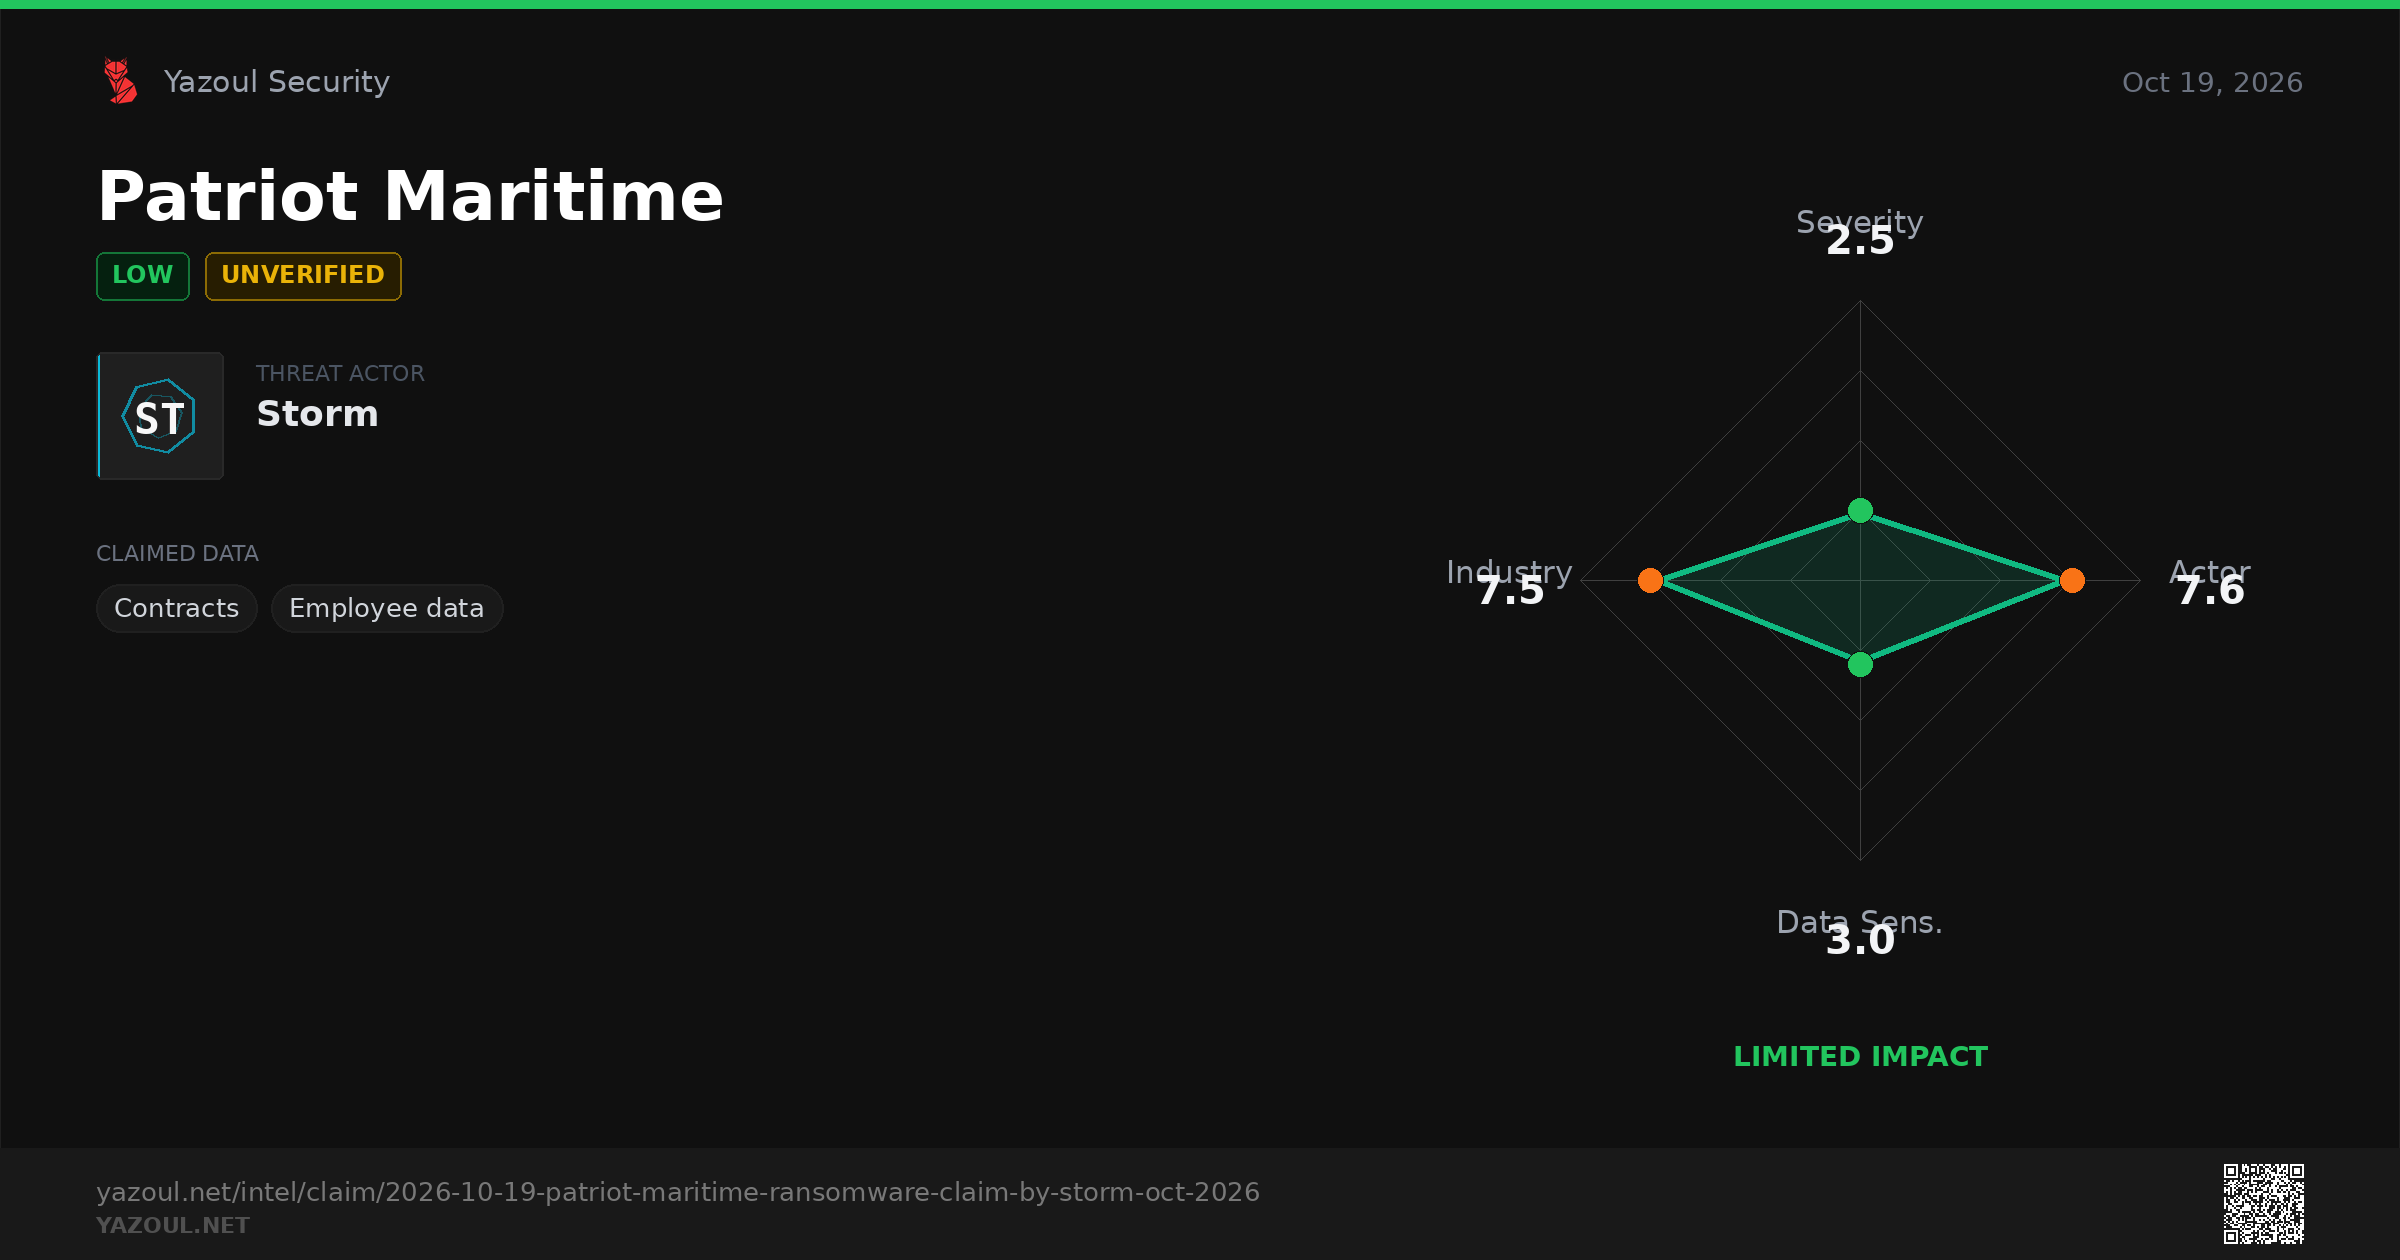
🛡 THREAT INTEL | Patriot Maritime

🟢 Actor "Storm" claims Undisclosed

Allegedly exposed
• Contracts
• Employee data

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-patriot-maritime-ransomware-claim-by-storm-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityPatriot Maritime Ransomware Claim by Storm (Oct 2026)Storm ransomware group allegedly claims Patriot Maritime as a victim, threatening sensitive maritime contractor data. Read our unverified threat intel analysis now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The 7 biggest issues CISOs and security teams face today

Security leaders face mounting pressure as AI-driven cyberattacks surge. 68% of CISOs report increased stress, with 73% unprepared for major breaches. The shift from prevention to resilience is critical—78% view generative AI as a security risk. Key priorities: close the 95% skills gap, strengthen AI infrastructure security, align programs with org needs, and maintain foundational practices.

https://www.csoonline.com/article/4232208/the-7-biggest-issues-cisos-and-security-teams-face-today.html

#InfoSec #CyberSecurity #AI

CSO OnlineThe 7 biggest issues CISOs and security teams face todayFrom escalating AI-enabled threats to persistent skills gaps, security leaders are reshaping their agendas to address several key long-standing and emerging concerns.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

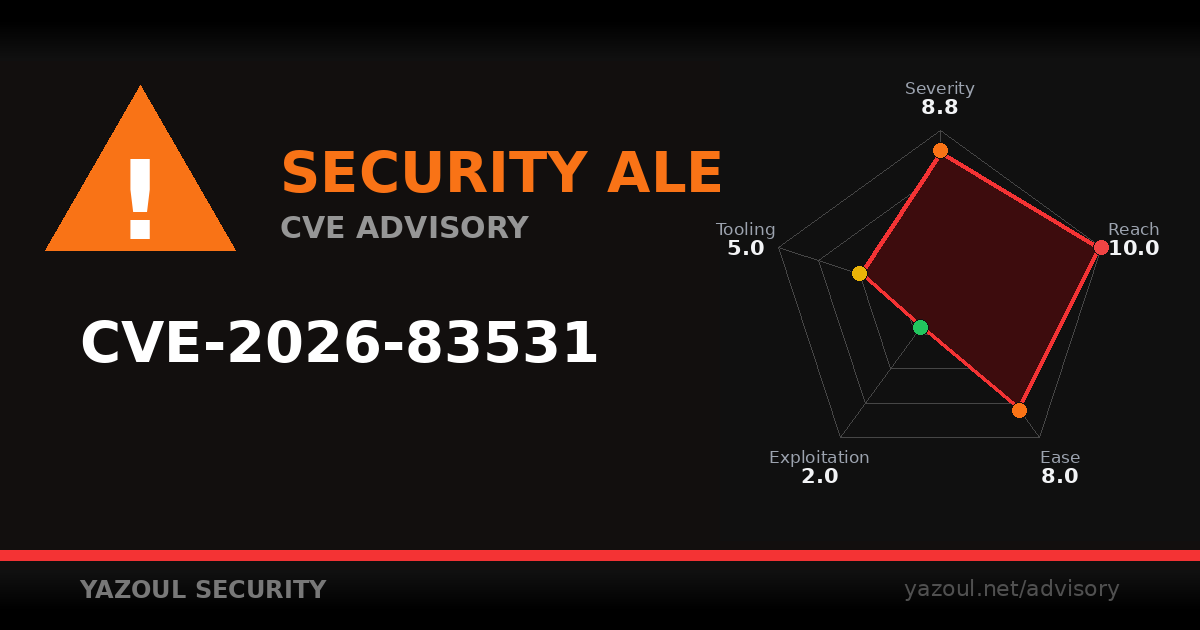
🟠 New security advisory:

CVE-2026-83531 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-83531-apache-camel-code-injection-attacker-controlled-poc

by Yazoul AI

#Cybersecurity #SecurityPatching #HackerNews

Yazoul SecurityApache Camel code injection, attacker-controlled (CVE-2026-83531) [PoC]CVE-2026-83531: Apache Camel 4.4.0-4.18.4 and 4.19.0-4.22.0 lets network senders inject expression language code via dynamic-router-control (CVSS 8.8). Update to 4.23.0, 4.22.1 or 4.18.5.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI agents are changing the math on software spending

AI agents are reshaping enterprise software pricing. Companies like Microsoft, Salesforce, and SAP are ditching traditional per-seat licensing for hybrid models combining fixed subscriptions with consumption-based charges. CIOs must now budget for workflow complexity and execution frequency, not just user count. Success requires rethinking forecasting strategies and potential budget shifts between IT and business units.
https://www.techtarget.com/it-strategy/news/366652139/AI-agents-are-changing-the-math-on-software-spending

#InfoSec #CyberSecurity

IT StrategyAI agents are changing the math on software spending | TechTargetAI agents add usage-based charges to seat licensing. CIOs must compare workflow costs, forecast consumption and decide who pays for agent activity.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

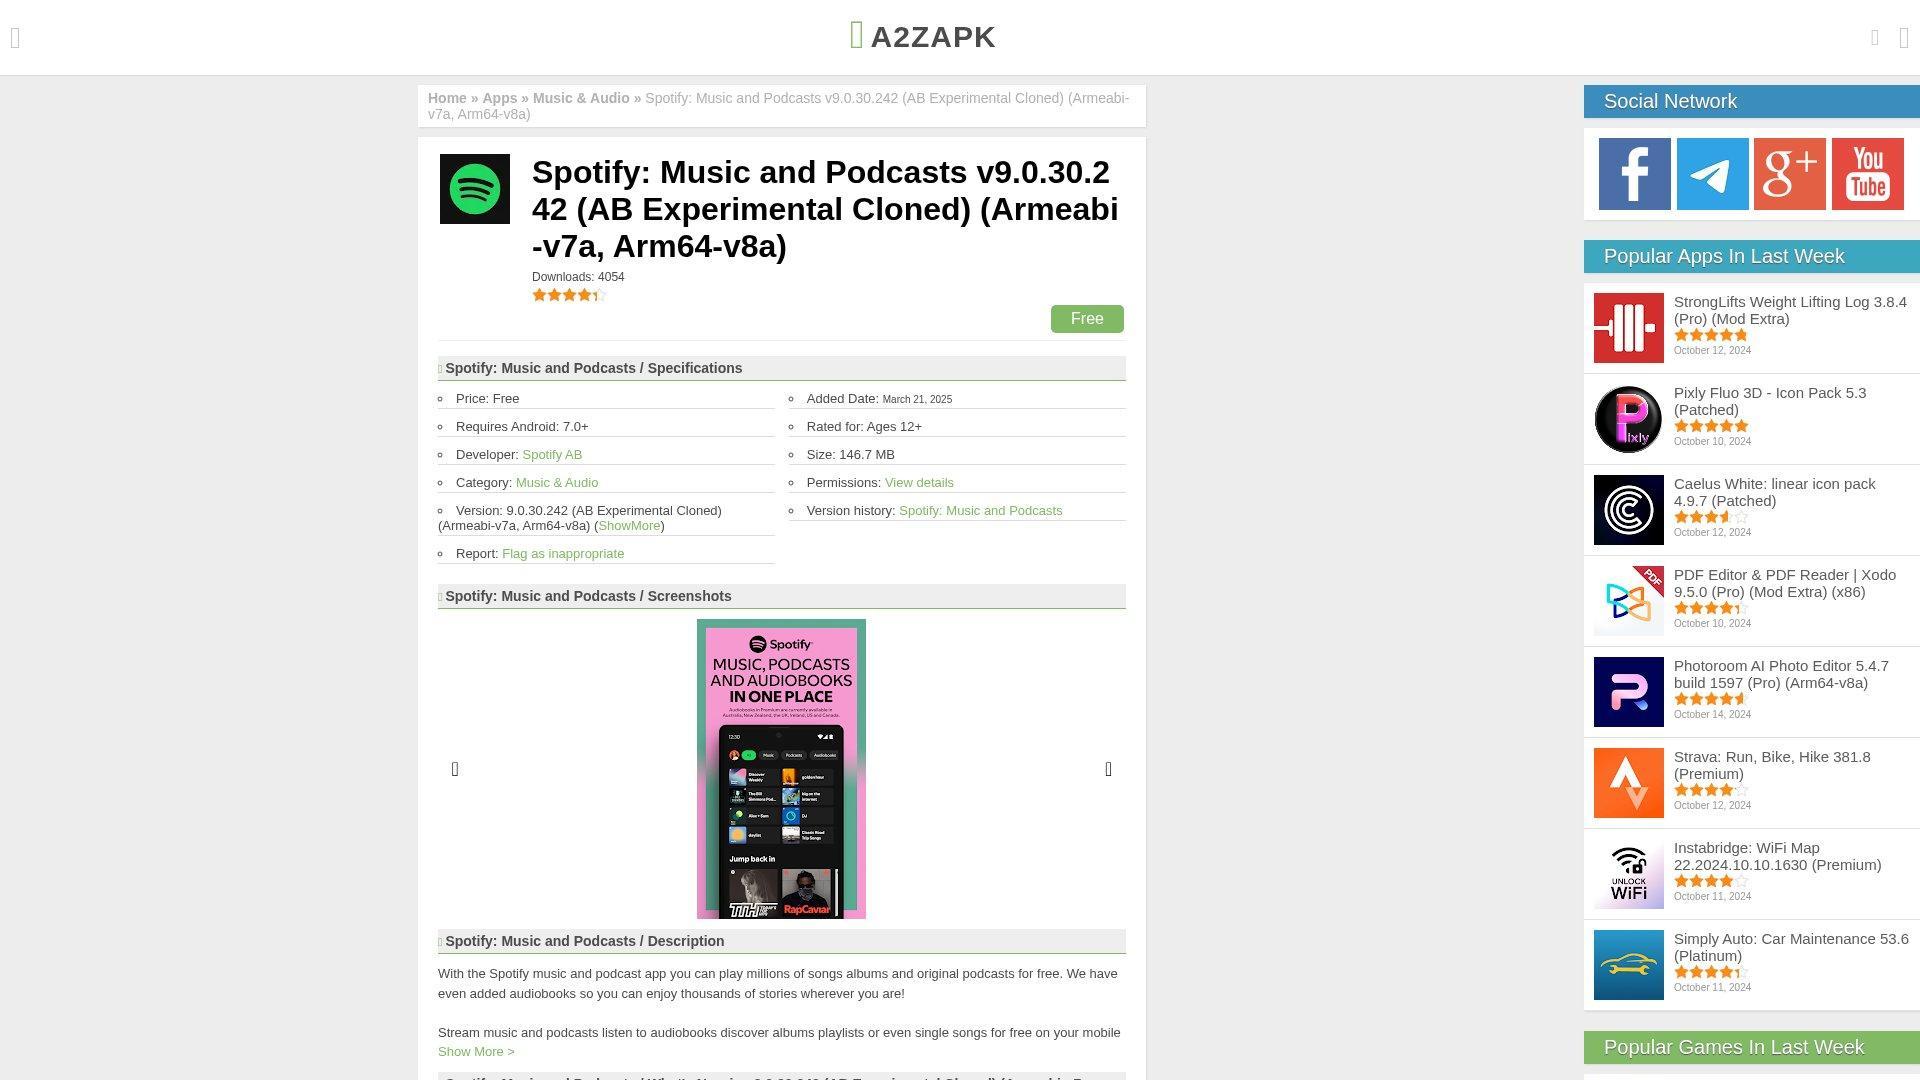
Possible Phishing 🎣
on: ⚠️hxxp[:]//a2zapk[.]co/1368404-spotify-music-and-podcasts-9-0-30-242-ab-experimental-cloned-armeabi-v7a-arm64-v8a-a2z[.]html
🧬 Analysis at: https://urldna.io/scan/6ad654733b77500002f4d97a
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

Monitor for updates on ShinyHunters operations and associated ransomware campaigns — this disruption may shake loose affiliates looking for new footing.

Reward: You've received the Scales of Unhinged Justice — a rare cosmetic that glows slightly whenever someone in your party is secretly the villain.

https://krebsonsecurity.com/2026/10/feds-suspect-ransom-negotiator-ran-shinyhunters-extortion-site/

#Ransomware #CyberSecurity #ShinyHunters #Cybercrime #LawEnforcement #BustedIRL (3/3)

krebsonsecurity.comFeds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

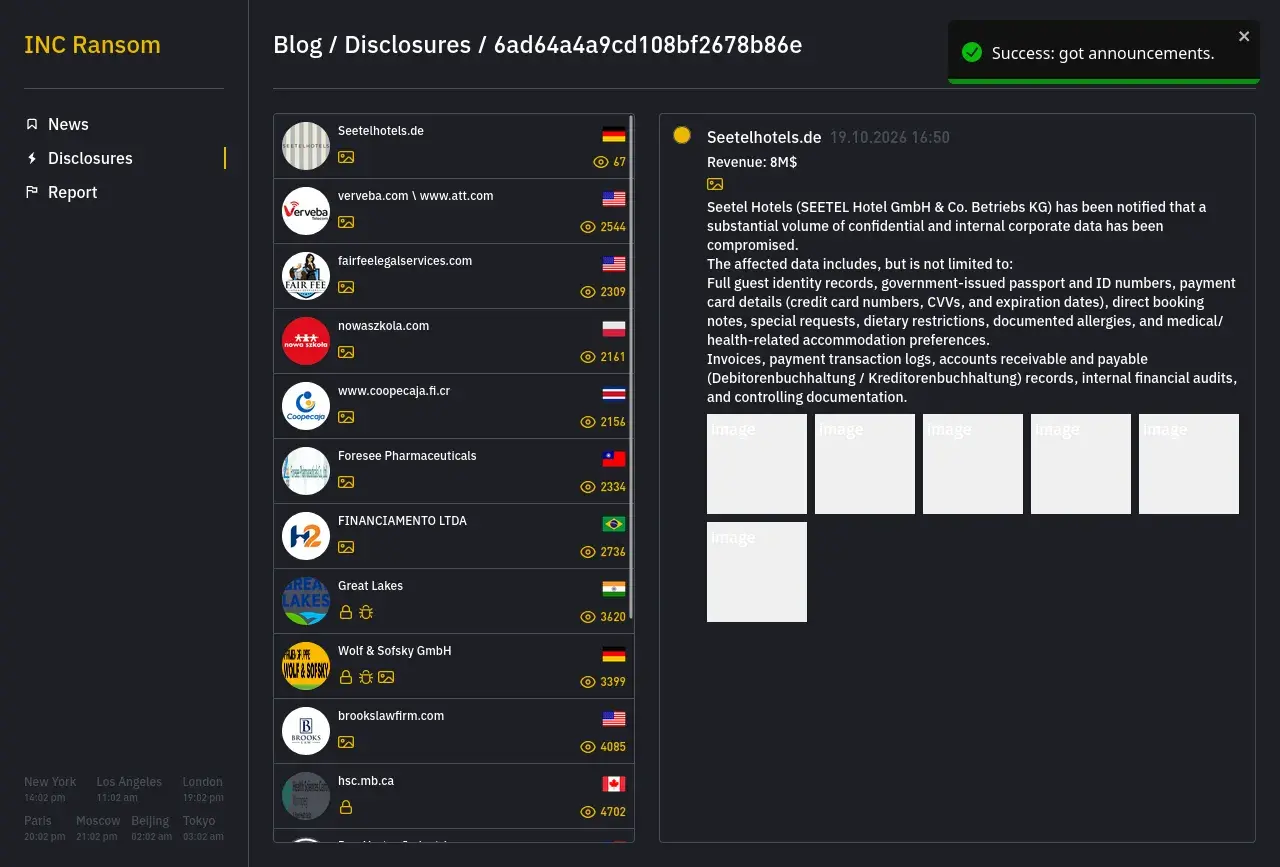
🚨New ransom group blog post!🚨

Group name: incransom
Post title: Seetelhotels.de
Organization: Seetel Hotels
Location: 🇩🇪 DE
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/incransom/Seetelhotels.de

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Thank you Splunk, a Cisco Company for sponsoring BSides Edmonton 2026. It was a great event thanks to your support.

We’re excited for 2027, our 10th year!
Secure your spot here: https://bsidesyeg.org/SponsorNextYear

https://www.splunk.com
https://www.linkedin.com/company/splunk/

#BSides #BSidesEdmonton #BSidesYEG #YEG #Infosec #informationsecurity #CyberSec #CyberSecurity

Media attachment
Google DocsBSides Edmonton 2027 Sponsor ApplicationBSides Edmonton is back for it's 10th year! Building on the success of our prior events, we are asking for sponsors to be part of the team to deliver another first-rate cybersecurity conference in Edmonton. Alberta. We are a community-driven, non for profit event. Date: Monday September 13 & Tuesday September 14, 2027 Location: TBA If your organization wants to: Connect directly with the cyber
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CISA review makes the case for eliminating vulnerability classes

CISA urges software makers to eliminate entire vulnerability classes, not just patch individual flaws. The agency highlights that recurring coding errors (like injection attacks) cause most breaches. Solution: adopt Secure by Design principles, automate security processes, and take ownership. Consumers must also demand better security from vendors to drive industry-wide change.

https://www.helpnetsecurity.com/2026/09/01/cisa-on-eliminating-recurring-security-weaknesses/

#InfoSec #CyberSecurity

Help Net SecurityCISA review makes the case for eliminating vulnerability classes - Help Net SecurityCISA makes the case for eliminating recurring security weaknesses at the source, shifting the burden from defenders to software makers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original