CVE-2026-112832 (CRITICAL, CVSS 9.8) in CozyThemes Rootblox <1.0.7 allows unauthenticated remote LFI via improper filename control in PHP. Full system compromise possible. Restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-112832-improper-control-of-filename-for-includerequire-statement-in-php-program-php-remote-3c455496d4cdf128 #OffSeq #infosec #PHP #LFI
#php
Public posts with this hashtag.
#errors in #software will exist
more #complex #software = more #errors
#php most likely will not be the cause of the #apocalypse but other #cyber security problems might :(
we have to rewrite everything in #rust anyone willing to give #rust workshops ? :D #HELP !
hence it is so important for every #government and #good #company (the #bad can go broke i don't care) to have a #offline #howto #plan in case the #internet is #f...ed
that is why 100% #digital #currency as planned and pushed by #ecb #euro is a receipt4 #disaster
1. have ALWAYS a complete set of data #offline in a #safe do not trust #cloud a #cloud can be #hacked and go down
2. with #android it is relatively easy to copy over #pictures to #usbstick or via #usb data cable to #laptop
with #iphone it's a complete #catastrophe not sure if #itunes still allows it, but per default all pictures on an #apple device go straight into #apple cloud and then you can download it via #browser
this is wrong on multiple levels
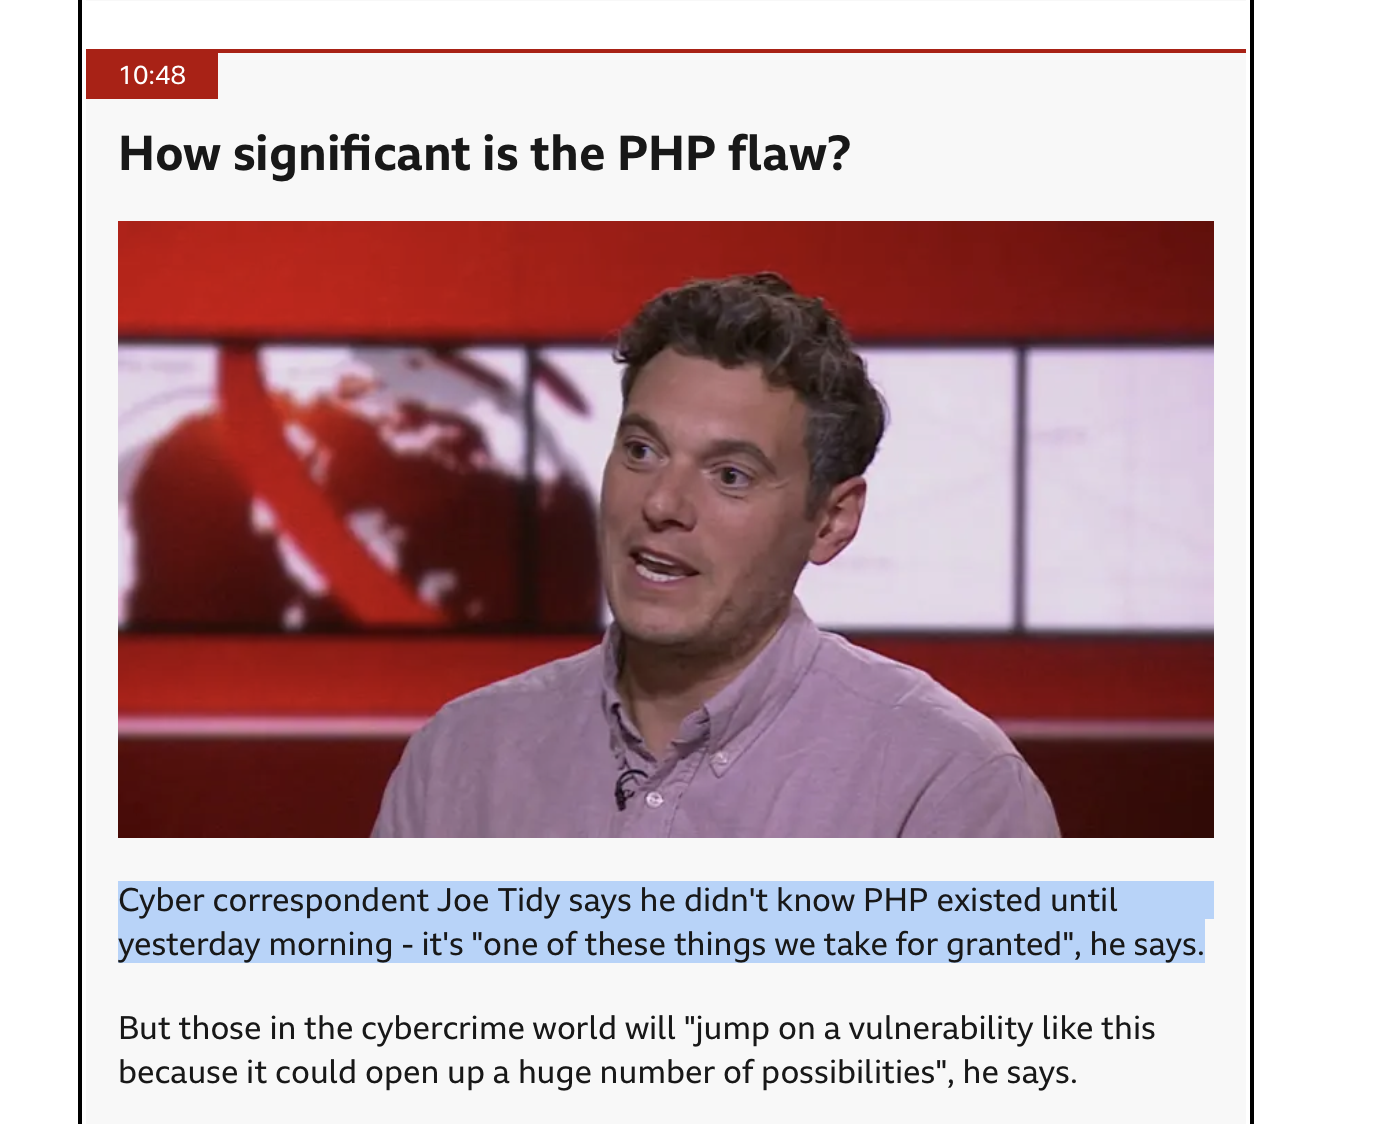
The BBC being absolutely on the button. Their Cyber correspondent had never even heard of php before? Really??? 🤦♀️
BBC NewsPHP: Minister says 32 UK government services unavailable due to global cyber-security issue - follow liveDowning Street says some "limited services may temporarily be offline" as security work takes place, adding: "This does not mean they were hacked."
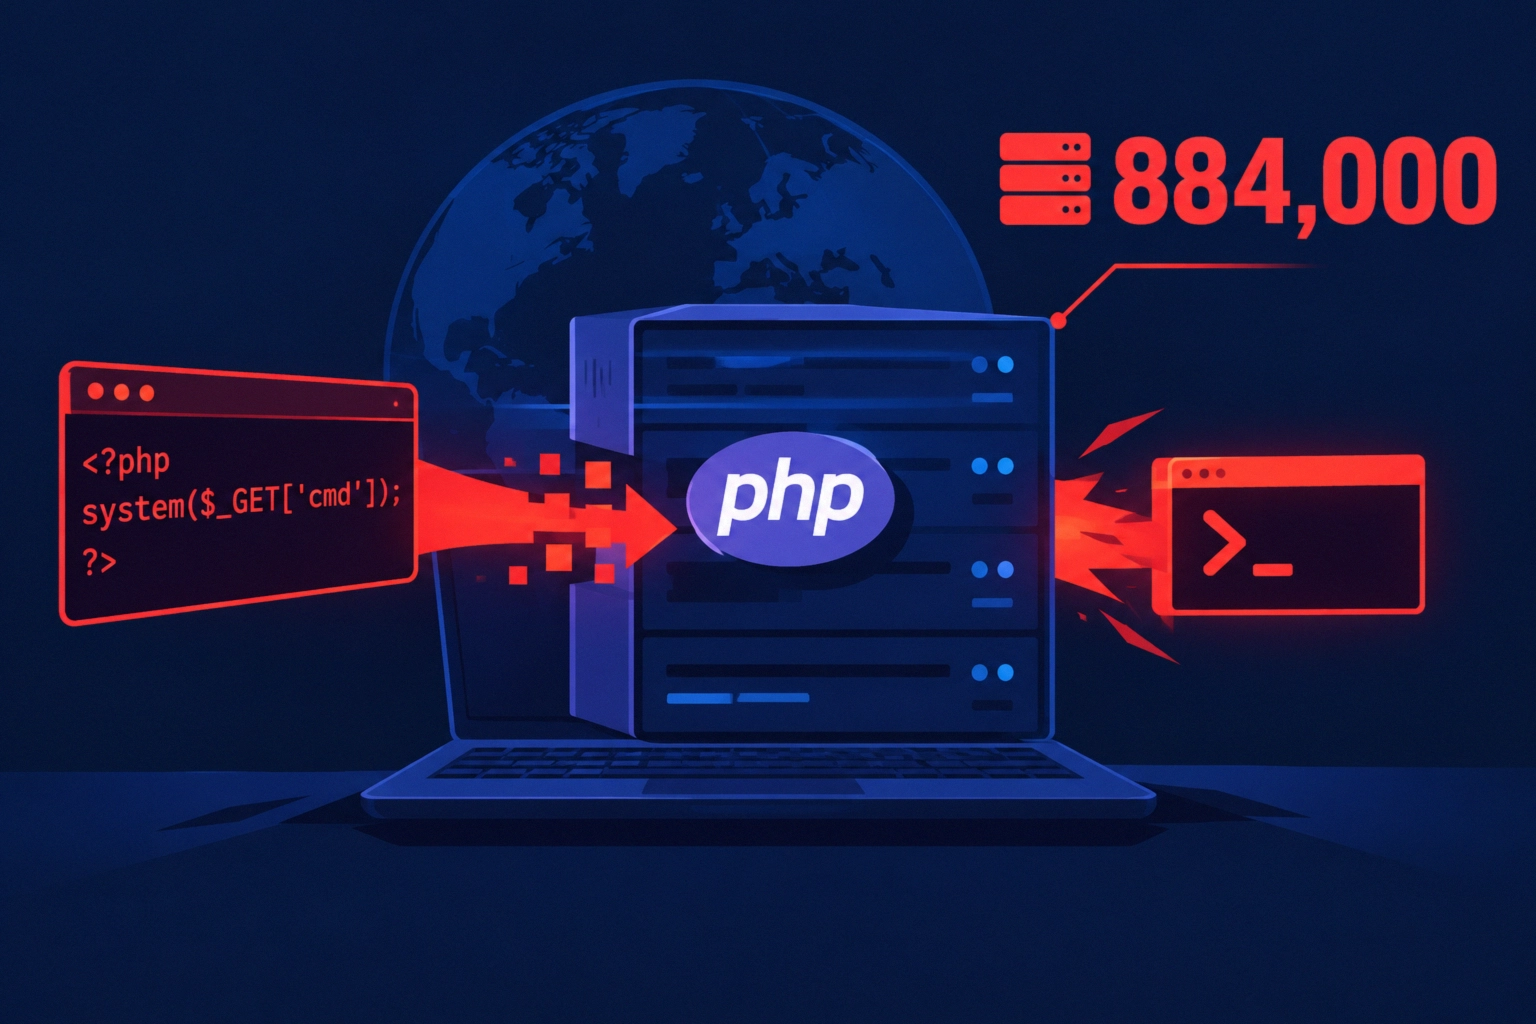
Critical PHP RCE vulnerabilities: emergency patch and 884,000 unprotected hosts
🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-emergency-patch
#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #critical #PHP #vulnerability
CyberSecureFoxCritical PHP RCE Vulnerabilities: Emergency Patch And 884,000 Unprotected HostsThe PHP security team has announced two critical vulnerabilities with a CVSS v4.0 score of 9.2 and scheduled an out-of-band security release for 21 October
Interesting understandable explanation of the PHP bug, the last paragraph says it all for me.
the GuardianWhat is PHP, and how bad is the computer language flaw causing website shutdowns globally?An estimated 70% of websites use the open-source language. What is the identified vulnerability in it?
I had been thinking about retiring my WordPress sites for a while anyway so now they just return a 410. #php #php2shell
PHP2Shell is now public and already under attack. Two flaws in PHP core, CVE-2026-109618 and 109619, both scored 9.2, give pre-authentication remote code execution on every PHP 7.x and 8.x release, through any reachable endpoint. Patches came a day early after the identifiers and a proof of concept leaked.
Amazon's honeypots saw an exploit attempt on 17 October, four days before disclosure, from an anonymised address. Broader attacks began within hours of release, and CrowdStrike notes they leave almost no log trace. The NCSC and CISA say patch at once or consider taking the system offline.
https://thehackernews.com/2026/10/someone-tried-to-exploit-php2shell-4.html
The Hacker NewsSomeone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly DisclosedAmazon detected a PHP2Shell exploit attempt on October 17, before disclosure, followed by further attempts after patches were released.
Chainguard have also raised over $700M in VC funding.
IMO, it would be more productive if they conceded to the inevitable unsustainable VC lifecycle, and donate whatever cash is left to the real heroes, like the PHP core team, community distro teams, and distro packagers, rather than making their lives more stressful to jump at marketing opportunities.
“PHP is dead”
It’s so dead there was absolutely no website who was put yesterday on a preventive maintenance mode while waiting a security patch.
It’s so dead I heard the journalist, on the newscast of the public broadcaster, trying to explain what is PHP while showing absolutely no understanding of what is PHP.
On the upside: I don't see many AI chatbots on websites as #PHP is still turned off.
Today's #PHP #Security Release, and How We're Strengthening PHP Security — The PHP Foundation — Supporting, Advancing, and Developing the PHP Language
https://thephp.foundation/blog/2026/10/21/todays-php-security-release-and-how-were-strengthening-php-security/
thephp.foundationToday's PHP Security Release, and How We're Strengthening PHP SecurityDescribing the story behind how critical security vulnerabilities were found and fixed.
#Mapbender 4.2.8 / 5.0.2 released
In response to the announced critical #PHP security updates, we have published updated Mapbender Docker releases. PHP 8.4.27 is the updated, patched PHP version.
The releases provide also some Bugfixes see
- https://github.com/mapbender/mapbender/blob/v5.0.2/CHANGELOG.md
- https://github.com/mapbender/mapbender/blob/v4.2.8/CHANGELOG.md
Read more https://lists.osgeo.org/pipermail/mapbender_users/2026-October/006601.html
Blogger Elias Taylor says public PHP2Shell PoCs fail on vanilla PHP and lean on a file-inclusion bug the target must already have. The top-starred PoC repo's README lists such app-side conditions for chain A and says code for chains D and E is for paid subscribers. PHP's advisory still says RCE was validated against default mod_php (attack complexity high), and Datadog says it reproduced both flaws.
The PHP Foundation says first signs of the flaw behind CVE-2026-109618 appeared in 2024, and the fix then stalled for months: "a structural failure." PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix it and CVE-2026-109619, both unauthenticated RCE (CVSS 9.2). It says Chainguard broke the embargo 6+ hours early; Chainguard's CEO told The Register he shipped because vendors reported exploitation. AWS saw a honeypot attempt on Oct 17.
thephp.foundationToday's PHP Security Release, and How We're Strengthening PHP SecurityDescribing the story behind how critical security vulnerabilities were found and fixed.
🚨 Urgent: PHP has two critical unauthenticated RCE flaws. Patch now — WordPress & others are vulnerable.
Sammy.HKPHP Releases Emergency Patches for Two Critical Unauthenticated RCE Vulnerabilities - Sammy.HKPHP Patches Two Critical Vulnerabilities: Unauthenticated Remote Code Execution Possible — Official Urges Immediate Update The PHP project has issued an emergency announcement on its official website stating that PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 patch two critical vulnerabilities that Continue reading PHP Releases Emergency Patches for Two Critical Unauthenticated RCE Vulnerabilities→
#PHP hate is back on the menu and it's making me feel all nostalgic 🥲 The OG slop is back in the spotlight
Vancouver Aquarium is looking someone to be their otter mascot. Fediverse, do your thing! #YVR #Mascot #Otter #Vancouver #Aquarium
People Making GamesPhilip Drobar 🎮 🎬 (@[email protected])Attached: 2 images
Vancouver Aquarium is looking someone to be their otter mascot.
Fediverse, do your thing!
#YVR #Mascot #Otter #Vancouver #Aquarium
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
#PHP2Shell #PHP #CVE2026109618 #CVE2026109619 #RCE #ExploitedInTheWild #PoC #CyberSecurity
Cheers everyone
Less code less problems,
Just sayin
🤖 PHP2Shell (CVE-2026-109618/109619): the bug is real, but the thousands of "PoCs" flooding GitHub don't work on vanilla PHP — most silently rely on an LFI prerequisite, i.e. a second bug. 24h after disclosure: no working exploit. Not a Log4Shell.
🔗 https://eliastaylor.com/noexploit/
#CVE #PHP #Exploit #InfoSec
Let’s not forget .php could be a top level domain.
Be sure to let ICANN know on the 17th how much a file name ending in .php would improve your life, much like today.
https://newgtldprogram-aps.icann.org/applications/KKWT2621T-T46596-R/summary
IYKYK
New docker image for HortusFox v6.4 is now live! 😊
A big thanks to @thephpf for working so hard on the PHP patches. And everyone involved building docker images, posting news, supporting maintainers, and updating their own projects. You did an awesome job today!
What a #Spooktober indeed. We all deserve some rest now. 😴
Good night everyone. See y'all tomorrow. 💚
#PHP #FOSS #OpenSource #SelfHosted #SelfHosting #PHP2Shell #InfoSec
Docker image is in the making ‼️
➡️ Monitor the release here:
https://github.com/danielbrendel/hortusfox-web/releases/tag/v6.4
If you use the unaltered dockerfile, please update your workspace as soon as possible once the image build has finished.📢
#FOSS #OpenSource #SelfHosted #SelfHosting #PHP #PHP2Shell #InfoSec #HortusFox