The #PHP #Bug That Broke The #Internet #MentalOutlaw #Security #Safety #php25hell
XFEDI
ActivityPub#php
Public posts with this hashtag.

A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
#Laravel #TokenGuard #CVE2026114509 #AuthBypass #PoC #PHP #WebSecurity #CyberSecurity
🚨🐛 SIGINT // Cybersecurity Watch — 2026-10-23
Critical PHP flaws affecting ~70% of websites now under active exploitation—patch immediately as exploit code is public and attacks accelerate.
https://www.securityweek.com/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws/
#PHP #CVE #InfoSec #Cybersecurity
 SecurityWeekPHP2Shell: Mass Exploitation Looms for Leaked Critical PHP FlawsPHP2Shell refers to two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that could lead to unauthenticated RCE.

HN user petecooper, who posted the PHP RCE CVE IDs on Oct 20, apologizes, saying a contact told them there was no embargo (their account; contact unnamed). Their post said CVSS 10.0. The PHP Foundation says the leaked IDs carried a wrong time and a wrong 10.0 score (actual 9.2) and names no one. AWS logged an exploit attempt on Oct 17 and calls the actor's source of details unclear.
🚨 This time the bug isn’t in your code, it’s in PHP itself.
PHP2Shell is two CVEs in the PHP runtime (CVE-2026-109618, CVE-2026-109619) that can lead to unauthenticated RCE.
When something like this lands, the first question is usually: what exactly is affected, and what do I need to patch?
I’d rather answer that from the terminal than from twelve browser tabs.
With the ZEN SecDB CLI:
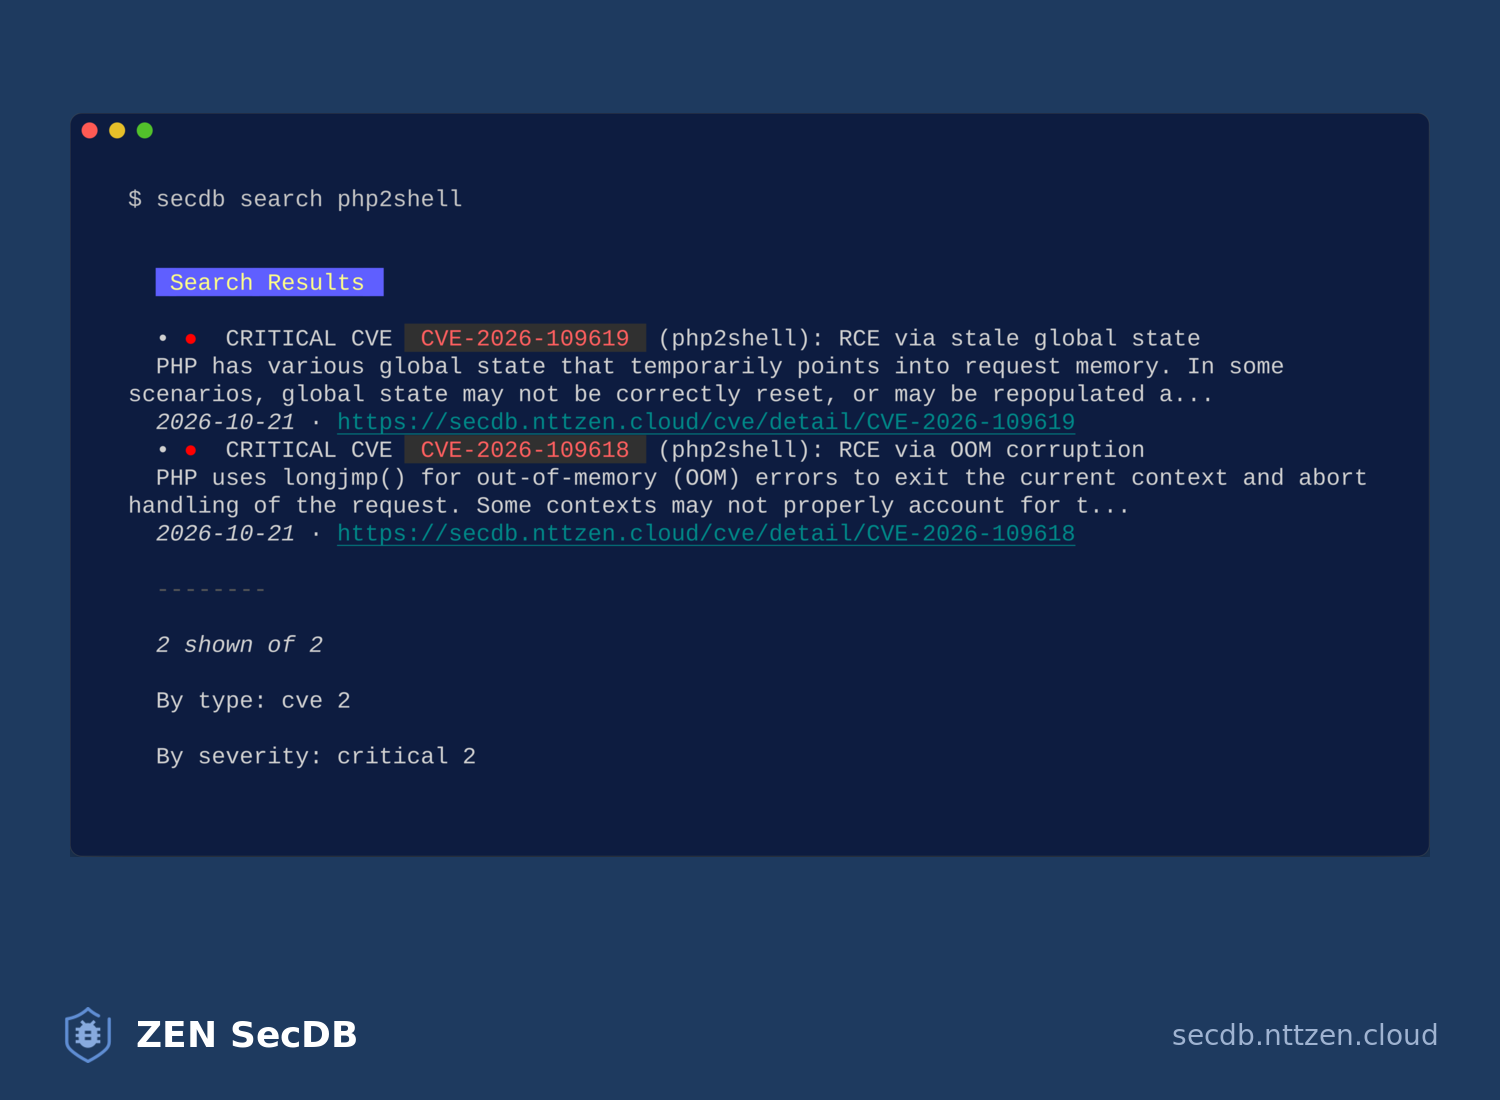
1️⃣ secdb search php2shell
finds both CVEs.
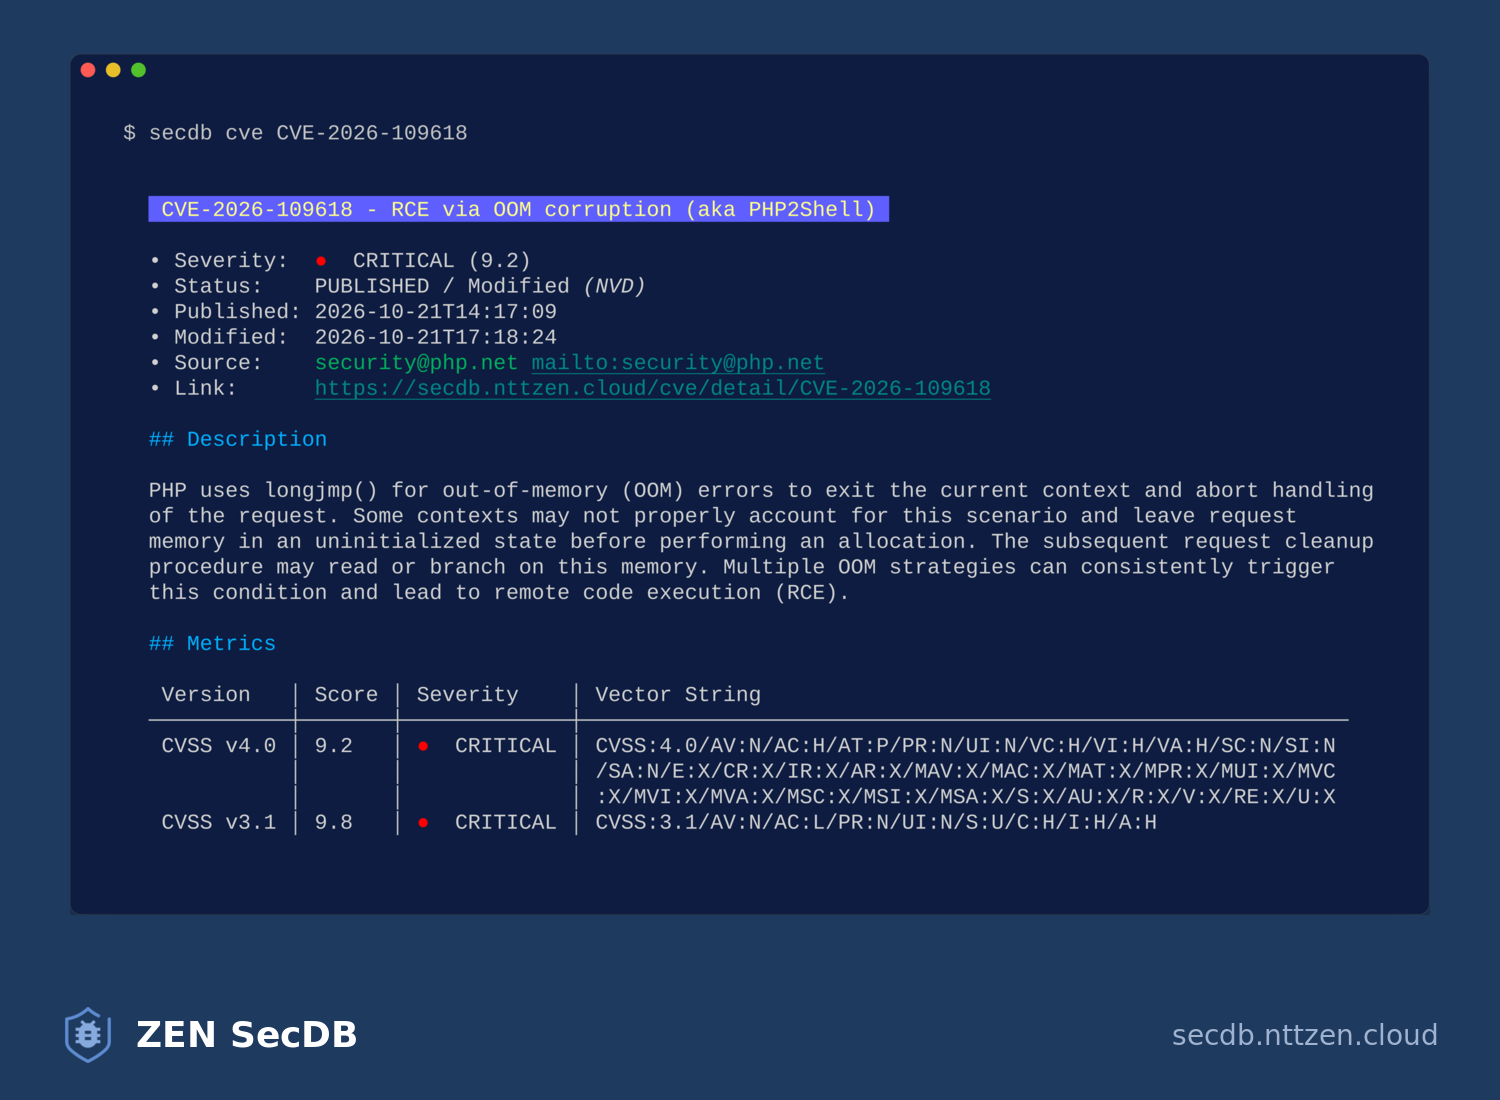
2️⃣ secdb cve CVE-2026-109618
gives the full record: description, CVSS 4.0 at 9.2, CVSS 3.1 at 9.8, vectors, references and vendor advisories from Debian, Red Hat, SUSE, Ubuntu, Arch, Gentoo, FreeBSD and others.
That’s useful because you can quickly check whether your distro already ships a fix, instead of going through each security tracker manually.
If you run PHP, upgrade to 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or use the patched package provided by your distro.
Configuration mitigations may reduce the risk, but they don’t replace patching.
And if the server was exposed, it’s probably worth checking whether it was already compromised.
ZEN SecDB: https://secdb.nttzen.cloud
CLI: https://github.com/giterlizzi/secdb-cli
CVE-2026-109618: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109618
CVE-2026-109619: https://secdb.nttzen.cloud/cve/detail/CVE-2026-109619
#PHP2Shell #PHP #RCE #InfoSec #VulnerabilityManagement #CVE
#NTTDATA #ZENSecDB
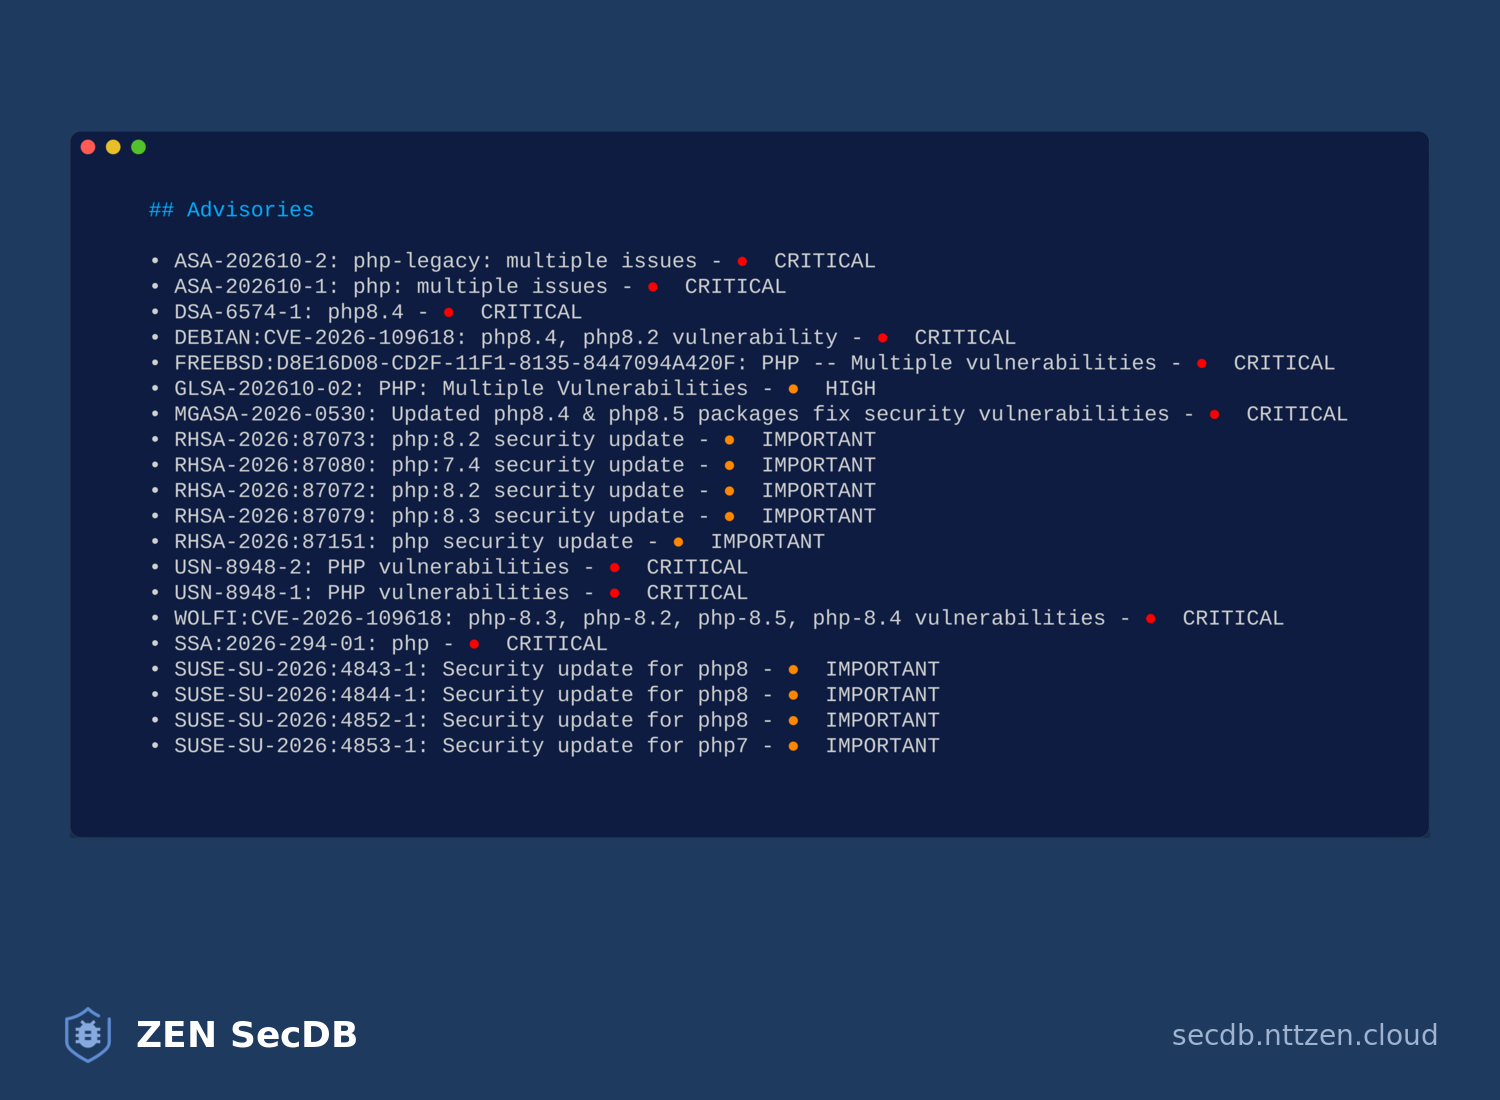
 ZEN SecDB PortalHome | ZEN SecDB Portalpowered by YaVS - YaVS Ain't Vulnerability Scanner...

#meme #php #cybersecurity #security #cybercrime #hack #web #www #server #patch #admin #administrator #Software #vulnerability #bug #internet #online


My goofy shared server is still working on a patch to their PHP version. As much as I love Pure Blog, this does make me miss hand coding some HTML or using a tiny static site again. I prefer my web sites all to be as minimalist and as unhackable as possible. #php

I've heard that #PHP went rogue and is allowing third parties to run code on its servers
TV news anchor trying to explain what php is.
"Php is a program that runs on servers. Servers are computers without a monitor."
He's not...wrong? 😂
#PHP
Active exploitation attempts have already been observed following the disclosure of the #PHP2Shell vulnerabilities.
Netcraft is supporting the NCSC response by helping notify potentially affected organizations and providing actionable guidance for remediation. https://www.netcraft.com/blog/php2shell-netcraft-supports-u.k.-response
 www.netcraft.comNetcraft Supports Response to PHP2ShellNetcraft and the NCSC have issued more than 50,000 proactive notifications in response to the critical PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619), helping organizations identify affected PHP systems and take urgent remediation action.

Recent activity on the #php hashtag has never been so high, smile and wave boys (and girls), smile and wave.


A lot of folks are having to deal with the php2shell issue in their infrastructure right now, and Nico Kruger has some advice on how you can check if your infrastructure is impacted, and how to roll out the patched packages:
1. Upgrade all PHP packages together.
2. Restart workers after patches.
3. Roll out in waves, noop first.
Full read:
https://www.puppet.com/blog/patching-php2shell-with-puppet
 PuppetHow to Secure Your PHP Infrastructure and Remediate php2shell with Puppet | PuppetThe critical PHP2Shell vulnerabilities put PHP systems at risk of remote code execution. Identify affected PHP versions, check your environment, and use Puppet to deploy patched packages consistently across your infrastructure.

Foundational open-source software is an enormous responsibility, and the people doing that work deserve recognition.
I hope this helps someone who was wondering whether their website is affected.

OpenAI says its AI found the PHP2Shell bugs before attackers did, and Amazon says it saw hackers trying to use them four days before the rest of us were told they existed. That lead doesn’t last long when the other side has AI too, or when a hint of exposure slips out while the fix is still being developed.
If you run a website, PHP is probably somewhere underneath it. Wiz says it powers about 70% of the web, mostly because WordPress is built on it. The National Security Agency’s advice was blunt: update right away, or take the site offline until you can.
Two things I’d do now:
・ Count your WordPress sites. Then count again. That campaign microsite that marketing launched in 2019 is on that list, and so is the one an agency still hosts for you.
・ Decide today who gets to say “take it down.” Pulling a public site is a business call, and you don’t want to be hunting for that person at 2 a.m. during an active attack.
Patch today, and then go find the sites you forgot you had!
#CyberSecurity #WordPress #AI #PHP #security #privacy #cloud #infosec
 Ars TechnicaHackers got a four-day head start on epic PHP2Shell vulnerabilityHackers were already probing the bug before defenders were told it existed.
Here's a thought about chainguards break of embargo, and I'm just throwing it out:
Intentional unfair business practices to gain market advantages at the expense of the whole world's cyber security.
#php2shell #php #chainguard #infosec #cybersecurity #opensource #crime
Internet code is heavily kludged, So an #LLM hit on a fundamental strut was inevitable. #PHP was an obvious target; we're now watching websites flicker out & critical infrastructures becoming endangered. RIP internet as anything but Harrison Bergeron noise machine. https://www.404media.co/php2shell-black-october-ai-is-changing-everything-about-hacking-no-one-knows-what-happens-next/ #cybersecurity #AI
 404 MediaAI Is Changing Everything About Hacking. No One Knows What Happens Next'Black October:' The PHP vulnerabilities and a series of other hacks and bugs have cybersecurity experts freaking out and unsure what happens next.

My new PHP2Shell Checker - Read - only PHP package checker for Debian 12/13. Checks PHP2Shell fixes (CVE-2026-109618, CVE-2026-109619), APT updates, and package holds. #critical #cve #php2shell #php #checker #CVE-2026-109618 #CVE-2026-109619 https://github.com/toxy4ny/php2shell-checker https://gitlab.com/toxy4ny/php2shell-checker
PHP2Shell: two critical PHP RCE vulnerabilities — patches and protection
🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-patches-protection
#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #PHP #vulnerability
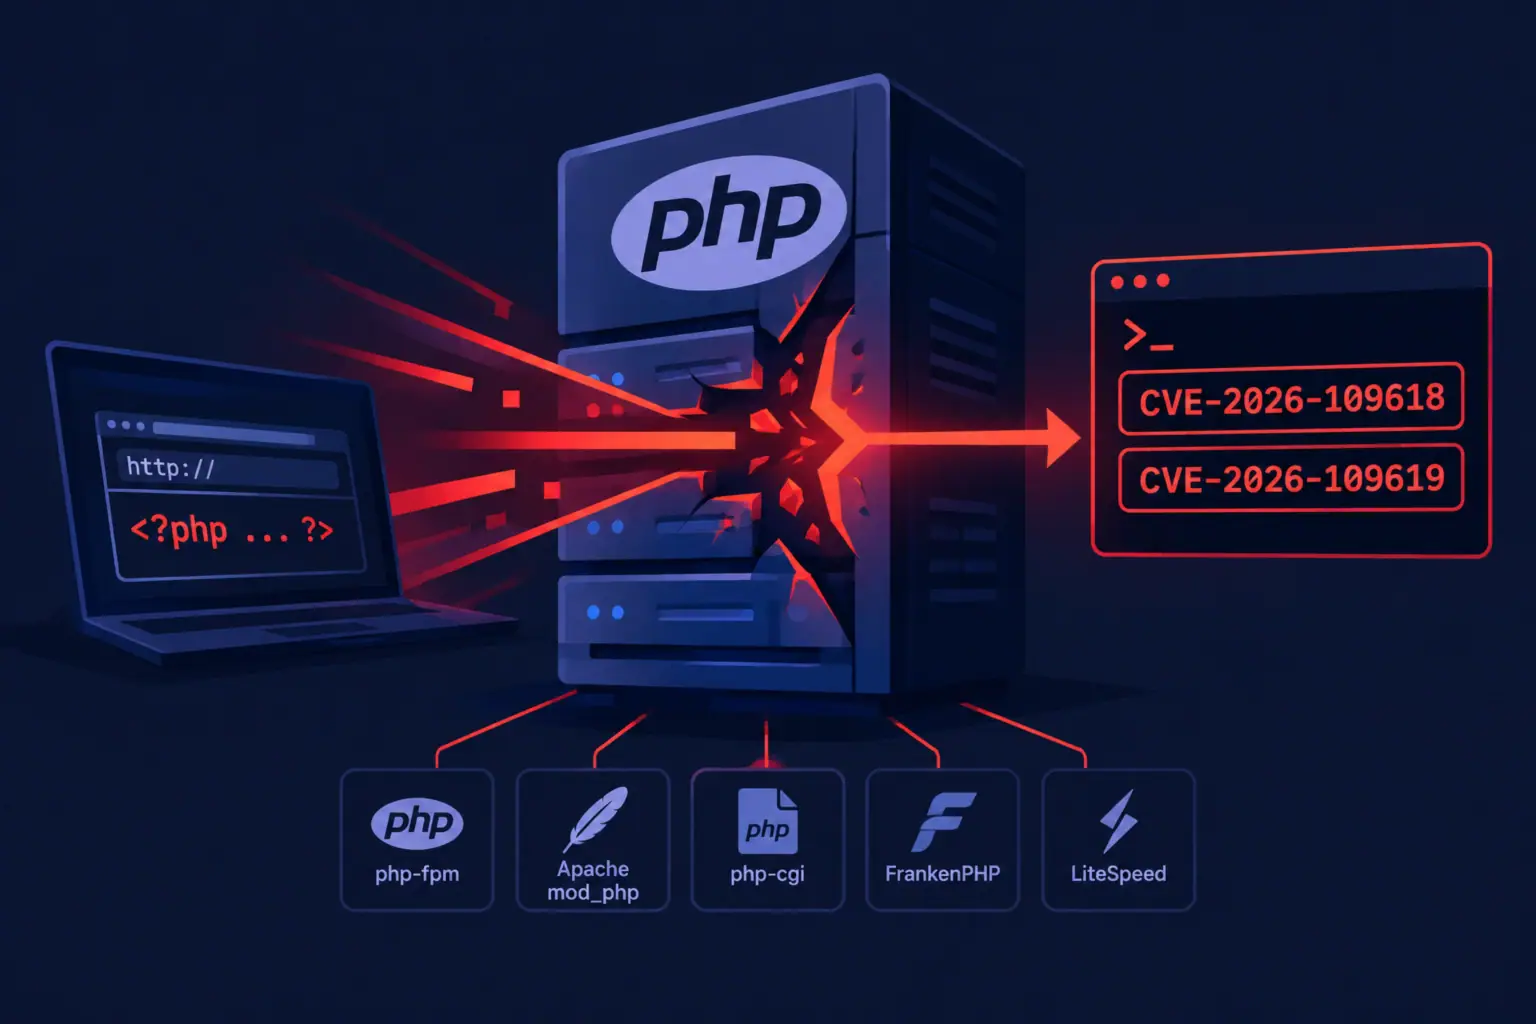 CyberSecureFoxPHP2Shell: Two Critical PHP RCE Vulnerabilities — Patches And ProtectionOn October 21, 2026, the PHP team released emergency updates for two critical remote code execution (RCE) vulnerabilities collectively dubbed PHP2Shell. The

We are getting reports of #php2shell attempts against web servers a day before the public announcement as seen in logs.
How is your Thursday going?

PHP2Shell (CVE-2026-109618/109619): two RCEs in PHP itself. Unauthenticated attackers can run code before any app code runs.
Patched: 8.5.12, 8.4.27, 8.3.36, 8.2.35. PHP 8.1 and older: no fix from the PHP project, ask your distro.
Can't update today? Free, tentative CrowdSec WAF virtual patches:
CVE-2026-109618: https://app.crowdsec.net/hub/author/crowdsecurity/waf-rules/vpatch-CVE-2026-109618
CVE-2026-109619: https://app.crowdsec.net/hub/author/crowdsecurity/waf-rules/vpatch-CVE-2026-109619
A stopgap, not a fix.

Cuando el 70% del mundo usa la misma tecnología.. y los hackers usan la IA para encontrar huecos de seguridad...
Varios sitios y servicios del gobierno de mi ciudad y mi provincia fueron parcialmente cerrados para arreglar su #PHP


A critical security update addresses two PHP zero-day RCE vulnerabilities. Learn how to protect your servers from CVE-2026-109618 and CVE-2026-109619 today.
 Daily Tech NowCritical PHP Zero-Day RCE Vulnerabilities Update ReleasedA critical security update addresses two PHP zero-day RCE vulnerabilities. Learn how to protect your servers from CVE-2026-109618 and CVE-2026-109619 today.
As ever, the biggest vulnerability of the last 36-48 hours has been managers panicking.
🤖 PHP2Shell: CVE-2026-109618 & CVE-2026-109619, critical unauthenticated RCE in PHP (mod_php, PHP-FPM, php-cgi, LiteSpeed). Fixed Oct 21 in 8.5.12/8.4.27/8.3.36/8.2.35. Amazon: exploitation began Oct 17, four days before disclosure.
🔗 https://www.bleepingcomputer.com/news/security/amazon-says-php2shell-exploitation-began-4-days-before-patches/
#CVE #Exploit #CyberSec #PHP
 BleepingComputerAmazon says PHP2Shell exploitation began 4 days before patchesSecurity researchers at Amazon Threat Intelligence say attackers began targeting the PHP2Shell flaws four days before security patches were released on Wednesday.

PHP2Shell field report — the attacker-side view.
The first exploit-shaped request hit our Mirage honeypot fleet at 21:57 UTC on 20 Oct, ~16h before the patch embargo lifted. Over the next 48h: 9 source IPs, 7 countries, 2 distinct attack shapes.
Highlights:
One actor swept body size <1KB → 16KB+, 200+ unique payloads in 2 min — live calibration of the OOM trigger
The lead tool stamps ----p2shell<hex> into its multipart boundary: a zero-false-positive detection tell we haven’t seen documented elsewhere
A B8RAT/1.0 actor reaching for the deserialization path (CVE-2026-109619) while others hammer the OOM path (CVE-2026-109618)
Independent confirmation of the pre-disclosure exploitation Amazon & Cloudflare reported, from a second sensor network
Full writeup + IOCs:
https://offseq.com/en/research/php2shell-first-48-hours/
 OffSeqPHP2Shell in the wild: the first 48 hours on a honeypot fleet – OffSeqPHP2Shell leaked before its patch, and the first exploit-shaped request hit OffSeq's Mirage fleet about sixteen hours before the fix shipped.

The day after another AI company scared the world out of its wits:
Reuters: In the 10 hours before it was publicly announced, across the network we saw thousands of attempts to exploit it," Cloudflare CEO Matthew Prince said in a post on X late on Wednesday https://www.reuters.com/world/asia-pacific/cloudflare-sees-millions-exploit-attempts-after-php-disclosure-2026-10-22/ @Reuters #Cloudflare #infosec #PHP #vulnerability
$ sudo zypper ref
$ sudo zypper up
$ sudo systemctl restart apache2.service

🚨 𝗖𝗥𝗜𝗧𝗜𝗖𝗔𝗟 𝗦𝗘𝗖𝗨𝗥𝗜𝗧𝗬 𝗔𝗟𝗘𝗥𝗧: 𝗣𝗛𝗣 𝗥𝗖𝗘 𝗗𝗘𝗧𝗘𝗖𝗧𝗘𝗗 🚨
If you're on affected versions, 𝗽𝗮𝘁𝗰𝗵 𝗜𝗠𝗠𝗘𝗗𝗜𝗔𝗧𝗘𝗟𝗬. Critical vulnerabilities (CVE-2026-109618 & CVE-2026-109619) require urgent action.
✅ 𝗥𝗘𝗟𝗜𝗔𝗡𝗢𝗜𝗗 𝗜𝗦 𝗦𝗔𝗙𝗘:
RELIANOID Load Balancer (Enterprise & Community Editions) is not affected because we do not use PHP internally. Your infrastructure remains secure.
Update others now: 👇
 RELIANOIDCritical PHP Remote Code Execution Vulnerabilities CVE-2026-109618 and CVE-2026-109619: Update Required