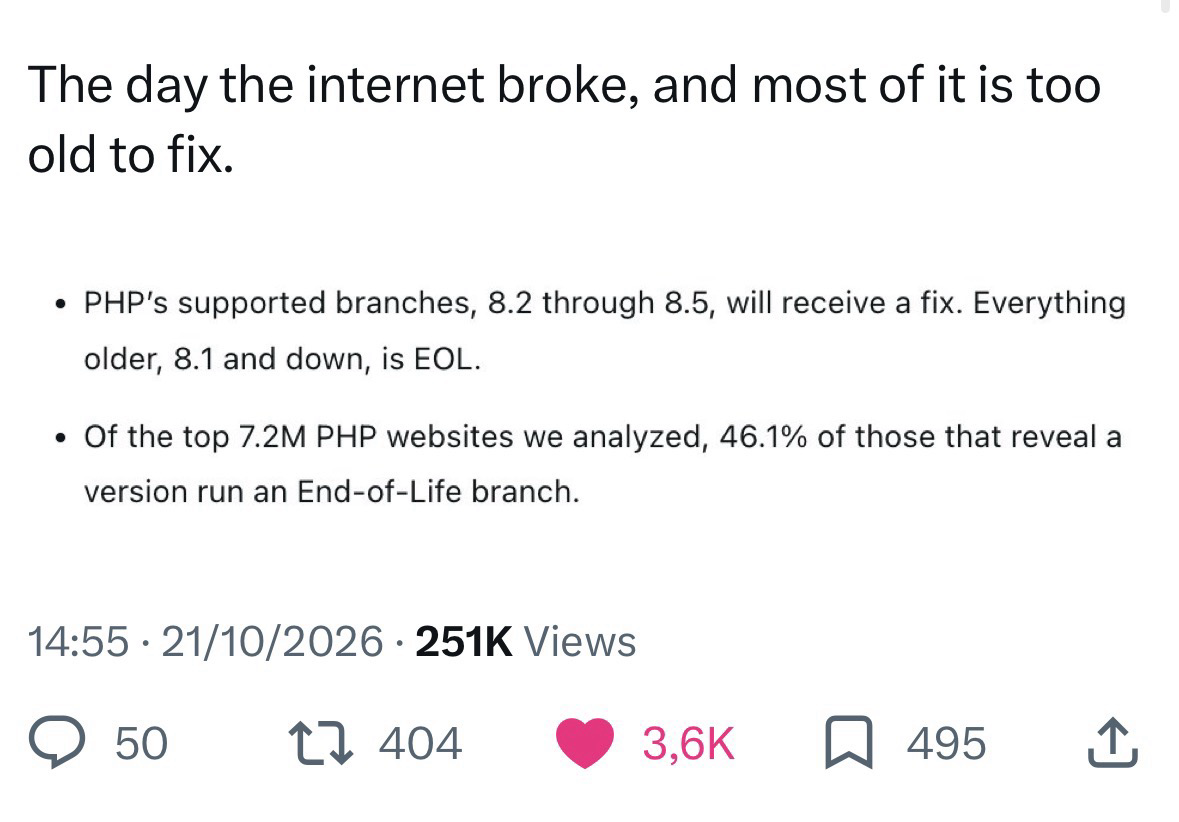
Today’s PHP Security Release, and How We’re Strengthening PHP Security, by @thephpf:
XFEDI
ActivityPub#php
Public posts with this hashtag.

Headline (and picture) of the day:
"The entire internet is officially in crisis mode."
Polygon: https://www.polygon.com/php-vulnerability-2026-what-is-security-update-today-issue-patch/ #infosec #PHP #vulnerability
 Polygon.comThe Entire Internet Is Officially In Crisis Mode TodayWebsites and services ranging from Spotify to WordPress are all at risk thanks to a massive PHP security breach

The next few days won’t be pretty. Brace yourself friends. #PHP #php2shell
This is HUGE. I mean it woke someone up in the European Union who may schedule a meeting about it #php https://www.bbc.com/news/articles/cmly0lg3w5x2o
 www.bbc.comWebsites taken down worldwide as critical PHP cyber-security update issuedThe vulnerabilities with PHP, a programming language widely used across the internet, have been described as the most significant ever found by AI.
Also, even tho I am not pro #OpenAI at all, the company has released a #codex skill that can help you in verifying if your website is at risk and needs to be updated ASAP. All you have to do is point your Codex at this GitHub repo: https://github.com/openai/php2shell-checker #PHP #php2shell
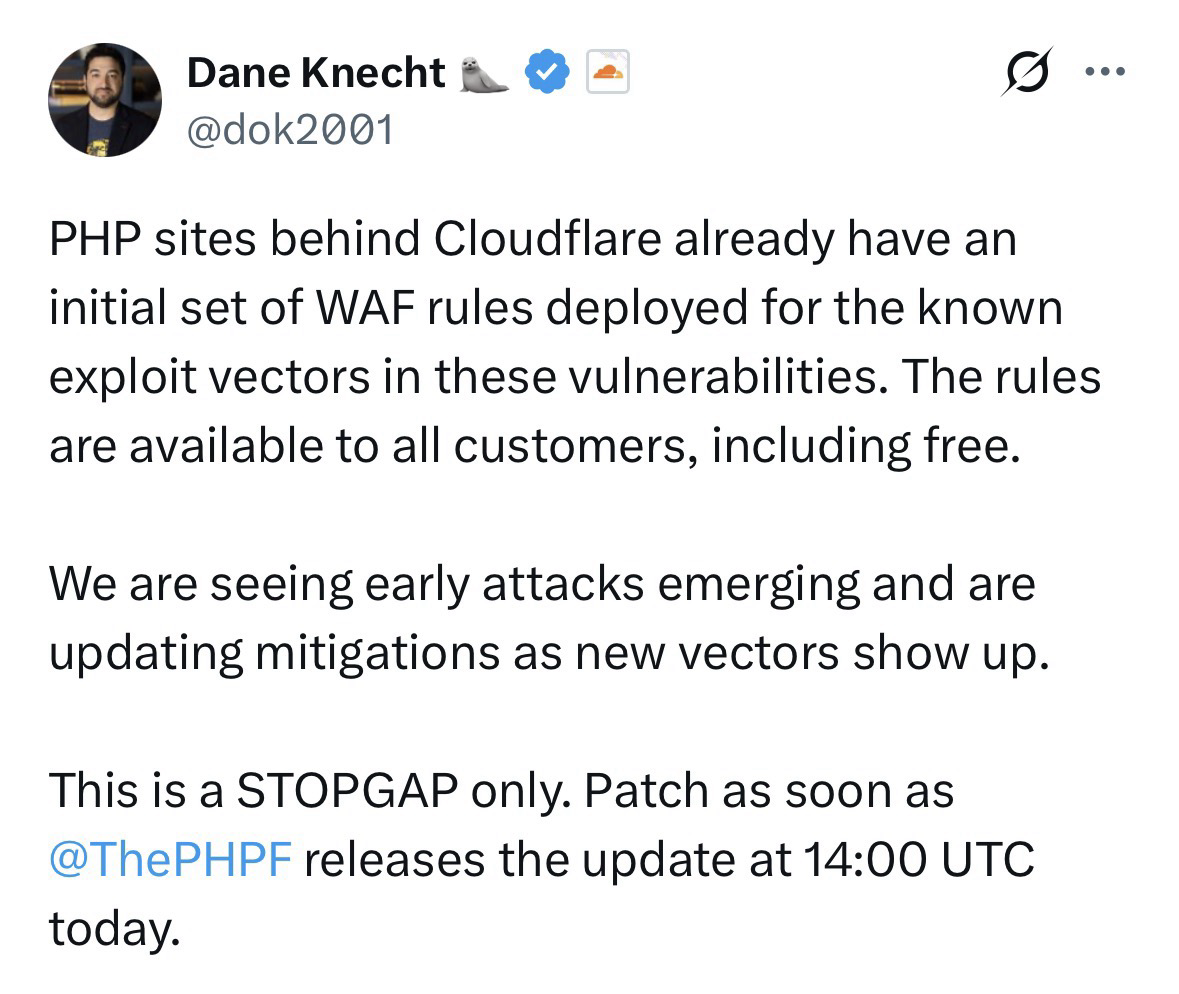
If you can’t update right away and your website is at risk, @cloudflare can temporarily help. Please note that this is a band-aid on a bleeding wound. #PHP #php2shell
Askip y a pas que PHP qui a en vulnérabilité, y a aussi les certificats SSL de emudhra.
Et là où c'est pas cool, c'est qu'on n'a pas eu de CERT-FR de l' #anssi à ce sujet (ou je l'ai pas vu passer T_T)
RE: https://fosstodon.org/@SocketSecurity/117479759341970308
Quantifications like "X% of the Web/Internet" are meaningless. What is the baseline? Total number of hosts? Total number of IP addresses? Total number of Web servers? Well I'm here to remind you that that total number is unknown so your count/total * 100 DOES NOT MAKE SENSE.
thank you for your attention.
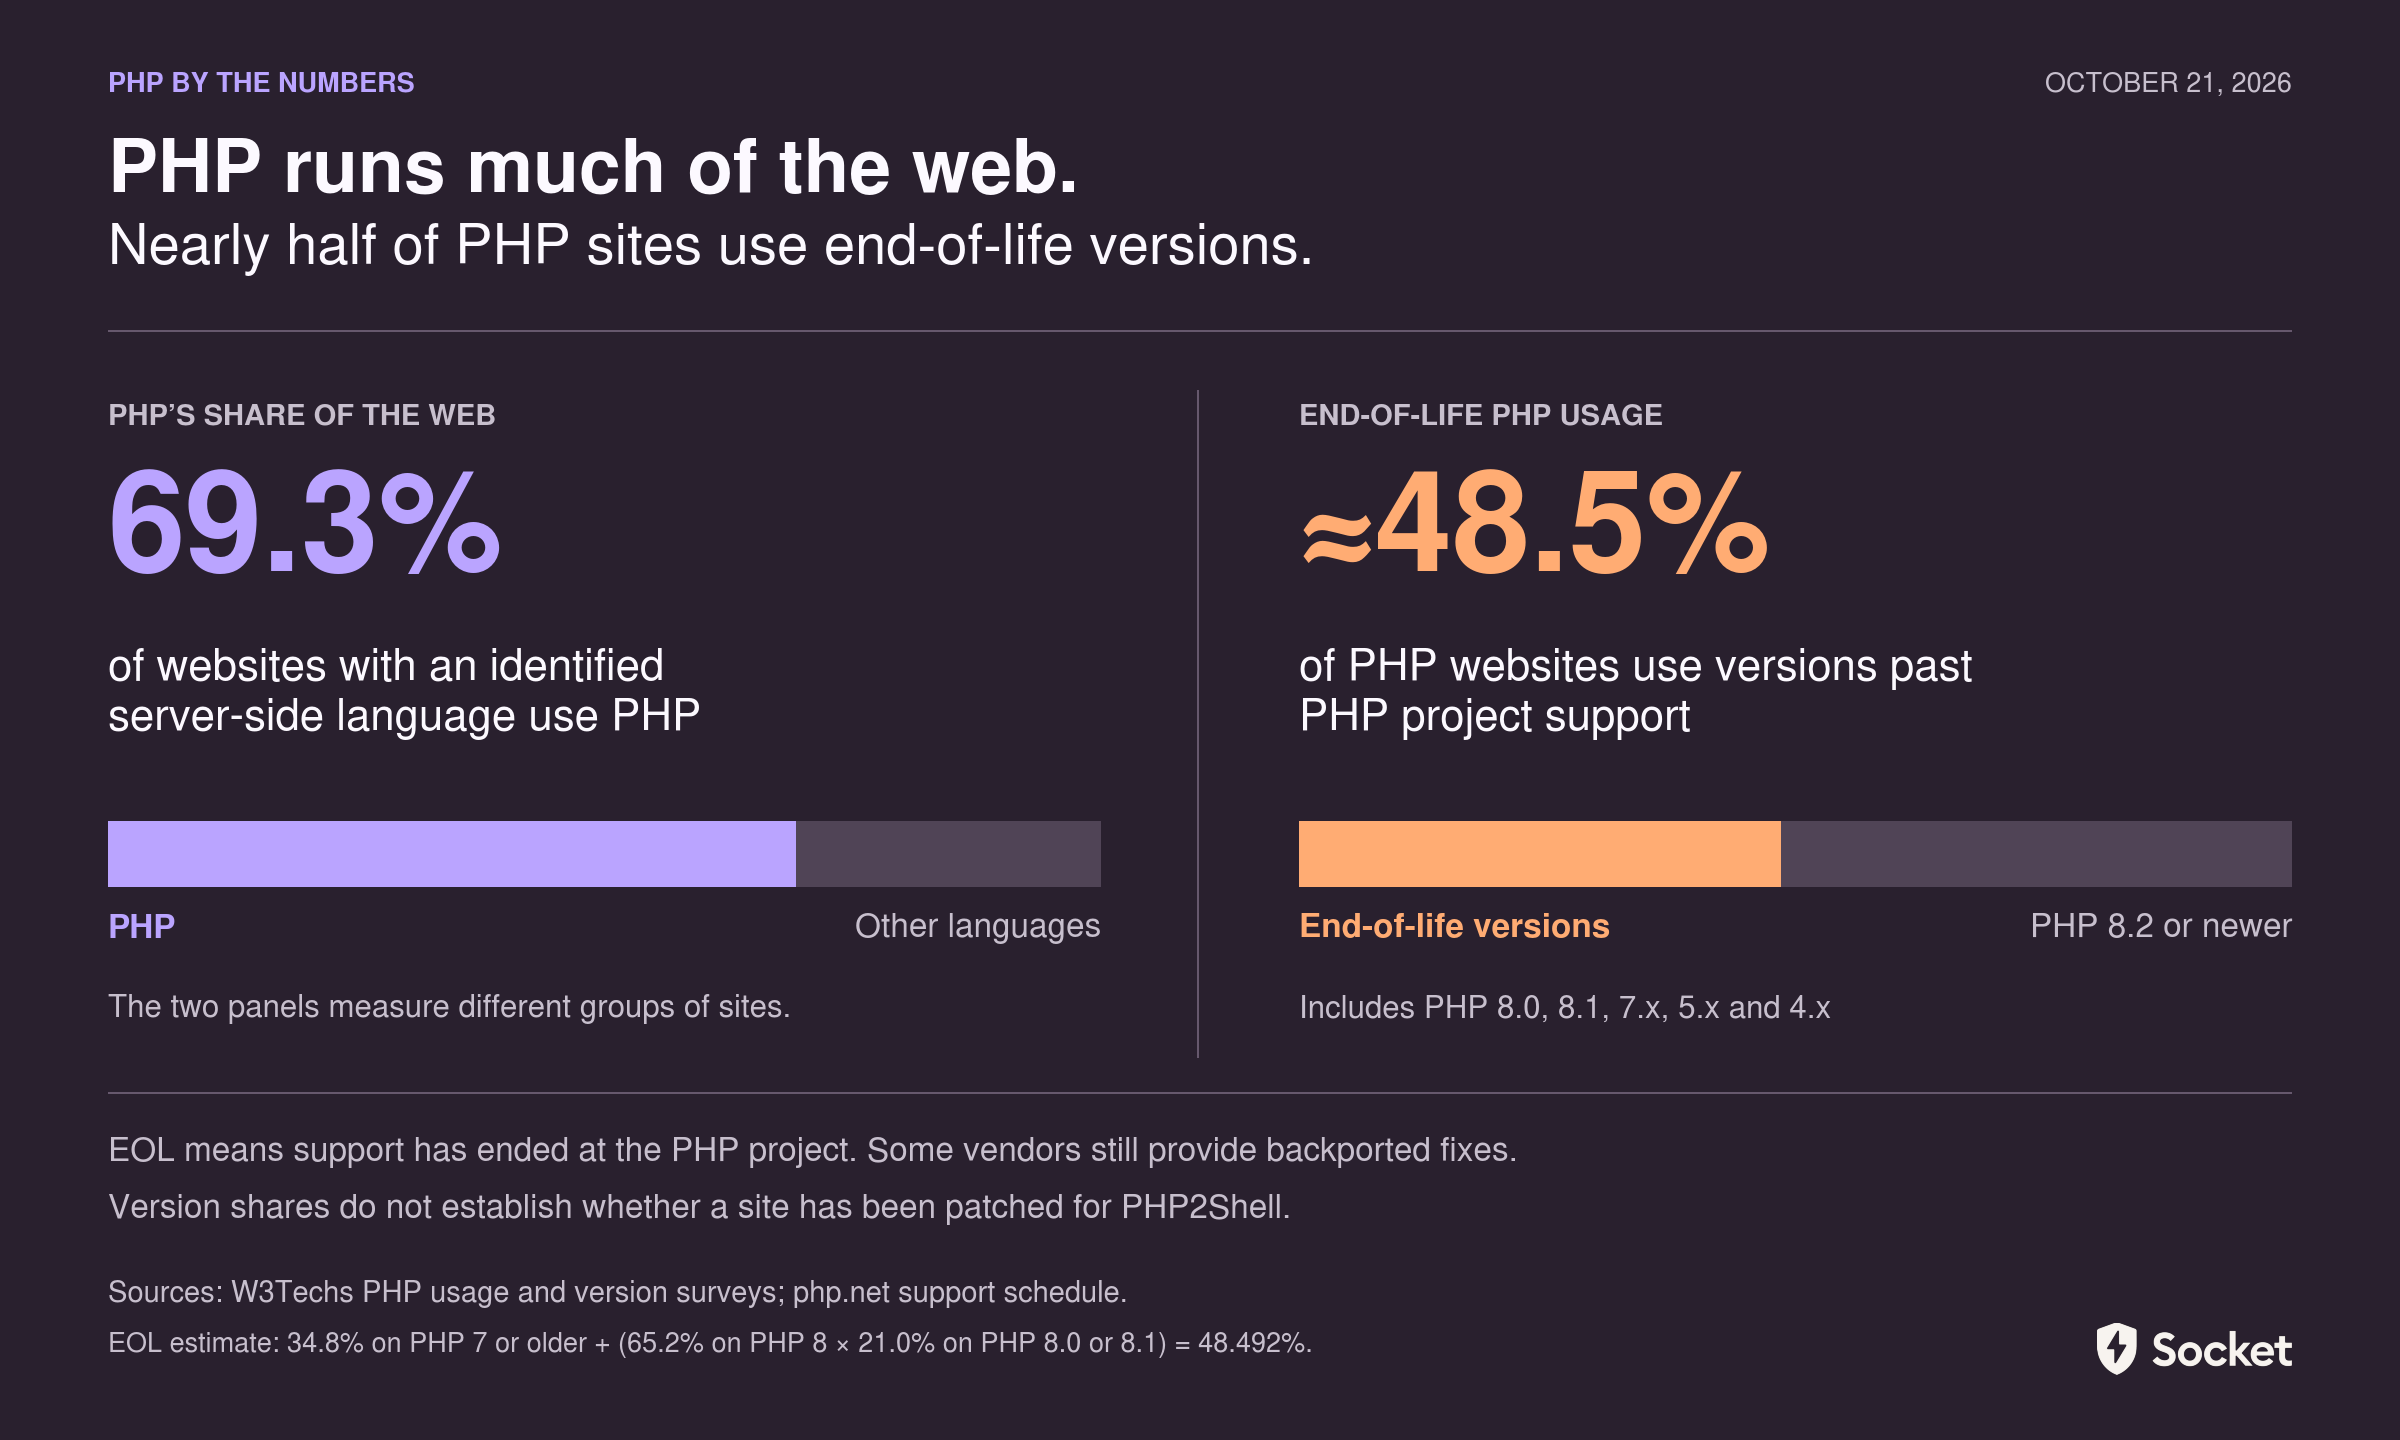
🚨 PHP has released emergency patches for two critical RCE vulnerabilities. Organizations unable to patch are advised to take affected systems offline. Believe it or not, PHP still runs an enormous amount of the web. And nearly half of #PHP sites run EOL versions. The vulnerabilit
 FosstodonSocket (@[email protected])Attached: 1 image
🚨 PHP has released emergency patches for two critical RCE vulnerabilities. Organizations unable to patch are advised to take affected systems offline.
Believe it or not, PHP still runs an enormous amount of the web. And nearly half of #PHP sites run EOL versions.
The vulnerabilities let attackers execute code on web servers without logging in. Cloudflare is already seeing expl
If you’ve been spending the day patching servers… don’t forget to eat!
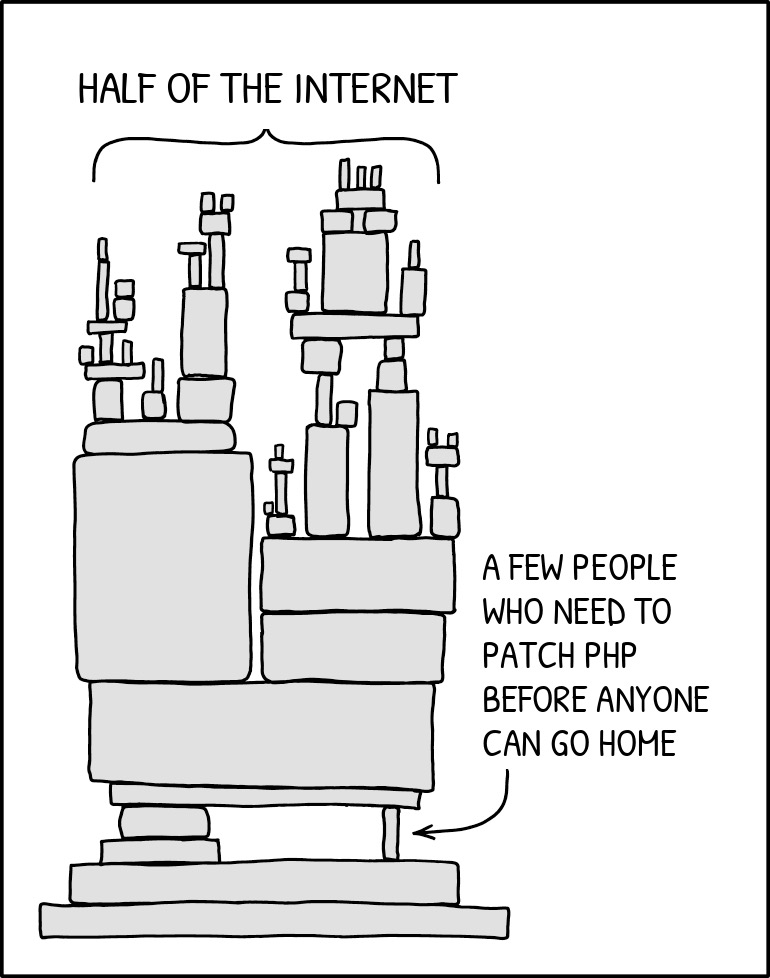
Remember that xkcd? Well, today is doomsday. Patch your PHP instances NOW. This is not a drill. https://www.php.net/archive/2026.php#2026-10-21-5 #PHP #php2shell
 www.php.netPHP: News Archive - 2026PHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
#Selfhosting and looking for a list of potential #PHP apps that may be impacted by the recent vulnerabilities?
This should be able to help:
https://selfh.st/apps/?language=PHP
#selfhost #selfhosted #opensource #foss #homelab #server #bug #bugs
 selfh.stSelf-Hosted Software and AppsA directory of self-hosted software and applications for easy browsing and discovery

What a fun day with #PHP #php2shell
Super Sache @heiseonline am besten durch #gemini ersetzen
https://www.heise.de/forum/heise-online/Kommentare/Wichtige-PHP-Updates-am-21-Oktober-beheben-Codeeinschleusung-Schwachstellen/Technische-Erlaeuterung-zum-Angriff/posting-46709771/show/
The Register: PHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatched https://www.theregister.com/security/2026/10/21/php-devs-publish-critical-bug-fix-as-site-owners-warned-pull-em-offline-if-youre-unpatched/5304519 @theregister #PHP #infosec #vulnerability
 theregisterPHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatchedWebsites down as precaution as exploits have already been published
Before everyone decides this is all #PHP's fault and they should switch to some other backend... ALL SOFTWARE IS VULNERABLE and #GenAI is making this far worse.
Look for projects that are sticking with human code rather than deskilling for some meaningless LoC benchmark, and digging themselves into a hole that every user of their project is being pulled into.
🚨 PHP has released emergency patches for two critical RCE vulnerabilities. Organizations unable to patch are advised to take affected systems offline.
Believe it or not, PHP still runs an enormous amount of the web. And nearly half of #PHP sites run EOL versions.
The vulnerabilities let attackers execute code on web servers without logging in. Cloudflare is already seeing exploits in the wild.
Patch the PHP runtime now. https://socket.dev/blog/php-critical-rce-patches
 socket.devPHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites OfflinePHP releases emergency patches for two critical RCE vulnerabilities as agencies urge organizations to take unpatched sites offline.
“PHP powers approximately 70% of websites”
Wow, had no idea #PHP was so widespread
 PHP2ShellPHP2Shell — AI uncovers critical vulnerabilities in the backbone of the webPHP2Shell is a family of critical vulnerabilities in core PHP that can allow unauthenticated attackers to execute code or disclose sensitive process memory.
CISA strongly urges organizations to immediately patch the recently disclosed critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619. These vulnerabilities, known as “php2shell,” allow for unauthenticated remote code execution in PHP and affect all PHP installations serving web requests. Organizations should immediately update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 to fix these vulnerabilities. While CISA has not observed exploitation of these vulnerabilities as of the time of publication, they pose a risk to organizations if left unpatched.

So it looks like all the Ubuntu fixed PHP versions are applied as backports?
Makes it a little tricky to guide users on how to validate that they're running a patched version.
Can't just do a PHP version check.

Someone patch #Wikipedia and bring it up ; kthxbye


Expect quite a few sites to return 404 or page not found errors today and possibly through the week. Here's my piece on the new PHP zero-day that affects about 70 percent of the Internet. We'll be updating the story with important new developments.
https://krebsonsecurity.com/2026/10/widespread-php-flaw-may-cause-many-site-outages-today/
 PHP2ShellPHP2Shell — AI uncovers critical vulnerabilities in the backbone of the webPHP2Shell is a family of critical vulnerabilities in core PHP that can allow unauthenticated attackers to execute code or disclose sensitive process memory.
Lienee ensimmäinen PHP ohjemointikielen Ylen uutisiin asti noussut ... uutinen. Tai mikään, vaikka merkittävä osa maailman webistä pyörii PHP:lla - siitä ei vain tiedä juuri kukaan muu kuin ATK henkilöt. Tai siis devaajat, iso osa muusta ATK porukasta lienee yhtä pimennossa tän faktan osalta kuin lähes koko muu väestökin.
About that PHP flaw ... the race to own has begun.
"Security company Wiz, which is owned by Google, claimed its researchers discovered the vulnerabilities in PHP partially using AI tools, while OpenAI and security firm Calif also say they independently discovered the issues and worked together."
Wired: ‘This Is Not a Drill’: Critical PHP Vulnerabilities Are Setting the Internet on Fire https://www.wired.com/story/this-is-not-a-drill-2-php-vulnerabilities-are-setting-the-internet-on-fire/ @WIRED #infosec #vulnerability #PHP
Update to php ≥ 8.5.12 and/or php-legacy ≥ 8.3.36 to prevent remote code execution

If you're running #Nextcloud or any other PHP application, whether in containers or natively, update your PHP installations!
Especially if you're using Apache with mod_php, which is considered the highest-risk configuration for #PHP2Shell.
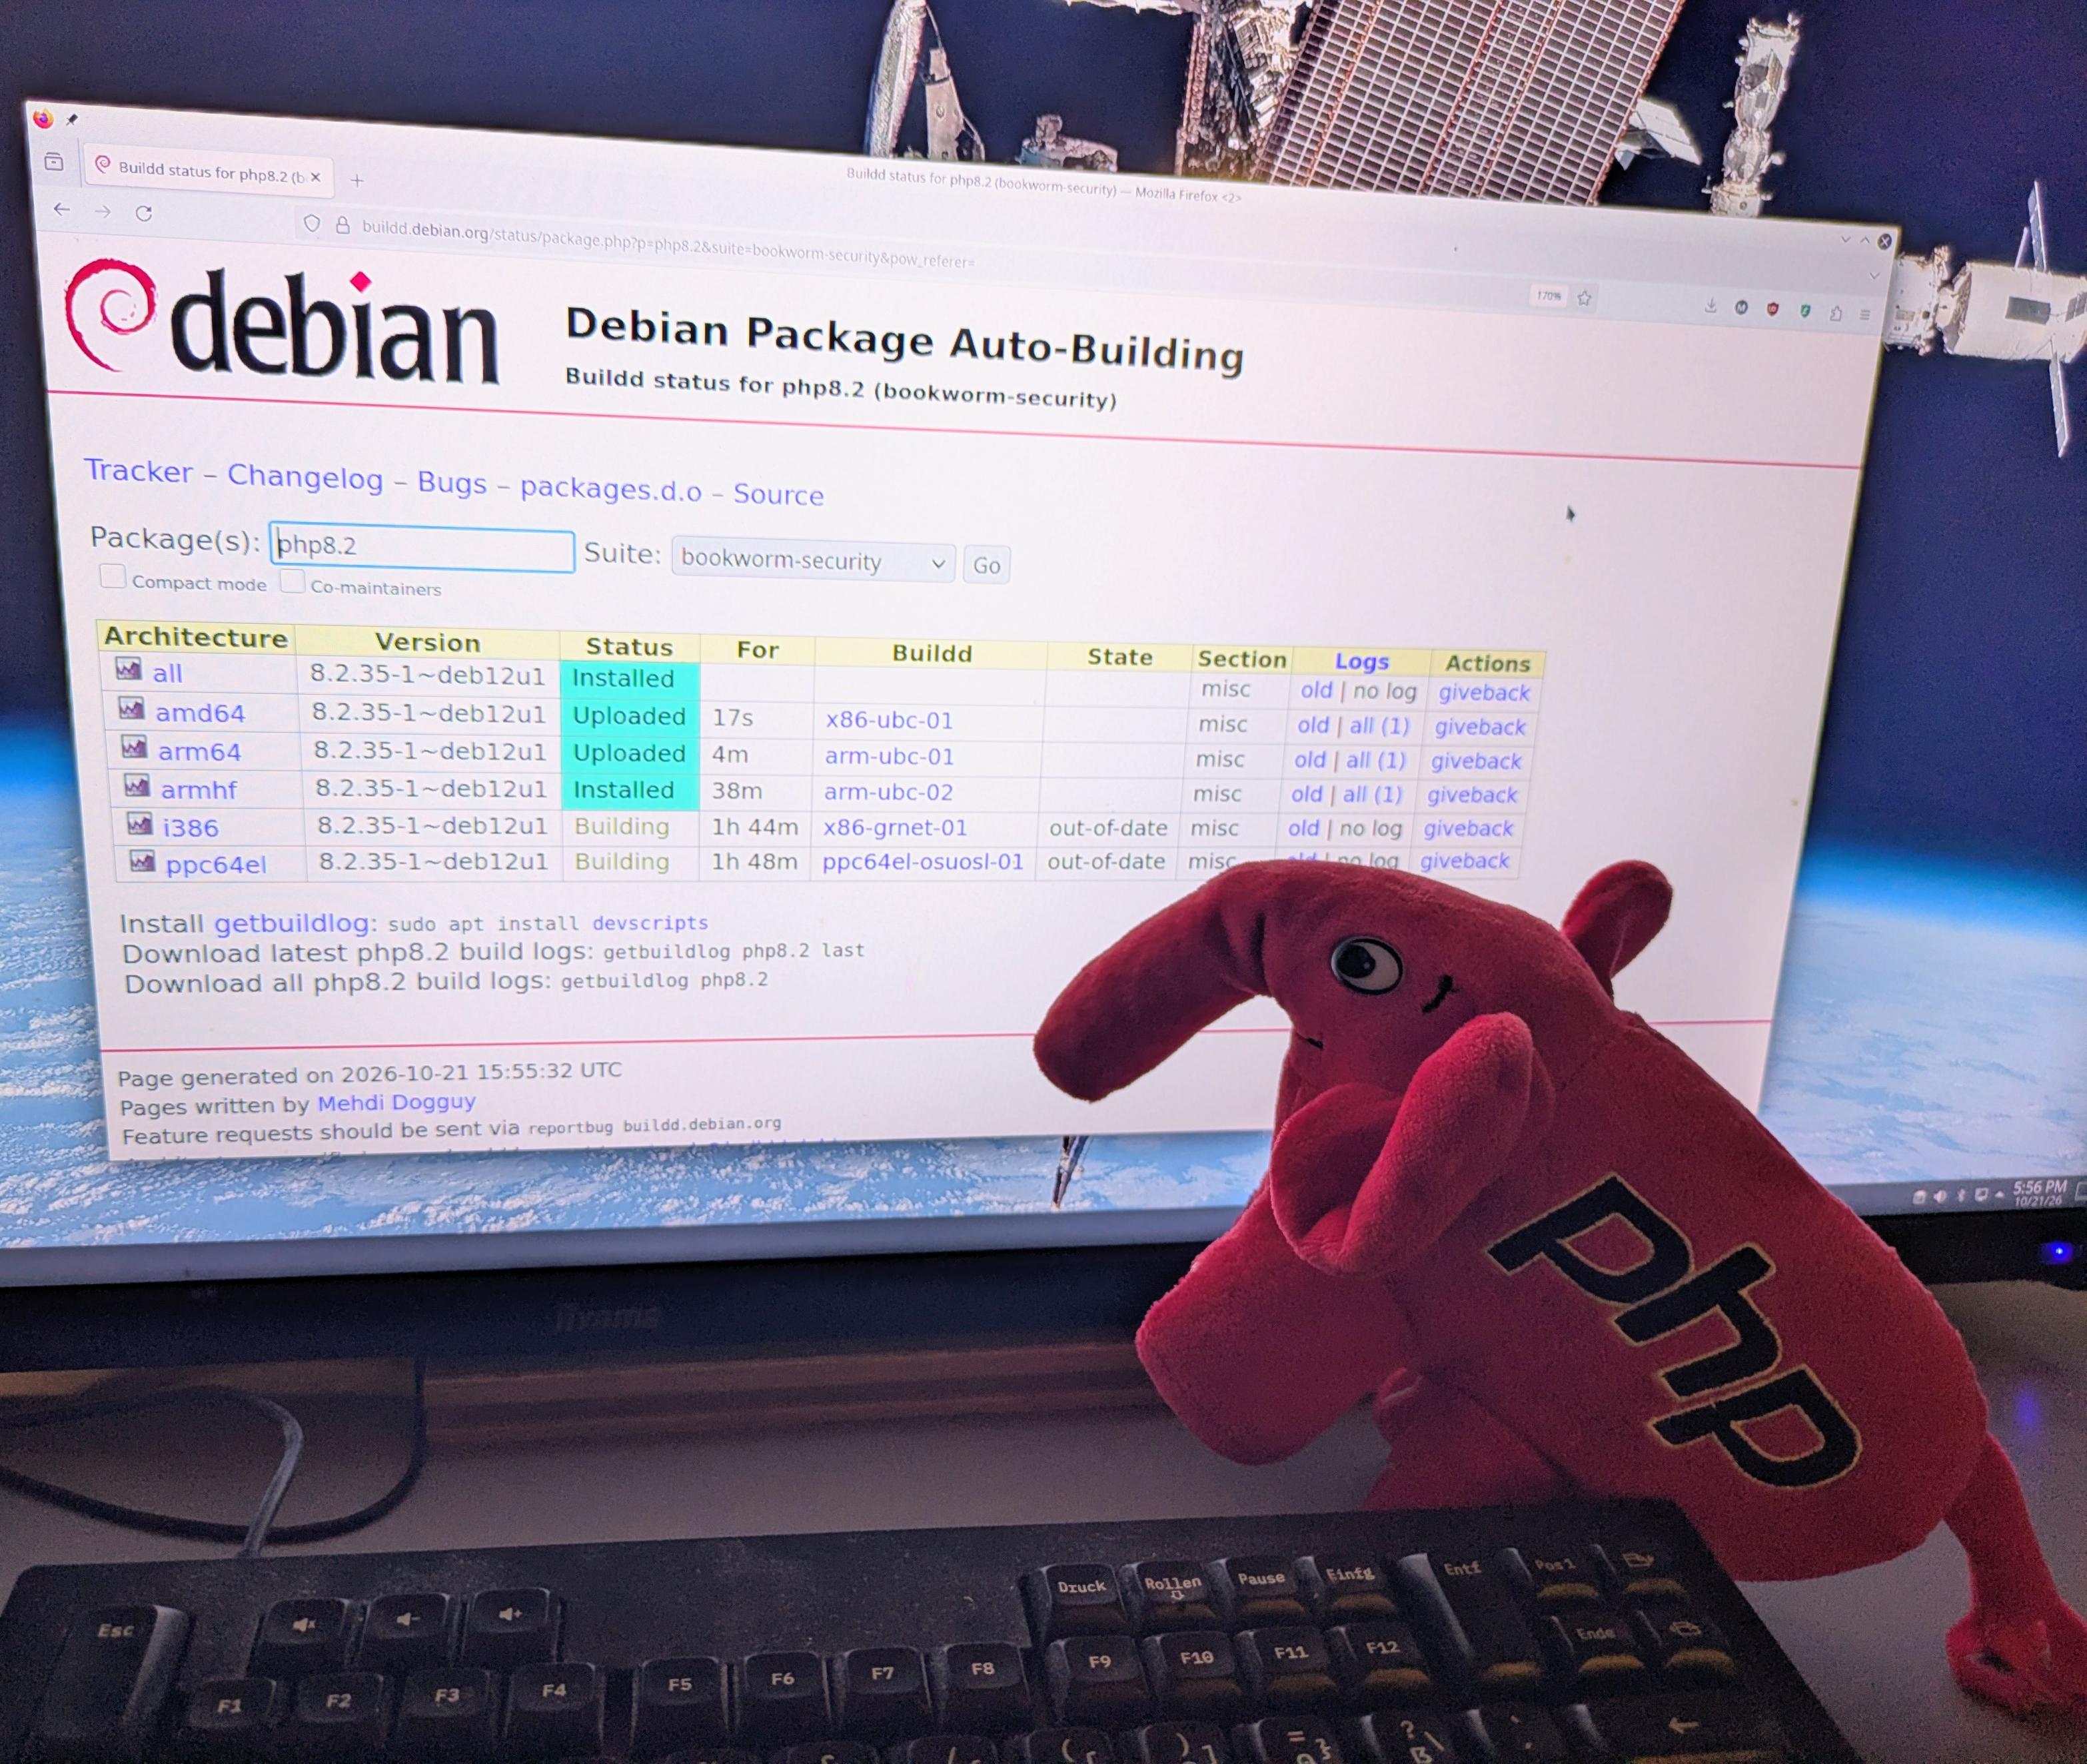
The #Debian Security Team has already released PHP 8.4.27-1~deb13u1 for #Trixie.
Happy host and container patching :)