X XFediYour place in the Fediverse
XFEDI

#php

ActivityPub

Public posts with this hashtag.

↳ In reply to a post

You know things get serious when even the german Tagesschau publishes news on the subject:

https://www.tagesschau.de/wirtschaft/technologie/it-sicherheit-php-luecke-100.html

Meanwhile, the PHP Group published the fixes:
https://github.com/php/php-src/releases/tag/php-8.5.12

#PHP #PHP2Shell #InfoSec #SysAdmin #OpenSource #SelfHosted

tagesschau.deProgrammiersprache PHP: Sicherheitslücke bedroht weltweit WebseitenZahlreiche Webseiten und Onlinedienste weltweit sind derzeit in Gefahr: Grund ist eine Sicherheitslücke in der weitverbreiteten Programmiersprache PHP. Das Gefahrenpotenzial ist demnach extrem hoch.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

We have posted more information about today's security releases, including the sequence of events that led to the discovery, how the PHP security team is improving their processes, and what we need from you to continue this critical work. https://thephp.foundation/blog/2026/10/21/todays-php-security-release-and-how-were-strengthening-php-security/
#php #security

thephp.foundationToday's PHP Security Release, and How We're Strengthening PHP SecurityDescribing the story behind how critical security vulnerabilities were found and fixed.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

🚨 PHP2Shell: Two critical RCE vulnerabilities. Emergency patches released.

CVE-2026-109618 and CVE-2026-109619 are rated CVSS 9.2/10 (CVSS v4.0) and can allow unauthenticated remote code execution against vulnerable PHP installations. The flaws affect PHP's core runtime, not just a particular CMS or plugin.

🔧 Fixed PHP releases:
• PHP 8.5 → 8.5.12
• PHP 8.4 → 8.4.27
• PHP 8.3 → 8.3.36
• PHP 8.2 → 8.2.35

⚠️ Running PHP 8.1 or older? These branches no longer receive regular upstream security updates. PHP has also provided minimal source-level backports for PHP 8.1, 8.0 and 7.4. Check your distribution or hosting provider for patched packages. Otherwise, upgrade to a supported branch, PHP 8.2 or later.

📊 Our analysis of over 7 million PHP websites found that 46.1% of sites disclosing their PHP version run an End-of-Life branch.

This is a serious exposure problem. Updating WordPress, Laravel or another application alone will not fix a vulnerability in the PHP runtime.

✅ Update PHP immediately.
✅ Verify the actual runtime used by PHP-FPM, Apache, CGI or your hosting environment.
✅ Check vendor advisories if your system uses backported security patches.

The PHP security team says there are no complete mitigations. Updating is the only safe choice.

Full technical analysis, vulnerability details and remediation:
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/

#InfoSec #CyberSecurity #PHP #RCE #CVE
❞ Quoted postThe CyberSec Guru

Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps

The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📣 Announcing the immediate availability of:

- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12

‼️ These address the following critical security issues:

- Remote Code Execution via Out of Memory corruption (CVE-2026-109618)
- Remote Code Execution via Stale Global State (CVE-2026-109619)

📝 https://www.php.net/ChangeLog-8.php
🎁 https://www.php.net/downloads?source=Y
:windows8: Windows: https://www.php.net/downloads.php?os=windows

Read more: https://www.php.net/archive/2026.php#2026-10-21-5

#PHP #Release #Security #CVE

www.php.netPHP: PHP 8 ChangeLogPHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

#PHP security advisories with technical details:

https://github.com/php/php-src/security/advisories/GHSA-w8hw-w9fx-j79w

https://github.com/php/php-src/security/advisories/GHSA-6wmf-4rv5-p3rp

GitHubRCE via OOM corruption## Summary PHP uses `longjmp()` for out-of-memory (OOM) errors to exit the current context and abort handling of the request. In some contexts, request memory is temporarily reachable before it ...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

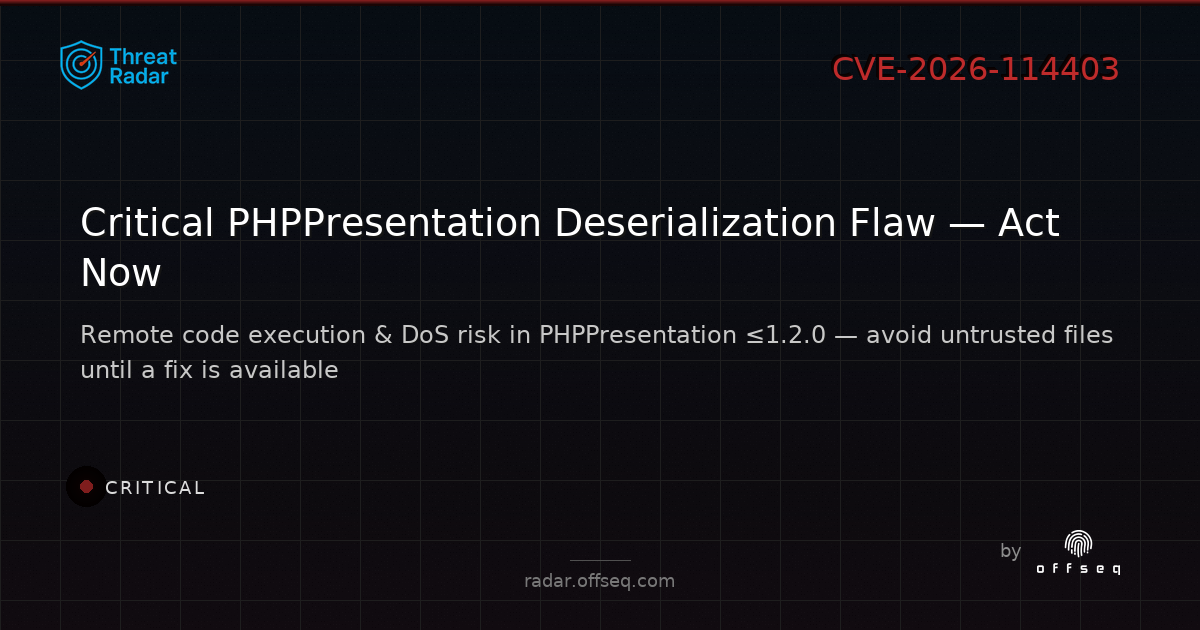
CVE-2026-114403: PHPOffice PHPPresentation ≤1.2.0 faces CRITICAL insecure deserialization (CVSS 9.2). Remote code execution & DoS possible via crafted uploads. No patch; avoid untrusted inputs. Details: https://radar.offseq.com/threat/cve-2026-114403-deserialization-of-untrusted-data-in-phpoffice-phppresentation-21b2eb9e24a6b900 #OffSeq #CVE2026114403 #PHP #AppSec

Critical threat: CVE-2026-114403: Deserialization of Untrusted Data in PHPOffice PHPPresentation
OffSeq Threat RadarCVE-2026-114403: Deserialization of Untrusted Data in… | Threat RadarVulnerability: PHPOffice PHPPresentation through 1.2.0 contains an insecure deserialization vulnerability that allows attackers to instantiate arbitrary PHP…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Happy PHP Wednesday.

"In the last hour, two remote code execution vulnerabilities in PHP have been leaked. These vulnerabilities were previously scheduled under embargo and due for release on Thursday at 11 am ET," watchTowr CEO Benjamin Harris told BleepingComputer.

https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/

#php #vulnerability #patchmanagement #infosec #incidentresponse

BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

I don't think this #PHP issue is related, though I might be wrong. The main issue here seems to be that there are loads of apps using older versions of PHP, which won't be patched because they've passed end of life. And remote code execution is a pretty bad vulnerability.

https://mastodon.xyz/@nextcloud/117478725232757164

❞ Quoted postNextcloud 📱☁️💻

⚠️ We have been informed by CERT of an issue affecting PHP: https://cert.europa.eu/publications/security-advisories/2026-018 https://www.php.net/archive/2026.php#2026-10-20-1 This would affect all online PHP servers and operations including Nextcloud as well as WordPress and othe

MastodonNextcloud 📱☁️💻 (@[email protected])⚠️ We have been informed by CERT of an issue affecting PHP: https://cert.europa.eu/publications/security-advisories/2026-018 https://www.php.net/archive/2026.php#2026-10-20-1 This would affect all online PHP servers and operations including Nextcloud as well as WordPress and other popular services. The CERT recommendation is to turn off servers running PHP based applications until updates to P
↩ Reply ♡ 0 · ↻ 0 ↗ Original