Seems relevant #php #wordpress #hacklu
Public posts with this hashtag.
Seems relevant #php #wordpress #hacklu
it looks like ACSC (cyber.gov.au) turned off all php pages. Which makes sense.
All their advisories require PHP at the presentation layer, which doesnt make sense.
They couldnt add a static page with the relevant information? yes the '/alerts' path is surely a CMS, but the front page is clearly static content. Is "<html>PHP is on fire</html> so hard to add?
#php #php2shell #acsc #australia
Who needs DDoS when gou can release dependency zero days?
So, no matter how bad the PHP fallout proves to be, I have to concede that they *have* cleaned up their act quite a bit in recent years and these sorts of bugs out of PHP are much, much rarer than they used to be
Did you know that, when I was a fiery young programmer in my 20s, I ran a hate blog dedicated to the PHP manual and how bad, unreliable, and unhelpful it was? Here are some highlights:
Special snowflake not-actually-a-function isset() https://phpmanualmasterpieces.tumblr.com/post/52082199266/unsettling
The notorious strcmp() footgun https://phpmanualmasterpieces.tumblr.com/post/44634822304/i-am-so-comically-angry-right-now
When 1 equals 4096 https://phpmanualmasterpieces.tumblr.com/post/33023415508/when-does-one-byte-equal-four-kilobytes
PBKDF API designed to trip you up https://phpmanualmasterpieces.tumblr.com/post/66426423275/i-cant-spell-pbkdf
And, my favorite, a review of the complete original PHP 2.0 manual from the late 90s: https://phpmanualmasterpieces.tumblr.com/post/65544023819/php-20-a-review-in-retrospect
(The picture of Espurr in that post links to a domain that used to play the Lavender Town theme. Please put on Lavender Town yourself for full effect)
All these posts are 12 to 15 years old and do not necessarily reflect the current state of either the documentation or the code. Gods, I hope they don't.
It's my hope that the php2shell debacle will help us consider more carefully when a websites needs to be interactive, and when having a static website is completely reasonable.
There are ways to have the niceties of a CMS and still run a static website.
The simpler a thing is, the less ways it can break down.
On the OWASP slack channel, they say that the exploits they have seen, are hitting several of the CRS rules at PL1. So if you are running modsecurity + Coreruleset, this helps. Also protecting Apparmor with a restrictive Apparmor profile should help a lot, as it will prevent PHP from executing random commands and reading/writing random files.
#php2shell #apparmor #OWASP #modsecurity #CRS #Coreruleset #PHP
Lol.
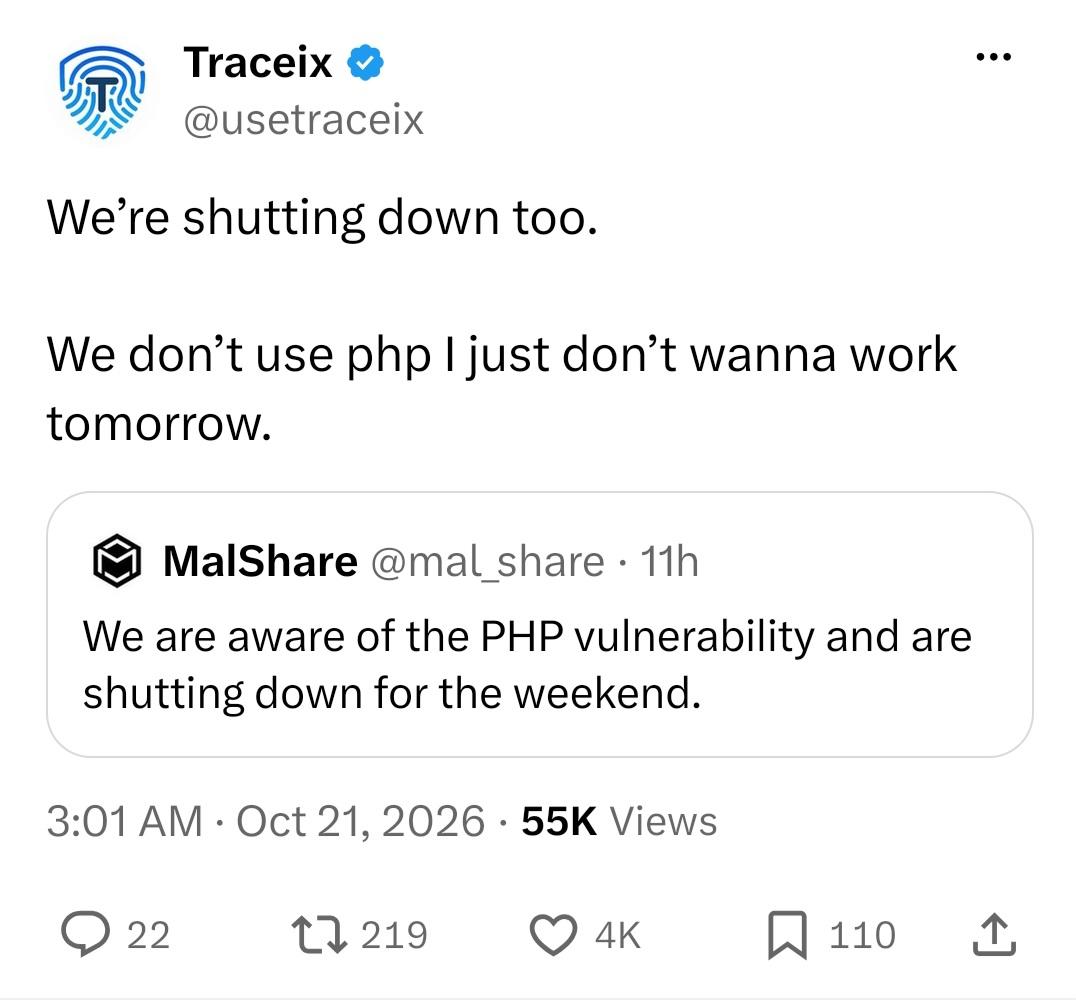
welp, I’ve taken the small number of #wordpress sites I manage for friends offline for a couple of days in anticipation of the impending #PHPocalypse 🤪
tbh I’ve been planning to migrate them from my very shitty old webhost to my hopefully-not-shitty new web host for some time for a bunch™ of reasons but haven't had the spoons so ¯⧹(ツ)⧸¯
the longer-term plan is to replace all but one with static sites & leave one on wordpress for reasons of ease-of-use for the owner 🤷♀️
I always run things pretty locked down regardless of webhost / platform / dynamic or static, but with the old webhost I was stuck on an EOL version of PHP with no way to get onto a supported version without switching to a different hosting plan on a newer shared server (and more 💵💵💵) & doing complete site migrations anyway, so #php2shell is just a convenient excuse to accelerate the process
I really wasn't planning to spend today with my head inside web hosting stuff, but sometimes our priorities get set for us by external events 🙃
for anyone else with internet-facing #PHP assets… 👇
Yet another day, yet another #security #vulnerability , this time it is #php and the fix is not available (yet).
If you want to take your website offline (temporarily of course), until your webhost has patched everything, you could deny access to to your entire website by putting this in your .htaccess :
Order Deny,Allow
Deny from all
ErrorDocument 403 "Temporarily offline"
 Ars TechnicaPHP warns it plans to release 2 emergency patches imminentlyUnconfirmed report claims PHP2Shell exploit remotely executes code on PHP sites.
CVE-2026-109618 & CVE-2026-109619: CRITICAL RCE in PHP (>=5.0.0). Patch lands Oct 21; only PHP 8.x supported. Mass exploitation likely post-release. Prepare to patch ASAP. Details: https://radar.offseq.com/threat/php2shell-mass-exploitation-looms-for-leaked-critical-php-flaws-47d22162f363ef2c #OffSeq #PHP #vuln #RCE
🚨 Critical PHP vulnerabilities 🚨
All PHP based servers - you should VERY SOON (!) update to the version that is released within the next 1-2 hours!
https://www.php.net/archive/2026.php#2026-10-20-1
Do not postpone this, take it very seriously!
 www.php.netPHP: News Archive - 2026PHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
I'm confused #Wikipedia still uses #PHP, right?
They're not taking it down out of precaution? Only a few Wikimedia services?
PHP ships fixes for two leaked critical flaws ("php2shell", CVSS 9.2) at 14:00 UTC today. Affected versions are still unconfirmed by PHP.
Some Japanese services didn't wait: childcare app Codmon stopped everything, website builder Studio froze its editor, Sakura Internet paused some functions. Pausing before a patch is a security decision, not a failure.
https://japancyberwatch.com/articles/php2shell-critical-php-flaws-japan-services-pause-2026
🚨 Critical Alert from Karen IT
Two critical unauthenticated RCE vulnerabilities in PHP (CVE-2026-109618 & CVE-2026-109619, CVSS 9.2) have leaked early.
Do not delay.
🚨 تنبيه حرج
ثغرتان حرجتان في PHP تسمحان بتنفيذ أكواد عن بُعد بدون مصادقة (CVE-2026-109618 و CVE-2026-109619، CVSS 9.2) تم تسريبهما مبكراً.
لا تتأخروا.
 KSRC - Karen IT Security Response CenterBlogKaren IT Security Response Center is part of the defender community and on the front line of security response evolution.
Tired of security bugs? 😞
Try podcast hosting without #PHP 😀
Or ask for a test account: [email protected]
Features:
* Import of existing podcasts
* Always up to date analytics
* Episode scheduling
* Web-player and subscribe-button
* Multi-tenant: host as many podcasts as you want
* Custom domain
* Transcripts and chapters
 Pods-BlitzPods-BlitzFree and easy podcast hosting for everyone
🚨 Critical Alert from Karen IT
Two critical unauthenticated RCE vulnerabilities in PHP (CVE-2026-109618 & CVE-2026-109619, CVSS 9.2) have leaked early.
Do not delay.
🚨 تنبيه حرج
ثغرتان حرجتان في PHP تسمحان بتنفيذ أكواد عن بُعد بدون مصادقة (CVE-2026-109618 و CVE-2026-109619، CVSS 9.2) تم تسريبهما مبكراً.
لا تتأخروا.
KSRC - Karen IT Security Response CenterBlogKaren IT Security Response Center is part of the defender community and on the front line of security response evolution.
just woke up.
🥱
good morning #php
If you rely on the volunteer maintained rpms.remirepo.net we urge you to move to distro packages or building from source now, so you can immediately apply updates. The repo will not have updates today.
🚨 PHP2Shell: CRITICAL PHP RCE ALERT
Two vulnerabilities. CVE-2026-109618 & CVE-2026-109619. CVSS 9.2.
PHP powers WordPress, Magento and millions of websites. This is a reminder that patching your CMS isn't enough when the vulnerability lives in the PHP runtime itself.
⚠️ Check your PHP version. Prepare to patch. Don't rely on WordPress auto-updates.
Technical breakdown, exposure, detection & mitigation 👇
https://thecybersecguru.com/advisory/php2shell-cve-2026-109618-109619-php-rce/
Content warning: PHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
 The CyberSec GuruPHP2Shell: Critical PHP RCE Flaws CVE-2026-109618 & CVE-2026-109619 | The CyberSec GuruPHP2Shell exposes two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619. Learn the risks, affected versions, mitigations and patching steps
I figure I'd better put my #dokuwiki pages into maintenance mode until the PHP thing is fixed.
Oh, OK. The docuwiki forum pages are all down. I suspect they are doing the same thing.
I don't like waking up to a possible internet collapse...
There seems to be two critical RCE vulnerabilities discovered in PHP.
If you are using HortusFox, please make sure it's not accessible from the public Internet. I will monitor the situation and see if I have to take any action when the security patches are live.
Ars TechnicaPHP warns it plans to release 2 emergency patches imminentlyUnconfirmed report claims PHP2Shell exploit remotely executes code on PHP sites.
Alle Leute mit #PHP im Einsatz haben heute einen Spaßtag
I've seen some disgusting rhetoric from some holier than thou IT people this morning on the #php security issue. None of who actually know what the problem is!
Comments like "swap to an alternative" are NOT helpful. Because moving everything to a different platform is so easy for everyone!
PHP is a good and accessible language that still runs a large chunk of the internet. Still pays my bills.
I can't remember the last major PHP security issue. Must have been at least 10 years now.
It’s not a vulnerability, it’s added involuntary functionality.
Is there a hashtag for that #PHP remote code execution bug yet? Looks like we‘re going to get lot of these because of #AI #infosec research. That‘s not a bad thing in first place, because secure software is good software. But as long as these serious bugs are coming I tend to hide my service behind a VPN very soon.
www.php.netPHPPHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
🤖 Two critical PHP vulns (CVSS v4.0 9.2), RCE according to watchTowr, get an out-of-cycle release today at 14:00 UTC. Fixes only for 8.2–8.5; 8.1/8.0/7.x/5.x are EOL and get no vendor patch. No exploitation reported yet.
🔗 https://news-web.php.net/php.announce/509
#CVE #CyberSec #PHP #RCE
Goodnight #php don't do anything while I'm asleep please.