CVE-2026-114108: CRITICAL vuln in HKUDS Vibe-Trading ≤0.1.6 – missing auth enables root shell commands, script uploads, session leaks. Set API_AUTH_KEY & restrict API access now. Patch unconfirmed. https://radar.offseq.com/threat/cve-2026-114108-missing-authentication-for-critical-function-in-hkuds-vibe-trading-dbf2add5e4f70bbe #OffSeq #vulnerability #infosec #HKUDS
#vulnerability
Public posts with this hashtag.
The PHP team issued an urgent advisory for critical PHP vulnerabilities CVE-2026-109618 and 109619, threatening millions of exposed web servers.
php2shell
php2shell
php2shell
#cybersecurity #infosec #vulnerability #vulnerabilityalert #php #php2shell
BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
It is Tuesday afternoon, and if you are in charge of a patching cycle, you are likely staring at a list of CVEs that feels less like a security roadmap and more like a grocery list for a disaster.
New Cisco advisory addresses a medium-level August vulnerability:
Cisco Unified Intelligence Center SQL Injection Vulnerability https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-cuic-sql-inject-2qbfWSm5 @TalosSecurity #Cisco #infosec #vulnerability
This isn't remotely funny. The research was posted yesterday:
Pillar Security: Open and Shut: Remote Code Execution in opencode via MCP OAuth https://www.pillar.security/blog/open-and-shut-remote-code-execution-in-opencode-via-mcp-oauth
More:
Infosecurity-Magazine: Researchers Warn OpenCode Quietly Patched Critical RCE Flaw, Leaving Users At Risk https://www.infosecurity-magazine.com/news/opencode-quietly-patched-critical/ #infosec #vulnerability #bots #GitHub
www.pillar.securityOpen and Shut: Remote Code Execution in opencode via MCP OAuthPillar Security found a critical remote code execution flaw in opencode on Windows and WSL. A remote MCP server could run code on your machine during the OAuth handshake. Affected 1.0.137 to 1.18.32, fixed in 1.18.33, no CVE issued.
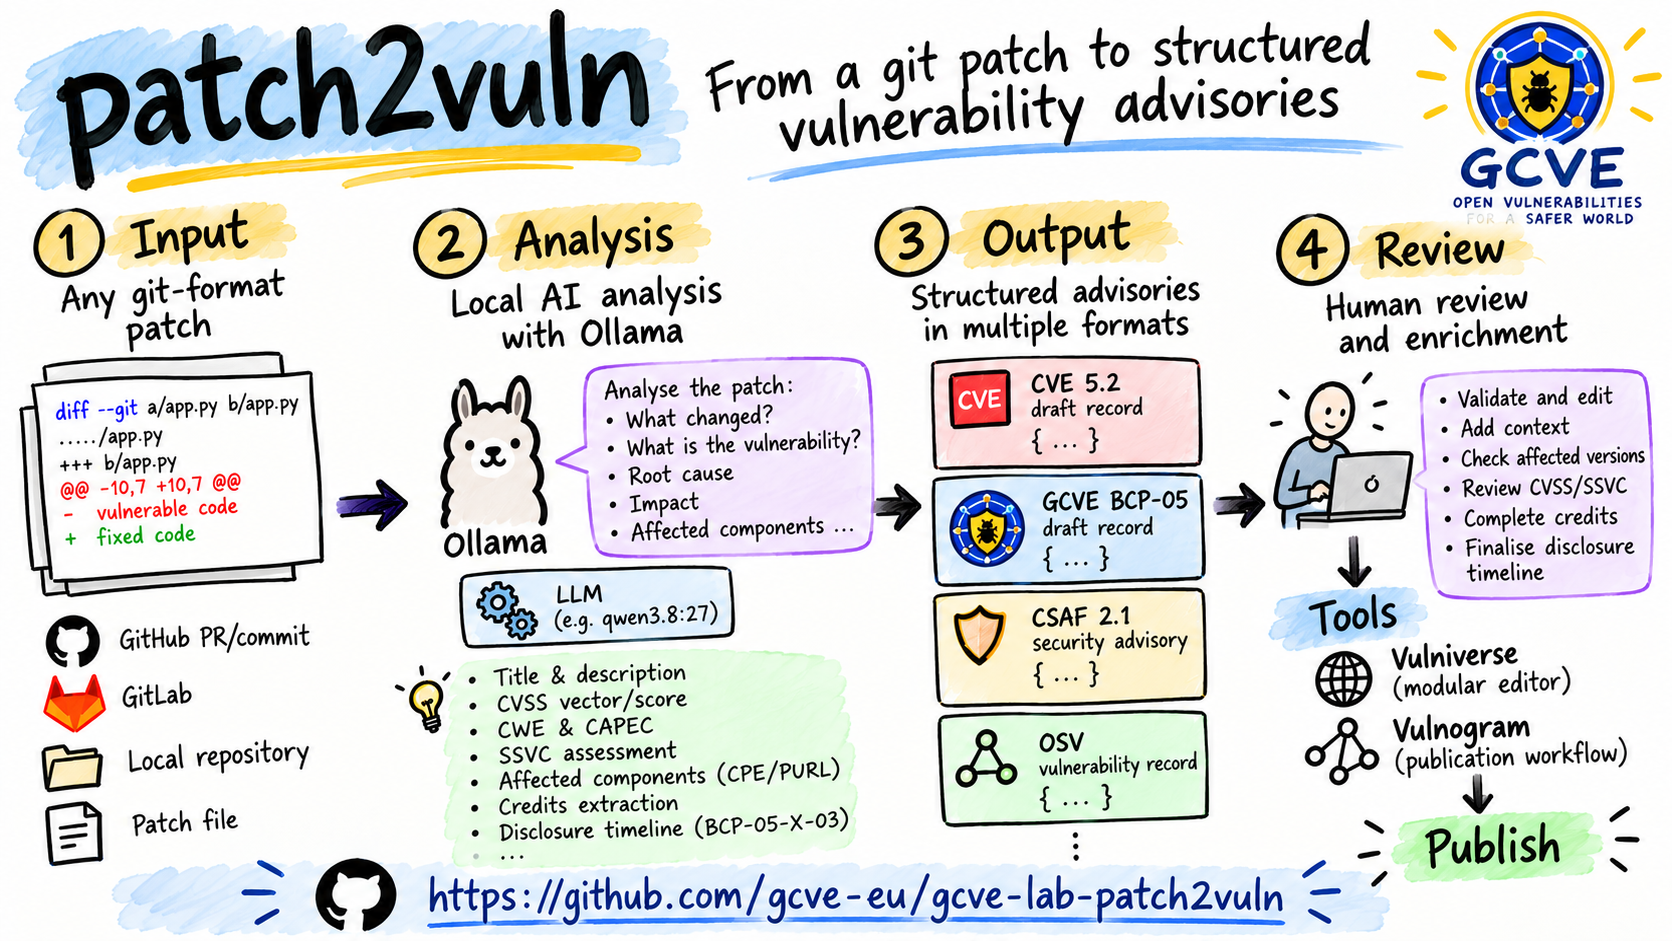
I presented at the lighting talk of @hack_lu the patch2vuln is a command-line tool that turns a git-format patch into a structured draft vulnerability advisory using a locally hosted Ollama model.
🔗 GitHub https://github.com/gcve-eu/gcve-lab-patch2vuln
#cve #gcve #vulnerability #cvd #vulnerabilityManagement #opensource #ai
CVE-2026-43845: Advantech ADAM-3600 has a critical password reset flaw (CVSS 9.2) enabling network-based auth bypass. No patch or known exploits yet. Restrict access, monitor activity. https://radar.offseq.com/threat/cve-2026-43845-vulnerability-in-advantech-adam-3600-332b402f61c80bb0 #OffSeq #ICS #Infosec #Vulnerability
F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws
F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L
BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
One of your employees likely has a Plex media server shoved under a desk or hidden in a closet. They probably set it up so the office could share movies and music without paying for ten different streaming services.
Discover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
#PwnEscape #LinuxKernel #Vulnerability #CloudSecurity #CyberSecurity
https://dailytechnow.com/critical-pwnescape-flaw-linux-virtual-machines/
Daily Tech NowCritical PwnEscape Flaw Found in Linux Virtual MachinesDiscover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
CVE-2026-112371: CRITICAL code injection in H3C Magic NX15 (CVSS 9.4). Public exploit allows remote code execution via /api/esps. No patch yet — restrict device access. Details: https://radar.offseq.com/threat/cve-2026-112371-code-injection-in-h3c-magic-nx15-047130e6380b2198 #OffSeq #H3C #infosec #vulnerability
New.
Rapid7: Authentication Bypass, Remote Code Execution, and Database Read in Eptura Archibus (FIXED) https://www.rapid7.com/blog/post/ve-authentication-bypass-remote-code-execution-and-database-read-in-eptura-archibus-fixed/ @Rapid7Official #infosec #vulnerability #threatresearch
Rapid7Rapid7While performing continuous red teaming exercises through Rapid7’s Vector Command service, Rapid7 discovered three new vulnerabilities in Eptura Archibus. A legacy API endpoint could be exploited to bypass authentication and run various functions without authentication (CVSS: 8.6 High). The most serious functions allow for full database read (CVSS: 8.5 High) and an insecure file upload (CVSS: 9.6