X XFediYour place in the Fediverse
XFEDI

#vulnerability

ActivityPub

Public posts with this hashtag.

Stop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.

https://theperimetersite.com/report/387

#vulnerability #healthcare #infosec

The Perimeter SiteYour Patching Schedule is a Work of Fiction — The Perimeter SiteStop staring at your dashboard trying to tell yourself your patching cadence is optimal. It isn't. Most companies treat their vulnerability lists like restaurant menus.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The latest Node.js security update addresses over ten vulnerabilities across 26.x, 24.x, and 22.x series, including four high-severity execution flaws.

#NodeJS #CyberSecurity #JavaScript #Vulnerability #TechNews

https://dailytechnow.com/node-js-security-update-flaws/

Daily Tech NowNode.js Security Update Fixes Critical FlawsThe latest Node.js security update addresses over ten vulnerabilities across 26.x, 24.x, and 22.x series, including four high-severity execution flaws.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Security Advisory: CVE-2025-71438 - Out-of-Bounds Read in GPAC/MP4Box

Processing a crafted AC-4 stream with an invalid `frame_rate_index` triggers an out-of-bounds read in `gf_odf_ac4_cfg_dsi_v1`, causing MP4Box to crash.

Summary:
The `gf_odf_ac4_cfg_dsi_v1` function in `odf/descriptors.c` uses a stream-supplied `frame_rate_index` to index into fixed-size lookup tables (`AC4_SAMPLE_DELTA_TABLE_48`, `AC4_MEDIA_TIMESCALE_48`). The function does not validate that the index is within bounds before performing the table lookup. A crafted AC-4 file carrying an out-of-range index (e.g., 15) causes an out-of-bounds read, ultimately resulting in a NULL dereference and process crash.

CWE:
CWE-125 - Out-of-bounds Read

Affected Component:
```
odf/descriptors.c:2179
Function: gf_odf_ac4_cfg_dsi_v1()
```

Affected Product:
MP4Box (GPAC Multimedia Open Source Project)

Affected Version:
2.5-DEV-rev1617-g856674b22-master; commit `856674b226d6cbe28a941ad223be38194cbf7d37`. Any codebase equivalent to this commit that has not applied the fix commit is affected.

Attack Conditions:
An attacker supplies a specially crafted AC-4 stream file containing an invalid `frame_rate_index` value. Local access is required; the victim must invoke `MP4Box -dash 100 <crafted_file>` or any equivalent DASH segmentation command that triggers the AC-4 configuration descriptor parsing path.

Impact:
The out-of-bounds read leads to an immediate process crash (SEGV READ at address 0x000000000000), resulting in Denial of Service. No evidence of arbitrary code execution was observed.

Fix / mitigation status:
The issue was fixed in GPAC commit:
```
13eb5b76560aaf7813b865a2ad433258478e2695
```
Users should update to a GPAC build containing this commit or later.

References:

- Issue: https://github.com/gpac/gpac/issues/3303
- PoC: https://github.com/sigdevel/pocs/blob/main/res/gpac/MP4Box/50/50_gf_odf_ac4_cfg_dsi_v1_odf_descriptors_c_2179
- Fix: https://github.com/gpac/gpac/commit/13eb5b76560aaf7813b865a2ad433258478e2695

Credit
Alexander A. Shvedov (@sigdevel)

#fuzzing #infosec #security #afl++ #revers #cybersecurity #bugbounty #vulnerability #opensource #linux #cve #advisory #gpac

GitHub[security] odf/descriptors.c:2179 out-of-bounds read in gf_odf_ac4_cfg_dsi_v1 · Issue #3303 · gpac/gpacodf/descriptors.c:2179 out-of-bounds read in gf_odf_ac4_cfg_dsi_v1 Description: When processing ac-4 streams with invalid frame rate indices, the code fails to validate "frame_rate_index" before ac...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Cisco fixed 34 CRITICAL vulns across Expressway, IOS XR, Snort 3 & Unified Comms 🚨 Risks: RCE as root, auth bypass, DoS. No active exploitation. Update to latest versions for protection. Details: https://radar.offseq.com/threat/cisco-patches-34-vulnerabilities-across-multiple-products-6b2acce3408b2ab2 #OffSeq #Cisco #Vulnerability #PatchManagement

Critical threat: Cisco Patches 34 Vulnerabilities Across Multiple Products
OffSeq Threat RadarCisco Patches 34 Vulnerabilities Across Multiple Products | Threat RadarCisco released patches addressing 34 vulnerabilities across multiple products including Expressway Series, IOS XR, Snort 3, and Unified Communications. The…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

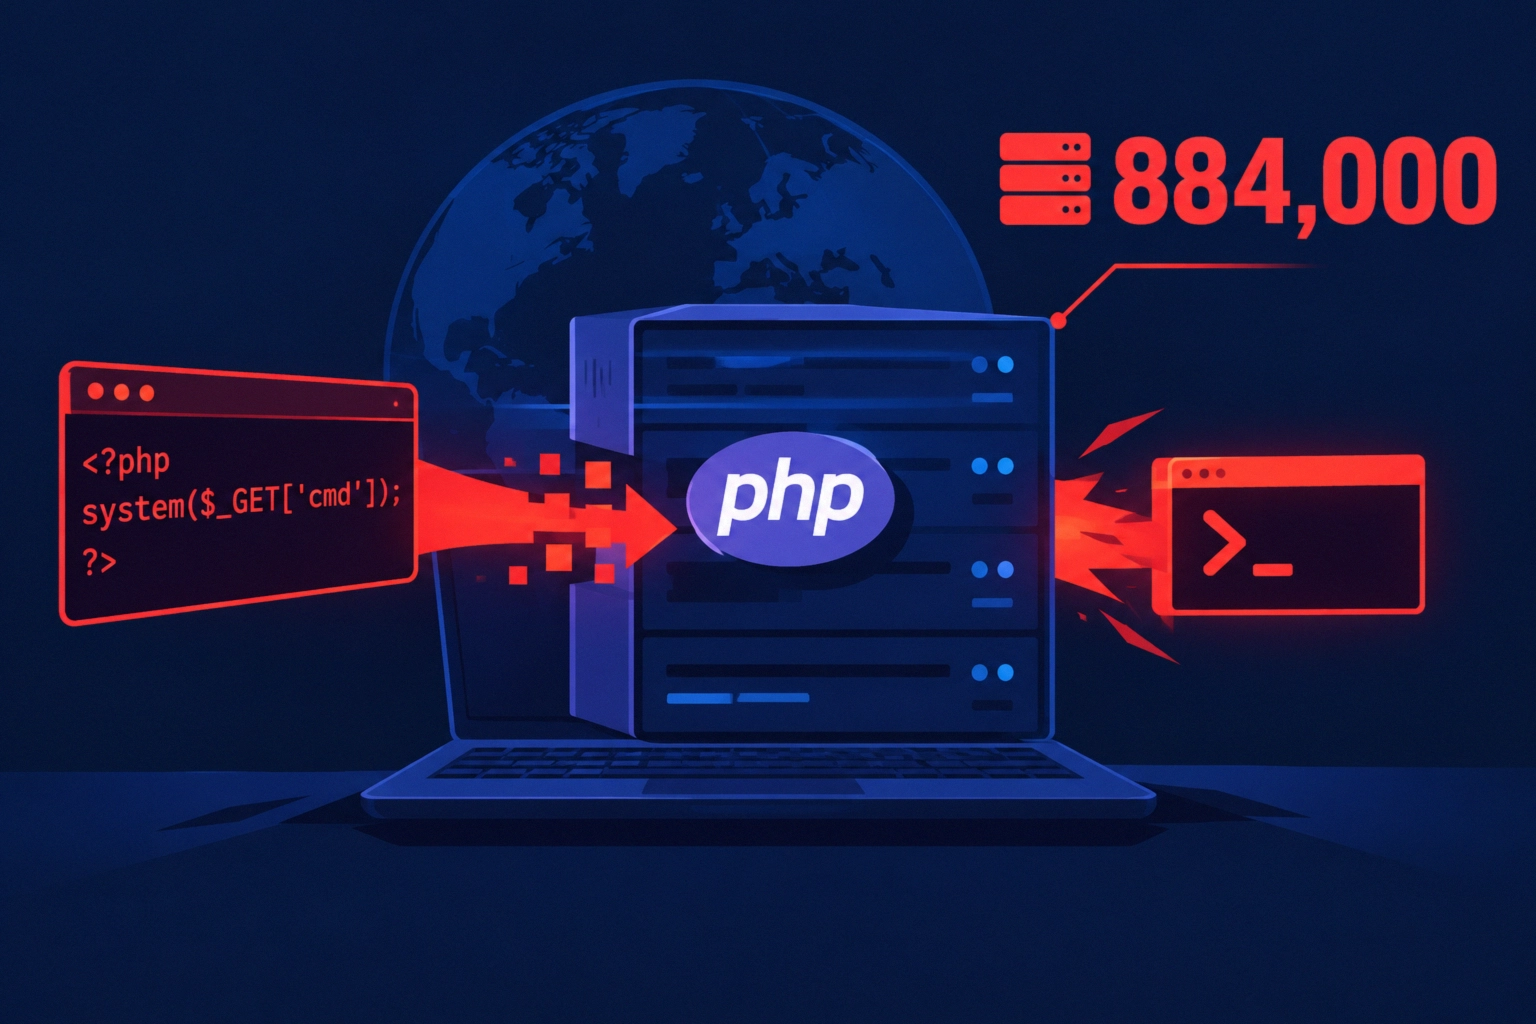
Critical PHP RCE vulnerabilities: emergency patch and 884,000 unprotected hosts

🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-emergency-patch

#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #critical #PHP #vulnerability

CyberSecureFoxCritical PHP RCE Vulnerabilities: Emergency Patch And 884,000 Unprotected HostsThe PHP security team has announced two critical vulnerabilities with a CVSS v4.0 score of 9.2 and scheduled an out-of-band security release for 21 October
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NT OneAPP (≤1.5.22) by NewType Infortech has a CRITICAL hard-coded credentials flaw (CVE-2026-114219, CVSS 9.1). Attackers can decrypt login data & access user creds. No patch yet — restrict access & monitor closely. https://radar.offseq.com/threat/cve-2026-114219-cwe-798-use-of-hard-coded-credentials-in-newtype-infortech-nt-oneapp-d8766d50ef7b2f82 #OffSeq #CVE #infosec #vulnerability

Critical threat: CVE-2026-114219: CWE-798 Use of Hard-coded Credentials in NewType Infortech NT OneAPP
OffSeq Threat RadarCVE-2026-114219: CWE-798 Use of Hard-coded Credentials in… | Threat RadarNT OneAPP by NewType Infortech contains a hard-coded credentials vulnerability (CWE-798) that allows unauthenticated remote attackers to obtain a hard-coded…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-114727 (HIGH): Roundcube Webmail <1.6.20/1.7.5 allows SVG/EPS uploads, risking remote code execution via ImageMagick. Upgrade to 1.6.20+ or 1.7.5+ to mitigate. Details: https://radar.offseq.com/threat/cve-2026-114727-cwe-829-inclusion-of-functionality-from-untrusted-control-sphere-in-roundcube-webmail-0e067a7fe4b46d68 #OffSeq #Vulnerability #Infosec #Roundcube

High threat: CVE-2026-114727: CWE-829 Inclusion of Functionality from Untrusted Control Sphere in Roundcube Webma
OffSeq Threat RadarCVE-2026-114727: CWE-829 Inclusion of Functionality from… | Threat RadarCVE-2026-114727 is a high-severity vulnerability in Roundcube Webmail before versions 1.6.20 and 1.7.5. The issue involves unsafe handling of SVG and EPS image…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Technology is currently the primary target for attackers, ranking first out of thirteen sectors this week with 252 stories hitting the wire.

https://theperimetersite.com/report/385

#vulnerability #infosec

The Perimeter SiteThe technology sector remains the top target — The Perimeter SiteTechnology is currently the primary target for attackers, ranking first out of thirteen sectors this week with 252 stories hitting the wire.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Here we go again.

Gitlab Releases fix for CVSS 10.0 vulnerability.

https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/

Have we had enough of Cybersecurity Awareness month yet?

#gitlab #vulnerability

GitLab DocsGitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 | GitLab DocsLearn more about GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13 for GitLab Community Edition (CE) and Enterprise Edition (EE).
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New Dell update for a June vulnerability affecting the Linux kernel and multiple CVEs:

Dell: Security Update for Dell VxRail for Multiple Third-Party Component Vulnerabilities https://www.dell.com/support/kbdoc/en-us/000473635/dsa-2026-245-security-update-for-dell-vxrail-for-multiple-third-party-component-vulnerabilities #Dell #Linux #vulnerability #infosec

www.dell.comDSA-2026-245: Security Update for Dell VxRail for Multiple Third-Party Component Vulnerabilities | Dell USDell VxRail remediation is available for multiple security vulnerabilities that could be exploited by malicious users to compromise the affected system.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

Palo Alto: CVE-2026-109618 Impact of Critical Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Palo Alto Networks Products https://security.paloaltonetworks.com/CVE-2026-109618 #infosec #PHP #vulnerability

@mttaggart

Palo Alto Networks Product Security AssuranceCVE-2026-109618 Impact of Critical Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Palo Alto Networks ProductsPalo Alto Networks is aware of two critical vulnerabilities in PHP: CVE-2026-109618 and CVE-2026-109619. CVE-2026-109618 involves a remote code execution vulnerability where handling out-of-memory er...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New advisory from Fortinet for a medium-severity bug:

CVE-2025-66178: FortiWeb improper neutralization of special elements used in an OS command vulnerability https://app.opencve.io/cve/CVE-2025-66178

Yesterday:

CRITICAL: CVE-2026-106173: improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiSIEM 7.5.0 https://app.opencve.io/cve/CVE-2026-106173 #Fortinet #infosec #vulnerability

app.opencve.ioCVE-2025-66178 - Vulnerability Details - OpenCVEA improper neutralization of special elements used in an os command ('os command injection') vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.2, FortiWeb 7.6.0 through 7.6.6, FortiWeb 7.4.0 through 7.4.11, FortiWeb 7.2.0 through 7.2.12, FortiWeb 7.0.0 through 7.0.12 may allow an authenticated attacked to execute arbitrary commands via a specialy crafted HTTP request.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New.

Very reassuring: "Notable among the observed TTPs is the exploitation of vulnerabilities in network devices such as FortiGate Firewalls and Palo Alto GlobalProtect to gain initial access."

"Group-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data."

Group-IB: Stray Cat, Open Doors: How k0t Wanders Through the Network Edge https://www.group-ib.com/blog/stray-cat-network-edge/ #infosec #vulnerability #Fortinet #cybercrime #threatintel #threatintelligence

Group-IBStray Cat, Open Doors: How k0t Wanders Through the Network EdgeGroup-IB and NyxLab expose threat actor k0t's large-scale campaign exploiting FortiGate, FortiWeb, and Palo Alto GlobalProtect edge devices to harvest credentials, establish persistent access and exfiltrate data
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Register: PHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatched https://www.theregister.com/security/2026/10/21/php-devs-publish-critical-bug-fix-as-site-owners-warned-pull-em-offline-if-youre-unpatched/5304519 @theregister #PHP #infosec #vulnerability

theregisterPHP devs publish critical bug fix as site owners warned: Pull 'em offline if you're unpatchedWebsites down as precaution as exploits have already been published
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The path to happiness and posterity runs through PHP. Here is some of the research dealing with that today - so far.

KrebsonSecurity: Widespread PHP Flaw May Cause Many Site Outages Today https://krebsonsecurity.com/2026/10/widespread-php-flaw-may-cause-many-site-outages-today/ @briankrebs

Akamai: Critical Remote Code Execution Vulnerabilities in PHP Core https://www.akamai.com/blog/security-research/critical-remote-code-execution-vulnerabilities-php-core

Cisco: Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers https://blog.talosintelligence.com/parasitizing-trust-how-legitimate-infrastructure-becomes-a-delivery-pipeline-for-attackers/ @TalosSecurity

CrowdStrike: Two critical memory-corruption RCE vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 have been disclosed in core PHP https://www.crowdstrike.com/en-us/blog/crowdstrike-protects-customers-from-php-rce-zero-days/

Kaspersky: Critical RCE vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) https://securelist.com/tr/php2shell-critical-vulnerabilities-in-php/121596/ @Kaspersky

Sophos: Proof-of-concept exploit released for PHP vulnerabilities (CVE-2026-109618, CVE-2026-109619) https://www.sophos.com/en-us/blog/proof-of-concept-exploit-released-for-php-vulnerabilities-109618-109619

Palo Alto: Millions of PHP Instances Exposed - What Organizations Need To Do Right Now https://www.paloaltonetworks.com/blog/2026/10/millions-of-php-instances-exposed-what-organizations-need-to-do-right-now/

VulnCheck: PHP2Shell Vulnerabilities: CVE-2026-109618 and CVE-2026-109619 https://www.vulncheck.com/blog/php2shell-vulnerabilities @vulncheck #infosec #vulnerability #threatresearch

krebsonsecurity.comWidespread PHP Flaw May Cause Many Site Outages Today – Krebs on Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

About that PHP flaw ... the race to own has begun.

"Security company Wiz, which is owned by Google, claimed its researchers discovered the vulnerabilities in PHP partially using AI tools, while OpenAI and security firm Calif also say they independently discovered the issues and worked together."

Wired: ‘This Is Not a Drill’: Critical PHP Vulnerabilities Are Setting the Internet on Fire https://www.wired.com/story/this-is-not-a-drill-2-php-vulnerabilities-are-setting-the-internet-on-fire/ @WIRED #infosec #vulnerability #PHP

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Happy PHP Wednesday.

"In the last hour, two remote code execution vulnerabilities in PHP have been leaked. These vulnerabilities were previously scheduled under embargo and due for release on Thursday at 11 am ET," watchTowr CEO Benjamin Harris told BleepingComputer.

https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/

#php #vulnerability #patchmanagement #infosec #incidentresponse

BleepingComputerPHP warns admins of two critical flaws, emergency patches coming tomorrowThe PHP security team is warning administrators to prepare for emergency security updates tomorrow to address two critical vulnerabilities, as information about the flaws has reportedly leaked ahead of their scheduled disclosure.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Anomaly Silently Patches Critical RCE in OpenCode AI Agent

Anomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.

**If you use OpenCode on Windows or WSL, upgrade to version 1.18.33 or later immediately, because a malicious or hijacked MCP server can take over your machine and everything on it (code, SSH keys, cloud tokens). Until you can update, remove any remote MCP servers you don't fully trust from your OpenCode configuration, and check your developers' machines yourself, since security scanners won't flag this one.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/anomaly-silently-patches-critical-rce-in-opencode-ai-agent-k-u-t-k-o/gD2P6Ple2L

BeyondMachinesAnomaly Silently Patches Critical RCE in OpenCode AI AgentAnomaly silently patched a critical remote code execution vulnerability in its OpenCode AI agent that allowed malicious servers to hijack developer machines via PowerShell command injection. The flaw affects Windows and WSL users and was fixed in version 1.18.33 without a formal CVE or security advisory.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Yet another day, yet another #security #vulnerability , this time it is #php and the fix is not available (yet).

https://arstechnica.com/security/2026/10/php-maintainers-tell-web-devs-to-prepare-themselves-for-critical-security-patches/

If you want to take your website offline (temporarily of course), until your webhost has patched everything, you could deny access to to your entire website by putting this in your .htaccess :

Order Deny,Allow
Deny from all
ErrorDocument 403 "Temporarily offline"

Ars TechnicaPHP warns it plans to release 2 emergency patches imminentlyUnconfirmed report claims PHP2Shell exploit remotely executes code on PHP sites.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨 Critical PHP vulnerabilities 🚨

All PHP based servers - you should VERY SOON (!) update to the version that is released within the next 1-2 hours!

https://www.php.net/archive/2026.php#2026-10-20-1

Do not postpone this, take it very seriously!

#php #security #vulnerability

www.php.netPHP: News Archive - 2026PHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PHP Issues Emergency Warning for Critical Remote Code Execution Vulnerabilities

PHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.

**If you run any website or app built on PHP (WordPress, online shops, internal tools), install the emergency security updates as soon as they're released today at 14:00 UTC. Until you've patched, restrict access to internal PHP systems and admin pages to trusted networks only, and monitor your servers closely for unusual logins, new files or strange activity.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/php-issues-emergency-warning-for-critical-remote-code-execution-vulnerabilities-y-t-1-8-c/gD2P6Ple2L

BeyondMachinesPHP Issues Emergency Warning for Critical Remote Code Execution VulnerabilitiesPHP is releasing emergency patches for two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619). The release follows a data leak that forced the development team to move the disclosure date earlier to limit exploitation.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Listen, kid. When you see a report from the FBI saying a group like SafePay is "among the most active" with over 600 victims since 2024, don't go hunting for a hooded figure in a dark room.

https://theperimetersite.com/report/382

#vulnerability #phishing #infosec

The Perimeter SiteThe reality of the SafePay operation — The Perimeter SiteListen, kid. When you see a report from the FBI saying a group like SafePay is "among the most active" with over 600 victims since 2024, don't go hunting for a hooded figure in a…
↩ Reply ♡ 0 · ↻ 0 ↗ Original