RE: https://infosec.exchange/@yossarian/117480316228420260
so cool that we're now 72+ hours (more if you include the revocation window) into the biggest CA compromise incident ever and Apple still hasn't fixed this
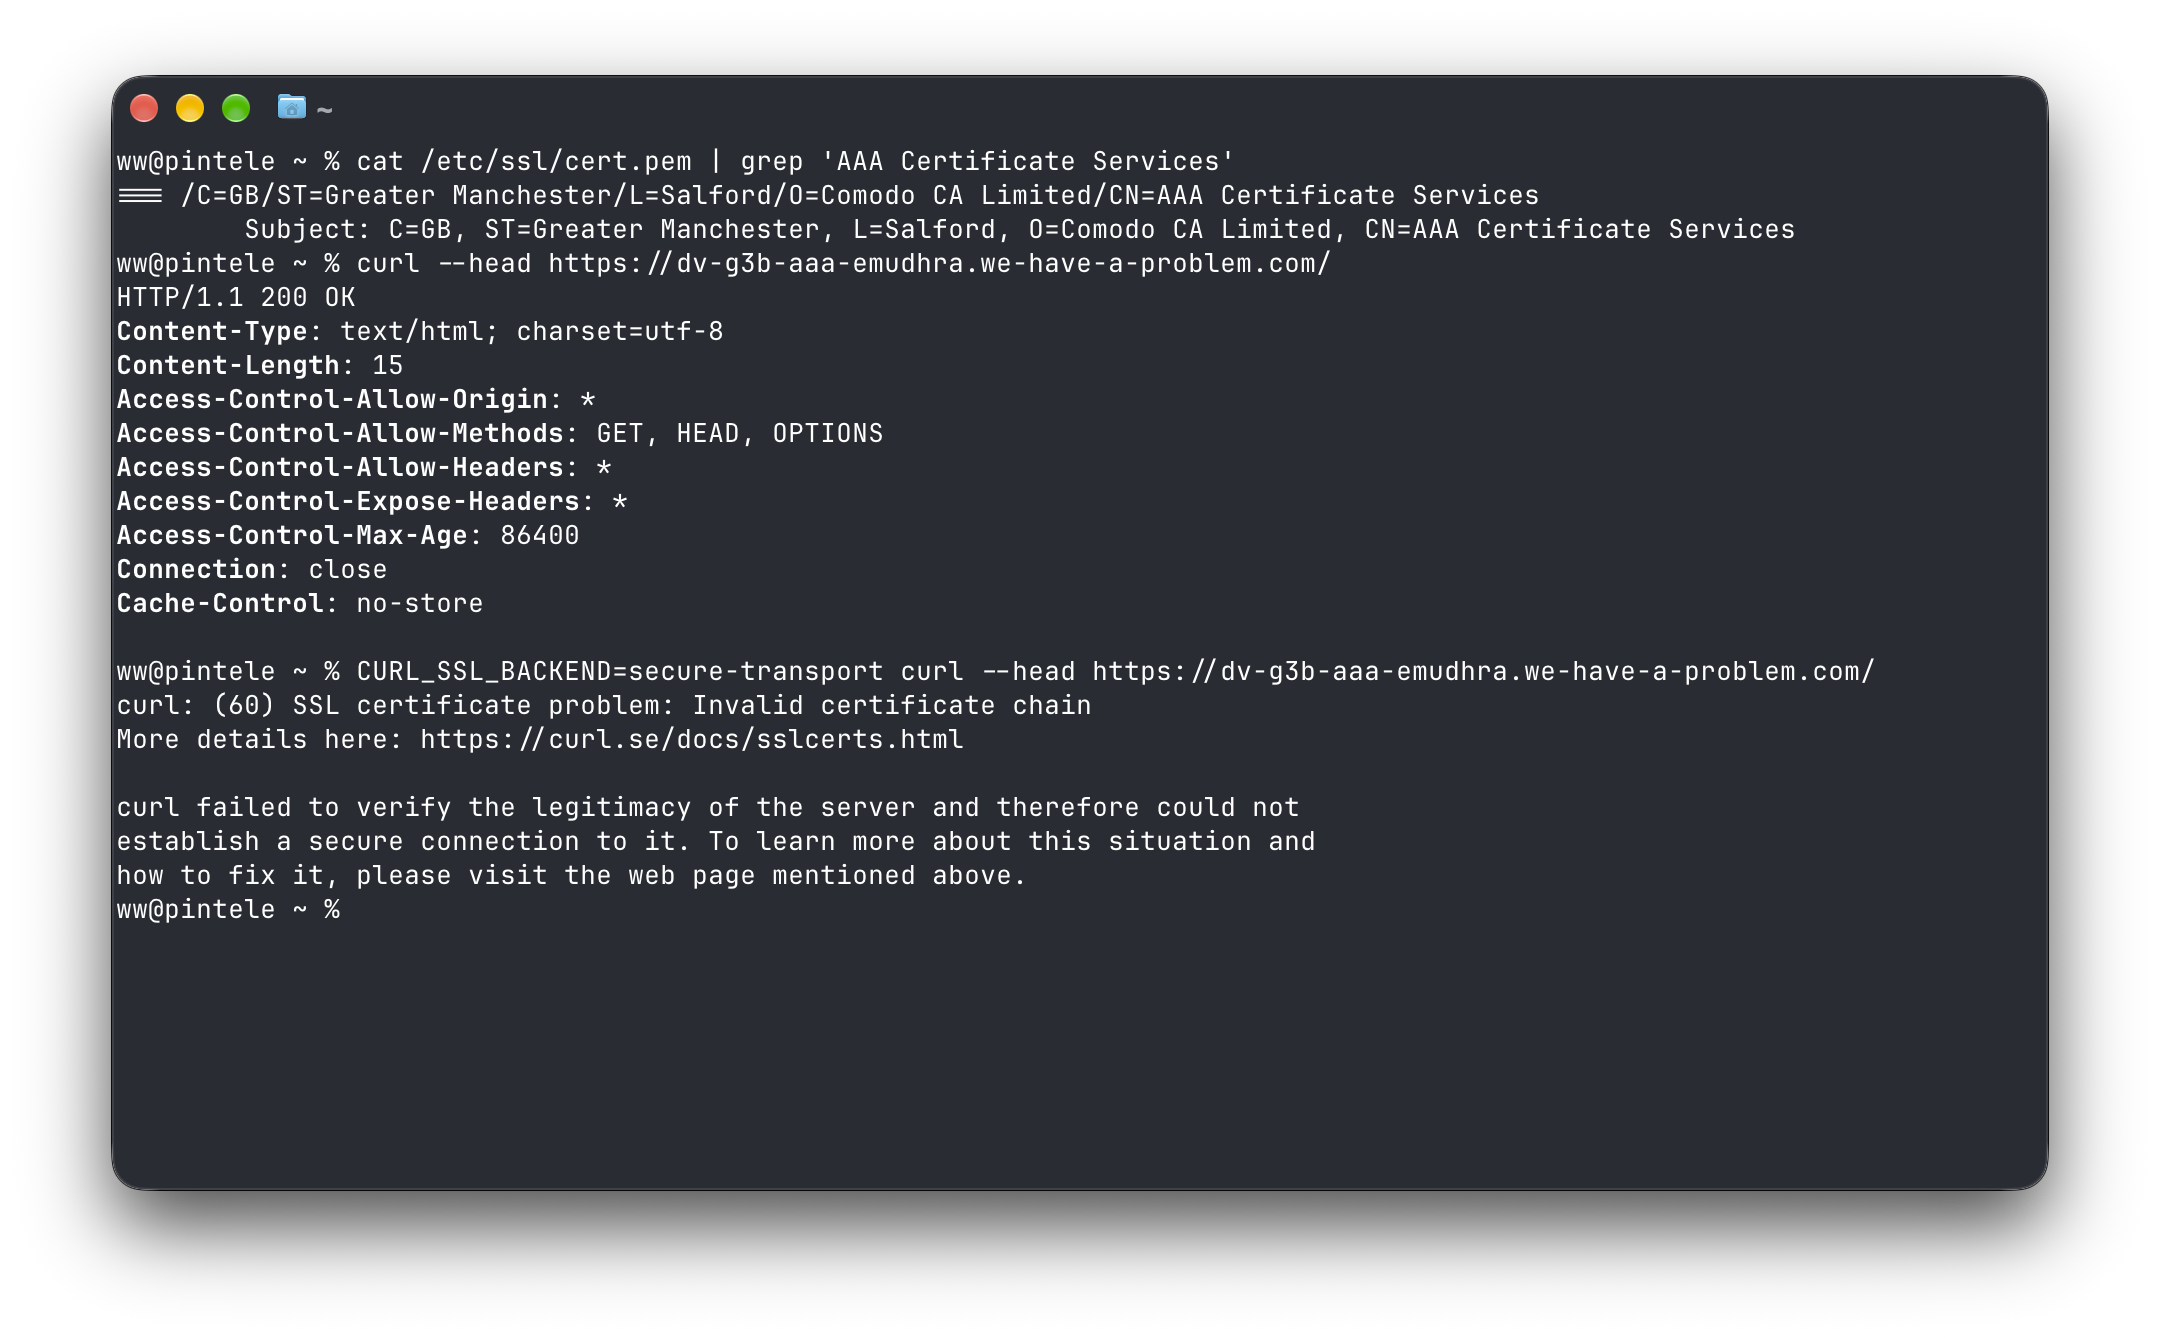
Apple appears to have rolled the eMudra distrust into their native root program, but **not** into `/etc/ssl/cert.pem`, meaning that macOS supplied tools like `curl` and the system Python are still affected by the compromised intermediates. setting `CURL_SSL_BACKEND=secure-transpo
 Infosec Exchangeyossarian (@[email protected])Attached: 1 image
Apple appears to have rolled the eMudra distrust into their native root program, but **not** into `/etc/ssl/cert.pem`, meaning that macOS supplied tools like `curl` and the system Python are still affected by the compromised intermediates.
setting `CURL_SSL_BACKEND=secure-transport` redirects the system curl to the platform verifier, but it's not great that every macOS host is