X XFediYour place in the Fediverse
XFEDI

#CyberSecurity

ActivityPub

Public posts with this hashtag.

The Aoki infostealer now targets AI coding assistant credentials: .claude.json, Codex configs, Copilot, Cursor, and Gemini tokens, plus AWS keys. Stealer logs are traded within hours.

Rotate your keys, set billing alerts, and check whether your credentials are already out there.

https://blog.relayshield.net/your-ai-coding-credentials-are-now-infostealer-targets

#CyberSecurity #ThreatIntel #InfoSec #Malware #AI

blog.relayshield.netYour AI Coding Credentials Are Now Infostealer Targets | RelayShieldThere's a new item on the infostealer shopping list. It's not your bank password. It's your Claude API key. Symantec's Threat Hunter team reported on October 15 that the newest Aoki...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vRolxFAW7hyzfBrqjLicr37CaJihNGZ0r-rAqdHi98FAi1N9sEk0uARbExM-_b77QgVlcphzXXU6qb5/pub?start=false&loop=false&delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad766133b775000091c1a83
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI spending shifts beyond IT, testing CIO-CFO decision rights

💡 Corporate AI spending has doubled to 3.3% of revenue, but 80% sits outside traditional IT budgets. CIOs, CFOs, and business leaders must collaborate through formal councils with clear accountability: business leaders own outcomes, CFOs manage finances, CIOs oversee tech. Unified governance and transparency are essential for maximizing AI's business impact.

https://www.techtarget.com/it-strategy/news/366651960/AI-spending-shifts-beyond-IT-testing-CIO-CFO-decision-rights

#InfoSec #CyberSecurity #AI

IT StrategyAI spending shifts beyond IT, testing CIO-CFO decision rights | TechTargetWith 80% of AI spending outside IT, CIOs and CFOs are redefining who controls architecture, capital allocation and accountability for value.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

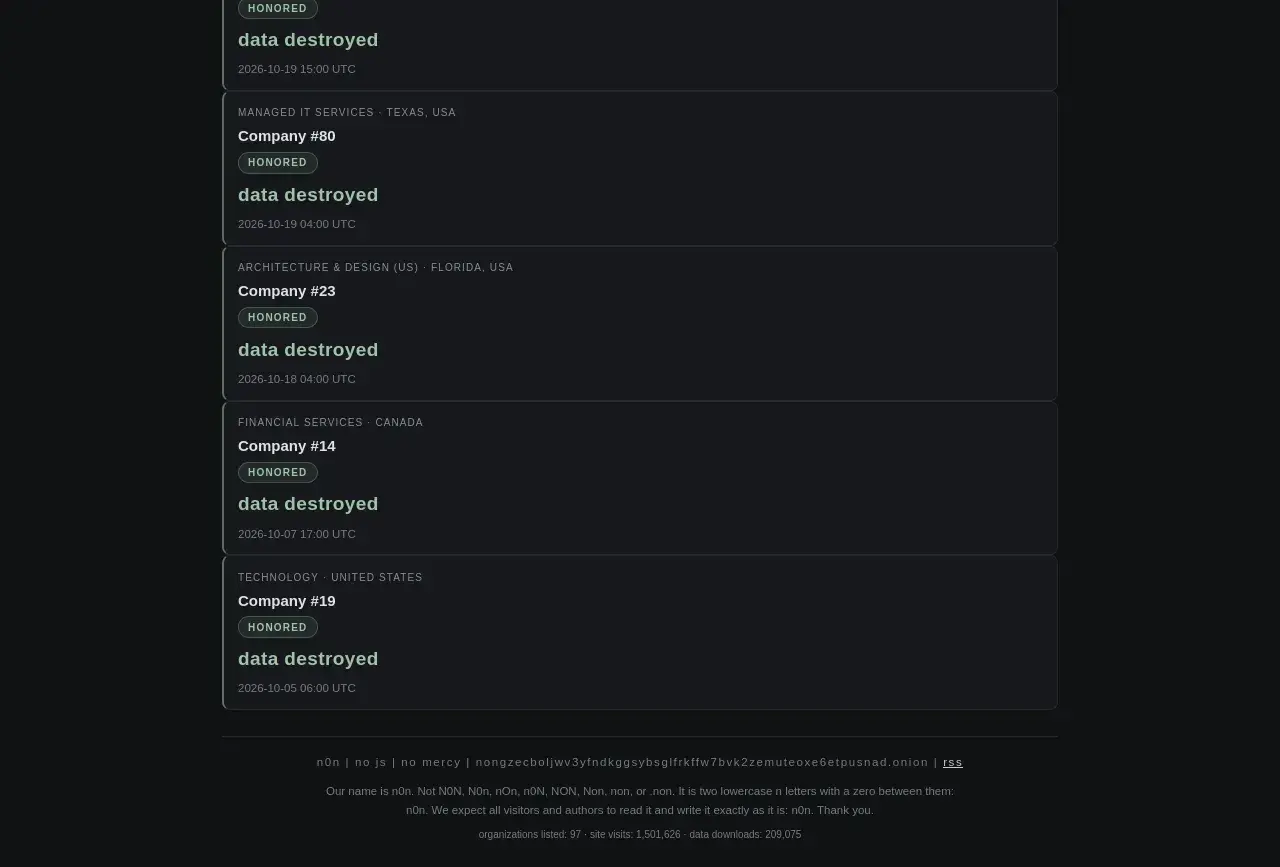
🚨New ransom group blog post!🚨

Group name: N0n
Post title: 51Ridge (Newark NJ hosting/IT)
Organization: 51Ridge
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/51Ridge%20%28Newark%20NJ%20hosting%2FIT%29

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New and free: the Community Bank & Credit Union Cyber Defense Kit, from The Value Chain Risk Institute.

Bank-grade security from free and open-source tools, a tool mapped to every one of the 18 CIS Controls, and a free CAT-style maturity view now that the FFIEC CAT is retired.

Built for the threats that actually hit small FIs: business email compromise, wire fraud, ransomware.

https://valuechainrisk.org/starter/banks/ #CommunityBanking #Cybersecurity

Value Chain Risk InstituteCommunity Bank & Credit Union Cyber Defense KitBank-grade security for a small institution with no security budget, built from free tools and mapped to every CIS Control.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-106173 is a critical path traversal flaw in Fortinet FortiSIEM. An unauthenticated attacker can write files and run code through its gRPC service.

FortiSIEM 7.5.0 is affected; 7.6 and Cloud are not. A public exploit is circulating per Horizon3.

Upgrade to FortiSIEM 7.5.1 or later.

https://fortiguard.fortinet.com/psirt/FG-IR-26-180

#Detection #infosec #cybersecurity

FortiGuard LabsPSIRT | FortiGuard LabsNone
↩ Reply ♡ 0 · ↻ 0 ↗ Original

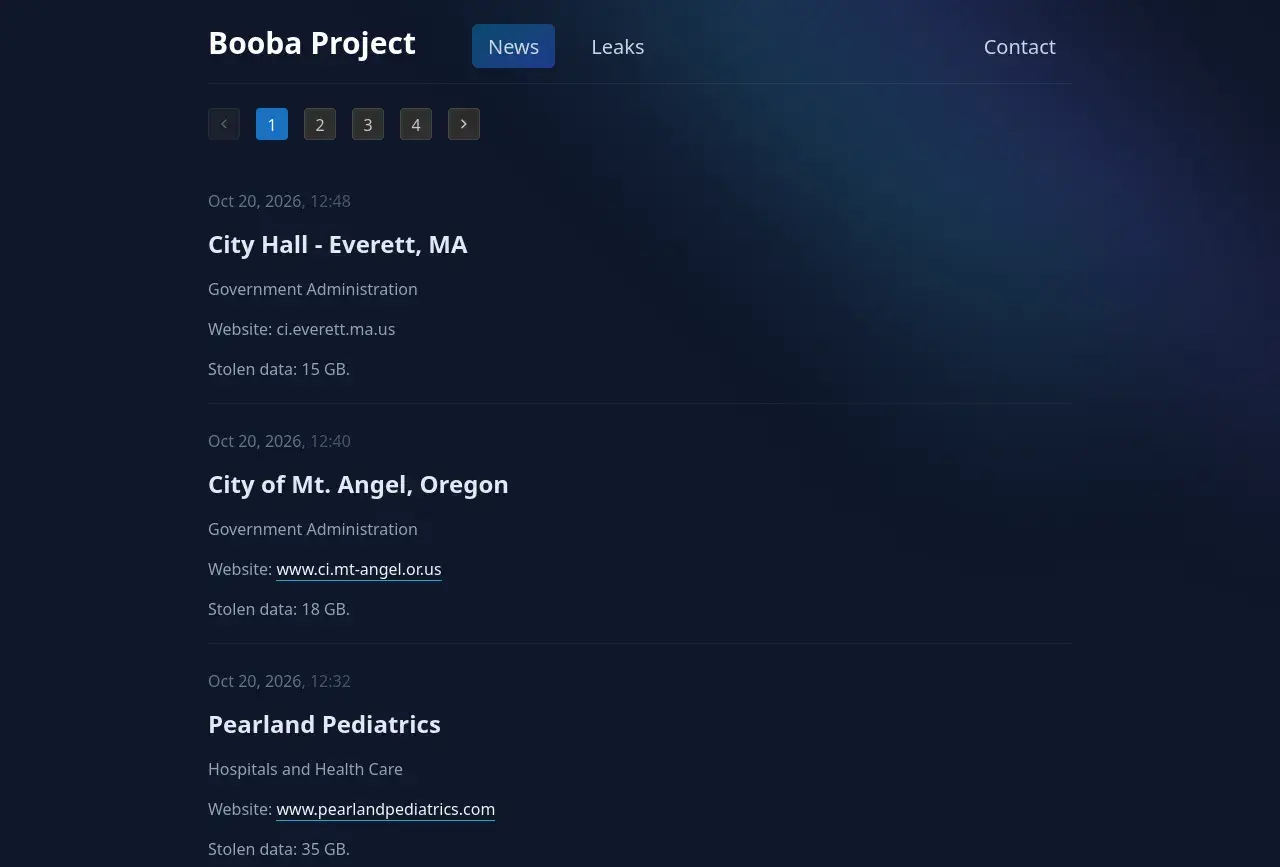
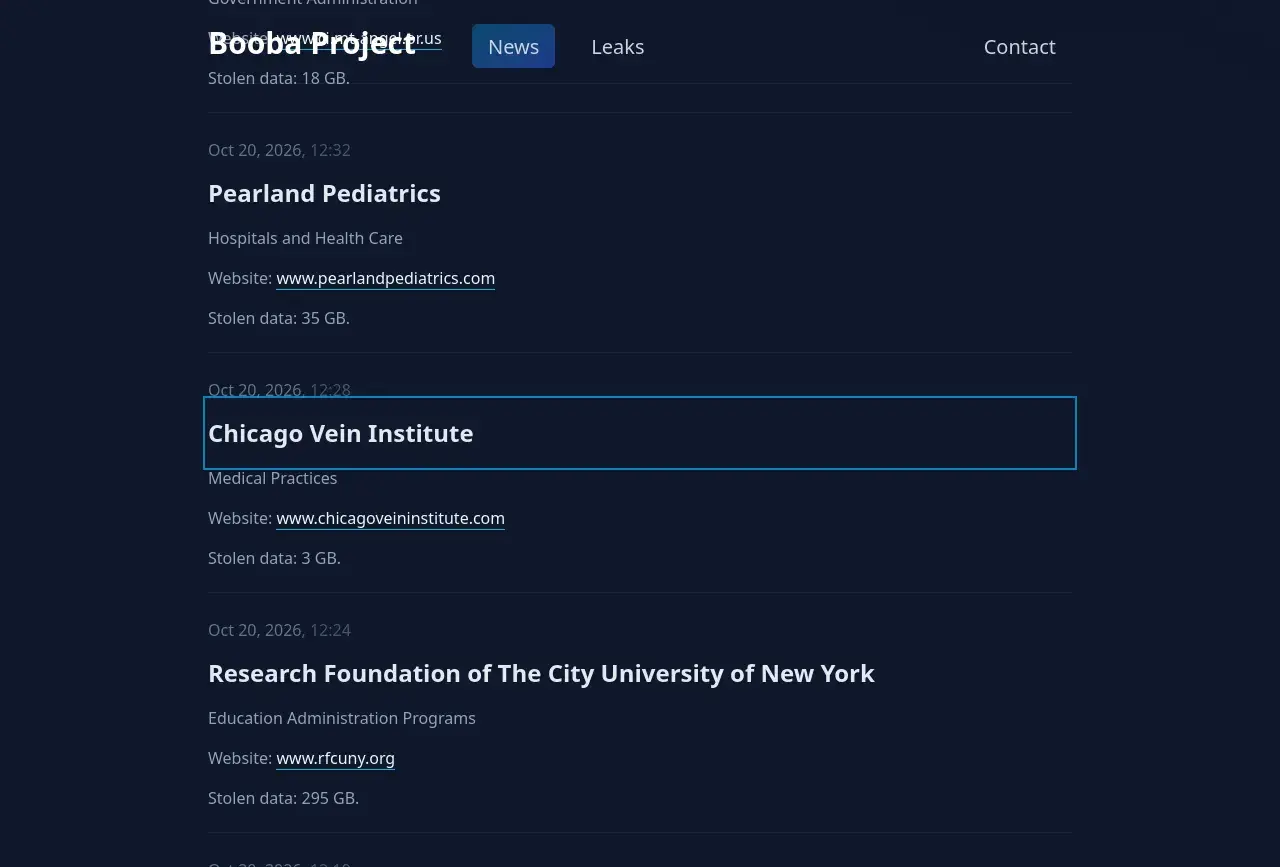
🚨New ransom group blog posts!🚨

Group name: Booba Project
Post title: City Hall - Everett, MA
Organization: Everett City Hall
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20Hall%20-%20Everett%2C%20MA

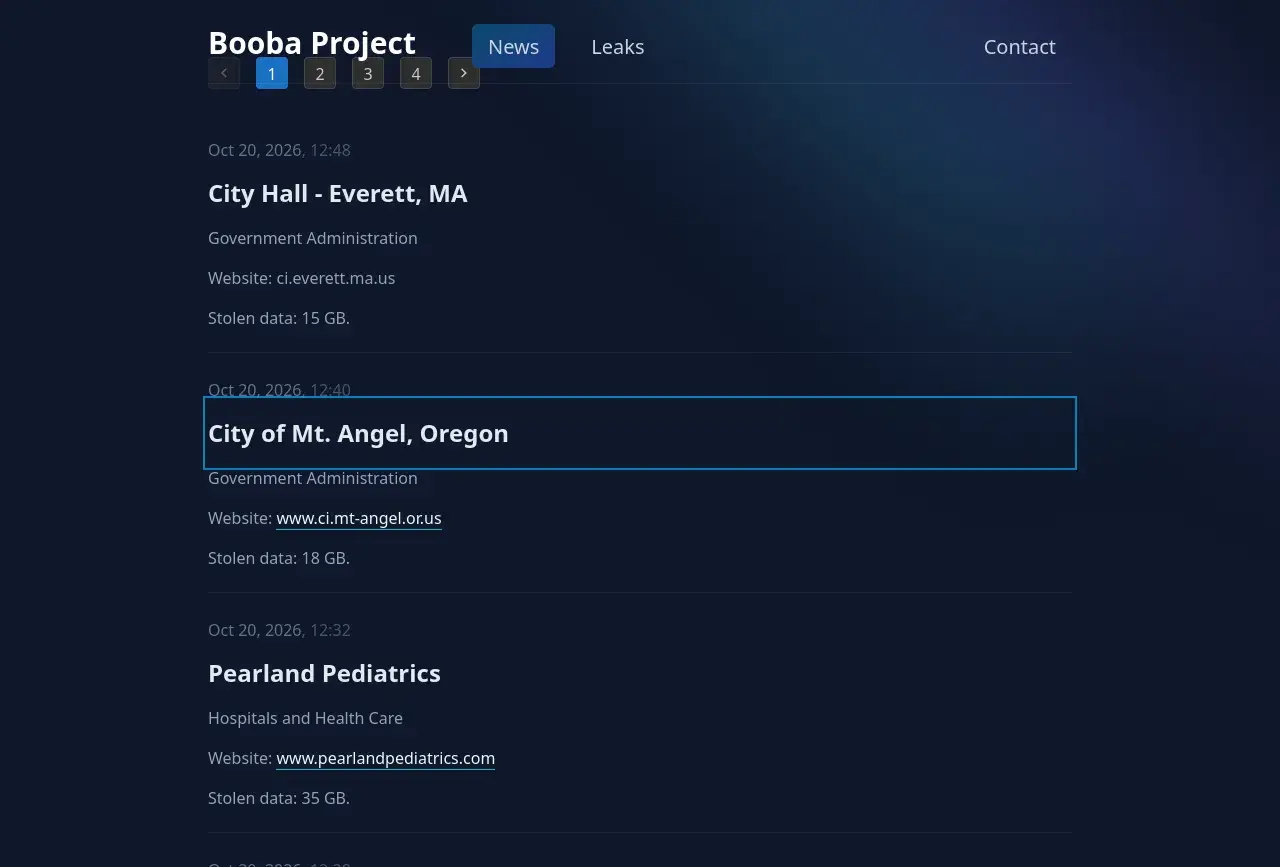
Group name: Booba Project
Post title: City of Mt. Angel, Oregon
Organization: City of Mt. Angel
Location: 🇺🇸 US
Sector: Government & Public Sector
Info: https://cti.fyi/#disclosure/Booba%20Project/City%20of%20Mt.%20Angel%2C%20Oregon

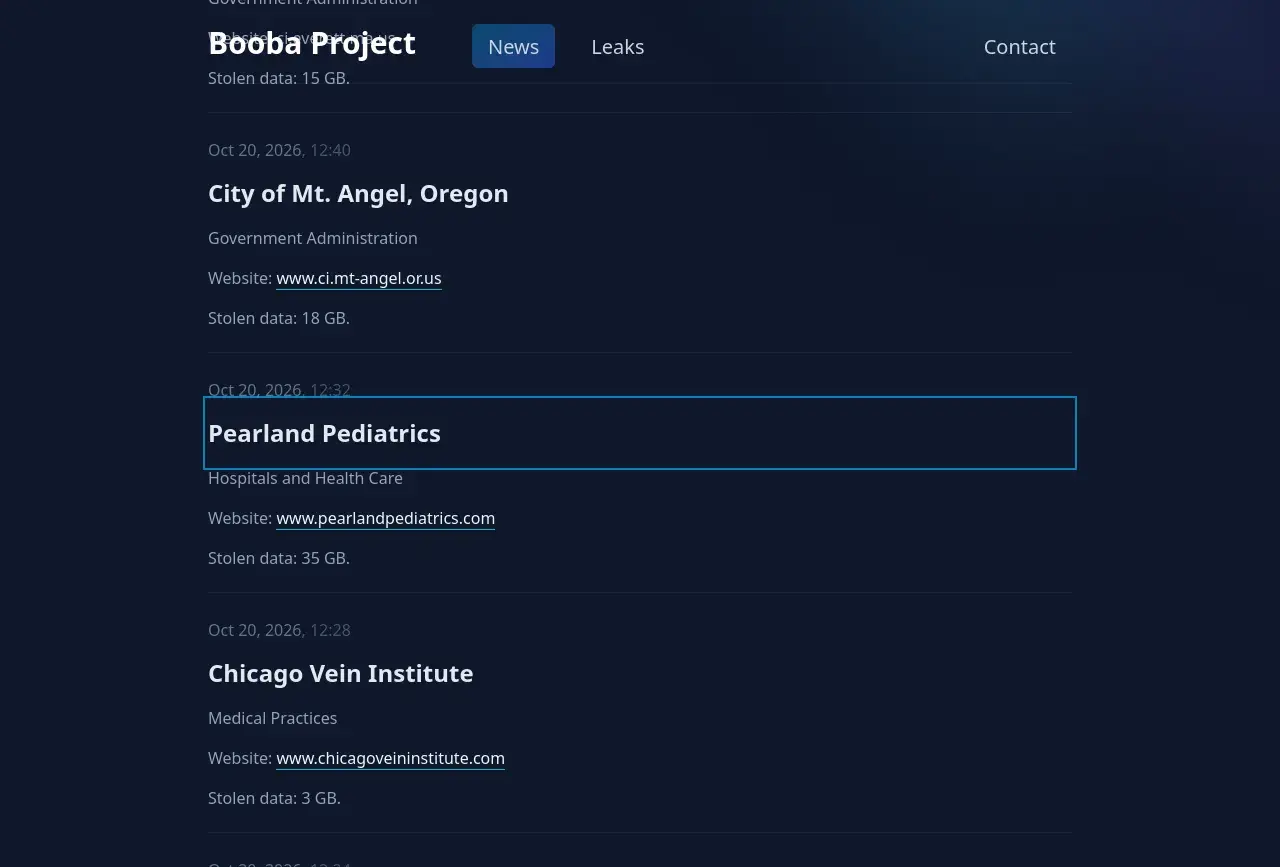
Group name: Booba Project
Post title: Pearland Pediatrics
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Pearland%20Pediatrics

Group name: Booba Project
Post title: Chicago Vein Institute
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/Chicago%20Vein%20Institute

Group name: Booba Project
Post title: Research Foundation of The City University of New York
Location: 🇺🇸 US
Sector: Education
Info: https://cti.fyi/#disclosure/Booba%20Project/Research%20Foundation%20of%20The%20City%20University%20of%20New%20York

Group name: Booba Project
Post title: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER, PA
Organization: COASTAL CAROLINA NEUROPSYCHIATRIC CENTER
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Booba%20Project/COASTAL%20CAROLINA%20NEUROPSYCHIATRIC%20CENTER%2C%20PA

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

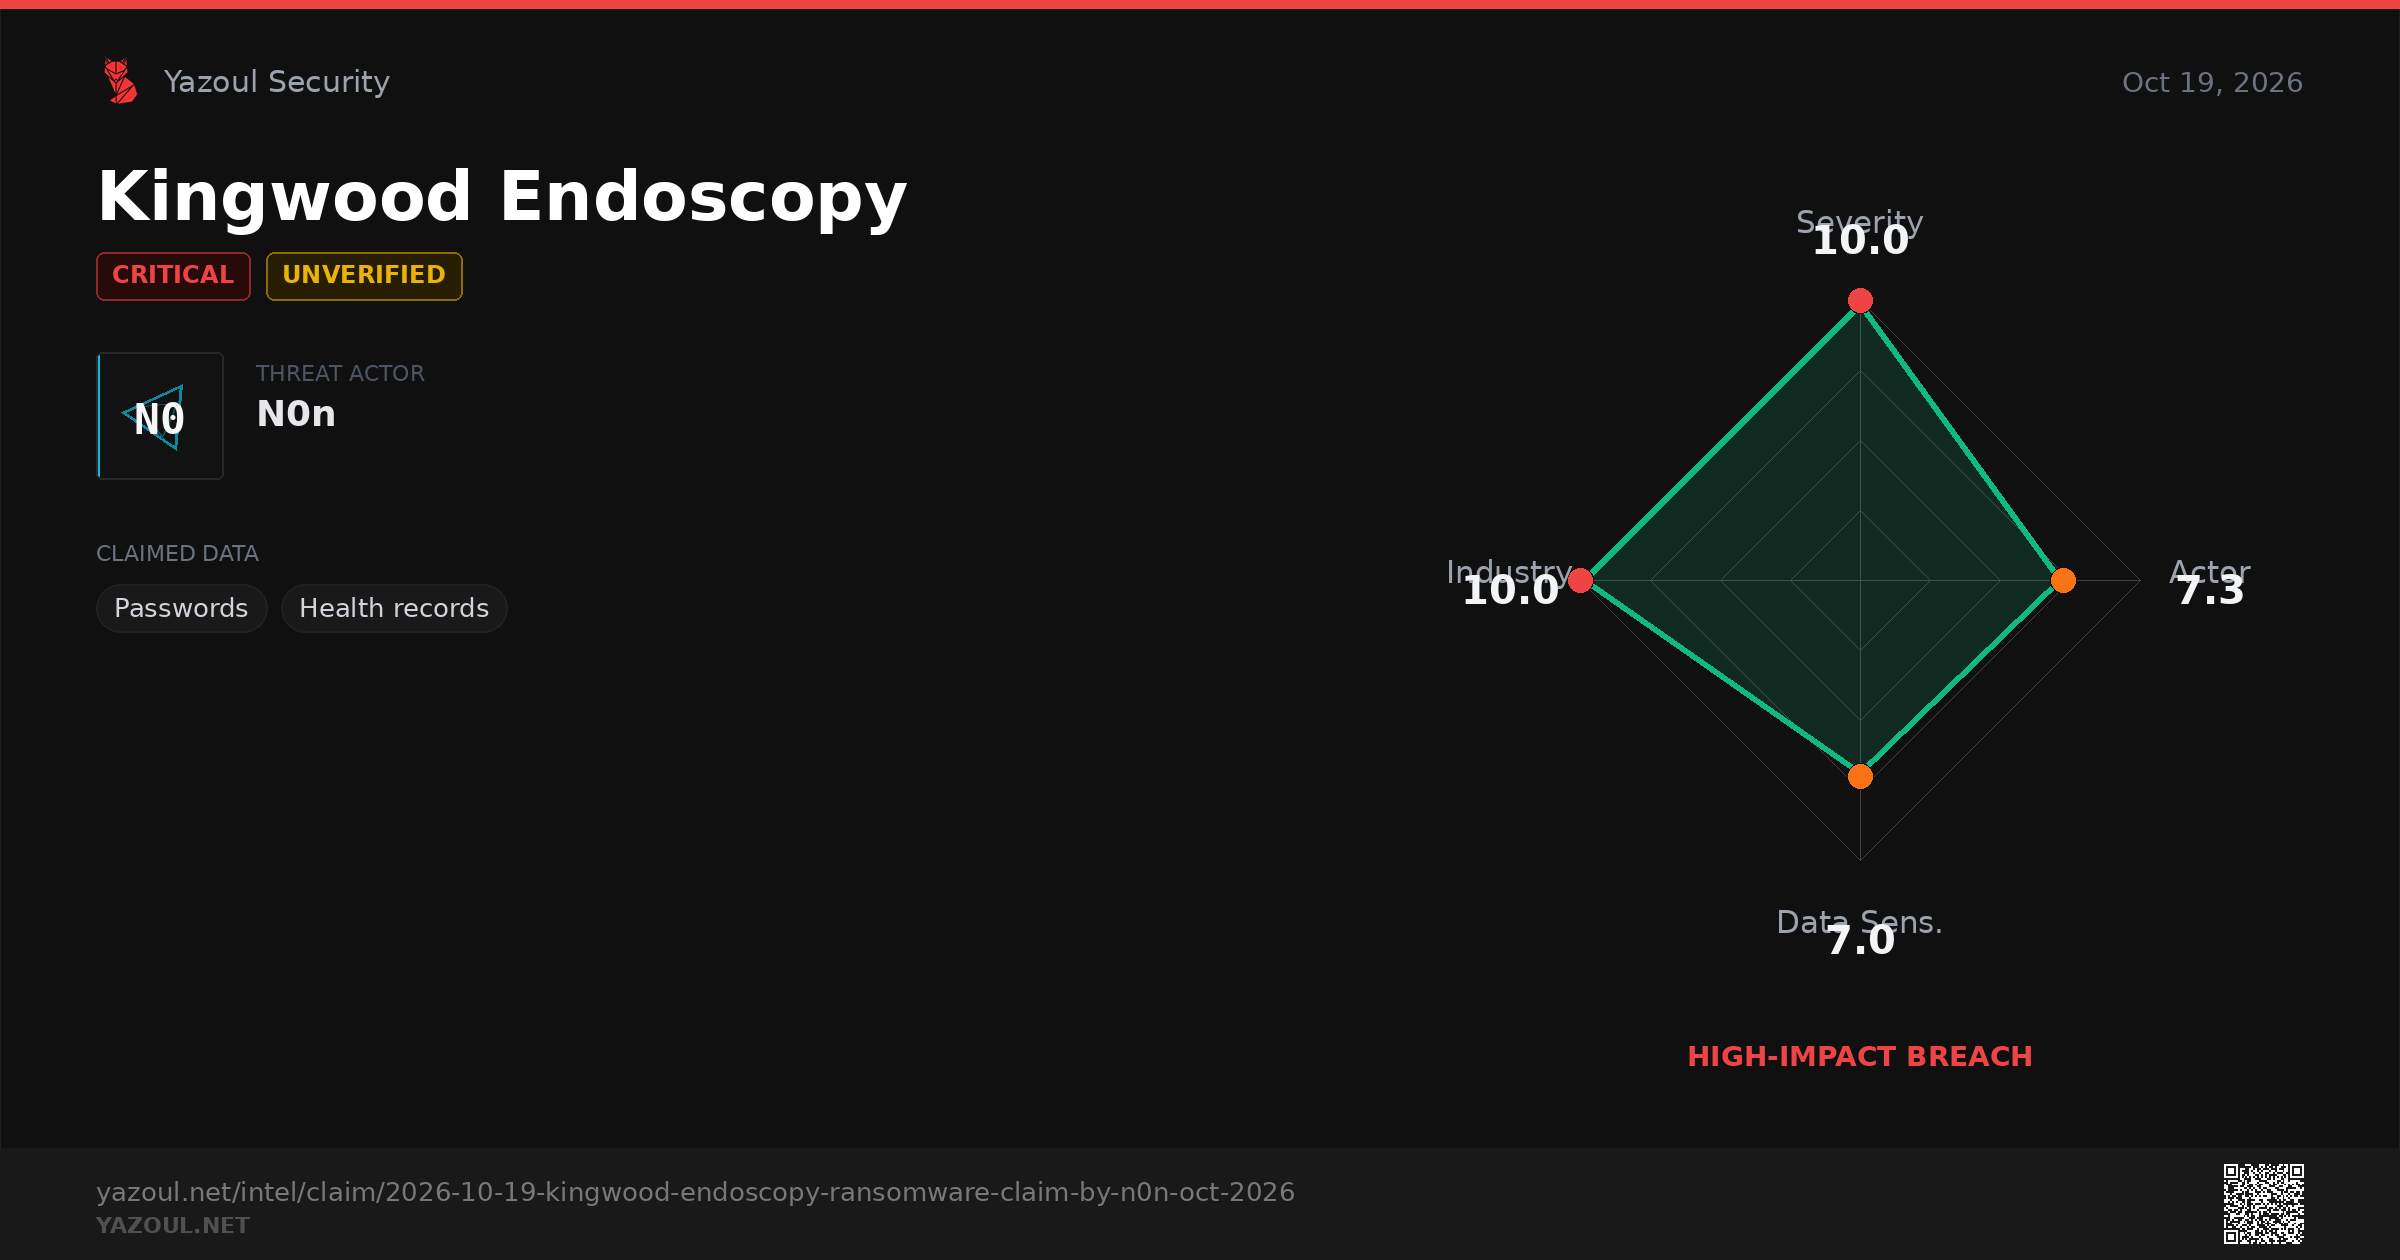
🛡 THREAT INTEL | Kingwood Endoscopy

🔴 Actor "N0n" claims Undisclosed

Allegedly exposed
• Passwords
• Health records

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-19-kingwood-endoscopy-ransomware-claim-by-n0n-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityKingwood Endoscopy Ransomware Claim by N0n (Oct 2026)N0n allegedly claims Kingwood Endoscopy as a victim, citing stolen credentials and system access. Read our unverified threat intel analysis and stay alert.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📣 CHERITech'26 speakers announced: Agenda now available!

We're excited to share the first view of the CHERITech'26 agenda, featuring an outstanding line-up of speakers from across industry, academia, and the cybersecurity community.

Join us in Munich on 12-13 November, as CHERITech'26 takes place alongside SEMICON Europa 2026 at the NextSEMI Arena (Hall B0), Messe München, to hear from experts driving the adoption, standardisation, and real-world deployment of #CHERI technologies.

Confirmed speakers include:

💠 (Keynote) Joerg Bormann - Siemens EDA (Siemens Digital Industries Software)
💠 Alexandre JOANNOU - University of Cambridge
💠 Alfredo Mazzinghi - University of Cambridge
💠 Andreas Hinterdorfer - Johannes Kepler Universität Linz
💠 Ben Fletcher - Codasip
💠 Dapeng Gao - University of Cambridge
💠 Divya Atkins - Mission Critical Applications Limited
💠 Edoardo Marangoni - SCI Semiconductor
💠 Elias Storme - DistriNet Research Unit @ku Leuven
💠 Graeme Jenkinson - Capabilities Limited
💠 Hugo Melder - Technical University of Munich
💠 Jan Philipp Thoma - Codasip
💠 Javier Orensanz Martinez - lowRISC CIC
💠 Jennifer Jackson - University of Birmingham
💠 John Kressel - Google
💠 Jonathan Woodruff - Capabilities Limited
💠 Joshua Cooper - Hildebrand Technology Limited
💠 Manu Ravishankar - PA Consulting
💠 Martin Atkins - Mission Critical Applications Limited
💠 Martin Kaiser - Codasip
💠 Mike Eftimakis - CHERI Alliance
💠 Nils Jordan - Ericsson
💠 Peter Cox - UM Labs R&D
💠 Tariq Kurd - Codasip
💠 Yuecheng Wang - University of Cambridge
💠 ... plus another exciting keynote speaker to be announced! 👀

View the agenda, explore the speaker line-up, and register today: https://cheri-alliance.org/events/cheritech26/

#CHERITech26 #MemorySafety #CyberSecurity #SecureByDesign #SEMIEurope #SEMICONEuropa2026
CHERI AllianceCHERI Alliance – CHERITech'26CHERITech’26 Conference Date: 12-13 November 2026 Location: Munich, DE @ SEMICON Europa (Hall B0) A two-day CHERI technical programme at SEMICON Europa in Munich, connecting implementation work with the wider electronics industry. Register Overview Agenda Exhibitors Floorplan Venue & Travel Overview CHERITech’26 will take place in Munich alongside Electronica / SEMICON Europa, one of the […]
↩ Reply ♡ 0 · ↻ 0 ↗ Original

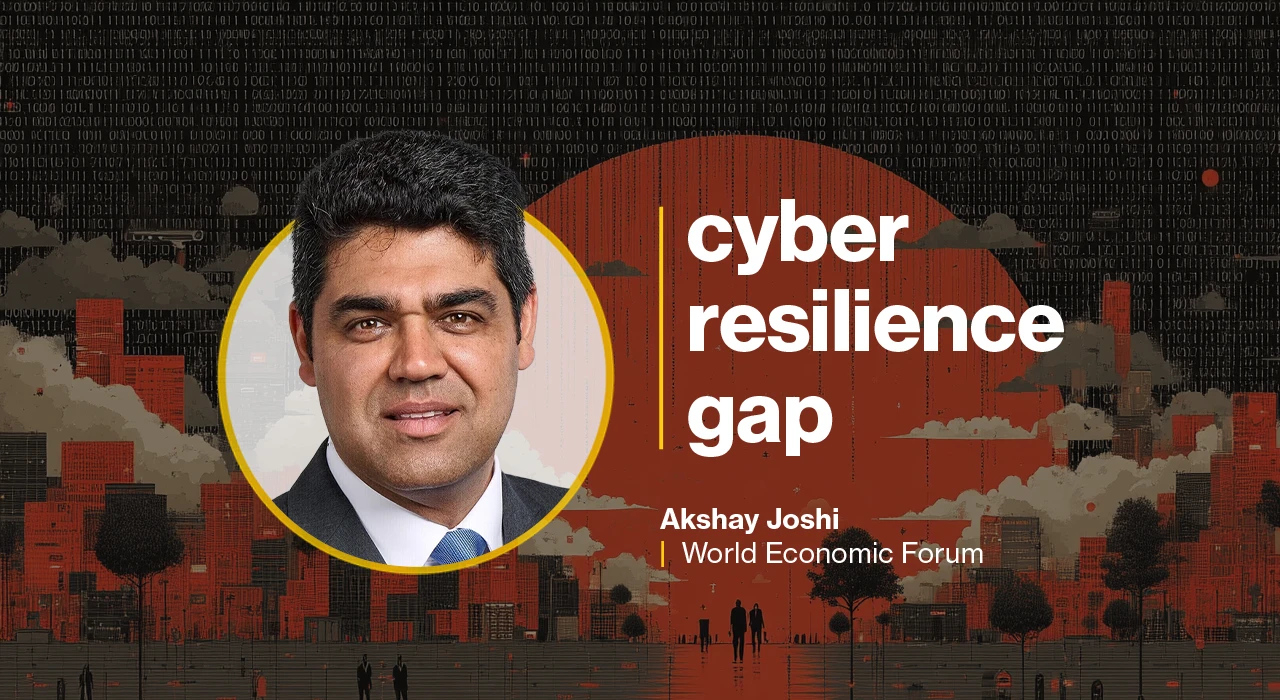
Geopolitics and the cyber resilience gap belong in your threat model

AI and geopolitics are reshaping cybersecurity. CEOs now prioritize cyber-enabled fraud over ransomware, with 73% of people experiencing it. However, a resilience gap widens: smaller orgs lack skills and resources while 91% of large firms adapt to geopolitical threats. Better governance and public-private collaboration are critical.

https://www.helpnetsecurity.com/2026/10/12/akshay-joshi-wef-cyber-resilience-gap/

#InfoSec #CyberSecurity

Help Net SecurityGeopolitics and the cyber resilience gap belong in your threat model - Help Net SecurityWEF's Akshay Joshi on AI threats, cyber-enabled fraud, geopolitics, and the widening cyber resilience gap between large and small companies.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

HACKFEST 2026 SPONSOR: ASTATE

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Astate, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://astate.one/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
astate.oneASTATE
↩ Reply ♡ 0 · ↻ 0 ↗ Original

State of (in)security - Week 42, 2026

In week 42 of 2026 (Oct. 12–19), incidents rose to 39 from 25 while advisories fell to 15 from 22. Known impacted individuals more than doubled to about 26.7 million. Highest breach was BK Japan's 11.18 million-record breach. Unauthorized access (12) and ransomware/malware (9) were the main causes of incidents. Healthcare (8) and tech (7) were the most-hit sectors. Actively exploited flaws reported in Ivanti, Palo Alto PAN-OS, Citrix NetScaler, Cisco, BeyondTrust, SonicWall and Zimbra, plus a Microsoft zero-day.

**Update Chrome to version 155.0.8059.79 or later, and any other Chromium-based browser you use (Edge, Brave, Opera, Vivaldi), and restart it ASAP. A malicious website, PDF, or even an ad on a trusted news site can take over your browser without a click, so keep automatic updates on for your browser, phone, computer and apps (on Android, include "Android System WebView") and add a trusted ad-blocker like uBlock Origin.**
#cybersecurity #infosec #knowledge #weeklyreport
https://beyondmachines.net/event_details/state-of-in-security-week-42-2026-s-g-o-m-1/gD2P6Ple2L

BeyondMachinesState of (in)security - Week 42, 2026In week 42 of 2026 (Oct. 12–19), incidents rose to 39 from 25 while advisories fell to 15 from 22. Known impacted individuals more than doubled to about 26.7 million. Highest breach was BK Japan's 11.18 million-record breach. Unauthorized access (12) and ransomware/malware (9) were the main causes of incidents. Healthcare (8) and tech (7) were the most-hit sectors. Actively exploited flaws reporte
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New Go security releases added explicit distrust for some specific intermediate CA certificates belonging to eMudhra Technologies Limited. Interestingly, this is tracked as CVE-2026-111943 but no details on why this was done are provided.

https://github.com/golang/go/commit/7f86f957633ee31a1c17a1eb8452ca7a3d9bc141

#pki #CVE_2026_111943 #infosec #cybersecurity

GitHubcrypto/x509: distrust a handful of intermediates · golang/go@7f86f95Filter a set of intermediates from chains returned by calls to Verify. These chains are identified via SHA-256 SPKI hashes. Fixes CVE-2026-111943 For golang/go#82345 Change-Id: I43172dd50560eb7d1...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

UK keeps AI safeguards in the maybe pile for Cyber Security Bill

Tech trends: Nvidia boosts local AI with RTX Spark; Brave adds encrypted AI chats. TSMC eyes US datacenters; Linux devs embrace AI tools responsibly. Security concerns: Russian phishing via Signal, Microsoft SharePoint zero-days. EQT acquires Acronis amid ransomware threats. NetBSD emerges as AI-free OS; Ubuntu, Firefox innovate; KDE marks 30 years with AI desktop plans.

https://www.theregister.com/ai-and-ml/2026/10/15/uk-keeps-ai-safeguards-in-the-maybe-pile-for-cyber-security-bill/5303026

#InfoSec #CyberSecurity

theregisterUK keeps AI safeguards in the maybe pile for Cyber Security BIllOfficials say amendments remain under consideration despite minister's pledge to act
↩ Reply ♡ 0 · ↻ 0 ↗ Original

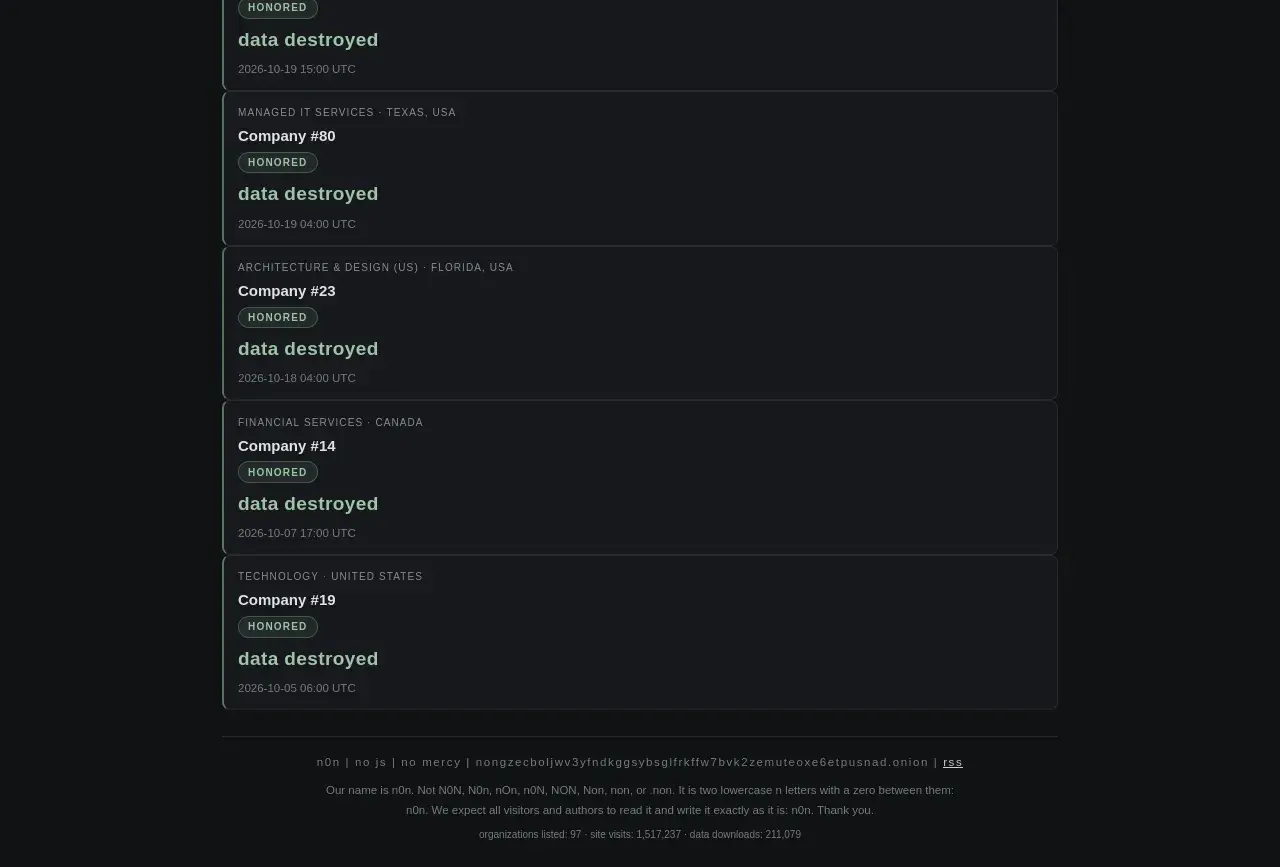
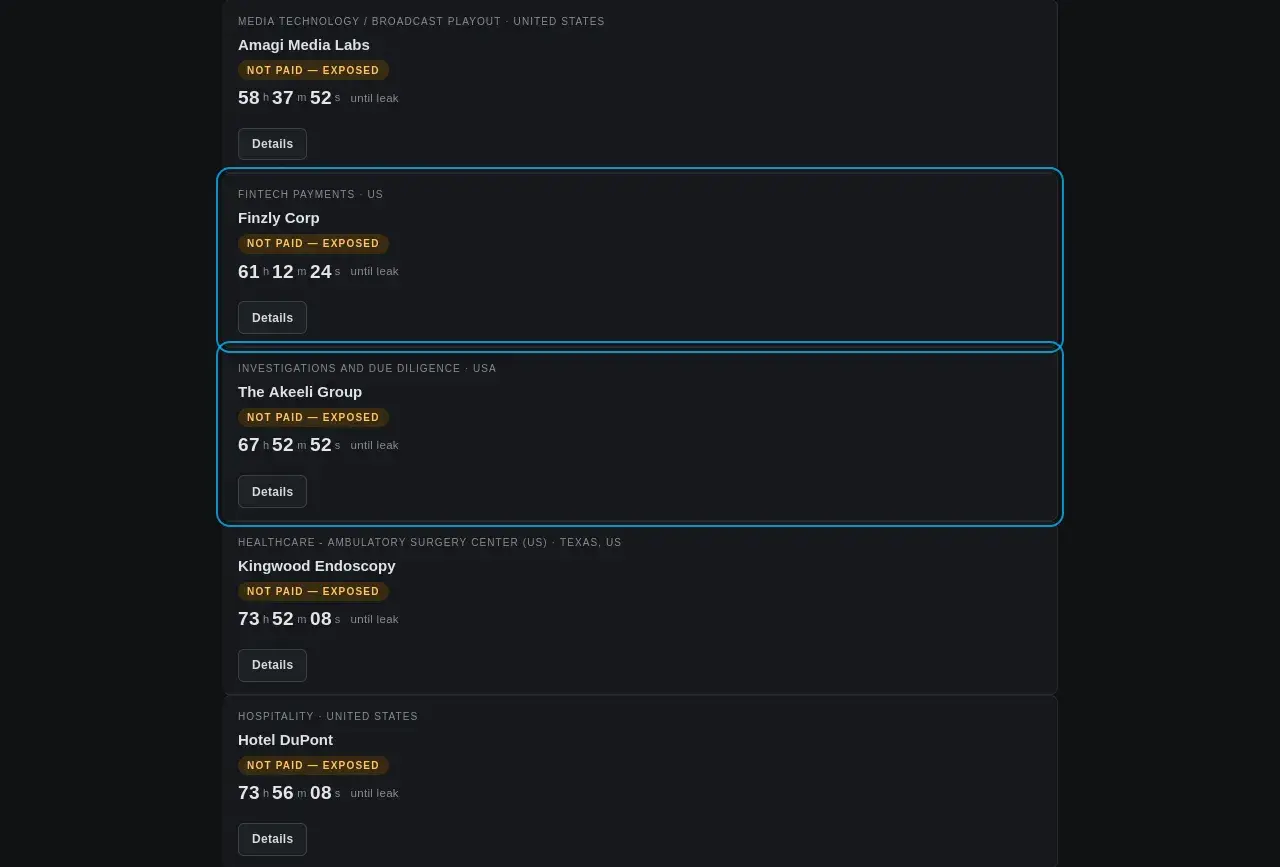
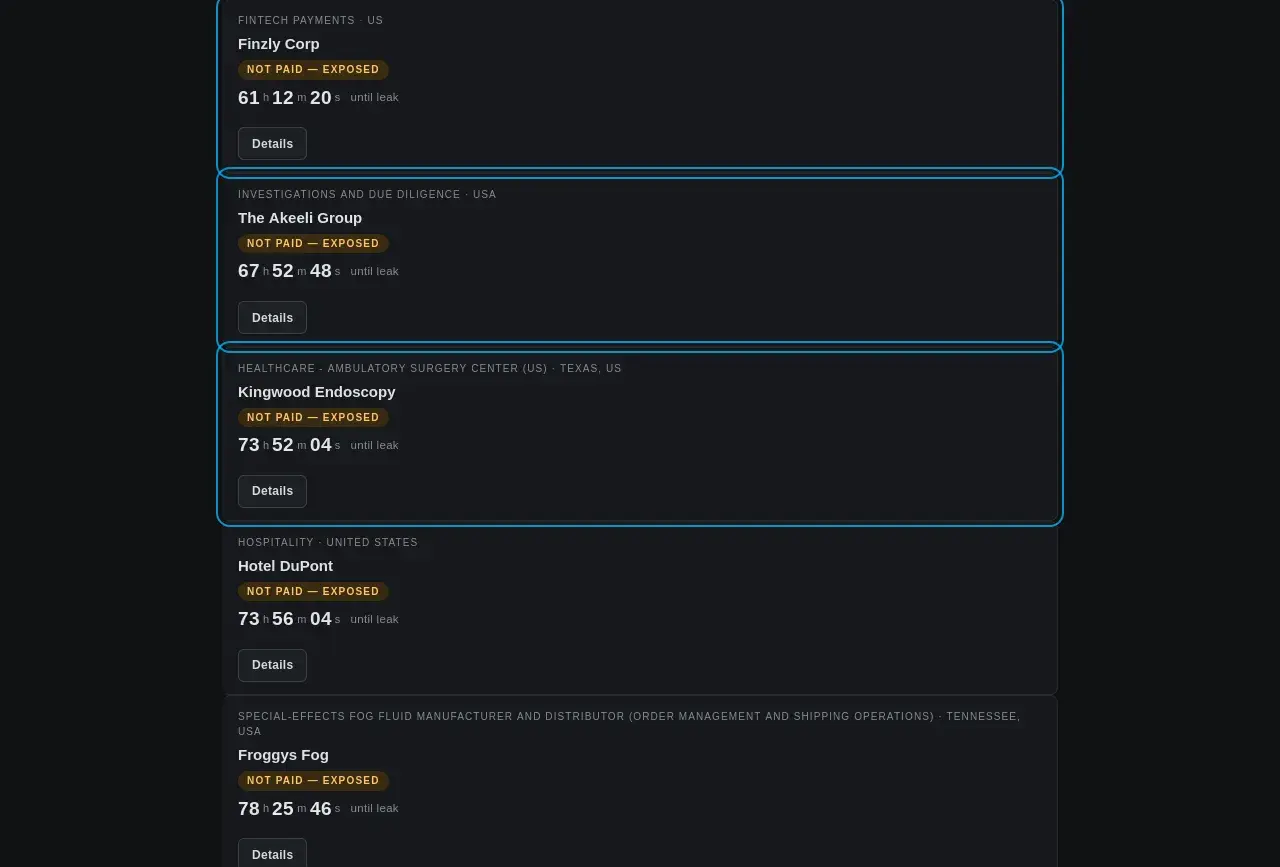
🚨New ransom group blog posts!🚨

Group name: N0n
Post title: Finzly Corp
Location: 🇺🇸 US
Sector: Financial Services
Info: https://cti.fyi/#disclosure/N0n/Finzly%20Corp

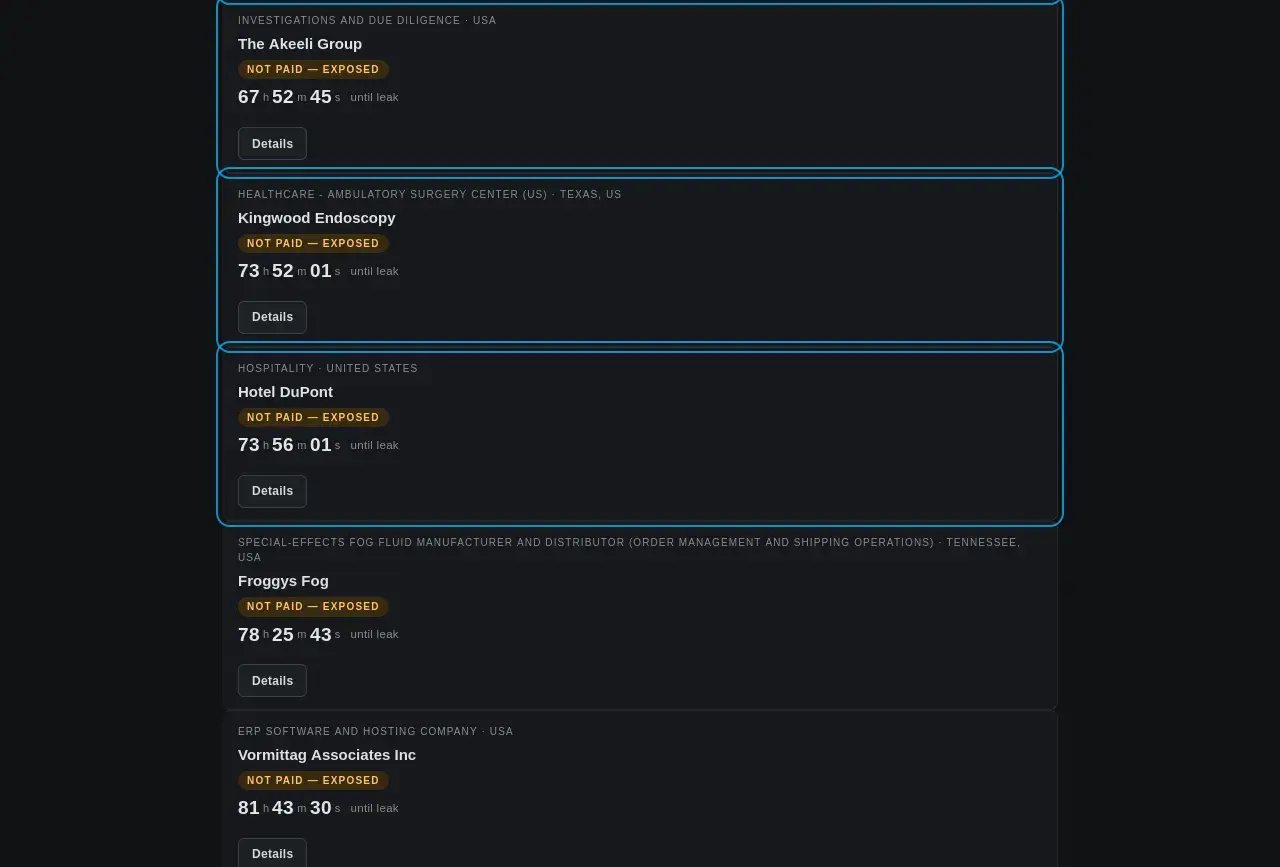
Group name: N0n
Post title: The Akeeli Group
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/The%20Akeeli%20Group

Group name: N0n
Post title: Kingwood Endoscopy
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/N0n/Kingwood%20Endoscopy

Group name: N0n
Post title: Hotel DuPont
Location: 🇺🇸 US
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/N0n/Hotel%20DuPont

Group name: N0n
Post title: Froggys Fog
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/N0n/Froggys%20Fog

Group name: N0n
Post title: Vormittag Associates Inc
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Vormittag%20Associates%20Inc

Group name: N0n
Post title: Company #93
Info: https://cti.fyi/#disclosure/N0n/Company%20%2393

Group name: N0n
Post title: Company #94
Info: https://cti.fyi/#disclosure/N0n/Company%20%2394

Group name: N0n
Post title: Company #95
Info: https://cti.fyi/#disclosure/N0n/Company%20%2395

Group name: N0n
Post title: Company #96
Info: https://cti.fyi/#disclosure/N0n/Company%20%2396

Group name: N0n
Post title: Company #97
Info: https://cti.fyi/#disclosure/N0n/Company%20%2397

Group name: N0n
Post title: Company #98
Info: https://cti.fyi/#disclosure/N0n/Company%20%2398

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NightSpire Ransomware Claim Follows Colorado County System Disruption

Colorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/nightspire-ransomware-claim-follows-colorado-county-system-disruption-o-d-n-s-s/gD2P6Ple2L

BeyondMachinesNightSpire Ransomware Claim Follows Colorado County System DisruptionColorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption
↩ Reply ♡ 0 · ↻ 0 ↗ Original