X XFediYour place in the Fediverse
XFEDI

#CyberSecurity

ActivityPub

Public posts with this hashtag.

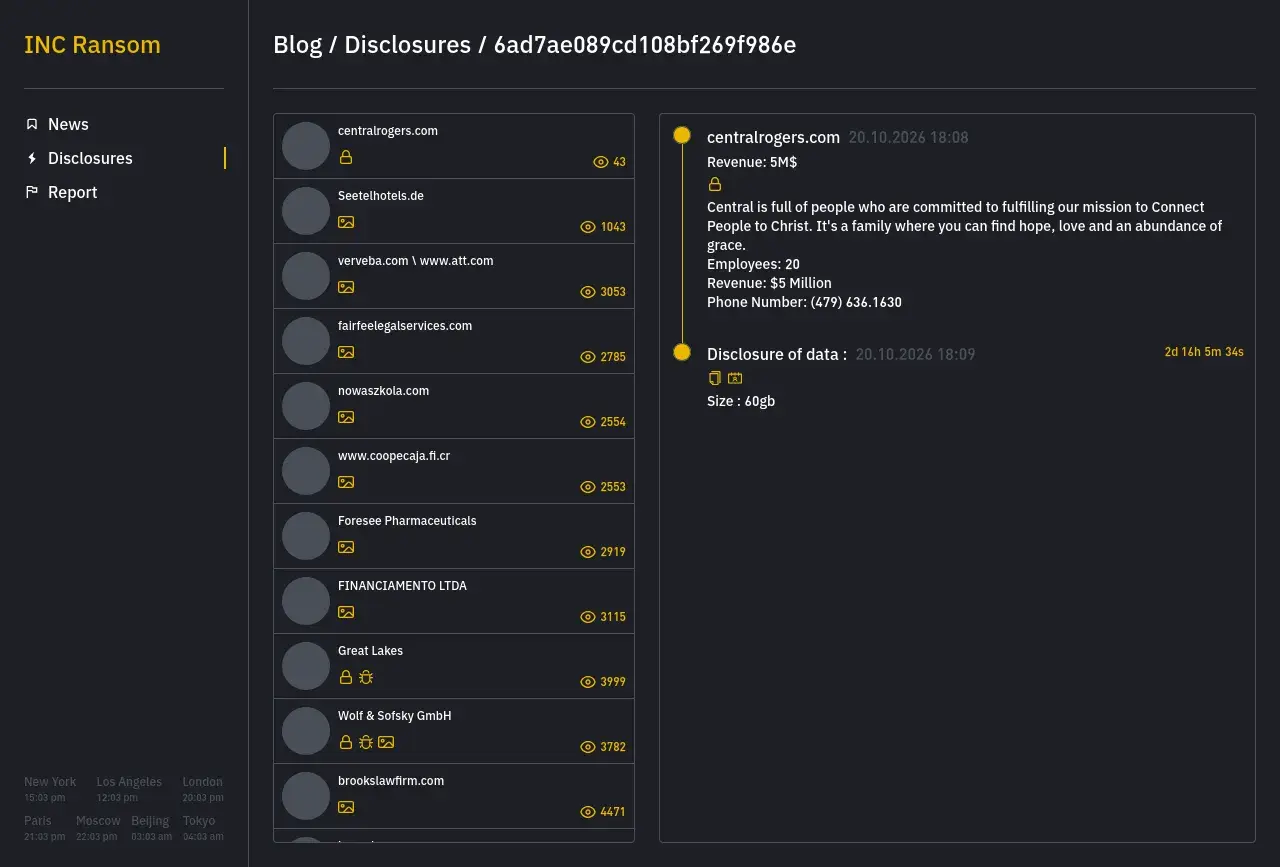
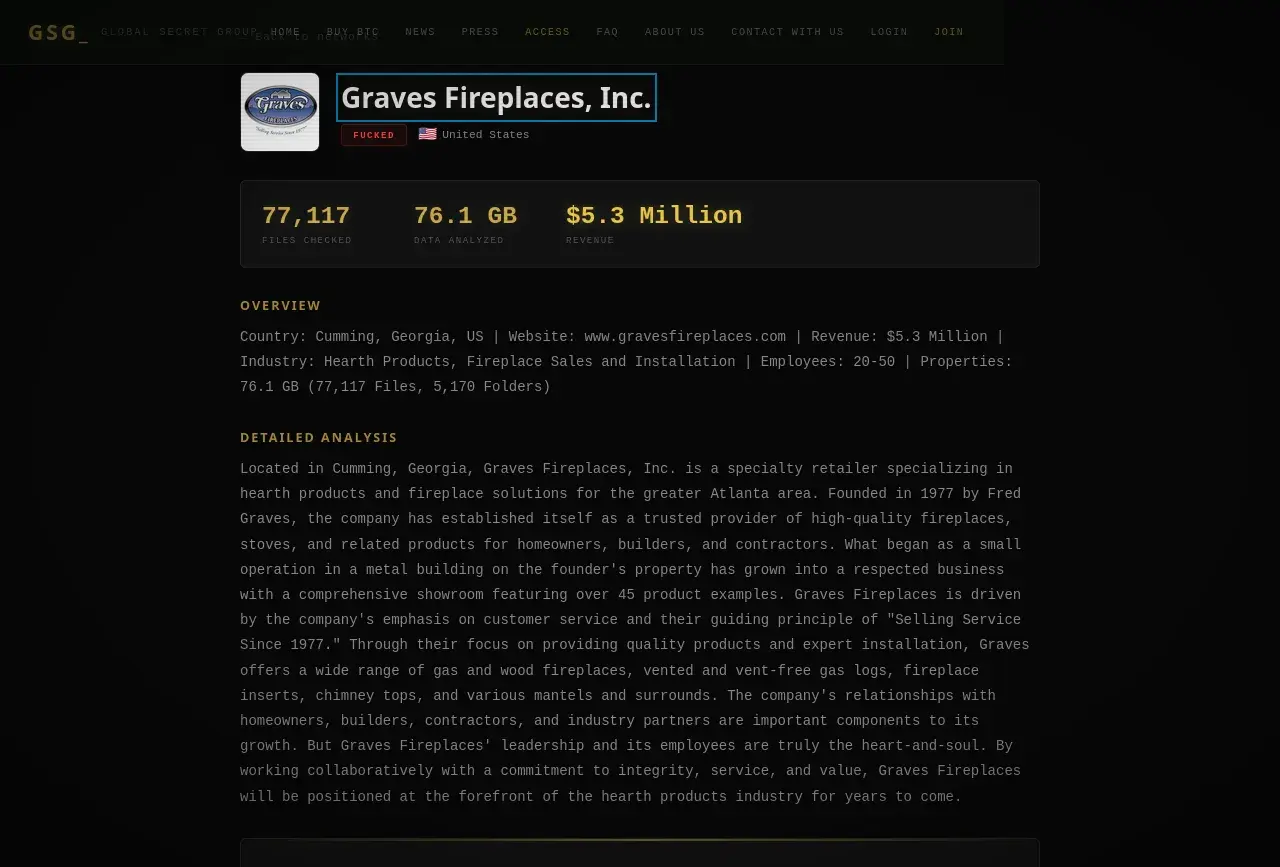
🚨New ransom group blog posts!🚨

Group name: incransom
Post title: centralrogers.com
Organization: Central
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/incransom/centralrogers.com

Group name: Global Secret Group
Post title: Graves Fireplaces, Inc.
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Global%20Secret%20Group/Graves%20Fireplaces%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

New! From Token Security, "Securing #AI agents requires a new playbook. The Agentic Universe is a free learning center built by #CISOs and #cybersecurity practitioners to help you understand agent risk, govern access, and put AI Agent Security into practice. Explore short videos, technical deep dives, and checklists built for how security teams actually learn and work."

https://api.cyfluencer.com/s/https-www-token-security-agentic-universe-30078

www.token.securityAgentic Universe | Token Security
↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI tokens got cheaper, but the deployment bill didn't

Falling AI token prices don't guarantee lower enterprise costs. Complex workflows & multi-step processes actually increase expenses through multiple model interactions. Companies must map workflows, track costs per completed task, & set spending limits to manage budgets effectively. Cheaper tokens ≠ cheaper operations.

https://www.techtarget.com/it-strategy/opinion/AI-tokens-got-cheaper-but-the-deployment-bill-didnt

#InfoSec #CyberSecurity

IT StrategyAI tokens got cheaper, but the deployment bill didn't | TechTargetFalling AI token prices lower initial costs, but complex workflows can drive up expenses. Map your AI process to control spending effectively.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

We need to retrain an entire generation of network engineers to be reluctant to put sensitive information on the Internet.

Today we have an entire generation of network engineers that don't even know private data circuits exist. They can't even think of them as an option.

You can quote me.
--Bob Young

#cybersecurity #AI

↩ Reply ♡ 0 · ↻ 0 ↗ Original

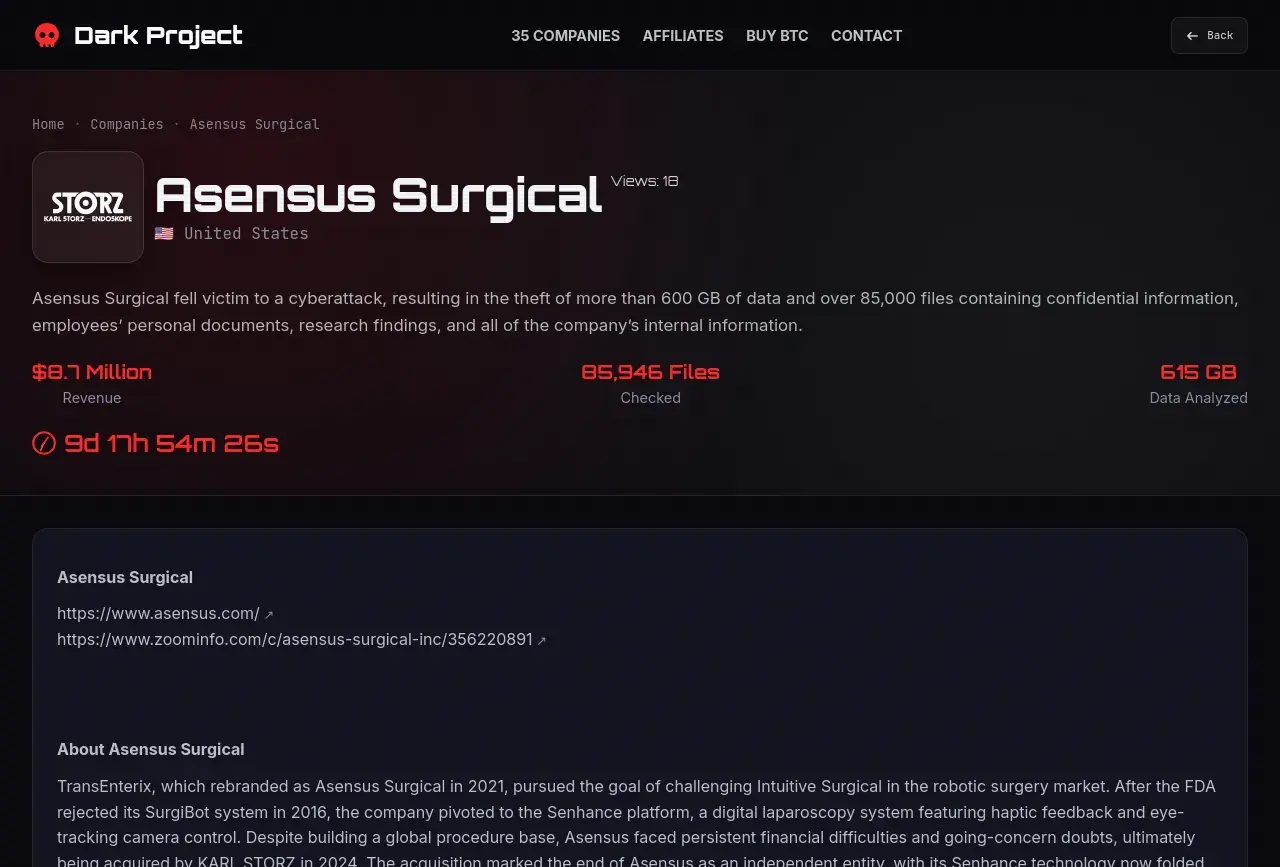
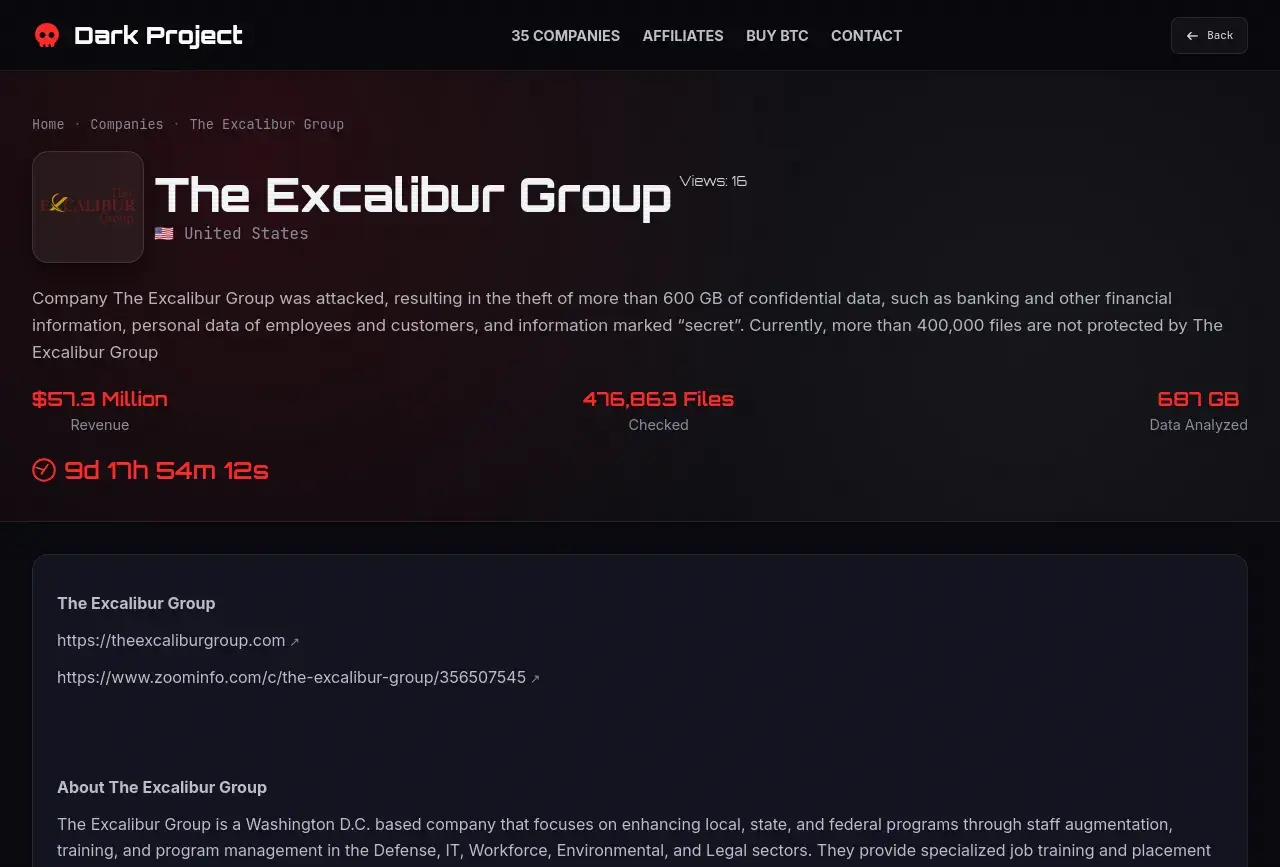
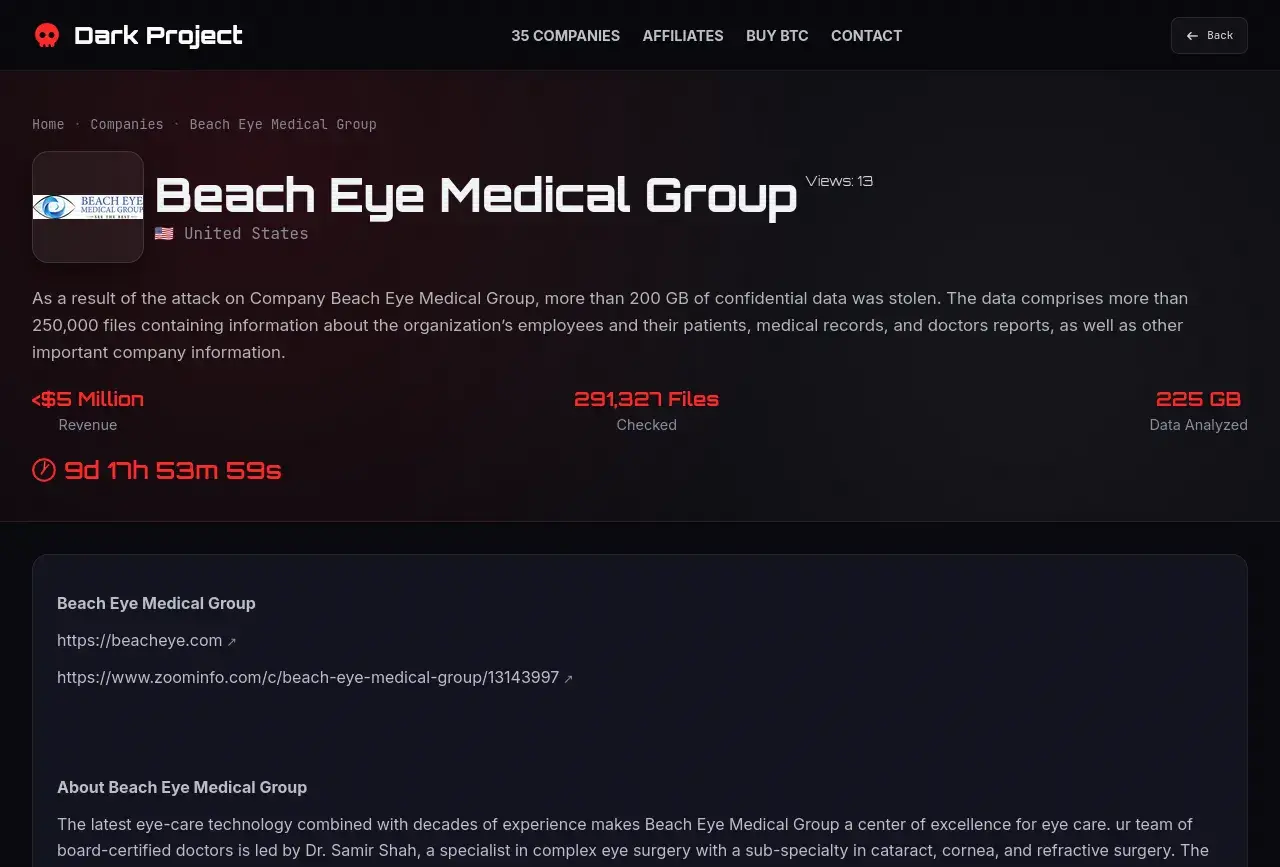
🚨New ransom group blog posts!🚨

Group name: Dark Project
Post title: Asensus Surgical
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Dark%20Project/Asensus%20Surgical

Group name: Dark Project
Post title: The Excalibur Group
Sector: Financial Services
Info: https://cti.fyi/#disclosure/Dark%20Project/The%20Excalibur%20Group

Group name: Dark Project
Post title: Beach Eye Medical Group
Sector: Healthcare
Info: https://cti.fyi/#disclosure/Dark%20Project/Beach%20Eye%20Medical%20Group

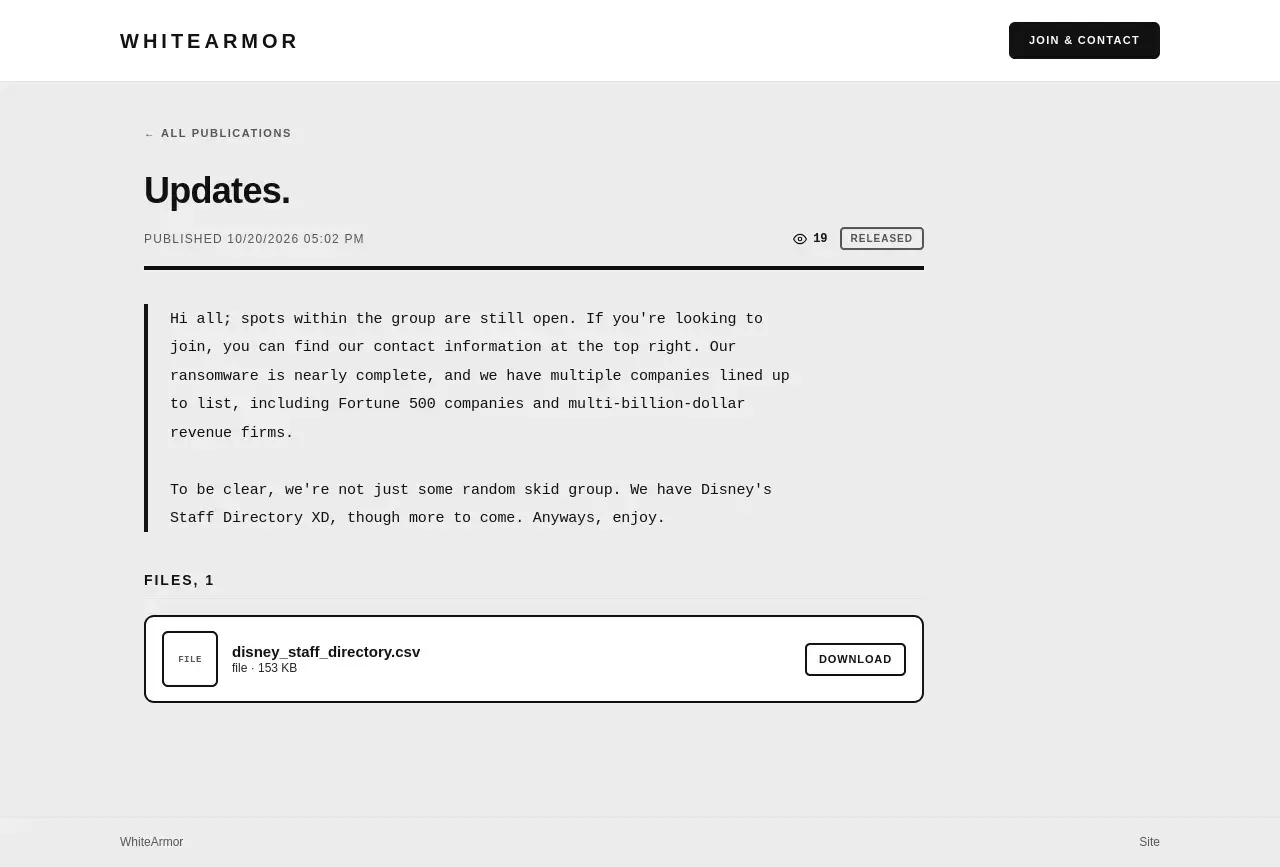
Group name: Whitearmor
Post title: Updates.
Organization: The Walt Disney Company
Location: 🇺🇸 US
Sector: Media & Entertainment
Info: https://cti.fyi/#disclosure/Whitearmor/Updates.

Group name: Whitearmor
Post title: W.A
Info: https://cti.fyi/#disclosure/Whitearmor/W.A

Group name: Mimori
Post title: OpenText
Location: 🇨🇦 CA
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/OpenText

Group name: Mimori
Post title: Aveva
Location: 🇬🇧 GB
Sector: Technology
Info: https://cti.fyi/#disclosure/Mimori/Aveva

#ransomware #cti #threatintelligence #cybersecurity #infosec

Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : GROUPE COSIOR

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Groupe Cosior, qui est un partenaire KIOSQUE!

Visiter leur site web : https://groupecosior.com/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
Hackfest 2026Accueil — Hackfest 2026Hackfest 2026 - L'événement en cybersécurité de l'année
↩ Reply ♡ 0 · ↻ 0 ↗ Original

How CIOs can climb out of the AI governance chasm

CIOs struggle to keep pace with AI adoption—84% say AI evolves faster than governance can handle. Key challenges: only 21% track AI costs effectively, data quality issues persist, and "shadow AI" undermines control. Less than 50% have clear governance in place. Solutions require simplified procedures, cross-leadership collaboration, better financial visibility, and ongoing responsible AI education.

https://www.informationweek.com/machine-learning-ai/how-cios-can-climb-out-of-the-ai-governance-chasm

#InfoSec #CyberSecurity

Information WeekAI overload: Governance gaps that can swallow CIOsAI governance is losing the race against adoption, and CIOs must figure out how to close the gap.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
T

RE: https://thecybersecguru.com/news/emudhra-ca-compromise-copy-slug/

🚨 eMudhra CA compromise: 8 intermediate certificate keys confirmed compromised.

The incident triggered emergency distrust measures across browsers and software, including Firefox’s OneCRL protections and urgent Go security updates.

The bigger concern is the long tail: outdated binaries, containers and applications with their own certificate stores may not inherit browser protections.

How do you revoke trust across the entire internet?

Technical breakdown 👇
https://thecybersecguru.com/news/emudhra-ca-compromise/

#InfoSec #CyberSecurity #TLS #PKI

❞ Quoted postThe CyberSec Guru

Content warning: Eight eMudhra intermediate CA keys were compromised, triggering emergency distrust updates. Learn how the breach affects TLS certificates, browsers and Go

The CyberSec GurueMudhra CA Compromise: 8 Certificate Keys Exposed | The CyberSec GuruEight eMudhra intermediate CA keys were compromised, triggering emergency distrust updates. Learn how the breach affects TLS certificates, browsers and Go
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-90797 and CVE-2026-107755 affect Apache CouchDB versions before 3.5.3.

One allows a pre-authentication denial of service through gzip decompression; the other lets an authenticated user read other users' replication credentials.

The Apache Software Foundation fixed both in CouchDB 3.5.3. No exploitation is confirmed.

https://seclists.org/oss-sec/2026/q4/244

#infosec #cybersecurity

seclists.orgoss-sec: CVE-2026-90797: Apache CouchDB: Pre-authentication gzip decompression bomb via POST /_session
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Is your architecture preventing you from calculating AI value?

Organizations face a critical trade-off: managed AI services enable quick deployment but hide costs, while self-managed infrastructure offers granular visibility. As enterprises scale AI agents, precise cost tracking becomes essential—yet managed services lack transparency on expenses. Future success requires shifting from price-per-token to cost-per-task metrics and controlling infrastructure for real-time insights into AI workload expenses.

https://www.cio.com/article/4231999/is-your-architecture-preventing-you-from-calculating-ai-value.html

#InfoSec #CyberSecurity

CIOIs your architecture preventing you from calculating AI value?The choice between managed services and infrastructure you control sets the ceiling on what you’ll ever know about AI spend.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CÉGEP GARNEAU

Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Cégep Garneau, a KIOSK sponsor!

If you want to learn more about this company’s mission, visit their website https://fc.cegepgarneau.ca/

PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
ProgressezProgressezFormation Continue du Cégep Garneau
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⚠️ CRITICAL: Pegasus Spyware Infection Confirmed on Serbian University Rector's iPhone Days Before Election

NSO Group's Pegasus spyware is actively targeting high-profile individuals in Serbia via zero-click exploits, with at least 14 victims confirmed including university leadership, prosecutors, and opposition figures since early 2026. Infections occur without user interaction and provide attackers ful…

https://threatnoir.com/focus

#infosec #cybersecurity

🤖 AI generated summary

threatnoir.comUrgent Threats & Advisories | ThreatNoirActive and archived urgent security threats, CVEs, and advisories for SOC teams and threat hunters.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Kentucky Medicaid Portal Breach Exposes Data of Approximately 3,900 Individuals

The Kentucky Cabinet for Health and Family Services disclosed a data breach after an unauthorized party accessed the KY Health-Net Provider Portal and downloaded Medicaid member information. Approximately 3,816 individuals were potentially affected across three unauthorized access incidents in 2026.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/kentucky-medicaid-portal-breach-exposes-data-of-approximately-3900-individuals-v-2-u-z-q/gD2P6Ple2L

BeyondMachinesKentucky Medicaid Portal Breach Exposes Data of Approximately 3,900 IndividualsThe Kentucky Cabinet for Health and Family Services disclosed a data breach after an unauthorized party accessed the KY Health-Net Provider Portal and downloaded Medicaid member information. Approximately 3,816 individuals were potentially affected across three unauthorized access incidents in 2026.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

PARTENAIRE HACKFEST 2026 SPONSOR : CÉGEP GARNEAU

La prochaine édition du 18e Hackfest Level Up ne serait pas possible sans nos partenaires. Nous sommes heureux d’avoir avec nous Cégep Garneau, qui est un partenaire KIOSQUE!

Visiter leur site web : https://fc.cegepgarneau.ca/

PS VOUS POUVEZ TOUJOURS ACHETER VOS BILLETS pour les 29, 30 et 31 octobre 2026 au Centre des congrès de Québec ;) Info sur notre site web : https://hackfest.ca/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors

#hacking #infosec #hackfest #hf2026 #cybersecurity

Media attachment
ProgressezProgressezFormation Continue du Cégep Garneau
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The real AI budget question: Where should we spend more?

🤖 AI budgeting needs a strategic overhaul: shift from cost control to ROI-driven value creation. CIOs should measure AI impact through business KPIs, not just usage metrics. Adopt flexible consumption-based models, tie funding to revenue-generating areas, and implement adaptive governance. The future? CIOs as strategic partners proving AI's business value.

https://www.cio.com/article/4230135/the-real-ai-budget-question-where-should-we-spend-more.html

#InfoSec #CyberSecurity

CIOThe real AI budget question: Where should we spend more?The AI budget question isn’t just how much you’re spending; it’s whether your biggest investments are producing enough business value to justify more.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Do you have any last minute question before the Open Security Conference? Check our FAQ, the answer might be in there already: https://opensecurityconference.org/faq/

Your point is not covered? Feel free to reach out :) https://opensecurityconference.org/contact/

We will soon send more information to all participants so you can prepare for the event. We're already looking forward to welcoming you!

#osco #osco26 #Security #CyberSecurity #InfoSec #AppSec [lisi]

Open Security ConferenceFAQWelcome to the Open Security Conference (osco), the people-centred international gathering for everyone interested in cybersecurity. Join us 5-8 November 2026 in Rückersbach, Germany.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

An intrusion discovered today may have started months ago. The NCSC tells you to size the log window to that gap, initial access to detection: 13 months for critical systems, 180 days otherwise. Rotate at 30 days and you can only reconstruct the last month.

How fast logs leave the box matters as much. Logs left on the box belong to whoever owns the box. Move them to a central store quickly and the attacker loses the chance to delete their own tracks.

Logging Made Easy, the NCSC's open source project, is built on something beats nothing. Their phrase is flight recorder.

https://www.ncsc.gov.uk/blog-post/what-exactly-should-we-be-logging

#CyberSecurity #InfoSec #Logging

National Cyber Security CentreWhat exactly should we be logging?A structured look at what data to collect for security purposes and when to collect it.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

OpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked Attack

OpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.

****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/opencode-console-breach-exposes-ai-provider-api-keys-after-legacy-system-compromise-c-6-0-f-4/gD2P6Ple2L

BeyondMachinesOpenCode Console Breach Exposes AI Provider API Keys in Distillation-Linked AttackOpenCode disclosed a breach affecting its cloud-based Console after attackers accessed a legacy system, potentially exposing AI provider API keys belonging to approximately 1.4% of Console users. The company linked the incident to a large-scale model distillation attack and is working with OpenAI, Anthropic, and Google to revoke compromised credentials and address unauthorized charges.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

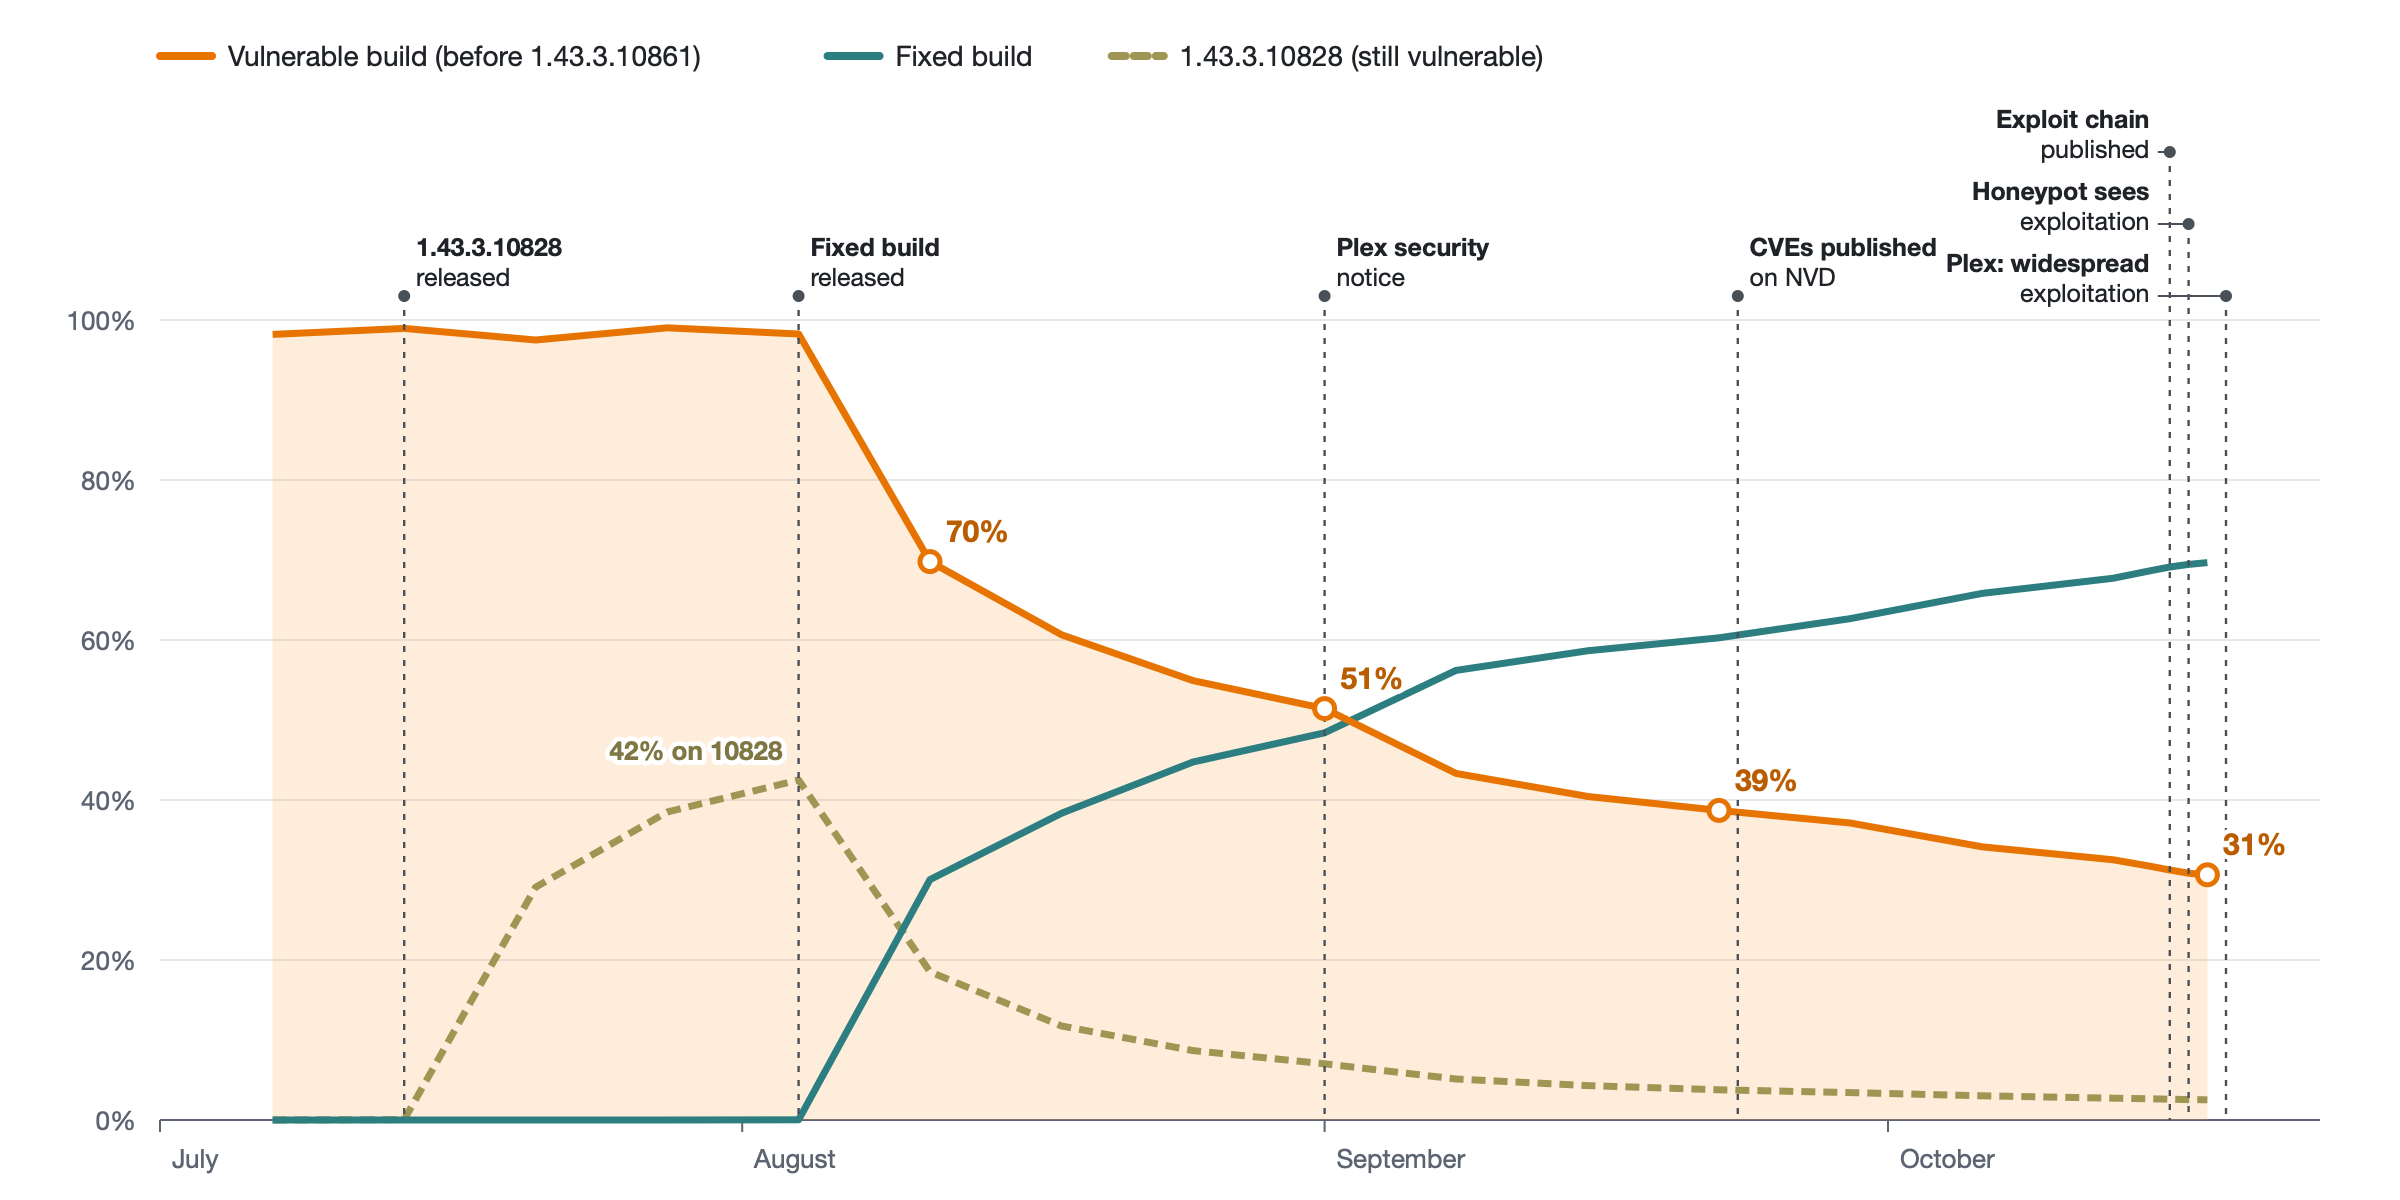
🚨 Rapid Response: Four vulnerabilities in Plex Media Server can be chained to achieve unauthenticated remote code execution. Plex reports compromised servers being used to run cryptocurrency miners and proxy software.

Censys ARC observes ~340,000 Internet-exposed Plex Media Server hosts. Roughly 30% run a vulnerable build, and nearly 8,000 run an early build that may be mistaken for patched.

Despite publication of the exploit chain and reports of exploitation, fewer than 2% of still-vulnerable hosts upgraded in the following three days.
Plex advises that previously exposed, unpatched servers may already be compromised and require additional remediation beyond patching.

Full Censys ARC advisory: https://censys.com/advisory/cve-2026-96652-cve-2026-96654-cve-2026-96655-cve-2026-96656/

#CensysARC #Cybersecurity #VulnerabilityManagement #Plex #InfoSec

Censys ARC graph showing trends in vulnerability and fixed build releases from July to October. One line shows the decline of vulnerable builds from 100% in July to 31% in October. Another line indicates the increase in fixed builds, peaking at 70% in August. Notable events are marked, including the release of 1.4.3.1080 in August and Plex security notices. CVEs published on NVD and explicit exploit chain events are annotated.
CensysOctober 20 Advisory: Plex Media Server Remote Code Execution Chain [CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656] - CensysCVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656 are four flaws in Plex Media Server before build 1.43.3.10861.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

The Aoki infostealer now targets AI coding assistant credentials: .claude.json, Codex configs, Copilot, Cursor, and Gemini tokens, plus AWS keys. Stealer logs are traded within hours.

Rotate your keys, set billing alerts, and check whether your credentials are already out there.

https://blog.relayshield.net/your-ai-coding-credentials-are-now-infostealer-targets

#CyberSecurity #ThreatIntel #InfoSec #Malware #AI

blog.relayshield.netYour AI Coding Credentials Are Now Infostealer Targets | RelayShieldThere's a new item on the infostealer shopping list. It's not your bank password. It's your Claude API key. Symantec's Threat Hunter team reported on October 15 that the newest Aoki...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Possible Phishing 🎣
on: ⚠️hxxps[:]//docs[.]google[.]com/presentation/d/e/2PACX-1vRolxFAW7hyzfBrqjLicr37CaJihNGZ0r-rAqdHi98FAi1N9sEk0uARbExM-_b77QgVlcphzXXU6qb5/pub?start=false&loop=false&delayms=3000
🧬 Analysis at: https://urldna.io/scan/6ad766133b775000091c1a83
#cybersecurity #phishing #infosec #urldna #scam #infosec

Media attachment
urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test

↩ Reply ♡ 0 · ↻ 0 ↗ Original

AI spending shifts beyond IT, testing CIO-CFO decision rights

💡 Corporate AI spending has doubled to 3.3% of revenue, but 80% sits outside traditional IT budgets. CIOs, CFOs, and business leaders must collaborate through formal councils with clear accountability: business leaders own outcomes, CFOs manage finances, CIOs oversee tech. Unified governance and transparency are essential for maximizing AI's business impact.
https://www.techtarget.com/it-strategy/news/366651960/AI-spending-shifts-beyond-IT-testing-CIO-CFO-decision-rights

#InfoSec #CyberSecurity #AI

IT StrategyAI spending shifts beyond IT, testing CIO-CFO decision rights | TechTargetWith 80% of AI spending outside IT, CIOs and CFOs are redefining who controls architecture, capital allocation and accountability for value.
↩ Reply ♡ 0 · ↻ 0 ↗ Original