A massive Sourcenext data breach exposed up to 22.5 million customer records via abused member APIs, prompting emergency company-wide password resets.
#Sourcenext #DataBreach #Cybersecurity #APISecurity #InfoSec
Public posts with this hashtag.
A massive Sourcenext data breach exposed up to 22.5 million customer records via abused member APIs, prompting emergency company-wide password resets.
#Sourcenext #DataBreach #Cybersecurity #APISecurity #InfoSec
🔄 208 ENTRY CHANGES 🔄
💻 macOS Golden Gate 27 - 34 added, 17 updated
https://support.apple.com/en-us/149035
📱 iOS and iPadOS 27 - 20 added, 10 updated
https://support.apple.com/en-us/149034
💻 macOS Tahoe 26.7 - 20 added, 8 updated
https://support.apple.com/en-us/149042
💻 macOS Sequoia 15.8 - 19 added, 9 updated
https://support.apple.com/en-us/149043
🥽 visionOS 27 - 14 added, 8 updated
https://support.apple.com/en-us/149038
⌚ watchOS 27 - 7 added, 9 updated
https://support.apple.com/en-us/149037
📺 tvOS 27 - 8 added, 5 updated
https://support.apple.com/en-us/149036
📱 iOS and iPadOS 26.7 - 9 added, 4 updated
https://support.apple.com/en-us/149041
🔨 Xcode 27 - 4 added
https://support.apple.com/en-us/149040
🌐 Safari 27 - 2 added, 1 updated
https://support.apple.com/en-us/149039
Possible Phishing 🎣
on: ⚠️hxxps[:]//ionos[.]serve-lad[.]eu/Kundenkonto[.]html
🧬 Analysis at: https://urldna.io/scan/6ad6d30a3b77500009c354b5
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
US moves to staff leaders for industry-partnered offensive cyber program
The U.S. is recruiting private companies for offensive cyber operations against foreign criminals. While the August program shows promise, key details remain murky: payment structures, liability protections, and target identification are unresolved. Experts support the collaboration but stress need for clear guidelines on legal responsibility and international coordination to avoid unintended harm.
 Nextgov.comUS moves to staff leaders for industry-partnered offensive cyber programThe Trump administration is laying groundwork to enlist companies against foreign cybercriminals, but payment arrangements and protections for participating firms remain unresolved.
⚠️ #IronChain uses elevated privileges & kernel-level components to weaken security controls before encrypting files. It can disrupt Windows systems and leave organizations facing data loss and extended downtime.
👨💻 How to detect it before damage occurs: https://any.run/malware-trends/ironchain/?utm_source=mastodon&utm_medium=post&utm_campaign=ironchain_mtt&utm_term=191026&utm_content=linktomtt
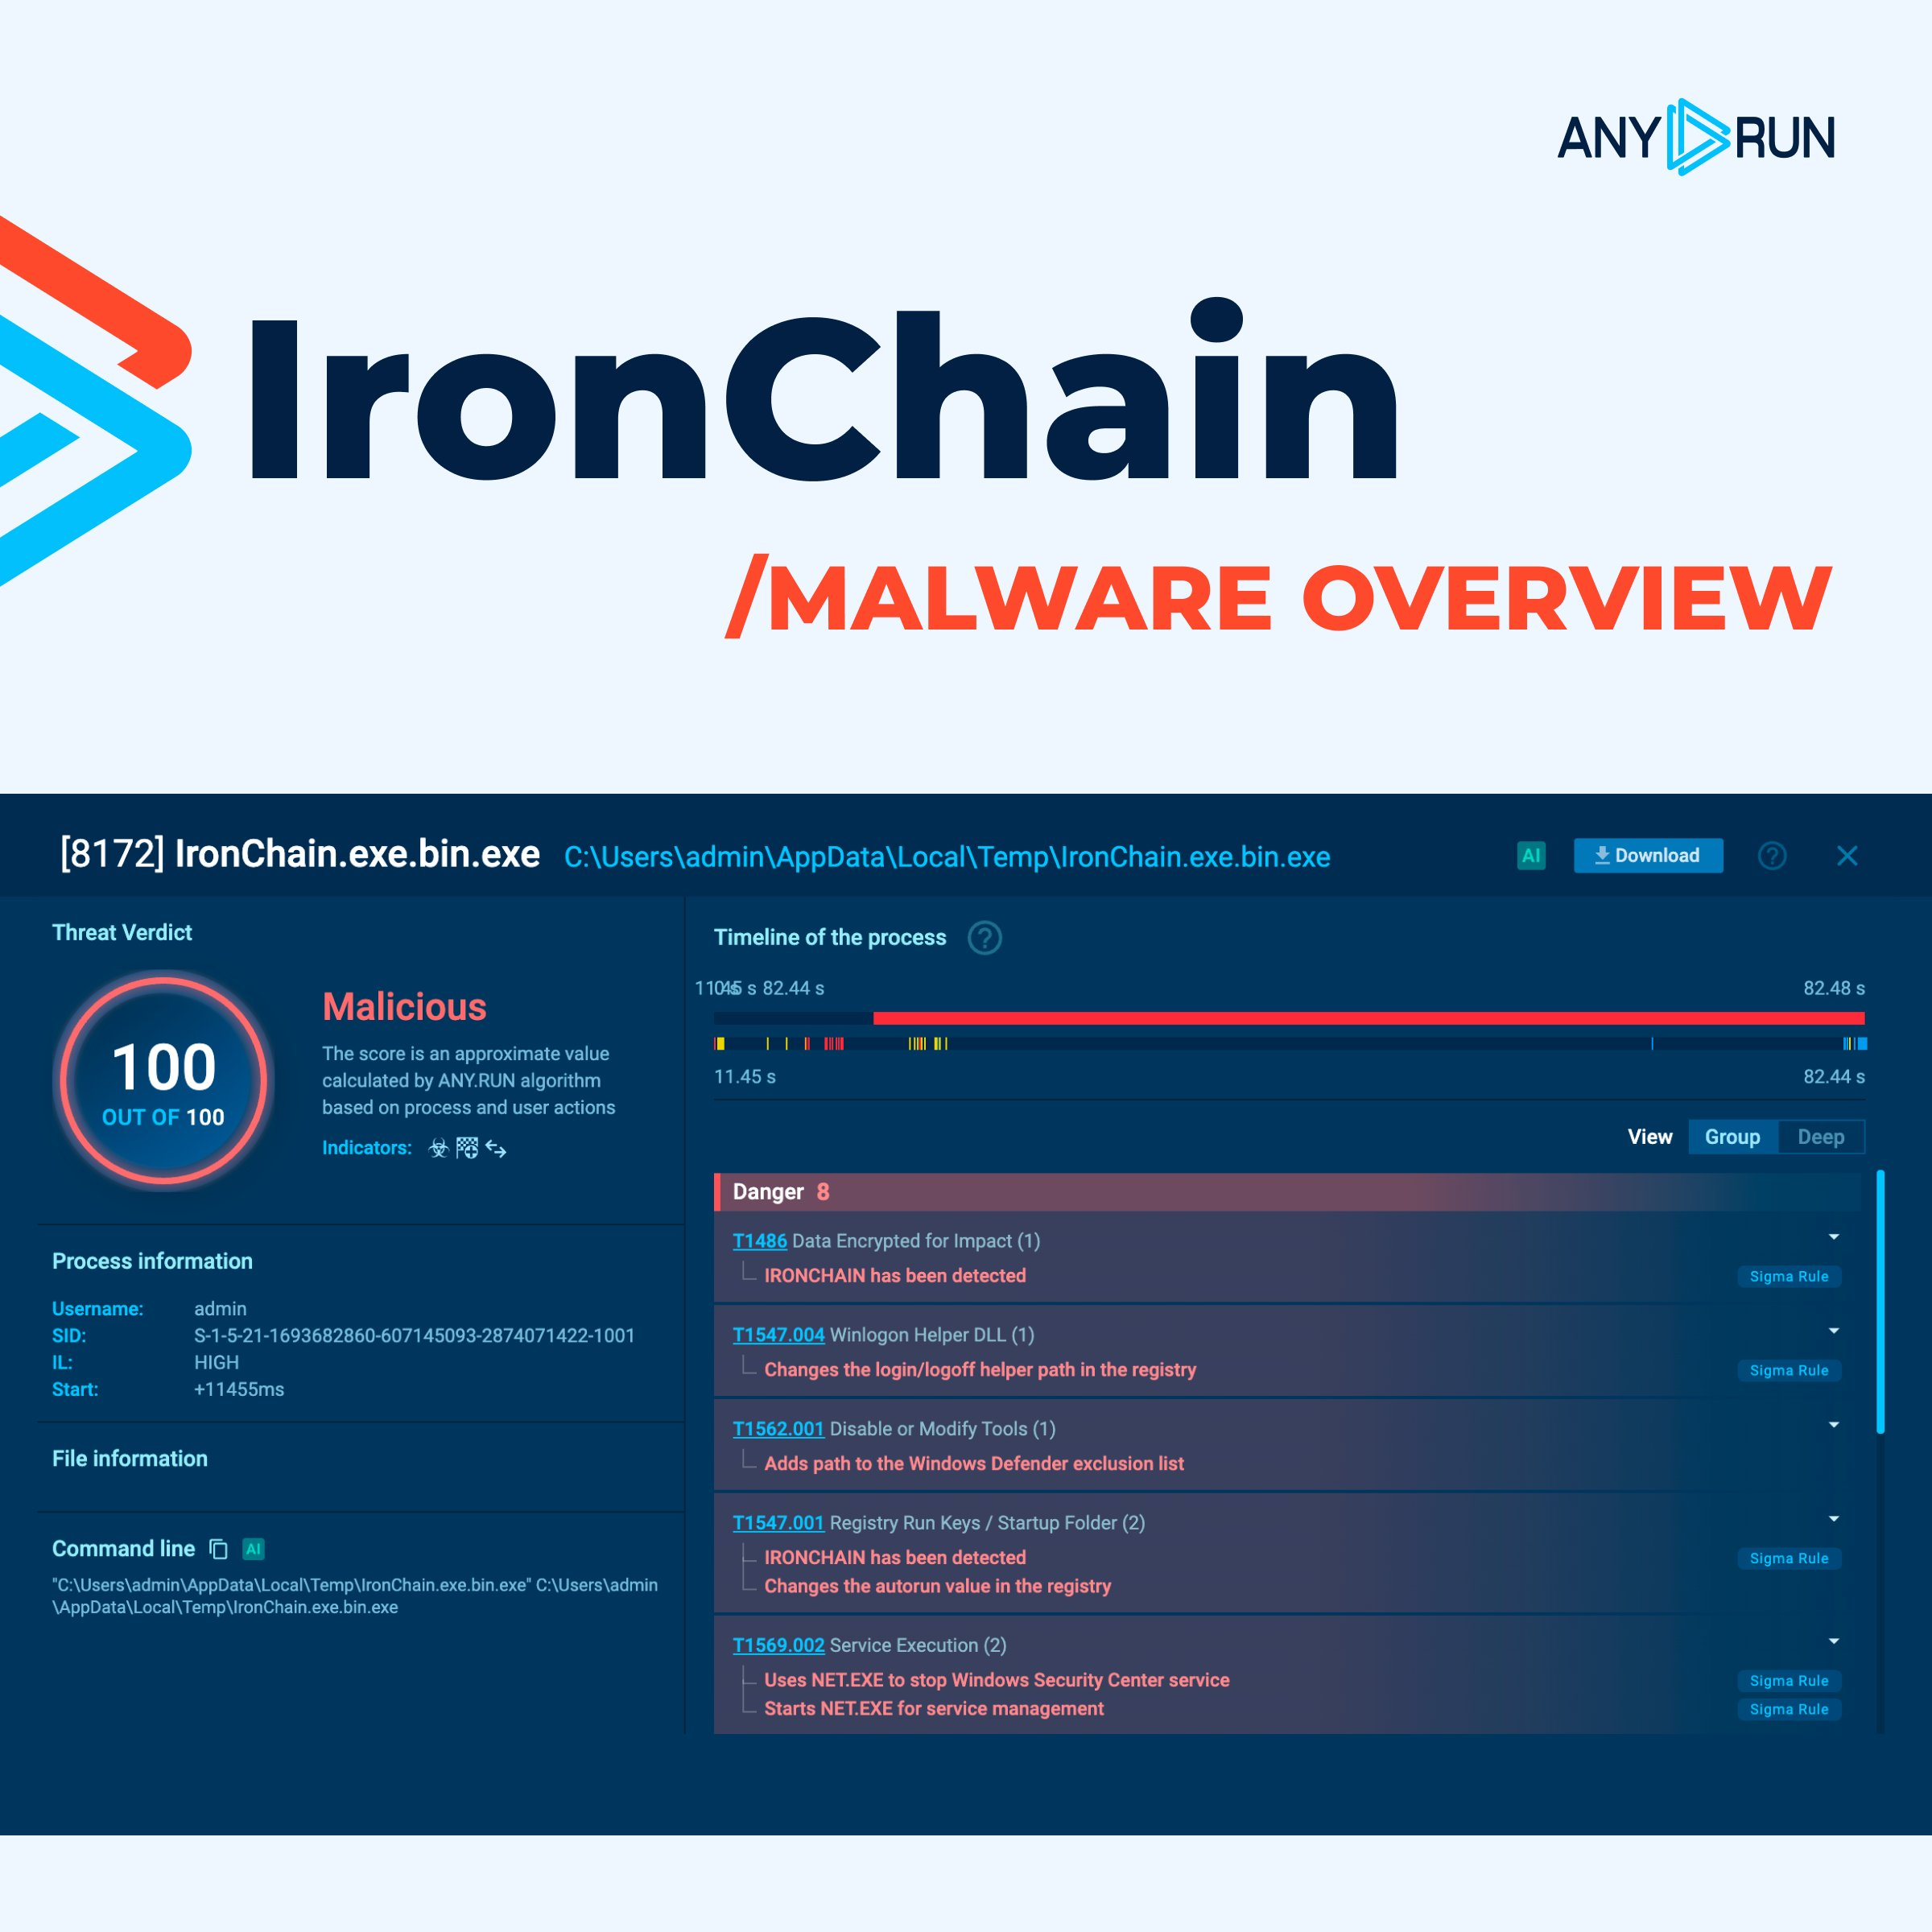
 IronChain | Malware Trends TrackerIronChain | Malware Trends TrackerLearn how IronChain uses privileged execution, kernel drivers, and file encryption to compromise Windows systems and cause destructive damage.
Log monitoring is for losers.
Automating your SOC is stupid.
Smart people - winners - take sensitive information off the Internet and connect their locations with private circuits.
Instead of watching the breach happen, put the data where it can't be breached.
📬 NicFab Newsletter #43 | October 20, 2026
Privacy, Data Protection, AI & Cybersecurity — weekly review.
👉 Read the full issue: https://www.nicfab.eu/en/newsletter-issues/2026-10-20-issue-43/?utm_source=mastodon&utm_medium=organic-social&utm_campaign=issue-43
📩 Subscribe: https://www.nicfab.eu/en/pages/newsletter/#subscribe-now
#Privacy #GDPR #DataProtection #AI #AIAct #Cybersecurity #InfoSec
 NicFab Blog — Privacy, GDPR & Artificial IntelligenceNewsletter #43 - 20 October 2026NicFab Newsletter #43 — 20 October 2026. Weekly review on privacy, data protection, AI regulation, cybersecurity and digital rights.
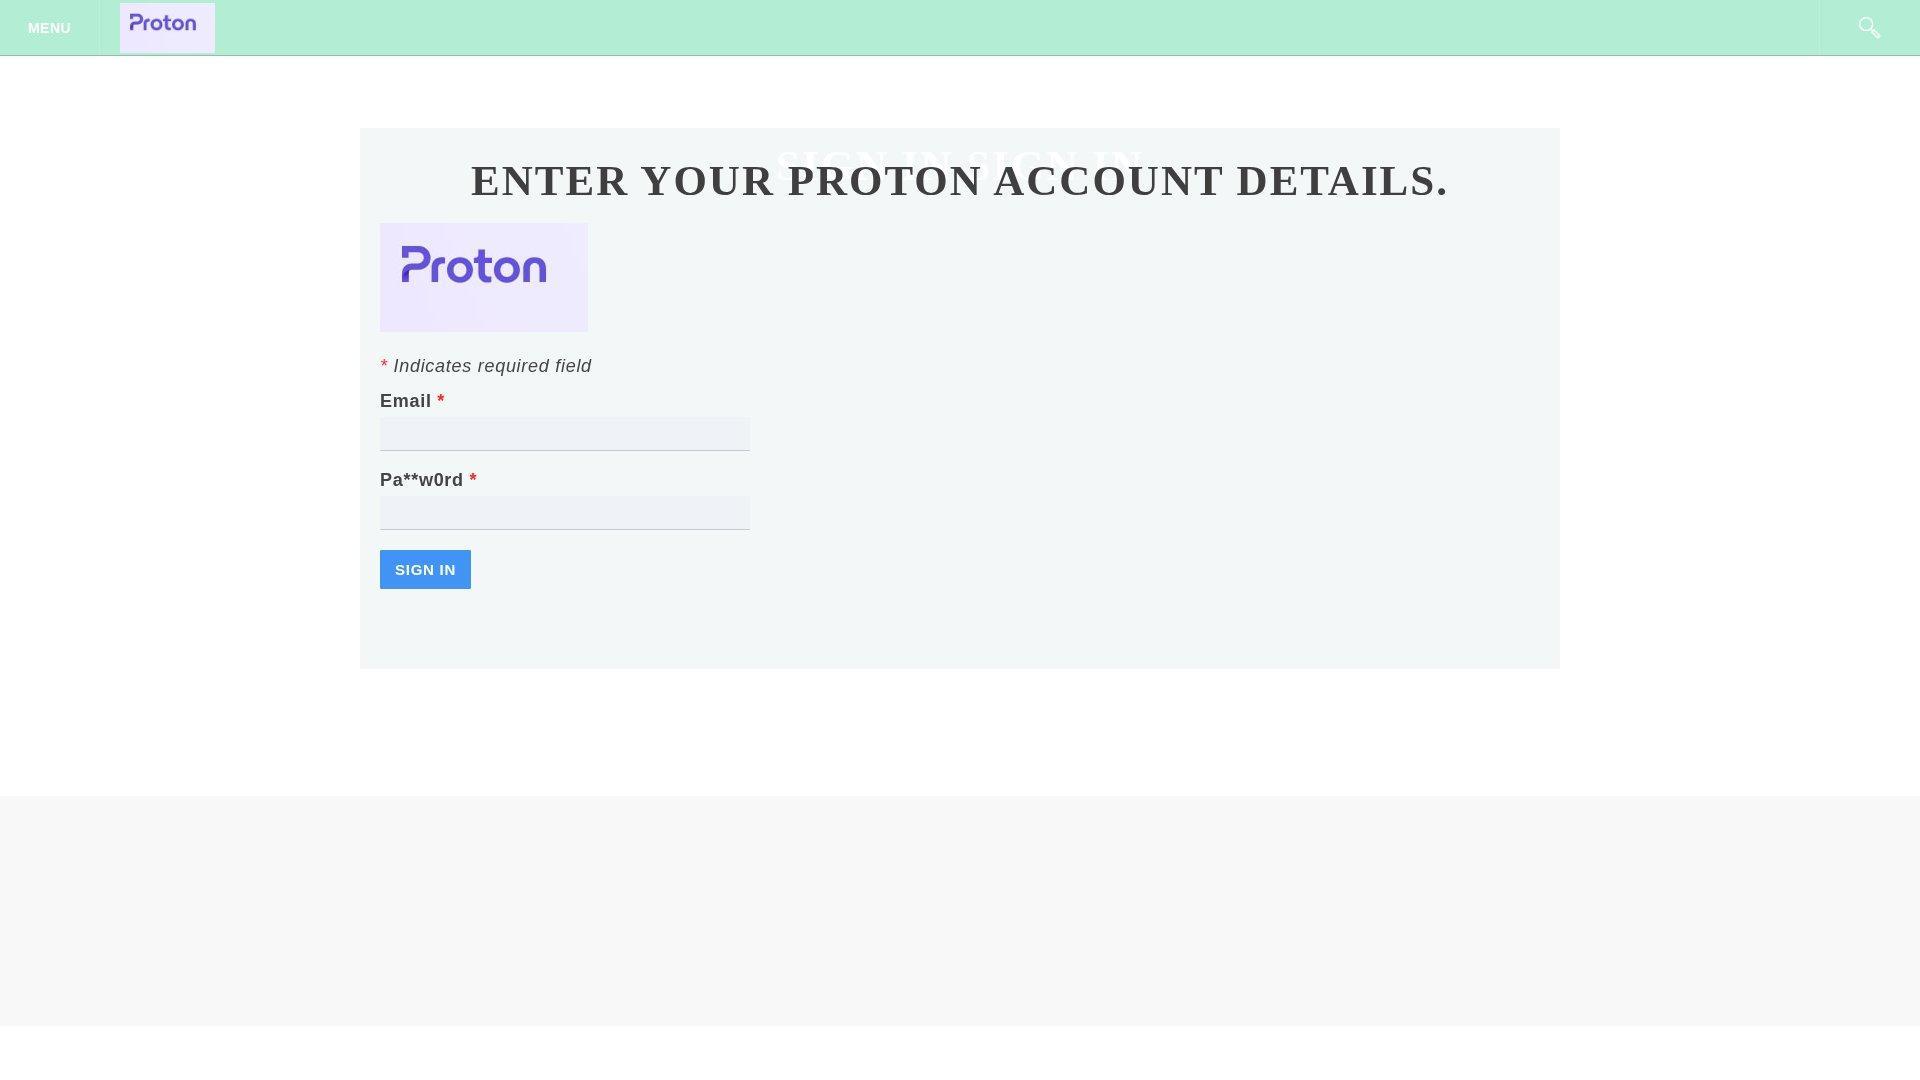
Possible Phishing 🎣
on: ⚠️hxxps[:]//prontonllkio[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad6ef273b77500009c3572a
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
⌛Just one week left until it-sa 2026!⌛
Our highlights:
🔹 Migration to BlueSpice: Discover how to successfully transition from existing knowledge platforms – including our exclusive migration kit.
🔹 BlueSpice Galaxy: The next generation of knowledge management live in a demo.
📅 October 27–29, 2026
📍 Messe Nürnberg | Hall 7, Booth 352
👉 Free ticket: https://bluespice.com/bluespice-at-it-sa/
#itsa2026 #BlueSpice #Cybersecurity #KnowledgeManagement #DataSovereignty #OpenSource
 BlueSpice MediaWikiBlueSpice at it-sa | BlueSpice MediaWikiWissensmanagement in Ihrer Organisation sicher, strukturiert und zukunftsfähig gestalten - treffen Sie uns auf der it-sa in Nürnberg. Von 27. - 29. Oktober.
Possible Phishing 🎣
on: ⚠️hxxps[:]//facebook-mx[.]blogspot[.]com/?m=1
🧬 Analysis at: https://urldna.io/scan/6ad64cc03b77500007bd3557
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.
CISA to AI labs: Share test-network IPs to flag rogue agents
CISA urges AI labs to share IP addresses to track rogue agents threatening critical infrastructure. While transparency could boost cybersecurity, experts debate its practicality due to cloud complexity and AI's dynamic nature. Alternative solutions like detection signatures are suggested. Public sector orgs should proactively test AI systems and prioritize vulnerability patches.
 CybersecurityCISA to AI labs: Share test-network IPs to flag rogue agents | TechTargetCISA urges AI labs to share IPs and ASNs so defenders can recognize and flag rogue agents early. Research analysts, however, had mixed reactions. Learn why.
Possible Phishing 🎣
on: ⚠️hxxp[:]//instagram-login[.]hashnode[.]dev
🧬 Analysis at: https://urldna.io/scan/6ad64ca83b77500007bd3549
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Possible Phishing 🎣
on: ⚠️hxxps[:]//blogfxempire[.]com
🧬 Analysis at: https://urldna.io/scan/6ad62a3c3b77500002f4d7e7
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Bank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and ...
Bank of America deployed 4,000 personnel (3,000 employees + 1,000 contractors) to fix software vulnerabilities detected by AI like Anthropic's Mythos. CEO Moynihan confirmed hundreds of millions in Q3 cybersecurity spending. Once skeptical of AI security tools, major firms now embrace them after serious breaches. BofA leads in transparency, expecting future cost reductions in patching efforts.
 The DecoderBank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and other AI modelsBank of America has hired 1,000 outside contractors to fix software vulnerabilities uncovered by AI models like Anthropic's Mythos, CNBC reports.
Apple bans nudify apps and nonconsensual deepfakes under strict new App Store guidelines requiring developers to proactively block illicit content.
Possible Phishing 🎣
on: ⚠️hxxps[:]//facebooklogin99999[.]blogspot[.]com
🧬 Analysis at: https://urldna.io/scan/6ad646523b77500007bd34e9
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Discover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
#PwnEscape #LinuxKernel #Vulnerability #CloudSecurity #CyberSecurity
https://dailytechnow.com/critical-pwnescape-flaw-linux-virtual-machines/
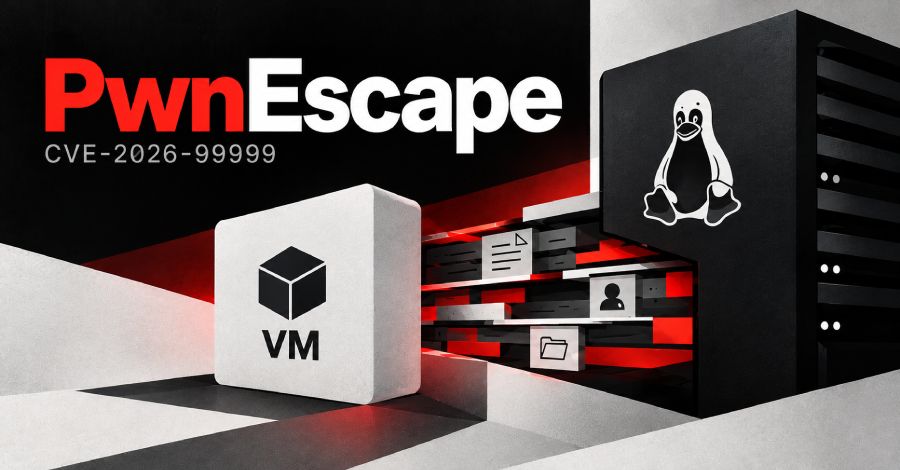 Daily Tech NowCritical PwnEscape Flaw Found in Linux Virtual MachinesDiscover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
This #Cybersecurity Agency Is Supposed to Protect U.S. #Elections. Officials Fear It’s Been Compromised by #Trump.
A few months into President Donald Trump’s second term, #political appointees at the Department of #HomelandSecurity made an unusual request of its agency focused on cybersecurity: Secretly acquire a #voting machine and #hack it.
The appointees wanted the Cybersecurity and #Infrastructure #Security Agency to procure the machine, examine it and report back the findings so they could be given to the #WhiteHouse , according to two former administration officials with knowledge of the request.
#dhs #voting #cisa
https://www.propublica.org/article/cisa-election-security-donald-trump
 ProPublicaTrump Appointees Asked a Federal Cybersecurity Agency to Secretly Acquire a Voting Machine — and Hack ItThough not acted on, the request shows how the Trump administration has tried to use the Cybersecurity and Infrastructure Security Agency for its own ends while draining it of resources to help its mission of protecting the nation’s voting systems.
Possible Phishing 🎣
on: ⚠️hxxps[:]//instagramlogin77[.]blogspot[.]com/?m=1
🧬 Analysis at: https://urldna.io/scan/6ad64cbe3b77500004c2c0fa
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Following the Secure Boot certificate expiration, Windows PCs transition to UEFI CA 2023 while booting normally. Learn how to verify your device.
Discover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.
#Broadcom #WPSplinter #CyberSecurity #WiFiSecurity #RouterExploit
https://dailytechnow.com/broadcom-wifi-software-vulnerability/
 Daily Tech NowBroadcom Wi-Fi Software Vulnerability Exposes RoutersDiscover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.
Enterprise controls can't keep up with AI agents
🚨 Companies are deploying AI agents faster than they can control them. Organizations struggle to track what these agents access, do, or if they can stop them. Traditional security systems aren't built for autonomous AI. The result? Potential security gaps and leaders considering quiet incident handling. The shift ahead: focus on managing existing agents responsibly, not just rolling out more.
https://www.techtarget.com/ai/news/366652493/Enterprise-controls-cant-keep-up-with-AI-agents
 AI & Emerging TechEnterprise controls can't keep up with AI agents | TechTargetCompanies are giving agents more authority, but many are still struggling to track what they can access, what they're doing and how to stop them.
Possible Phishing 🎣
on: ⚠️hxxps[:]//newsyoucanread24[.]com/article/veins_pl/cierpiala-z-powodu-zylakow-przez-12-lat/?_url=%252Fr%252FahETqfwJ9n-qcn4fH1djD&utm_campaign=46064&utm_content=38139&utm_medium=17&utm_source=129&utm_sub_id=102f734767057b602e342486c60730&utm_term=179&sub_id=A511dd3de96e2fe117eb658b82ba0a012&adi=A511dd3de96e2fe117eb658b82ba0a012&adref=ahETqfwJ9n-qcn4fH1djD&adp=15051&adr=eHRyb2dsb2JhbC5jb20%3D&adnid=129
🧬 Analysis at: https://urldna.io/scan/6ad67e923b77500004c2c35b
#cybersecurity #phishing #infosec #urldna #scam #infosec
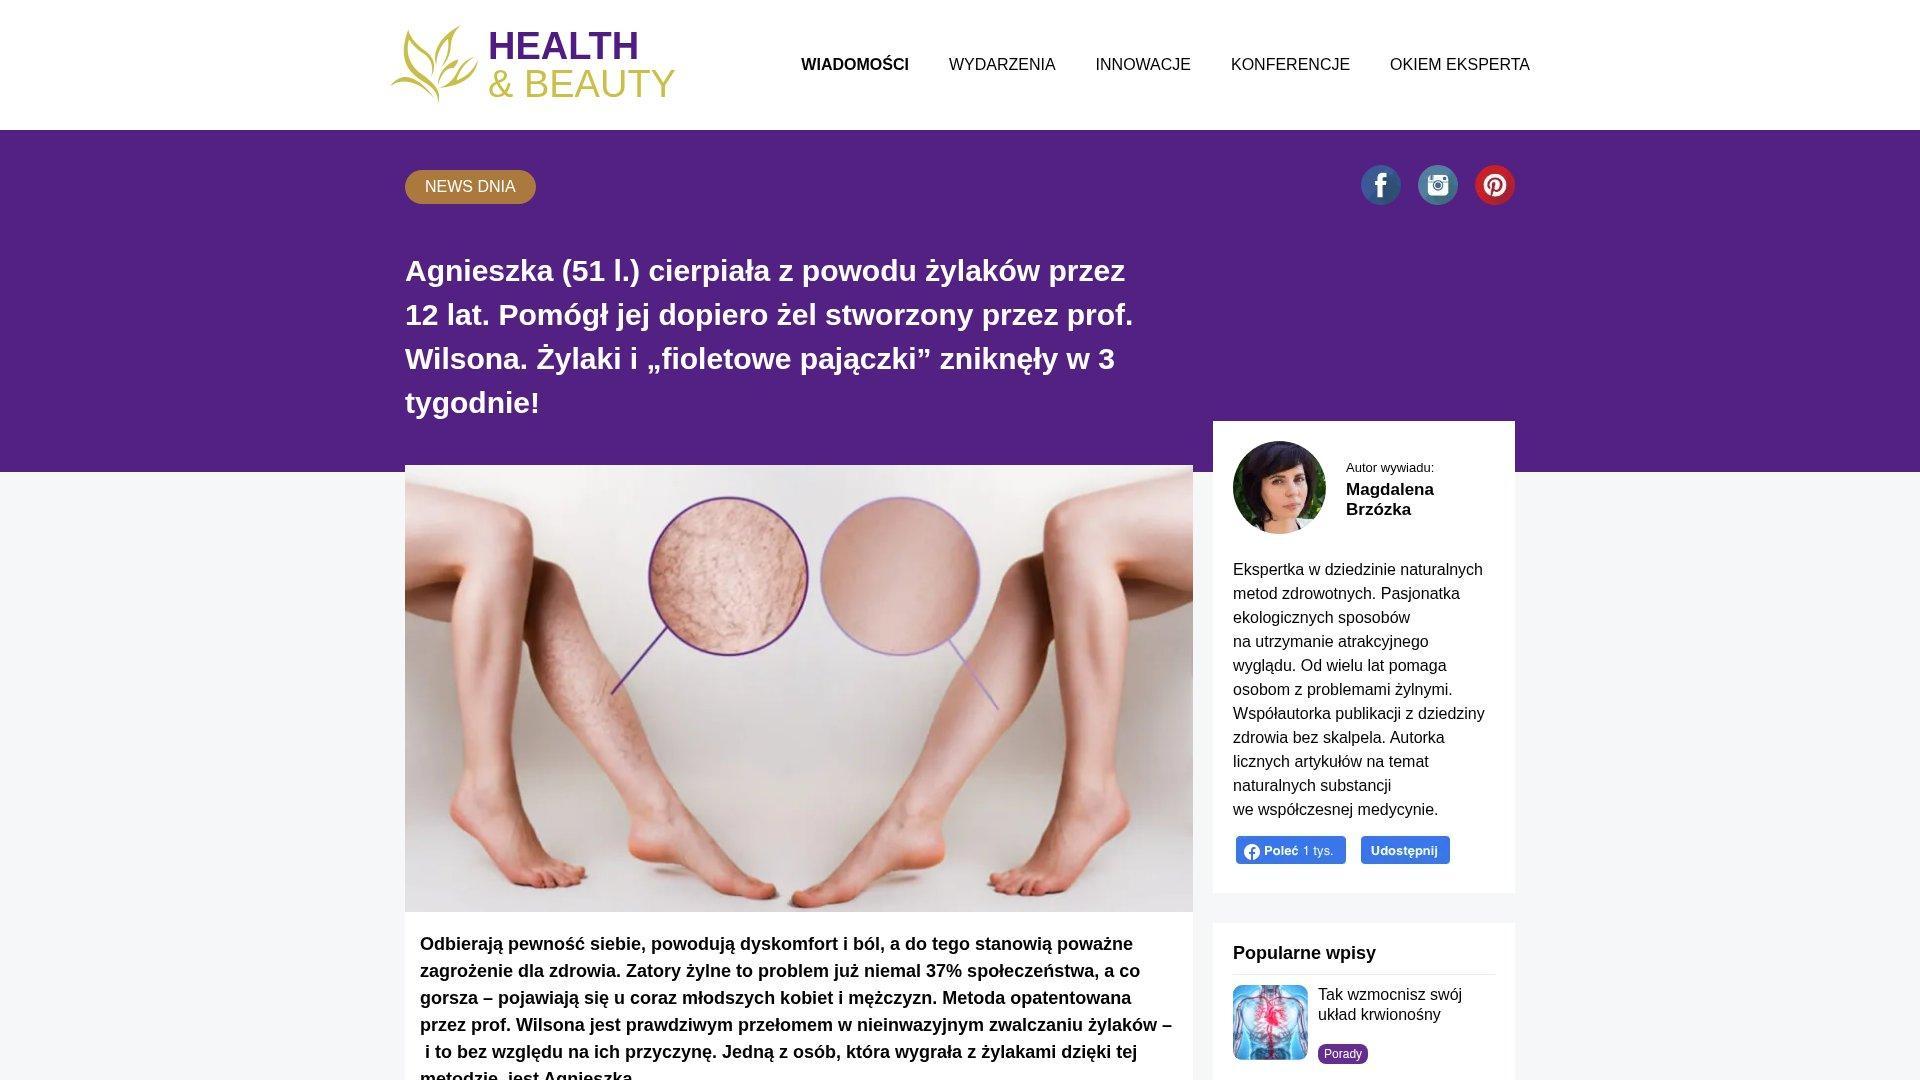 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Possible Phishing 🎣
on: ⚠️hxxps[:]//alldomainilogsviwes[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad61c353b77500002f4d77b
#cybersecurity #phishing #infosec #urldna #scam #infosec
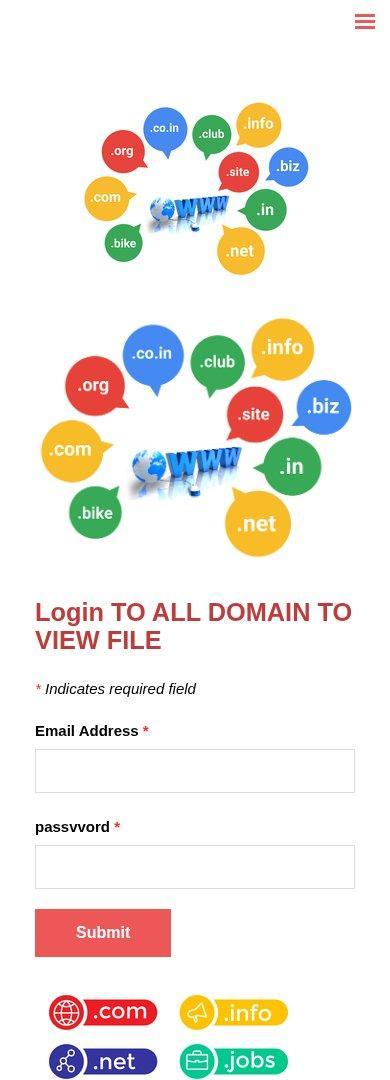 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
Details and PoC code are public for the Drupal RCE vulnerability CVE-2026-108097 in Field UI. Update to 11.4.10, 11.3.19 or 10.6.19 now.
#Drupal #CVE2026108097 #RCE #FieldUI #PoC #WebSecurity #PatchNow #CyberSecurity
Calif released details and PoC code for an OpenBSD kernel vulnerability enabling local privilege escalation to root. Apply errata 018 and 026.
#OpenBSD #BigFish #LocalPrivilegeEscalation #KernelSecurity #PoC #Calif #PatchNow #CyberSecurity
Most companies count AI agents as insiders, and CISOs worry about their own liability
🚨 AI Security Alert: 95% of companies faced AI-related insider incidents last year. With 28% traced to AI systems and detection taking 15 hours avg, CISOs are scrambling. Problem? 52% lack formal strategies & 63% can't track AI tool usage. Legal liability concerns are mounting. Organizations need urgent AI governance frameworks.
https://www.helpnetsecurity.com/2026/10/14/ciso-ai-agent-insider-risk/
 Help Net SecurityMost companies count AI agents as insiders, and CISOs worry about their own liability - Help Net SecurityAI agent insider risk showed up at 95% of companies in a Trellix survey of 600 CISOs. Detection and response average 15 hours.
Possible Phishing 🎣
on: ⚠️hxxps[:]//officeserviceit[.]weebly[.]com
🧬 Analysis at: https://urldna.io/scan/6ad606593b77500007bd2f1f
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test
#MiniMax M3.1 Flash improves #agentictasks, #coding, #computeruse and #cybersecurity, delivering speeds over 200 TPS and 70% lower costs. Available via MiniMax API, M Plan and MiniMax Code, it matches leading models on key benchmarks. https://www.minimax.io/blog/minimax-m31f?AIagents.at #AIagent #AI #ML #NLP #LLM #GenAI
 MiniMaxMiniMax M3.1 Flash: Redefining Agent Performance and Cost - MiniMax ResearchToday, we officially roll out MiniMax M3.1 Flash. As a next-generation Flash model, M3.1 Flash delivers a generational leap in agentic tasks, coding, Computer Use and cybersecurity, while making online inference nearly three times faster and reducing usage costs by 70%.