X XFediYour place in the Fediverse
XFEDI

#CyberSecurity

ActivityPub

Public posts with this hashtag.

Formula 1 Team x Cybersecurity company news latest:

ThreatLocker joins Visa Cash App Racing Bulls as official cybersecurity partner

"The team will implement the ThreatLocker Zero Trust Platform across its systems and operations, adding a further layer of protection against cyberattacks, including emerging threats enabled by AI. ThreatLocker provides Zero Trust cybersecurity solutions built to prevent cyberattacks from compromising endpoints, networks, and cloud environments."

#cybersecurity

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Frazer LLP Discloses 2025 Qilin Ransomware Attack and Data Theft

Frazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/frazer-llp-discloses-2025-qilin-ransomware-attack-and-data-theft-k-z-7-2-i/gD2P6Ple2L

BeyondMachinesFrazer LLP Discloses 2025 Qilin Ransomware Attack and Data TheftFrazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

We are deeply sorry for the inconvenience of your arrest and are working to resolve it in 5-7 business years.

Operators: coordinate with law enforcement and monitor for gang retaliation activity following high-profile arrests of affiliated threat actors.

Reward: You've received the Handcuffs of Account Termination. They are Soulbound.

https://www.bitdefender.com/en-us/blog/hotforsecurity/qilin-ransomware-arrested-synnovis-patient-death

#Ransomware #Qilin #Synnovis #CyberSecurity (2/2)

Hot for SecurityPolice arrest Qilin ransomware suspect on holiday, as links made to Synnovis hack that contributed to patient's deathA 28-year-old Russian man has been arrested by German police, suspected of being a key member of the Qilin ransomware gang.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🚨🔑 Hackers breached OpenCode, a popular open-source AI coding tool, breaking into a legacy system it was actually in the process of shutting down. Stolen credentials included OpenAI, Anthropic, and Google API keys that developers had saved to use AI models through the platform. Some users reported unauthorized charges from the hundreds of dollars up past $1,700, with the attack described as a large-scale "distillation attack," using someone else's stolen access to harvest AI model outputs at their expense.

This wasn't a password leak, it's worse. A stolen password gets someone into one account. A stolen API key is more like a live line of credit against your wallet, usable instantly from anywhere, until someone notices the bill.

If you use OpenCode Console, revoke and replace any linked API keys immediately and check your provider billing for anything you didn't authorize.

🔗 https://techcrunch.com/2026/10/19/hackers-hit-ai-coding-tool-opencode-running-up-charges-on-users-ai-accounts/

#Cybersecurity #DataBreach #AI #OpenCode #StaySafe

TechCrunchHackers hit AI coding tool OpenCode, running up charges on users’ AI accounts | TechCrunchOpenCode is an open source AI coding agent that's become a popular alternative to Claude Code and Cursor. But hackers got into part of its online platform and stole some users’ API keys, and the AI tools it turned to for help kept refusing to look at the malicious code.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Sasha here!! @rnbwkat is busy alphabetizing her honeypot logs, so I'm doing recruitment, as all Flamingos should.

18–20 November, Porto. Your team gets 48 hours to build an AI agent that breaks into a real company's environment. On purpose. With a signed scope. Nobody calls legal (honest)

Mentors, AI credits, and a winning build that a real company can actually adopt.

I have one leg and I'd still out-recon most of you. Prove me wrong. 🦩

Read more: https://fixathon.ai/editions/vulnerability-discovery/
or
Apply: fixathon.ai/apply/fixer

#Fixathon #infosec #redteam #Cybersecurity #ai

AI FixathonVulnerability discovery agents | AI FixathonBuild an agent that finds the weak points in real organisations’ internet-facing systems, and see whether their detection notices.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔴 EXPLOITED

SiteGuard, a web firewall used to protect WordPress sites, has a bug (CVE-2026-106931) that hands attackers root. It is already being exploited.

Affects SiteGuard Server Edition before 8.00 Update 5.

Patch now.

https://suriq.io/blog/siteguard-cve-2026-106931-command-injection-root

#CVE #infosec #cybersecurity

Tall smooth barrier wall with a single doorway split through its middle
SuriqSiteGuard CVE-2026-106931: Command Injection to RootCVE-2026-106931 is an actively exploited command injection in SiteGuard Server Edition's default-on feature that gives root or SYSTEM. Patch to 8.00 Update 5.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

Reward: You've received a laminated Certificate of Participation in the 2026 Breach Awareness Seminar. It is not accredited.

https://shattered.io/california-student-data-breach-ets-2026

#DataBreach #Education #CyberSecurity #ETS #StudentData #BreachAlert (3/3)

ShatteredCalifornia Student Data Breach: ETS Hack Explained [2026]ETS exposed California student names, birth dates, addresses, and disability data for 4 months before the state began notifying families on Oct. 16, 2026.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

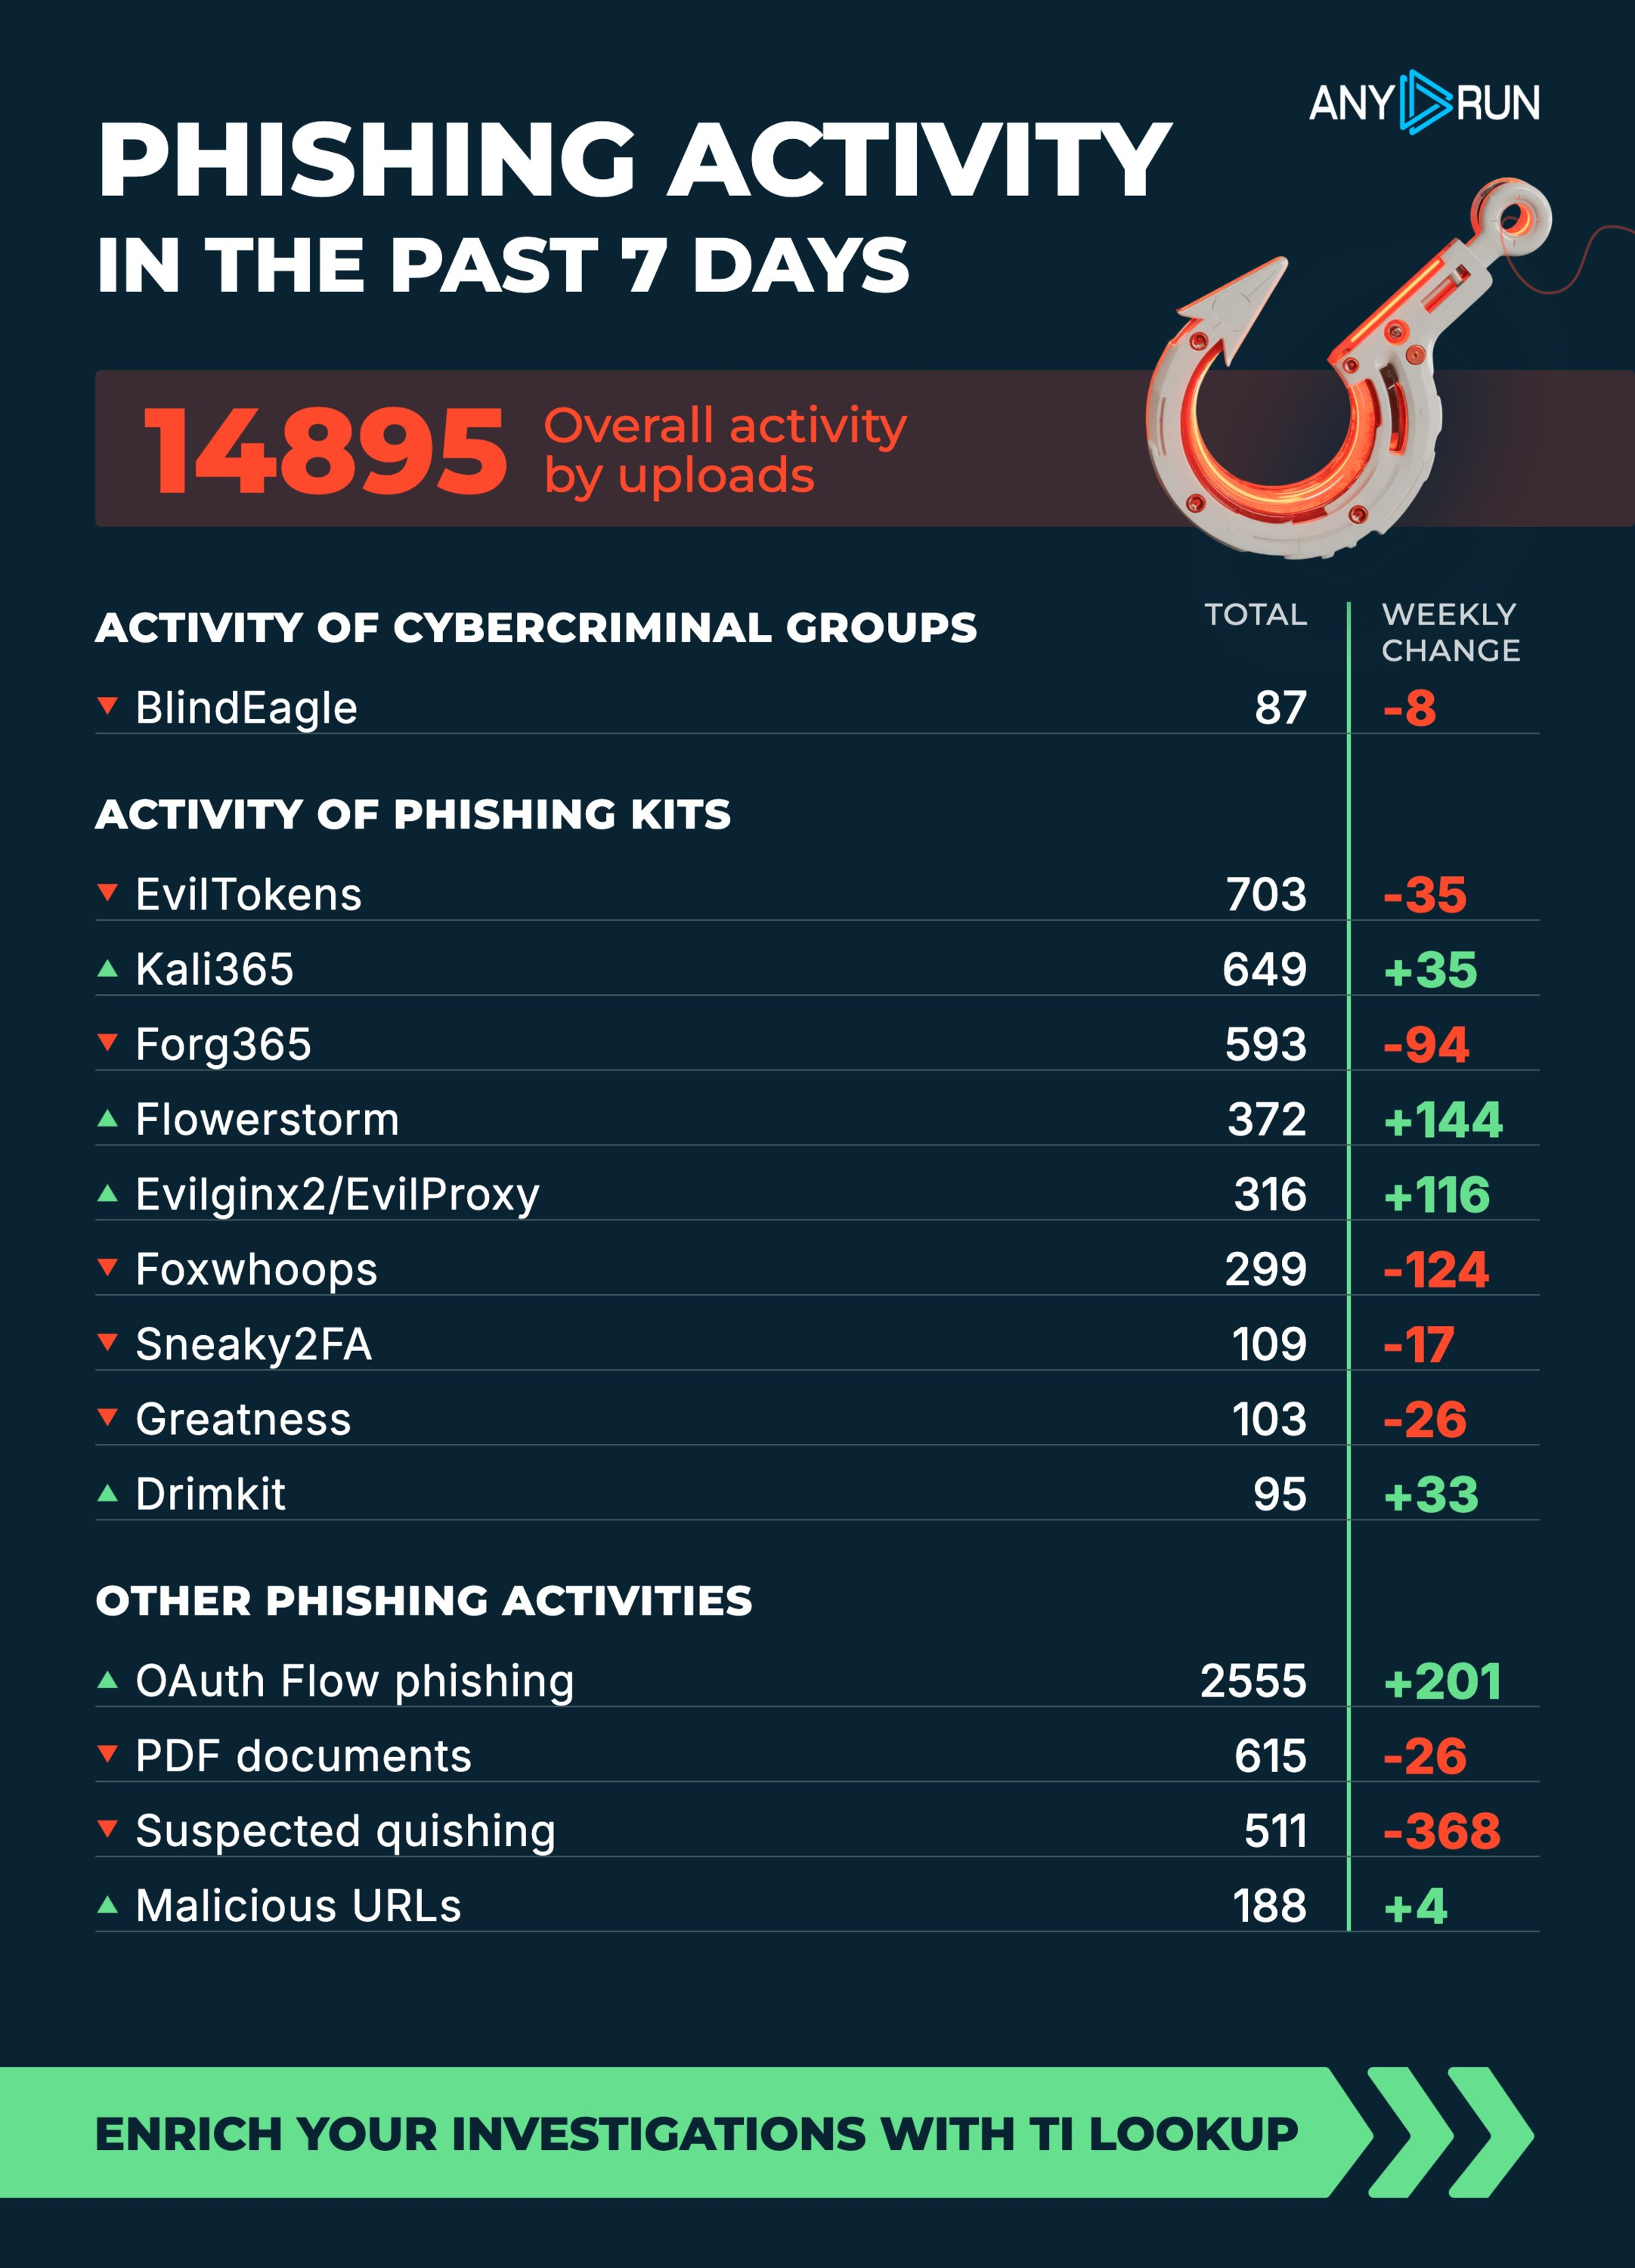
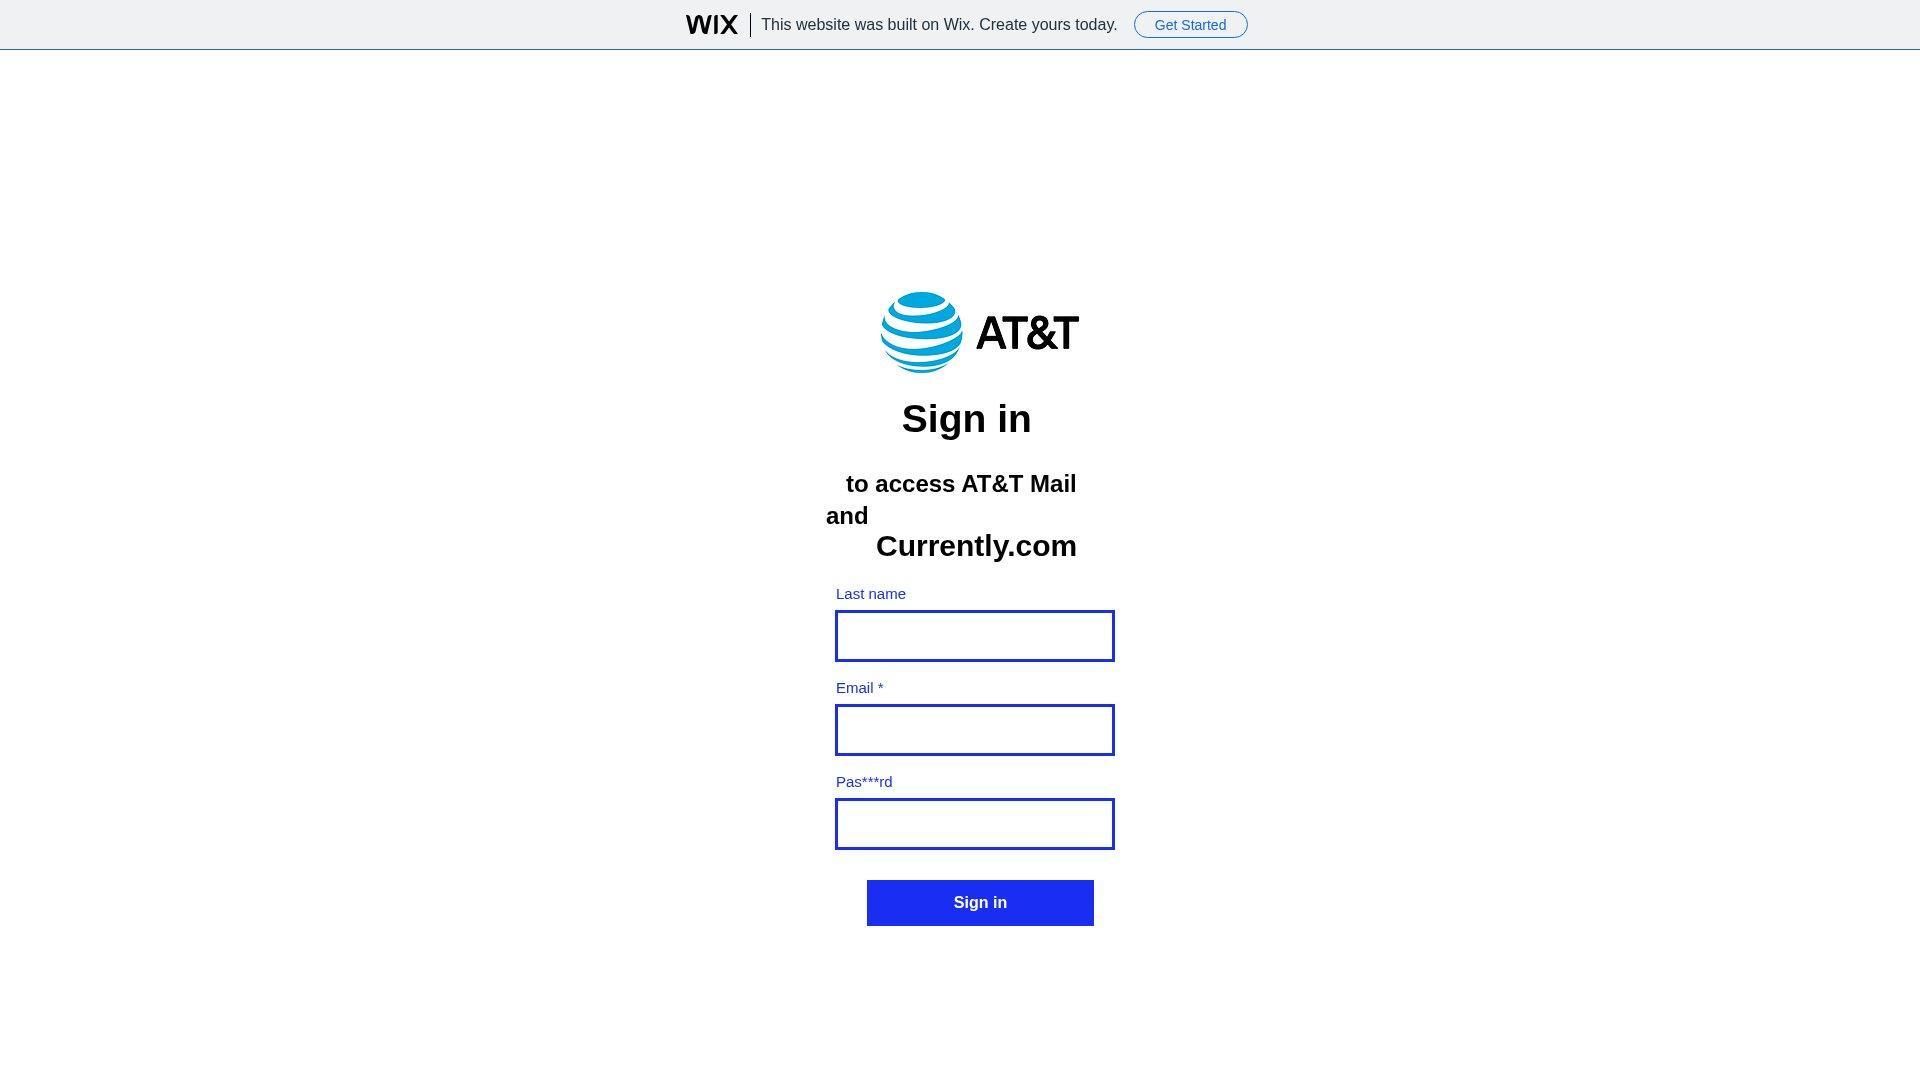
Phishing activity in the past 7 days 🐟
Track latest #phishing threats in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=top_phishing&utm_content=linktoti&utm_term=201026#%7B%2522query%2522:%2522threatName:%255C%2522%5Ephishing$%255C%2522%2522,%2522dateRange%2522:180%7D

#cybersecurity

Media attachment
intelligence.any.runThreat Intelligence Lookup – ANY.RUNSearch and enrich IOCs, get deep threat context, uncover related infrastructure, and investigate threats faster with ANY.RUN TI Lookup.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Ahold Delhaize confirmed on Monday that the outage hitting its websites and apps since 12 October was an attack. The Dutch group behind Albert Heijn, Delhaize, Food Lion and Stop & Shop took the systems offline itself, as a precaution, across most of its European and American brands. Stores stayed open throughout.

The group told the Dutch NCSC within 24 hours of detecting the activity and filed a police report yesterday. No customer data is believed taken, though the investigation continues. It is the second attack in two years; the 2024 incident exposed data on 2.2 million people.

https://newsroom.aholddelhaize.com/ahold-delhaize-update-on-status-of-cybersecurity-incident/

#CyberSecurity #InfoSec #Retail

Ahold Delhaize update on status of cybersecurity incidentAhold Delhaize update on status of cybersecurity incidentZaandam, October 19, 2026  – Ahold Delhaize today announced an update about the cybersecurity issue that was previously disclosed on Monday, October 12, 2026. The update outlines the actions taken since the incident was detected, the progress made in restoring services and the company’s continued cooperation with the relevant authorities....
↩ Reply ♡ 0 · ↻ 0 ↗ Original

F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws

F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.

**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L

BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Tanishq.

Password must contain:
- 6 to 16 characters.
- At least one special character (@, #, $, %, * and & only).
- At least one alphabet.
- At least one number.

https://dumbpasswordrules.com/sites/tanishq/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comTanishq - Dumb Password RulesPassword must contain: - 6 to 16 characters. - At least one special character (@, #, $, %, * and & only). - At least one alphabet. - At least one number.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

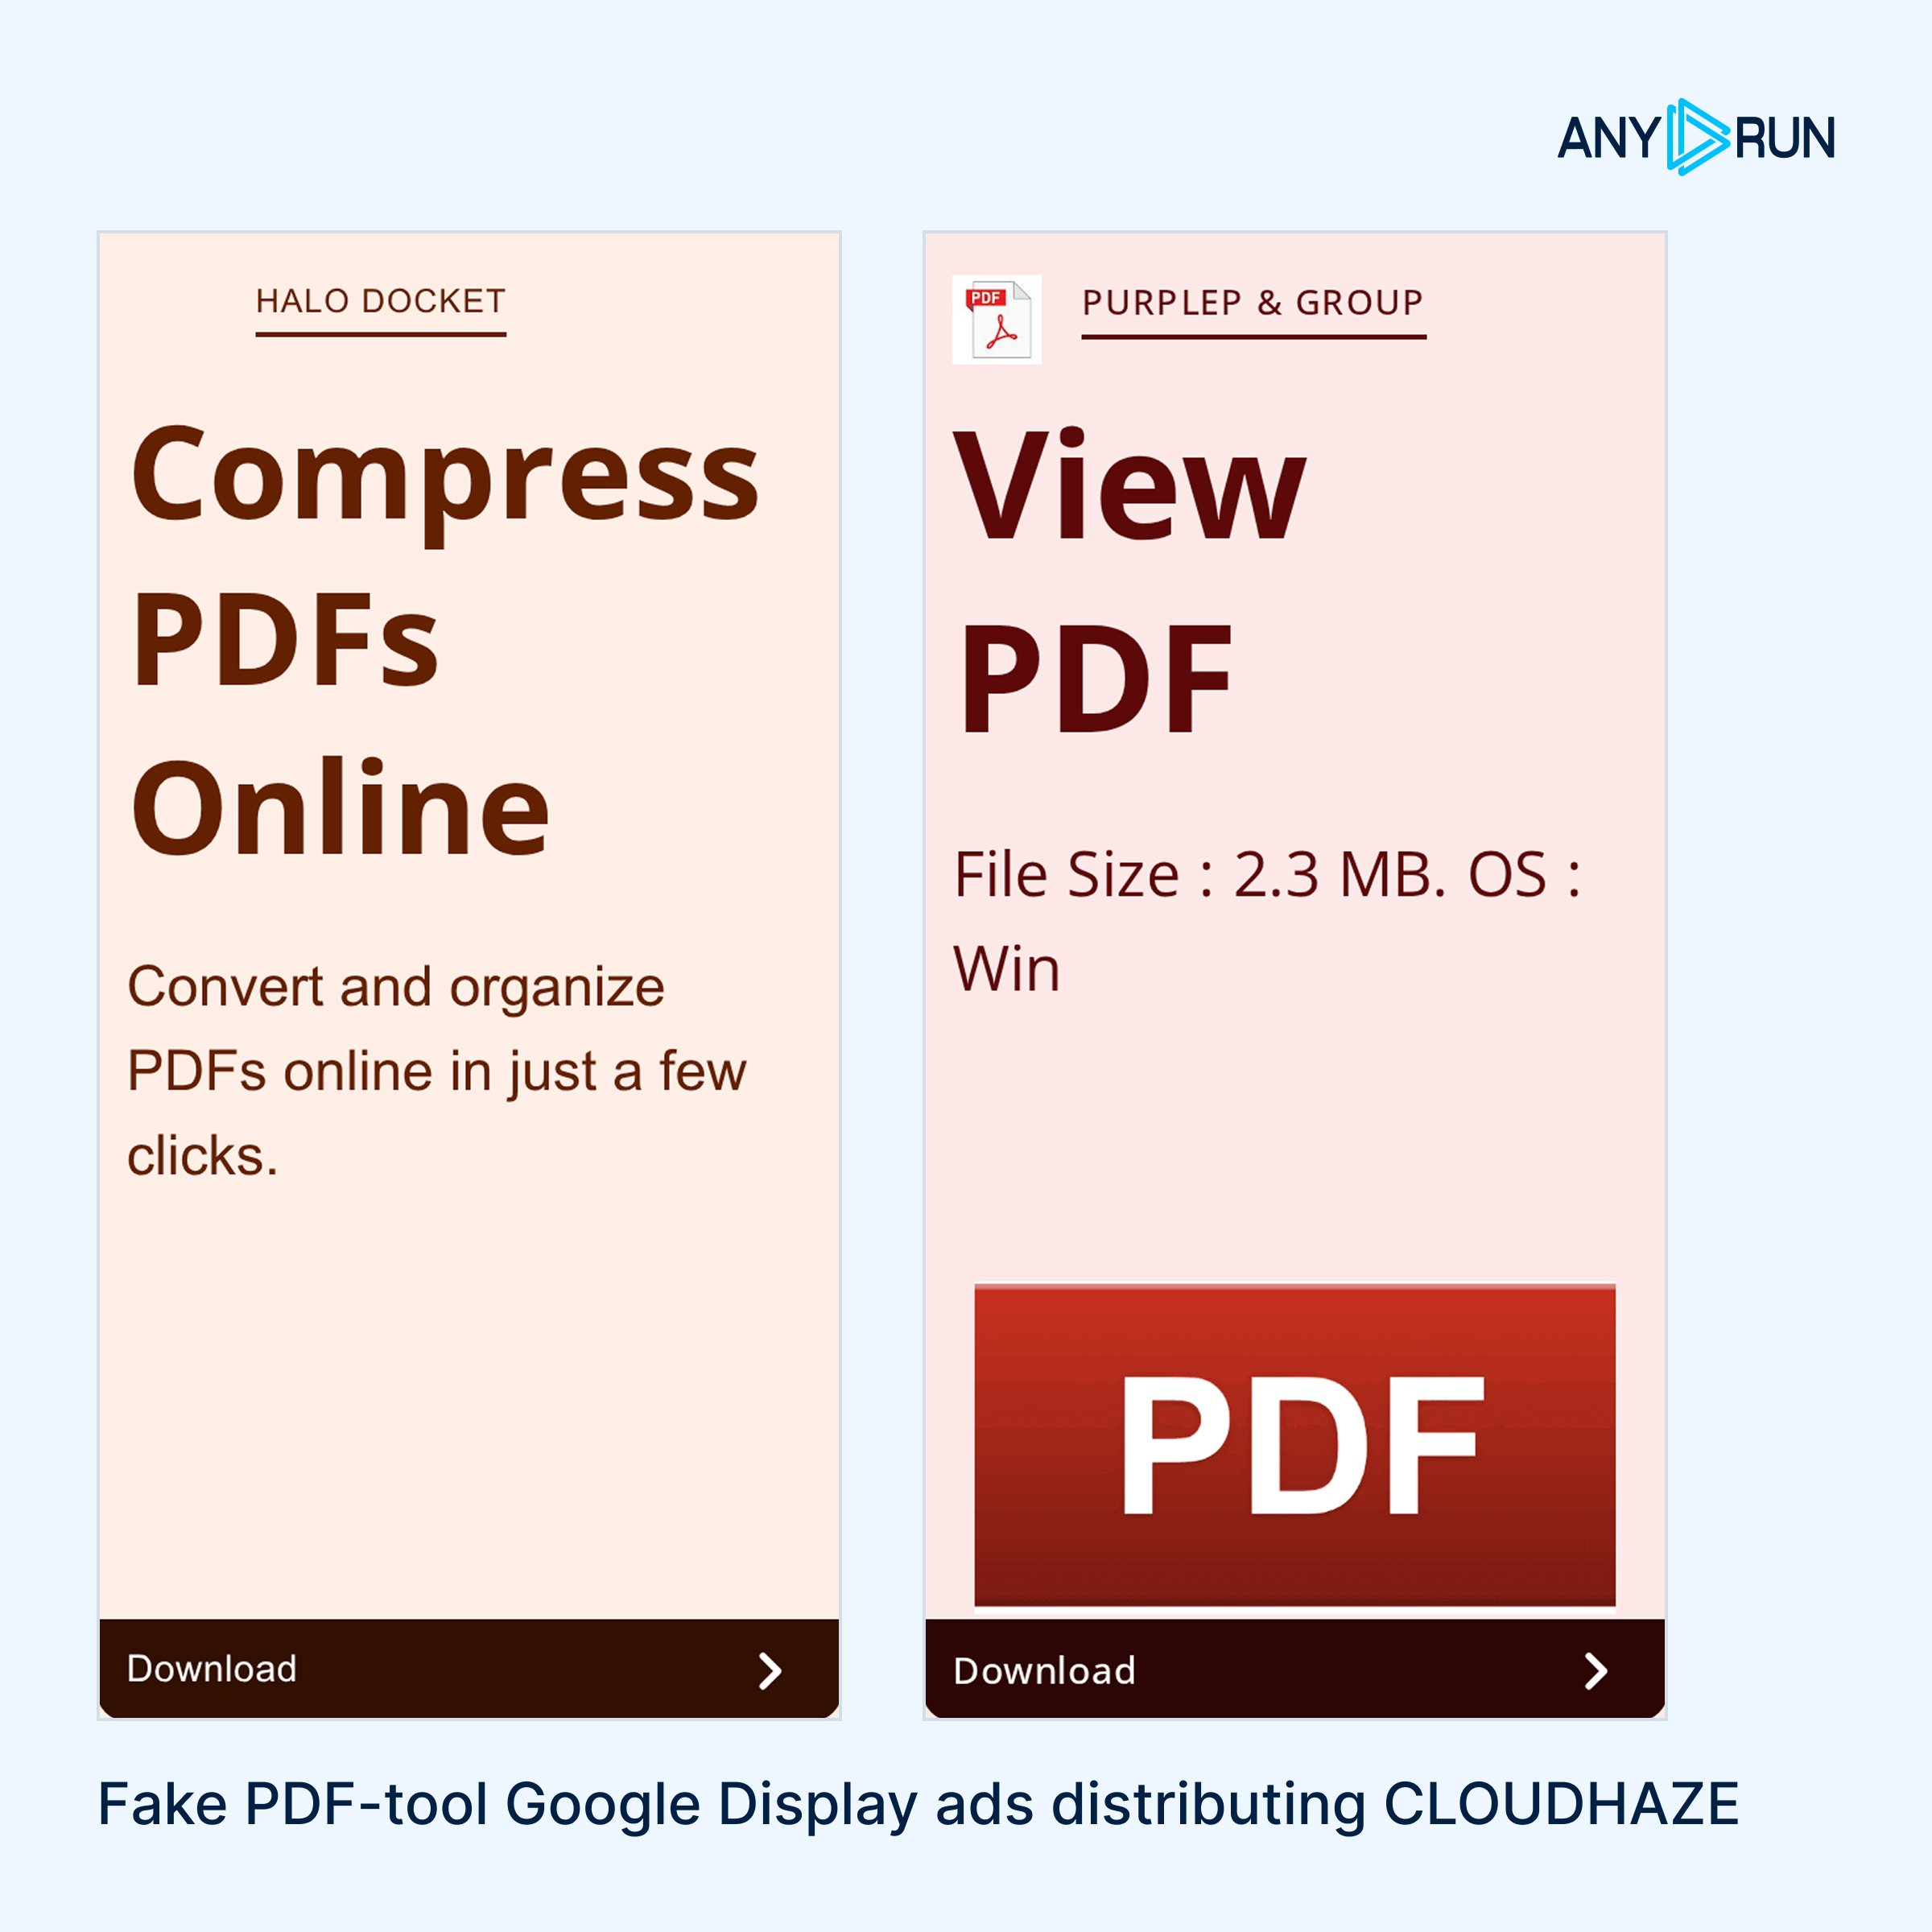
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.

586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.

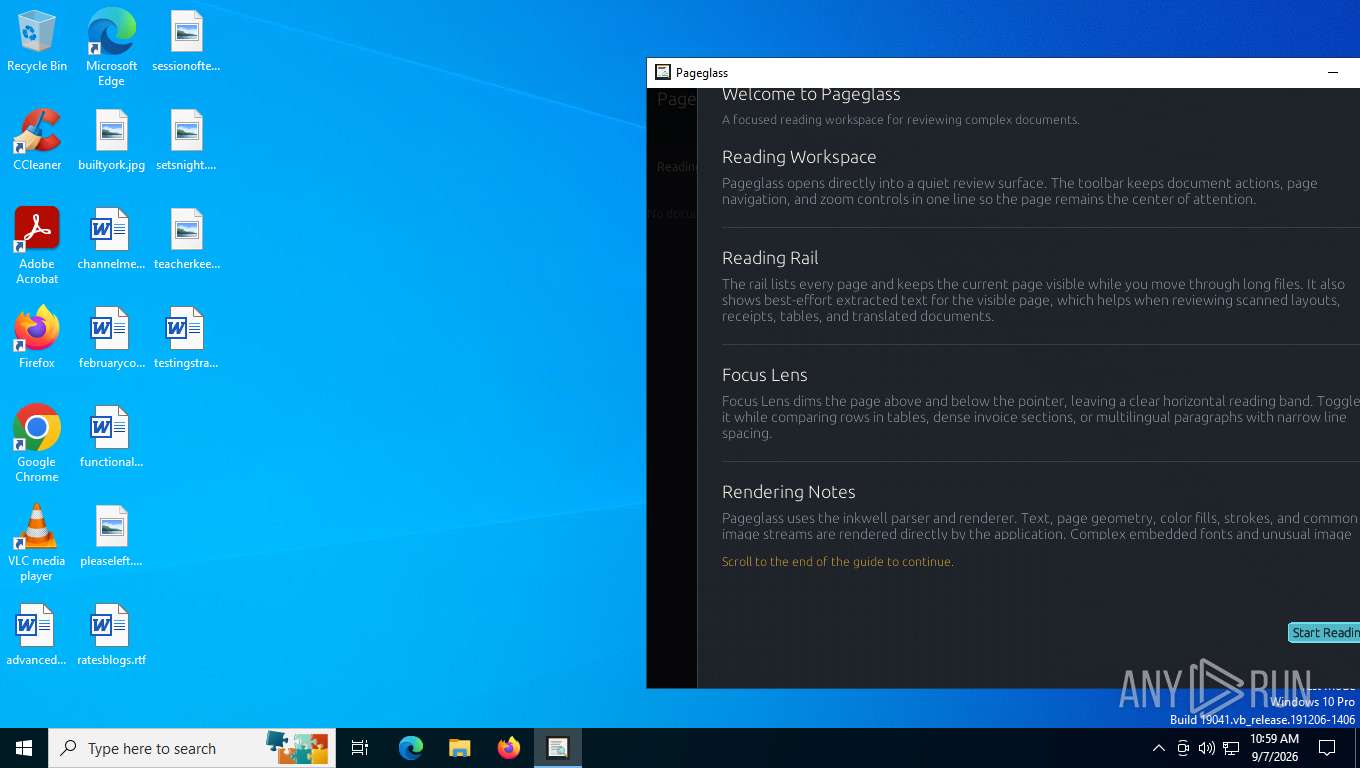
❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026

⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D

#cybersecurity #infosec

Media attachment
app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔄 208 ENTRY CHANGES 🔄

💻 macOS Golden Gate 27 - 34 added, 17 updated
https://support.apple.com/en-us/149035
📱 iOS and iPadOS 27 - 20 added, 10 updated
https://support.apple.com/en-us/149034
💻 macOS Tahoe 26.7 - 20 added, 8 updated
https://support.apple.com/en-us/149042
💻 macOS Sequoia 15.8 - 19 added, 9 updated
https://support.apple.com/en-us/149043
🥽 visionOS 27 - 14 added, 8 updated
https://support.apple.com/en-us/149038
⌚ watchOS 27 - 7 added, 9 updated
https://support.apple.com/en-us/149037
📺 tvOS 27 - 8 added, 5 updated
https://support.apple.com/en-us/149036
📱 iOS and iPadOS 26.7 - 9 added, 4 updated
https://support.apple.com/en-us/149041
🔨 Xcode 27 - 4 added
https://support.apple.com/en-us/149040
🌐 Safari 27 - 2 added, 1 updated
https://support.apple.com/en-us/149039

#apple #cybersecurity #infosec #security #ios

Apple SupportAbout the security content of macOS Golden Gate 27 - Apple SupportThis document describes the security content of macOS Golden Gate 27.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

US moves to staff leaders for industry-partnered offensive cyber program

The U.S. is recruiting private companies for offensive cyber operations against foreign criminals. While the August program shows promise, key details remain murky: payment structures, liability protections, and target identification are unresolved. Experts support the collaboration but stress need for clear guidelines on legal responsibility and international coordination to avoid unintended harm.

https://www.nextgov.com/cybersecurity/2026/10/us-moves-staff-leaders-industry-partnered-offensive-cyber-program/416613/

#InfoSec #CyberSecurity

Nextgov.comUS moves to staff leaders for industry-partnered offensive cyber programThe Trump administration is laying groundwork to enlist companies against foreign cybercriminals, but payment arrangements and protections for participating firms remain unresolved.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

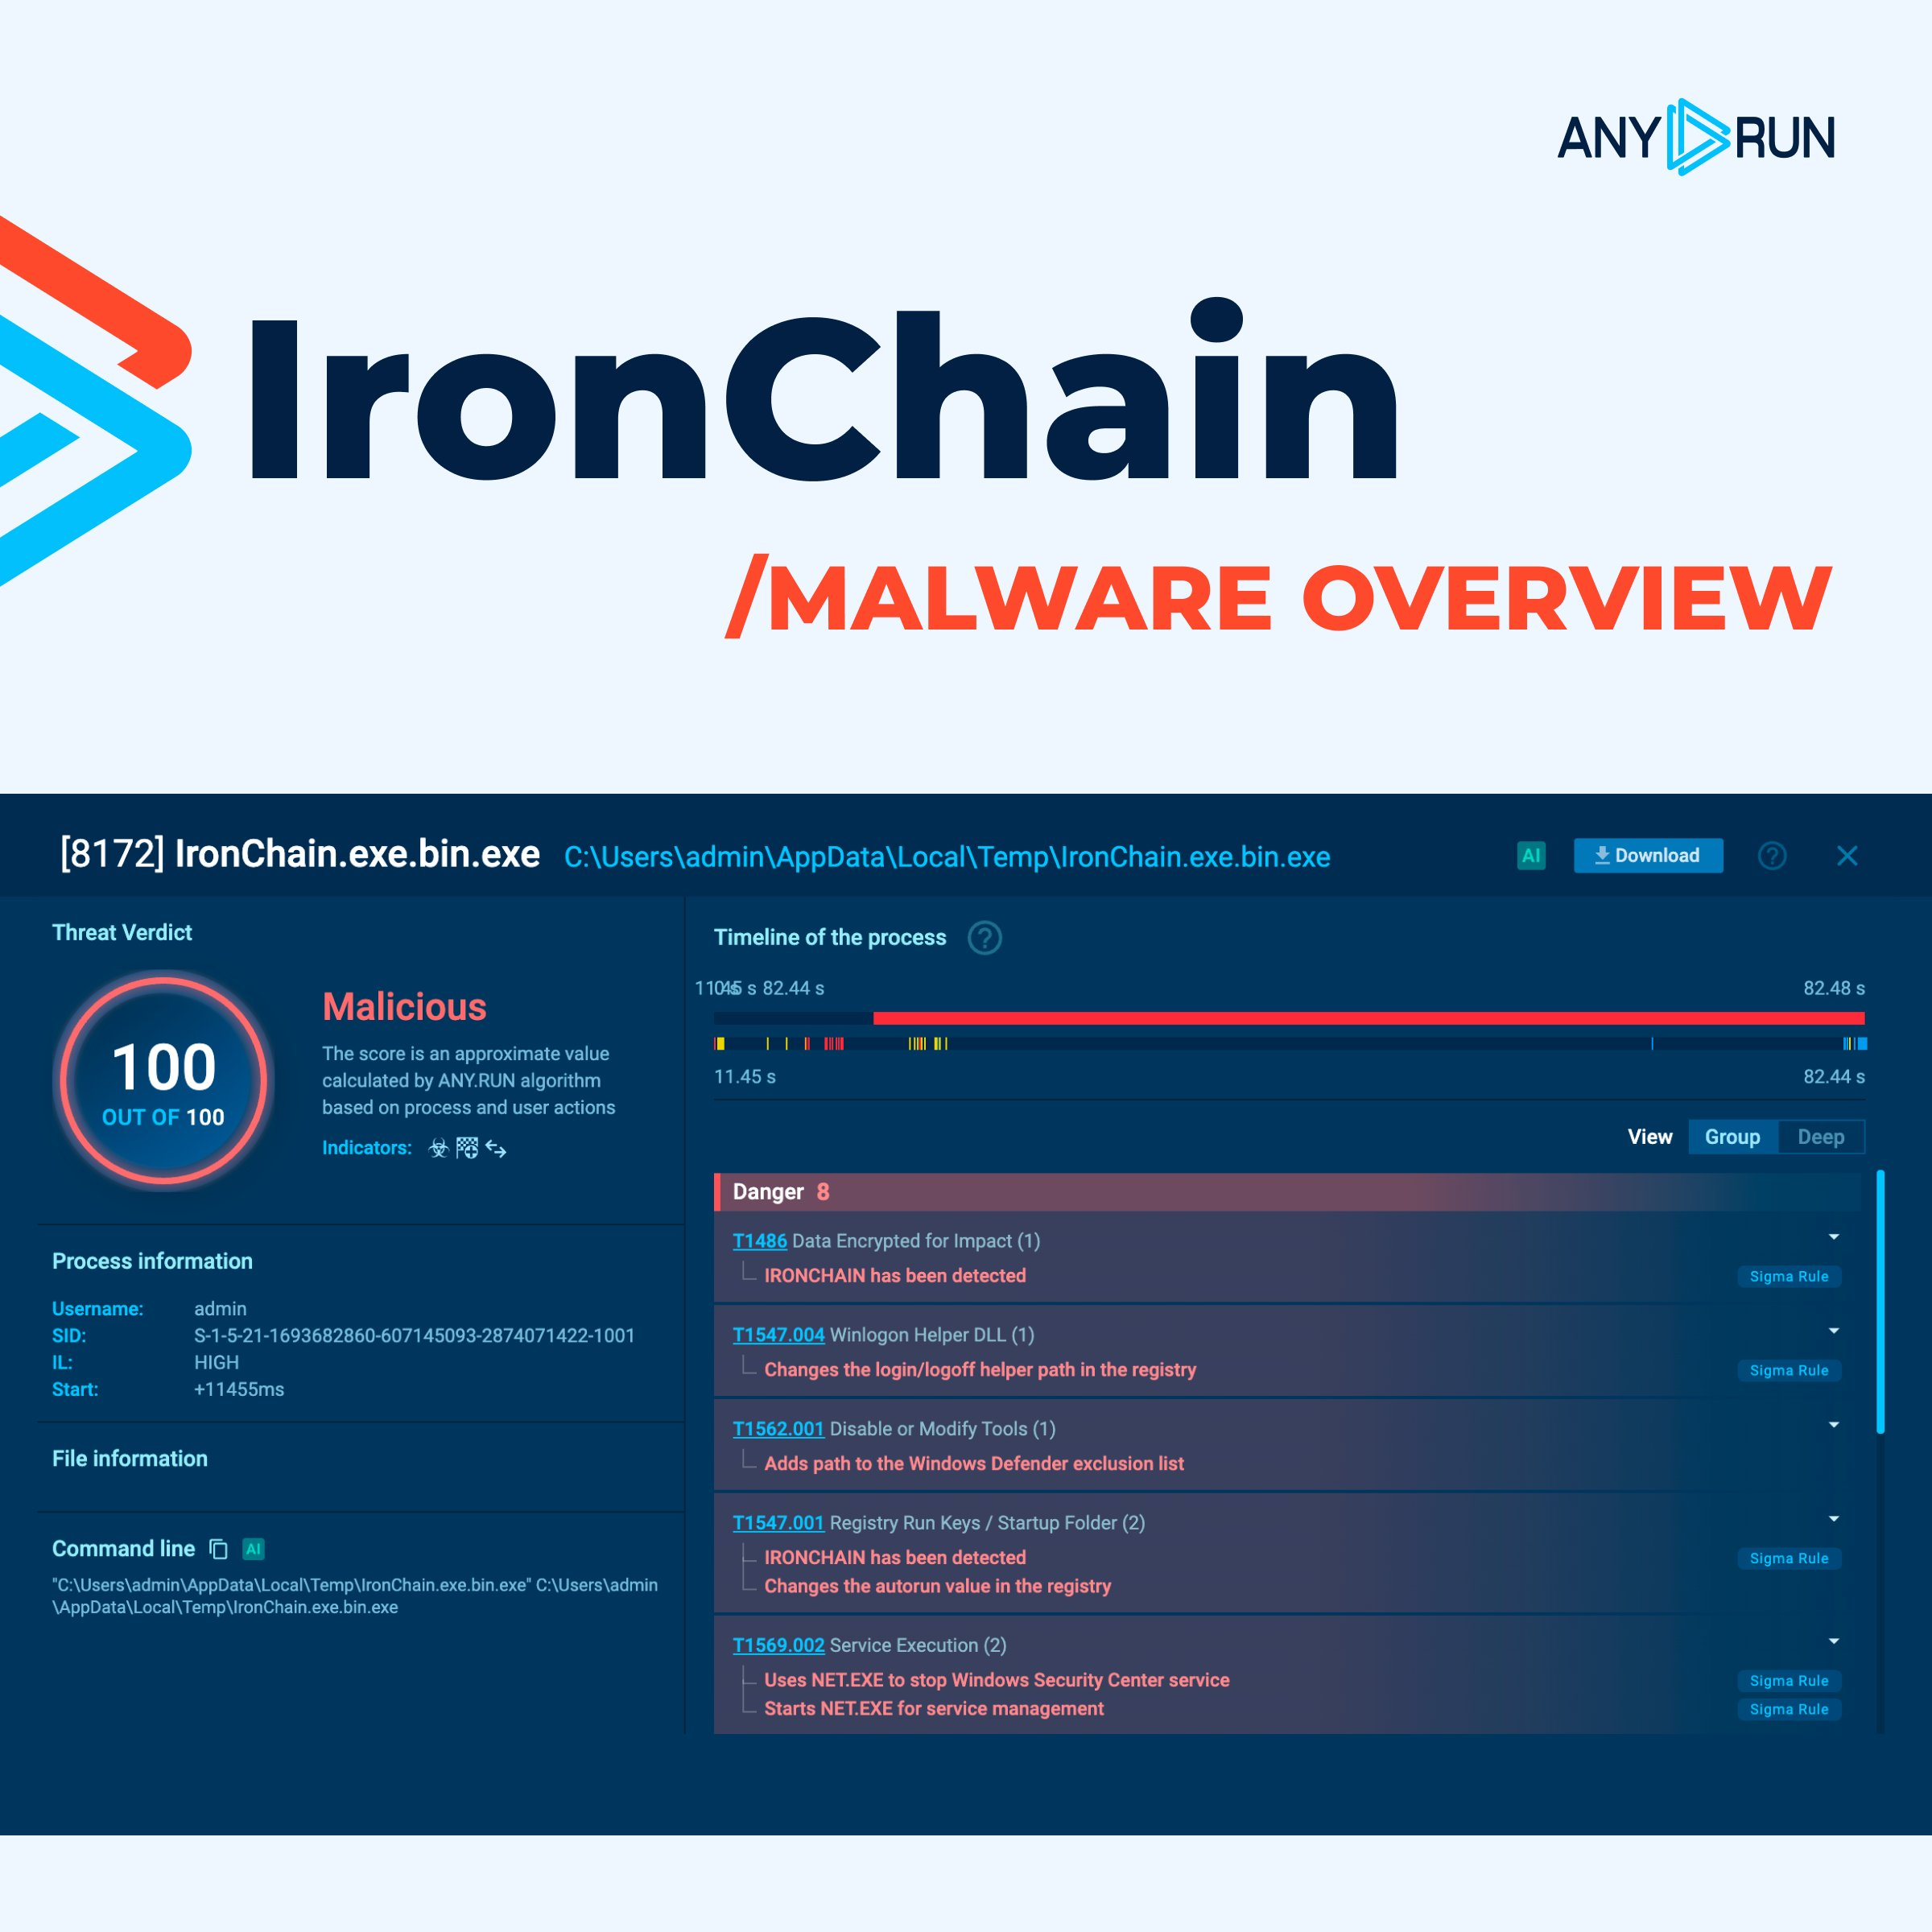
⚠️ #IronChain uses elevated privileges & kernel-level components to weaken security controls before encrypting files. It can disrupt Windows systems and leave organizations facing data loss and extended downtime.

👨‍💻 How to detect it before damage occurs: https://any.run/malware-trends/ironchain/?utm_source=mastodon&utm_medium=post&utm_campaign=ironchain_mtt&utm_term=191026&utm_content=linktomtt

#cybersecurity #infosec

Media attachment
IronChain | Malware Trends TrackerIronChain | Malware Trends TrackerLearn how IronChain uses privileged execution, kernel drivers, and file encryption to compromise Windows systems and cause destructive damage.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📬 NicFab Newsletter #43 | October 20, 2026

Privacy, Data Protection, AI & Cybersecurity — weekly review.

👉 Read the full issue: https://www.nicfab.eu/en/newsletter-issues/2026-10-20-issue-43/?utm_source=mastodon&utm_medium=organic-social&utm_campaign=issue-43

📩 Subscribe: https://www.nicfab.eu/en/pages/newsletter/#subscribe-now

#Privacy #GDPR #DataProtection #AI #AIAct #Cybersecurity #InfoSec

NicFab Blog — Privacy, GDPR & Artificial IntelligenceNewsletter #43 - 20 October 2026NicFab Newsletter #43 — 20 October 2026. Weekly review on privacy, data protection, AI regulation, cybersecurity and digital rights.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⌛Just one week left until it-sa 2026!⌛

Our highlights:
🔹 Migration to BlueSpice: Discover how to successfully transition from existing knowledge platforms – including our exclusive migration kit.
🔹 BlueSpice Galaxy: The next generation of knowledge management live in a demo.

📅 October 27–29, 2026
📍 Messe Nürnberg | Hall 7, Booth 352

👉 Free ticket: https://bluespice.com/bluespice-at-it-sa/

#itsa2026 #BlueSpice #Cybersecurity #KnowledgeManagement #DataSovereignty #OpenSource

In the foreground it says "Home of IT Security" and "Secure Ticket Voucher Now". Additionally there is the it-sa Logo and a see-through lock.
BlueSpice MediaWikiBlueSpice at it-sa | BlueSpice MediaWikiWissensmanagement in Ihrer Organisation sicher, strukturiert und zukunftsfähig gestalten - treffen Sie uns auf der it-sa in Nürnberg. Von 27. - 29. Oktober.
↩ Reply ♡ 0 · ↻ 0 ↗ Original