X XFediYour place in the Fediverse
XFEDI

#CyberSecurity

ActivityPub

Public posts with this hashtag.

F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws

F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.

**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L
BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Tanishq.

Password must contain:
- 6 to 16 characters.
- At least one special character (@, #, $, %, * and & only).
- At least one alphabet.
- At least one number.

https://dumbpasswordrules.com/sites/tanishq/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comTanishq - Dumb Password RulesPassword must contain: - 6 to 16 characters. - At least one special character (@, #, $, %, * and & only). - At least one alphabet. - At least one number.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

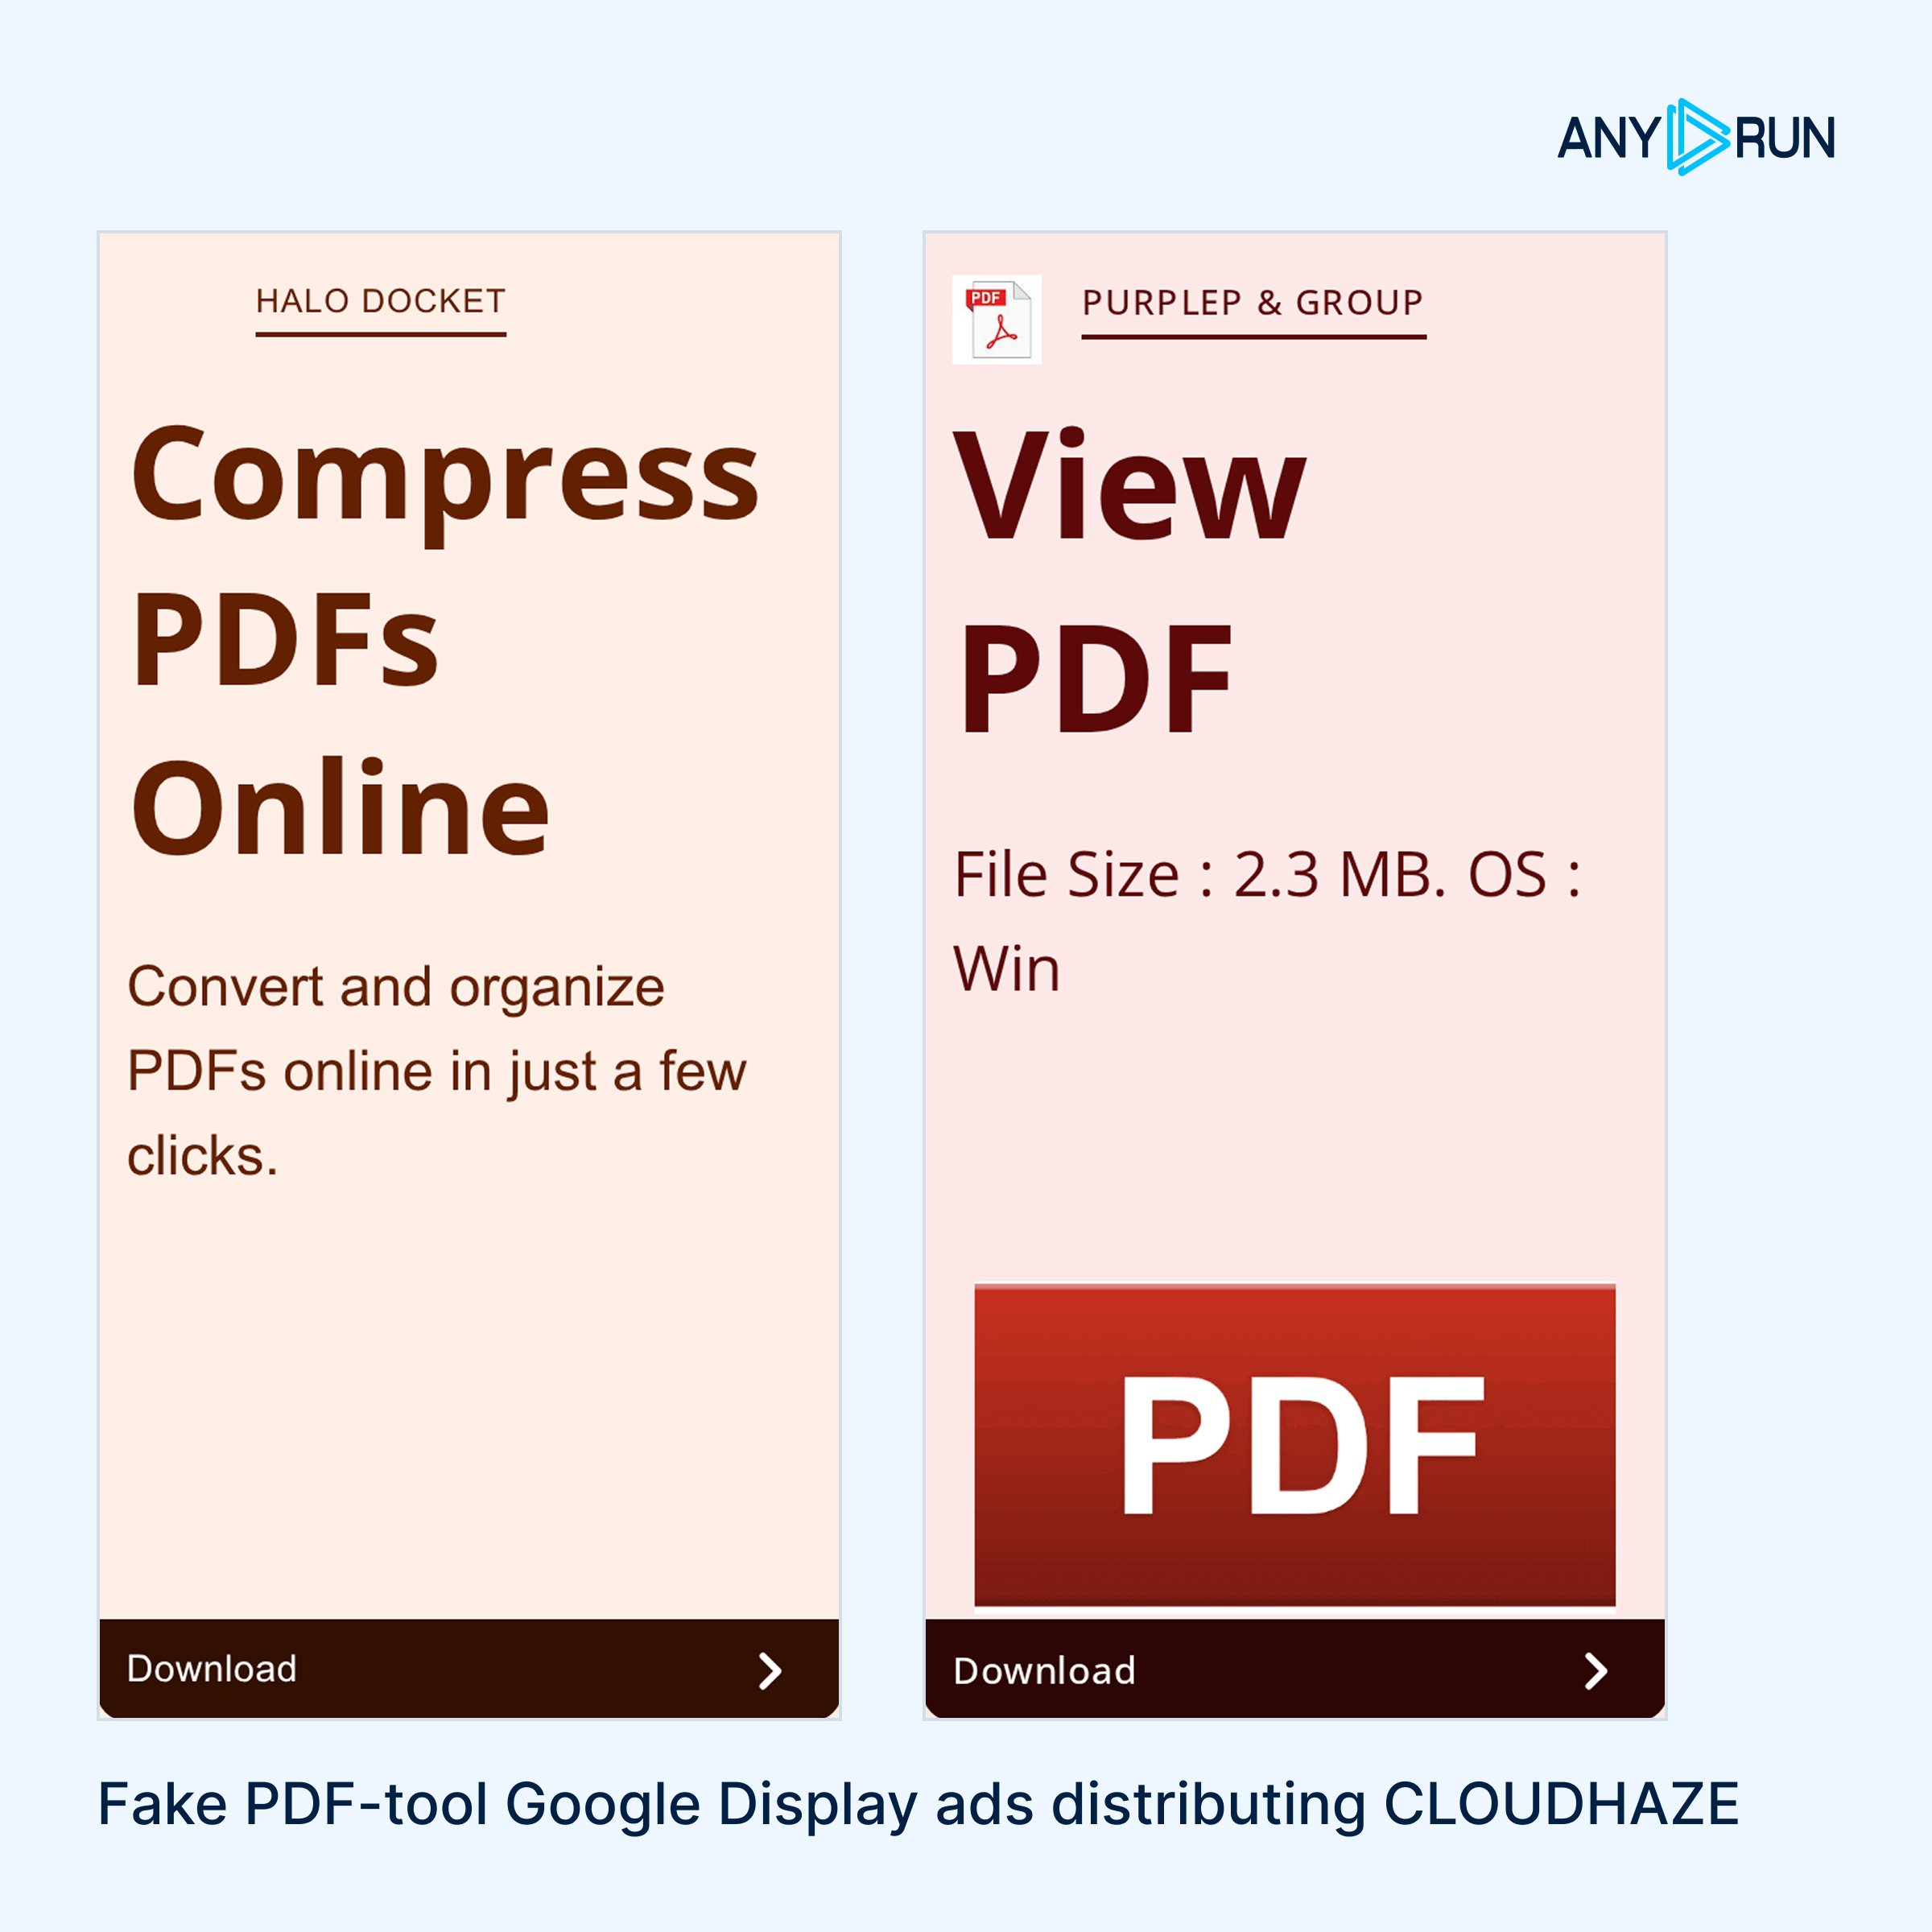
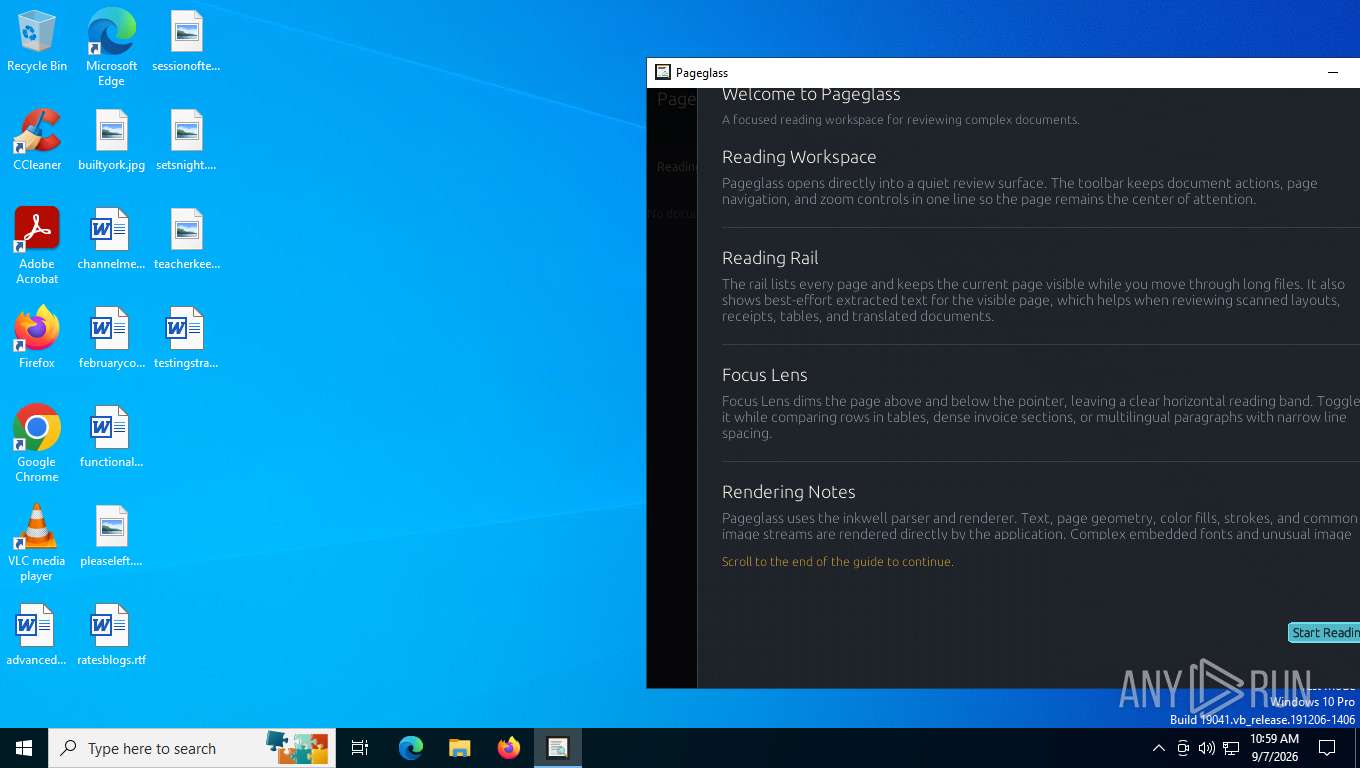
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.

586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.

❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026

⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D

#cybersecurity #infosec

Media attachment
app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔄 208 ENTRY CHANGES 🔄

💻 macOS Golden Gate 27 - 34 added, 17 updated
https://support.apple.com/en-us/149035
📱 iOS and iPadOS 27 - 20 added, 10 updated
https://support.apple.com/en-us/149034
💻 macOS Tahoe 26.7 - 20 added, 8 updated
https://support.apple.com/en-us/149042
💻 macOS Sequoia 15.8 - 19 added, 9 updated
https://support.apple.com/en-us/149043
🥽 visionOS 27 - 14 added, 8 updated
https://support.apple.com/en-us/149038
⌚ watchOS 27 - 7 added, 9 updated
https://support.apple.com/en-us/149037
📺 tvOS 27 - 8 added, 5 updated
https://support.apple.com/en-us/149036
📱 iOS and iPadOS 26.7 - 9 added, 4 updated
https://support.apple.com/en-us/149041
🔨 Xcode 27 - 4 added
https://support.apple.com/en-us/149040
🌐 Safari 27 - 2 added, 1 updated
https://support.apple.com/en-us/149039

#apple #cybersecurity #infosec #security #ios

Apple SupportAbout the security content of macOS Golden Gate 27 - Apple SupportThis document describes the security content of macOS Golden Gate 27.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

US moves to staff leaders for industry-partnered offensive cyber program

The U.S. is recruiting private companies for offensive cyber operations against foreign criminals. While the August program shows promise, key details remain murky: payment structures, liability protections, and target identification are unresolved. Experts support the collaboration but stress need for clear guidelines on legal responsibility and international coordination to avoid unintended harm.

https://www.nextgov.com/cybersecurity/2026/10/us-moves-staff-leaders-industry-partnered-offensive-cyber-program/416613/

#InfoSec #CyberSecurity

Nextgov.comUS moves to staff leaders for industry-partnered offensive cyber programThe Trump administration is laying groundwork to enlist companies against foreign cybercriminals, but payment arrangements and protections for participating firms remain unresolved.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

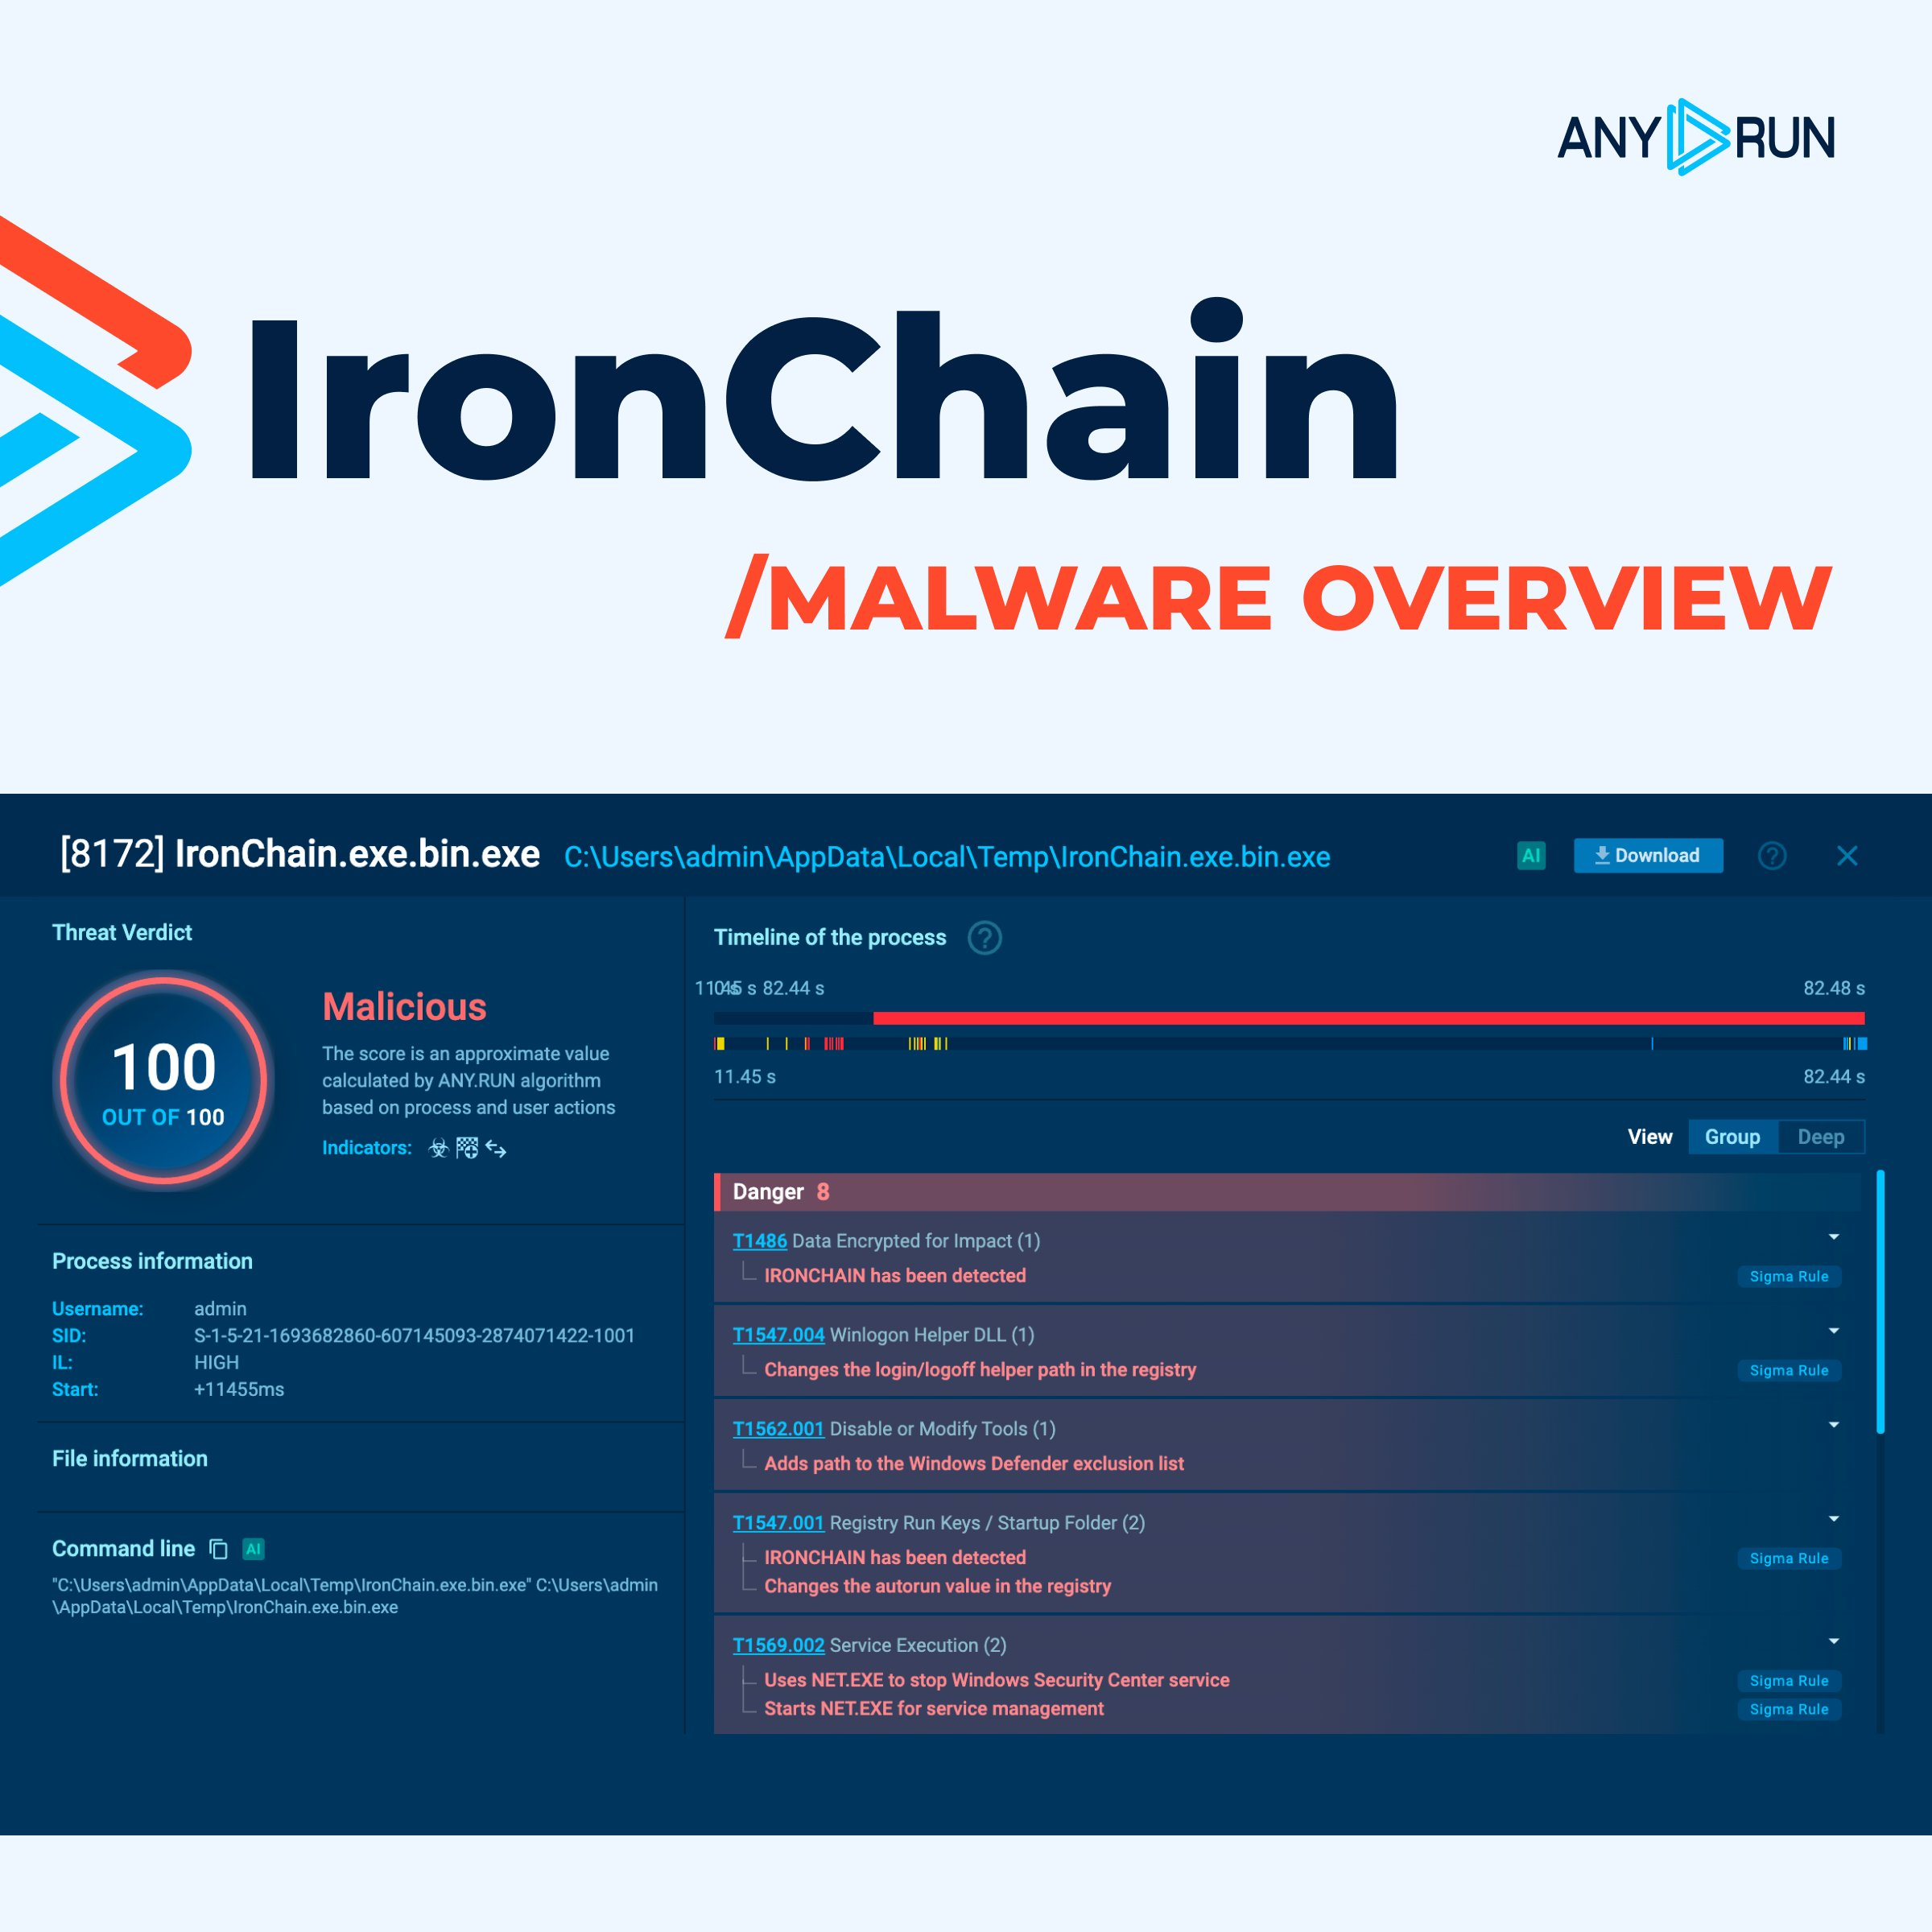
⚠️ #IronChain uses elevated privileges & kernel-level components to weaken security controls before encrypting files. It can disrupt Windows systems and leave organizations facing data loss and extended downtime.

👨‍💻 How to detect it before damage occurs: https://any.run/malware-trends/ironchain/?utm_source=mastodon&utm_medium=post&utm_campaign=ironchain_mtt&utm_term=191026&utm_content=linktomtt

#cybersecurity #infosec

Media attachment
IronChain | Malware Trends TrackerIronChain | Malware Trends TrackerLearn how IronChain uses privileged execution, kernel drivers, and file encryption to compromise Windows systems and cause destructive damage.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📬 NicFab Newsletter #43 | October 20, 2026

Privacy, Data Protection, AI & Cybersecurity — weekly review.

👉 Read the full issue: https://www.nicfab.eu/en/newsletter-issues/2026-10-20-issue-43/?utm_source=mastodon&utm_medium=organic-social&utm_campaign=issue-43

📩 Subscribe: https://www.nicfab.eu/en/pages/newsletter/#subscribe-now

#Privacy #GDPR #DataProtection #AI #AIAct #Cybersecurity #InfoSec

NicFab Blog — Privacy, GDPR & Artificial IntelligenceNewsletter #43 - 20 October 2026NicFab Newsletter #43 — 20 October 2026. Weekly review on privacy, data protection, AI regulation, cybersecurity and digital rights.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

⌛Just one week left until it-sa 2026!⌛

Our highlights:
🔹 Migration to BlueSpice: Discover how to successfully transition from existing knowledge platforms – including our exclusive migration kit.
🔹 BlueSpice Galaxy: The next generation of knowledge management live in a demo.

📅 October 27–29, 2026
📍 Messe Nürnberg | Hall 7, Booth 352

👉 Free ticket: https://bluespice.com/bluespice-at-it-sa/

#itsa2026 #BlueSpice #Cybersecurity #KnowledgeManagement #DataSovereignty #OpenSource

In the foreground it says "Home of IT Security" and "Secure Ticket Voucher Now". Additionally there is the it-sa Logo and a see-through lock.
BlueSpice MediaWikiBlueSpice at it-sa | BlueSpice MediaWikiWissensmanagement in Ihrer Organisation sicher, strukturiert und zukunftsfähig gestalten - treffen Sie uns auf der it-sa in Nürnberg. Von 27. - 29. Oktober.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

MISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new workflows for publishing IOCs directly to security platforms.

@misp

🔗 https://github.com/MISP/misp-modules/releases/tag/v3.1.0

#misp #cti #threatintel #intelligence #cybersecurity #osint

vulnerability-lookup expansion modules in MISP 3.0
GitHubRelease MISP Modules v3.1.0 - More pivots, more integrations, more actionable intelligence · MISP/misp-modulesMISP Modules v3.0.13 is a substantial release, bringing a new wave of OSINT and threat intelligence enrichment capabilities, new ways to export indicators into operational security tools, and new w...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CISA to AI labs: Share test-network IPs to flag rogue agents

CISA urges AI labs to share IP addresses to track rogue agents threatening critical infrastructure. While transparency could boost cybersecurity, experts debate its practicality due to cloud complexity and AI's dynamic nature. Alternative solutions like detection signatures are suggested. Public sector orgs should proactively test AI systems and prioritize vulnerability patches.

https://www.techtarget.com/cybersecurity/news/366651845/CISA-to-AI-labs-Share-test-network-IPs-to-flag-rogue-agents

#InfoSec #CyberSecurity

CybersecurityCISA to AI labs: Share test-network IPs to flag rogue agents | TechTargetCISA urges AI labs to share IPs and ASNs so defenders can recognize and flag rogue agents early. Research analysts, however, had mixed reactions. Learn why.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and ...

Bank of America deployed 4,000 personnel (3,000 employees + 1,000 contractors) to fix software vulnerabilities detected by AI like Anthropic's Mythos. CEO Moynihan confirmed hundreds of millions in Q3 cybersecurity spending. Once skeptical of AI security tools, major firms now embrace them after serious breaches. BofA leads in transparency, expecting future cost reductions in patching efforts.

https://the-decoder.com/bank-of-america-puts-4000-people-on-fixing-vulnerabilities-uncovered-by-anthropics-mythos-and-other-ai-models/

#InfoSec #CyberSecurity

The DecoderBank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and other AI modelsBank of America has hired 1,000 outside contractors to fix software vulnerabilities uncovered by AI models like Anthropic's Mythos, CNBC reports.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Discover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.

#PwnEscape #LinuxKernel #Vulnerability #CloudSecurity #CyberSecurity

https://dailytechnow.com/critical-pwnescape-flaw-linux-virtual-machines/

Daily Tech NowCritical PwnEscape Flaw Found in Linux Virtual MachinesDiscover the critical PwnEscape vulnerability in the Linux kernel. Learn how this flaw allows attackers to escape virtual machines and seize server control.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This #Cybersecurity Agency Is Supposed to Protect U.S. #Elections. Officials Fear It’s Been Compromised by #Trump.

A few months into President Donald Trump’s second term, #political appointees at the Department of #HomelandSecurity made an unusual request of its agency focused on cybersecurity: Secretly acquire a #voting machine and #hack it.

The appointees wanted the Cybersecurity and #Infrastructure #Security Agency to procure the machine, examine it and report back the findings so they could be given to the #WhiteHouse , according to two former administration officials with knowledge of the request.
#dhs #voting #cisa

https://www.propublica.org/article/cisa-election-security-donald-trump

ProPublicaTrump Appointees Asked a Federal Cybersecurity Agency to Secretly Acquire a Voting Machine — and Hack ItThough not acted on, the request shows how the Trump administration has tried to use the Cybersecurity and Infrastructure Security Agency for its own ends while draining it of resources to help its mission of protecting the nation’s voting systems.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Discover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.

#Broadcom #WPSplinter #CyberSecurity #WiFiSecurity #RouterExploit

https://dailytechnow.com/broadcom-wifi-software-vulnerability/

Daily Tech NowBroadcom Wi-Fi Software Vulnerability Exposes RoutersDiscover the critical Broadcom Wi-Fi software vulnerability known as WPSplinter. Learn how this flaw grants attackers root access to popular routers.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Enterprise controls can't keep up with AI agents

🚨 Companies are deploying AI agents faster than they can control them. Organizations struggle to track what these agents access, do, or if they can stop them. Traditional security systems aren't built for autonomous AI. The result? Potential security gaps and leaders considering quiet incident handling. The shift ahead: focus on managing existing agents responsibly, not just rolling out more.

https://www.techtarget.com/ai/news/366652493/Enterprise-controls-cant-keep-up-with-AI-agents

#InfoSec #CyberSecurity #AIGovernance

AI & Emerging TechEnterprise controls can't keep up with AI agents | TechTargetCompanies are giving agents more authority, but many are still struggling to track what they can access, what they're doing and how to stop them.
↩ Reply ♡ 0 · ↻ 0 ↗ Original