🚨🐛 SIGINT // Cybersecurity Watch — 2026-10-25
Critical PHP RCE flaws found with AI drew millions of exploit attempts and took sites offline; NSA, CISA and partners urge immediate patching of PHP systems.
https://www.reuters.com/world/asia-pacific/cloudflare-sees-millions-exploit-attempts-after-php-disclosure-2026-10-22/
#PHP2Shell #PHP #Vulnerability #InfoSec
XFEDI
ActivityPub#vulnerability
Public posts with this hashtag.
The most interesting story on the wire this week isn't a breach, but a confession.
The federal deadline to patch CVE-2026-114625 is October 26. If you're managing Arista VeloCloud Orchestrators, you've got about 48 hours (hardly any time at all) to stop an active SQL injection from taking up permanent…
AWS claims attackers tried to use these new PHP vulnerabilities days before the fix went live.

Pillow 13.0.0 Patches Critical Remote Code Execution Flaws in Python Image Processing
Pillow version 13.0.0 addresses over 30 security vulnerabilities, including critical remote code execution flaws in EPS, JPEG, and TIFF processing that allow attackers to take over servers via crafted image uploads.
**If your Python applications or servers process images (most do, through the Pillow library), update Pillow to version 13.0.0 ASAP and rebuild all your containers and virtual environments. Note that this version needs Python 3.11 or newer. Until everything is patched, remove Ghostscript from any server that handles uploaded images, and treat all image uploads from outsiders as potentially dangerous.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/pillow-13-0-0-patches-critical-remote-code-execution-flaws-in-python-image-processing-5-m-i-2-0/gD2P6Ple2L
 BeyondMachinesPillow 13.0.0 Patches Critical Remote Code Execution Flaws in Python Image ProcessingPillow version 13.0.0 addresses over 30 security vulnerabilities, including critical remote code execution flaws in EPS, JPEG, and TIFF processing that allow attackers to take over servers via crafted image uploads.
Node.js Releases Critical Security Updates to Fix Brotli Remote Code Execution and Network Flaws
Node.js released security updates for 10 vulnerabilities, including a critical remote code execution flaw in the Brotli decoder (CVE-2026-111497) and multiple network validation bypasses. These vulnerabilities reside in the core runtime, requiring administrators to update host systems, rebuild container images, and restart all services.
**If you run Node.js anywhere, update it right away to version 22.23.4, 24.22.1 or 26.12.1, then rebuild any containers or apps that bundle Node.js and restart all Node.js services (your usual dependency scanners won't catch this, so check the runtime versions yourself). If you're still on old versions like 20.x, 23.x or 25.x, they will never be fixed. Move to a supported version ASAP. Until you can patch, block Brotli-compressed (br) traffic at your proxy or firewall as a temporary shield.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/node-js-releases-critical-security-updates-to-fix-brotli-remote-code-execution-and-network-flaws-e-l-q-t-c/gD2P6Ple2L
 BeyondMachinesNode.js Releases Critical Security Updates to Fix Brotli Remote Code Execution and Network FlawsNode.js released security updates for 10 vulnerabilities, including a critical remote code execution flaw in the Brotli decoder (CVE-2026-111497) and multiple network validation bypasses. These vulnerabilities reside in the core runtime, requiring administrators to update host systems, rebuild container images, and restart all services.

Brace for impact.
Several Linux Kernel Vulnerabilities Accidentally Posted To Public Kernel Mailing List
#linux #itsec #foss #vulnerability
https://www.phoronix.com/news/LKML-New-Trend-Vulnerabilities
HPE Patches 72 Vulnerabilities in ArubaOS Including Eight CVSS 10.0 Flaws
HPE released security updates for ArubaOS to fix 72 vulnerabilities, including 33 critical flaws that allow unauthenticated remote code execution and authentication bypass on wireless infrastructure.
**If you use HPE Aruba devices running ArubaOS (AOS-8 or AOS-10), upgrade ASAP to a fixed version (AOS-10.8.1.2, 10.7.2.7, 10.4.1.14, 8.13.3.1 or 8.10.0.24). The patch has dozens of critical flaws let attackers take full control without a password. Make sure the web and CLI management interfaces are never reachable from the internet and can only be accessed from a dedicated, trusted management network.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/hpe-patches-72-vulnerabilities-in-arubaos-including-eight-cvss-10-0-flaws-m-1-k-i-d/gD2P6Ple2L
 BeyondMachinesHPE Patches 72 Vulnerabilities in ArubaOS Including Eight CVSS 10.0 FlawsHPE released security updates for ArubaOS to fix 72 vulnerabilities, including 33 critical flaws that allow unauthenticated remote code execution and authentication bypass on wireless infrastructure.
3. That is how many zero-day vulnerabilities hit Arista VeloCloud Orchestrator in four months. If you run a ten person shop, you might not even know what an orchestrator is.

CVE-2026-107685: agentjido req_llm WebSocket client (1.9.0 – 1.28.x) disables TLS certificate validation, letting on-path attackers hijack or modify OpenAI sessions 🛡️ Avoid vulnerable versions & monitor vendor updates. https://radar.offseq.com/threat/improper-certificate-validation-vulnerability-in-the-websocket-streaming-client-in-agentjido-reqllm-46b1400882c2a012 #OffSeq #CVE #Vulnerability #Cybersecurity
CVE-2026-81212 — IBM DataStage 10.0. Unauthenticated write into shared Redis under any tenant’s key. Credential-encryption boundary collapses across the whole instance.
A:N/S:C/C:H/I:H. Nothing goes down. No crash, no alert. The platform just serves poisoned flow parameters to every tenant’s jobs.
No PoC, not in KEV.
Fix: Cloud Pak for Data 5.4 patch 8 — shipped the same day as the CVE. At least one tracker still says no patch. It’s wrong.
IBM documents no workaround. Restrict Redis reachability to the pods that need it until you patch.
Also in 5.4.0.0: CVE-2026-82107 (9.6), CVE-2026-42586 (9.1), CVE-2026-81207 (8.5). Patch the cluster.
https://threataft.com/articles/ibm-datastage-cve-2026-81212-redis-tenant-write
 ThreatAftDataStage 10.0: One Redis, Every Tenant's Key | ThreatAftCVE-2026-81212: unauthenticated write to shared Redis under any tenant's key in IBM DataStage 5.4.0.0. CVSS 10.0. Fixed in 5.4 patch 8.
⚠️ RELAY // Cyber Watch — 2026-10-24
TechCrunch reports security teams are also dealing with flaws in Node.js and the AI tool LiteLLM, on top of the AI-discovered PHP vulnerabilities.
🔗 https://techcrunch.com/2026/10/21/the-internet-is-having-a-very-bad-cybersecurity-day/
 TechCrunchThe internet is having a very bad cybersecurity day | TechCrunchFrom AI-discovered PHP vulnerabilities to flaws in Node.js and popular AI tool LiteLLM, cybersecurity teams have plenty to worry about this week.
The wire is currently obsessed with the resurgence of Mirai. The consensus narrative suggests we're seeing a sophisticated, coordinated campaign leveraging a "PHP2Shell" exploit to build a botnet on a scale that could…
Yeah, can we go back to cool name please?
CVE-2026-114119 — Bp Premier (60% of Australian GP clinics) ships the same SQL Server sysadmin password across every installation. It cannot be changed without breaking the app.
Reach TCP 1433 → authenticate as sysadmin → bypass app login → xp_cmdshell as SYSTEM → patient records, Medicare data, prescribing history.
No PoC needed. The credential is in the installer.
Fix: Oxford SP1 1.14.1.1128 / 1.14.1.1129. Verify the Database Connector service is running after upgrade. Block 1433 from untrusted networks now.
Two records disagree on AV:N vs AV:A. Don't assume the safer one.
https://threataft.com/articles/bp-premier-cve-2026-114119-hardcoded-sql-server-password
 ThreatAftBp Premier: One SQL Password for Every Clinic | ThreatAftCVE-2026-114119: Bp Premier ships one SQL Server sysadmin password for every clinic. 60% of Australian GP practices. Fixed in 1.14.1.1128/1129.

An updated advisory from Cisco:
CRITICAL: CVE-2026-109618 and CVE-2026-109619: Vulnerabilities in PHP Affecting Cisco Products: October 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-php-october26-Jj384Daq @TalosSecurity #Cisco #infosec #PHP #vulnerability
Capcom just confirmed that 11.7 million CAPCOM ID accounts were hit in a breach that's still leaking details this afternoon. When you build a centralized identity system, you aren't just making things easy for the user.
It ain't over 'til it's over.
New:
PHP: Informational advisory: Session upload progress https://www.php.net/archive/2026.php#2026-10-23-1
The Hacker News: PHP Warns of Another Unpatched RCE Risk Two Days After Emergency PHP2Shell Patches https://thehackernews.com/2026/10/urgent-php-warns-of-another-unpatched.html @thehackernews #infosec #PHP #vulnerability
 www.php.netPHP: News Archive - 2026PHP is a popular general-purpose scripting language that powers everything from your blog to the most popular websites in the world.
Six SOHO router CVEs, Oct 20–22. Four CVSS 10.0s. All have public PoCs. None has a documented patch.
Tenda AC19 (CVE-2026-113744, formSetFirewallCfg stack overflow), TOTOLINK EX200 ×2 (CVE-2026-114382/383, cstecgi.cgi stack overflows), TOTOLINK A950RG (CVE-2026-114575, UploadCustomModule command injection), Tenda BE3L Pro 9.9, D-Link DHP-W610AV 9.8 — EOL since Nov 2025, D-Link says retire it.
The A950RG Boa config sets User=root. Every exploit on that device is a root shell.
Block management at WAN. Retire the D-Link. Isolate the rest.
https://threataft.com/articles/soho-router-october-2026-roundup-tenda-totolink-dlink
 ThreatAftSOHO Router Roundup: Four 10.0s, No Patches | ThreatAftOctober SOHO router roundup: Tenda AC19, TOTOLINK EX200 ×2, A950RG, D-Link DHP-W610AV, BE3L Pro. Four CVSS 10.0s, public PoCs, almost no fixes.
CVE-2026-107685 (CRITICAL, CVSS 9.1): agentjido req_llm <1.29.0 WebSocket client disables TLS verification, exposing OpenAI sessions to MITM attacks. Restrict use or network access until patched. https://radar.offseq.com/threat/cve-2026-107685-cwe-295-improper-certificate-validation-in-agentjido-reqllm-c06aa809808f4159 #OffSeq #CVE #infosec #vulnerability
CVE-2026-114625: CRITICAL SQL injection in Arista VeloCloud Orchestrator (<5.2.3.18, <6.1.3.10, <6.4.2.12). Actively exploited! Authenticated users can escalate to operator. Patch ASAP. Block 74.82.197.86 & 38.54.50.151. https://radar.offseq.com/threat/attackers-exploit-third-velocloud-orchestrator-zero-day-in-four-months-d21f081e4a87c8fd #OffSeq #Vulnerability #Arista
Siemens October 2026 Advisories: Six Critical Fixes for PLCs, Edge Devices and CROSSBOW
Siemens' October 2026 security updates patch critical vulnerabilities in four product families: the SIMATIC S7-1500 MFP GNU/Linux subsystem (code execution, privilege escalation), the S7-1500 web server's Trace page (eight XSS flaws enabling unauthorized PLC operations), Industrial Edge devices (authenticated path traversal), and RUGGEDCOM CROSSBOW (SQLite-based code execution). Only Industrial Edge and CROSSBOW (V6.0) have fixes so far, so for the MFP and web server issues Siemens advises restricting access, disabling unneeded web servers, keeping industrial devices off the internet and office networks, and watching ProductCERT for upcoming patches.
**If you use Siemens industrial devices, make sure all of them (PLCs, HMIs, edge devices) are isolated from the internet and reachable only from trusted networks. Update RUGGEDCOM CROSSBOW to V6.0 and your Industrial Edge devices to the fixed versions ASAP. For SIMATIC S7-1500 controllers there are no fixes yet, so turn off the web server where you don't need it, never import trace files or run applications from untrusted sources. Apply Siemens' patches as soon as they're released.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/siemens-october-2026-advisories-six-critical-fixes-for-plcs-edge-devices-and-crossbow-8-r-a-3-i/gD2P6Ple2L
 BeyondMachinesSiemens October 2026 Advisories: Six Critical Fixes for PLCs, Edge Devices and CROSSBOWSiemens' October 2026 security updates patch critical vulnerabilities in four product families: the SIMATIC S7-1500 MFP GNU/Linux subsystem (code execution, privilege escalation), the S7-1500 web server's Trace page (eight XSS flaws enabling unauthorized PLC operations), Industrial Edge devices (authenticated path traversal), and RUGGEDCOM CROSSBOW (SQLite-based code execution). Only Industrial Ed
CRITICAL: CVE-2026-55981 in Creative Sound Blaster Katana V2, V2X, SE (v1.30.260813.1100) allows firmware modification & upload. No fix yet — monitor for updates and restrict device access. https://radar.offseq.com/threat/cve-2026-55981-vulnerability-in-creative-labs-creative-sound-blaster-katana-v2-v2x-se-b5b2482bb26c4567 #OffSeq #infosec #firmware #vulnerability

Discover how critical Trend Micro ZDI Linux kernel vulnerabilities were accidentally leaked on the public LKML before being fully patched.
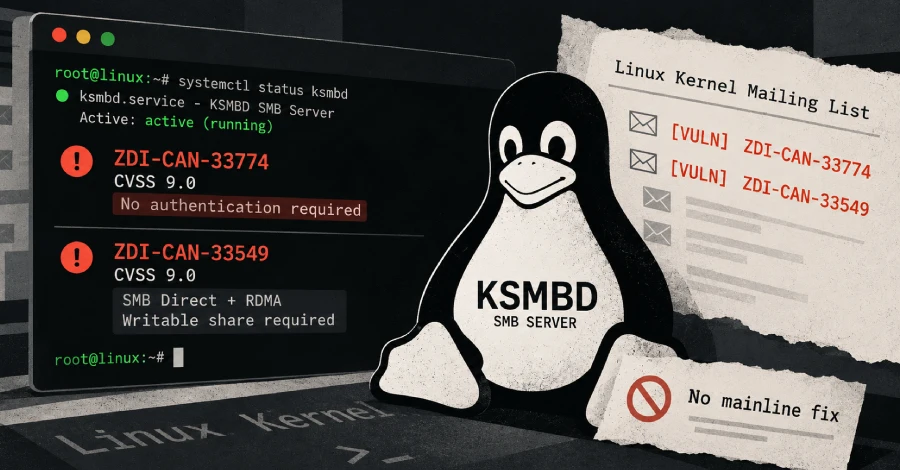 Daily Tech NowCritical Trend Micro ZDI Linux Vulnerabilities Leaked on LKMLDiscover how critical Trend Micro ZDI Linux kernel vulnerabilities were accidentally leaked on the public LKML before being fully patched.
Oracle October 2026 CPU — the numbers that actually matter:
1,295 patches / 1,209 CVEs (not 1,283 — that's the wrong figure)
~590 patches for unauthenticated flaws
Six CVSS 10.0s, all unauth
The 9.8 to patch first: CVE-2026-101767 — EBS SQL injection with a published Horizon3 chain that bypasses the default URL firewall and reaches a shell via the Concurrent Manager.
CVE-2026-35273 (PeopleSoft, KEV): ShinyHunters / UNC6240 are URL-encoding the PSEMHUB path to bypass WAF blocks. Patch, don't WAF.
https://threataft.com/articles/oracle-october-2026-cpu-1209-cves-six-cvss-10
 ThreatAftOracle October 2026 CPU: 1,209 CVEs, Six 10.0s | ThreatAftOracle's October 2026 CPU fixes 1,209 CVEs across 33 families, including six CVSS 10.0 flaws. Patch Fusion Middleware, EBS and PeopleSoft first.
Craft CMS 8-CVE patch batch — the one to prioritise:
CVE-2026-112776 (9.8): unauthenticated GraphQL site-scope bypass. Cross-site data access on multi-tenant installs with no credentials.
Plus five Twig sandbox escapes and a verification-code ATO flaw that chains into them.
Craft 5.x → 5.11.0 | Craft 4.x → 4.18.8
https://threataft.com/articles/craft-cms-cve-2026-112776-graphql-twig-sandbox-rce
ThreatAftCraft CMS 9.8 GraphQL Bypass + 7 Twig RCEs | ThreatAftCraft CMS 5.x/4.x: 8 CVEs incl. 9.8 GraphQL site-scope bypass and five Twig sandbox RCEs. Fixed in 5.11.0 / 4.18.8.

#meme #php #cybersecurity #security #cybercrime #hack #web #www #server #patch #admin #administrator #Software #vulnerability #bug #internet #online

PHP2Shell: two critical PHP RCE vulnerabilities — patches and protection
🔗 https://cybersecurefox.com/en/php2shell-critical-php-rce-vulnerabilities-patches-protection
#PHP2Shell #CVE-2026-109618 #CVE-2026-109619 #PHP #RCE #PHP #vulnerability
 CyberSecureFoxPHP2Shell: Two Critical PHP RCE Vulnerabilities — Patches And ProtectionOn October 21, 2026, the PHP team released emergency updates for two critical remote code execution (RCE) vulnerabilities collectively dubbed PHP2Shell. The
A critical security update addresses two PHP zero-day RCE vulnerabilities. Learn how to protect your servers from CVE-2026-109618 and CVE-2026-109619 today.
 Daily Tech NowCritical PHP Zero-Day RCE Vulnerabilities Update ReleasedA critical security update addresses two PHP zero-day RCE vulnerabilities. Learn how to protect your servers from CVE-2026-109618 and CVE-2026-109619 today.
The day after another AI company scared the world out of its wits:
Reuters: In the 10 hours before it was publicly announced, across the network we saw thousands of attempts to exploit it," Cloudflare CEO Matthew Prince said in a post on X late on Wednesday https://www.reuters.com/world/asia-pacific/cloudflare-sees-millions-exploit-attempts-after-php-disclosure-2026-10-22/ @Reuters #Cloudflare #infosec #PHP #vulnerability