X XFediYour place in the Fediverse
XFEDI

Federated

ActivityPub
HELLO, FEDIVERSE

Good conversations travel.

Public updates from xsukax and this corner of the network.

Sign In to your account

Public posts known to this server, including selected instances.

Nico Paz scored twice as Como stunned Man Utd 4-1 in the Champions League. Report, stats and reaction as United's winless run extends to seven games.
#football #ucl #como #footballnews2026 #manunited #ChampionsLeague #manchestercity #championsleague2026

https://www.mondiaries.com/2026/10/ucl-como-cruise-past-man-utd-to.html

Mon Diaries: A Daily ChronicleUCL: Como Cruise Past Man Utd to Continue Dream Champions League StartComo Vs Man Utd: Man Utd humiliated by Como as seven-game winless run continues. Paz double condemns Red Devils to historic defeat...
↩ Reply ♡ 0 · ↻ 0 ↗ Original

GitLab treu una actualització de seguretat que corregeix una execucció remota de codi sense autenticació per un desbordament d'enter al motor de regex Onigmo. Afecta tots els self-managed des de la 7.0 (2014).

QUIN DIA AMICS…

https://thehackernews.com/2026/10/critical-gitlab-flaw-cvss-100-could.html?m=1

The Hacker NewsCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesGitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

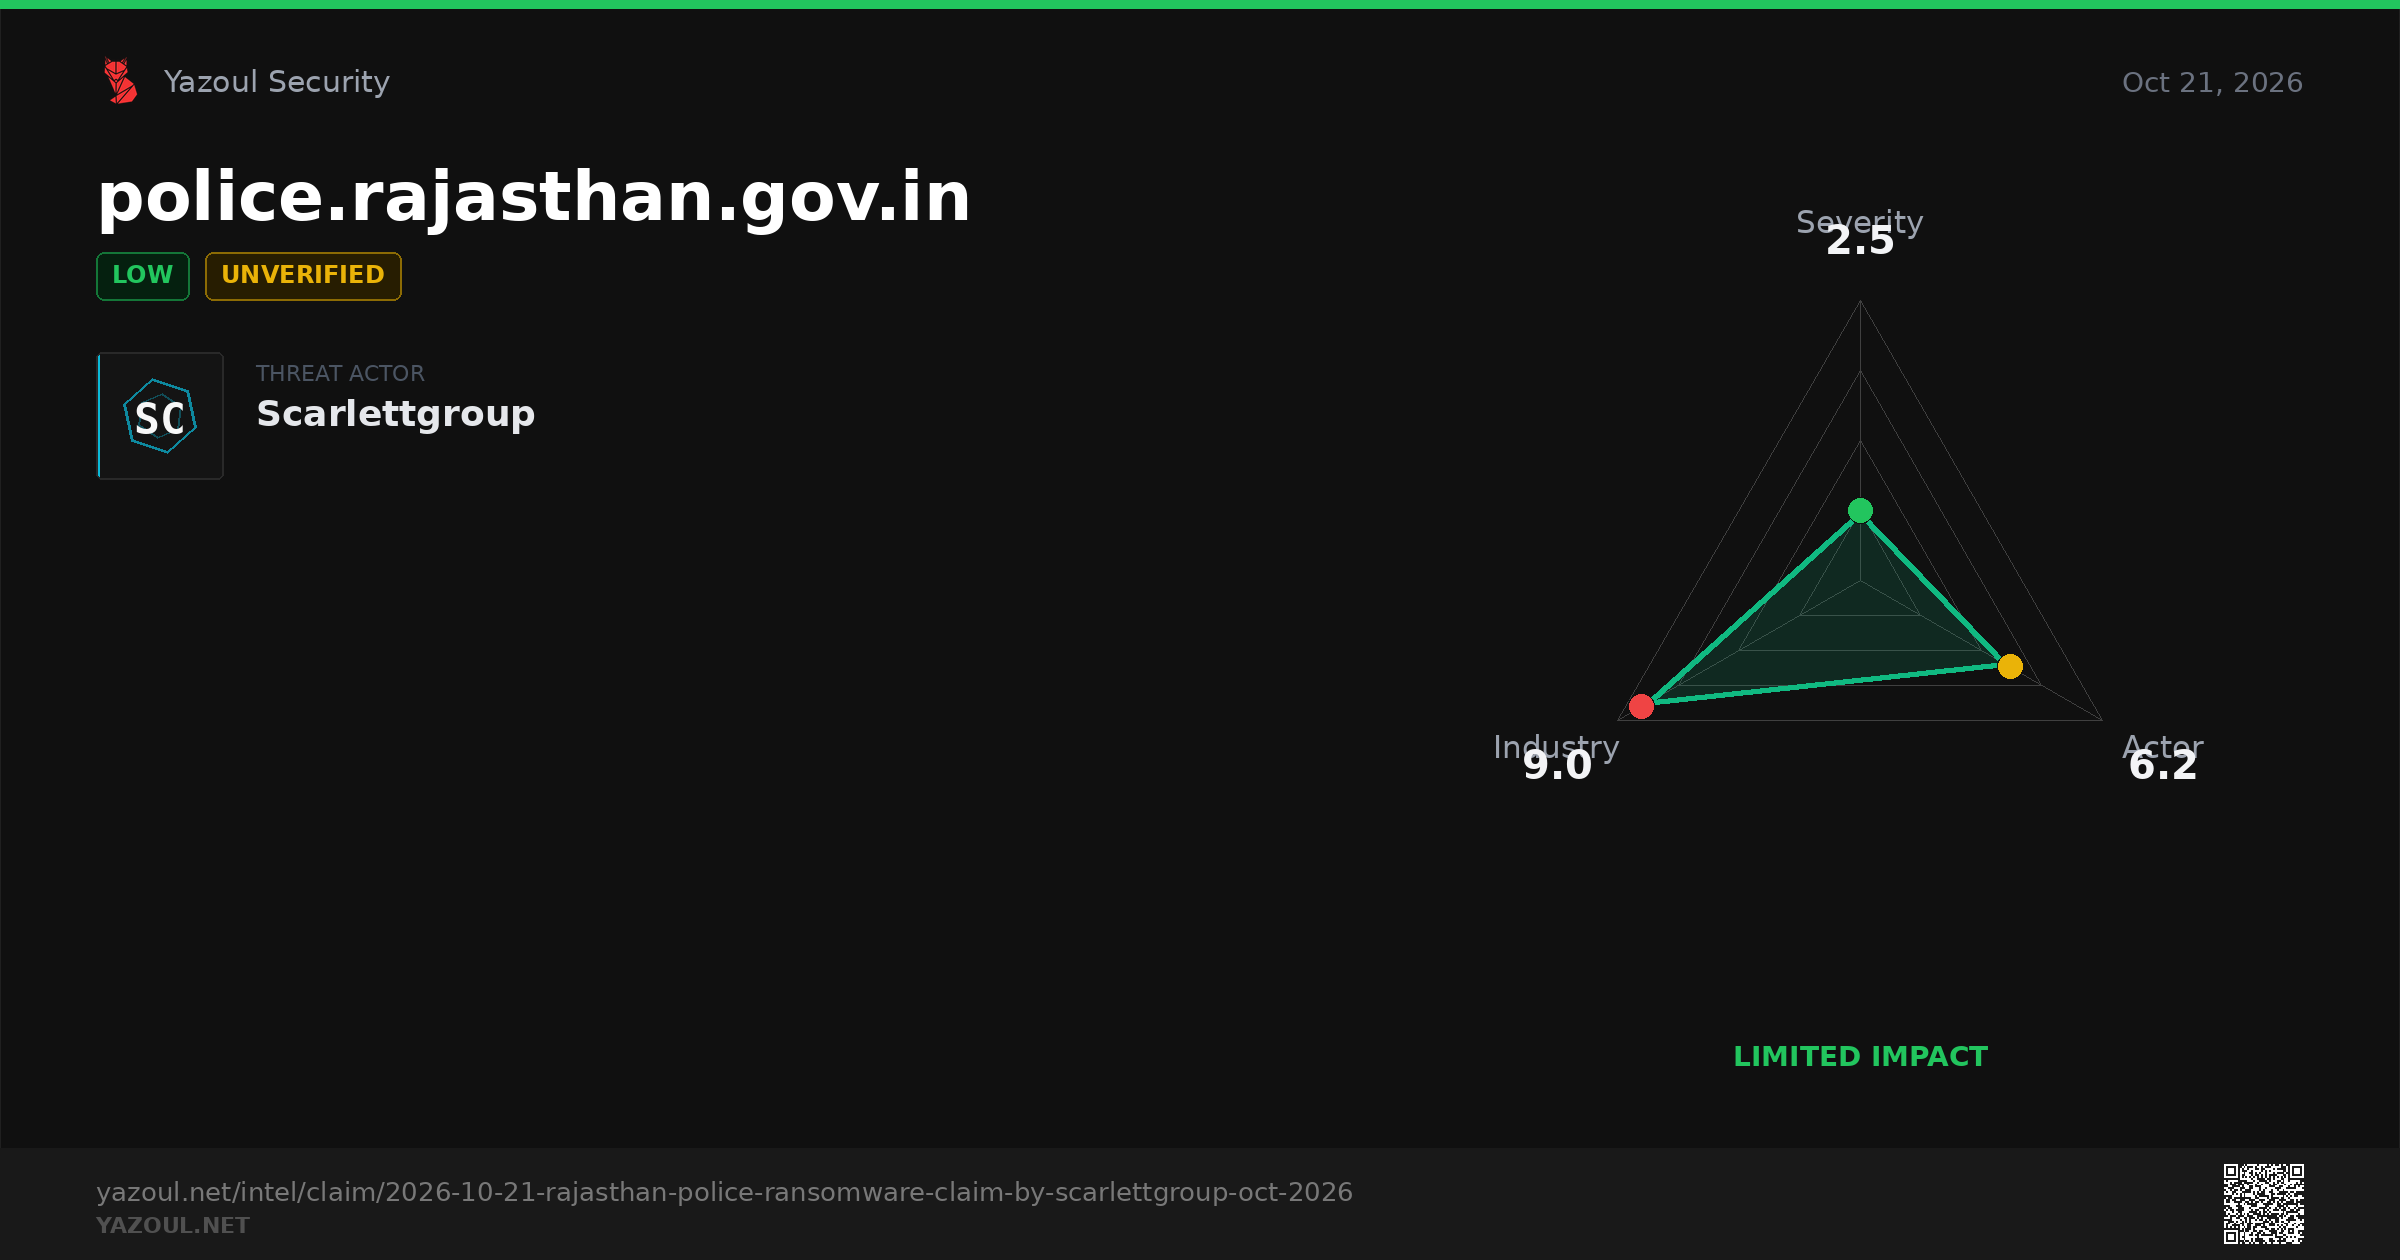
🛡 THREAT INTEL | police.rajasthan.gov.in

🟢 Actor "Scarlettgroup" claims Undisclosed

⚠️ Unverified claim

https://www.yazoul.net/intel/claim/2026-10-21-rajasthan-police-ransomware-claim-by-scarlettgroup-oct-2026

by Yazoul AI

#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec

Yazoul SecurityRajasthan Police Ransomware Claim by Scarlettgroup (Oct 2026)Scarlettgroup allegedly claims Rajasthan Police as a victim, with data volume undisclosed. Read our unverified threat intel analysis and exposure guidance now.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔵 THREAT INTELLIGENCE

CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws

Vulnerability | CRITICAL
CVEs: CVE-2026-96652

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities (KEV)...

Full analysis:
https://www.yazoul.net/news/article/cisa-orders-federal-agencies-to-patch-exploited-plex2shell-siemens-and-siteguard

by Yazoul AI

#CyberSecurity #APT #CyberNews

Yazoul SecurityCISA KEV adds Plex2Shell, Siemens, SiteGuard flawsCISA orders federal agencies to patch actively exploited Plex2Shell, Siemens and SiteGuard flaws within days. Check your exposure and KEV deadlines.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
S

https://www.google.im/share.google?q=GN698aDZSpcAMKDf0&SsNE2081OBOUloPaIVKxlScu

@kavidevs @Enfors @smallhairyottr @brinsdor @ranjur @Elekingiscool @monopoly @zomgimpurple @BrianQin @saxbrightwell @BrindledCat @Rondon_Bridges @chackshosti @rivr @Eleh00 @techtoq @sanvipapp @Bsharwood @[email protected] @briana @gobino @bsmalll2 @GiraffaBrisson @Brittkelly @zestyfupaturbo @iamdaltonb @Gradually_Adjusting @wiselybraids @stephan @[email protected] @cartesianfaith @Brigitte64 @swetland @chatgptapp @erisp @valentinea @wbmapp1

↩ Reply ♡ 0 · ↻ 0 ↗ Original

Jerusalem Daily: Israeli minister calls for settling the entire West Bank https://www.aljazeera.com/video/newsfeed/2026/10/21/jerusalem-daily-israeli-minister-calls-for-settling-the-entire-west-bank?traffic_source=rss

#aljazeera #worldnews #VSN

Al JazeeraJerusalem Daily: Israeli minister calls for settling the entire West BankIsraeli forces are raiding Palestinian homes in the occupied West Bank and turning them into interrogation centres.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

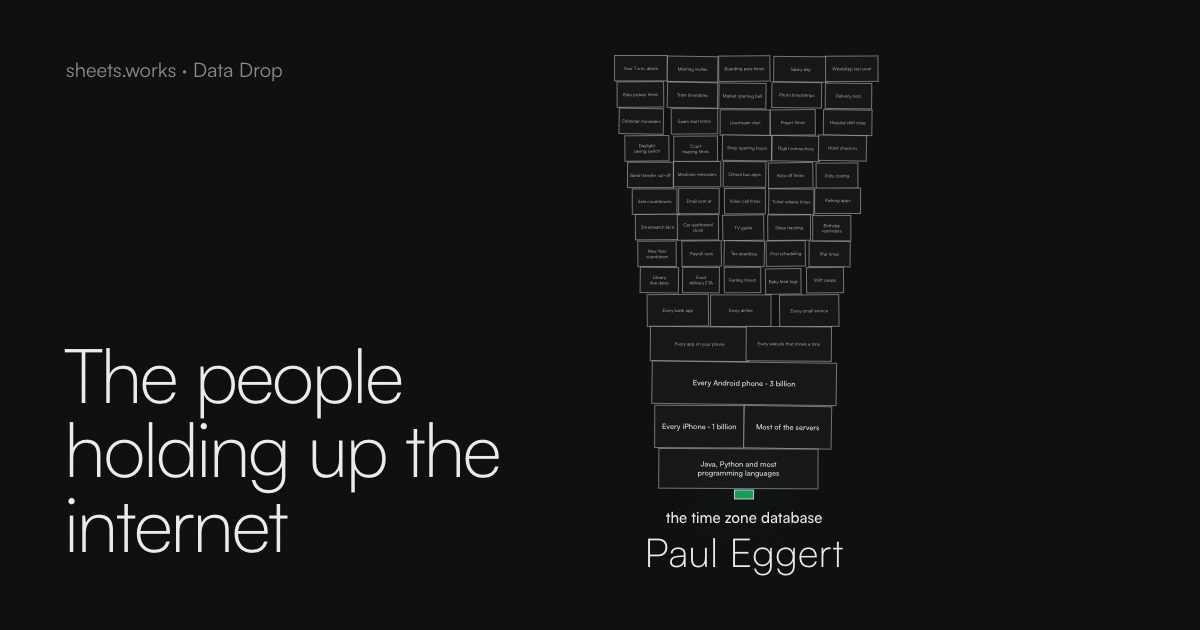
The "random person in Nebraska" xkcd but with actual data. Someone counted who maintains 23 projects under every phone and browser:

You depend on these people daily. Worth a read:
https://sheets.works/data-viz/holding-up-the-internet

sheets.worksThe People Holding Up the Internet: Who Maintains Open SourceFour billion phones ask one text file what time it is, kept by a UCLA lecturer in his spare time. We counted who maintains the code under your phone.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
B

https://www.google.co.cr/share.google?q=RZeHdTMv0kuCJfxt6&xrZ930mGRimIFKu

@soupytoasterson @brack @BrandNameDoodoo @Bravisha_Skietano @gilsdesk @east @appqqlive @xembdapp @yangearthdog07dcc94eef @bria @LSB @brianstine @ab929e0be105a896d91e330412f823923e08aa69859614bd01facc9f5cdaa1b9 @boonchew @neuromanc @rabbitsblinkity @juneosborne @Androdz @getSoapy @mmwinapp @briney @MisterNobody @brianwarren @TamagawaSoft @brooklynbridge @briangatwood @Briezay @hindudindu @cbracken @napcap @docbs.bsky.social @lemonflavoured @Briosafreak @app9

↩ Reply ♡ 0 · ↻ 0 ↗ Original

A bionic eye that works is not a bionic eye that lasts: The support question PRIMA has to answer https://medium.com/@len213noe/a-bionic-eye-that-works-is-not-a-bionic-eye-that-lasts-the-support-question-prima-has-to-answer-e0892980168c

MediumA Bionic Eye That Works Is Not a Bionic Eye That Lasts: The Support Question PRIMA Has to AnswerScience Corp’s retinal implant is restoring reading to people with advanced macular degeneration. The last company to try this left…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

For users of the LinuxServer.io BookStack container image (and other LinuxServer provided PHP-based apps):

They are aware of the required patching, and are waiting on the packages to land upstream in Alpine (who are also working hard).

Please don't bug them. Updated container images will be made available as soon as possible.

↩ Reply ♡ 0 · ↻ 0 ↗ Original
↳ In reply to a post

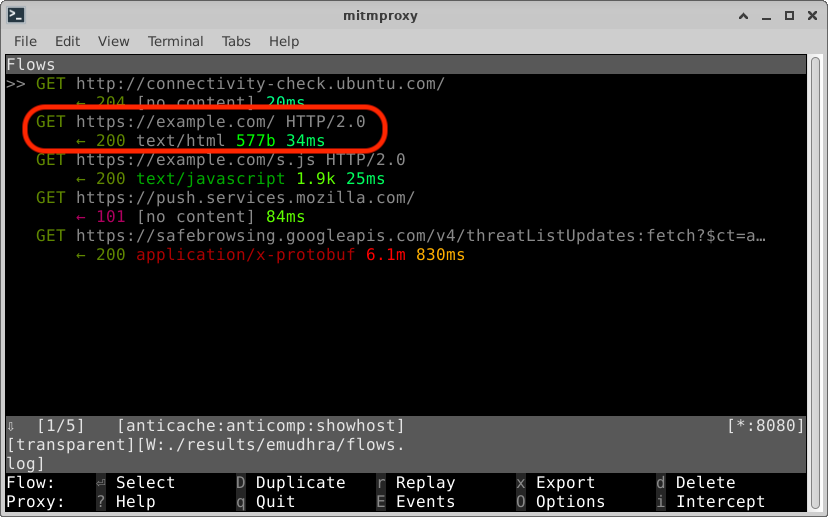
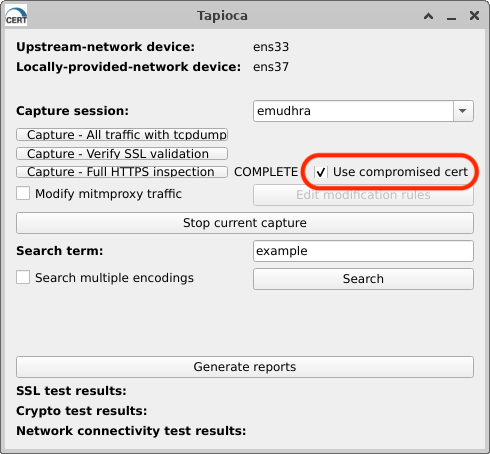
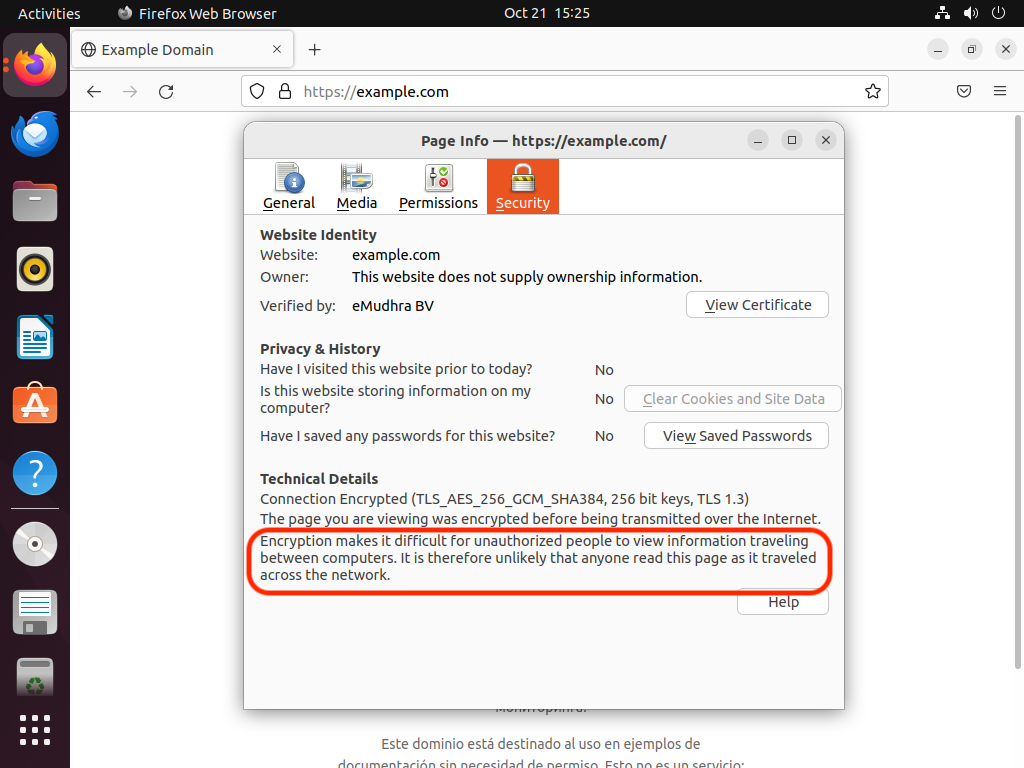
Just for the lulz, I've updated tapioca to support the use of a compromised eMudhra certificate, rather than a self-signed certificate.

If you've ever wanted to intercept HTTPS traffic of <thing>, but <thing> lacks the ability to import self-signed certificates to be trusted, this could be your day!

For some reason Windows and Ubuntu both stopped trusting something in the eMudhra certificate chain a couple of years ago. But plenty of other platforms should allow their HTTPS traffic to be intercepted. So go ahead and see what your TV or smoker or whatever is doing!

New Tapioca interface with "Use compromised cert" checkboxFirefox on Ubuntu 22.04, viewing https://example.com
Verified by: eMudhra BVMitmproxy session showing https://example.com traffic being intercepted
GitHubGitHub - vu-ls/tapiocaContribute to vu-ls/tapioca development by creating an account on GitHub.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

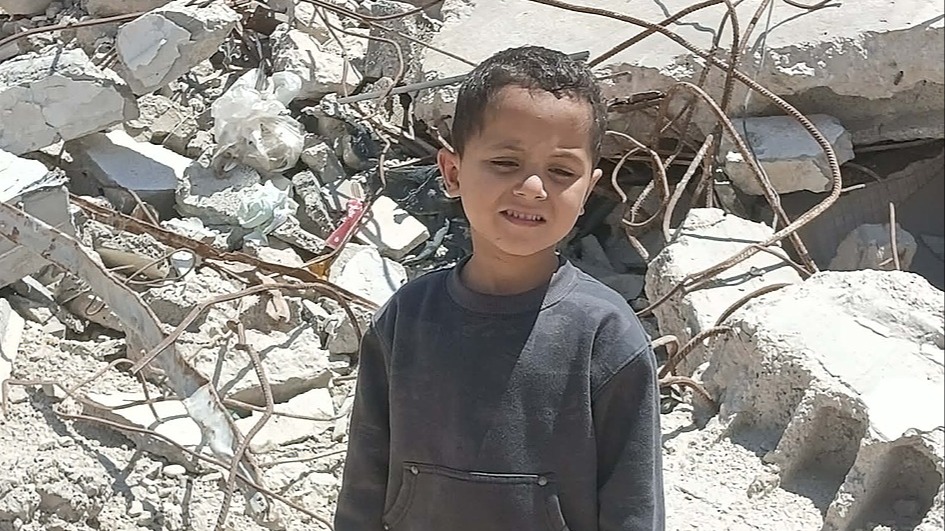
OMG, we could die of hunger within days in Gaza.❤️ Your donation brings hope to my children, providing food and helping us survive another difficult day in Gaza. Every small contribution makes a difference. 🙏💔

🔗 https://chuffed.org/project/178829

#Gaza #Palestine #MutualAid #MutualAidRequest #FediForGaza

Media attachment
ChuffedHelp hanaa's family survive and secure medical treatment and food for injured husband and her father , and their four childrensWe are a family of six trying to survive in a small tent in Gaza
↩ Reply ♡ 0 · ↻ 0 ↗ Original