#IronFox v158.0.1 is now available, go update! :)
NOTE: 158.0.1 isn't yet live on Accrescent, due to issues with their developer console that will hopefully be resolved soon.
 IronFoxIronFoxThe private, secure, user first web browser for Android
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.
#IronFox v158.0.1 is now available, go update! :)
NOTE: 158.0.1 isn't yet live on Accrescent, due to issues with their developer console that will hopefully be resolved soon.
IronFoxIronFoxThe private, secure, user first web browser for Android
Higashiyama, 113th Emperor of #Japan, was born OTD in 1675 https://cromwell-intl.com/travel/japan/kofun/konabe.html?s=mb #travel #history
 Bob's Pages of Travel, Linux, Cybersecurity, and MoreKonabe Kofun — Megalithic Tombs of Japan's Ancient RulersKonabe Kofun is a megalithic tomb with a distinctive keyhole shape. Kofun were built in Japan from the early 3rd to the early 7th century CE. Today they are believed to be the tombs of Emperors.
🚨New ransom group blog posts!🚨
Group name: SilentRansomGroup
Post title: Porter Hedges LLP
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/SilentRansomGroup/Porter%20Hedges%20LLP
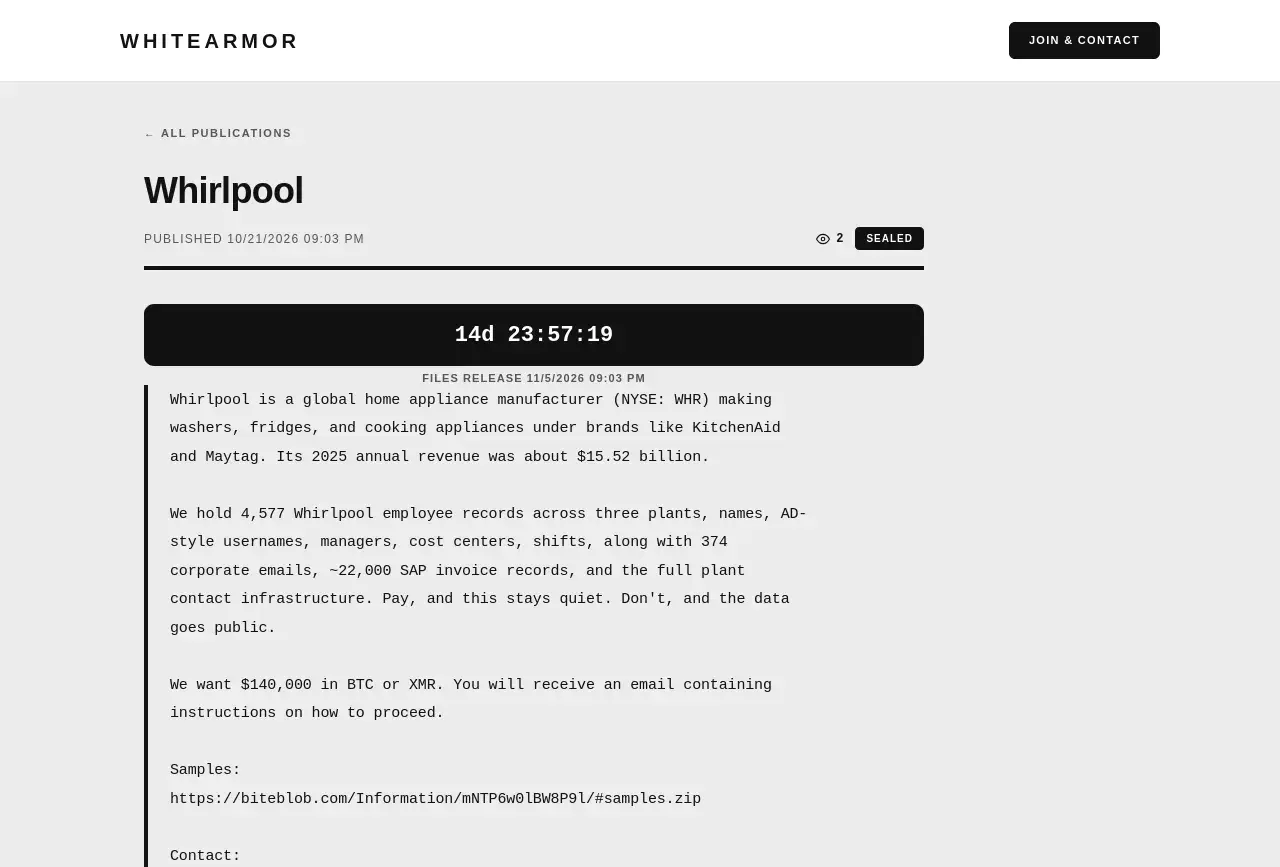
Group name: Whitearmor
Post title: Whirlpool
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/Whitearmor/Whirlpool
#ransomware #cti #threatintelligence #cybersecurity #infosec
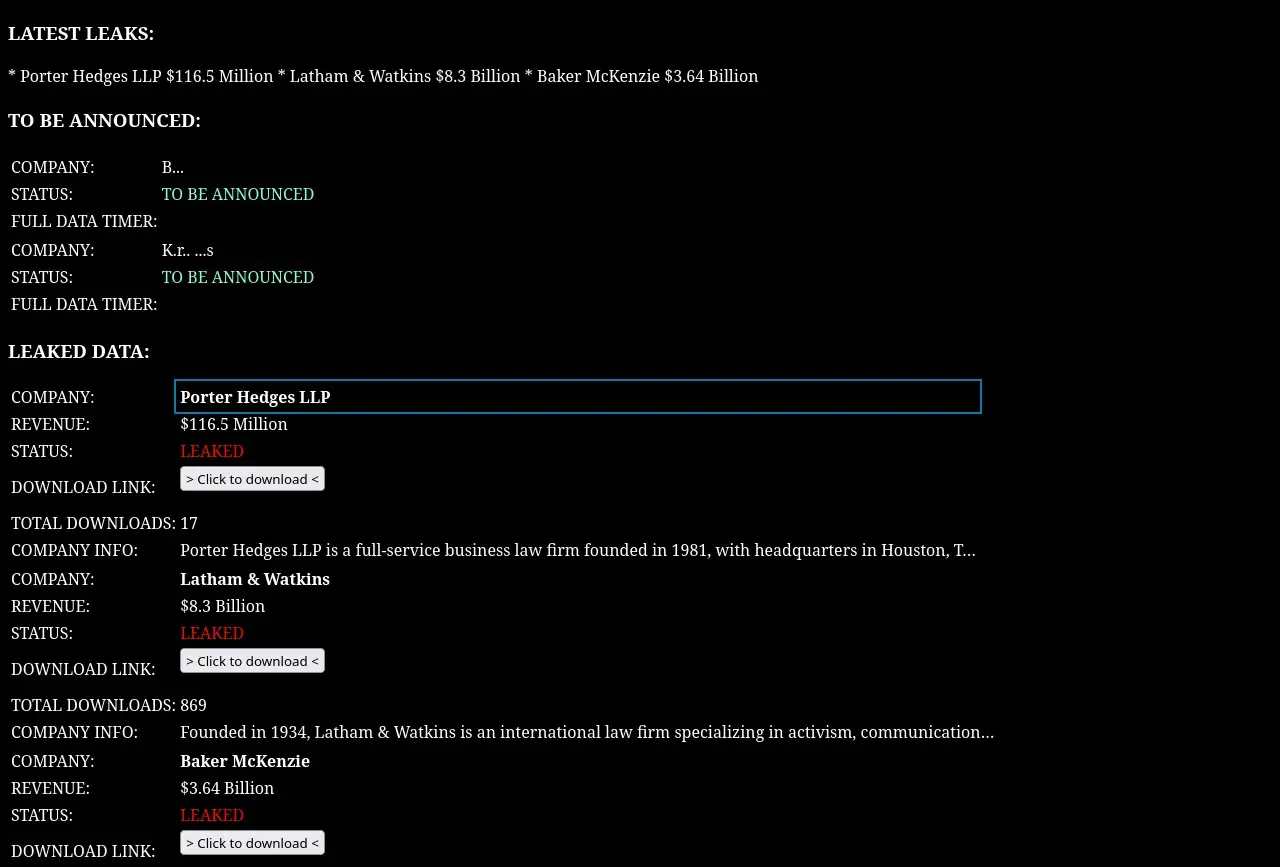
 CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.

Österreicherin: Ex-Notenbankchef Matolcsy festgenommen
What a day
@gottalaff.bsky.social FACT: the trump regime fucking kidnapped a foreign head of state and installed a puppet regime, like 4 months ago.
Where's Maduro now? When are the Venezuelan elections?
 cara.appArborlune (@arborlune) | Cara - Artist Social & Portfolio PlatformDay 17: Bamboo
#plantober #plantober2026
#illustration #art #painting #dailyart #dailysketch #drawing #1draw #speedpainting
#leaf
“It’s unlikely Musk acted alone. Reuters reported last week the decision to sabotage Ukraine came from the White House, the implication being it was Donald Trump’s. But Musk said publicly that the administration did it. Administration sources said publicly Musk did it. Common sense says both did. The Journal said Musk’s team contacted the White House to “coordinate messaging.” A source told the Telegraph: “The reality is that they were both in it.””
https://www.editorialboard.com/elon-musk-is-too-big-to-trust/
 The Editorial BoardElon Musk is too big to trustHe's going all-out to stay out of jail.
A German cunt has just told me that there are no English speaking EU countries and to "speak Irish"
What a fucking asshole.
More trouble in Galicia: Poland has reportedly paused a large military aid package for Ukraine after the Lviv regional council declared 2027 a year honoring the UPA, a WWII nationalist army that killed tens of thousands of ethnic Poles. https://www.rbc.ua/rus/news/polshcha-prizupinila-peredachu-ukrayini-paketa-1792600955.html
 РБК-УкраїнаПольща призупинила передачу Україні пакета зі зброєю через новий скандал, - джерелоПодробиці читайте на сайті
and we have php82 too...
Muy triste noticia: https://observador.cr/otra-libreria-historica-cerrara-en-costa-rica-nueva-decada-se-despide-tras-46-anos-cerca-de-la-ucr/
 El Observador CROtra librería histórica cerrará en Costa Rica: Nueva Década se despide tras 46 años cerca de la UCREl cierre de Nueva Década se suma a los de las librerías Lehmann y Cartago durante este 2026. Acá los detalles.
From AP: Christian Watson held onto confidence after tearing his ACL https://www.youtube.com/shorts/wroDspXcr9c?utm_source=dlvr.it&utm_medium=mastodon * VSN-GDPM c1996 #news #SupportIndependentMedia #vsn
From AP: Do Trump supporters expect $5,000 checks if the
GOP wins the midterms? https://www.youtube.com/shorts/2CXnATFkzL4?utm_source=dlvr.it&utm_medium=mastodon * VSN-GDPM c1996 #news #SupportIndependentMedia #vsn
TAKEMITSU Aya #竹光あや
#AyaTAKEMITSU #TAKEMITSU_Aya #kinbaku #shibari #rope #JapaneseRopeBondage #crotchRope #nurse #costume #SexyJapanese #SexyAsian #gravure


4 yıldır süren savaş bitiyor mu? Zelenski’den barış anlaşmasına onay
 ABC Haber4 yıldır süren savaş bitiyor mu? Zelenski’den barış anlaşmasına onayUkrayna Devlet Başkanı Volodimir Zelenski, mevcut cephe hattının korunmasını öngören bir barış anlaşmasını kabul edebileceğini açıkladı. Fox News’e konuşan Ze..
https://www.google.mu/share.google?q=Wgr6tLoCiWHzXLROp&PkuN7149IgiGDM
@brentharrell @Heart_Break1 @MysticBrew @brewere @sergeyb @Marmalade @BrownIsBeautiful @parimalkumar @brodriguesco @Puppetcams @jCarttarBrooke @brot @markb @brentg @breaksaigaiidx @slicebread @BRESPI @JoergRR @mr0vka @lightfootbrosgames @herestomwiththeweather @creativityfound @broccoliccoli @garow @brokenbulb @brokenbear @gothicaltomb @Broomicorns @BremboTheFourth @maondoza @dorisbrockmann.bsky.social @Captain_bros @BrokenOpenHart @corpubro @bre @So_Breizh
Et donc, Emmanuel #MACRON aura réussi à faire exploser le taux d'intérêt de la dette française.
Ce n'est pas le seul indicateur tout pourri dans son carnet de correspondance, tant s'en faut.
C'est #violent, ça, ou pas ?
#France
#LePlusGrandPrésidentDeTousLesTemps
#ParceQueCestLeurProjet
if an orb is in the forest and there is no paranormal detective to find it, does it really exist?
https://www.youtube.com/watch?v=Qvv3URsN5gs
Oh, I'm so sorry, Andre. Is your Molly comedown relevant to global security? Guys, We are shadow-running the free world here. Let's try to take this job seriously.
thats why php packages are in community. only latest stable is supported. currently 3.24
RE: https://mstdn.ca/@avilewis/117480909552262880
That the leader of the federal NDP is pouring one out for BioWare, that's pretty dope in my books.
This is private equity, this is what it does. Buy up businesses, run them into the ground, and rip them apart for short-term profit. The developers at BioWare know how to run the studio. They know how to make the games we all love. They should be given the first opportunity - a
Mastodon CanadaAvi Lewis (@[email protected])This is private equity, this is what it does. Buy up businesses, run them into the ground, and rip them apart for short-term profit. The developers at BioWare know how to run the studio. They know how to make the games we all love. They should be given the first opportunity - and the federal support - to buy it and run it themselves. And if we want to avoid the Mass Effect effect in Canada, wEven though things have sped up, the quality of the end result still entirely depends on the amount of time and care (blood and sweat) spent on it.
People are asking when fixes for php are landing in alpine <old>. we have php85, php84 and php83. five maintained branches (edge, v3.24, v3.23, v3.22, v3.21). This is 15 packages that needs to be fixed. test suite regressions needs to be handled. It is not realistic to expect all that work be done for every php security fix for two years for free.
If you care about one branch, help us fix it. We may accept merge requests if CI is green, but don't *expect* anything
ooh yeah we're so back
🚨🇺🇸 South Carolina man arrested after tip involving Google account
Ryan Mark Hannan, 33, was arrested by the Horry County Sheriff’s Office Internet Crimes Against Children Task Force for allegedly possessing child sexual abuse material.
⠀
Investigators opened the case after receiving a tip from the National Center for Missing and Exploited Children regarding suspected criminal activity connected to a Google account.
⠀
Hannan was charged with third-degree sexual exploitation of a minor. Authorities said the charge involved between 26 and 250 images.
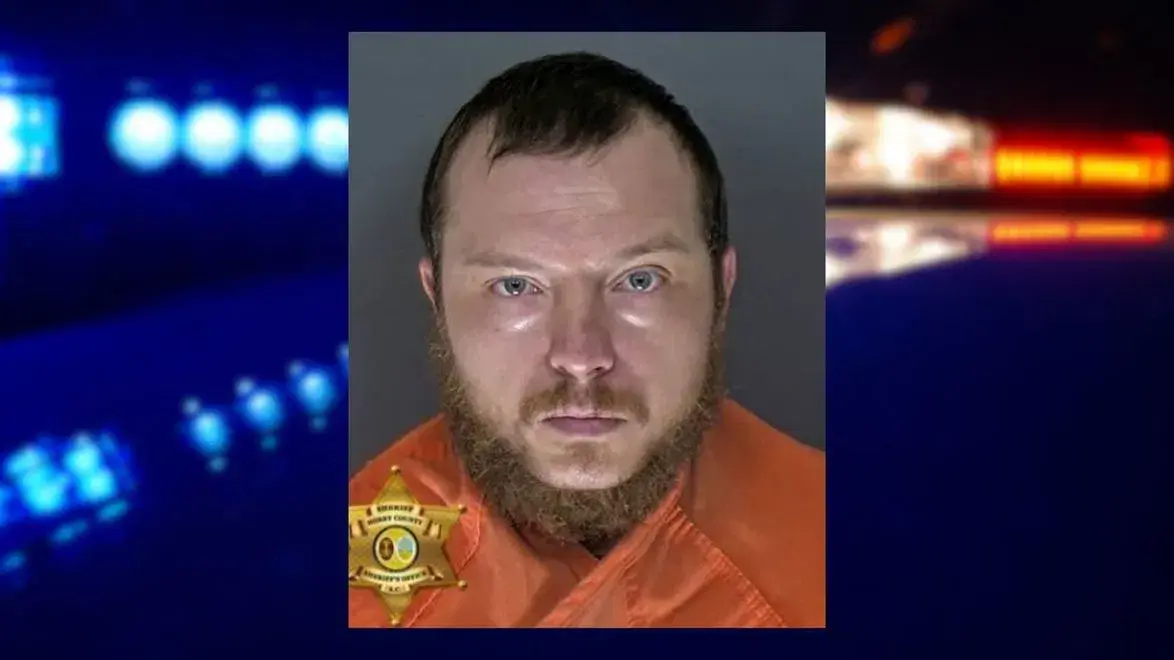
 WPDEGoogle account tip leads to arrest of Horry Co. manThe Horry County Sheriff's Office has arrested a man for possessing child sex material.
PARTENAIRE HACKFEST 2026 SPONSOR : WIZ
Our 18th edition, Hackfest Level Up, would not be possible without our sponsors. And this year, we are happy to have Wiz, a KIOSK sponsor!
If you want to learn more about this company’s mission, visit their website https://wiz.io/
PS: YOU CAN STILL BUY YOUR TICKET for October 29–31, 2026 at the Convention Center of Québec ;) More info: https://hackfest.ca/en/?utm_source=mastodon&utm_medium=socmed&utm_campaign=sponsors
 wiz.ioWiz: AI Cybersecurity for All Your Cloud and AI ApplicationsWiz connects code, cloud, and runtime into one agentic cybersecurity platform. Prevent risk, detect threats, and start secure – across every cloud and AI layer.
RE: https://infosec.exchange/@Spartan_1986/117480764972910966
So, that build date got me thinking. What if Canonical did implement the fix, but they are not reporting all the build digits? I know. That's stupid. But fortunately I can check on that. I've a Pro account and the server is, of course, registered with the Pro binary installed. You can force any CVE update with a the command "sudo pro fix CVE-YYYY-XXXX". So I ran the command for the two CVEs involved with this vuln. Here's what I got:
*******************************
$ sudo pro fix CVE-2026-109618
CVE-2026-109618: PHP vulnerabilities
- https://ubuntu.com/security/CVE-2026-109618
1 affected source package is installed: php8.3
(1/1) php8.3:
A fix is available in Ubuntu standard updates.
The update is already installed.
✔ CVE-2026-109618 is resolved.
$ sudo pro fix CVE-2026-109619
CVE-2026-109619: PHP vulnerabilities
- https://ubuntu.com/security/CVE-2026-109619
1 affected source package is installed: php8.3
(1/1) php8.3:
A fix is available in Ubuntu standard updates.
The update is already installed.
✔ CVE-2026-109619 is resolved.
*******************************
Damn it Canonical! Digits f-ing matter!!! Why do you have to be so stupid. I frankly don't even know if I can trust this. It should report the correct version with 'php -v' you numbskulls. This is why I got out of system administration in the first place.
Here’s a good laugh. When I run ‘PHP -v’ on my newly upgraded Ubuntu server, the one with PHP 8.3.6 installed, it tells me the build date is “Oct 19 2026 15:16:58”. How’s that for a swing and a miss?
Infosec ExchangeMark Bryant (@[email protected])Here’s a good laugh. When I run ‘PHP -v’ on my newly upgraded Ubuntu server, the one with PHP 8.3.6 installed, it tells me the build date is “Oct 19 2026 15:16:58”. How’s that for a swing and a miss?