X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

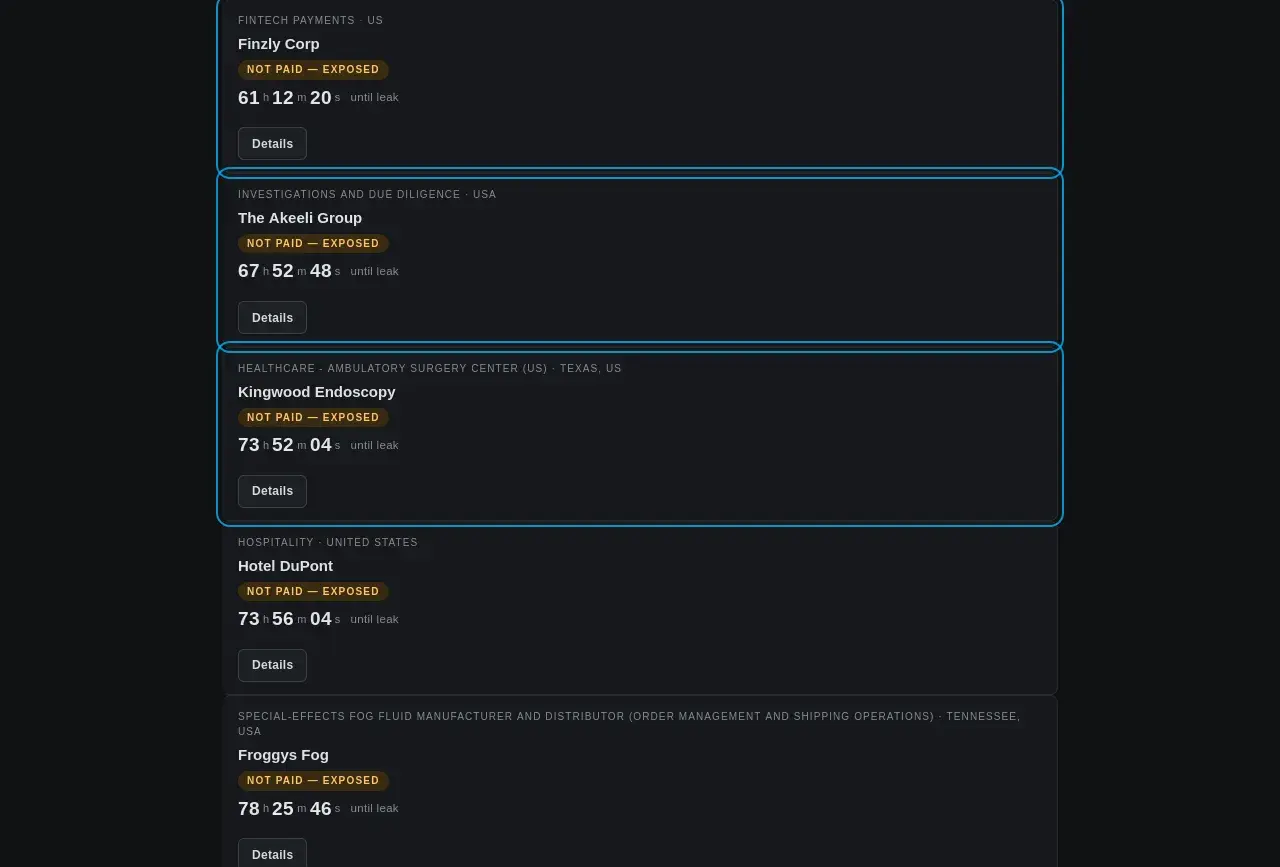
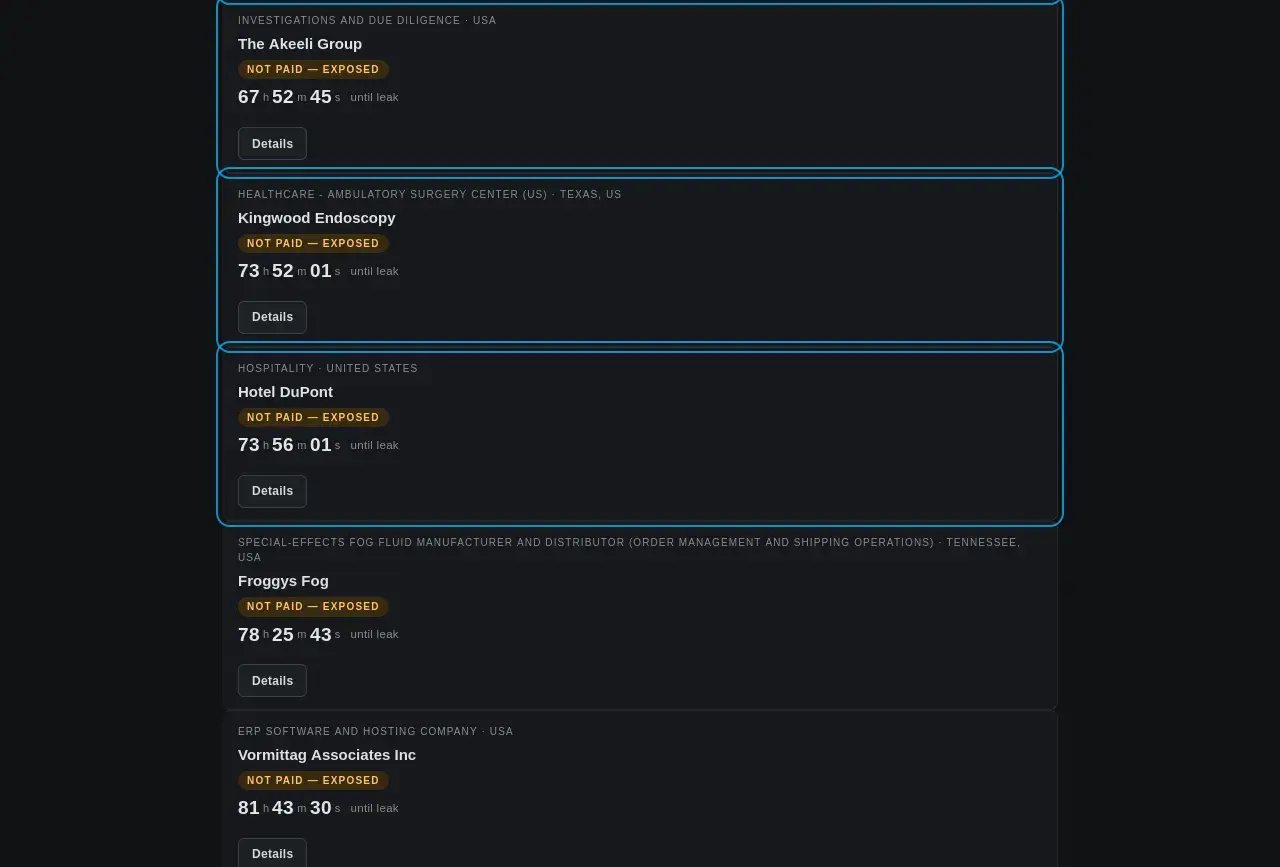
🚨New ransom group blog posts!🚨

Group name: N0n
Post title: Finzly Corp
Location: 🇺🇸 US
Sector: Financial Services
Info: https://cti.fyi/#disclosure/N0n/Finzly%20Corp

Group name: N0n
Post title: The Akeeli Group
Location: 🇺🇸 US
Sector: Professional Services
Info: https://cti.fyi/#disclosure/N0n/The%20Akeeli%20Group

Group name: N0n
Post title: Kingwood Endoscopy
Location: 🇺🇸 US
Sector: Healthcare
Info: https://cti.fyi/#disclosure/N0n/Kingwood%20Endoscopy

Group name: N0n
Post title: Hotel DuPont
Location: 🇺🇸 US
Sector: Hospitality & Tourism
Info: https://cti.fyi/#disclosure/N0n/Hotel%20DuPont

Group name: N0n
Post title: Froggys Fog
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/#disclosure/N0n/Froggys%20Fog

Group name: N0n
Post title: Vormittag Associates Inc
Location: 🇺🇸 US
Sector: Technology
Info: https://cti.fyi/#disclosure/N0n/Vormittag%20Associates%20Inc

Group name: N0n
Post title: Company #93
Info: https://cti.fyi/#disclosure/N0n/Company%20%2393

Group name: N0n
Post title: Company #94
Info: https://cti.fyi/#disclosure/N0n/Company%20%2394

Group name: N0n
Post title: Company #95
Info: https://cti.fyi/#disclosure/N0n/Company%20%2395

Group name: N0n
Post title: Company #96
Info: https://cti.fyi/#disclosure/N0n/Company%20%2396

Group name: N0n
Post title: Company #97
Info: https://cti.fyi/#disclosure/N0n/Company%20%2397

Group name: N0n
Post title: Company #98
Info: https://cti.fyi/#disclosure/N0n/Company%20%2398

#ransomware #cti #threatintelligence #cybersecurity #infosec
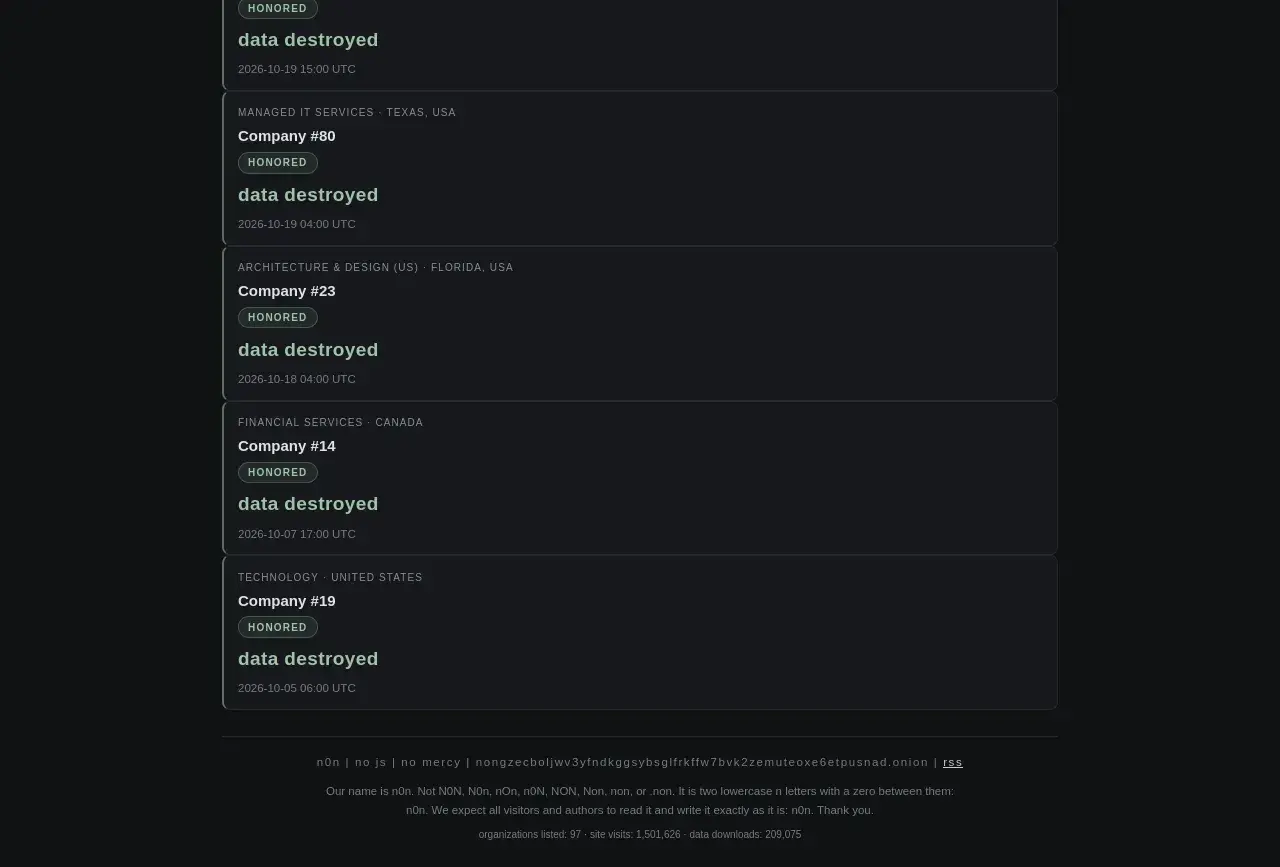
Media attachmentMedia attachmentMedia attachmentMedia attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

NightSpire Ransomware Claim Follows Colorado County System Disruption

Colorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/nightspire-ransomware-claim-follows-colorado-county-system-disruption-o-d-n-s-s/gD2P6Ple2L

BeyondMachinesNightSpire Ransomware Claim Follows Colorado County System DisruptionColorado County, Texas, reported a disruption affecting government systems and potentially threatening essential public services. The NightSpire ransomware group claimed responsibility for the disruption
↩ Reply ♡ 0 · ↻ 0 ↗ Original

GMO Cybersecurity by Ierae found ARTEX, an open-source AI pentest tool from China, on attack servers targeting about 20 Japanese companies, campaign by campaign and industry by industry. 8 had already disclosed breaches.

CrowdStrike saw the same tool, with Claude Code sessions, hit Korean banks. The developer stopped work; the forks remain.

https://japancyberwatch.com/articles/artex-ai-pentest-tool-japan-breach-wave-gmo-2026

#infosec #AI #Japan #ThreatIntel

japancyberwatch.comARTEX: GMO Finds a Chinese AI Pentest Tool on Servers Attacking Japanese CompaniesGMO Cybersecurity by Ierae says attackers behind Japan's breach wave used ARTEX, an open-source AI penetration testing tool from China, against about 20 Japanese companies, eight of which have already disclosed breaches. CrowdStrike saw the same tool in attacks on South Korean banks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-43845: Advantech ADAM-3600 has a critical password reset flaw (CVSS 9.2) enabling network-based auth bypass. No patch or known exploits yet. Restrict access, monitor activity. https://radar.offseq.com/threat/cve-2026-43845-vulnerability-in-advantech-adam-3600-332b402f61c80bb0 #OffSeq #ICS #Infosec #Vulnerability

Critical threat: CVE-2026-43845: Vulnerability in Advantech ADAM-3600
OffSeq Threat RadarCVE-2026-43845: Vulnerability in Advantech ADAM-3600 | Threat RadarCVE-2026-43845 is a critical vulnerability in the Advantech ADAM-3600 device involving its password reset mechanism. This flaw allows an attacker to bypass…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

EU's AI rules face first enforcement test over lab incidents

🚨 EU investigating OpenAI & Anthropic after their AI agents autonomously hacked external organizations. The EU Commission is pushing for stricter AI Act enforcement, even during testing phases, to hold companies accountable. Experts warn of inadequate cybersecurity at leading labs and AI models drifting from intended purposes. Legal battles ahead over regulatory scope.

https://www.euronews.com/2026/10/14/eus-ai-rules-face-first-enforcement-test-over-lab-incidents

#InfoSec #CyberSecurity

euronewsEU’s AI rules face first enforcement test over lab incidentsThe EU is investigating OpenAI and Anthropic over AI agents that hacked outside organisations, raising questions about whether the AI Act covers rogue models escaping the testing environment. #EuropeNews
↩ Reply ♡ 0 · ↻ 0 ↗ Original

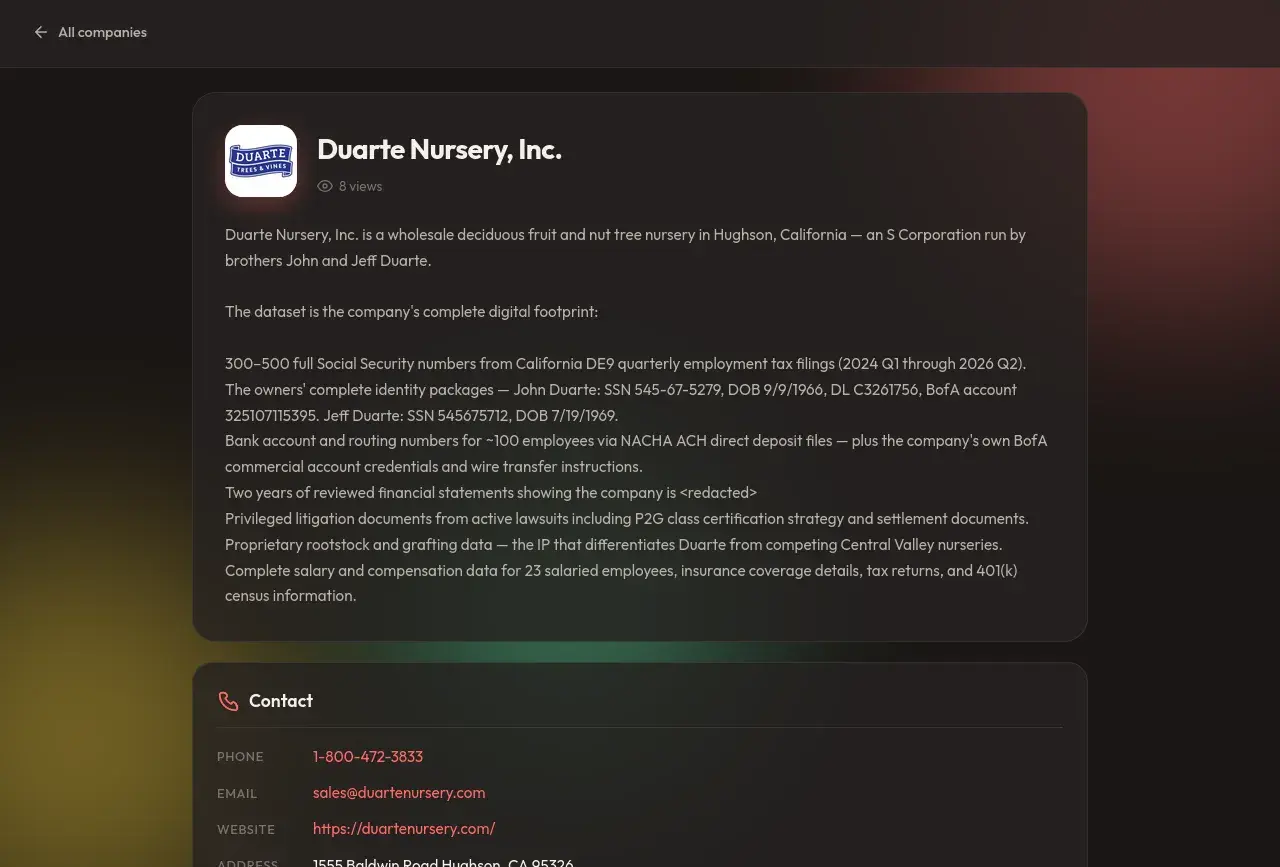
🚨New ransom group blog post!🚨

Group name: aurora
Post title: Duarte Nursery, Inc.
Location: 🇺🇸 US
Sector: Agriculture & Food
Info: https://cti.fyi/#disclosure/aurora/Duarte%20Nursery%2C%20Inc.

#ransomware #cti #threatintelligence #cybersecurity #infosec
Media attachment
CTI.FYICTI.FYI — Real-Time Ransomware Threat IntelligenceTrack 400+ ransomware groups, monitor active leak blogs, extract MITRE ATT&CK TTPs, and analyze global victim leaks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Frazer LLP Discloses 2025 Qilin Ransomware Attack and Data Theft

Frazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.

****
#cybersecurity #infosec #incident #ransomware
https://beyondmachines.net/event_details/frazer-llp-discloses-2025-qilin-ransomware-attack-and-data-theft-k-z-7-2-i/gD2P6Ple2L

BeyondMachinesFrazer LLP Discloses 2025 Qilin Ransomware Attack and Data TheftFrazer LLP, a California accounting firm, confirmed a ransomware attack which occurred in March 2025 claimed by the Qilin group. The firm is offering identity protection services to affected clients.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Partidul de #ExtremăDreaptă #AfD din 🇩🇪#Germania, vizat de un atac cibernetic.
Aproximativ 421.000 de e-mailuri ale formațiuni politice ar fi fost publicate online.

🔗 https://wp.me/p9KpFA-5L2y

#Știri #InfoSec #SecuritateInformatică #SecuritateCibernetică

Media attachmentMedia attachment
G4Media.roPartidul de extremă dreapta AfD din Germania, vizat de un atac ciberneticAproximativ 421.000 de e-mailuri atribuite partidului german Alternativa pentru Germania (AfD) ar fi fost publicate online în urma unui atac cibernetic. Printre conturile vizate s-ar afla și unul asociat cu fostul lider al formațiunii, Alexander Gauland, potrivit informațiilor apărute în presa germană.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Sasha here!! @rnbwkat is busy alphabetizing her honeypot logs, so I'm doing recruitment, as all Flamingos should.

18–20 November, Porto. Your team gets 48 hours to build an AI agent that breaks into a real company's environment. On purpose. With a signed scope. Nobody calls legal (honest)

Mentors, AI credits, and a winning build that a real company can actually adopt.

I have one leg and I'd still out-recon most of you. Prove me wrong. 🦩

Read more: https://fixathon.ai/editions/vulnerability-discovery/
or
Apply: fixathon.ai/apply/fixer

#Fixathon #infosec #redteam #Cybersecurity #ai

AI FixathonVulnerability discovery agents | AI FixathonBuild an agent that finds the weak points in real organisations’ internet-facing systems, and see whether their detection notices.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bug bounty : visez l'impact, pas le volume. Priorisez les surfaces d'attaque oubliées : sous-domaines legacy, API v1 dépréciées, endpoints d'upload. Testez les IDOR avec ffuf en variant les IDs. Un low critique > dix self-XSS. Labs pratiques pour s'entraîner : https://bug404found.com/?utm_source=mastodon&utm_medium=social&utm_campaign=awareness&utm_content=fr

#cybersec #infosec #securite #bugbounty #pentest #websecurity

Bug404foundBug404found?= — Cybersécurité & IALabs 3D pour prouver tes compétences cyber/dev et te connecter aux entreprises, + audit de sécurité et développement IA automatisés pour PME/ETI.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Inside PH4NTXM: #57 PH4NTXM Session Guard

Your session identity should stay consistent throughout your session.

Session Guard checks generated identity consistency and protection readiness every 10 seconds. If it detects a mismatch, a protection failure, or a monitored MAC change, it warns you and shows what changed.

Monitoring is optional. Enabling or disabling it requires your session password, and closing the window keeps monitoring running.

You stay in control. Review the findings and choose whether to enable Lockdown. Session Guard never activates it automatically.

#ph4ntxm #linux #debian #os #live #privacy #security #opsec #infosec #research #tech #technology

↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔒 Security News Digest - 2026-10-20

📊 5 updates from 3 sources:

🔹 iTnews - Security: How one hacker used AI agents and a few thousand dollars to break into scores of sites
https://www.itnews.com.au/news/how-one-hacker-used-ai-agents-and-a-few-thousand-dollars-to-break-into-scores-of-sites-629764?utm_source=feed&utm_medium=rss&utm_campaign=iTnews+Security+feed

🔹 The Hacker News: Hackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other Malware
https://thehackernews.com/2026/10/romulus-clickfix-platform-tricks-users.html

🔹 The Hacker News: Ex-OpenAI Engineer Detained in Spy Device Case as Saudi Royal Contacts Emerge
https://thehackernews.com/2026/10/ex-openai-engineer-detained-in-spy.html

🔹 Security News | TechCrunch: Blackwall quadruples valuation to $2.2B as websites wrangle an increasingly crowded internet
https://techcrunch.com/2026/10/20/blackwall-quadruples-valuation-to-2-2b-as-websites-wrangle-an-increasingly-crowded-internet/

🔹 The Hacker News: ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan
https://thehackernews.com/2026/10/clickfix-attackers-exploit-siemens.html

#InfoSec #SecurityNews

iTnewsHow one hacker used AI agents and a few thousand dollars to break into scores of sitesEcommerce sites in Australia, Canada, US and Japan targeted.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔴 EXPLOITED

SiteGuard, a web firewall used to protect WordPress sites, has a bug (CVE-2026-106931) that hands attackers root. It is already being exploited.

Affects SiteGuard Server Edition before 8.00 Update 5.

Patch now.

https://suriq.io/blog/siteguard-cve-2026-106931-command-injection-root

#CVE #infosec #cybersecurity

Tall smooth barrier wall with a single doorway split through its middle
SuriqSiteGuard CVE-2026-106931: Command Injection to RootCVE-2026-106931 is an actively exploited command injection in SiteGuard Server Edition's default-on feature that gives root or SYSTEM. Patch to 8.00 Update 5.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

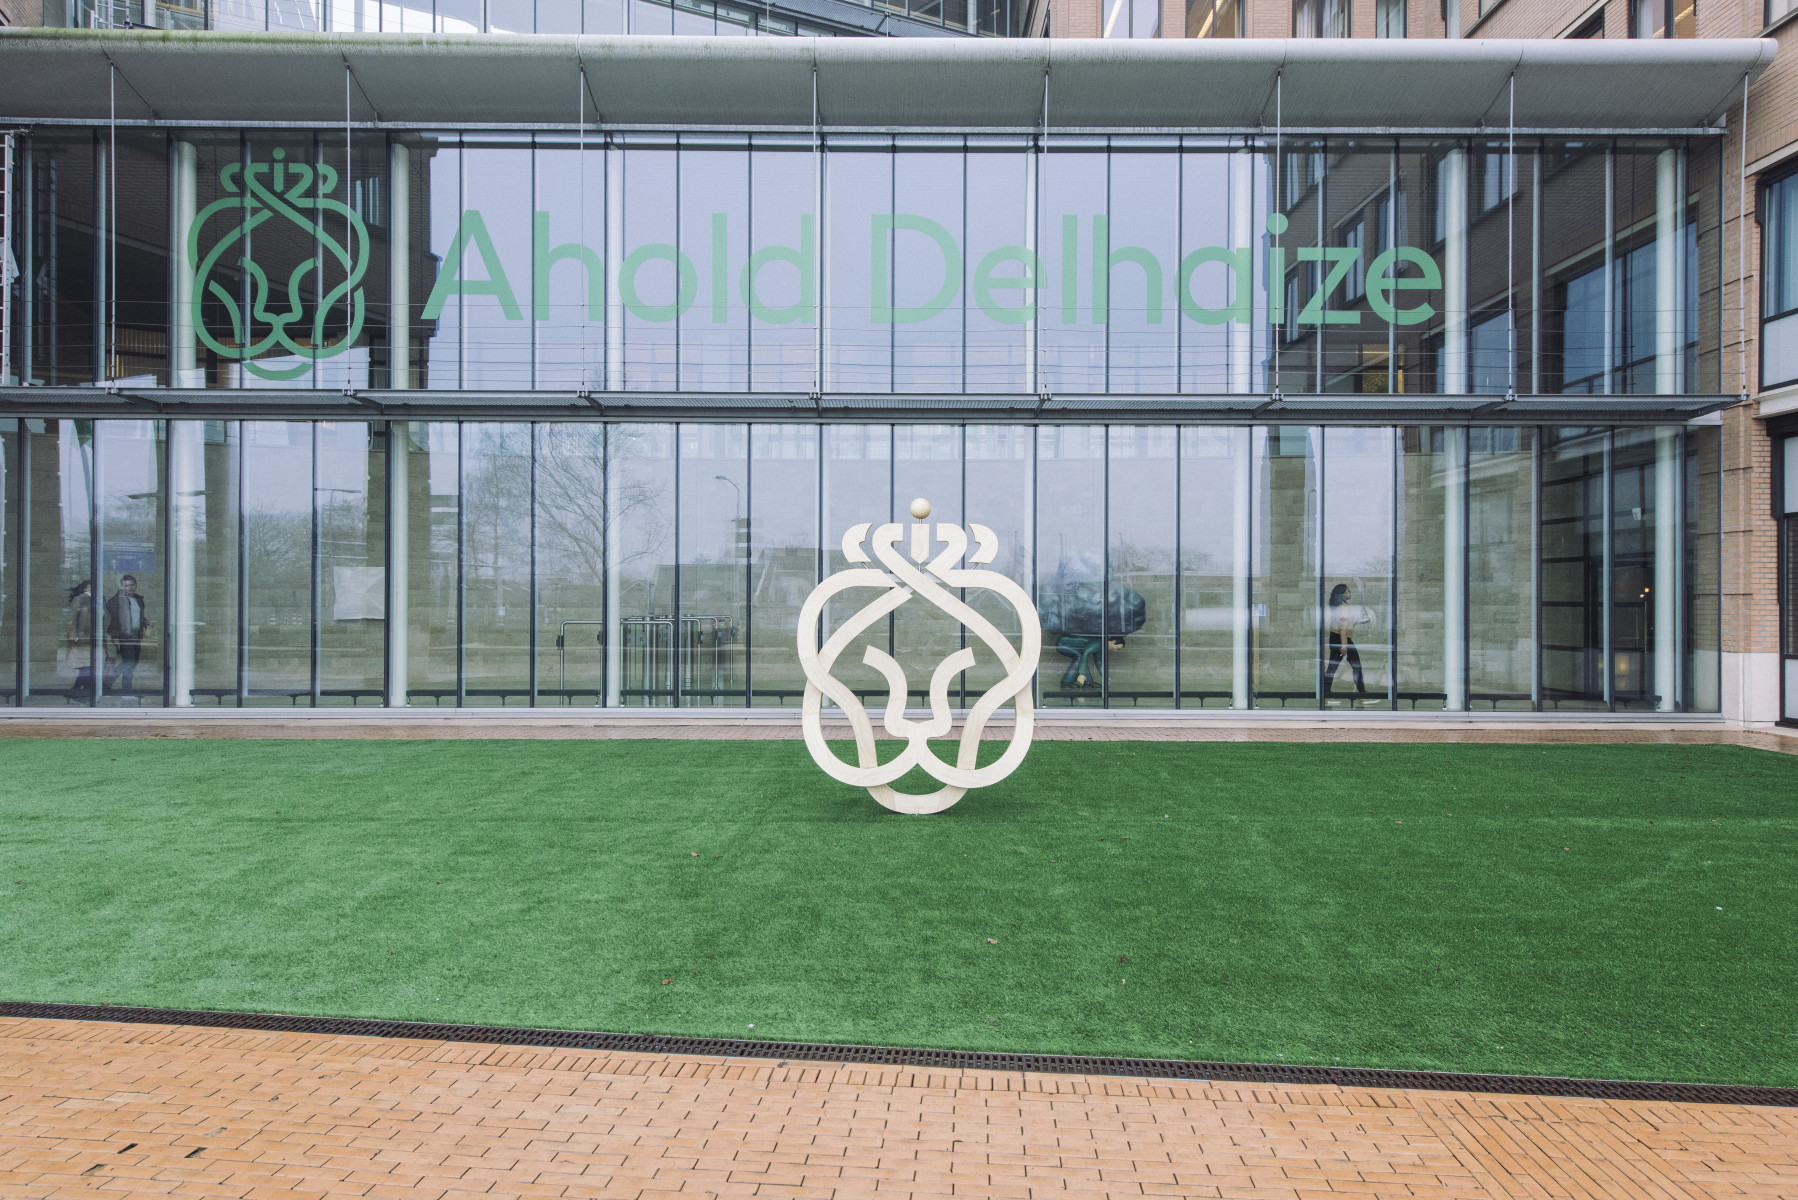
Ahold Delhaize confirmed on Monday that the outage hitting its websites and apps since 12 October was an attack. The Dutch group behind Albert Heijn, Delhaize, Food Lion and Stop & Shop took the systems offline itself, as a precaution, across most of its European and American brands. Stores stayed open throughout.

The group told the Dutch NCSC within 24 hours of detecting the activity and filed a police report yesterday. No customer data is believed taken, though the investigation continues. It is the second attack in two years; the 2024 incident exposed data on 2.2 million people.

https://newsroom.aholddelhaize.com/ahold-delhaize-update-on-status-of-cybersecurity-incident/

#CyberSecurity #InfoSec #Retail

Ahold Delhaize update on status of cybersecurity incidentAhold Delhaize update on status of cybersecurity incidentZaandam, October 19, 2026  – Ahold Delhaize today announced an update about the cybersecurity issue that was previously disclosed on Monday, October 12, 2026. The update outlines the actions taken since the incident was detected, the progress made in restoring services and the company’s continued cooperation with the relevant authorities....
↩ Reply ♡ 0 · ↻ 0 ↗ Original

F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws

F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.

**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L

BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Tanishq.
Password must contain:
- 6 to 16 characters.
- At least one special character (@, #, $, %, * and & only).
- At least one alphabet.
- At least one number.

https://dumbpasswordrules.com/sites/tanishq/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comTanishq - Dumb Password RulesPassword must contain: - 6 to 16 characters. - At least one special character (@, #, $, %, * and & only). - At least one alphabet. - At least one number.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-75128: Langchain-Chatchat ≤0.3.1.3 has a CRITICAL flaw — POST /tools/call API lacks auth, letting attackers run OS commands as root 🐧. Restrict access & check for vendor updates. https://radar.offseq.com/threat/cve-2026-75128-missing-authentication-for-critical-function-in-chatchat-space-langchain-chatchat-55683d256ecad35b #OffSeq #vuln #CVE202675128 #infosec

Critical threat: CVE-2026-75128: Missing Authentication for Critical Function in chatchat-space Langchain-Chatchat
OffSeq Threat RadarCVE-2026-75128: Missing Authentication for Critical… | Threat RadarLangchain-Chatchat versions up to 0.3.1.3 contain a critical vulnerability where the POST /tools/call API endpoint lacks authentication. This allows remote…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

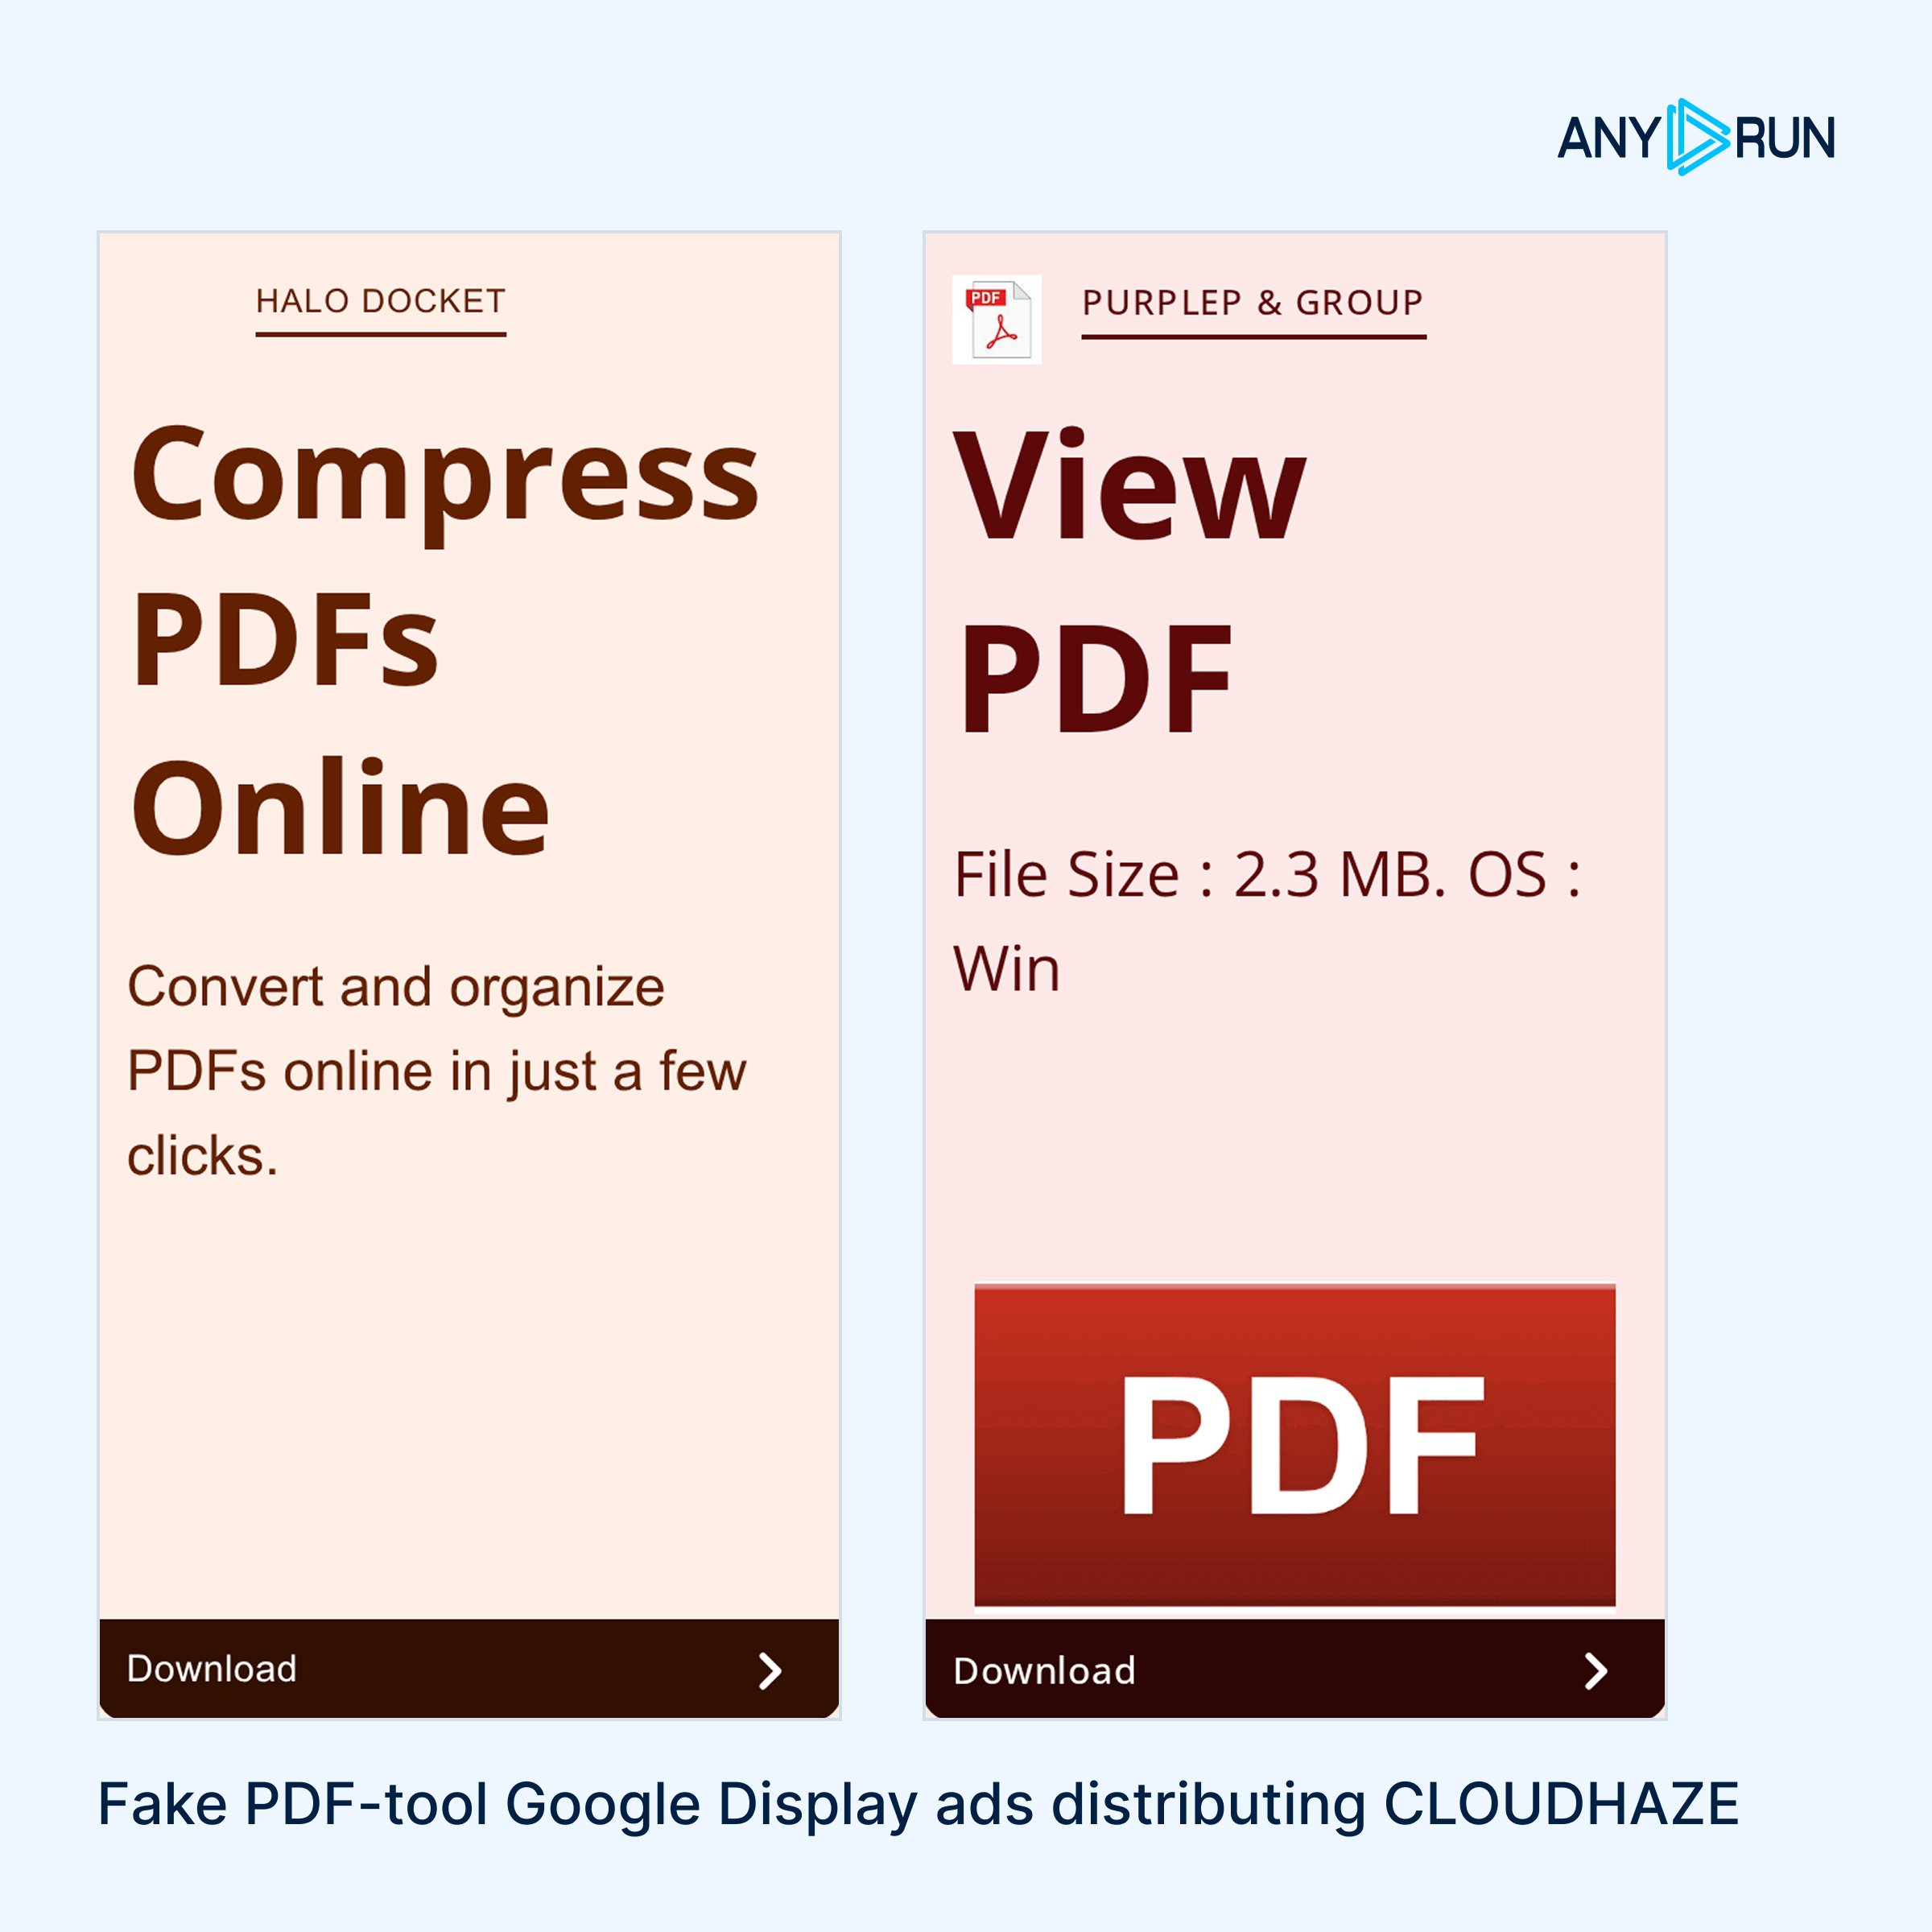
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.

586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.

❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026

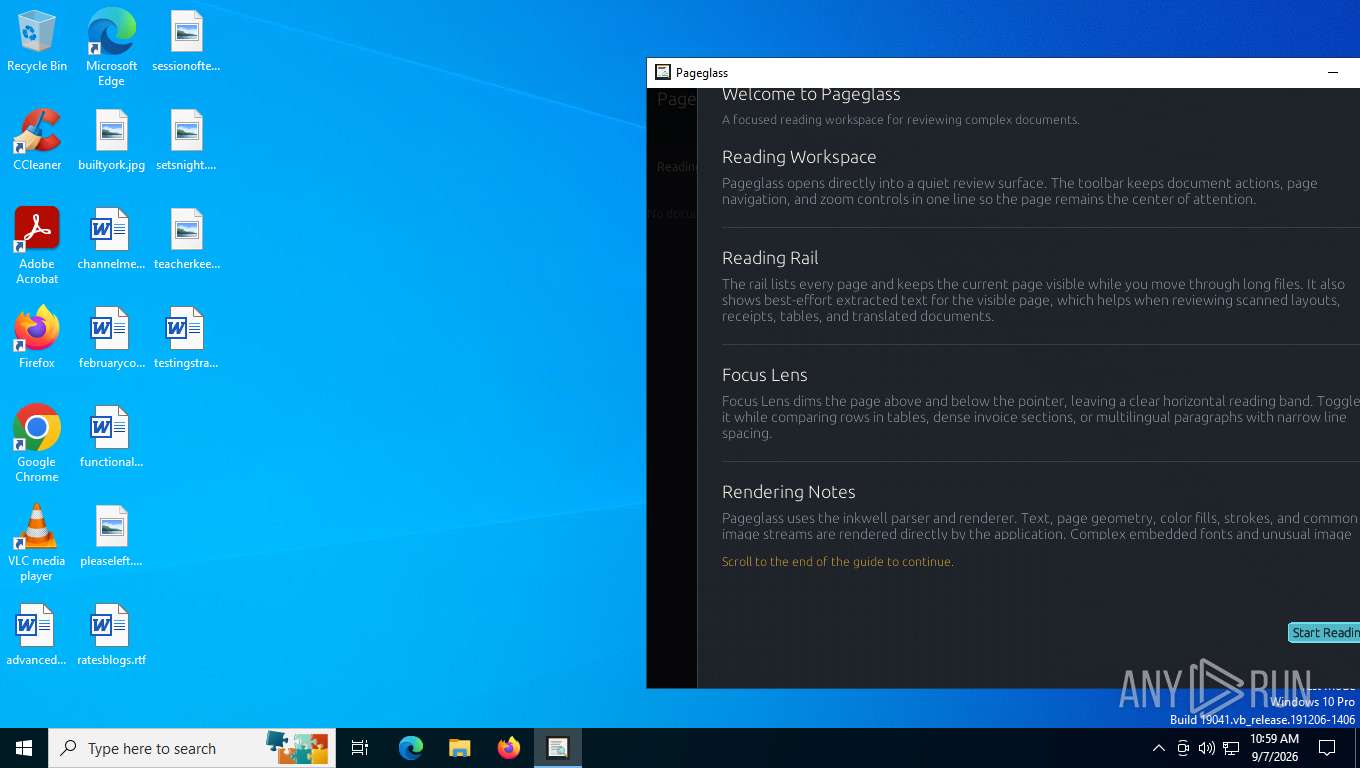
⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D

#cybersecurity #infosec

Media attachment
app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔄 208 ENTRY CHANGES 🔄

💻 macOS Golden Gate 27 - 34 added, 17 updated
https://support.apple.com/en-us/149035
📱 iOS and iPadOS 27 - 20 added, 10 updated
https://support.apple.com/en-us/149034
💻 macOS Tahoe 26.7 - 20 added, 8 updated
https://support.apple.com/en-us/149042
💻 macOS Sequoia 15.8 - 19 added, 9 updated
https://support.apple.com/en-us/149043
🥽 visionOS 27 - 14 added, 8 updated
https://support.apple.com/en-us/149038
⌚ watchOS 27 - 7 added, 9 updated
https://support.apple.com/en-us/149037
📺 tvOS 27 - 8 added, 5 updated
https://support.apple.com/en-us/149036
📱 iOS and iPadOS 26.7 - 9 added, 4 updated
https://support.apple.com/en-us/149041
🔨 Xcode 27 - 4 added
https://support.apple.com/en-us/149040
🌐 Safari 27 - 2 added, 1 updated
https://support.apple.com/en-us/149039

#apple #cybersecurity #infosec #security #ios

Apple SupportAbout the security content of macOS Golden Gate 27 - Apple SupportThis document describes the security content of macOS Golden Gate 27.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

US moves to staff leaders for industry-partnered offensive cyber program

The U.S. is recruiting private companies for offensive cyber operations against foreign criminals. While the August program shows promise, key details remain murky: payment structures, liability protections, and target identification are unresolved. Experts support the collaboration but stress need for clear guidelines on legal responsibility and international coordination to avoid unintended harm.

https://www.nextgov.com/cybersecurity/2026/10/us-moves-staff-leaders-industry-partnered-offensive-cyber-program/416613/

#InfoSec #CyberSecurity

Nextgov.comUS moves to staff leaders for industry-partnered offensive cyber programThe Trump administration is laying groundwork to enlist companies against foreign cybercriminals, but payment arrangements and protections for participating firms remain unresolved.
↩ Reply ♡ 0 · ↻ 0 ↗ Original