X XFediYour place in the Fediverse
XFEDI

#InfoSEC

ActivityPub

Public posts with this hashtag.

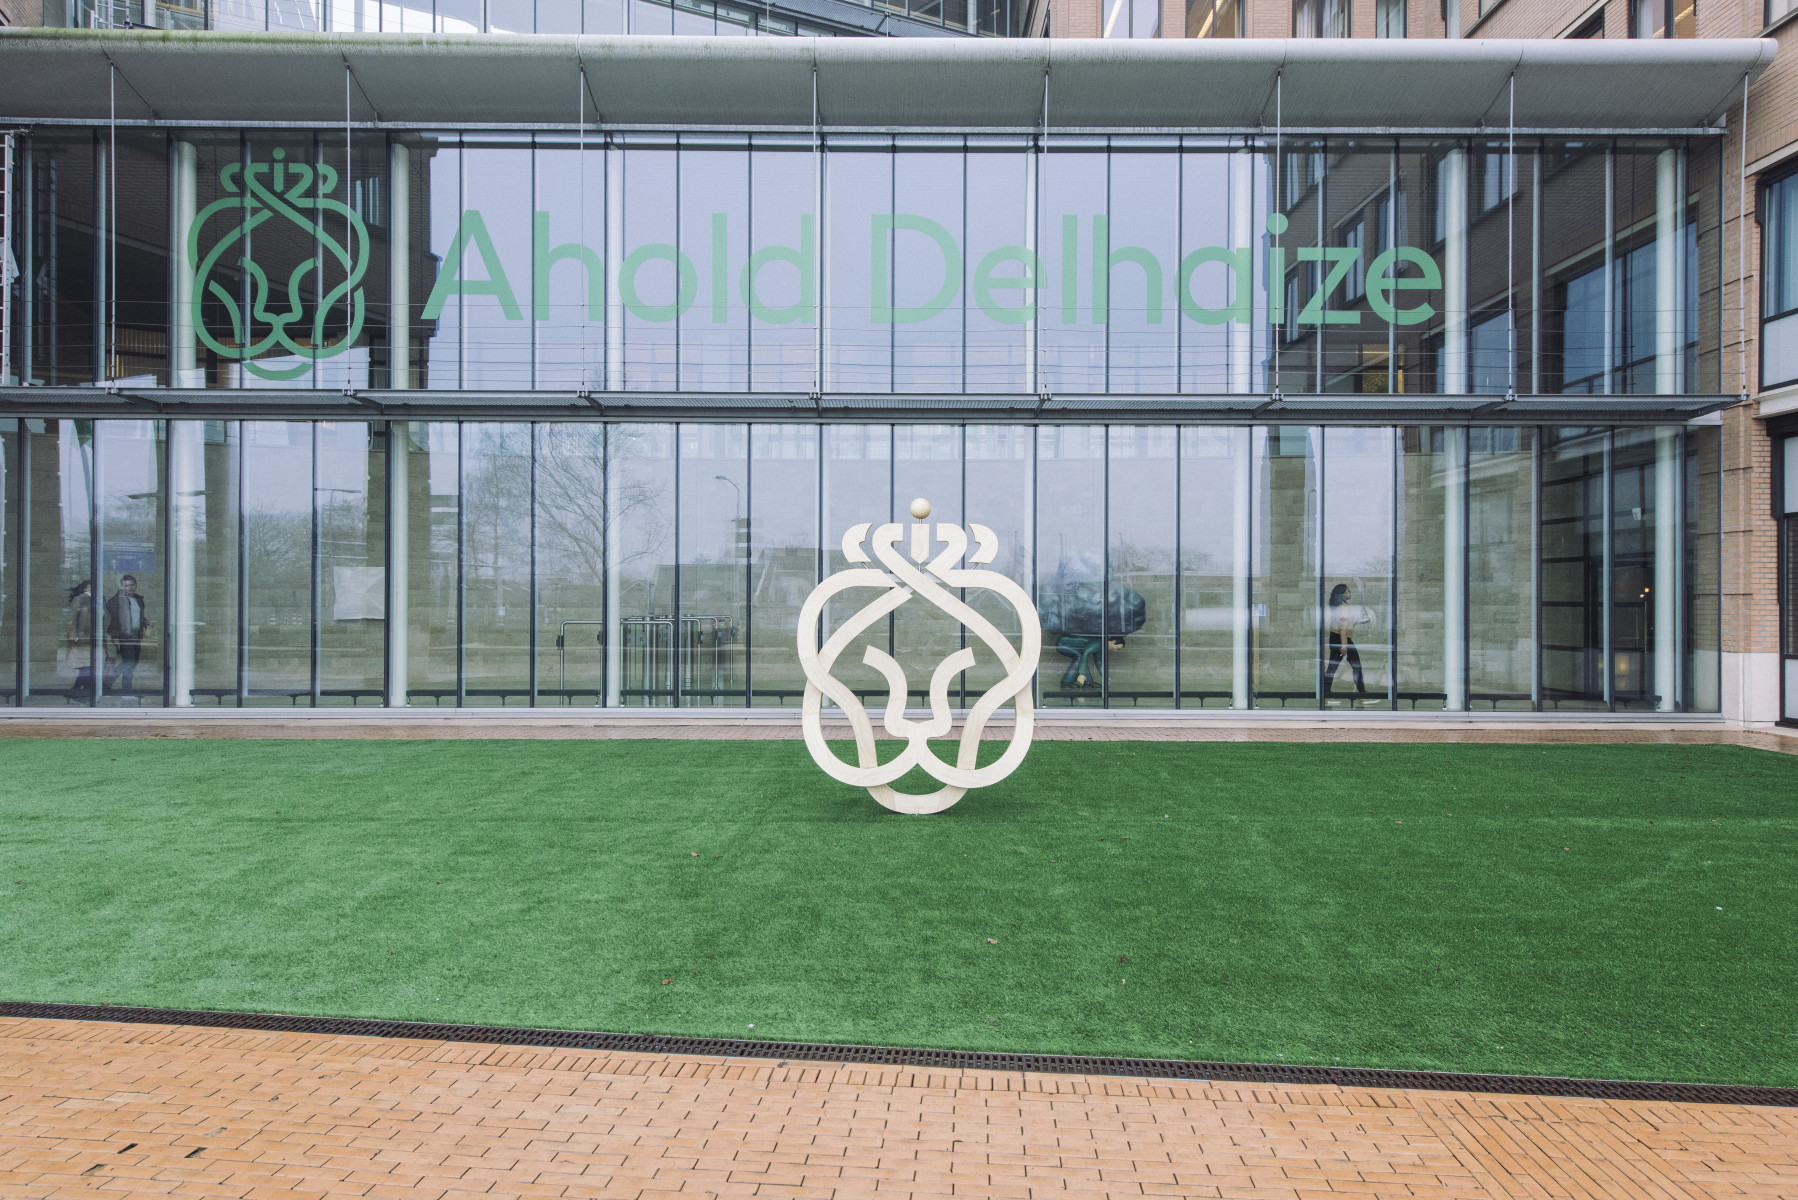
Ahold Delhaize confirmed on Monday that the outage hitting its websites and apps since 12 October was an attack. The Dutch group behind Albert Heijn, Delhaize, Food Lion and Stop & Shop took the systems offline itself, as a precaution, across most of its European and American brands. Stores stayed open throughout.

The group told the Dutch NCSC within 24 hours of detecting the activity and filed a police report yesterday. No customer data is believed taken, though the investigation continues. It is the second attack in two years; the 2024 incident exposed data on 2.2 million people.

https://newsroom.aholddelhaize.com/ahold-delhaize-update-on-status-of-cybersecurity-incident/

#CyberSecurity #InfoSec #Retail

Ahold Delhaize update on status of cybersecurity incidentAhold Delhaize update on status of cybersecurity incidentZaandam, October 19, 2026  – Ahold Delhaize today announced an update about the cybersecurity issue that was previously disclosed on Monday, October 12, 2026. The update outlines the actions taken since the incident was detected, the progress made in restoring services and the company’s continued cooperation with the relevant authorities....
↩ Reply ♡ 0 · ↻ 0 ↗ Original

F5 Issues Emergency Patches for Critical NGINX Code Execution Flaws

F5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.

**If you run NGINX in any form (open-source web server, NGINX Plus, Ingress Controller, Gateway Fabric, or the NGINX WAF/App Protect products), install F5's latest security patches ASAP. If you can't patch, turn off Server Side Includes and asynchronous file I/O, and have your team remove alias directives that use $request_filename and switch regex maps to named captures until the patch is in.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/f5-issues-emergency-patches-for-critical-nginx-code-execution-flaws-p-9-m-u-w/gD2P6Ple2L

BeyondMachinesF5 Issues Emergency Patches for Critical NGINX Code Execution FlawsF5 released emergency patches for three critical NGINX vulnerabilities (CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479) that allow unauthenticated remote code execution and denial-of-service attacks.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

This dumb password rule is from Tanishq.

Password must contain:
- 6 to 16 characters.
- At least one special character (@, #, $, %, * and & only).
- At least one alphabet.
- At least one number.

https://dumbpasswordrules.com/sites/tanishq/

#password #passwords #infosec #cybersecurity #dumbpasswordrules

dumbpasswordrules.comTanishq - Dumb Password RulesPassword must contain: - 6 to 16 characters. - At least one special character (@, #, $, %, * and & only). - At least one alphabet. - At least one number.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-75128: Langchain-Chatchat ≤0.3.1.3 has a CRITICAL flaw — POST /tools/call API lacks auth, letting attackers run OS commands as root 🐧. Restrict access & check for vendor updates. https://radar.offseq.com/threat/cve-2026-75128-missing-authentication-for-critical-function-in-chatchat-space-langchain-chatchat-55683d256ecad35b #OffSeq #vuln #CVE202675128 #infosec

Critical threat: CVE-2026-75128: Missing Authentication for Critical Function in chatchat-space Langchain-Chatchat
OffSeq Threat RadarCVE-2026-75128: Missing Authentication for Critical… | Threat RadarLangchain-Chatchat versions up to 0.3.1.3 contain a critical vulnerability where the POST /tools/call API endpoint lacks authentication. This allows remote…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

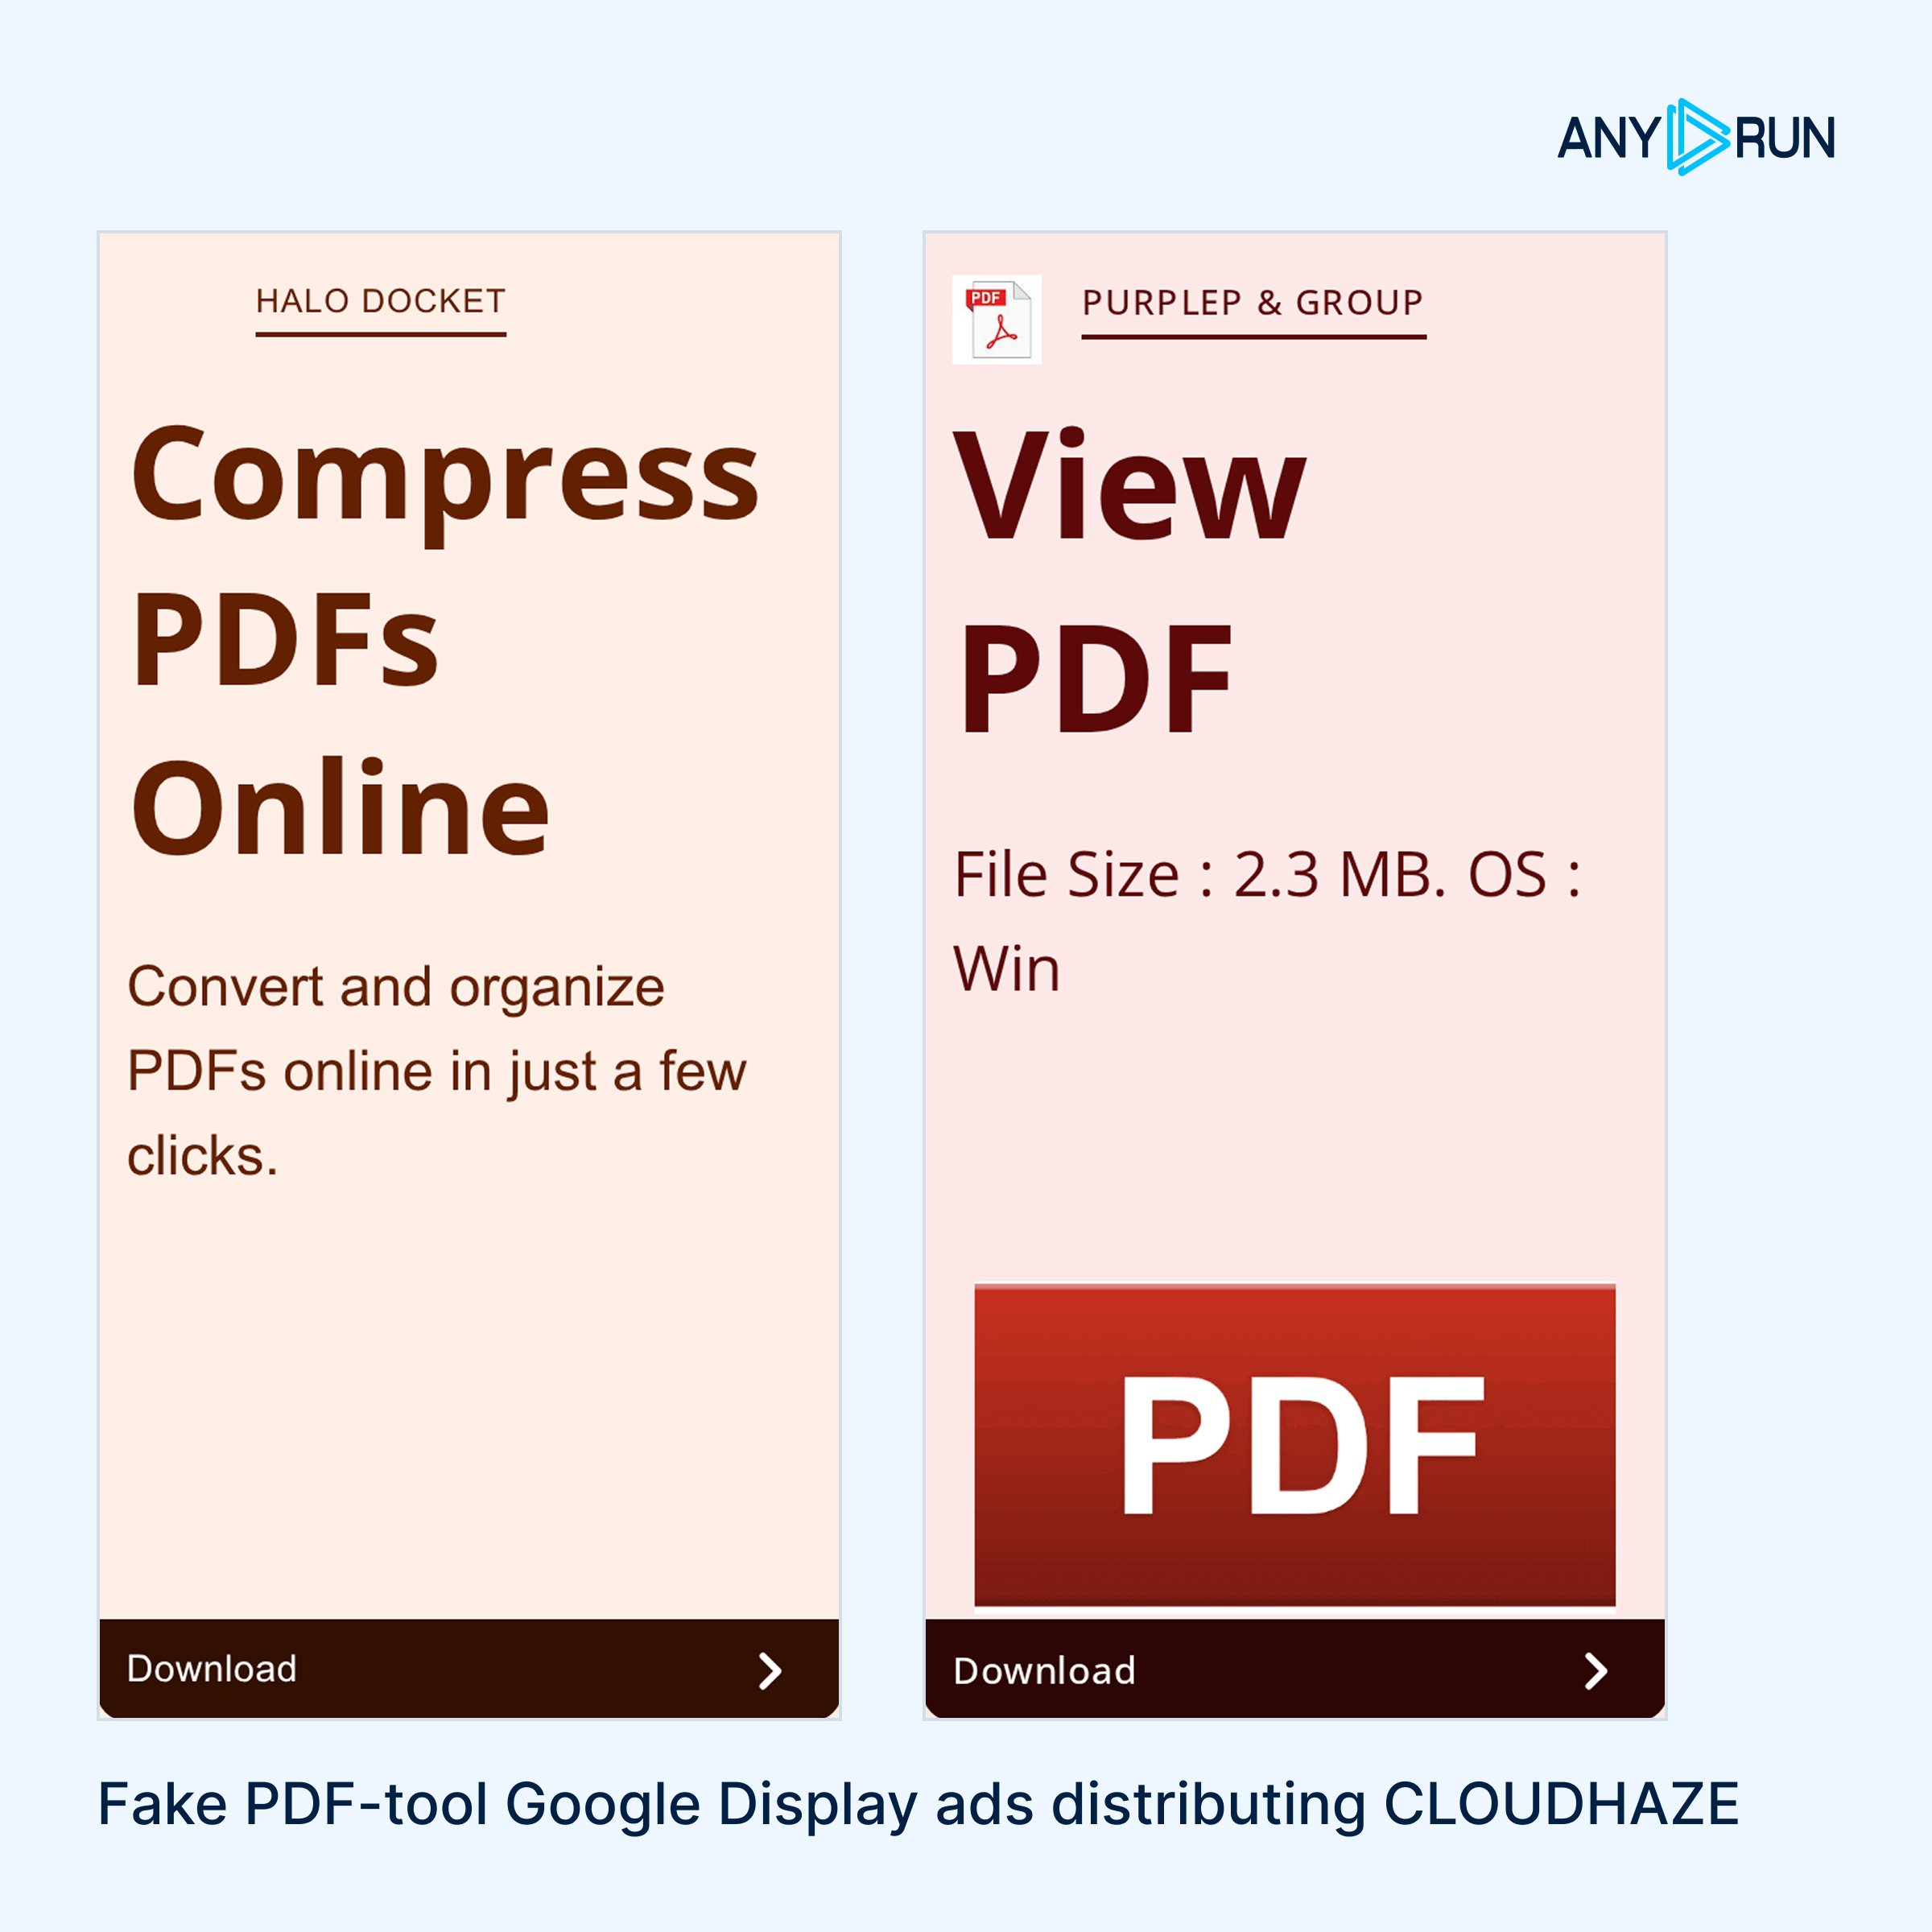
🚨 Detect it early: #CLOUDHAZE is a signed Rust implant distributed through fake PDF-tool Google Display ads, with high activity targeting US users.

586 ads from two verified advertisers on calendar and template sites led victims to download an implant that runs without admin rights.

❗️ Three signed samples had zero AV detections at the time of analysis. See the analysis & collect #IOCs: https://app.any.run/tasks/d033300c-1c20-4d03-9a32-b37da69bceea?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktoservice&utm_term=191026

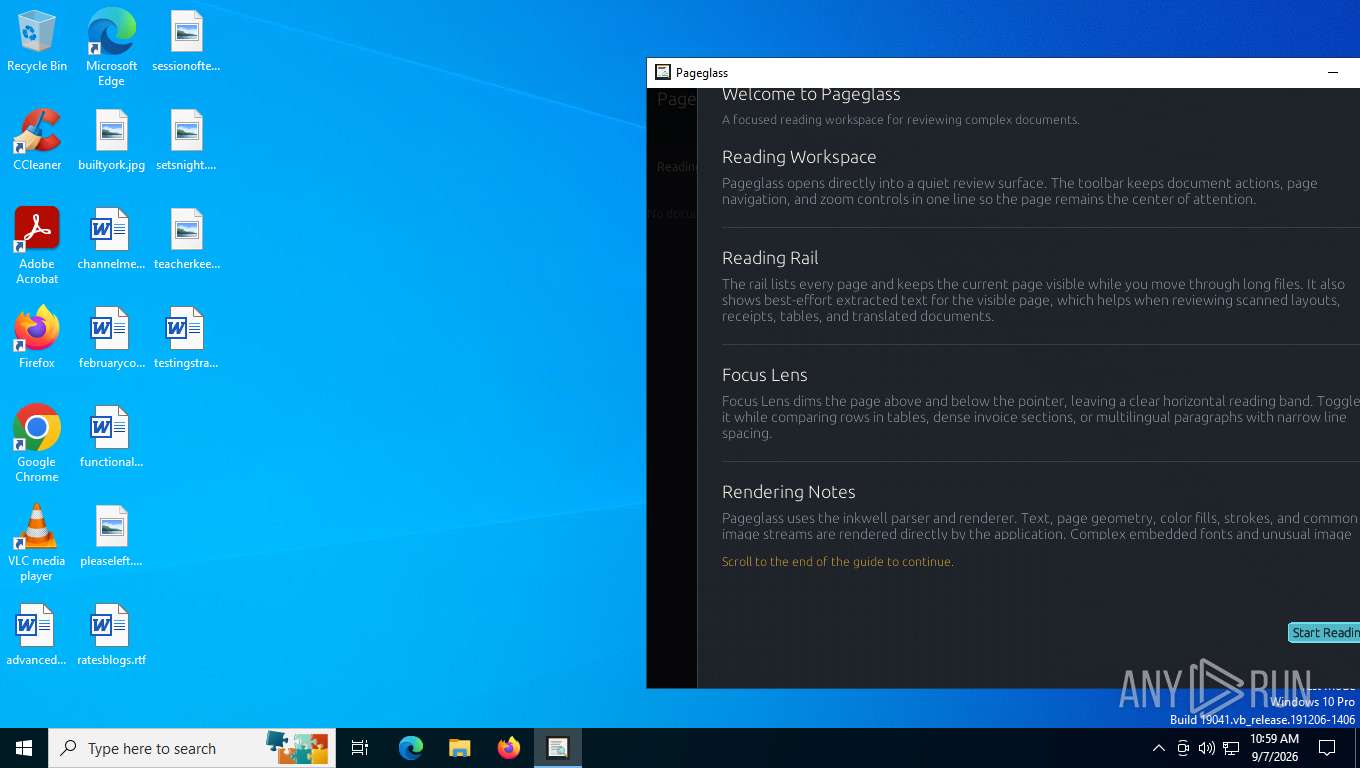
⚠️ CLOUDHAZE executes C2 commands and hijacks Chrome search. Since February, the operator has used brands including GalacticPDF, LuminaRead, Ironbark, QuartzLine, PageGlass, and PageStone across six C2 generations with new domains. Track activity and uncover related infrastructure in TI Lookup: https://intelligence.any.run/analysis/lookup?utm_source=mastodon&utm_medium=post&utm_campaign=cloudhaze&utm_content=linktotilookup&utm_term=191026#%7B%22query%22:%22url:%5C%22*/quarry/vein%5C%22%20OR%20url:%5C%22*/quarry/deposit%5C%22%20OR%20url:%5C%22*/quarry/geode%5C%22%20OR%20url:%5C%22*/quarry/talc%5C%22%20OR%20url:%5C%22*/mosaic/anchor%5C%22%20OR%20url:%5C%22*/mosaic/shoal%5C%22%20OR%20url:%5C%22*/mosaic/current%5C%22%20OR%20url:%5C%22*/mosaic/harbor%5C%22%20OR%20url:%5C%22*/grove/heartwood%5C%22%20OR%20url:%5C%22*/grove/phloem%5C%22%20OR%20url:%5C%22*/grove/barkline%5C%22%20OR%20url:%5C%22*/filament/radiance%5C%22%20OR%20url:%5C%22*/filament/prism%5C%22%20OR%20url:%5C%22*/filament/resonance%5C%22%20OR%20url:%5C%22*/pluto/zen%5C%22%20OR%20url:%5C%22*/pluto/oak%5C%22%20OR%20url:%5C%22*/piglet/trestle%5C%22%22,%22dateRange%22:30%7D

#cybersecurity #infosec

Media attachment
app.any.runAnalysis PageGlass_1.1611.08.exe (MD5: CF1FF043218279388666B76088E556D7) Malicious activity - Interactive analysis ANY.RUNInteractive malware hunting service. Live testing of most type of threats in any environments. No installation and no waiting necessary.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

🔄 208 ENTRY CHANGES 🔄

💻 macOS Golden Gate 27 - 34 added, 17 updated
https://support.apple.com/en-us/149035
📱 iOS and iPadOS 27 - 20 added, 10 updated
https://support.apple.com/en-us/149034
💻 macOS Tahoe 26.7 - 20 added, 8 updated
https://support.apple.com/en-us/149042
💻 macOS Sequoia 15.8 - 19 added, 9 updated
https://support.apple.com/en-us/149043
🥽 visionOS 27 - 14 added, 8 updated
https://support.apple.com/en-us/149038
⌚ watchOS 27 - 7 added, 9 updated
https://support.apple.com/en-us/149037
📺 tvOS 27 - 8 added, 5 updated
https://support.apple.com/en-us/149036
📱 iOS and iPadOS 26.7 - 9 added, 4 updated
https://support.apple.com/en-us/149041
🔨 Xcode 27 - 4 added
https://support.apple.com/en-us/149040
🌐 Safari 27 - 2 added, 1 updated
https://support.apple.com/en-us/149039

#apple #cybersecurity #infosec #security #ios

Apple SupportAbout the security content of macOS Golden Gate 27 - Apple SupportThis document describes the security content of macOS Golden Gate 27.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

US moves to staff leaders for industry-partnered offensive cyber program

The U.S. is recruiting private companies for offensive cyber operations against foreign criminals. While the August program shows promise, key details remain murky: payment structures, liability protections, and target identification are unresolved. Experts support the collaboration but stress need for clear guidelines on legal responsibility and international coordination to avoid unintended harm.

https://www.nextgov.com/cybersecurity/2026/10/us-moves-staff-leaders-industry-partnered-offensive-cyber-program/416613/

#InfoSec #CyberSecurity

Nextgov.comUS moves to staff leaders for industry-partnered offensive cyber programThe Trump administration is laying groundwork to enlist companies against foreign cybercriminals, but payment arrangements and protections for participating firms remain unresolved.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

One of your employees likely has a Plex media server shoved under a desk or hidden in a closet. They probably set it up so the office could share movies and music without paying for ten different streaming services.

https://theperimetersite.com/report/378

#vulnerability #phishing #infosec

The Perimeter SiteWho's Still Using a Single Password? — The Perimeter SiteOne of your employees likely has a Plex media server shoved under a desk or hidden in a closet.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

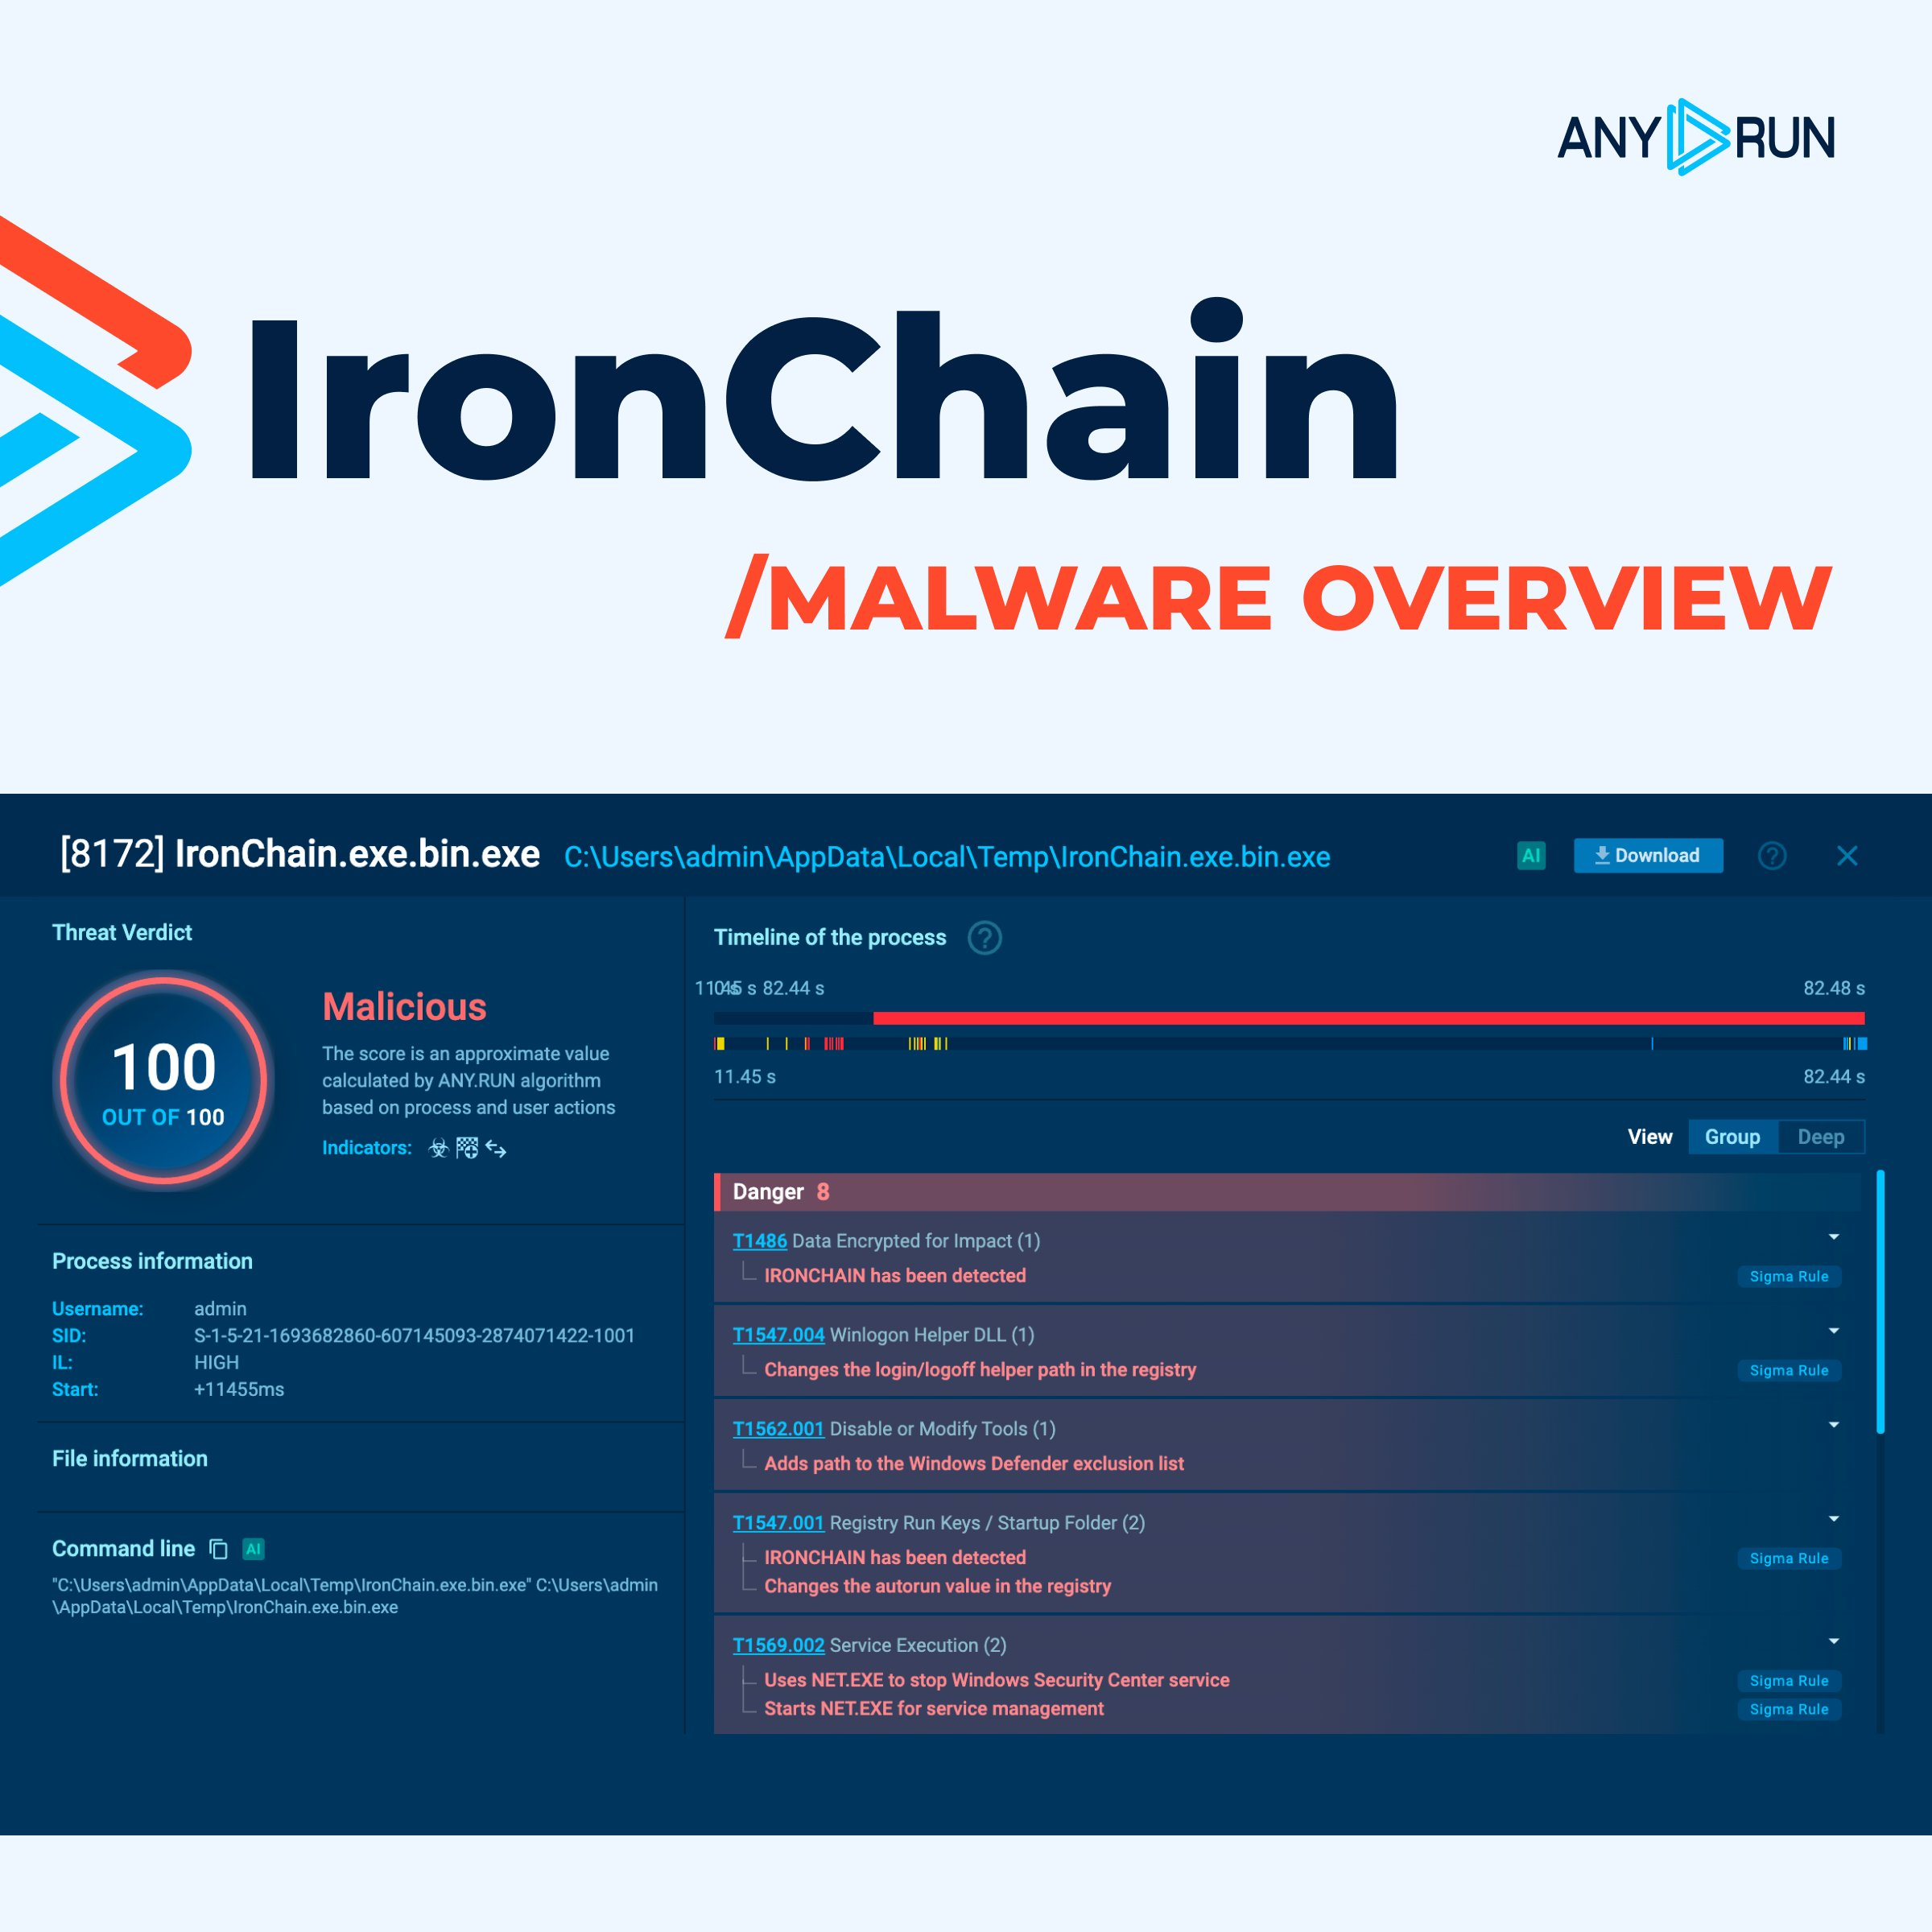
⚠️ #IronChain uses elevated privileges & kernel-level components to weaken security controls before encrypting files. It can disrupt Windows systems and leave organizations facing data loss and extended downtime.

👨‍💻 How to detect it before damage occurs: https://any.run/malware-trends/ironchain/?utm_source=mastodon&utm_medium=post&utm_campaign=ironchain_mtt&utm_term=191026&utm_content=linktomtt

#cybersecurity #infosec

Media attachment
IronChain | Malware Trends TrackerIronChain | Malware Trends TrackerLearn how IronChain uses privileged execution, kernel drivers, and file encryption to compromise Windows systems and cause destructive damage.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

📬 NicFab Newsletter #43 | October 20, 2026

Privacy, Data Protection, AI & Cybersecurity — weekly review.

👉 Read the full issue: https://www.nicfab.eu/en/newsletter-issues/2026-10-20-issue-43/?utm_source=mastodon&utm_medium=organic-social&utm_campaign=issue-43

📩 Subscribe: https://www.nicfab.eu/en/pages/newsletter/#subscribe-now

#Privacy #GDPR #DataProtection #AI #AIAct #Cybersecurity #InfoSec

NicFab Blog — Privacy, GDPR & Artificial IntelligenceNewsletter #43 - 20 October 2026NicFab Newsletter #43 — 20 October 2026. Weekly review on privacy, data protection, AI regulation, cybersecurity and digital rights.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Spyware Arrived Through an Ad Auction. The AdFection Case Shows How Much Ads Reveal About You

Researchers at Citizen Lab at the University of Toronto published a report on October 15, 2026, according to which spyware from the Israeli company Candiru…

https://vsx.global/adfection-spyware-ads/

#infosec #privacy #opensource #digitalsovereignty

VSX.is | Digital Privacy and SovereigntySpyware Arrived Through an Ad Auction. The AdFection Case Shows How Much Ads Reveal About You - VSX.is | Digital Privacy and SovereigntyResearchers at Citizen Lab at the University of Toronto published a report on October 15, 2026, according to which spyware from the Israeli company Candiru…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-113380 | CRITICAL: Signal RingRTC <2.72.0 has a flaw in FSM queue handling — remote peers can block call teardown, causing DoS for call sessions. Patch to 2.72.0+ now. https://radar.offseq.com/threat/cve-2026-113380-cwe-754-improper-check-for-unusual-or-exceptional-conditions-in-signal-ringrtc-7b225fb333cf31fe #OffSeq #CVE2026113380 #Signal #InfoSec

Critical threat: CVE-2026-113380: CWE-754 Improper Check for Unusual or Exceptional Conditions in Signal RingRTC
OffSeq Threat RadarCVE-2026-113380: CWE-754 Improper Check for Unusual or… | Threat RadarCVE-2026-113380 is a critical vulnerability in the RingRTC library used by Signal before version 2.72.0. It involves an improper check for unusual or…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CISA to AI labs: Share test-network IPs to flag rogue agents

CISA urges AI labs to share IP addresses to track rogue agents threatening critical infrastructure. While transparency could boost cybersecurity, experts debate its practicality due to cloud complexity and AI's dynamic nature. Alternative solutions like detection signatures are suggested. Public sector orgs should proactively test AI systems and prioritize vulnerability patches.

https://www.techtarget.com/cybersecurity/news/366651845/CISA-to-AI-labs-Share-test-network-IPs-to-flag-rogue-agents

#InfoSec #CyberSecurity

CybersecurityCISA to AI labs: Share test-network IPs to flag rogue agents | TechTargetCISA urges AI labs to share IPs and ASNs so defenders can recognize and flag rogue agents early. Research analysts, however, had mixed reactions. Learn why.
↩ Reply ♡ 0 · ↻ 0 ↗ Original
C

🤖 Forescout's Vedere Labs documents ROMULUS, a ClickFix delivery platform run like a malware-as-a-service: bogus landing pages trick visitors into pasting and running PowerShell, dropping LegionLoader and other families, with payloads rotated per campaign.

🔗 https://thehackernews.com/2026/10/romulus-clickfix-platform-tricks-users.html
#Malware #ClickFix #InfoSec

The Hacker NewsHackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other MalwareROMULUS uses ClickFix lures and PowerShell scripts to deliver malware, including Legion Loader, across infrastructure spanning six IP addresses.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Bank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and ...

Bank of America deployed 4,000 personnel (3,000 employees + 1,000 contractors) to fix software vulnerabilities detected by AI like Anthropic's Mythos. CEO Moynihan confirmed hundreds of millions in Q3 cybersecurity spending. Once skeptical of AI security tools, major firms now embrace them after serious breaches. BofA leads in transparency, expecting future cost reductions in patching efforts.
https://the-decoder.com/bank-of-america-puts-4000-people-on-fixing-vulnerabilities-uncovered-by-anthropics-mythos-and-other-ai-models/

#InfoSec #CyberSecurity

The DecoderBank of America puts 4,000 people on fixing vulnerabilities uncovered by Anthropic's Mythos and other AI modelsBank of America has hired 1,000 outside contractors to fix software vulnerabilities uncovered by AI models like Anthropic's Mythos, CNBC reports.
↩ Reply ♡ 0 · ↻ 0 ↗ Original

CVE-2026-77932 | eosphoros-ai DB-GPT ≤0.8.2 has a CRITICAL RCE flaw via /api/v1/chat/react-agent. Unauthenticated attackers can gain root on the container & DB. Restrict endpoint now; patch status pending. https://radar.offseq.com/threat/cve-2026-77932-missing-authentication-for-critical-function-in-eosphoros-ai-db-gpt-cadf6cb00dbfb5cd #OffSeq #CVE #RCE #Infosec
Critical threat: CVE-2026-77932: Missing Authentication for Critical Function in eosphoros-ai DB-GPT
OffSeq Threat RadarCVE-2026-77932: Missing Authentication for Critical… | Threat RadarDB-GPT versions up to 0.8.2 have a critical vulnerability allowing unauthenticated remote code execution via the /api/v1/chat/react-agent endpoint. This…
↩ Reply ♡ 0 · ↻ 0 ↗ Original

Enterprise controls can't keep up with AI agents

🚨 Companies are deploying AI agents faster than they can control them. Organizations struggle to track what these agents access, do, or if they can stop them. Traditional security systems aren't built for autonomous AI. The result? Potential security gaps and leaders considering quiet incident handling. The shift ahead: focus on managing existing agents responsibly, not just rolling out more.

https://www.techtarget.com/ai/news/366652493/Enterprise-controls-cant-keep-up-with-AI-agents

#InfoSec #CyberSecurity #AIGovernance

AI & Emerging TechEnterprise controls can't keep up with AI agents | TechTargetCompanies are giving agents more authority, but many are still struggling to track what they can access, what they're doing and how to stop them.
↩ Reply ♡ 0 · ↻ 0 ↗ Original