I'm on the height spectrum
XFEDI
ActivityPubFederated
HELLO, FEDIVERSE
Good conversations travel.
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.
Bird Flu Is Raging on a Mink Farm. It Could Spark a Human Pandemic, Experts Say, but Officials Won’t Act. — ProPublica
https://www.propublica.org/article/bird-flu-mink-farm-utah-human-risk
 ProPublicaBird Flu Is Raging on a Mink Farm. It Could Spark a Human Pandemic, Experts Say, but Officials Won’t Act.Federal officials brushed off the issue as Utah prioritized the fur industry’s interests. Little has been done to stop the spread of the virus and ensure it can’t spread to humans, a failure that experts called “irresponsible” and “astounding.”
Gentlemen, You Can't Fight Light A Fire In Here! This is The War Room Hitler's Eagle Nest!
里斯本 Baixa 的圣胡斯塔升降机(Elevador de Santa Justa)常被说成是埃菲尔的学生设计的。实际设计者是 Raoul Mesnier du Ponsard,生在波尔图,父母是法国人。然而,没有记录表明他做过埃菲尔的学生,或者和埃菲尔合作过。
在这之前,Mesnier 已经主持修建了 Braga 的 Bom Jesus

MongoDB is hiring Software Engineer 3
🔧 #golang #java #javascript #python #react #aws #azure #docker #gcp #kubernetes #mongodb
🌎 Gurugram, India
⏰ Full-time
🏢 MongoDB
Job details https://jobsfordevelopers.com/jobs/software-engineer-3-at-mongodb-com-sep-24-2026-df82b6?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
 jobsfordevelopers.comSoftware Engineer 3 at MongoDBMongoDB is hiring Software Engineer 3

How to Eat Out and Still Lose Fat (No Tracking, No Sad Salad) https://www.youtube.com/watch?v=4EZ2X-A9n1g 👉 Join us inside the Savage Sisters community on Skool:
https://ift.tt/kFEwmnu
You eat well all week. Then Saturday night dinner out hits and the whole plan quietly falls apart. That's not …
 www.skool.comSavage SistersHave fun getting addicted to what makes you fit, healthy, & badass... And learn to embrace life's uncomfortable moments instead of fighting them! 💪🏼

克服难关,交付吧。
🇰🇪#Kenya anunță al doilea deces provocat de Ebola.
Epidemia s-a extins în patru țări africane.
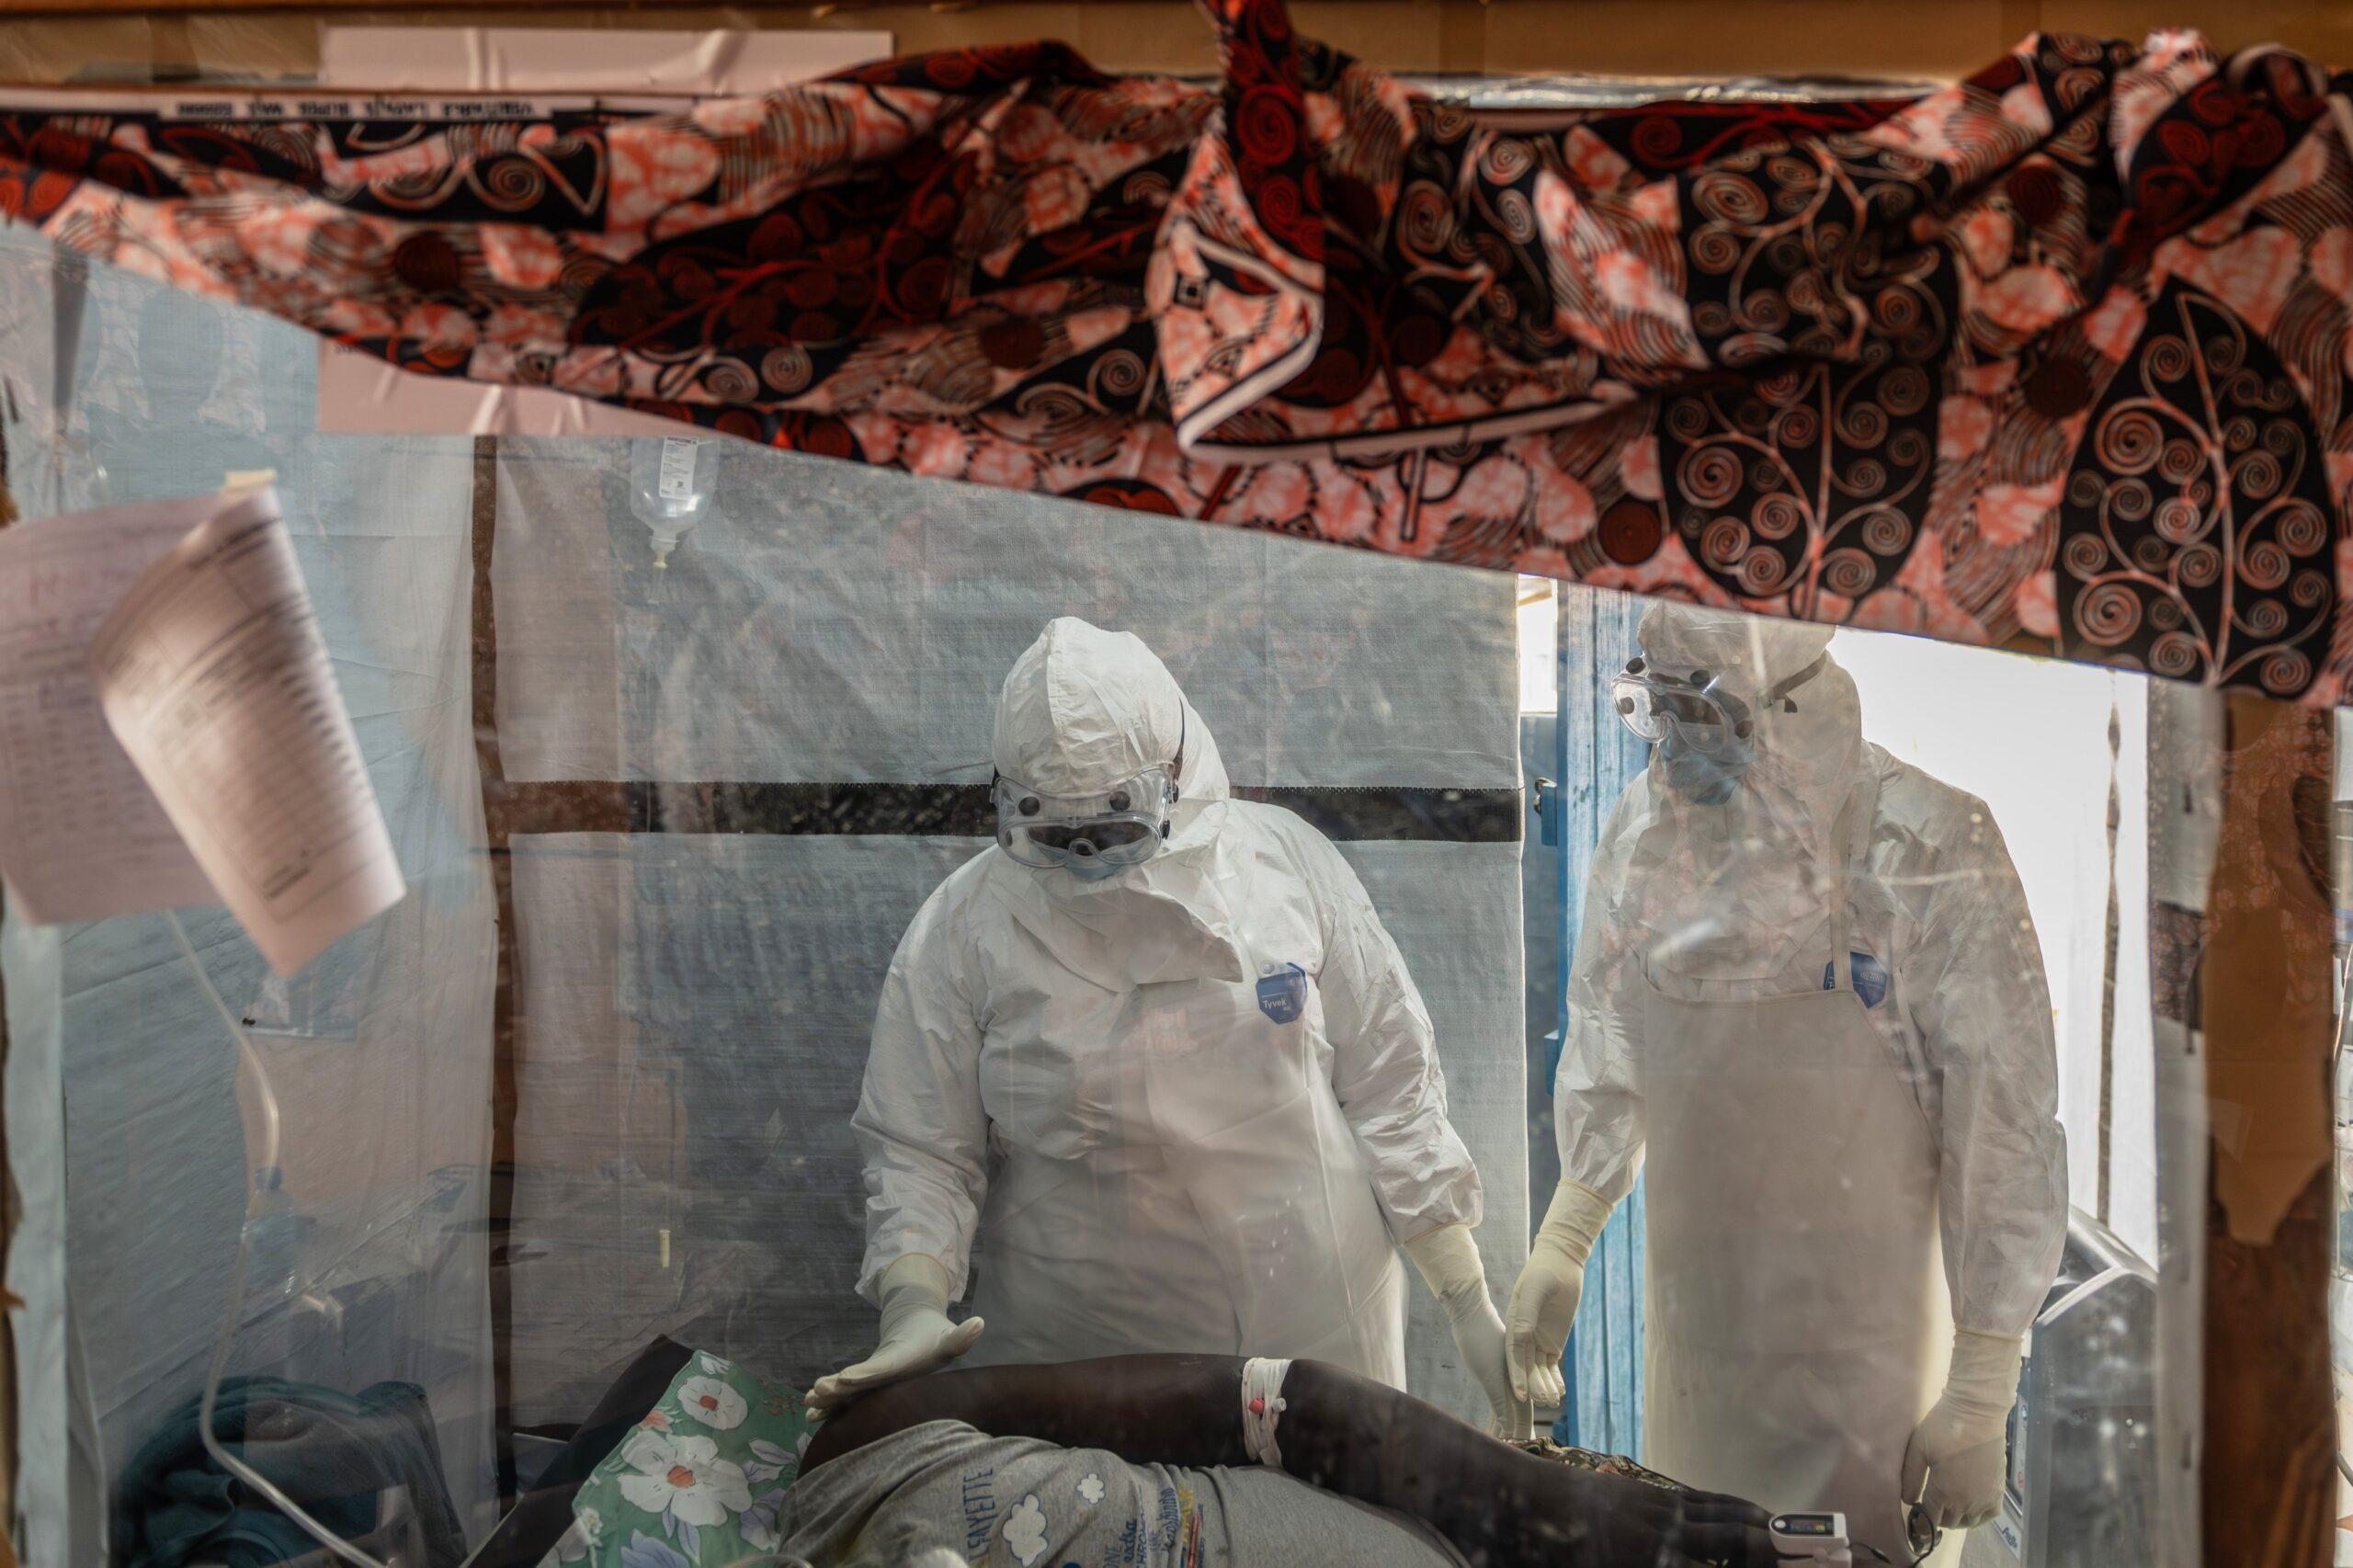
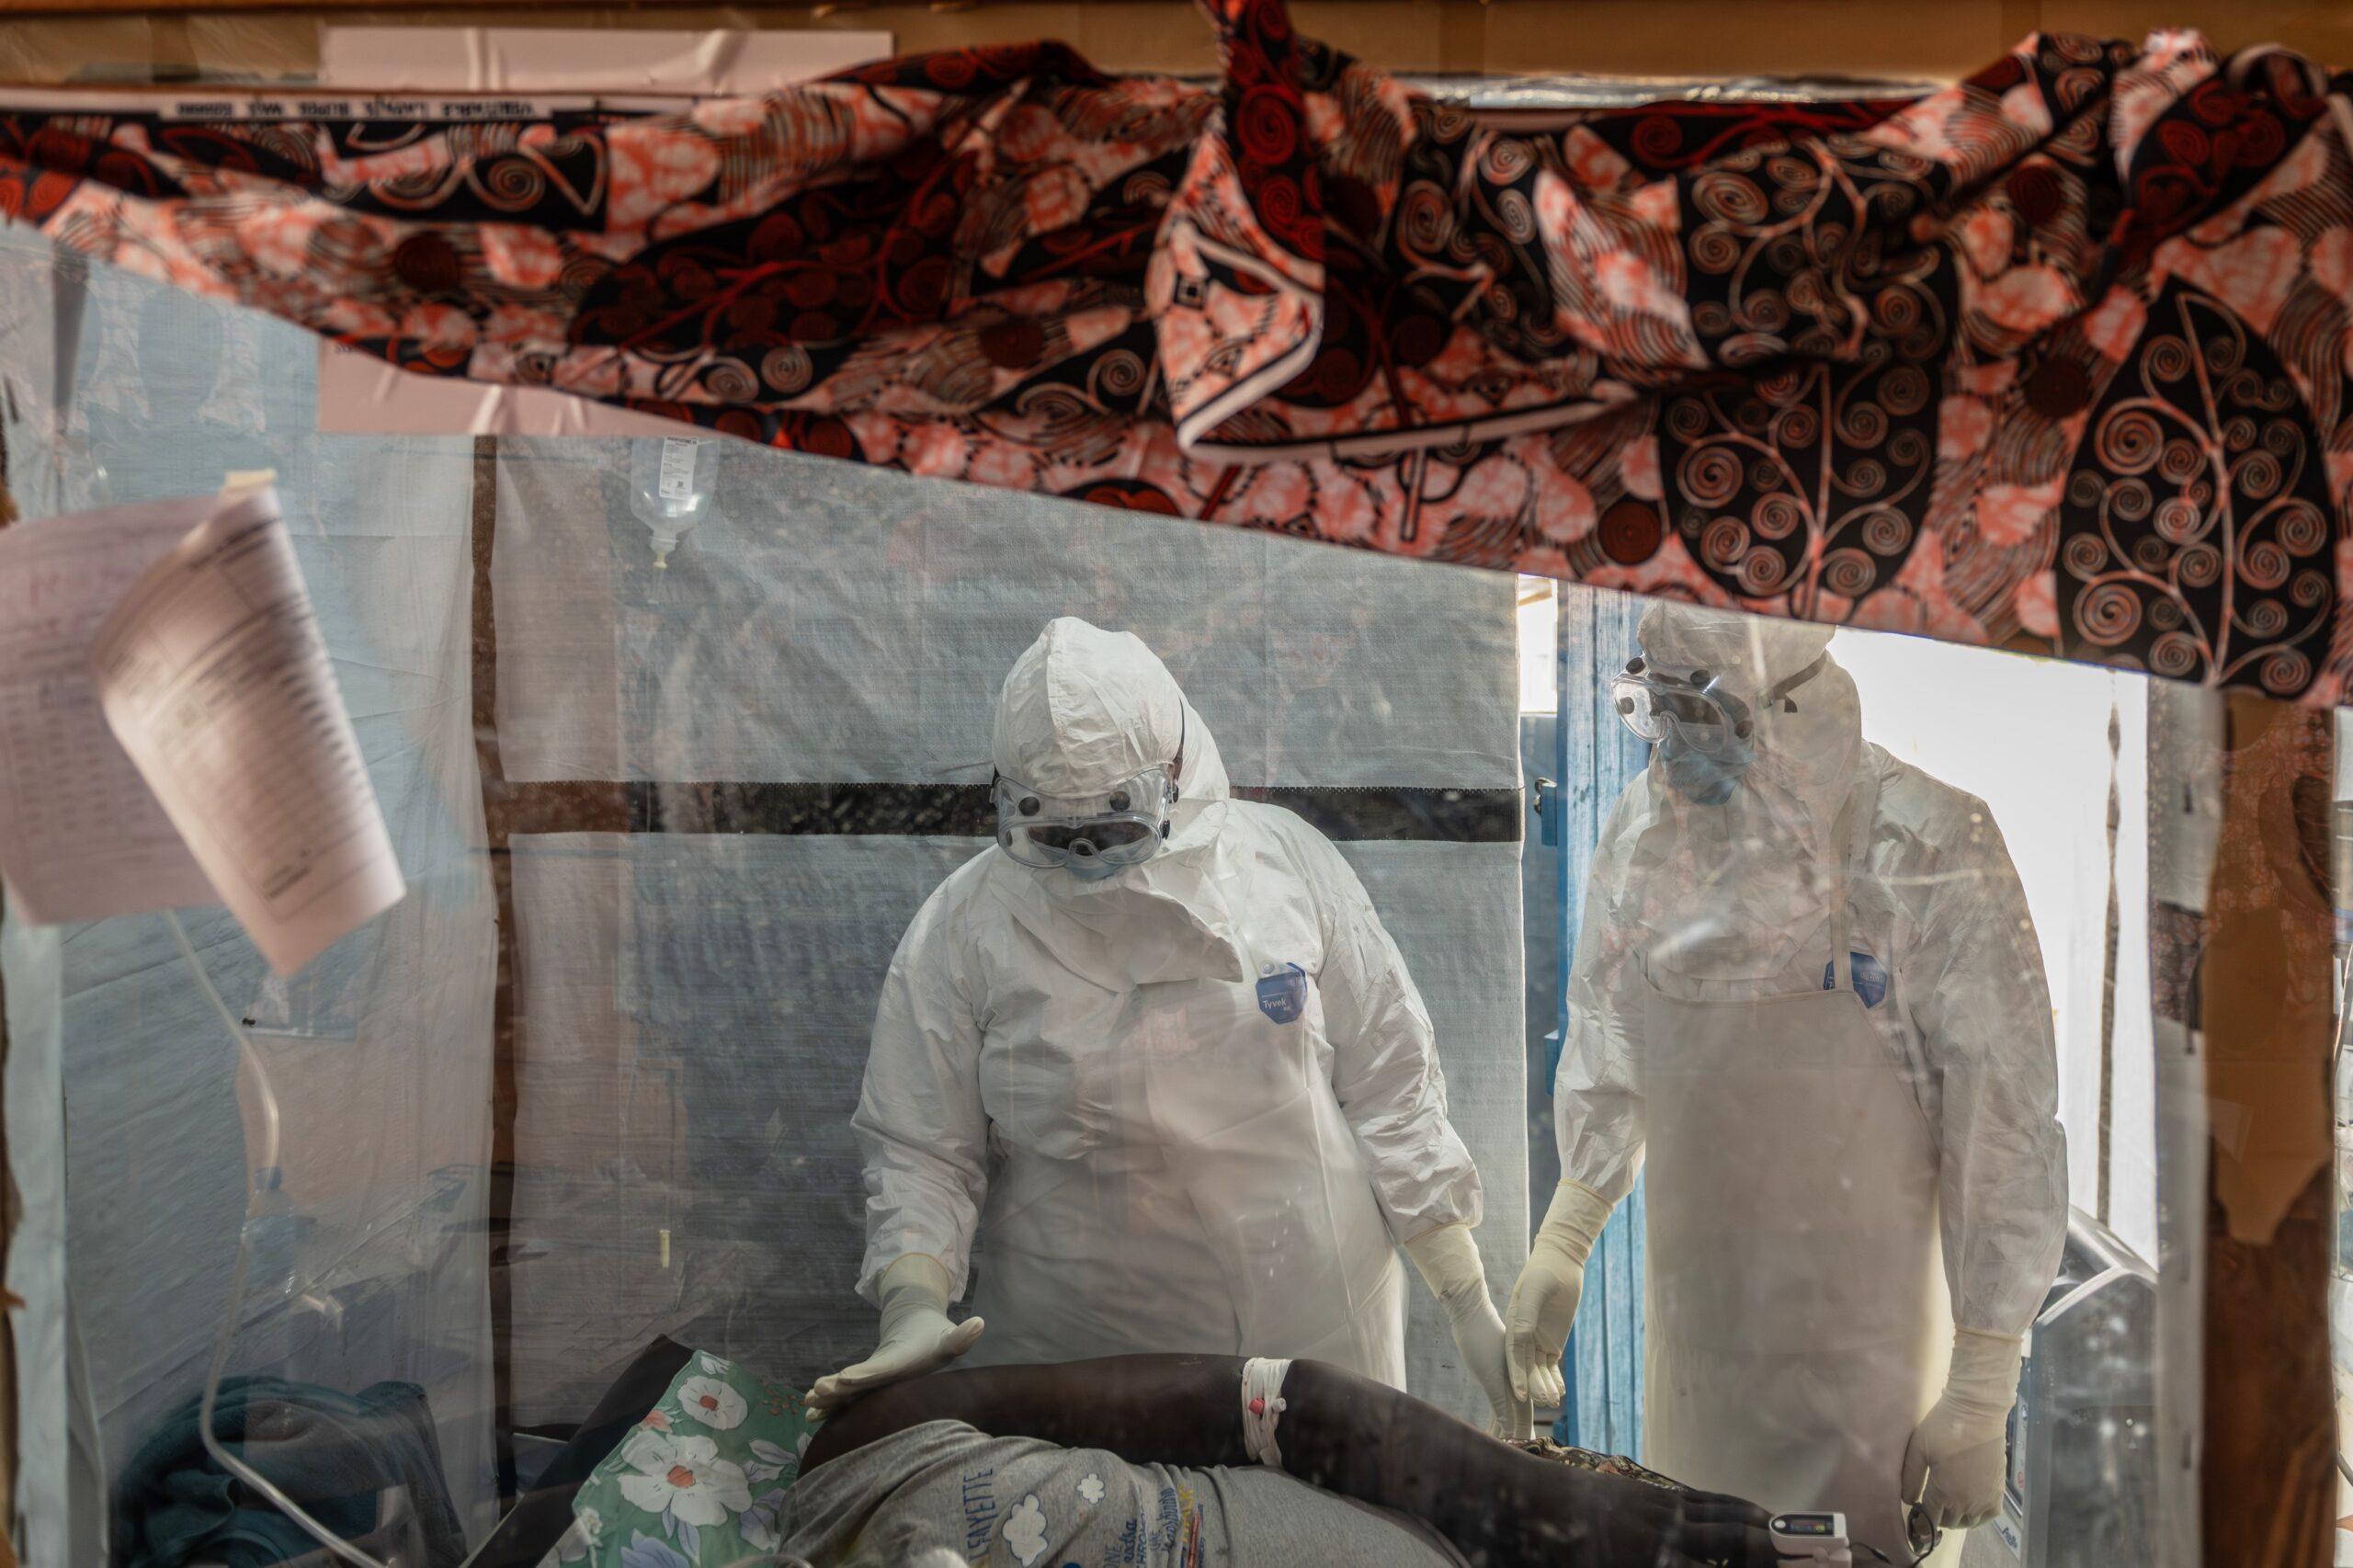 G4Media.roKenya anunță al doilea deces provocat de EbolaKenya a confirmat al doilea deces provocat de Ebola, după ce o femeie în vârstă de 65 de ani a murit în urma infectării cu virusul, a anunțat vineri seara

Der Planet braucht keine erfolgreichen Menschen mehr. Der Planet braucht dringend Friedensstifter, Heiler, Erneuerer, Geschichtenerzähler und Liebende aller Arten.

any other orbs out there?

And bonus features, like this ergonomic travel setting.
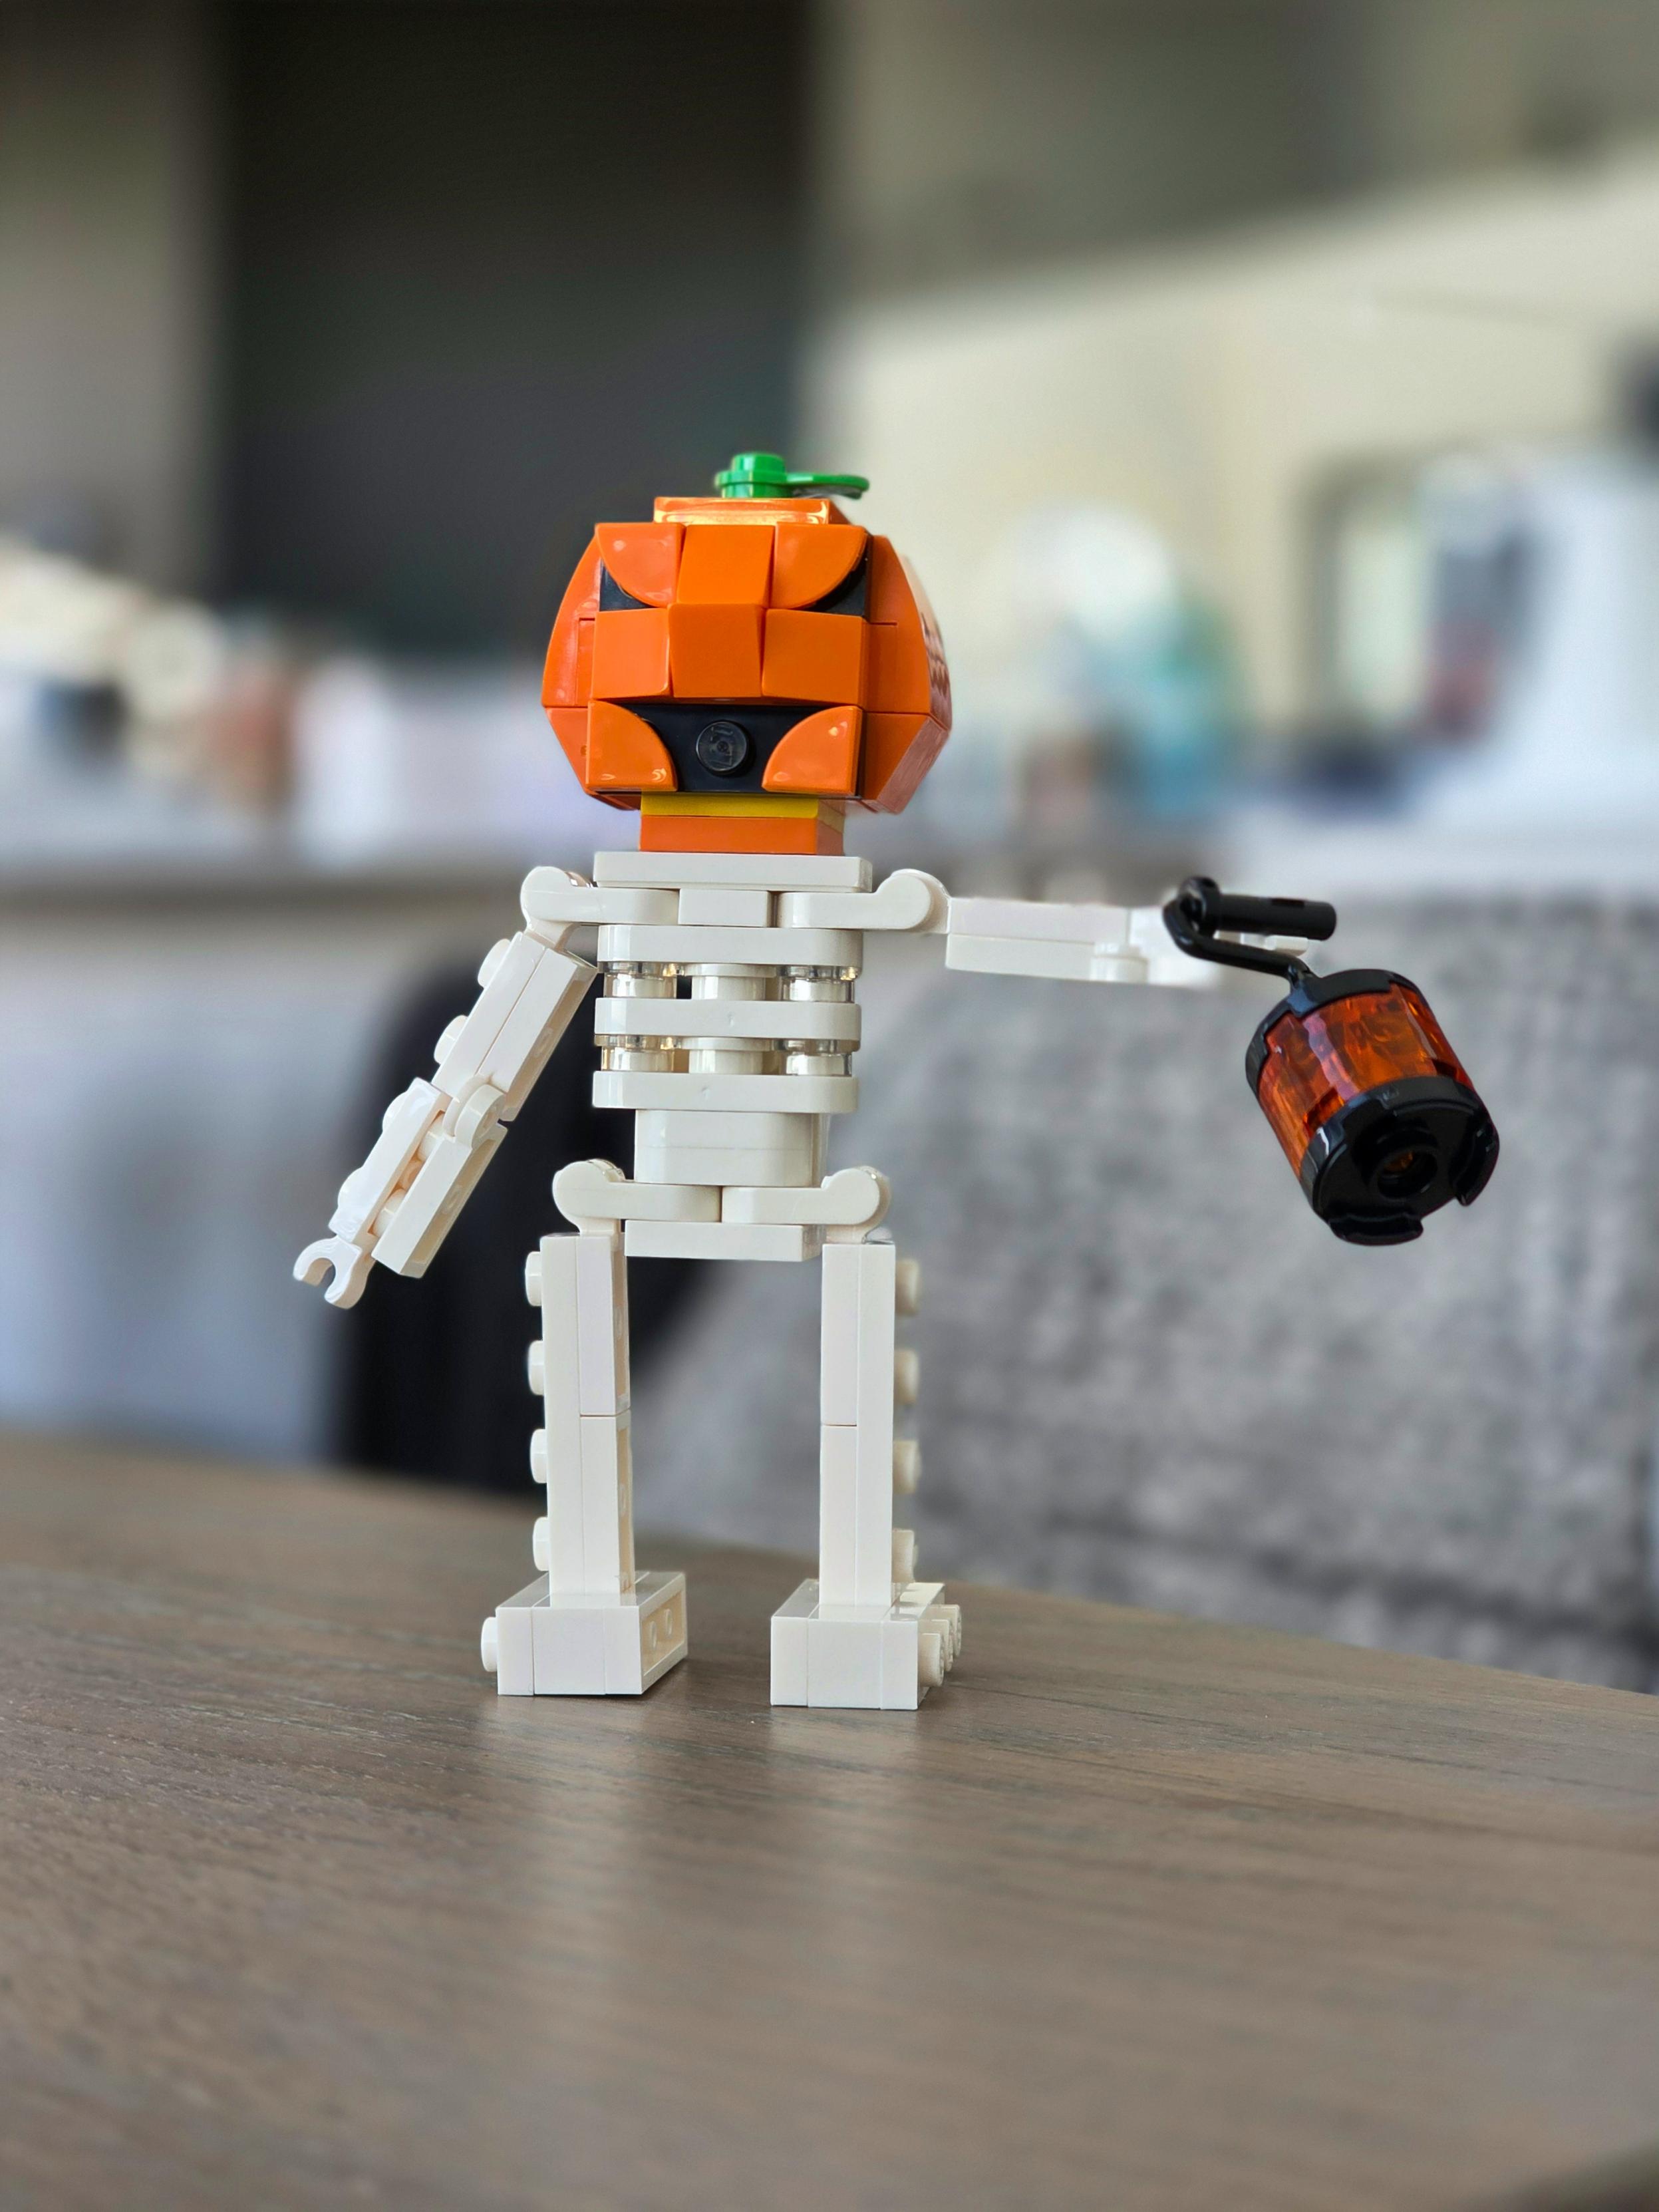
Did I get Lego PokeBall ? Maybe. But I got this one from the insiders program so I'm ready for the Halloween party.
↻ @[email protected] boosted

This Week in Plasma: Fixing All the Bugs, PiP, and Performance
blogs.kde.org/2026/10/24/this-week-in-plasma-fixing-all-the-bugs-pip-and-performance
Welcome to a new issue of This Week in Plasma. And it’s going to be a big one, folks! This week, a familiar pattern played out: people upgraded to Plasma 6.8 and found all the bugs that nobody reported during the beta period, and the Plasma team worked…

HPE Patches 72 Vulnerabilities in ArubaOS Including Eight CVSS 10.0 Flaws
HPE released security updates for ArubaOS to fix 72 vulnerabilities, including 33 critical flaws that allow unauthenticated remote code execution and authentication bypass on wireless infrastructure.
**If you use HPE Aruba devices running ArubaOS (AOS-8 or AOS-10), upgrade ASAP to a fixed version (AOS-10.8.1.2, 10.7.2.7, 10.4.1.14, 8.13.3.1 or 8.10.0.24). The patch has dozens of critical flaws let attackers take full control without a password. Make sure the web and CLI management interfaces are never reachable from the internet and can only be accessed from a dedicated, trusted management network.**
#cybersecurity #infosec #advisory #vulnerability
https://beyondmachines.net/event_details/hpe-patches-72-vulnerabilities-in-arubaos-including-eight-cvss-10-0-flaws-m-1-k-i-d/gD2P6Ple2L
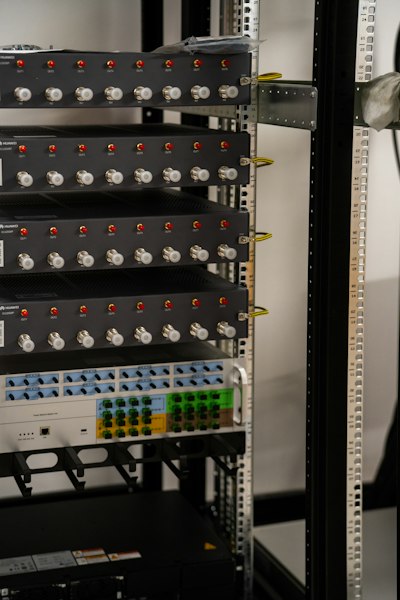 BeyondMachinesHPE Patches 72 Vulnerabilities in ArubaOS Including Eight CVSS 10.0 FlawsHPE released security updates for ArubaOS to fix 72 vulnerabilities, including 33 critical flaws that allow unauthenticated remote code execution and authentication bypass on wireless infrastructure.
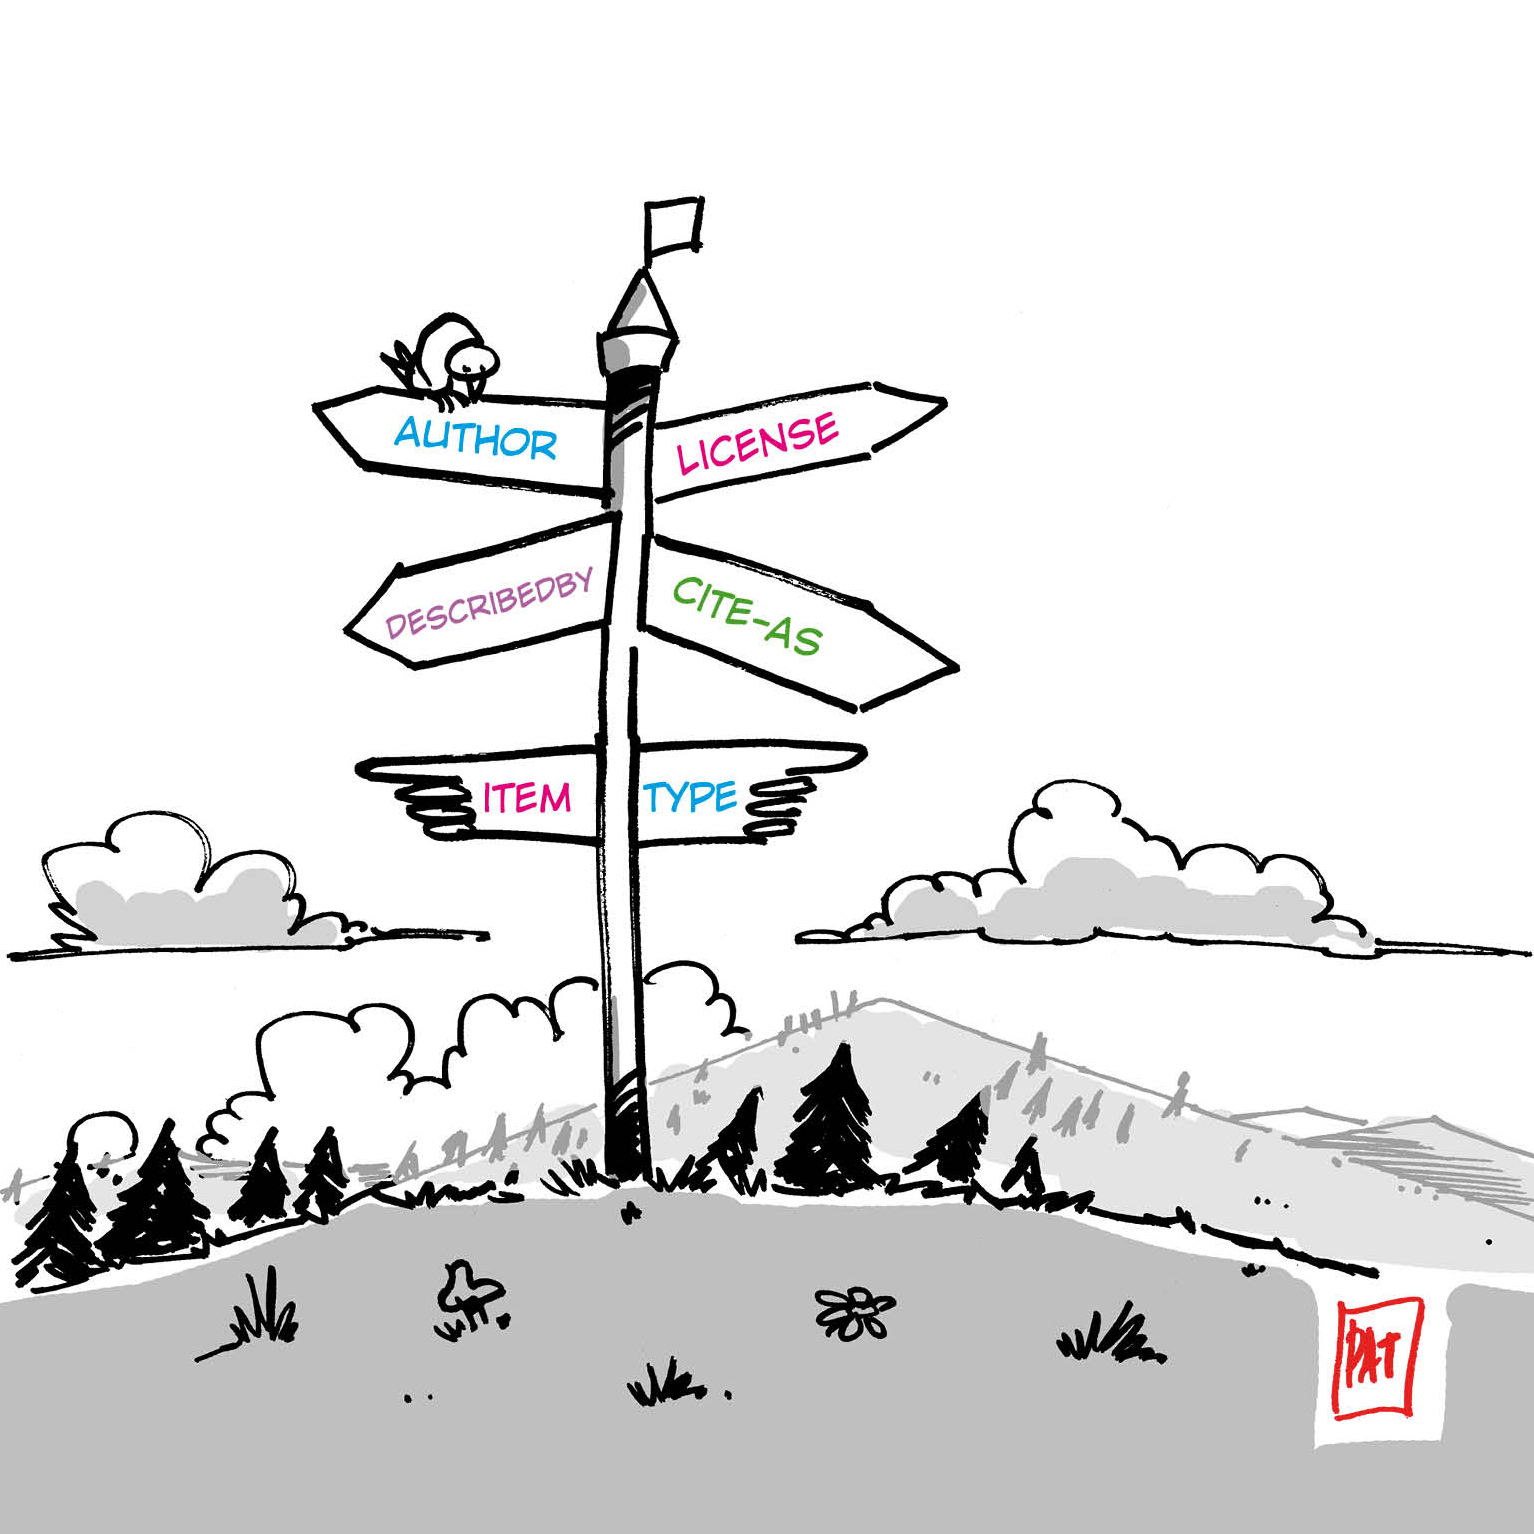
FAIR Signposting (2016-) is an HTTP-based simplistic interpretation of FAIR DOs focusing on features that are realistically implementable at scale, see https://signposting.org/FAIR/. For example, it relies on typed links to group DO components and relies on media types (https://www.iana.org/assignments/media-types) to associate operations with DO content; no special purpose registries. Adoption is steadily growing and major repository platforms have already implemented support, see https://signposting.org/adopters/.
3/3

360 Raw Viewer (0.1.91) http://apps.nextcloud.com/apps/files_360viewer

AI-Assisted Paper on Z-Library Cites a TorrentFreak Article That Doesn’t Exist https://torrentfreak.com/ai-assisted-paper-on-z-library-cites-a-torrentfreak-article-that-doesnt-exist/
A fresh academic paper on Z-Library cites a TorrentFreak article that doesn’t exist, and several other sources in the paper are also unfindable. The authors disclose that they used AI tools, which may explain what is going on. The use of AI in an academic paper on shadow libraries is also somewhat ironic, as rightsholders are suing AI companies for using these s


 torrentfreak.comAI-Assisted Paper on Z-Library Cites a TorrentFreak Article That Doesn’t Exist * TorrentFreakA fresh academic paper on Z-Library cites a TorrentFreak article that doesn’t exist, and several other sources in the paper are also unfindable. The authors disclose that they used AI tools, which may explain what is going on. The use of AI in an academic paper on shadow libraries is also somewhat ironic, as rightsholders are suing AI companies for using these sites to train AI models.
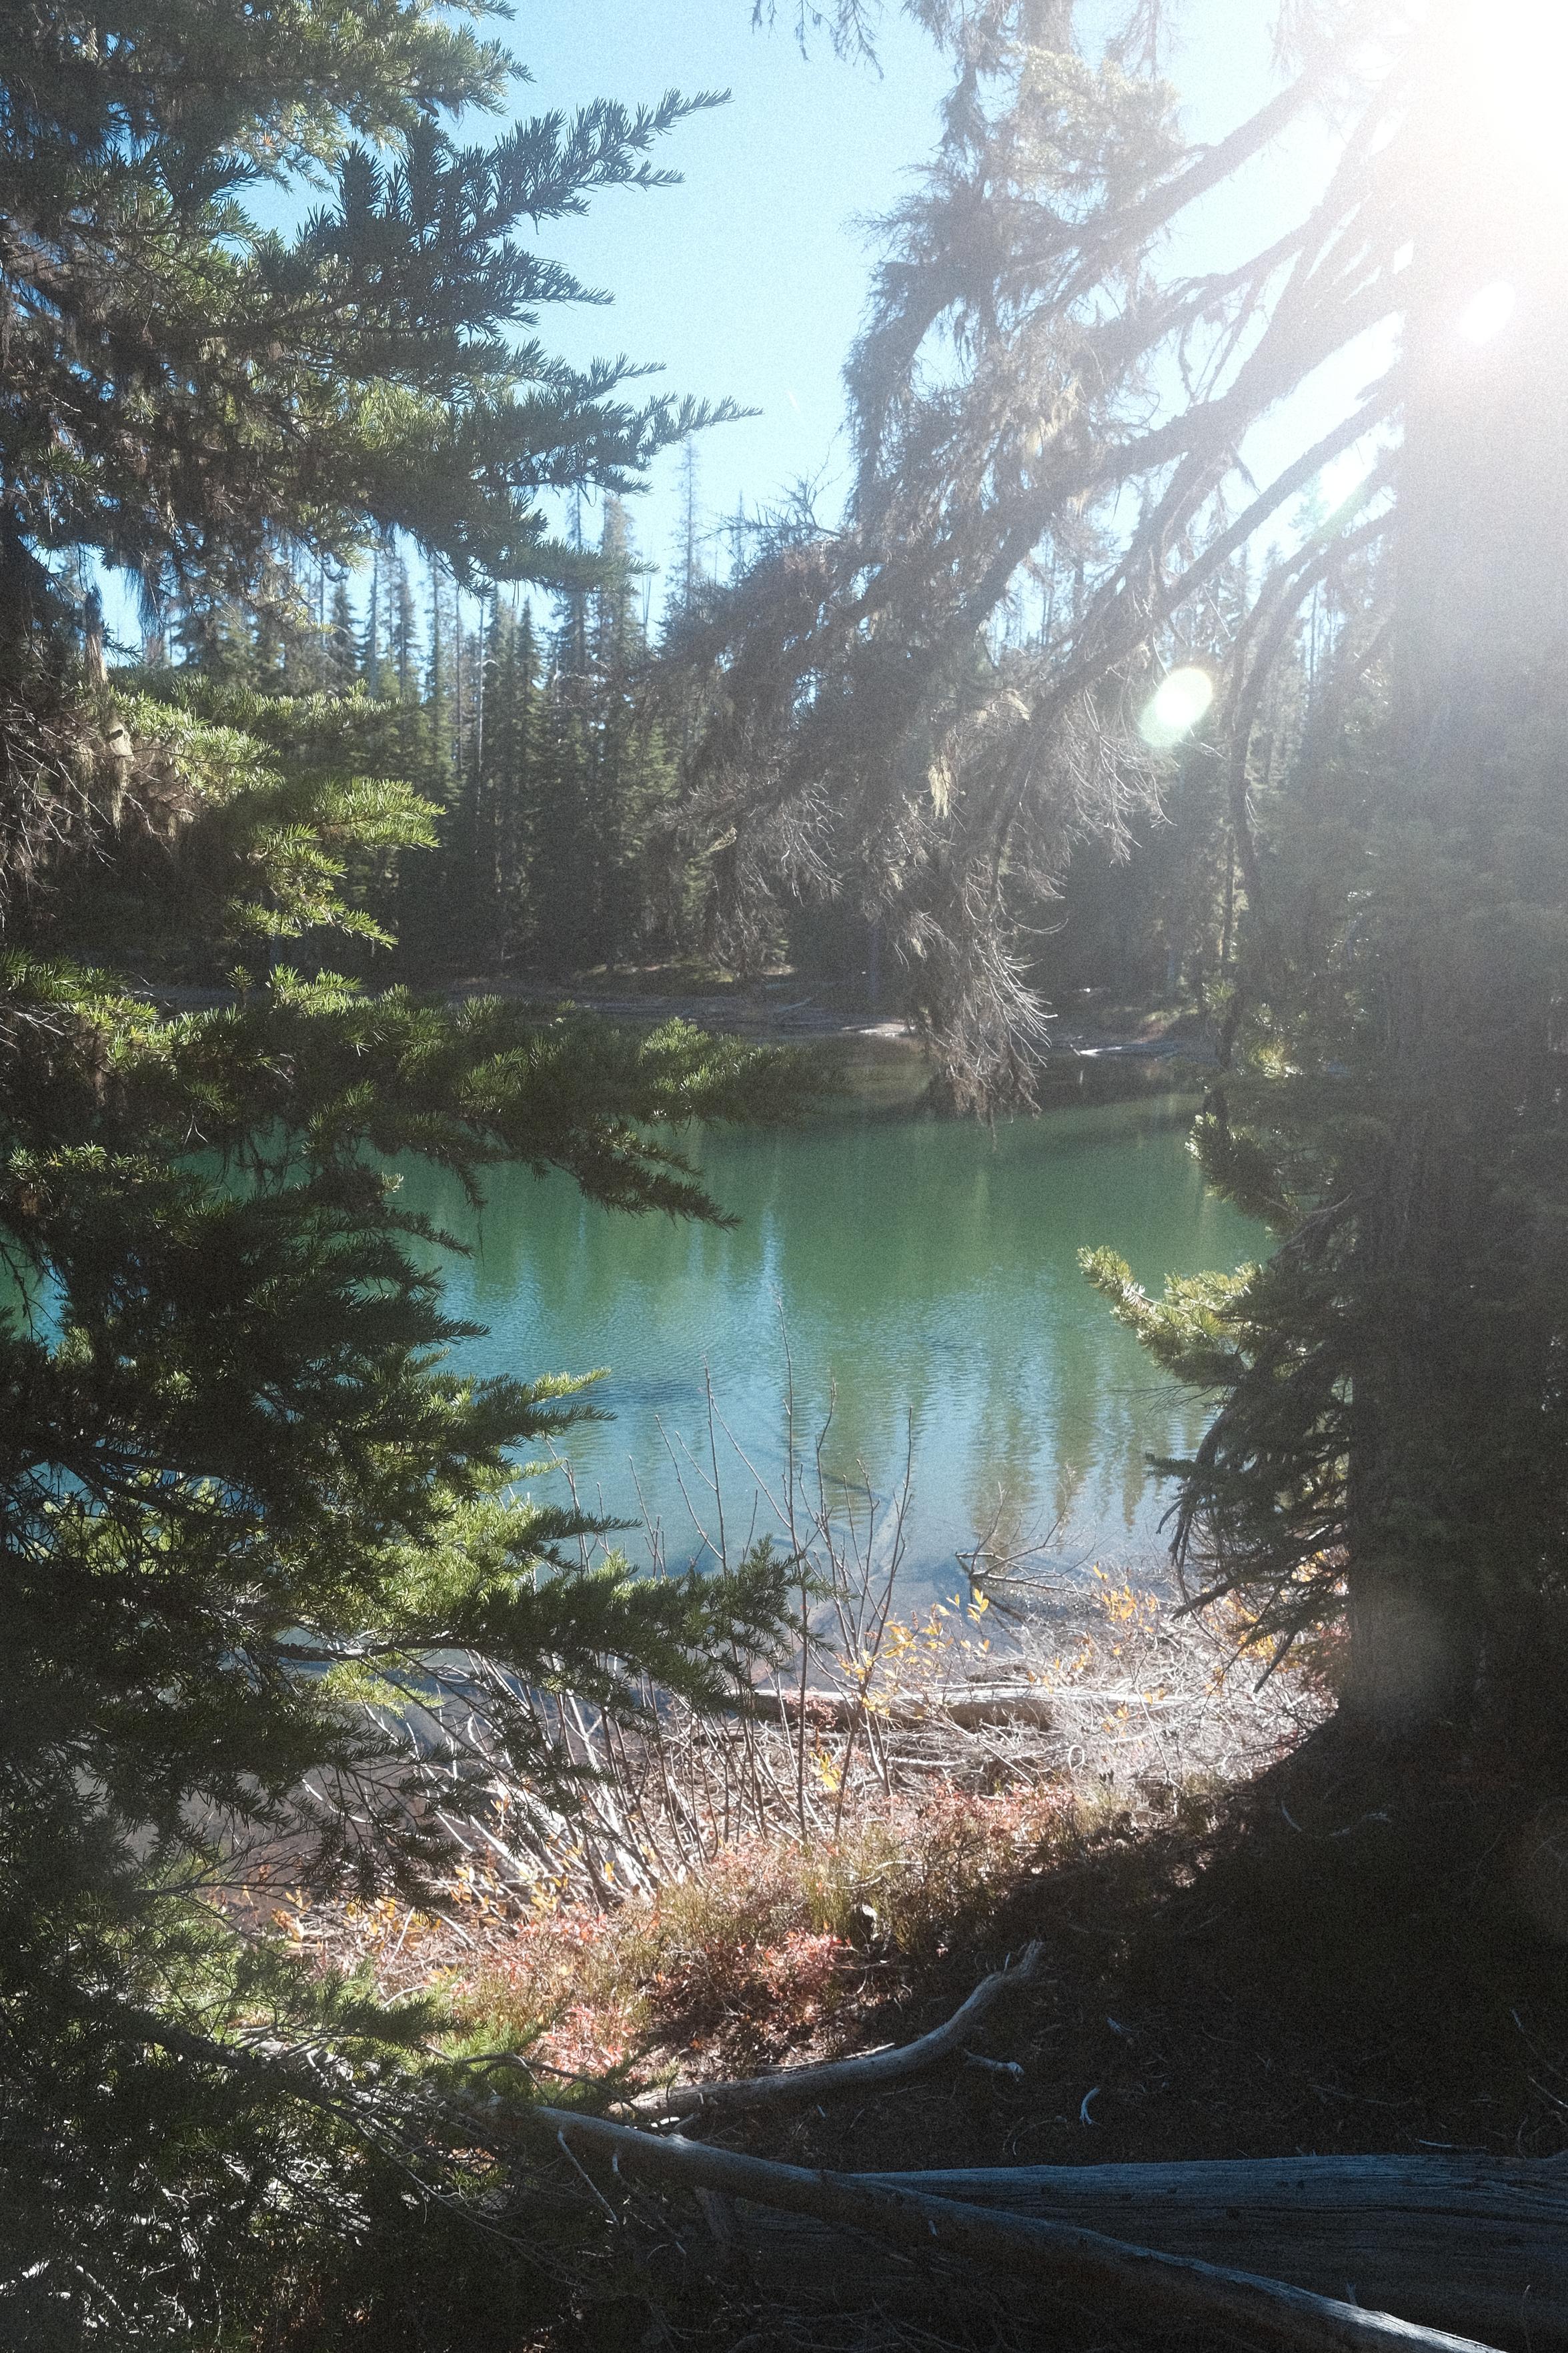
alpine lakes are so cool (literally)

¿Router 5G o fibra en tu segunda vivienda?
https://blog.elhacker.net/2026/10/router-5g-o-fibra-en-tu-segunda-vivienda.html
 Blog elhacker.NET¿Router 5G o fibra en tu segunda vivienda?Blog sobre informática, tecnología y seguridad con manuales, tutoriales y documentación sobre herramientas y programas

If a major vulnerability alert (which is a good thing in the long run) and some data breaches constitute “Black October” in cyberspace, what will the reaction be like if something very bad but entirely precedented like NotPetya, WannaCry or the ransomware crisis of 2021 actually happens?


Confira a letra da música “Sweet Life” de Frank Ocean
#FrankOcean #SweetLife
https://daletra.com.br/frank-ocean/letra/sweet-life.html

 DaLetraSweet Life - Frank OceanThe best song wasn't the single, but you weren't either. Livin' in Ladera Heights, the black Beverly Hills. Domesticated paradise, palm trees and pools.

Prometna nesreča 24. 10. 2026 08:14
Ob 8.14 sta na Kovaški cesti v Zrečah trčili osebni vozili. Gasilci PGD Zreče so zavarovali kraj dogodka, odklopili akumulatorja in nevtralizirali iztekle motorne tekočine. Poškodovanih ni bilo.
https://spin3.sos112.si/javno/zemljevid/473402

Possible Phishing 🎣
on: ⚠️hxxps[:]//mxg-e63fe1[.]webflow[.]io
🧬 Analysis at: https://urldna.io/scan/6adc35143b775000058a6021
#cybersecurity #phishing #infosec #urldna #scam #infosec
 urldna.iourlDNA - The DNA test for websitesUnleash website insights! urldna.io analyzes data, monitors brands and exposes security risks. Analyze URLs like a DNA test

ASN: AS10014
Location: Narashino, JP
Added: 2026-10-21T07:43
Sensitive media · Show


Irischer traditioneller Cheddar in Scheiben. 4 Jahre drüber. Erfüllt den Zweck.

[2172106] Please remove hdhomerun-config-gui from tenacious

Sensitive media · Show
