"Robotic Invasion" - Fu Manchu
XFEDI
ActivityPubFederated
HELLO, FEDIVERSE
Good conversations travel.
Public updates from xsukax and this corner of the network.
Sign In to your accountPublic posts known to this server, including selected instances.
My mind is like
an autumn moon
glowing purely
in a clear blue abyss.
Nothing compares to it.
What could I possibly say?
Cold Mountain (Hanshan)
📢 There is still time to request a ballot for the 2026 Midterms.
Request your ballot today at https://www.votefromabroad.org/. Ask for your ballot to be sent to you by email and send it back by email or fax if your state allows.
Need help? Voting questions? We can help. Go to https://www.votefromabroad.org/voter-support

I’ve been hoping that the stick Labour gets for approving Jackdaw – which already has a licence and can readily supply gas we’d import otherwise – will mean Rosebank doesn’t get the go-ahead.
— ‘Doug Parr, chief scientist at Greenpeace, said: “The Burnham government is facing a series of big decisions over the next few months that could define its legacy on climate. This administration seems to get the urgency of cutting the emissions causing deadly heatwaves and droughts, but there’s a real risk they could still sleepwalk into reversing the strong progress the UK has made so far.”
Last week, the government gave the go-ahead to drill the Jackdaw gasfield, despite warnings that it would create only 27 new jobs, fail to cut the cost of living, and add little to UK tax revenues. Now, the North Sea fossil fuel industry is pressing for a green light to the more controversial Rosebank oilfield, west of Shetland, which would produce higher emissions.’
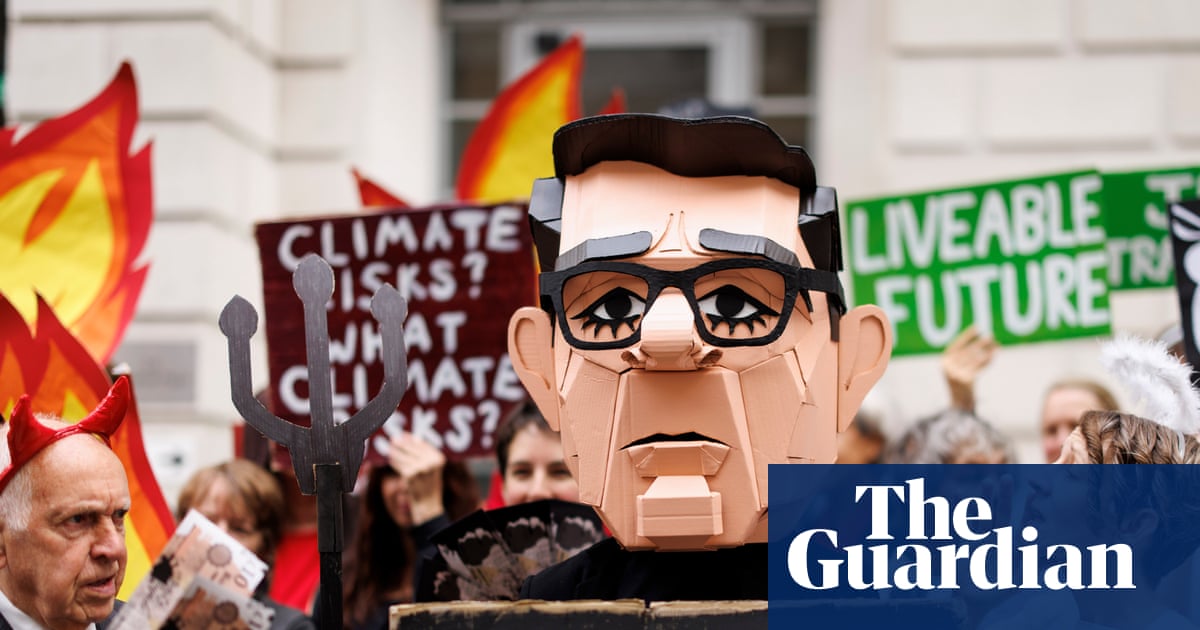 the GuardianBurnham in danger of sleepwalking into climate disaster, say campaignersLetter to PM argues series of wrong choices on North Sea oil, Heathrow, EVs and heat pumps will scupper net zero plans
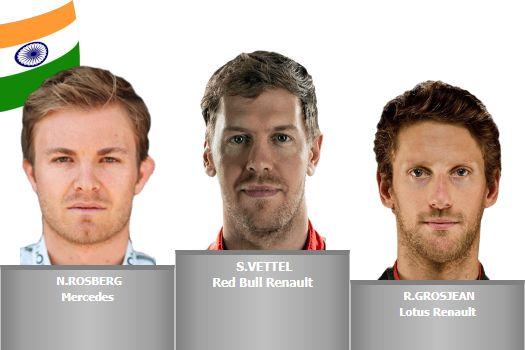
#EnUnDiaComoHoy El 27 de octubre de 2013, durante el Gran Premio de la India, Sebastian Vettel ganó la carrera y se coronó así Campeón del Mundo, uno de los momentos más destacados de la Fórmula 1 hasta esa fecha.
Donald Trump crossed a boundary — and it will cost the GOP everything https://www.alternet.org/alternet-exclusives/donald-trump-crossed-a-boundary-and-it-will-cost-the-gop-everything/ via Alternet.org
 Alternet.orgDonald Trump crossed a boundary — and it will cost the GOP everythingRepublicans thought they had locked in a historic realignment. Instead, they’re facing a California-style electoral disaster.
🛡️ Security Analyst at UltraViolet Cyber
📍 On-site
Apply: https://blueteamjobs.com/job/security-analyst-ultraviolet-cyber-fyypgp/
 BlueTeamJobsSecurity Analyst at UltraViolet Cyber | BlueTeamJobsUltraViolet Cyber is hiring a Security Analyst. Job Summary We are looking for a Vulnerability Management Analyst with 2–3 years of experience to support…
StealC Malware Returns as Stadia RAT After Operation Endgame Takedown
Four months after Europol’s Operation Endgame disrupted the StealC infostealer, its seller has returned with Stadia, a remote access trojan that reuses StealC v3.5 code, according to Varonis research covered by Hackread. Stadia combines credential theft — targeting more than 50 browsers, 120 cryptocurrency browser extensions and 50 desktop wallets — with hidden desktop control, remote command execution and a loader, and is sold by subscription starting at $300 a month, with former StealC customers offered a free month of the Pro tier. https://hackread.com/stealc-malware-stadia-rat-operation-endgame-takedown/
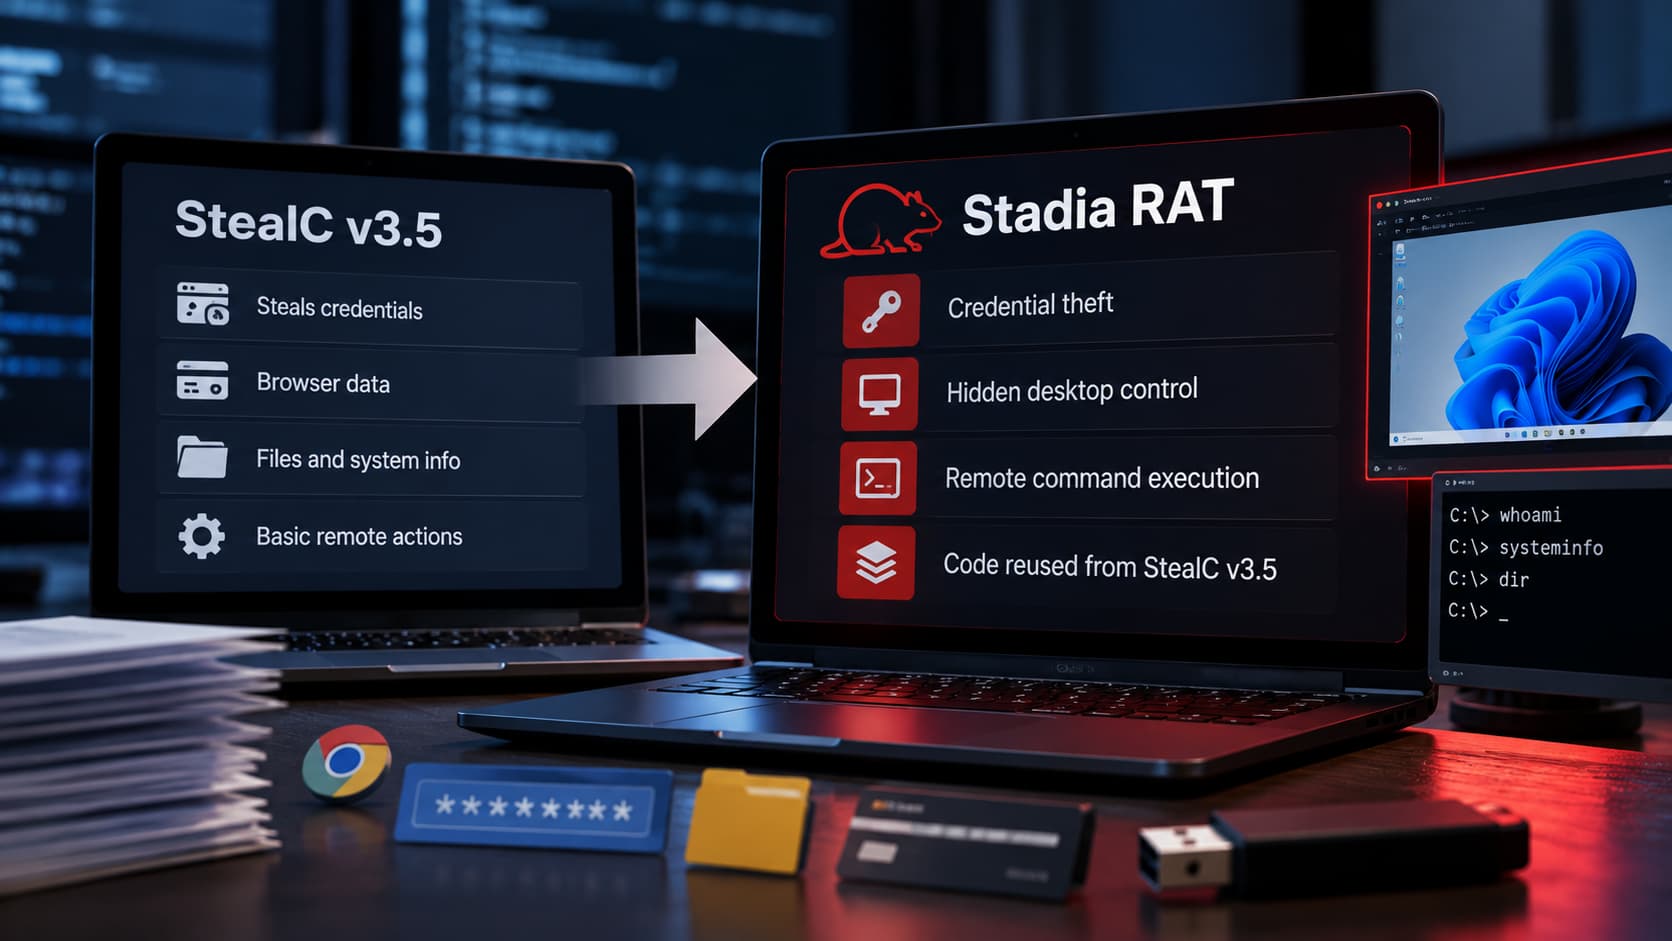 Hackread - Cybersecurity News, Data Breaches, AI and MoreStealC Malware Returns as Stadia RAT After Operation Endgame TakedownStealC's seller has returned with Stadia RAT, combining credential theft, hidden desktop control, and remote command execution using code reused from StealC v3.5.
Gheist Uses Stolen GitHub Tokens to Steal Private Repository Secrets via Actions Logs
An automated campaign dubbed Gheist is using stolen GitHub tokens to plant workflows that print a repository’s secrets into its GitHub Actions logs, which the attackers then download before deleting the runs, The Hacker News reports. According to analysis by cloud security company Wiz, the attacks have succeeded in private repositories and GitHub Enterprise environments. https://thehackernews.com/2026/10/gheist-uses-stolen-github-tokens-to.html
 The Hacker NewsGheist Uses Stolen GitHub Tokens to Steal Private Repository Secrets via Actions LogsGheist uses stolen GitHub tokens to extract secrets through Actions logs, planting over 13,500 branches across 850 compromised accounts.
🛡️ CyberHost Malware List · 26 Oct
+136 new domains blocked (96,807 total)
Top TLDs: .com · .org · .tv
Intel: VirusTotal (91), malwrhunterteam, monitorsg
Source links in the replies ↓
Full list: https://cyberhost.uk/malware-blocklist
 CyberHost🛡️CyberHost Malware and Phishing BlocklistUpdated Regularly | Free to Use | Verified Malicious Domains
Overview
Our Malware & Phishing Blocklist is a carefully curated list of known malicious domains, collected from reputable public threat intelligence sources, Infosec communities, and user submissions.
🔗 Available via: https://lists.cyberhost.uk/malware.txt
📜 License: CC BY-SA 4.0
Alternative Formats
Genesys Hack Exposes Customer Data From Internal Systems
Genesys says hackers accessed its internal business systems, including a learning management system and a customer relationship management environment, and likely downloaded business and account information such as names, phone numbers, business email addresses and job titles, SecurityWeek reports. The company says its Genesys Cloud, Genesys Engage and Genesys Engage Cloud platforms were not compromised, that the incident it announced on October 19 was fully contained by October 23, and that a recently emerged group called ScarlettGroup has claimed the attack. https://www.securityweek.com/genesys-hack-exposes-customer-data-from-internal-systems/
 SecurityWeekGenesys Hack Exposes Customer Data From Internal SystemsGenesys says it has contained a cyberattack that resulted in unauthorized access and theft of data from its LMS and CRM environments.
Cross-request KV cache exposure in the GLM-5.3 Workers AI model, and our remediation with SGLang
Cloudflare has disclosed that a configuration mismatch in the GLM-5.3 model on Workers AI, combined with a bug in the SGLang inference engine, caused some responses to contain data from other customers' requests between August 27 and September 9, 2026. In total 155 responses were affected, all to prompts longer than 681,280 tokens; Cloudflare says it found no evidence of deliberate exploitation, took the model offline within a day of the report, and has patched the engine and its configuration as part of a coordinated disclosure. https://blog.cloudflare.com/kv-cache-exposure-remediation/
 Cloudflare BlogCross-request KV cache exposure in the GLM-5.3 Workers AI model, and our remediation with SGLangA configuration mismatch in GLM 5.3 on Workers AI triggered an SGLang bug that exposed KV cache pages across requests. Here is how we addressed the issue.

از میان کانالهایی که آخرین اخبار سیاسی را منتشر میکنند، فقط یکی را دنبال میکردم که از بقیه خلوتتر هم بود. چند روزی است همانیکی را هم به کانالهای بایگانیشده منتقل کردهام و فقط روزی یک بار نگاهی گذرا به آن میاندازم تا خیلی هم از رخدادها بیخبر نمانم.
این کار واقعاً کمک کرده اضطراب ناشی از پیگیری اخبار کمتر شود. جالب اینجاست که با وجود این فاصله گرفتن، اصلاً احساس نمیکنم چیزی را از دست دادهام. انگار میشود هم خیلی از خبرها دور نماند و هم آرامش بیشتری داشت.

Serbia, Brazil...come on Israel, make it three in a row!

Wordle 1,956 Show content
#Wordle 1,956 4/6*
⬜⬜⬜⬜⬜
⬜⬜🟨🟨⬜
🟨🟨🟨⬜⬜
🟩🟩🟩🟩🟩

The Joys of Privatization https://www.blogger.com/feeds/6293408133336820692/posts/default/8430740146598776835
Water rates in the United States are 62% more then they were in 2016, well above the rate of inflation.Maybe selling off government owned water systems to private for a few magic beans was not a good idea.US households are paying 62% more for drinking water than they did a decade ago – outpacing inflation, grocery prices and household incomes, according to a new study.Food & Water
UK government met 137 businesses over AI datacentres – but no environmental groups
https://www.theguardian.com/uk-news/2026/oct/27/uk-government-environmental-groups-ai-datacentres-expansion-plans-investigation
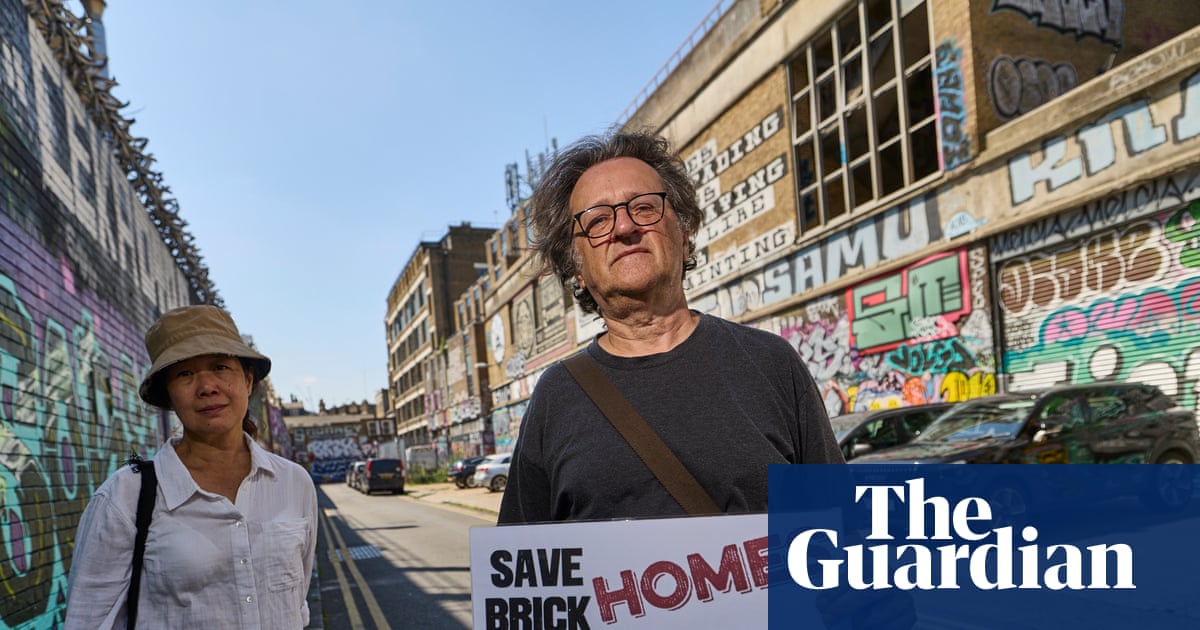 the GuardianUK government met 137 businesses over AI datacentres – but no environmental groupsInvestigation finds dozens of ministers and civil servants moved into AI roles as government developed datacentre expansion plans
Book of Wills
"In Gaza, where the world wavers between silence and forgetting, the written word becomes a final sanctuary – a fragile, luminous act of survival,”
 Middle East MonitorBook of Wills“In Gaza, where the world wavers between silence and forgetting, the written word becomes a final sanctuary – a fragile, luminous act of survival,” Reem Ghanayem writes in the Editor’s Note to the …

вот уже последний луч осенний
держится за суть едва едва
хорошо когда души спасенье
вскрыло все покровы бытия

I swear if I were able I would ban the use of the word 'shape' in regard to describing anything code related.
Workshop Antikorupsi KPK, Gubernur Andra Soni Tekankan Penyelenggara Negara di Banten Perkuat Integritas
BANTEN, dialoguejakarta.com - Pemerintah Provinsi (Pemprov) Banten terus mengoptimalkan pendidikan dan pencegahan korupsi di lingkungan pemerintahan. Upaya penguatan integritas ini ditekankan kepada seluruh penyelenggara negara, baik di tingkat eksekutif maupun legislatif. Hal tersebut disampaikan Gubernur Banten Andra Soni pada Workshop Integritas dan Antikorupsi…
 Dialoguejakarta.comWorkshop Antikorupsi KPK, Gubernur Andra Soni Tekankan Penyelenggara Negara di Banten Perkuat IntegritasBANTEN, dialoguejakarta.com – Pemerintah Provinsi (Pemprov) Banten terus mengoptimalkan pendidikan dan pencegahan korupsi di lingkungan pemerintahan. Upaya penguatan integritas ini ditekankan…

Das #PlayFestival sieht sehr interessant aus (aber ist dieses Jahr zu weit weg für mich) – aber schon wieder eine Veranstaltung, die einem einfach nicht verraten will, wo sie stattfindet!
Weder unter "Über" noch unter "Programm" erfährt man irgendetwas über den Ort. Unter "Besuch" gibt es zwar Adressen, aber keinen Hinweis auf die Stadt, in der sie sich befinden! Klar, auf der interaktiven Karte finde selbst ich als Nicht-Hamburger mehr heraus, aber da gibt es wirklich noch Verbesserungsbedarf!
Originally released in the late 90s, Ecstatica and Ecstatica II are survival-horror games with a unique style not to be missed.
https://www.gamingonlinux.com/2026/10/classic-survivor-horrors-ecstatica-and-ecstatica-ii-get-re-released-with-upgrades/
#Steam #Wine #Horror #Survival #GOG #Retro #Proton #NewRelease
 GamingOnLinuxClassic survival-horrors Ecstatica and Ecstatica II get re-released with upgradesOriginally released in the late 90s, Ecstatica and Ecstatica II are survival-horror games with a unique style not to be missed.
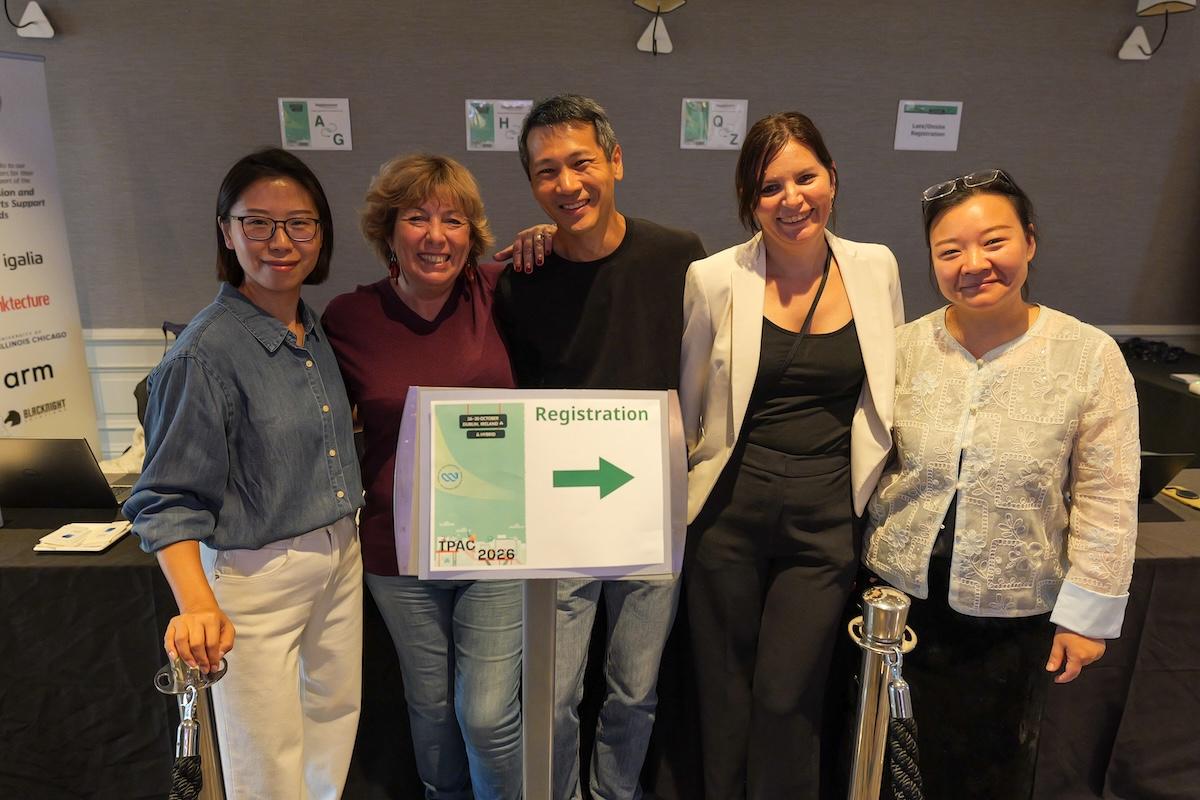
We welcome TPAC 2026 Dublin attendees to Day 2! 👋 👋 🇮🇪
It's an exciting and busy day with Group meetings, Breakouts, our All Community meeting and more!
https://www.w3.org/news-events/tpac/2026/schedule/#tuesday-27-october
#w3cTPAC #aboutW3C
 W3CScheduleThis page provides a high-level view of each day’s schedule during TPAC 2026.
CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added the two PHP2Shell flaws, CVE-2026-109618 and CVE-2026-109619, to its Known Exploited Vulnerabilities catalog, confirming active exploitation of the unauthenticated remote code execution vulnerabilities, both rated CVSS 9.2. The flaws were fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21, federal agencies have until October 29 to apply the fixes, and Censys estimates more than 32.5 million PHP services are still running an affected version. https://thehackernews.com/2026/10/cisa-confirms-active-exploitation-of.html
 The Hacker NewsCISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code ExecutionCISA adds two exploited PHP2Shell flaws to its KEV catalog after honeypot tests confirm remote code execution on a single-worker mod_php setup.

🎤 ■ Rauw Alejandro y las colaboraciones de su próximo álbum: ¿Dei V, Yovng Chimi, Kali Uchis, Myke Towers y Eladio Carrión? ■
https://los40.com/2026/10/27/rauw-alejandro-y-las-colaboraciones-de-su-proximo-album-dei-v-yovng-chimi-kali-uchis-myke-towers-y-eladio-carrion/?int=MASTODON_WORLD
#discosmusica #colaboracionmusical #los40urban #rauwalejandro
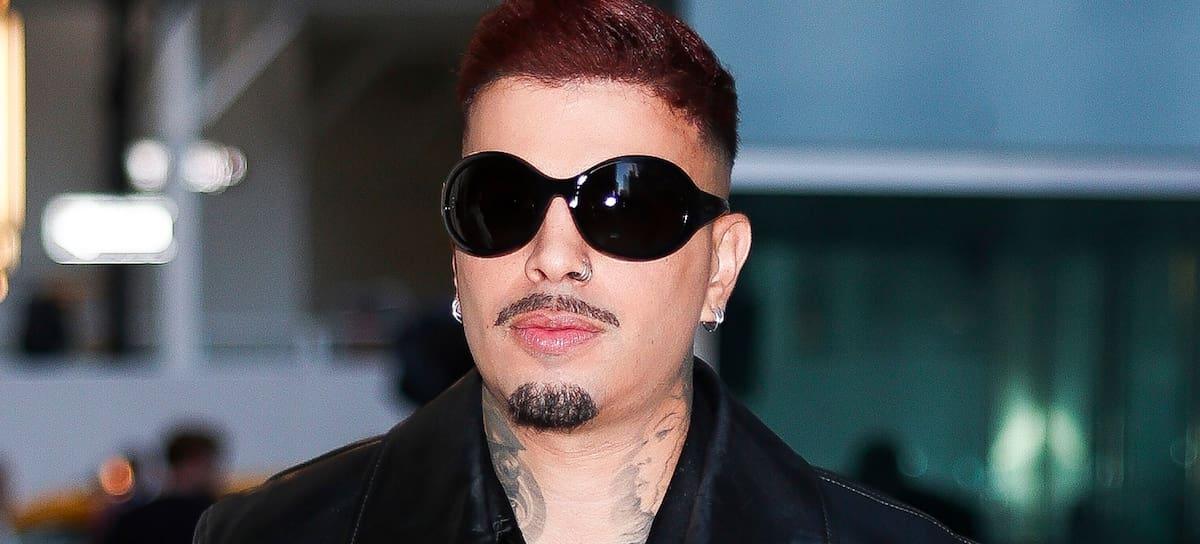
 LOS40Rauw Alejandro y las colaboraciones de su próximo álbum: ¿Dei V, Yovng Chimi, Kali Uchis, Myke Towers y Eladio Carrión? | LOS40 Urban | LOS40El Zorro da pistas sobre lo que se viene y no solo en lo musical

Fixed the issue with the DEF CON directory only being visible when using our .onion address. Now debugging our missing updates header. #InfoCon

Denver Health Medical Plan Discloses 14-Month Data Exposure via Vendor Credential Leak
Denver Health Medical Plan disclosed that a vendor inadvertently published an active access key online, potentially exposing the health and personal data of 238,083 members for 14 months.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/denver-health-medical-plan-discloses-14-month-data-exposure-via-vendor-credential-leak-m-x-9-7-8/gD2P6Ple2L
 BeyondMachinesDenver Health Medical Plan Discloses 14-Month Data Exposure via Vendor Credential LeakDenver Health Medical Plan disclosed that a vendor inadvertently published an active access key online, potentially exposing the health and personal data of 238,083 members for 14 months.